Commit 566a5ce4ec
Unsigned
Layout: unified · split
content/blog/2024-02-21-self-hosting-otter-wiki.md added +135
| @@ -0,0 +1,135 @@ | |||
| 1 | +++ | ||
| 2 | date = 2024-02-21 | ||
| 3 | title = "Self-Hosting An Otter Wiki" | ||
| 4 | description = "Learn how to easily self-host An Otter Wiki." | ||
| 5 | +++ | ||
| 6 | |||
| 7 | ## An Otter Wiki | ||
| 8 | |||
| 9 | [An Otter Wiki](https://otterwiki.com/) is an easy to use wiki software that | ||
| 10 | takes almost no effort to set up and maintain. | ||
| 11 | |||
| 12 | ## Installation | ||
| 13 | |||
| 14 | To install An Otter Wiki, I'm going to use Docker Compose to create the | ||
| 15 | container and then use Nginx as a reverse proxy to allow external access via a | ||
| 16 | subdomain I own. | ||
| 17 | |||
| 18 | ### Docker Compose | ||
| 19 | |||
| 20 | Start by creating a directory for the container's files. | ||
| 21 | |||
| 22 | ```sh | ||
| 23 | mkdir ~/otterwiki | ||
| 24 | ``` | ||
| 25 | |||
| 26 | Next, create the `docker-compose.yml` file to define the container's parameters. | ||
| 27 | |||
| 28 | ```sh | ||
| 29 | nano ~/otterwiki/docker-compose.yml | ||
| 30 | ``` | ||
| 31 | |||
| 32 | Within the file, paste the following content. You can read the project's | ||
| 33 | documentation if you want to further override or customize the container. | ||
| 34 | |||
| 35 | ```conf | ||
| 36 | version: '3' | ||
| 37 | services: | ||
| 38 | otterwiki: | ||
| 39 | image: redimp/otterwiki:2 | ||
| 40 | restart: unless-stopped | ||
| 41 | # Internal port must be assigned to port 80 | ||
| 42 | # External port can be customized | ||
| 43 | ports: | ||
| 44 | - 8337:80 | ||
| 45 | volumes: | ||
| 46 | - ./app-data:/app-data | ||
| 47 | ``` | ||
| 48 | |||
| 49 | Once the file is saved and closed, you can launch the container. | ||
| 50 | |||
| 51 | ```sh | ||
| 52 | cd ~/otterwiki | ||
| 53 | sudo docker-compose up -d | ||
| 54 | ``` | ||
| 55 | |||
| 56 | The container is now available at `localhost:8337`. Next, we will use Nginx to | ||
| 57 | serve this app externally. | ||
| 58 | |||
| 59 | ### Nginx | ||
| 60 | |||
| 61 | To access the app externally, let's set up a reverse proxy. I'll start by | ||
| 62 | creating the Nginx configuration file for my wiki. | ||
| 63 | |||
| 64 | ```sh | ||
| 65 | sudo nano /etc/nginx/sites-available/wiki | ||
| 66 | ``` | ||
| 67 | |||
| 68 | Within the file, I have saved the following content. This assumes you already | ||
| 69 | have a TLS/SSL cert to use with this subdomain. If not, simply remove the | ||
| 70 | `ssl_*` variables, remove the `80` server block, and change the `443` | ||
| 71 | server block to `80` to serve the app without SSL. | ||
| 72 | |||
| 73 | ```conf | ||
| 74 | server { | ||
| 75 | if ($host ~ ^[^.]+\.example\.com$) { | ||
| 76 | return 301 https://$host$request_uri; | ||
| 77 | } | ||
| 78 | |||
| 79 | listen [::]:80; | ||
| 80 | listen 80; | ||
| 81 | server_name wiki.example.com; | ||
| 82 | return 404; | ||
| 83 | } | ||
| 84 | |||
| 85 | server { | ||
| 86 | listen [::]:443 ssl http2; | ||
| 87 | listen 443 ssl http2; | ||
| 88 | server_name wiki.example.com; | ||
| 89 | access_log /var/log/nginx/wiki.access.log; | ||
| 90 | error_log /var/log/nginx/wiki.error.log; | ||
| 91 | |||
| 92 | ssl_certificate /etc/letsencrypt/live/example.com/fullchain.pem; | ||
| 93 | ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem; | ||
| 94 | include /etc/letsencrypt/options-ssl-nginx.conf; | ||
| 95 | ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; | ||
| 96 | |||
| 97 | location / { | ||
| 98 | set $upstream_wiki http://127.0.0.1:8337; | ||
| 99 | proxy_pass $upstream_wiki; | ||
| 100 | |||
| 101 | proxy_set_header Host $http_host; | ||
| 102 | proxy_set_header X-Real-IP $remote_addr; | ||
| 103 | proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for; | ||
| 104 | proxy_set_header X-Forwarded-Host $http_host; | ||
| 105 | } | ||
| 106 | } | ||
| 107 | ``` | ||
| 108 | |||
| 109 | Save and close the configuration file. On Nginx, we need to symlink the file to | ||
| 110 | enable it. | ||
| 111 | |||
| 112 | ```sh | ||
| 113 | sudo ln -s /etc/nginx/sites-available/wiki /etc/nginx/sites-enabled/wiki | ||
| 114 | ``` | ||
| 115 | |||
| 116 | Once enabled, restart the Nginx server to start serving the app externally. | ||
| 117 | |||
| 118 | ```sh | ||
| 119 | sudo systemctl restart nginx.service | ||
| 120 | ``` | ||
| 121 | |||
| 122 | ## Screenshots | ||
| 123 | |||
| 124 | In the screenshot below, you can see the initial launch screen for An Otter | ||
| 125 | Wiki. Start by creating your admin account and configure the app as necessary. | ||
| 126 | |||
| 127 | 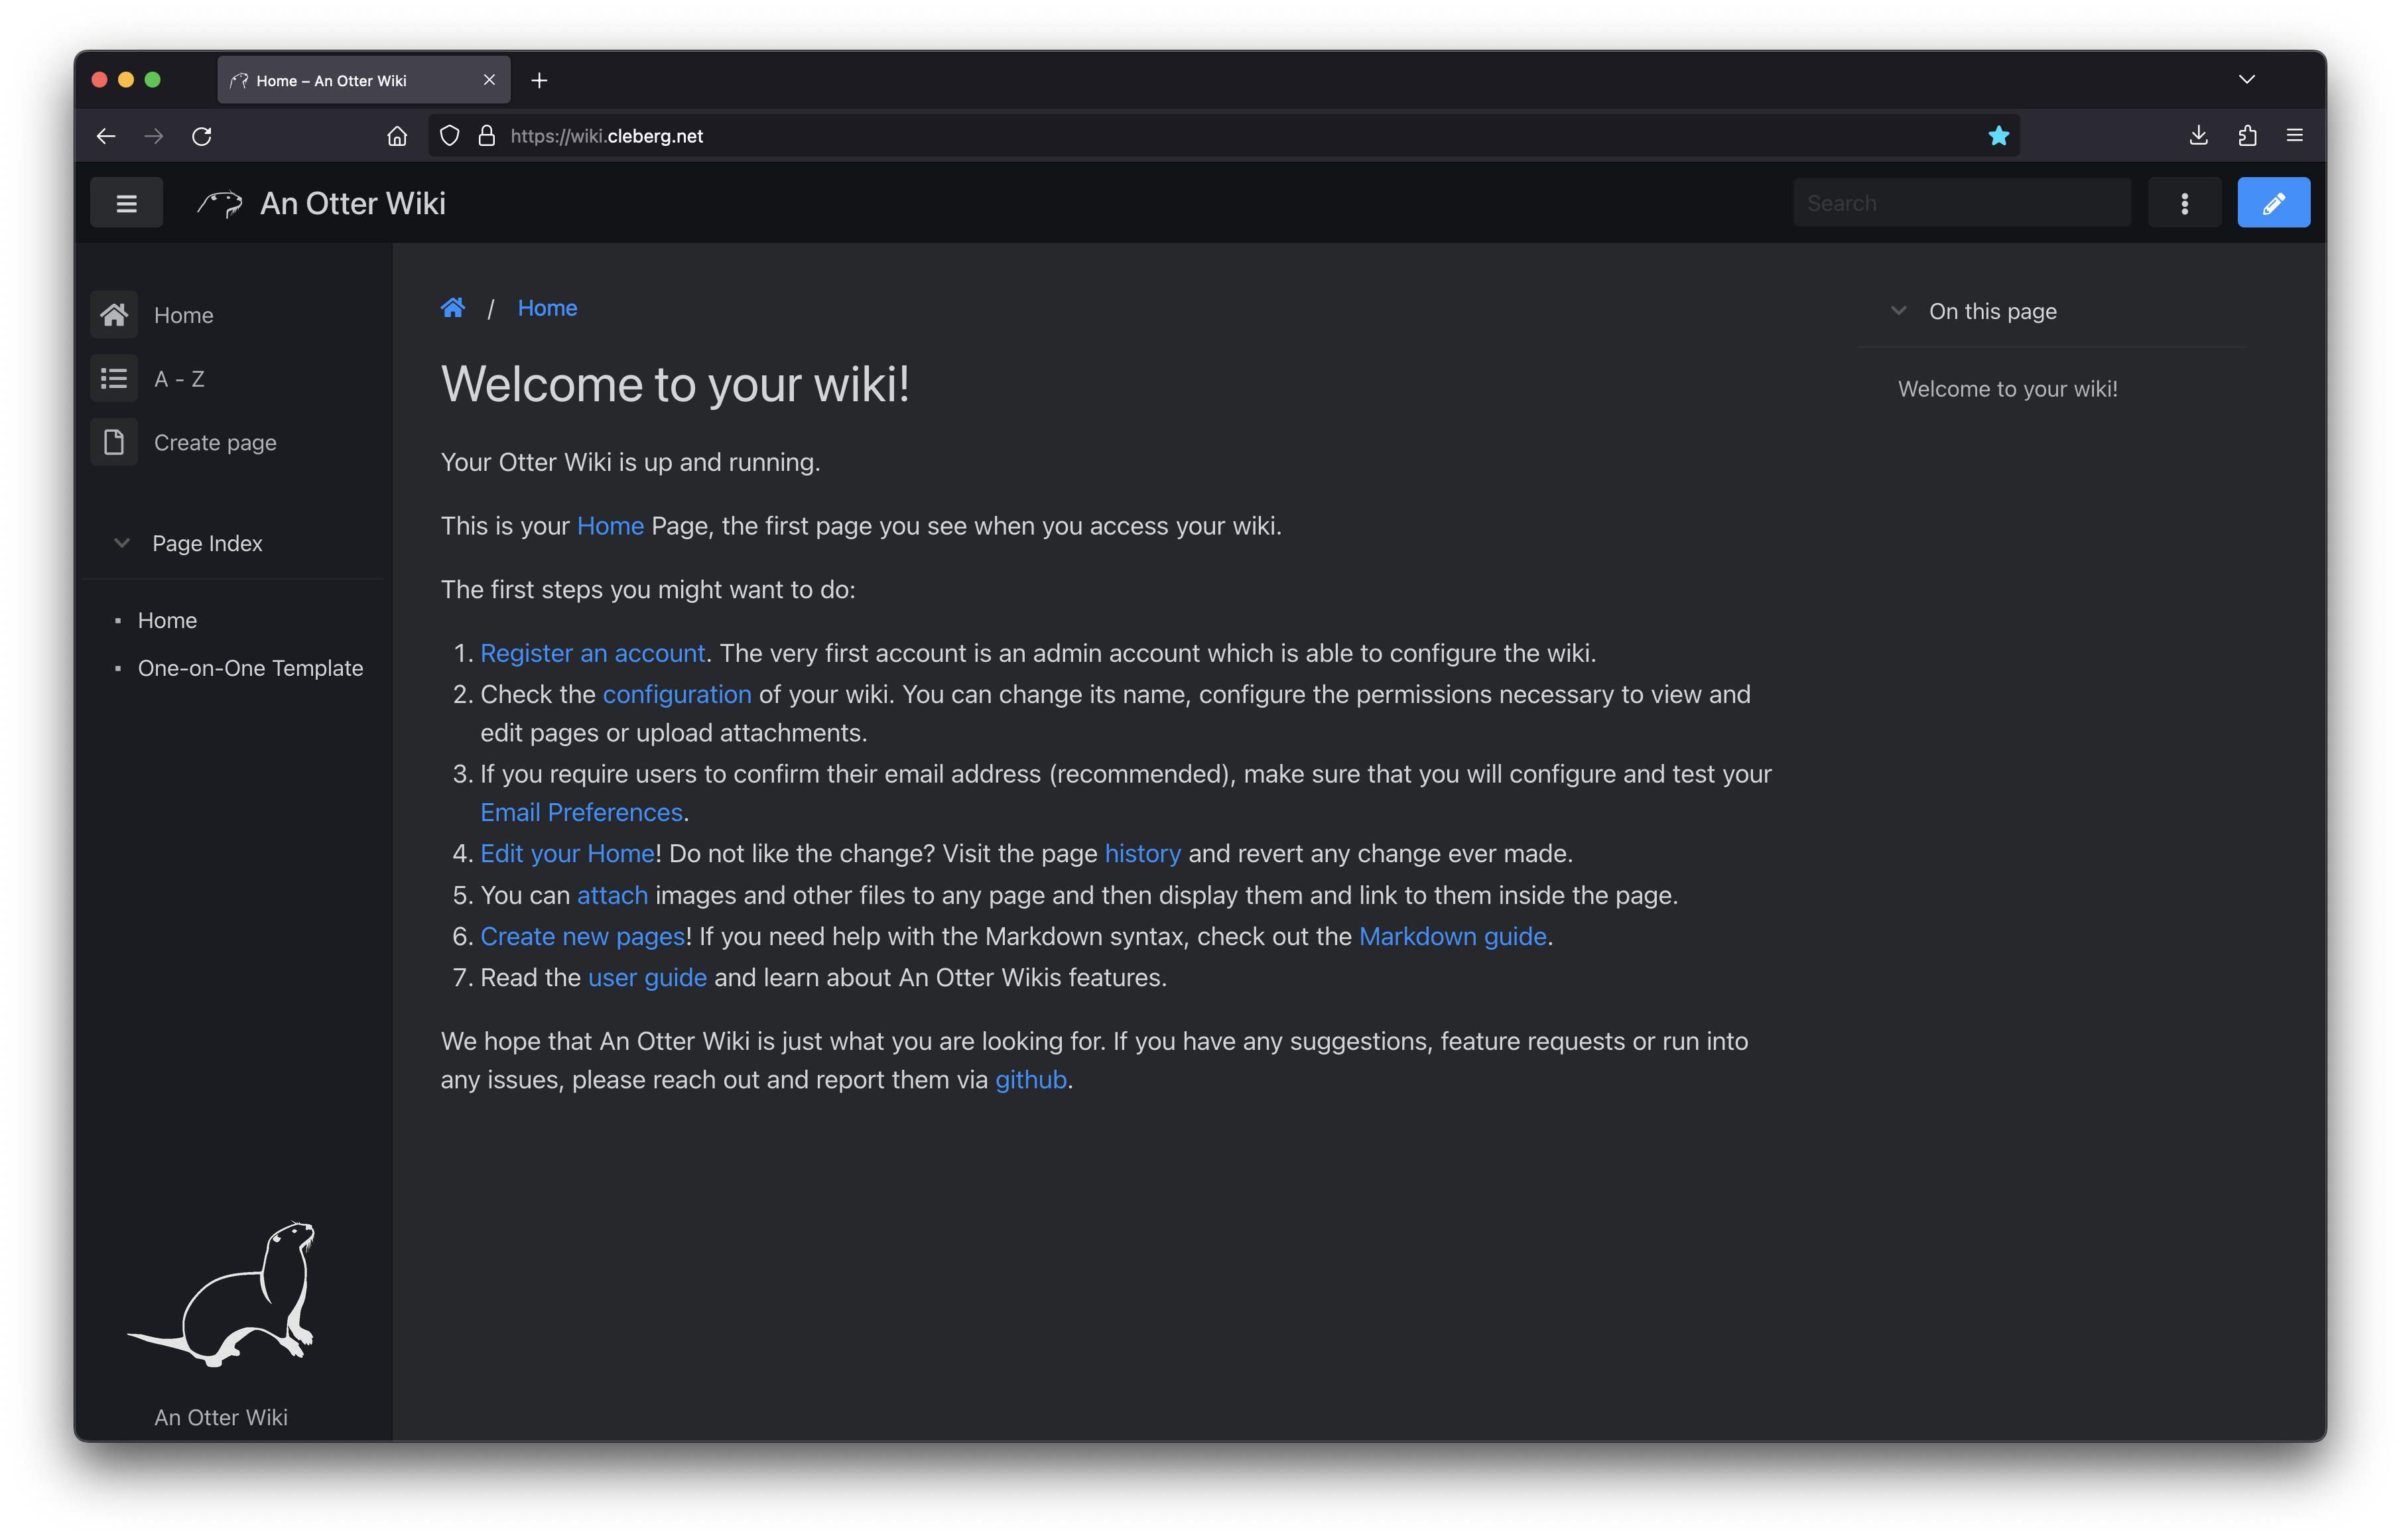 | ||
| 128 | |||
| 129 | You can also see the default editing screen for creating and editing pages. It's | ||
| 130 | as easy as typing Markdown and hitting the save button. | ||
| 131 | |||
| 132 | 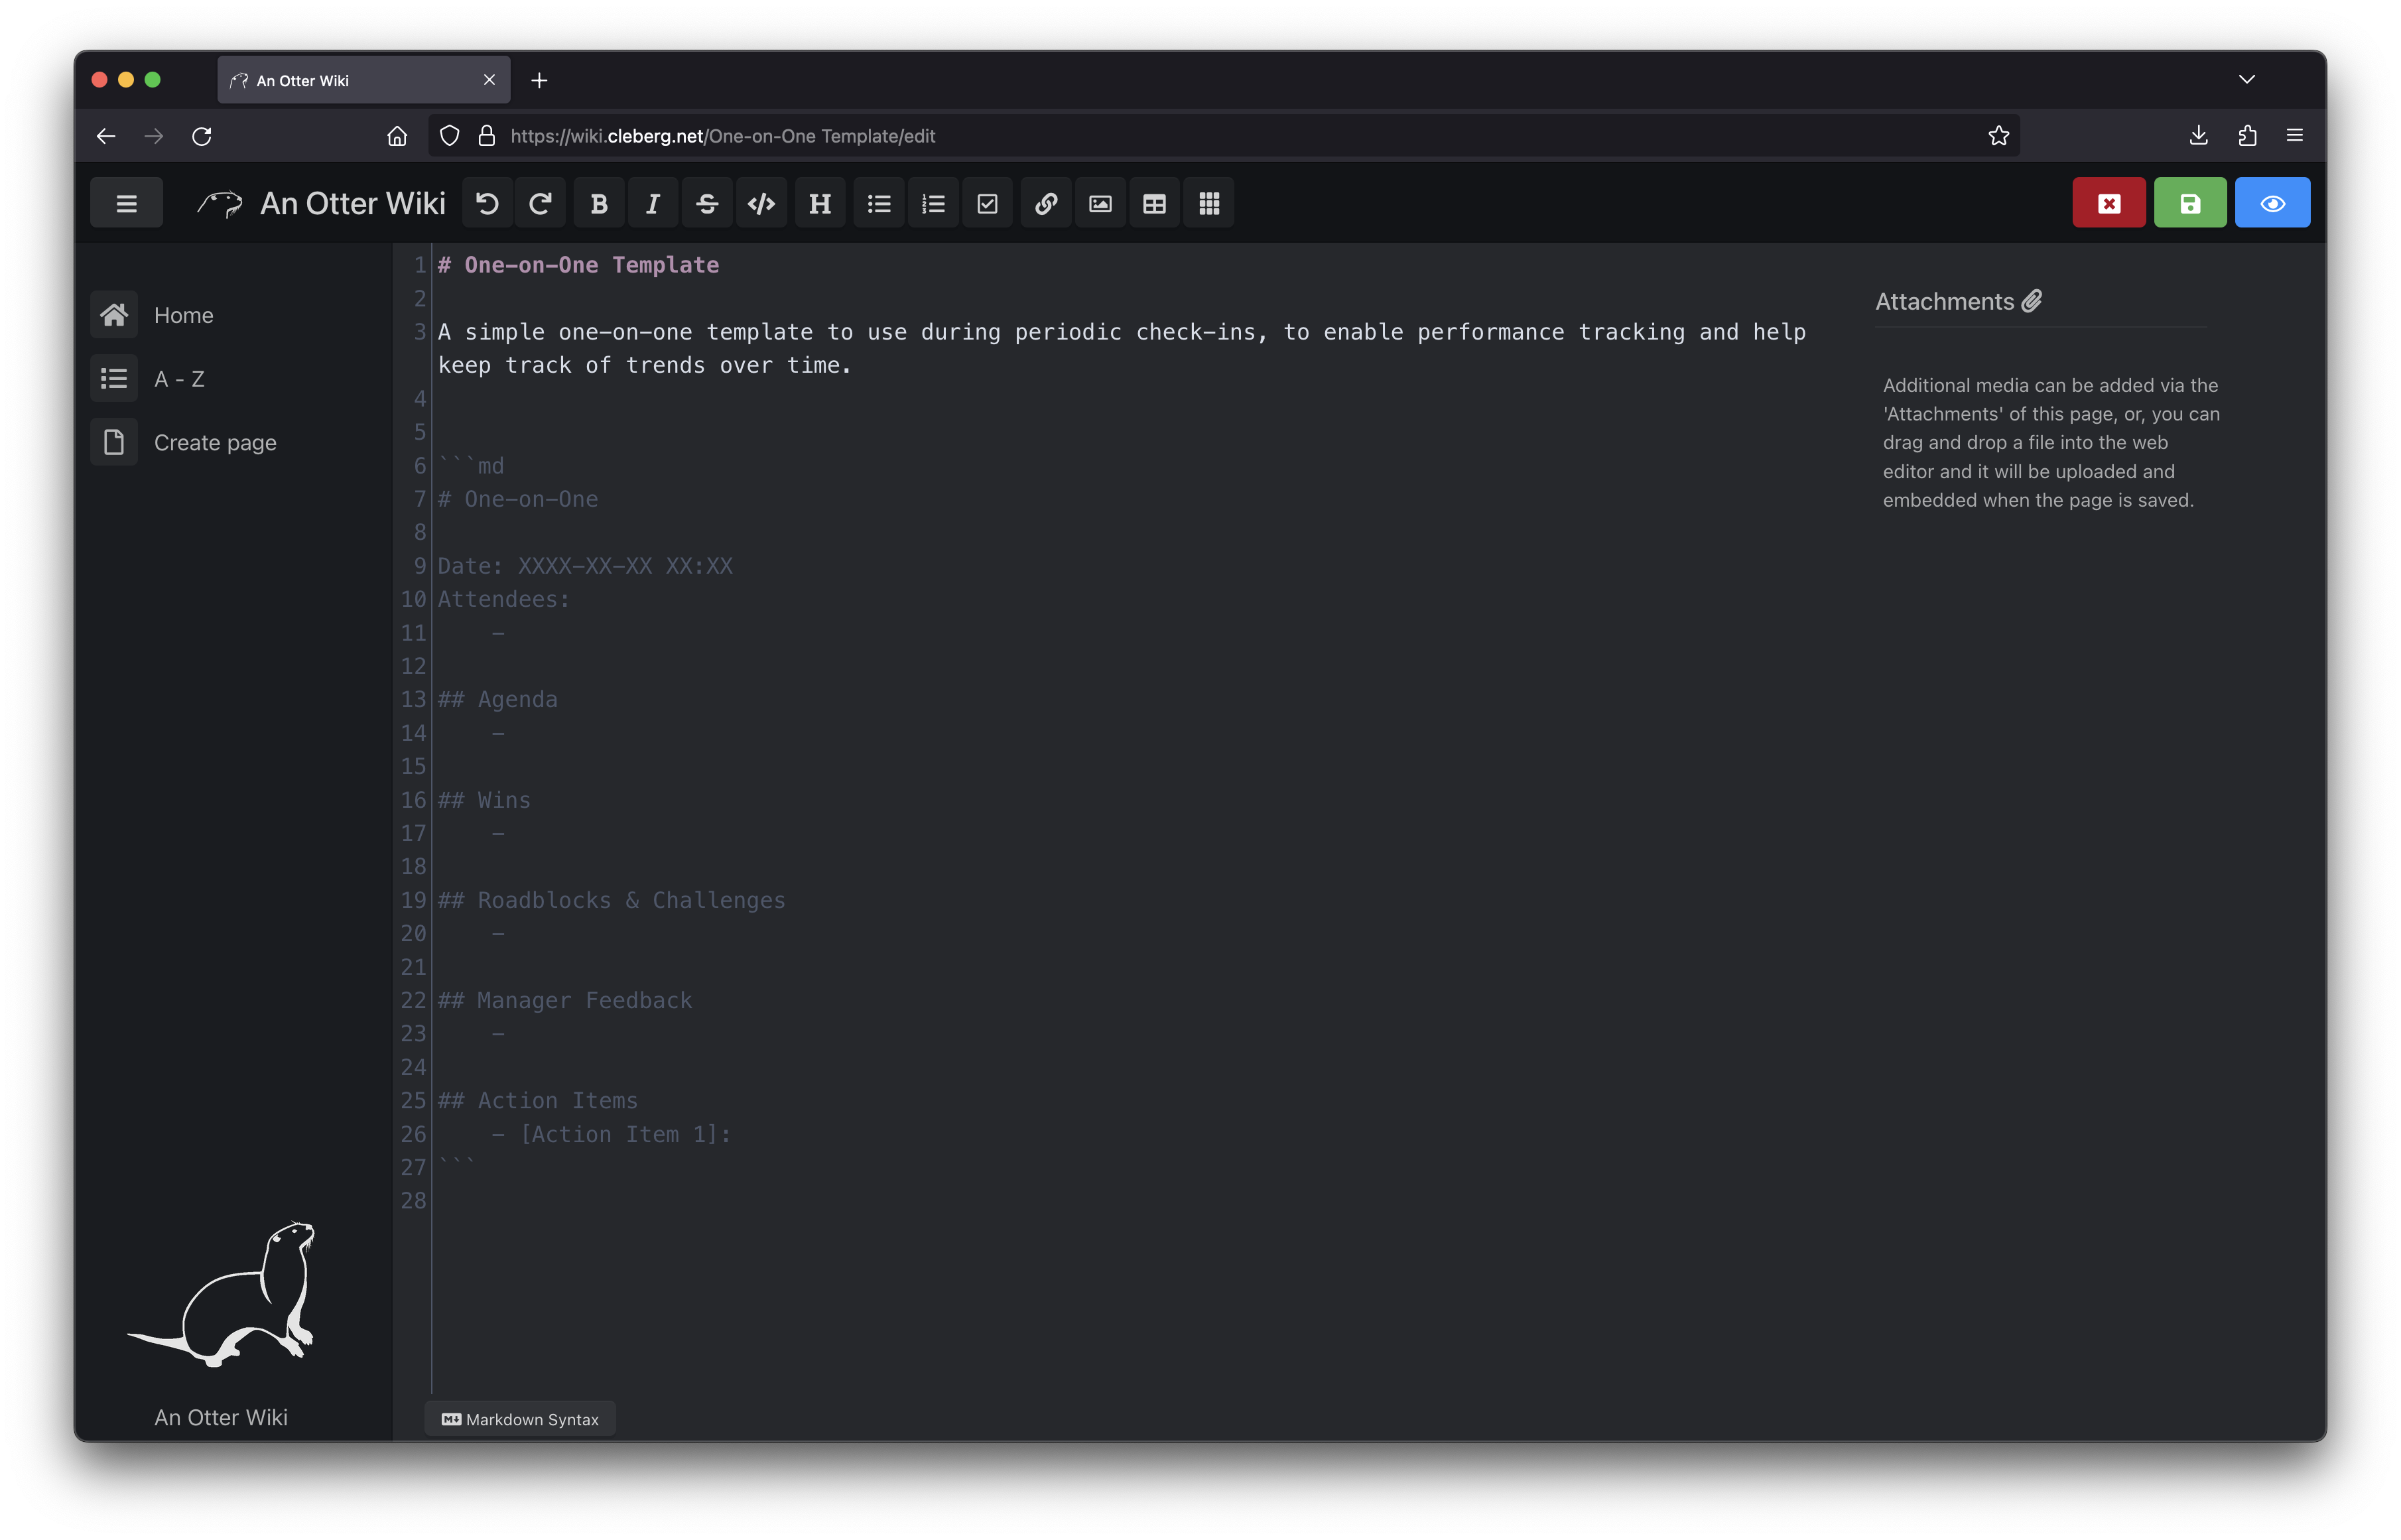 | ||
| 133 | |||
| 134 | Overall, I like An Otter Wiki and will be looking forward to seeing how much use | ||
| 135 | I get out of it going forward. | ||