Commit c71a52cb7a
Unsigned
Layout: unified · split
.gitignore +2 −2
| @@ -1,3 +1,3 @@ | ||
| 1 | public/ | |
| 2 | static/syntax* | |
| 3 | 1 | .DS_Store |
| 2 | public/* | |
| 3 | sitemap.org | |
README.md deleted −28
| @@ -1,28 +0,0 @@ | ||
| 1 | # cleberg.net | |
| 2 | ||
| 3 | [cleberg.net](https://cleberg.net) is my personal webpage. | |
| 4 | ||
| 5 | ## Overview | |
| 6 | ||
| 7 | This website & blog uses Markdown and [Zola](https://www.getzola.org/). | |
| 8 | ||
| 9 | ## Building | |
| 10 | ||
| 11 | Local testing: | |
| 12 | ||
| 13 | ```sh | |
| 14 | zola serve | |
| 15 | ``` | |
| 16 | ||
| 17 | Building: | |
| 18 | ||
| 19 | ```sh | |
| 20 | zola build | |
| 21 | ``` | |
| 22 | ||
| 23 | If you want to build locally and push remotely, you can include `zola build` | |
| 24 | in your CI\CD pipeline, or simply use `scp` after building. | |
| 25 | ||
| 26 | ```sh | |
| 27 | scp -r public/* user@remote_host:/var/www/your_website/ | |
| 28 | ``` | |
README.org added +83
| @@ -0,0 +1,83 @@ | ||
| 1 | #+title: README | |
| 2 | #+description: Project README. | |
| 3 | ||
| 4 | * cleberg.net | |
| 5 | ||
| 6 | [[https://cleberg.net][cleberg.net]] is my personal webpage. | |
| 7 | ||
| 8 | This README is viewable on [[https://git.cleberg.net/cleberg.net.git/tree/README.org][cgit]] (raw), or on [[https://cleberg.net/README.html][my website]] (html). | |
| 9 | ||
| 10 | ** Overview | |
| 11 | ||
| 12 | This website & blog uses [[https://orgmode.org/][Org-Mode]], published with =org-publish=. | |
| 13 | ||
| 14 | ** Configuration | |
| 15 | ||
| 16 | In order to configure the project for publishing, add the following code to your =~/.emacs= file (for Doom, =~/.doom.d/config.el=). | |
| 17 | ||
| 18 | #+begin_src lisp | |
| 19 | ;; org-publish | |
| 20 | (require 'ox-publish) | |
| 21 | ||
| 22 | (setq org-publish-project-alist | |
| 23 | `(("blog" | |
| 24 | :base-directory "~/Source/cleberg.net/" | |
| 25 | :base-extension "org" | |
| 26 | :recursive t | |
| 27 | :publishing-directory "~/Source/cleberg.net/public/" | |
| 28 | :publishing-function org-html-publish-to-html) | |
| 29 | ;; HTML5 | |
| 30 | :html-doctype "html5" | |
| 31 | :html-html5-fancy t | |
| 32 | ;; Disable some Org's HTML defaults | |
| 33 | :html-head-include-scripts nil | |
| 34 | :html-head-include-default-style nil | |
| 35 | ;; Generate sitemap | |
| 36 | :auto-sitemap t | |
| 37 | :sitemap-filename "sitemap.org" | |
| 38 | ;; Customize head, preamble, & postamble | |
| 39 | :html-head "<link rel='stylesheet' href='/static/styles.css' type='text/css'>" | |
| 40 | :html-preamble "" | |
| 41 | :html-postamble "" | |
| 42 | ("static" | |
| 43 | :base-directory "~/Source/cleberg.net/static/" | |
| 44 | :base-extension "css\\|txt\\|jpg\\|gif\\|png" | |
| 45 | :recursive t | |
| 46 | :publishing-directory "~/Source/cleberg.net/public/" | |
| 47 | :publishing-function org-publish-attachment) | |
| 48 | ||
| 49 | ("cleberg.net" :components ("blog" "static"))));; org-publish | |
| 50 | (require 'ox-publish) | |
| 51 | #+end_src | |
| 52 | ||
| 53 | ** Building | |
| 54 | ||
| 55 | Local testing can be done via [[https://www.gnu.org/software/emacs/][Emacs]]. | |
| 56 | ||
| 57 | To get running: | |
| 58 | ||
| 59 | #+begin_src shell | |
| 60 | git clone https://git.cleberg.net/cleberg.net.git | |
| 61 | cd cleberg.net | |
| 62 | emacs -nw | |
| 63 | #+end_src | |
| 64 | ||
| 65 | Within Emacs, open any of the repository files. In Doom, I do this with =Spc f f= and selecting =README.org=. Once a file has been opened, you can publish the project with =C-c C-e P a=. | |
| 66 | ||
| 67 | If you need to re-publish unchanged files, I recommend using the following command: | |
| 68 | ||
| 69 | #+begin_src lisp | |
| 70 | M-: (org-publish "project name" t) | |
| 71 | #+end_src | |
| 72 | ||
| 73 | The files will be published to the =public= directory. | |
| 74 | ||
| 75 | ** Tasks | |
| 76 | ||
| 77 | *** TODO Create RSS feed | |
| 78 | Possible Solution: [[https://writepermission.com/org-blogging-rss-feed.html][Org mode blogging: RSS feed]] | |
| 79 | Possible Solution: [[https://www.zoraster.org/blog/script-to-generate-rss-feed][Script to Generate RSS Feeds]] | |
| 80 | *** TODO Format all blog posts with =M q= | |
| 81 | *** TODO Create script to auto-generate the =/blog/= list and =/= most recent posts | |
| 82 | Possible Solution: [[https://taingram.org/blog/org-mode-blog.html#orgde61a58][Sitemap]] | |
| 83 | *** TODO Figure out how to get filetags to show up | |
blog/aes-encryption/index.org added +103
| @@ -0,0 +1,103 @@ | ||
| 1 | #+title: AES Encryption | |
| 2 | #+description: Learn how the AES Encryption algorithm works. | |
| 3 | #+date: <2018-11-28 Wed> | |
| 4 | #+filetags: :security: | |
| 5 | ||
| 6 | * Basic AES | |
| 7 | If you're not familiar with encryption techniques, [[https://en.wikipedia.org/wiki/Advanced_Encryption_Standard][AES]] is the *Advanced | |
| 8 | Encryption Standard*. This specification was established by the National | |
| 9 | Institute of Standards and Technology, sub-selected from the Rijndael family of | |
| 10 | ciphers (128, 192, and 256 bits) in 2001. Furthering its popularity and status, | |
| 11 | the US government chose AES as their default encryption method for top-secret | |
| 12 | data, removing the previous standard which had been in place since 1977. | |
| 13 | ||
| 14 | AES has proven to be an extremely safe encryption method, with 7-round and | |
| 15 | 8-round attacks making no material improvements since the release of this | |
| 16 | encryption standard almost two decades ago. | |
| 17 | ||
| 18 | #+begin_quote | |
| 19 | Though many papers have been published on the cryptanalysis of AES, the fastest | |
| 20 | single-key attacks on round-reduced AES variants [20, 33] so far are only | |
| 21 | slightly more powerful than those proposed 10 years ago [23,24]. | |
| 22 | ||
| 23 | - [[http://research.microsoft.com/en-us/projects/cryptanalysis/aesbc.pdf][Bogdonav, et al.]] | |
| 24 | #+end_quote | |
| 25 | ||
| 26 | * How Secure is AES? | |
| 27 | In theory, AES-256 is non-crackable due to the massive number of combinations | |
| 28 | that can be produced. However, AES-128 is no longer recommended as a viable | |
| 29 | implementation to protect important data. | |
| 30 | ||
| 31 | A semi-short [[http://www.moserware.com/2009/09/stick-figure-guide-to-advanced.html][comic strip]] from Moserware quickly explains AES for the public to | |
| 32 | understand. Basically AES encrypts the data by obscuring the relationship | |
| 33 | between the data and the encrypted data. Additionally, this method spreads the | |
| 34 | message out. Lastly, the key produced by AES is the secret to decrypting it. | |
| 35 | Someone may know the method of AES, but without the key, they are powerless. | |
| 36 | ||
| 37 | To obscure and spread the data out, AES creates a substitution-permutation | |
| 38 | network. Wikipedia has a wonderful [[https://upload.wikimedia.org/wikipedia/commons/thumb/c/cd/SubstitutionPermutationNetwork2.png/468px-SubstitutionPermutationNetwork2.png][example of an SP network]] available. This | |
| 39 | network sends the data through a set of S boxes (using the unique key) to | |
| 40 | substitute the bits with another block of bits. Then, a P box will permutate, or | |
| 41 | rearrange, the bits. This is done over and over, with the key being derived from | |
| 42 | the last round. For AES, the key size specifies the number of transformation | |
| 43 | rounds: 10, 12, and 14 rounds for 128-bit, 192-bit, and 256-bit keys, | |
| 44 | respectively. | |
| 45 | ||
| 46 | * The Process | |
| 47 | 1. *KeyExpansion=: Using [[https://en.m.wikipedia.org/wiki/Advanced_Encryption_Standard][Rijndael's key schedule]], the keys are dynamically | |
| 48 | generated. | |
| 49 | 2. *AddRoundKey*: Each byte of the data is combined with this key using bitwise | |
| 50 | xor. | |
| 51 | 3. *SubBytes*: This is followed by the substitution of each byte of data. | |
| 52 | 4. *ShiftRows*: Then, the final three rows are shifted a certain number of | |
| 53 | steps, dictated by the cipher. | |
| 54 | 5. *MixColumns*: After the rows have been shifted, the columns are mixed and | |
| 55 | combined. | |
| 56 | ||
| 57 | This process does not necessarily stop after one full round. Steps 2 through 5 | |
| 58 | will repeat for the number of rounds specified by the key. However, the final | |
| 59 | round excludes the MixColumns step. As you can see, this is a fairly complex | |
| 60 | process. One must have a solid understanding of general mathematic principles to | |
| 61 | fully understand how the sequence works (and to even attempt to find a | |
| 62 | weakness). | |
| 63 | ||
| 64 | According to research done by Bogdanov et al., it would take billions of years | |
| 65 | to brute force a 126-bit key with current hardware. Additionally, this brute | |
| 66 | force attack would require storing 2^{88} bits of data! However, there are a few | |
| 67 | different attacks that have been used to show vulnerabilities with the use of | |
| 68 | this technology. Side-channel attacks use inadvertent leaks of data from the | |
| 69 | hardware or software, which can allow attackers to obtain the key or run | |
| 70 | programs on a user's hardware. | |
| 71 | ||
| 72 | Please note that this is not something you should run out and try to implement | |
| 73 | in your =Hello, World!= app after only a few hours of research. While AES | |
| 74 | (basically all encryption methods) is extremely efficient in what it does, it | |
| 75 | takes a lot of time and patience to understand. If you're looking for something | |
| 76 | which currently implements AES, check out the [[https://www.bouncycastle.org/documentation.html][Legion of the Bouncy Castle]] for | |
| 77 | Java implementations of cryptographic algorithms. | |
| 78 | ||
| 79 | * Why Does Encryption Matter? | |
| 80 | There are limitless reasons to enable encryption at-rest or in-transit for | |
| 81 | various aspects of your digital life. You can research specific examples, such | |
| 82 | as [[https://arstechnica.com/tech-policy/2018/12/australia-passes-new-law-to-thwart-strong-encryption/][Australia passes new law to thwart strong encryption]]. However, I will simply | |
| 83 | list a few basic reasons to always enable encryption, where feasible: | |
| 84 | ||
| 85 | 1. Privacy is a human right and is recognized as a national right in some | |
| 86 | countries (e.g., [[https://www.law.cornell.edu/wex/fourth_amendment][US Fourth Amendment]]). | |
| 87 | 2. "Why not?" Encryption rarely affects performance or speed, so there's usually | |
| 88 | not a reason to avoid it in the first place. | |
| 89 | 3. Your digital identity and activity (texts, emails, phone calls, online | |
| 90 | accounts, etc.) are extremely valuable and can result in terrible | |
| 91 | consequences, such as identity theft, if leaked to other parties. Encrypting | |
| 92 | this data prevents such leaks from ruining lives. | |
| 93 | 4. Wiping or factory-resetting does not actually wipe all data from the storage | |
| 94 | device. There are methods to read data from the physical disks/boards inside | |
| 95 | devices. | |
| 96 | 5. Corporations, governments, and other nefarious groups/individuals are | |
| 97 | actively looking for ways to collect personal information about anyone they | |
| 98 | can. If someone's data is unencrypted, that person may become a target due to | |
| 99 | the ease of data collection. | |
| 100 | ||
| 101 | *Read More:* | |
| 102 | ||
| 103 | - [[http://nvlpubs.nist.gov/nistpubs/FIPS/NIST.FIPS.197.pdf][Federal Information Processing Standards Publication 197]] | |
blog/agile-auditing/index.org added +137
| @@ -0,0 +1,137 @@ | ||
| 1 | #+title: Agile Auditing: An Introduction | |
| 2 | #+date: <2023-08-18> | |
| 3 | #+description: A quick introduction to using the Agile methodology in an audit. | |
| 4 | #+filetags: :audit: | |
| 5 | ||
| 6 | * What is Agile Auditing? | |
| 7 | [[https://en.wikipedia.org/wiki/Agile_software_development][Agile]], the collaborative philosophy behind many software development methods, | |
| 8 | has been picking up steam as a beneficial tool to use in the external and | |
| 9 | internal auditing world. | |
| 10 | ||
| 11 | This blog post will walk through commonly used terms within Agile, Scrum, and | |
| 12 | Kanban in order to translate these terms and roles into audit-specific terms. | |
| 13 | ||
| 14 | Whether your team is in charge of a financial statement audit, an attestation | |
| 15 | (SOC 1, SOC 2, etc.), or a unique internal audit, the terms used throughout this | |
| 16 | post should still apply. | |
| 17 | ||
| 18 | * Agile | |
| 19 | To start, I'll take a look at Agile. | |
| 20 | ||
| 21 | #+begin_quote | |
| 22 | The Agile methodology is a project management approach that involves breaking | |
| 23 | the project into phases and emphasizes continuous collaboration and improvement. | |
| 24 | Teams follow a cycle of planning, executing, and evaluating. | |
| 25 | #+end_quote | |
| 26 | ||
| 27 | While this approach may seem familiar to what audit teams have historically | |
| 28 | done, an audit team must make distinct changes in their mentality and how they | |
| 29 | approach and manage a project. | |
| 30 | ||
| 31 | ** Agile Values | |
| 32 | The Agile Manifesto, written in 2001 at a summit in Utah, contain a set of four | |
| 33 | main values that comprise the Agile approach: | |
| 34 | ||
| 35 | 1. Individuals and interactions over processes and tools. | |
| 36 | 2. Working software over comprehensive documentation. | |
| 37 | 3. Customer collaboration over contract negotiation. | |
| 38 | 4. Responding to change over following a plan. | |
| 39 | ||
| 40 | Beyond the four values, [[https://agilemanifesto.org/principles.html][twelve principles]] were also written as part of the | |
| 41 | summit. | |
| 42 | ||
| 43 | In order to relate these values to an audit or attestation engagement, we need | |
| 44 | to shift the focus from software development to the main goal of an engagement: | |
| 45 | completing sufficient audit testing to address to relevant risks over the | |
| 46 | processes and controls at hand. | |
| 47 | ||
| 48 | Audit Examples: | |
| 49 | ||
| 50 | - Engagement teams must value the team members, client contacts, and their | |
| 51 | interactions over the historical processes and tools that have been used. | |
| 52 | - Engagement teams must value a final report that contains sufficient audit | |
| 53 | documentation over excessive documentation or scope creep. | |
| 54 | - Engagement teams must collaborate with the audit clients as much as feasible | |
| 55 | to ensure that both sides are constantly updated with current knowledge of the | |
| 56 | engagement's status and any potential findings, rather than waiting for | |
| 57 | pre-set meetings or the end of the engagement to communicate. | |
| 58 | - Engagement teams must be able to respond to change in an engagement's | |
| 59 | schedule, scope, or environment to ensure that the project is completed in a | |
| 60 | timely manner and that all relevant areas are tested. | |
| 61 | - In terms of an audit department's portfolio, they must be able to respond to | |
| 62 | changes in their company's or client's environment and be able to | |
| 63 | dynamically change their audit plan accordingly. | |
| 64 | ||
| 65 | * Scrum | |
| 66 | The above section discusses the high-level details of the Agile philosophy and | |
| 67 | how an audit team can potentially mold that mindset into the audit world, but | |
| 68 | how does a team implement these ideas? | |
| 69 | ||
| 70 | There are many methods that use an Agile mindset, but I prefer [[https://en.wikipedia.org/wiki/Scrum_(software_development)][Scrum]]. Scrum is a | |
| 71 | framework based on Agile that enables a team to work through a project through a | |
| 72 | series of roles, ceremonies, artifacts, and values. | |
| 73 | ||
| 74 | Let's dive into each of these individually. | |
| 75 | ||
| 76 | ** Scrum Team | |
| 77 | A scrum project is only as good as the team running the project. Standard scrum | |
| 78 | teams are separated into three distinct areas: | |
| 79 | ||
| 80 | 1. *Product Owner (Client Contact)*: The client contact is the audit equivalent | |
| 81 | of the product owner in Scrum. They are responsible for partnering with the | |
| 82 | engagement or audit team to ensure progress is being made, priorities are | |
| 83 | established, and clear guidance is given when questions or findings arise | |
| 84 | within each sprint. | |
| 85 | 2. *Scrum Master (Engagement Lead)*: The engagement or audit team lead is | |
| 86 | responsible for coaching the team and the client contact on the scrum | |
| 87 | process, tracking team progress against plan, scheduling necessary resources, | |
| 88 | and helping remove obstacles. | |
| 89 | 3. *Scrum Developers (Engagement Members)*: The engagement or audit team is the | |
| 90 | set of team members responsible for getting the work done. These team members | |
| 91 | will work on each task, report progress, resolve obstacles, and collaborate | |
| 92 | with other team members and the client contact to ensure goals are being met. | |
| 93 | ||
| 94 | ** Scrum Ceremonies | |
| 95 | Scrum ceremonies are events that are performed on a regular basis. | |
| 96 | ||
| 97 | 1. *Sprint Planning*: The team works together to plan the upcoming sprint goal | |
| 98 | and which user stories (tasks) will be added to the sprint to achieve that | |
| 99 | goal. | |
| 100 | 2. *Sprint*: The time period, typically at least one week and no more than one | |
| 101 | month in length, where the team works on the stories and anything in the | |
| 102 | backlog. | |
| 103 | 3. *Daily Scrum*: A very short meeting held each day, typically 15 minutes, to | |
| 104 | quickly emphasize alignment on the sprint goal and plan the next 24 hours. | |
| 105 | Each team member may share what they did the day before, what they'll do | |
| 106 | today, and any obstacles to their work. | |
| 107 | 4. *Sprint Review*: At the end of each sprint, the team will gather and discuss | |
| 108 | the progress, obstacles, and backlog from the previous sprint. | |
| 109 | 5. *Sprint Retrospective*: More specific than the sprint review, the | |
| 110 | retrospective is meant to discuss what worked and what did not work during | |
| 111 | the sprint. This may be processes, tools, people, or even things related to | |
| 112 | the Scrum ceremonies. | |
| 113 | ||
| 114 | One additional ceremony that may be applicable is organizing the backlog. This | |
| 115 | is typically the responsibility of the engagement leader and is meant to | |
| 116 | prioritize and clarify what needs to be done to complete items in the backlog. | |
| 117 | ||
| 118 | ** Artifacts | |
| 119 | While artifacts are generally not customizable in the audit world (i.e., each | |
| 120 | control test must include some kind of working paper with evidence supporting | |
| 121 | the test results), I wanted to include some quick notes on associating scrum | |
| 122 | artifact terms with an audit. | |
| 123 | ||
| 124 | 1. *Product Backlog*: This is the overall backlog of unfinished audit tasks from | |
| 125 | all prior sprints. | |
| 126 | 2. *Sprint Backlog*: This is the backlog of unfinished audit tasks from one | |
| 127 | individual sprint. | |
| 128 | 3. *Increment*: This is the output of each sprint - generally this is best | |
| 129 | thought of as any documentation prepared during the sprint, such as risk | |
| 130 | assessments, control working papers, deficiency analysis, etc. | |
| 131 | ||
| 132 | * Kanban | |
| 133 | Last but not least, Kanban is a methodology that relies on boards to categorize | |
| 134 | work into distinct, descriptive categories that allow an agile or scrum team to | |
| 135 | effectively plan the work of a sprint or project. | |
| 136 | ||
| 137 | See Atlassian's [[https://www.atlassian.com/agile/kanban][Kanban]] page for more information. | |
content/blog/2022-12-23-alpine-desktop.md → blog/alpine-desktop/index.org renamed +78 −89
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-12-23 | |
| 3 | title = "Alpine Linux as a Desktop OS" | |
| 4 | description = "Learn how to set up Alpine Linux with Sway to use as a desktop operating system." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Isn't Alpine Linux for Servers? | |
| 1 | #+title: Alpine Linux as a Desktop OS | |
| 2 | #+date: 2022-12-23 | |
| 3 | #+description: Learn how to set up Alpine Linux with Sway to use as a desktop operating system. | |
| 4 | #+filetags: :linux: | |
| 8 | 5 | |
| 6 | * Isn't Alpine Linux for Servers? | |
| 9 | 7 | This is a question I see a lot when people are presented with an example |
| 10 | 8 | of Alpine Linux running as a desktop OS. |
| 11 | 9 | |
| @@ -15,76 +13,73 @@ functioning at a productive level for desktop users. | ||
| 15 | 13 | This post is documentation of how I installed and modified Alpine Linux |
| 16 | 14 | to become my daily desktop OS. |
| 17 | 15 | |
| 18 | ## Installation | |
| 19 | ||
| 16 | * Installation | |
| 20 | 17 | Note that I cover the installation of Alpine Linux in my other post, so |
| 21 | I won't repeat it here: [Alpine Linux: My New Server | |
| 22 | OS](/blog/alpine-linux/). | |
| 18 | I won't repeat it here: [[../alpine-linux/][Alpine Linux: My New | |
| 19 | Server OS]]. | |
| 23 | 20 | |
| 24 | 21 | Basically, get a bootable USB or whatever you prefer with Alpine on it, |
| 25 | 22 | boot the ISO, and run the setup script. |
| 26 | 23 | |
| 27 | ```sh | |
| 24 | #+begin_src sh | |
| 28 | 25 | setup-alpine |
| 29 | ``` | |
| 26 | #+end_src | |
| 30 | 27 | |
| 31 | 28 | Once you have gone through all the options and installer finishes |
| 32 | 29 | without errors, reboot. |
| 33 | 30 | |
| 34 | ```sh | |
| 31 | #+begin_src sh | |
| 35 | 32 | reboot |
| 36 | ``` | |
| 37 | ||
| 38 | ## Initial Setup | |
| 33 | #+end_src | |
| 39 | 34 | |
| 35 | * Initial Setup | |
| 40 | 36 | Once Alpine is installed and the machine has rebooted, login is as root |
| 41 | initially or `su` to root once you log in as your user. From | |
| 42 | here, you should start by updating and upgrading the system in case the | |
| 43 | ISO was not fully up-to-date. | |
| 37 | initially or =su= to root once you log in as your user. From here, you | |
| 38 | should start by updating and upgrading the system in case the ISO was | |
| 39 | not fully up-to-date. | |
| 44 | 40 | |
| 45 | ```sh | |
| 41 | #+begin_src sh | |
| 46 | 42 | # Update and upgrade system |
| 47 | 43 | apk -U update && apk -U upgrade |
| 48 | 44 | |
| 49 | 45 | # Add an editor so we can enable the community repository |
| 50 | 46 | apk add nano |
| 51 | ``` | |
| 47 | #+end_src | |
| 52 | 48 | |
| 53 | You need to uncomment the `community` repository for your | |
| 54 | version of Alpine Linux. | |
| 49 | You need to uncomment the =community= repository for your version of | |
| 50 | Alpine Linux. | |
| 55 | 51 | |
| 56 | For v3.17, the `repositories` file should look like this: | |
| 52 | For v3.17, the =repositories= file should look like this: | |
| 57 | 53 | |
| 58 | ```sh | |
| 54 | #+begin_src sh | |
| 59 | 55 | nano /etc/apk/repositories |
| 60 | ``` | |
| 56 | #+end_src | |
| 61 | 57 | |
| 62 | ```conf | |
| 58 | #+begin_src conf | |
| 63 | 59 | #/media/sda/apks |
| 64 | 60 | http://mirrors.gigenet.com/alpinelinux/v3.17/main |
| 65 | 61 | http://mirrors.gigenet.com/alpinelinux/v3.17/community |
| 66 | 62 | #http://mirrors.gigenet.com/alpinelinux/edge/main |
| 67 | 63 | #http://mirrors.gigenet.com/alpinelinux/edge/community |
| 68 | 64 | #http://mirrors.gigenet.com/alpinelinux/edge/testing |
| 69 | ``` | |
| 65 | #+end_src | |
| 70 | 66 | |
| 71 | ```sh | |
| 67 | #+begin_src sh | |
| 72 | 68 | # Add the rest of your packages |
| 73 | 69 | apk add linux-firmware iwd doas git curl wget |
| 74 | 70 | |
| 75 | 71 | # Add yourself to the wheel group so you can use the doas command |
| 76 | 72 | adduser $USER wheel |
| 77 | ``` | |
| 78 | ||
| 79 | ## Window Manager (Desktop) | |
| 73 | #+end_src | |
| 80 | 74 | |
| 81 | The [Sway installation guide](https://wiki.alpinelinux.org/wiki/Sway) | |
| 75 | * Window Manager (Desktop) | |
| 76 | The [[https://wiki.alpinelinux.org/wiki/Sway][Sway installation guide]] | |
| 82 | 77 | has everything you need to get Sway working on Alpine. |
| 83 | 78 | |
| 84 | 79 | However, I'll include a brief list of the commands I ran and their |
| 85 | 80 | purpose for posterity here. |
| 86 | 81 | |
| 87 | ```sh | |
| 82 | #+begin_src sh | |
| 88 | 83 | # Add eudev and set it up |
| 89 | 84 | apk add eudev |
| 90 | 85 | setup-devd udev |
| @@ -121,43 +116,41 @@ apk add \ # Install optional dependencies: | ||
| 121 | 116 | swaylock swaylockd \ # lockscreen tool |
| 122 | 117 | swaybg \ # wallpaper daemon |
| 123 | 118 | swayidle # idle management (DPMS) daemon |
| 124 | ``` | |
| 119 | #+end_src | |
| 125 | 120 | |
| 126 | 121 | Once you have the packages installed and set-up, you need to export the |
| 127 | `XDG_RUNTIME_DIR` upon login. To do this, edit your | |
| 128 | `.profile` file. | |
| 122 | =XDG_RUNTIME_DIR= upon login. To do this, edit your =.profile= file. | |
| 129 | 123 | |
| 130 | If you use another shell, such as `zsh`, you need to edit | |
| 131 | that shell's profile (e.g., `~/.zprofile`)! | |
| 124 | If you use another shell, such as =zsh=, you need to edit that shell's | |
| 125 | profile (e.g., =~/.zprofile=)! | |
| 132 | 126 | |
| 133 | ```sh | |
| 127 | #+begin_src sh | |
| 134 | 128 | nano ~/.profile |
| 135 | ``` | |
| 129 | #+end_src | |
| 136 | 130 | |
| 137 | 131 | Within the file, paste this: |
| 138 | 132 | |
| 139 | ```sh | |
| 133 | #+begin_src sh | |
| 140 | 134 | if test -z "${XDG_RUNTIME_DIR}"; then |
| 141 | 135 | export XDG_RUNTIME_DIR=/tmp/$(id -u)-runtime-dir |
| 142 | if ! test -d "${XDG_RUNTIME_DIR}"; then | |
| 136 | if ! test -d "${XDG_RUNTIME_DIR}"; then | |
| 143 | 137 | mkdir "${XDG_RUNTIME_DIR}" |
| 144 | 138 | chmod 0700 "${XDG_RUNTIME_DIR}" |
| 145 | 139 | fi |
| 146 | 140 | fi |
| 147 | ``` | |
| 141 | #+end_src | |
| 148 | 142 | |
| 149 | 143 | Once that's complete, you can launch Sway manually. |
| 150 | 144 | |
| 151 | ```sh | |
| 145 | #+begin_src sh | |
| 152 | 146 | dbus-run-session -- sway |
| 153 | ``` | |
| 154 | ||
| 155 | ## Personal Touches | |
| 147 | #+end_src | |
| 156 | 148 | |
| 149 | ** Personal Touches | |
| 157 | 150 | I also added the following packages, per my personal preferences and |
| 158 | 151 | situation. |
| 159 | 152 | |
| 160 | ```sh | |
| 153 | #+begin_src sh | |
| 161 | 154 | doas apk add brightnessctl \ # Brightness controller |
| 162 | 155 | zsh \ # Shell |
| 163 | 156 | firefox \ # Browser |
| @@ -167,93 +160,89 @@ doas apk add brightnessctl \ # Brightness controller | ||
| 167 | 160 | neomutt \ # CLI email client |
| 168 | 161 | thunderbird \ # GUI email client |
| 169 | 162 | gnupg # GPG key manager |
| 170 | ``` | |
| 163 | #+end_src | |
| 171 | 164 | |
| 172 | 165 | From here, I use my Syncthing storage to pull all the configuration |
| 173 | files I stored from prior desktops, such as [my | |
| 174 | dotfiles](https://git.sr.ht/~cmc/dotfiles). | |
| 175 | ||
| 176 | ## Resolving Issues | |
| 166 | files I stored from prior desktops, such as | |
| 167 | [[https://git.sr.ht/~cmc/dotfiles][my dotfiles]]. | |
| 177 | 168 | |
| 178 | ### WiFi Issues | |
| 169 | * Resolving Issues | |
| 170 | ** WiFi Issues | |
| 171 | I initially tried to set up my Wi-Fi the standard way with =iwd=, but it | |
| 172 | didn't work. | |
| 179 | 173 | |
| 180 | I initially tried to set up my Wi-Fi the standard way with | |
| 181 | `iwd`, but it didn't work. | |
| 174 | Here is what I initially tried (I did all of this as =root=): | |
| 182 | 175 | |
| 183 | Here is what I initially tried (I did all of this as `root`): | |
| 184 | ||
| 185 | ```sh | |
| 176 | #+begin_src sh | |
| 186 | 177 | apk add iwd |
| 187 | 178 | rc-service iwd start |
| 188 | 179 | iwctl station wlan0 connect <SSID> # This will prompt for the password |
| 189 | 180 | rc-update add iwd boot && rc-update add dbus boot |
| 190 | ``` | |
| 181 | #+end_src | |
| 191 | 182 | |
| 192 | 183 | Then, I added the Wi-Fi entry to the bottom of the networking interface |
| 193 | 184 | file: |
| 194 | 185 | |
| 195 | ```sh | |
| 186 | #+begin_src sh | |
| 196 | 187 | nano /etc/network/interfaces |
| 197 | ``` | |
| 188 | #+end_src | |
| 198 | 189 | |
| 199 | ```conf | |
| 190 | #+begin_src conf | |
| 200 | 191 | auto wlan0 |
| 201 | 192 | iface wlan0 inet dhcp |
| 202 | ``` | |
| 193 | #+end_src | |
| 203 | 194 | |
| 204 | 195 | Finally, restart the networking service: |
| 205 | 196 | |
| 206 | ```sh | |
| 197 | #+begin_src sh | |
| 207 | 198 | rc-service networking restart |
| 208 | ``` | |
| 199 | #+end_src | |
| 209 | 200 | |
| 210 | 201 | My Wi-Fi interface would receive an IP address from the router, but it |
| 211 | 202 | could not ping anything in the network. To solve the Wi-Fi issues, I |
| 212 | originally upgraded to Alpine's `edge` repositories, which | |
| 213 | was unnecessary. | |
| 203 | originally upgraded to Alpine's =edge= repositories, which was | |
| 204 | unnecessary. | |
| 214 | 205 | |
| 215 | Really, the solution was to enable the | |
| 216 | `NameResolvingService=resolvconf` in | |
| 217 | `/etc/iwd/main.conf`. | |
| 206 | Really, the solution was to enable the =NameResolvingService=resolvconf= | |
| 207 | in =/etc/iwd/main.conf=. | |
| 218 | 208 | |
| 219 | ```sh | |
| 209 | #+begin_src sh | |
| 220 | 210 | doas nano /etc/iwd/main.conf |
| 221 | ``` | |
| 211 | #+end_src | |
| 222 | 212 | |
| 223 | ```conf | |
| 213 | #+begin_src conf | |
| 224 | 214 | [Network] |
| 225 | 215 | |
| 226 | 216 | NameResolvingService=resolvconf |
| 227 | ``` | |
| 217 | #+end_src | |
| 228 | 218 | |
| 229 | 219 | Once I finished this process, my Wi-Fi is working flawlessly. |
| 230 | 220 | |
| 231 | ### Sound Issues | |
| 232 | ||
| 221 | ** Sound Issues | |
| 233 | 222 | Same as with the Wi-Fi, I had no sound and could not control the |
| 234 | 223 | mute/unmute or volume buttons on my laptop. |
| 235 | 224 | |
| 236 | 225 | To resolve this, I installed |
| 237 | [pipewire](https://wiki.alpinelinux.org/wiki/PipeWire). | |
| 226 | [[https://wiki.alpinelinux.org/wiki/PipeWire][pipewire]]. | |
| 238 | 227 | |
| 239 | ```sh | |
| 228 | #+begin_src sh | |
| 240 | 229 | # Add your user to the following groups |
| 241 | 230 | addgroup $USER audio |
| 242 | 231 | addgroup $USER video |
| 243 | 232 | |
| 244 | 233 | # Install pipewire and other useful packages |
| 245 | 234 | apk add pipewire wireplumber pipewire-pulse pipewire-jack pipewire-alsa |
| 246 | ``` | |
| 235 | #+end_src | |
| 247 | 236 | |
| 248 | Finally, I needed to add `/usr/libexec/pipewire-launcher` to | |
| 249 | my `.config/sway/config` file so that Pipewire would run | |
| 250 | every time I launched sway. | |
| 237 | Finally, I needed to add =/usr/libexec/pipewire-launcher= to my | |
| 238 | =.config/sway/config= file so that Pipewire would run every time I | |
| 239 | launched sway. | |
| 251 | 240 | |
| 252 | ```sh | |
| 241 | #+begin_src sh | |
| 253 | 242 | nano ~/.config/sway/config |
| 254 | ``` | |
| 243 | #+end_src | |
| 255 | 244 | |
| 256 | ```conf | |
| 245 | #+begin_src conf | |
| 257 | 246 | # Run pipewire audio server |
| 258 | 247 | exec /usr/libexec/pipewire-launcher |
| 259 | 248 | |
| @@ -262,7 +251,7 @@ bindsym XF86AudioRaiseVolume exec --no-startup-id pactl set-sink-volume @DEFAULT | ||
| 262 | 251 | bindsym XF86AudioLowerVolume exec --no-startup-id pactl set-sink-volume @DEFAULT_SINK@ -5% |
| 263 | 252 | bindsym XF86AudioMute exec --no-startup-id pactl set-sink-mute @DEFAULT_SINK@ toggle |
| 264 | 253 | bindsym XF86AudioMicMute exec --no-startup-id pactl set-source-mute @DEFAULT_SOURCE@ toggle |
| 265 | ``` | |
| 254 | #+end_src | |
| 266 | 255 | |
| 267 | 256 | Note that I do not use bluetooth or screen sharing, so I won't cover |
| 268 | 257 | those options in this post. |
blog/alpine-linux/index.org added +269
| @@ -0,0 +1,269 @@ | ||
| 1 | #+title: Alpine Linux: My New Server OS | |
| 2 | #+date: 2022-10-22 | |
| 3 | #+description: A retrospective on installing and configuring Alpine Linux as my new server operating system. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * Alpine Linux | |
| 7 | [[https://alpinelinux.org][Alpine Linux]] is a very small distro, built | |
| 8 | on musl libc and busybox. It uses ash as the default shell, OpenRC as | |
| 9 | the init system, and apk as the package manager. According to their | |
| 10 | website, an Alpine container "requires no more than 8 MB and a minimal | |
| 11 | installation to disk requires around 130 MB of storage." An actual bare | |
| 12 | metal machine is recommended to have 100 MB of RAM and 0-700 MB of | |
| 13 | storage space. | |
| 14 | ||
| 15 | Historically, I've used Ubuntu's minimal installation image as my server | |
| 16 | OS for the last five years. Ubuntu worked well and helped as my original | |
| 17 | server contained an nVidia GPU and no onboard graphics, so quite a few | |
| 18 | distros won't boot or install without a lot of tinkering. | |
| 19 | ||
| 20 | Alpine has given me a huge increase in performance across my Docker apps | |
| 21 | and Nginx websites. CPU load for the new server I'm using to test Alpine | |
| 22 | hovers around 0-5% on average with an Intel(R) Core(TM) i3-6100 CPU @ | |
| 23 | 3.70GHz. | |
| 24 | ||
| 25 | The only services I haven't moved over to Alpine are Plex Media Server | |
| 26 | and Syncthing, which may increase CPU load quite a bit depending on how | |
| 27 | many streams are running. | |
| 28 | ||
| 29 | ** Installation | |
| 30 | In terms of installation, Alpine has an incredibly useful | |
| 31 | [[https://wiki.alpinelinux.org/wiki/Installation][wiki]] that will guide | |
| 32 | a user throughout the installation and post-installation processes, as | |
| 33 | well as various other articles and guides. | |
| 34 | ||
| 35 | To install Alpine, find an appropriate | |
| 36 | [[https://alpinelinux.org/downloads/][image to download]] and flash it | |
| 37 | to a USB using software such as Rufus or Etcher. I opted to use the | |
| 38 | Standard image for my x86_{64} architecture. | |
| 39 | ||
| 40 | Once the USB is ready, plug it into the machine and reboot. Note that | |
| 41 | you may have to use a key such as =Esc= or =F1-12= to access the boot | |
| 42 | menu. The Alpine Linux terminal will load quickly and for a login. | |
| 43 | ||
| 44 | To log in to the installation image, use the =root= account; there is no | |
| 45 | password. Once logged-in, execute the setup command: | |
| 46 | ||
| 47 | #+begin_src sh | |
| 48 | setup-alpine | |
| 49 | #+end_src | |
| 50 | ||
| 51 | The setup script will ask a series of questions to configure the system. | |
| 52 | Be sure to answer carefully or else you may have to re-configure the | |
| 53 | system after boot. | |
| 54 | ||
| 55 | - Keyboard Layout (Local keyboard language and usage mode, e.g., us and | |
| 56 | variant of us-nodeadkeys.) | |
| 57 | - Hostname (The name for the computer.) | |
| 58 | - Network (For example, automatic IP address discovery with the "DHCP" | |
| 59 | protocol.) | |
| 60 | - DNS Servers (Domain Name Servers to query. For privacy reasons, it is | |
| 61 | NOT recommended to route every local request to servers like Google's | |
| 62 | 8.8.8.8 .) | |
| 63 | - Timezone | |
| 64 | - Proxy (Proxy server to use for accessing the web. Use "none" for | |
| 65 | direct connections to the internet.) | |
| 66 | - Mirror (From where to download packages. Choose the organization you | |
| 67 | trust giving your usage patterns to.) | |
| 68 | - SSH (Secure SHell remote access server. "Openssh" is part of the | |
| 69 | default install image. Use "none" to disable remote login, e.g. on | |
| 70 | laptops.) | |
| 71 | - NTP (Network Time Protocol client used for keeping the system clock in | |
| 72 | sync with a time-server. Package "chrony" is part of the default | |
| 73 | install image.) | |
| 74 | - Disk Mode (Select between diskless (disk="none"), "data" or "sys", as | |
| 75 | described above.) | |
| 76 | ||
| 77 | Once the setup script is finished, be sure to reboot the machine and | |
| 78 | remove the USB device. | |
| 79 | ||
| 80 | #+begin_src sh | |
| 81 | reboot | |
| 82 | #+end_src | |
| 83 | ||
| 84 | ** Post-Installation | |
| 85 | There are many things you can do once your Alpine Linux system is up and | |
| 86 | running, and it largely depends on what you'll use the machine for. I'm | |
| 87 | going to walk through my personal post-installation setup for my web | |
| 88 | server. | |
| 89 | ||
| 90 | 1. Upgrade the System | |
| 91 | ||
| 92 | First, login as =root= in order to update and upgrade the system: | |
| 93 | ||
| 94 | #+begin_src sh | |
| 95 | apk -U upgrade | |
| 96 | #+end_src | |
| 97 | ||
| 98 | 2. Adding a User | |
| 99 | ||
| 100 | I needed to add a user so that I don't need to log in as root. Note | |
| 101 | that if you're used to using the =sudo= command, you will now need to | |
| 102 | use the =doas= command on Alpine Linux. | |
| 103 | ||
| 104 | #+begin_src sh | |
| 105 | apk add doas | |
| 106 | adduser <username> | |
| 107 | adduser <username> wheel | |
| 108 | #+end_src | |
| 109 | ||
| 110 | You can now log out and log back in using the newly-created user: | |
| 111 | ||
| 112 | #+begin_src sh | |
| 113 | exit | |
| 114 | #+end_src | |
| 115 | ||
| 116 | 3. Enable Community Packages | |
| 117 | ||
| 118 | In order to install more common packages that aren't found in the | |
| 119 | =main= repository, you will need to enable the =community= | |
| 120 | repository: | |
| 121 | ||
| 122 | #+begin_src sh | |
| 123 | doas nano /etc/apk/repositories | |
| 124 | #+end_src | |
| 125 | ||
| 126 | Uncomment the community line for whichever version of Alpine you're | |
| 127 | running: | |
| 128 | ||
| 129 | #+begin_src sh | |
| 130 | /media/usb/apks | |
| 131 | http://dl-cdn.alpinelinux.org/alpine/v3.16/main | |
| 132 | http://dl-cdn.alpinelinux.org/alpine/v3.16/community | |
| 133 | #http://dl-cdn.alpinelinux.org/alpine/edge/main | |
| 134 | #http://dl-cdn.alpinelinux.org/alpine/edge/community | |
| 135 | #http://dl-cdn.alpinelinux.org/alpine/edge/testing | |
| 136 | #+end_src | |
| 137 | ||
| 138 | 4. Install Required Packages | |
| 139 | ||
| 140 | Now that the community packages are available, you can install any | |
| 141 | packages you need. In my case, I installed the web server packages I | |
| 142 | need for my services: | |
| 143 | ||
| 144 | #+begin_src sh | |
| 145 | doas apk add nano nginx docker docker-compose ufw | |
| 146 | #+end_src | |
| 147 | ||
| 148 | 5. SSH | |
| 149 | ||
| 150 | If you didn't install OpenSSH as part of the installation, you can do | |
| 151 | so now: | |
| 152 | ||
| 153 | #+begin_src sh | |
| 154 | doas apk add openssh | |
| 155 | #+end_src | |
| 156 | ||
| 157 | Next, either create a new key or copy your SSH key to the server from | |
| 158 | your current machines: | |
| 159 | ||
| 160 | #+begin_src sh | |
| 161 | # Create a new key | |
| 162 | ssh-keygen | |
| 163 | #+end_src | |
| 164 | ||
| 165 | If you need to copy an existing SSH key from a current machine: | |
| 166 | ||
| 167 | #+begin_src sh | |
| 168 | # Copy key from existing machines | |
| 169 | ssh-copy-id <username>@<ip_address> | |
| 170 | #+end_src | |
| 171 | ||
| 172 | 6. Firewall | |
| 173 | ||
| 174 | Lastly, I installed =ufw= above as my firewall. To set up, default to | |
| 175 | deny incoming and allow outgoing connections. Then selectively allow | |
| 176 | other ports or apps as needed. | |
| 177 | ||
| 178 | #+begin_src sh | |
| 179 | doas ufw default deny incoming | |
| 180 | doas ufw default allow outgoing | |
| 181 | doas ufw allow SSH | |
| 182 | doas ufw allow "WWW Full" | |
| 183 | doas ufw allow 9418 # Git server port | |
| 184 | #+end_src | |
| 185 | ||
| 186 | 7. Change Hostname | |
| 187 | ||
| 188 | If you don't like the hostname set during installation, you just need | |
| 189 | to edit two files. First, edit the simple hostname file: | |
| 190 | ||
| 191 | #+begin_src sh | |
| 192 | doas nano /etc/hostname | |
| 193 | #+end_src | |
| 194 | ||
| 195 | #+begin_src sh | |
| 196 | <hostname> | |
| 197 | #+end_src | |
| 198 | ||
| 199 | Next, edit the =hosts= file: | |
| 200 | ||
| 201 | #+begin_src sh | |
| 202 | doas nano /etc/hosts | |
| 203 | #+end_src | |
| 204 | ||
| 205 | #+begin_src sh | |
| 206 | 127.0.0.1 <hostname>.local <hostname> localhost.local localhost | |
| 207 | ::1 <hostname> <hostname>.local | |
| 208 | #+end_src | |
| 209 | ||
| 210 | * Nginx Web Server | |
| 211 | To set up my web server, I simply created the =www= user and created the | |
| 212 | necessary files. | |
| 213 | ||
| 214 | #+begin_src sh | |
| 215 | doas adduser -D -g 'www' www | |
| 216 | mkdir /www | |
| 217 | doas mkdir /www | |
| 218 | doas chown -R www:www /var/lib/nginx/ | |
| 219 | doas chown -R www:www /www | |
| 220 | #+end_src | |
| 221 | ||
| 222 | If you're running a simple webroot, you can alter the main =nginx.conf= | |
| 223 | file. Otherwise, you can drop configuration files in the following | |
| 224 | directory. You don't need to enable or symlink the configuration file | |
| 225 | like you do in other systems. | |
| 226 | ||
| 227 | #+begin_src sh | |
| 228 | doas nano /etc/nginx/http.d/example_website.conf | |
| 229 | #+end_src | |
| 230 | ||
| 231 | Once the configuration is set and pointed at the =/www= directory to | |
| 232 | serve files, enable the Nginx service: | |
| 233 | ||
| 234 | #+begin_src sh | |
| 235 | # Note that 'default' must be included or Nginx will not start on boot | |
| 236 | doas rc-update add nginx default | |
| 237 | #+end_src | |
| 238 | ||
| 239 | * Docker Containers | |
| 240 | Docker works exactly the same as other systems. Either execute a | |
| 241 | =docker run= command or create a =docker-compose.yml= file and do | |
| 242 | =docker-compose up -d=. | |
| 243 | ||
| 244 | * Git Server | |
| 245 | I went in-depth on how to self-host a git server in another post: | |
| 246 | [[../git-server/][Self-Hosting a Personal Git Server]]. | |
| 247 | ||
| 248 | However, there are a few differences with Alpine. First note that in | |
| 249 | order to change the =git= user's shell, you must do a few things a | |
| 250 | little different: | |
| 251 | ||
| 252 | #+begin_src sh | |
| 253 | doas apk add libuser | |
| 254 | doas touch /etc/login.defs | |
| 255 | doas mkdir /etc/default | |
| 256 | doas touch /etc/default/useradd | |
| 257 | doas lchsh git | |
| 258 | #+end_src | |
| 259 | ||
| 260 | * Thoughts on Alpine | |
| 261 | So far, I love Alpine Linux. I have no complaints about anything at this | |
| 262 | point, but I'm not completely finished with the migration yet. Once I'm | |
| 263 | able to upgrade my hardware to a rack-mounted server, I will migrate | |
| 264 | Plex and Syncthing over to Alpine as well - possibly putting Plex into a | |
| 265 | container or VM. | |
| 266 | ||
| 267 | The performance is stellar, the =apk= package manager is seamless, and | |
| 268 | system administration tasks are effortless. My only regret is that I | |
| 269 | didn't install Alpine sooner. | |
content/blog/2023-10-15-alpine-ssh-hardening.md → blog/alpine-ssh-hardening/index.org renamed +37 −40
| @@ -1,74 +1,71 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-10-15 | |
| 3 | title = "SSH Hardening for Alpine Linux" | |
| 4 | description = "A quick guide to harden SSH configuration on Alpine." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Overview | |
| 1 | #+title: SSH Hardening for Alpine Linux | |
| 2 | #+date: 2023-10-15 | |
| 3 | #+description: A quick guide to harden SSH configuration on Alpine. | |
| 4 | #+filetags: :linux: | |
| 8 | 5 | |
| 6 | * Overview | |
| 9 | 7 | This guide follows the standard |
| 10 | [ssh-audit](https://www.ssh-audit.com/hardening_guides.html) hardening | |
| 8 | [[https://www.ssh-audit.com/hardening_guides.html][ssh-audit]] hardening | |
| 11 | 9 | guide, tweaked for Alpine Linux. |
| 12 | 10 | |
| 13 | ## Hardening Guide | |
| 14 | ||
| 15 | These steps must be performed as root. You can try to use | |
| 16 | `doas` or `sudo`, but there may be issues. | |
| 11 | * Hardening Guide | |
| 12 | These steps must be performed as root. You can try to use =doas= or | |
| 13 | =sudo=, but there may be issues. | |
| 17 | 14 | |
| 18 | 1. Re-generate the RSA and ED25519 keys | |
| 15 | 1. Re-generate the RSA and ED25519 keys | |
| 19 | 16 | |
| 20 | ```sh | |
| 17 | #+begin_src sh | |
| 21 | 18 | rm /etc/ssh/ssh_host_* |
| 22 | 19 | ssh-keygen -t rsa -b 4096 -f /etc/ssh/ssh_host_rsa_key -N "" |
| 23 | 20 | ssh-keygen -t ed25519 -f /etc/ssh/ssh_host_ed25519_key -N "" |
| 24 | ``` | |
| 21 | #+end_src | |
| 25 | 22 | |
| 26 | 2. Remove small Diffie-Hellman moduli | |
| 23 | 2. [@2] Remove small Diffie-Hellman moduli | |
| 27 | 24 | |
| 28 | ```sh | |
| 25 | #+begin_src sh | |
| 29 | 26 | awk '$5 >= 3071' /etc/ssh/moduli > /etc/ssh/moduli.safe |
| 30 | 27 | mv /etc/ssh/moduli.safe /etc/ssh/moduli |
| 31 | ``` | |
| 28 | #+end_src | |
| 32 | 29 | |
| 33 | 3. Enable the RSA and ED25519 HostKey directives in the | |
| 34 | /etc/ssh/sshd~config~ file | |
| 30 | 3. [@3] Enable the RSA and ED25519 HostKey directives in the | |
| 31 | /etc/ssh/sshd_{config} file | |
| 35 | 32 | |
| 36 | ```sh | |
| 33 | #+begin_src sh | |
| 37 | 34 | sed -i 's/^\#HostKey \/etc\/ssh\/ssh_host_\(rsa\|ed25519\)_key$/HostKey \/etc\/ssh\/ssh_host_\1_key/g' /etc/ssh/sshd_config |
| 38 | ``` | |
| 35 | #+end_src | |
| 39 | 36 | |
| 40 | 4. Restrict supported key exchange, cipher, and MAC algorithms | |
| 37 | 4. [@4] Restrict supported key exchange, cipher, and MAC algorithms | |
| 41 | 38 | |
| 42 | ```sh | |
| 39 | #+begin_src sh | |
| 43 | 40 | echo -e "\n# Restrict key exchange, cipher, and MAC algorithms, as per sshaudit.com\n# hardening guide.\nKexAlgorithms sntrup761x25519-sha512@openssh.com,curve25519-sha256,curve25519-sha256@libssh.org,diffie-hellman-group16-sha512,diffie-hellman-group18-sha512,diffie-hellman-group-exchange-sha256\nCiphers chacha20-poly1305@openssh.com,aes256-gcm@openssh.com,aes128-gcm@openssh.com,aes256-ctr,aes192-ctr,aes128-ctr\nMACs hmac-sha2-256-etm@openssh.com,hmac-sha2-512-etm@openssh.com,umac-128-etm@openssh.com\nHostKeyAlgorithms ssh-ed25519,ssh-ed25519-cert-v01@openssh.com,sk-ssh-ed25519@openssh.com,sk-ssh-ed25519-cert-v01@openssh.com,rsa-sha2-512,rsa-sha2-512-cert-v01@openssh.com,rsa-sha2-256,rsa-sha2-256-cert-v01@openssh.com" > /etc/ssh/sshd_config.d/ssh-audit_hardening.conf |
| 44 | ``` | |
| 41 | #+end_src | |
| 45 | 42 | |
| 46 | 5. Include the /etc/ssh/sshd~config~.d directory | |
| 43 | 5. [@5] Include the /etc/ssh/sshd_{config}.d directory | |
| 47 | 44 | |
| 48 | ```sh | |
| 45 | #+begin_src sh | |
| 49 | 46 | echo -e "Include /etc/ssh/sshd_config.d/*.conf" > /etc/ssh/sshd_config |
| 50 | ``` | |
| 47 | #+end_src | |
| 51 | 48 | |
| 52 | 6. Restart OpenSSH server | |
| 49 | 6. [@6] Restart OpenSSH server | |
| 53 | 50 | |
| 54 | ```sh | |
| 51 | #+begin_src sh | |
| 55 | 52 | rc-service sshd restart |
| 56 | ``` | |
| 57 | ||
| 58 | ## Testing SSH | |
| 53 | #+end_src | |
| 59 | 54 | |
| 60 | You can test the results with the `ssh-audit` python script. | |
| 55 | * Testing SSH | |
| 56 | You can test the results with the =ssh-audit= python script. | |
| 61 | 57 | |
| 62 | ```sh | |
| 58 | #+begin_src sh | |
| 63 | 59 | pip3 install ssh-audit |
| 64 | 60 | ssh-audit localhost |
| 65 | ``` | |
| 61 | #+end_src | |
| 66 | 62 | |
| 67 | 63 | If everything succeeded, the results will show as all green. If anything |
| 68 | 64 | is yellow, orange, or red, you may need to tweak additional settings. |
| 69 | 65 | |
| 70 | ```txt | |
| 71 | #+caption: ssh audit | |
| 72 | ``` | |
| 66 | #+begin_src txt | |
| 67 | ,#+caption: ssh audit | |
| 68 | #+end_src | |
| 73 | 69 | |
| 74 | 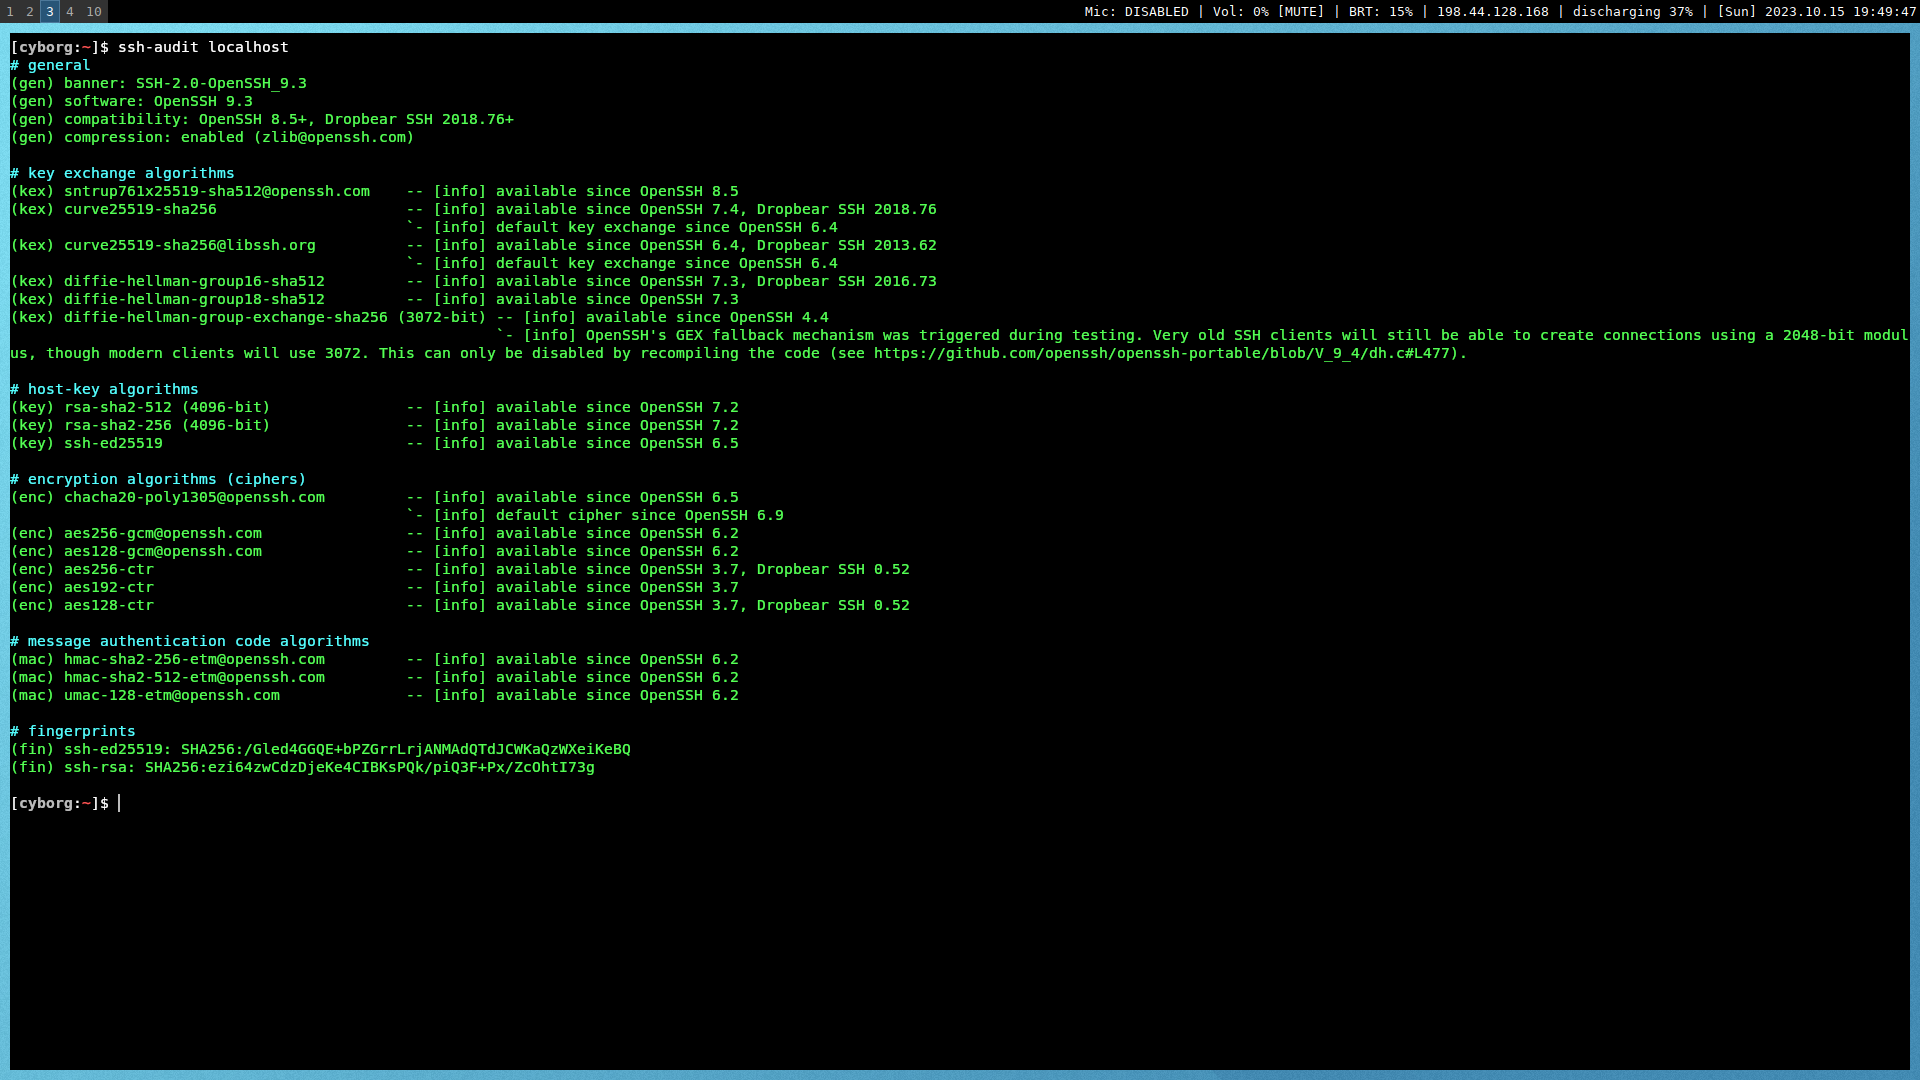 | |
| 70 | #+caption: ssh-audit | |
| 71 | [[https://img.cleberg.net/blog/20231015-ssh-hardening/ssh-audit.png]] | |
blog/apache-redirect/index.org added +43
| @@ -0,0 +1,43 @@ | ||
| 1 | #+title: Apache Redirect HTML Files to a Directory | |
| 2 | #+date: 2021-10-09 | |
| 3 | #+description: A guide on redirecting HTML files to directory in Apache. | |
| 4 | #+filetags: :apache: | |
| 5 | ||
| 6 | * The Problem | |
| 7 | After recently switching static site generators (SSG), my blog URLs | |
| 8 | changed with no option to preserve the classic =.html= extension at the | |
| 9 | end of my blog post URLs. | |
| 10 | ||
| 11 | I really disliked using my old SSG ([[https://jekyllrb.com][Jekyll]]) | |
| 12 | and prefer my new tool ([[https://www.getzola.org][Zola]]) much more, so | |
| 13 | I was determined to figure out a way to get the proper redirect set up | |
| 14 | so that people who find my posts online aren't constantly met by 404 | |
| 15 | errors. | |
| 16 | ||
| 17 | * The Solution | |
| 18 | To solve this problem, I really needed to solve two pieces: | |
| 19 | ||
| 20 | 1. Redirect all blog post URL requests from =/blog/some-post.html= to | |
| 21 | =/blog/some-post/=. | |
| 22 | 2. Ensure that no other =.html= files are redirected, such as | |
| 23 | =index.html=. | |
| 24 | ||
| 25 | After /a lot/ of tweaking and testing, I believe I have finally found | |
| 26 | the solution. The solution is shown below. | |
| 27 | ||
| 28 | #+begin_src conf | |
| 29 | RewriteEngine On | |
| 30 | RewriteCond %{REQUEST_URI} !\index.html$ [NC] | |
| 31 | RewriteRule ^(.*).html$ https://example.com/$1 [R=301,L] | |
| 32 | #+end_src | |
| 33 | ||
| 34 | This piece of code in the Apache =.conf= or =.htaccess= file will do the | |
| 35 | following: | |
| 36 | ||
| 37 | 1. Turn on the RewriteEngine so that we can modify URLs. | |
| 38 | 2. Ignore any =index.html= files from the rule we are about to specify. | |
| 39 | 3. Find any =.html= files within the website directory and redirect it | |
| 40 | to exclude the file extension. | |
| 41 | 4. The final piece is adding the trailing slash (=/=) at the end of the | |
| 42 | URL - you'll notice that I don't have an Apache rule for that since | |
| 43 | Apache handles that automatically. | |
content/blog/2019-09-09-audit-analytics.md → blog/audit-analytics/index.org renamed +119 −121
| @@ -1,17 +1,15 @@ | ||
| 1 | +++ | |
| 2 | date = 2019-09-09 | |
| 3 | title = "Data Analysis in Auditing" | |
| 4 | description = "Learn how to use data analysis in the world of auditing." | |
| 5 | +++ | |
| 6 | ||
| 7 | # What Are Data Analytics? | |
| 8 | ||
| 9 | A quick aside before I dive into this post: `data analytics` is a | |
| 10 | vague term that has become popular in recent years. Think of a `data | |
| 11 | analytic` as the output of any data analysis you perform. For example, | |
| 12 | a pivot table or a pie chart could be a data analytic. | |
| 13 | ||
| 14 | [Data analysis](https://en.wikipedia.org/wiki/Data_analysis) is a | |
| 1 | #+title: Data Analysis in Auditing | |
| 2 | #+date: 2019-09-09 | |
| 3 | #+description: Learn how to use data analysis in the world of auditing. | |
| 4 | #+filetags: :audit: | |
| 5 | ||
| 6 | * What Are Data Analytics? | |
| 7 | A quick aside before I dive into this post: =data analytics= is a vague | |
| 8 | term that has become popular in recent years. Think of a =data analytic= | |
| 9 | as the output of any data analysis you perform. For example, a pivot | |
| 10 | table or a pie chart could be a data analytic. | |
| 11 | ||
| 12 | [[https://en.wikipedia.org/wiki/Data_analysis][Data analysis]] is a | |
| 15 | 13 | process that utilizes statistics and other mathematical methods to |
| 16 | 14 | discover useful information within datasets. This involves examining, |
| 17 | 15 | cleaning, transforming, and modeling data so that you can use the data |
| @@ -23,18 +21,16 @@ make is assuming that everything involved with this process is "data | ||
| 23 | 21 | analytics". In fact, data analytics are only a small part of the |
| 24 | 22 | process. |
| 25 | 23 | |
| 26 | See **Figure 1** for a more accurate representation of where data | |
| 27 | analysis sits within the full process. This means that data analysis | |
| 28 | does not include querying or extracting data, selecting samples, or | |
| 29 | performing audit tests. These steps can be necessary for an audit (and | |
| 30 | may even be performed by the same associates), but they are not data | |
| 31 | analytics. | |
| 32 | ||
| 33 | 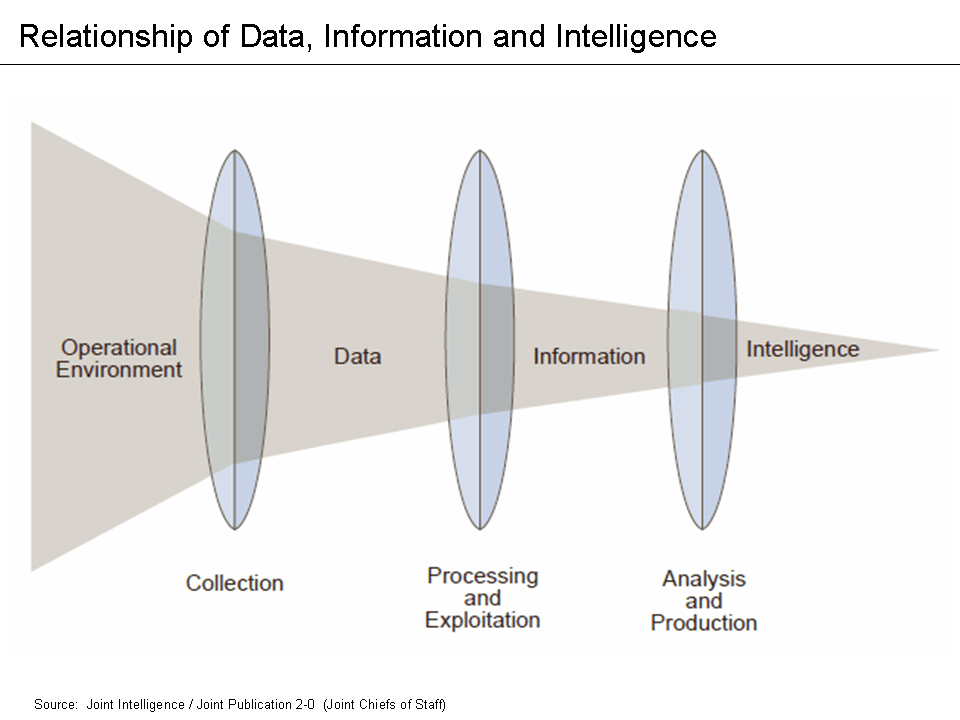 | |
| 24 | See *Figure 1** for a more accurate representation of where data analysis | |
| 25 | sits within the full process. This means that data analysis does not | |
| 26 | include querying or extracting data, selecting samples, or performing | |
| 27 | audit tests. These steps can be necessary for an audit (and may even be | |
| 28 | performed by the same associates), but they are not data analytics. | |
| 35 | 29 | |
| 36 | # Current Use of Analytics in Auditing | |
| 30 | #+caption: The Intelligence Cycle | |
| 31 | [[https://img.cleberg.net/blog/20190909-data-analysis-in-auditing/intelligence_cycle-min.png]] | |
| 37 | 32 | |
| 33 | * Current Use of Analytics in Auditing | |
| 38 | 34 | While data analysis has been an integral part of most businesses and |
| 39 | 35 | departments for the better part of the last century, only recently have |
| 40 | 36 | internal audit functions been adopting this practice. The internal audit |
| @@ -42,21 +38,23 @@ function works exclusively to provide assurance and consulting services | ||
| 42 | 38 | to the business areas within the firm (except for internal auditing |
| 43 | 39 | firms who are hired by different companies to perform their roles). |
| 44 | 40 | |
| 45 | > Internal Auditing helps an organization accomplish its objectives by | |
| 46 | > bringing a systematic, disciplined approach to evaluate and improve | |
| 47 | > the effectiveness of risk management, control and governance | |
| 48 | > processes. | |
| 49 | > | |
| 50 | > - The IIA's Definition of Internal Audit | |
| 41 | #+begin_quote | |
| 42 | Internal Auditing helps an organization accomplish its objectives by | |
| 43 | bringing a systematic, disciplined approach to evaluate and improve the | |
| 44 | effectiveness of risk management, control and governance processes. | |
| 45 | ||
| 46 | - The IIA's Definition of Internal Audit | |
| 47 | ||
| 48 | #+end_quote | |
| 51 | 49 | |
| 52 | 50 | Part of the blame for the slow adoption of data analysis can be |
| 53 | 51 | attributed to the fact that internal auditing is strongly based on |
| 54 | 52 | tradition and following the precedents set by previous auditors. |
| 55 | 53 | However, there can be no progress without auditors who are willing to |
| 56 | break the mold and test new audit techniques. In fact, as of 2018, [only | |
| 57 | 63% of internal audit departments currently utilize data | |
| 58 | analytics](https://www.cpapracticeadvisor.com/accounting-audit/news/12404086/internal-audit-groups-are-lagging-in-data-analytics) | |
| 59 | in North America. This number should be as close as possible to 100%. I | |
| 54 | break the mold and test new audit techniques. In fact, as of 2018, | |
| 55 | [[https://www.cpapracticeadvisor.com/accounting-audit/news/12404086/internal-audit-groups-are-lagging-in-data-analytics][only | |
| 56 | 63% of internal audit departments currently utilize data analytics]] in | |
| 57 | North America. This number should be as close as possible to 100%. I | |
| 60 | 58 | have never been part of an audit that would not have benefited from data |
| 61 | 59 | analytics. |
| 62 | 60 | |
| @@ -66,66 +64,70 @@ Chief Audit Executive that you're going to start implementing analytics | ||
| 66 | 64 | in the next audit. You need a plan and a system to make the analysis |
| 67 | 65 | process as effective as possible. |
| 68 | 66 | |
| 69 | # The DELTA Model | |
| 70 | ||
| 67 | * The DELTA Model | |
| 71 | 68 | One of the easiest ways to experiment with data analytics and gain an |
| 72 | 69 | understanding of the processes is to implement them within your own |
| 73 | 70 | department. But how do we do this if we've never worked with analysis |
| 74 | 71 | before? One of the most common places to start is to research some data |
| 75 | analysis models currently available. For this post, we'll take a look | |
| 76 | at the DELTA model. You can take a look at ****Figure 2**** for a quick | |
| 72 | analysis models currently available. For this post, we'll take a look at | |
| 73 | the DELTA model. You can take a look at ****Figure 2***** for a quick | |
| 77 | 74 | overview of the model. |
| 78 | 75 | |
| 79 | 76 | The DELTA model sets a few guidelines for areas wanting to implement |
| 80 | 77 | data analytics so that the results can be as comprehensive as possible: |
| 81 | 78 | |
| 82 | - **Data**: Must be clean, accessible, and (usually) unique. | |
| 83 | - **Enterprise-Wide Focus**: Key data systems and analytical resources | |
| 84 | must be available for use (by the Internal Audit Function). | |
| 85 | - **Leaders**: Must promote a data analytics approach and show the | |
| 86 | value of analytical results. | |
| 87 | - **Targets**: Must be set for key areas and risks that the analytics | |
| 88 | can be compared against (KPIs). | |
| 89 | - **Analysts**: There must be auditors willing and able to perform | |
| 90 | data analytics or else the system cannot be sustained. | |
| 79 | - *Data*: Must be clean, accessible, and (usually) unique. | |
| 80 | - *Enterprise-Wide Focus*: Key data systems and analytical resources | |
| 81 | must be available for use (by the Internal Audit Function). | |
| 82 | - *Leaders*: Must promote a data analytics approach and show the value | |
| 83 | of analytical results. | |
| 84 | - *Targets*: Must be set for key areas and risks that the analytics can | |
| 85 | be compared against (KPIs). | |
| 86 | - *Analysts*: There must be auditors willing and able to perform data | |
| 87 | analytics or else the system cannot be sustained. | |
| 91 | 88 | |
| 92 | 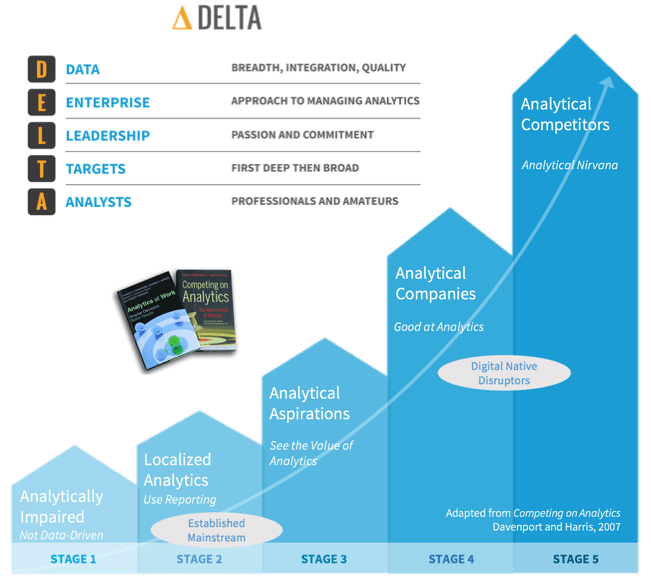 | |
| 94 | ||
| 95 | # Finding the Proper KPIs | |
| 89 | #+caption: The Delta Model | |
| 90 | [[https://img.cleberg.net/blog/20190909-data-analysis-in-auditing/delta-min.png]] | |
| 96 | 91 | |
| 92 | * Finding the Proper KPIs | |
| 97 | 93 | Once the Internal Audit Function has decided that they want to start |
| 98 | using data analytics internally and have ensured they're properly set | |
| 99 | up to do so, they need to figure out what they will be testing against. | |
| 100 | Key Performance Indicators (KPIs) are qualitative or quantitative | |
| 101 | factors that can be evaluated and assessed to determine if the | |
| 102 | department is performing well, usually compared to historical or | |
| 103 | industry benchmarks. Once KPIs have been agreed upon and set, auditors | |
| 104 | can use data analytics to assess and report on these KPIs. This allows | |
| 105 | the person performing the analytics the freedom to express opinions on | |
| 106 | the results, whereas the results are ambiguous if no KPIs exist. | |
| 94 | using data analytics internally and have ensured they're properly set up | |
| 95 | to do so, they need to figure out what they will be testing against. Key | |
| 96 | Performance Indicators (KPIs) are qualitative or quantitative factors | |
| 97 | that can be evaluated and assessed to determine if the department is | |
| 98 | performing well, usually compared to historical or industry benchmarks. | |
| 99 | Once KPIs have been agreed upon and set, auditors can use data analytics | |
| 100 | to assess and report on these KPIs. This allows the person performing | |
| 101 | the analytics the freedom to express opinions on the results, whereas | |
| 102 | the results are ambiguous if no KPIs exist. | |
| 107 | 103 | |
| 108 | 104 | It should be noted that tracking KPIs in the department can help ensure |
| 109 | 105 | you have a rigorous Quality Assurance and Improvement Program (QAIP) in |
| 110 | 106 | accordance with some applicable standards, such as IPPF Standard 1300. |
| 111 | 107 | |
| 112 | > The chief audit executive must develop and maintain a quality assurance | |
| 113 | > and improvement program that covers all aspects of the internal audit | |
| 114 | > activity. | |
| 115 | > | |
| 116 | > - IPPF Standard 1300 | |
| 108 | #+begin_quote | |
| 109 | The chief audit executive must develop and maintain a quality assurance | |
| 110 | and improvement program that covers all aspects of the internal audit | |
| 111 | activity. | |
| 112 | ||
| 113 | - IPPF Standard 1300 | |
| 114 | ||
| 115 | #+end_quote | |
| 117 | 116 | |
| 118 | 117 | Additionally, IPPF Standard 2060 discusses reporting: |
| 119 | 118 | |
| 120 | > The chief audit executive must report periodically to senior | |
| 121 | > management and the board on the internal audit activity's purpose, | |
| 122 | > authority, responsibility, and performance relative to its plan and on | |
| 123 | > its conformance with the Code of Ethics and the Standards. Reporting | |
| 124 | > must also include significant risk and control issues, including fraud | |
| 125 | > risks, governance issues, and other matters that require the attention | |
| 126 | > of senior management and/or the board. | |
| 127 | > | |
| 128 | > - IPPF Standard 2060 | |
| 119 | #+begin_quote | |
| 120 | The chief audit executive must report periodically to senior management | |
| 121 | and the board on the internal audit activity's purpose, authority, | |
| 122 | responsibility, and performance relative to its plan and on its | |
| 123 | conformance with the Code of Ethics and the Standards. Reporting must | |
| 124 | also include significant risk and control issues, including fraud risks, | |
| 125 | governance issues, and other matters that require the attention of | |
| 126 | senior management and/or the board. | |
| 127 | ||
| 128 | - IPPF Standard 2060 | |
| 129 | ||
| 130 | #+end_quote | |
| 129 | 131 | |
| 130 | 132 | The hardest part of finding KPIs is to determine which KPIs are |
| 131 | 133 | appropriate for your department. Since every department is different and |
| @@ -133,37 +135,35 @@ has different goals, KPIs will vary drastically between companies. To | ||
| 133 | 135 | give you an idea of where to look, here are some ideas I came up with |
| 134 | 136 | when discussing the topic with a few colleagues. |
| 135 | 137 | |
| 136 | - Efficiency/Budgeting: | |
| 137 | - Audit hours to staff utilization ratio (annual hours divided by | |
| 138 | total annual work hours). | |
| 139 | - Audit hours compared to the number of audits completed. | |
| 140 | - Time between audit steps or to complete the whole audit. E.g., | |
| 141 | time from fieldwork completion to audit report issuance. | |
| 142 | - Reputation: | |
| 143 | - The frequency that management has requested the services of the | |
| 144 | IAF. | |
| 145 | - Management, audit committee, or external audit satisfaction | |
| 146 | survey results. | |
| 147 | - Education, experience, certifications, tenure, and training of | |
| 148 | the auditors on staff. | |
| 149 | - Quality: | |
| 150 | - Number and frequency of audit findings. Assign monetary or | |
| 151 | numerical values, if possible. | |
| 152 | - Percentage of recommendations issued and implemented. | |
| 153 | - Planning: | |
| 154 | - Percentage or number of key risks audited per year or per audit. | |
| 155 | - Proportion of audit universe audited per year. | |
| 156 | ||
| 157 | # Data Analysis Tools | |
| 158 | ||
| 138 | - Efficiency/Budgeting: | |
| 139 | - Audit hours to staff utilization ratio (annual hours divided by | |
| 140 | total annual work hours). | |
| 141 | - Audit hours compared to the number of audits completed. | |
| 142 | - Time between audit steps or to complete the whole audit. E.g., time | |
| 143 | from fieldwork completion to audit report issuance. | |
| 144 | - Reputation: | |
| 145 | - The frequency that management has requested the services of the IAF. | |
| 146 | - Management, audit committee, or external audit satisfaction survey | |
| 147 | results. | |
| 148 | - Education, experience, certifications, tenure, and training of the | |
| 149 | auditors on staff. | |
| 150 | - Quality: | |
| 151 | - Number and frequency of audit findings. Assign monetary or numerical | |
| 152 | values, if possible. | |
| 153 | - Percentage of recommendations issued and implemented. | |
| 154 | - Planning: | |
| 155 | - Percentage or number of key risks audited per year or per audit. | |
| 156 | - Proportion of audit universe audited per year. | |
| 157 | ||
| 158 | * Data Analysis Tools | |
| 159 | 159 | Finally, to be able to analyze and report on the data analysis, auditors |
| 160 | 160 | need to evaluate the tools at their disposal. There are many options |
| 161 | 161 | available, but a few of the most common ones can easily get the job |
| 162 | 162 | done. For example, almost every auditor already has access to Microsoft |
| 163 | 163 | Excel. Excel is more powerful than most people give it credit for and |
| 164 | can accomplish a lot of basic statistics without much work. If you | |
| 165 | don't know a lot about statistics but still want to see some of the | |
| 166 | more basic results, Excel is a great option. | |
| 164 | can accomplish a lot of basic statistics without much work. If you don't | |
| 165 | know a lot about statistics but still want to see some of the more basic | |
| 166 | results, Excel is a great option. | |
| 167 | 167 | |
| 168 | 168 | To perform more in-depth statistical analysis or to explore large |
| 169 | 169 | datasets that Excel cannot handle, auditors will need to explore other |
| @@ -182,8 +182,7 @@ increases, it usually means that the learning curve for that tool will | ||
| 182 | 182 | also be higher. It will take auditors longer to learn how to utilize |
| 183 | 183 | Python, R, or ACL versus learning how to utilize Excel. |
| 184 | 184 | |
| 185 | # Visualization | |
| 186 | ||
| 185 | * Visualization | |
| 187 | 186 | Once an auditor has finally found the right data, KPIs, and tools, they |
| 188 | 187 | must report these results so that actions can be taken. Performing |
| 189 | 188 | in-depth data analysis is only useful if the results are understood by |
| @@ -196,34 +195,33 @@ Microsoft PowerBI and Tableau Desktop. However, other tools exist such | ||
| 196 | 195 | as JMP, Plotly, Qlikview, Alteryx, or D3. Some require commercial |
| 197 | 196 | licenses while others are simply free to use. For corporate data, you |
| 198 | 197 | may want to make sure that the tool does not communicate any of the data |
| 199 | outside the company (such as cloud storage). I won't be going into | |
| 200 | depth on any of these tools since visualization is largely a subjective | |
| 201 | and creative experience, but remember to constantly explore new options | |
| 202 | as you repeat the process. | |
| 198 | outside the company (such as cloud storage). I won't be going into depth | |
| 199 | on any of these tools since visualization is largely a subjective and | |
| 200 | creative experience, but remember to constantly explore new options as | |
| 201 | you repeat the process. | |
| 203 | 202 | |
| 204 | 203 | Lastly, let's take a look at an example of data visualization. This |
| 205 | example comes from a [blog post written by Kushal | |
| 206 | Chakrabarti](https://talent.works/2018/03/28/the-science-of-the-job-search-part-iii-61-of-entry-level-jobs-require-3-years-of-experience/) | |
| 207 | in 2018 about the percent of entry-level US jobs that require | |
| 208 | experience. **Figure 3** shows us an easy-to-digest picture of the data. | |
| 209 | We can quickly tell that only about 12.5% of entry-level jobs don't | |
| 210 | require experience. | |
| 204 | example comes from a | |
| 205 | [[https://talent.works/2018/03/28/the-science-of-the-job-search-part-iii-61-of-entry-level-jobs-require-3-years-of-experience/][blog | |
| 206 | post written by Kushal Chakrabarti]] in 2018 about the percent of | |
| 207 | entry-level US jobs that require experience. *Figure 3** shows us an | |
| 208 | easy-to-digest picture of the data. We can quickly tell that only about | |
| 209 | 12.5% of entry-level jobs don't require experience. | |
| 211 | 210 | |
| 212 | 211 | This is the kind of result that easily describes the data for you. |
| 213 | 212 | However, make sure to include an explanation of what the results mean. |
| 214 | 213 | Don't let the reader assume what the data means, especially if it |
| 215 | relates to a complex subject. *Tell a story* about the data and why the | |
| 216 | results matter. For example, **Figure 4** shows a part of the | |
| 217 | explanation the author gives to illustrate his point. | |
| 218 | ||
| 219 | 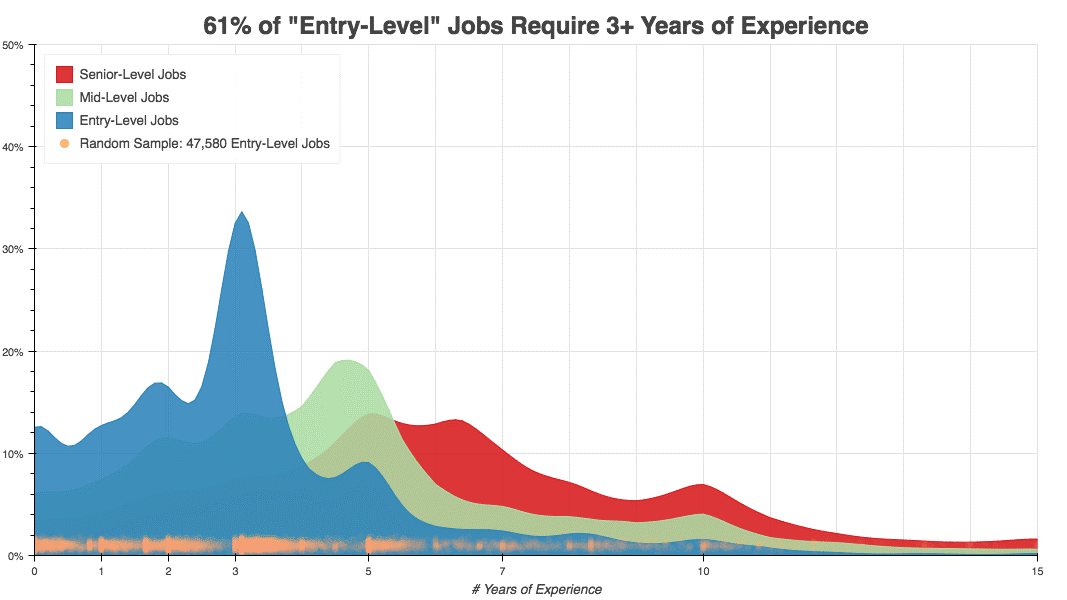 | |
| 214 | relates to a complex subject. /Tell a story/ about the data and why the | |
| 215 | results matter. For example, *Figure 4** shows a part of the explanation | |
| 216 | the author gives to illustrate his point. | |
| 221 | 217 | |
| 222 | 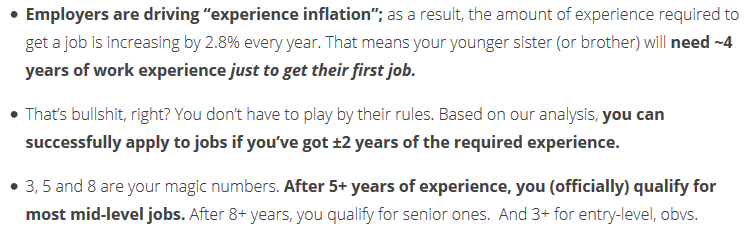 | |
| 218 | #+caption: Entry-Level Visualization | |
| 219 | [[https://img.cleberg.net/blog/20190909-data-analysis-in-auditing/vis_example-min.png]] | |
| 224 | 220 | |
| 225 | # Wrap-Up | |
| 221 | #+caption: Visualization Explanation | |
| 222 | [[https://img.cleberg.net/blog/20190909-data-analysis-in-auditing/vis_example_explanation-min.png]] | |
| 226 | 223 | |
| 224 | * Wrap-Up | |
| 227 | 225 | While this is not an all-encompassing program that you can just adopt |
| 228 | 226 | into your department, it should be enough to get anyone started on the |
| 229 | 227 | process of understanding and implementing data analytics. Always |
blog/audit-dashboard/index.org added +171
| @@ -0,0 +1,171 @@ | ||
| 1 | #+title: Building an Audit Status Dashboard | |
| 2 | #+date: 2024-01-26 | |
| 3 | #+description: Learn how to utilize Alteryx Designer and Power BI Desktop to build a simple status tracking dashboard for an audit or other engagement. | |
| 4 | #+filetags: :audit: | |
| 5 | ||
| 6 | Alteryx and Power BI are powerful tools that can help turn your | |
| 7 | old-school audit trackers into interactive tools that provide useful | |
| 8 | insights and potential action plans. | |
| 9 | ||
| 10 | With these tools, we are going to build the following dashboard: | |
| 11 | ||
| 12 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/dashboard_01.png]] | |
| 13 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/dashboard_02.png]] | |
| 14 | ||
| 15 | * Requirements | |
| 16 | This project assumes the following: | |
| 17 | ||
| 18 | - You have access to Alteryx Designer and Power BI Desktop. | |
| 19 | - If you only have Power BI Desktop, you may need to perform some | |
| 20 | analysis in Power BI instead of Alteryx. | |
| 21 | - Your data is in a format that can be imported into Alteryx and/or | |
| 22 | Power BI. | |
| 23 | - You have a basic understanding of data types and visualization. | |
| 24 | ||
| 25 | * Alteryx: Data Preparation & Analysis | |
| 26 | ** Import Data | |
| 27 | With Alteryx, importing data is easy with the use of the =Input Data= | |
| 28 | tool. Simply drag this tool onto the canvas from the =In/Out= tab in the | |
| 29 | Ribbon to create it as a node. | |
| 30 | ||
| 31 | You can choose the File Format manually or simply connect to your | |
| 32 | file/database and let Alteryx determine the format for you. For this | |
| 33 | example, we will be importing an Excel file and changing the | |
| 34 | =Start Data Import on Line= variable to =2=. | |
| 35 | ||
| 36 | #+caption: Alteryx Excel Import | |
| 37 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/alteryx_import.png]] | |
| 38 | ||
| 39 | ** Transform Data | |
| 40 | Next, let's replace null data and remove whitespace to clean up our | |
| 41 | data. We can do this with the =Data Cleansing= tool in the =Preparation= | |
| 42 | tab in the Ribbon. | |
| 43 | ||
| 44 | Ensure that the following options are enabled: | |
| 45 | ||
| 46 | - Replace Nulls | |
| 47 | - Replace with Blanks (String Fields) | |
| 48 | - Replace with 0 (Numeric Fields) | |
| 49 | - Remove Unwanted Characters | |
| 50 | - Leading and Trailing Whitespace | |
| 51 | ||
| 52 | #+caption: Data Cleansing | |
| 53 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/alteryx_cleansing.png]] | |
| 54 | ||
| 55 | For our next step, we will transform the date fields from strings to | |
| 56 | datetime format. Add a =Datetime= tool for each field you want to | |
| 57 | transform - in the example below, I am using the tool twice for the | |
| 58 | "Started On" and "Submitted On" fields. | |
| 59 | ||
| 60 | #+caption: Data Transformation | |
| 61 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/alteryx_transformation.png]] | |
| 62 | ||
| 63 | Now that the dates are in the correct format, let's perform a | |
| 64 | calculation based on those fields. Start by adding a =Filter= tool, | |
| 65 | naming a new Output Column, and pasting the formula below into it (the | |
| 66 | two fields used in this formula must match the output of the =Datetime= | |
| 67 | tools above): | |
| 68 | ||
| 69 | #+begin_src txt | |
| 70 | DateTimeDiff([SubmittedOn_Out],[StartedOn_Out], "days") | |
| 71 | #+end_src | |
| 72 | ||
| 73 | #+caption: Data Analysis | |
| 74 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/alteryx_analysis.png]] | |
| 75 | ||
| 76 | ** Export Data | |
| 77 | Finalize the process by exporting the transformed data set to a new | |
| 78 | file, for use in the following visualization step. | |
| 79 | ||
| 80 | #+caption: Data Export | |
| 81 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/alteryx_export.png]] | |
| 82 | ||
| 83 | * Power BI: Data Visualization | |
| 84 | ** Import Data | |
| 85 | To start, open the Power BI Desktop application. Upon first use, Power | |
| 86 | BI will ask if you want to open an existing dashboard or import new | |
| 87 | data. | |
| 88 | ||
| 89 | As we are creating our first dashboard, let's import our data. In my | |
| 90 | example below, I'm importing data from the "Tracker" sheet of the Excel | |
| 91 | file I'm using for this project. | |
| 92 | ||
| 93 | During this process, I also imported the export from the Alteryx | |
| 94 | workflow above. Therefore, we have two different files available for use | |
| 95 | in our dashboard. | |
| 96 | ||
| 97 | #+caption: Excel Tracker | |
| 98 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/excel_tracker.png]] | |
| 99 | ||
| 100 | #+caption: Power BI Excel Import | |
| 101 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/powerbi_import.png]] | |
| 102 | ||
| 103 | ** Add Visuals | |
| 104 | To create the dashboard below, you will need to follow the list | |
| 105 | instructions below and format as needed: | |
| 106 | ||
| 107 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/dashboard_01.png]] | |
| 108 | [[https://img.cleberg.net/blog/20240126-audit-dashboard/dashboard_02.png]] | |
| 109 | ||
| 110 | Instructions to create the visuals above: | |
| 111 | ||
| 112 | - =Text Box=: Explain the name and purpose of the dashboard. You can | |
| 113 | also add images and logos at the top of the dashboard. | |
| 114 | - =Donut Chart=: Overall status of the project. | |
| 115 | - =Legend=: Status | |
| 116 | - =Values=: Count of Status | |
| 117 | - =Stacked Column Chart=: Task count by assignee. | |
| 118 | - =X-axis=: Preparer | |
| 119 | - =Y-axis=: Count of Control ID | |
| 120 | - =Legend=: Status | |
| 121 | - =Treemap=: Top N client submitters by average days to submit. | |
| 122 | - =Details=: Preparer | |
| 123 | - =Values=: Sum of Avg_DaysToSubmit | |
| 124 | - =Line Chart=: Projected vs. actual hours over time. | |
| 125 | - =Clustered Bar Chart=: Projected vs. actual hours per person. | |
| 126 | - =Slicer & Table= - Upcoming due dates. | |
| 127 | - =Slicer=: | |
| 128 | - =Values=: Date Due | |
| 129 | - =Table=: | |
| 130 | - =Columns=: Count of Control ID, Date Due, Preparer, Status | |
| 131 | ||
| 132 | ** Format the Dashboard | |
| 133 | You can choose a theme in the View tab of the Ribbon. You can even | |
| 134 | browse for custom JSON files that define themes, such as ones found | |
| 135 | online or custom ones created by your organization. | |
| 136 | ||
| 137 | For each visual, you can click the =Format= button in the | |
| 138 | =Visualizations= side pane and explore the options. You can custom | |
| 139 | options such as: | |
| 140 | ||
| 141 | - Visual | |
| 142 | - Legend | |
| 143 | - Colors | |
| 144 | - Data labels | |
| 145 | - Category labels | |
| 146 | - General | |
| 147 | - Properties | |
| 148 | - Title | |
| 149 | - Effects | |
| 150 | - Header icons | |
| 151 | - Tooltips | |
| 152 | - Alt text | |
| 153 | ||
| 154 | You can always look online for inspiration when trying to decide how | |
| 155 | best to organize and style your dashboard. | |
| 156 | ||
| 157 | * Sharing the Results | |
| 158 | Generally, you have a few different options for sharing your dashboards | |
| 159 | with others: | |
| 160 | ||
| 161 | 1. Export the dashboard as a PDF in the file menu of Power BI. This will | |
| 162 | export all tabs and visuals as they are set when the export button is | |
| 163 | pressed. You will lose all interactivity with this option. | |
| 164 | 2. Send the full Power BI file to those you wish to share the dashboard. | |
| 165 | This will retain all settings and interactivity. However, you will | |
| 166 | also need to send the source files if they need to refresh the | |
| 167 | dashboard and you will need to re-send the files if you make updates. | |
| 168 | 3. Store the dashboard in a synced location, such as a shared drive or | |
| 169 | Microsoft Teams. Depending on how a user configures their local | |
| 170 | Windows paths, the data source paths may not be compatible for all | |
| 171 | users with such a setup. | |
blog/audit-review-template/index.org added +76
| @@ -0,0 +1,76 @@ | ||
| 1 | #+title: Audit Testing Review Template | |
| 2 | #+date: 2023-06-20 | |
| 3 | #+description: A handy reference template for audit review. | |
| 4 | #+filetags: :audit: | |
| 5 | ||
| 6 | * Overview | |
| 7 | This post is a /very/ brief overview on the basic process to review | |
| 8 | audit test results, focusing on work done as part of a financial | |
| 9 | statement audit (FSA) or service organization controls (SOC) report. | |
| 10 | ||
| 11 | While there are numerous different things to review and look for - all | |
| 12 | varying wildly depending on the report, client, and tester - this list | |
| 13 | serves as a solid base foundation for a reviewer. | |
| 14 | ||
| 15 | I have used this throughout my career as a starting point to my reviews, | |
| 16 | and it has worked wonders for creating a consistent and objective | |
| 17 | template to my reviews. The goal is to keep this base high-level enough | |
| 18 | to be used on a wide variety of engagements, while still ensuring that | |
| 19 | all key areas are covered. | |
| 20 | ||
| 21 | * Review Template | |
| 22 | 1. [ ] Check all documents for spelling and grammar. | |
| 23 | 2. [ ] Ensure all acronyms are fully explained upon first use. | |
| 24 | 3. [ ] For all people referenced, use their full names and job titles | |
| 25 | upon first use. | |
| 26 | 4. [ ] All supporting documents must cross-reference to the lead sheet | |
| 27 | and vice-versa. | |
| 28 | 5. [ ] Verify that the control has been adequately tested: | |
| 29 | - [ ] *Test of Design*: Did the tester obtain information regarding | |
| 30 | how the control should perform normally and abnormally (e.g., | |
| 31 | emergency scenarios)? | |
| 32 | - [ ] *Test of Operating Effectiveness*: Did the tester inquire, | |
| 33 | observe, inspect, or re-perform sufficient evidence to support | |
| 34 | their conclusion over the control? Inquiry alone is not adequate! | |
| 35 | 6. [ ] For any information used in the control, whether by the control | |
| 36 | operator or by the tester, did the tester appropriately document the | |
| 37 | source (system or person), extraction method, parameters, and | |
| 38 | completeness and accuracy (C&A)? | |
| 39 | - [ ] For any reports, queries, etc. used in the extraction, did the | |
| 40 | tester include a copy and notate C&A considerations? | |
| 41 | 7. [ ] Did the tester document the specific criteria that the control is | |
| 42 | being tested against? | |
| 43 | 8. [ ] Did the tester notate in the supporting documents where each | |
| 44 | criterion was satisfied? | |
| 45 | 9. [ ] If testing specific policies or procedures, are the documents | |
| 46 | adequate? | |
| 47 | - [ ] e.g., a test to validate that a review of policy XYZ occurs | |
| 48 | periodically should also evaluate the sufficiency of the policy | |
| 49 | itself, if meant to cover the risk that such a policy does not | |
| 50 | exist and is not reviewed. | |
| 51 | 10. [ ] Does the test cover the appropriate period under review? | |
| 52 | - [ ] If the test is meant to cover only a portion of the audit | |
| 53 | period, do other controls exist to mitigate the risks that exist | |
| 54 | for the remainder of the period? | |
| 55 | 11. [ ] For any computer-aided audit tools (CAATs) or other automation | |
| 56 | techniques used in the test, is the use of such tools explained and | |
| 57 | appropriately documented? | |
| 58 | 12. [ ] If prior-period documentation exists, are there any missing | |
| 59 | pieces of evidence that would further enhance the quality of the | |
| 60 | test? | |
| 61 | 13. [ ] Was any information discovered during the walkthrough or inquiry | |
| 62 | phase that was not incorporated into the test? | |
| 63 | 14. [ ] Are there new rules or expectations from your company's internal | |
| 64 | guidance or your regulatory bodies that would affect the audit | |
| 65 | approach for this control? | |
| 66 | 15. [ ] Was an exception, finding, or deficiency identified as a result | |
| 67 | of this test? | |
| 68 | - [ ] Was the control deficient in design, operation, or both? | |
| 69 | - [ ] What was the root cause of the finding? | |
| 70 | - [ ] Does the finding indicate other findings or potential fraud? | |
| 71 | - [ ] What's the severity and scope of the finding? | |
| 72 | - [ ] Do other controls exist as a form of compensation against the | |
| 73 | finding's severity, and do they mitigate the risk within the | |
| 74 | control objective? | |
| 75 | - [ ] Does the finding exist at the end of the period, or was it | |
| 76 | resolved within the audit period? | |
content/blog/2021-08-25-audit-sampling.md → blog/audit-sampling/index.org renamed +74 −87
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-08-25 | |
| 3 | title = "Audit Sampling with Python" | |
| 4 | description = "Learn how to sample populations with Python." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Introduction | |
| 1 | #+title: Audit Sampling with Python | |
| 2 | #+date: 2021-08-25 | |
| 3 | #+description: Learn how to sample populations with Python. | |
| 4 | #+filetags: :audit: | |
| 8 | 5 | |
| 6 | * Introduction | |
| 9 | 7 | For anyone who is familiar with internal auditing, external auditing, or |
| 10 | 8 | consulting, you will understand how tedious audit testing can become |
| 11 | 9 | when you are required to test large swaths of data. When we cannot |
| @@ -16,37 +14,35 @@ represent the population. | ||
| 16 | 14 | |
| 17 | 15 | However, sampling data within the world of audit still seems to confuse |
| 18 | 16 | quite a lot of people. While some audit-focused tools have introduced |
| 19 | sampling functionality (e.g. Wdesk), many audit departments and firms | |
| 17 | sampling functionality (e.g. Wdesk), many audit departments and firms | |
| 20 | 18 | cannot use software like this due to certain constraints, such as the |
| 21 | 19 | team's budget or knowledge. Here is where this article comes in: we're |
| 22 | going to use [Python](https://www.python.org), a free and open-source | |
| 20 | going to use [[https://www.python.org][Python]], a free and open-source | |
| 23 | 21 | programming language, to generate random samples from a dataset in order |
| 24 | 22 | to suffice numerous audit situations. |
| 25 | 23 | |
| 26 | ## Audit Requirements for Sampling | |
| 27 | ||
| 24 | * Audit Requirements for Sampling | |
| 28 | 25 | Before we get into the details of how to sample with Python, I want to |
| 29 | 26 | make sure I discuss the different requirements that auditors may have of |
| 30 | 27 | samples used within their projects. |
| 31 | 28 | |
| 32 | ### Randomness | |
| 33 | ||
| 34 | First, let's discuss randomness. When testing out new technology to | |
| 35 | help assist with audit sampling, you need to understand exactly how your | |
| 29 | ** Randomness | |
| 30 | First, let's discuss randomness. When testing out new technology to help | |
| 31 | assist with audit sampling, you need to understand exactly how your | |
| 36 | 32 | samples are being generated. For example, if the underlying function is |
| 37 | 33 | just picking every 57th element from a list, that's not truly random; |
| 38 | 34 | it's a systematic form of sampling. Luckily, since Python is |
| 39 | 35 | open-source, we have access to its codebase. Through this blog post, I |
| 40 | will be using the [pandas](https://pandas.pydata.org) module in order to | |
| 41 | generate the random samples. More specifically, I will be using the | |
| 42 | [pandas.DataFrame.sample](https://pandas.pydata.org/pandas-docs/stable/reference/api/pandas.DataFrame.sample.html) | |
| 36 | will be using the [[https://pandas.pydata.org][pandas]] module in order | |
| 37 | to generate the random samples. More specifically, I will be using the | |
| 38 | [[https://pandas.pydata.org/pandas-docs/stable/reference/api/pandas.DataFrame.sample.html][pandas.DataFrame.sample]] | |
| 43 | 39 | function provided by Pandas. |
| 44 | 40 | |
| 45 | 41 | Now that you know what you're using, you can always check out the code |
| 46 | behind `pandas.DataFrame.sample`. This function does a lot of | |
| 47 | work, but we really only care about the following snippets of code: | |
| 42 | behind =pandas.DataFrame.sample=. This function does a lot of work, but | |
| 43 | we really only care about the following snippets of code: | |
| 48 | 44 | |
| 49 | ```python | |
| 45 | #+begin_src python | |
| 50 | 46 | # Process random_state argument |
| 51 | 47 | rs = com.random_state(random_state) |
| 52 | 48 | |
| @@ -58,24 +54,22 @@ if ignore_index: | ||
| 58 | 54 | result.index = ibase.default_index(len(result)) |
| 59 | 55 | |
| 60 | 56 | return result |
| 61 | ``` | |
| 62 | ||
| 63 | The block of code above shows you that if you assign a | |
| 64 | `random_state` argument when you run the function, that will | |
| 65 | be used as a seed number in the random generation and will allow you to | |
| 66 | reproduce a sample, given that nothing else changes. This is critical to | |
| 67 | the posterity of audit work. After all, how can you say your audit | |
| 68 | process is adequately documented if the next person can't run the code | |
| 69 | and get the same sample? The final piece here on randomness is to look | |
| 70 | at the | |
| 71 | [choice](https://docs.%20python.org/3/library/random.html#random.choice) | |
| 57 | #+end_src | |
| 58 | ||
| 59 | The block of code above shows you that if you assign a =random_state= | |
| 60 | argument when you run the function, that will be used as a seed number | |
| 61 | in the random generation and will allow you to reproduce a sample, given | |
| 62 | that nothing else changes. This is critical to the posterity of audit | |
| 63 | work. After all, how can you say your audit process is adequately | |
| 64 | documented if the next person can't run the code and get the same | |
| 65 | sample? The final piece here on randomness is to look at the | |
| 66 | [[https://docs.%20python.org/3/library/random.html#random.choice][choice]] | |
| 72 | 67 | function used above. This is the crux of the generation and can also be |
| 73 | 68 | examined for more detailed analysis on its reliability. As far as |
| 74 | 69 | auditing goes, we will trust that these functions are mathematically |
| 75 | 70 | random. |
| 76 | 71 | |
| 77 | ### Sample Sizes | |
| 78 | ||
| 72 | ** Sample Sizes | |
| 79 | 73 | As mentioned in the intro, sampling is only an effective method of |
| 80 | 74 | auditing when it truly represents the entire population. While some |
| 81 | 75 | audit departments or firms may consider certain judgmental sample sizes |
| @@ -94,35 +88,32 @@ proprietary, table that will instruct auditors which sample sizes to | ||
| 94 | 88 | choose. This allows for uniform testing and reduces overall workload. |
| 95 | 89 | See the table below for a common implementation of sample sizes: |
| 96 | 90 | |
| 97 | Control Frequency Sample Size - High Risk Sample Size - Low Risk | |
| 98 | ------------------- ------------------------- ------------------------ | |
| 99 | More Than Daily 40 25 | |
| 100 | Daily 40 25 | |
| 101 | Weekly 12 5 | |
| 102 | Monthly 5 3 | |
| 103 | Quarterly 2 2 | |
| 104 | Semi-Annually 1 1 | |
| 105 | Annually 1 1 | |
| 106 | Ad-hoc 1 1 | |
| 107 | ||
| 108 | ## Sampling with Python & Pandas | |
| 109 | ||
| 91 | | Control Frequency | Sample Size - High Risk | Sample Size - Low Risk | | |
| 92 | |-------------------+-------------------------+------------------------| | |
| 93 | | More Than Daily | 40 | 25 | | |
| 94 | | Daily | 40 | 25 | | |
| 95 | | Weekly | 12 | 5 | | |
| 96 | | Monthly | 5 | 3 | | |
| 97 | | Quarterly | 2 | 2 | | |
| 98 | | Semi-Annually | 1 | 1 | | |
| 99 | | Annually | 1 | 1 | | |
| 100 | | Ad-hoc | 1 | 1 | | |
| 101 | ||
| 102 | *** Sampling with Python & Pandas | |
| 110 | 103 | In this section, I am going to cover a few basic audit situations that |
| 111 | 104 | require sampling. While some situations may require more effort, the |
| 112 | 105 | syntax, organization, and intellect used remain largely the same. If |
| 113 | you've never used Python before, note that lines starting with a | |
| 114 | '`#`' symbol are called comments, and they will be skipped | |
| 115 | by Python. I highly recommend taking a quick tutorial online to | |
| 116 | understand the basics of Python if any of the code below is confusing to | |
| 117 | you. | |
| 118 | ||
| 119 | ### Simple Random Sample | |
| 106 | you've never used Python before, note that lines starting with a '=#=' | |
| 107 | symbol are called comments, and they will be skipped by Python. I highly | |
| 108 | recommend taking a quick tutorial online to understand the basics of | |
| 109 | Python if any of the code below is confusing to you. | |
| 120 | 110 | |
| 111 | ** Simple Random Sample | |
| 121 | 112 | First, let's look at a simple, random sample. The code block below will |
| 122 | import the `pandas` module, load a data file, sample the | |
| 123 | data, and export the sample to a file. | |
| 113 | import the =pandas= module, load a data file, sample the data, and | |
| 114 | export the sample to a file. | |
| 124 | 115 | |
| 125 | ```python | |
| 116 | #+begin_src python | |
| 126 | 117 | # Import the Pandas module |
| 127 | 118 | import pandas |
| 128 | 119 | |
| @@ -140,14 +131,13 @@ sample = df.sample(n=25, random_state=0) | ||
| 140 | 131 | |
| 141 | 132 | # Save the sample to Excel |
| 142 | 133 | sample.to_excel(file_output) |
| 143 | ``` | |
| 144 | ||
| 145 | ### Simple Random Sample: Using Multiple Input Files | |
| 134 | #+end_src | |
| 146 | 135 | |
| 136 | ** Simple Random Sample: Using Multiple Input Files | |
| 147 | 137 | Now that we've created a simple sample, let's create a sample from |
| 148 | 138 | multiple files. |
| 149 | 139 | |
| 150 | ```python | |
| 140 | #+begin_src python | |
| 151 | 141 | # Import the Pandas module |
| 152 | 142 | import pandas |
| 153 | 143 | |
| @@ -174,15 +164,14 @@ sample = pandas.concat([sample_01, sample_02, sample_03], ignore_index=True) | ||
| 174 | 164 | |
| 175 | 165 | # Save the sample to Excel |
| 176 | 166 | sample.to_excel(file_output) |
| 177 | ``` | |
| 178 | ||
| 179 | ### Stratified Random Sample | |
| 167 | #+end_src | |
| 180 | 168 | |
| 169 | ** Stratified Random Sample | |
| 181 | 170 | Well, what if you need to sample distinct parts of a single file? For |
| 182 | 171 | example, let's write some code to separate our data by "Region" and |
| 183 | 172 | sample those regions independently. |
| 184 | 173 | |
| 185 | ```python | |
| 174 | #+begin_src python | |
| 186 | 175 | # Import the Pandas module |
| 187 | 176 | import pandas |
| 188 | 177 | |
| @@ -208,16 +197,15 @@ sample = pandas.concat([sample_east, sample_west], ignore_index=True) | ||
| 208 | 197 | |
| 209 | 198 | # Save the sample to Excel |
| 210 | 199 | sample.to_excel(file_output) |
| 211 | ``` | |
| 212 | ||
| 213 | ### Stratified Systematic Sample | |
| 200 | #+end_src | |
| 214 | 201 | |
| 202 | ** Stratified Systematic Sample | |
| 215 | 203 | This next example is quite useful if you need audit coverage over a |
| 216 | 204 | certain time period. This code will generate samples for each month in |
| 217 | 205 | the data and combine them all together at the end. Obviously, this code |
| 218 | 206 | can be modified to stratify by something other than months, if needed. |
| 219 | 207 | |
| 220 | ```python | |
| 208 | #+begin_src python | |
| 221 | 209 | # Import the Pandas module |
| 222 | 210 | import pandas |
| 223 | 211 | |
| @@ -257,21 +245,20 @@ def monthly_stratified_sample(df: pandas.DataFrame, date_column: str, num_select | ||
| 257 | 245 | sample_size = 3 |
| 258 | 246 | sample = monthly_stratified_sample(df, 'Date of Sale', sample_size) |
| 259 | 247 | sample.to_excel(file_output) |
| 260 | ``` | |
| 261 | ||
| 262 | ## Documenting the Results | |
| 263 | ||
| 264 | Once you've generated a proper sample, there are a few things left to | |
| 265 | do in order to properly ensure your process is reproducible. | |
| 266 | ||
| 267 | 1. Document the sample. Make sure the resulting file is readable and | |
| 268 | includes the documentation listed in the next bullet. | |
| 269 | 2. Include documentation around the data source, extraction techniques, | |
| 270 | any modifications made to the data, and be sure to include a copy of | |
| 271 | the script itself. | |
| 272 | 3. Whenever possible, perform a completeness and accuracy test to | |
| 273 | ensure your sample is coming from a complete and accurate | |
| 274 | population. To ensure completeness, compare the record count from | |
| 275 | the data source to the record count loaded into Python. To ensure | |
| 276 | accuracy, test a small sample against the source data (e.g., test 5 | |
| 277 | sales against the database to see if the details are accurate). | |
| 248 | #+end_src | |
| 249 | ||
| 250 | *** Documenting the Results | |
| 251 | Once you've generated a proper sample, there are a few things left to do | |
| 252 | in order to properly ensure your process is reproducible. | |
| 253 | ||
| 254 | 1. Document the sample. Make sure the resulting file is readable and | |
| 255 | includes the documentation listed in the next bullet. | |
| 256 | 2. Include documentation around the data source, extraction techniques, | |
| 257 | any modifications made to the data, and be sure to include a copy of | |
| 258 | the script itself. | |
| 259 | 3. Whenever possible, perform a completeness and accuracy test to ensure | |
| 260 | your sample is coming from a complete and accurate population. To | |
| 261 | ensure completeness, compare the record count from the data source to | |
| 262 | the record count loaded into Python. To ensure accuracy, test a small | |
| 263 | sample against the source data (e.g., test 5 sales against the | |
| 264 | database to see if the details are accurate). | |
content/blog/2023-09-19-audit-sql-scripts.md → blog/audit-sql-scripts/index.org renamed +45 −55
| @@ -1,24 +1,21 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-09-19 | |
| 3 | title = "Useful SQL Scripts for Auditing Logical Access" | |
| 4 | description = "A reference of SQL scripts for auditing logical access for common databases." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Overview | |
| 1 | #+title: Useful SQL Scripts for Auditing Logical Access | |
| 2 | #+date: 2023-09-19 | |
| 3 | #+description: A reference of SQL scripts for auditing logical access for common databases. | |
| 4 | #+filetags: :audit: | |
| 8 | 5 | |
| 6 | * Overview | |
| 9 | 7 | When you have to scope a database into your engagement, you may be |
| 10 | 8 | curious how to best extract the information from the database. While |
| 11 | 9 | there are numerous different methods to extract this type of |
| 12 | information, I'm going to show an example of how to gather all users | |
| 13 | and privileges from three main database types: Oracle, Microsoft SQL, | |
| 14 | and MySQL. | |
| 15 | ||
| 16 | ## Oracle | |
| 10 | information, I'm going to show an example of how to gather all users and | |
| 11 | privileges from three main database types: Oracle, Microsoft SQL, and | |
| 12 | MySQL. | |
| 17 | 13 | |
| 14 | * Oracle | |
| 18 | 15 | You can use the following SQL script to see all users and their |
| 19 | 16 | privileges in an Oracle database: |
| 20 | 17 | |
| 21 | ```sql | |
| 18 | #+begin_src sql | |
| 22 | 19 | SELECT |
| 23 | 20 | grantee AS "User", |
| 24 | 21 | privilege AS "Privilege" |
| @@ -34,40 +31,37 @@ FROM | ||
| 34 | 31 | dba_tab_privs |
| 35 | 32 | WHERE |
| 36 | 33 | grantee IN (SELECT DISTINCT grantee FROM dba_tab_privs); |
| 37 | ``` | |
| 34 | #+end_src | |
| 38 | 35 | |
| 39 | This script queries the `dba_sys_privs` and | |
| 40 | `dba_tab_privs` views to retrieve system and table-level | |
| 41 | privileges respectively. It then combines the results using | |
| 42 | `UNION ALL` to show all users and their associated | |
| 43 | privileges. Please note that this method does not extract information | |
| 44 | from the `dba_role_privs` table - use the method below for | |
| 36 | This script queries the =dba_sys_privs= and =dba_tab_privs= views to | |
| 37 | retrieve system and table-level privileges respectively. It then | |
| 38 | combines the results using =UNION ALL= to show all users and their | |
| 39 | associated privileges. Please note that this method does not extract | |
| 40 | information from the =dba_role_privs= table - use the method below for | |
| 45 | 41 | that data. |
| 46 | 42 | |
| 47 | 43 | Please note that you might need appropriate privileges (e.g., DBA |
| 48 | 44 | privileges) to access these views, and you should exercise caution when |
| 49 | 45 | querying system tables in a production Oracle database. |
| 50 | 46 | |
| 51 | ### Alternative Oracle Query | |
| 52 | ||
| 47 | ** Alternative Oracle Query | |
| 53 | 48 | You can also extract each table's information separately and perform |
| 54 | 49 | processing outside the database to explore and determine the information |
| 55 | 50 | necessary for the audit: |
| 56 | 51 | |
| 57 | ```sql | |
| 58 | SELECT * FROM sys.dba_role_privs; | |
| 59 | SELECT * FROM sys.dba_sys_privs; | |
| 60 | SELECT * FROM sys.dba_tab_privs; | |
| 61 | SELECT * FROM sys.dba_users; | |
| 62 | ``` | |
| 63 | ||
| 64 | ## Microsoft SQL | |
| 52 | #+begin_src sql | |
| 53 | SELECT ** FROM sys.dba_role_privs; | |
| 54 | SELECT ** FROM sys.dba_sys_privs; | |
| 55 | SELECT ** FROM sys.dba_tab_privs; | |
| 56 | SELECT ** FROM sys.dba_users; | |
| 57 | #+end_src | |
| 65 | 58 | |
| 59 | * Microsoft SQL | |
| 66 | 60 | You can use the following SQL script to see all users and their |
| 67 | 61 | privileges in a Microsoft SQL Server database |
| 68 | ([source](https://stackoverflow.com/a/30040784)): | |
| 62 | ([[https://stackoverflow.com/a/30040784][source]]): | |
| 69 | 63 | |
| 70 | ```sql | |
| 64 | #+begin_src sql | |
| 71 | 65 | /* |
| 72 | 66 | Security Audit Report |
| 73 | 67 | 1) List all access provisioned to a sql user or windows user/group directly |
| @@ -98,7 +92,7 @@ ObjectName : Name of the object that the user/role is assigned permissions | ||
| 98 | 92 | definitions. |
| 99 | 93 | ColumnName : Name of the column of the object that the user/role is assigned permissions on. This value |
| 100 | 94 | is only populated if the object is a table, view or a table value function. |
| 101 | */ | |
| 95 | ,*/ | |
| 102 | 96 | |
| 103 | 97 | --List all access provisioned to a sql user or windows user/group directly |
| 104 | 98 | SELECT |
| @@ -212,45 +206,41 @@ ORDER BY | ||
| 212 | 206 | perm.[permission_name], |
| 213 | 207 | perm.[state_desc], |
| 214 | 208 | obj.type_desc--perm.[class_desc] |
| 215 | ``` | |
| 216 | ||
| 217 | ## MySQL | |
| 209 | #+end_src | |
| 218 | 210 | |
| 211 | * MySQL | |
| 219 | 212 | You can use the following SQL script to see all users and their |
| 220 | 213 | privileges in a MySQL database: |
| 221 | 214 | |
| 222 | ```sh | |
| 215 | #+begin_src sh | |
| 223 | 216 | mysql -u root -p |
| 224 | ``` | |
| 217 | #+end_src | |
| 225 | 218 | |
| 226 | 219 | Find all users and hosts with access to the database: |
| 227 | 220 | |
| 228 | ```sql | |
| 229 | SELECT * FROM information_schema.user_privileges; | |
| 230 | ``` | |
| 221 | #+begin_src sql | |
| 222 | SELECT ** FROM information_schema.user_privileges; | |
| 223 | #+end_src | |
| 231 | 224 | |
| 232 | 225 | This script retrieves user information and their associated |
| 233 | database-level privileges from the | |
| 234 | `information_schema.user_privileges` table in MySQL. It lists | |
| 235 | various privileges such as SELECT, INSERT, UPDATE, DELETE, CREATE, and | |
| 236 | more for each user and database combination. | |
| 226 | database-level privileges from the =information_schema.user_privileges= | |
| 227 | table in MySQL. It lists various privileges such as SELECT, INSERT, | |
| 228 | UPDATE, DELETE, CREATE, and more for each user and database combination. | |
| 237 | 229 | |
| 238 | Please note that you may need appropriate privileges (e.g., | |
| 239 | `SELECT` privileges on | |
| 240 | `information_schema.user_privileges`) to access this | |
| 230 | Please note that you may need appropriate privileges (e.g., =SELECT= | |
| 231 | privileges on =information_schema.user_privileges=) to access this | |
| 241 | 232 | information in a MySQL database. Additionally, some privileges like |
| 242 | 233 | GRANT OPTION, EXECUTE, EVENT, and TRIGGER may not be relevant for all |
| 243 | 234 | users and databases. |
| 244 | 235 | |
| 245 | ### Alternative MySQL Query | |
| 246 | ||
| 236 | ** Alternative MySQL Query | |
| 247 | 237 | You can also grab individual sets of data from MySQL if you prefer to |
| 248 | 238 | join them after extraction. I have marked the queries below with |
| 249 | `SELECT ...` and excluded most `WHERE` clauses for | |
| 250 | brevity. You should determine the relevant privileges in-scope and query | |
| 251 | for those privileges to reduce the length of time to query. | |
| 239 | =SELECT ...= and excluded most =WHERE= clauses for brevity. You should | |
| 240 | determine the relevant privileges in-scope and query for those | |
| 241 | privileges to reduce the length of time to query. | |
| 252 | 242 | |
| 253 | ```sql | |
| 243 | #+begin_src sql | |
| 254 | 244 | -- Global Permissions |
| 255 | 245 | SELECT ... FROM mysql.user; |
| 256 | 246 | |
| @@ -269,4 +259,4 @@ WHERE db = @db_name; | ||
| 269 | 259 | -- Password Configuration |
| 270 | 260 | SHOW GLOBAL VARIABLES LIKE 'validate_password%'; |
| 271 | 261 | SHOW VARIABLES LIKE 'validate_password%'; |
| 272 | ``` | |
| 262 | #+end_src | |
blog/backblaze-b2/index.org added +176
| @@ -0,0 +1,176 @@ | ||
| 1 | #+title: Getting Started with Backblaze B2 Cloud Storage | |
| 2 | #+date: 2023-06-28 | |
| 3 | #+description: An introduction to the free ttier of Backblaze B2 Cloud Storage. | |
| 4 | #+filetags: :sysadmin: | |
| 5 | ||
| 6 | * Overview | |
| 7 | Backblaze [[https://www.backblaze.com/b2/cloud-storage.html][B2 Cloud | |
| 8 | Storage]] is an inexpensive and reliable on-demand cloud storage and | |
| 9 | backup solution. | |
| 10 | ||
| 11 | The service starts at $5/TB/month ($0.005/GB/month) with a download rate | |
| 12 | of $0.01/GB/month. | |
| 13 | ||
| 14 | However, there are free tiers: | |
| 15 | ||
| 16 | - The first 10 GB of storage is free. | |
| 17 | - The first 1 GB of data downloaded each day is free. | |
| 18 | - Class A transactions are free. | |
| 19 | - The first 2500 Class B transactions each day are free. | |
| 20 | - The first 2500 Class C transactions each day are free. | |
| 21 | ||
| 22 | You can see which API calls fall into categories A, B, or C here: | |
| 23 | [[https://www.backblaze.com/b2/b2-transactions-price.html][Pricing | |
| 24 | Organized by API Calls]]. | |
| 25 | ||
| 26 | For someone like me, who wants an offsite backup of their server's | |
| 27 | =/home/= directory and various other server configs that fall under 10 | |
| 28 | GB total, Backblaze is a great solution from a financial perspective. | |
| 29 | ||
| 30 | * Create An Account | |
| 31 | To start with Backblaze, you'll need to | |
| 32 | [[https://www.backblaze.com/b2/sign-up.html][create a free account]] - | |
| 33 | no payment method is required to sign up. | |
| 34 | ||
| 35 | Once you have an account, you can test out the service with their web | |
| 36 | GUI, their mobile app, or their CLI tool. I'm going to use the CLI tool | |
| 37 | below to test a file upload and then sync an entire directory to my | |
| 38 | Backblaze bucket. | |
| 39 | ||
| 40 | * Create a Bucket | |
| 41 | Before you can start uploading, you need to create a bucket. If you're | |
| 42 | familiar with other object storage services, this will feel familiar. If | |
| 43 | not, it's pretty simple to create one. | |
| 44 | ||
| 45 | As their webpage says: | |
| 46 | ||
| 47 | #+begin_quote | |
| 48 | A bucket is a container that holds files that are uploaded into B2 Cloud | |
| 49 | Storage. The bucket name must be globally unique and must have a minimum | |
| 50 | of 6 characters. A limit of 100 buckets may be created per account. An | |
| 51 | unlimited number of files may be uploaded into a bucket. | |
| 52 | ||
| 53 | #+end_quote | |
| 54 | ||
| 55 | Once you click the =Create a Bucket= button on their webpage or mobile | |
| 56 | app, you need to provide the following: | |
| 57 | ||
| 58 | - Bucket Unique Name | |
| 59 | - Files in Bucket are: =Private= or =Public= | |
| 60 | - Default Encryption: =Disable= or =Enable= | |
| 61 | - Object Lock: =Disable= or =Enable= | |
| 62 | ||
| 63 | For my bucket, I created a private bucket with encryption enabled and | |
| 64 | object lock disabled. | |
| 65 | ||
| 66 | Once your bucket is created, you can test the upload/download feature on | |
| 67 | their web GUI or mobile app! At this point, you have a fully functional | |
| 68 | bucket and account. | |
| 69 | ||
| 70 | * Linux CLI Tool | |
| 71 | ** Installation | |
| 72 | To install the =b2= CLI tool, you'll need to download it from the | |
| 73 | [[https://www.backblaze.com/docs/cloud-storage-command-line-tools][CLI | |
| 74 | Tools]] page. I recommend copying the URL from the link that says | |
| 75 | =Linux= and using wget to download it, as shown below. | |
| 76 | ||
| 77 | Once downloaded, make the file executable and move it to a location on | |
| 78 | your =$PATH=, so that you can execute that command from anywhere on the | |
| 79 | machine. | |
| 80 | ||
| 81 | #+begin_src sh | |
| 82 | wget <b2_cli_url> | |
| 83 | chmod +x b2_linux | |
| 84 | mv b2_linux /usr/bin/b2 | |
| 85 | #+end_src | |
| 86 | ||
| 87 | ** Log In | |
| 88 | The first step after installation is to log in. To do this, execute the | |
| 89 | following command and provide your =<applicationKeyId>= and | |
| 90 | =<applicationKey>=. | |
| 91 | ||
| 92 | If you don't want to provide these values in the command itself, you can | |
| 93 | simply execute the base command and it will request them in an | |
| 94 | interactive prompt. | |
| 95 | ||
| 96 | #+begin_src sh | |
| 97 | # if you want to provide the keys directly: | |
| 98 | b2 authorize-account [<applicationKeyId>] [<applicationKey>] | |
| 99 | ||
| 100 | # or, if you don't want your keys in your shell history: | |
| 101 | b2 authorize-account | |
| 102 | #+end_src | |
| 103 | ||
| 104 | ** Upload a Test File | |
| 105 | In order to test the functionality of the CLI tool, I'll start by | |
| 106 | uploading a single test file to the bucket I created above. We can do | |
| 107 | this with the =upload_file= function. | |
| 108 | ||
| 109 | The command is issued as follows: | |
| 110 | ||
| 111 | #+begin_src sh | |
| 112 | b2 upload_file <bucket_name> <local_file> <remote_file> | |
| 113 | #+end_src | |
| 114 | ||
| 115 | In my situation, I executed the following command with my username. | |
| 116 | ||
| 117 | #+begin_src sh | |
| 118 | b2 upload_file my_unique_bucket /home/<user>/test.md test.md | |
| 119 | #+end_src | |
| 120 | ||
| 121 | To confirm that the file was uploaded successfully, list the files in | |
| 122 | your bucket: | |
| 123 | ||
| 124 | #+begin_src sh | |
| 125 | b2 ls <bucket_name> | |
| 126 | #+end_src | |
| 127 | ||
| 128 | #+begin_src txt | |
| 129 | test.md | |
| 130 | #+end_src | |
| 131 | ||
| 132 | ** Sync a Directory | |
| 133 | If you have numerous files, you can use the =sync= function to perform | |
| 134 | functionality similar to =rsync=, where you can check what's in your | |
| 135 | bucket and sync anything that is new or modified. | |
| 136 | ||
| 137 | The command is issued as follows: | |
| 138 | ||
| 139 | #+begin_src sh | |
| 140 | b2 sync <source file location> <B2 bucket destination> | |
| 141 | #+end_src | |
| 142 | ||
| 143 | In my case, I can sync my user's entire home directory to my bucket | |
| 144 | without specifying any of the files directly: | |
| 145 | ||
| 146 | #+begin_src sh | |
| 147 | b2 sync /home/<user>/ "b2://<bucketName>/home/<user>" | |
| 148 | #+end_src | |
| 149 | ||
| 150 | * Caveats | |
| 151 | ** Timing of Updates to the Web GUI | |
| 152 | When performing actions over a bucket, there is a slight delay in the | |
| 153 | web GUI when inspecting a bucket or its file. Note that simple actions | |
| 154 | such as uploading or deleting files may have a delay of a few minutes up | |
| 155 | to 24 hours. In my experience (<10 GB and ~20,000 files), any actions | |
| 156 | took only a few minutes to update across clients. | |
| 157 | ||
| 158 | ** Symlinks | |
| 159 | Note that symlinks are resolved by b2, so if you have a link from | |
| 160 | =/home/<user>/nas-storage= that symlinks out to a =/mnt/nas-storage= | |
| 161 | folder that has 10TB of data, =b2= will resolve that link and start | |
| 162 | uploading all 10TB of data linked within the folder. | |
| 163 | ||
| 164 | If you're not sure if you have any symlinks, a symlink will look like | |
| 165 | this (note the =->= symbol): | |
| 166 | ||
| 167 | #+begin_src sh | |
| 168 | > ls -lha | |
| 169 | lrwxrwxrwx 1 root root 20 Jun 28 13:32 nas -> /mnt/nas-storage/ | |
| 170 | #+end_src | |
| 171 | ||
| 172 | You can recursively find symlink in a path with the following command: | |
| 173 | ||
| 174 | #+begin_src sh | |
| 175 | ls -lR /path/to/search | grep '^l' | |
| 176 | #+end_src | |
content/blog/2022-07-31-bash-it.md → blog/bash-it/index.org renamed +98 −107
| @@ -1,117 +1,113 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-07-31 | |
| 3 | title = "Upgrade Bash with Bash-It & Ble.sh" | |
| 4 | description = "Learn how to increase the power of bash with Bash-It and Ble.sh." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Bash | |
| 1 | #+title: Upgrade Bash with Bash-It & Ble.sh | |
| 2 | #+date: 2022-07-31 | |
| 3 | #+description: Learn how to increase the power of bash with Bash-It and Ble.sh. | |
| 4 | #+filetags: :sysadmin: | |
| 8 | 5 | |
| 6 | * Bash | |
| 9 | 7 | For those who are not familiar, |
| 10 | [Bash](https://en.wikipedia.org/wiki/Bash_(Unix_shell)) is a Unix shell | |
| 11 | that is used as the default login shell for most Linux distributions. | |
| 12 | This shell and command processor should be familiar if you've used | |
| 13 | Linux (or older version of macOS) before. | |
| 8 | [[https://en.wikipedia.org/wiki/Bash_(Unix_shell)][Bash]] is a Unix | |
| 9 | shell that is used as the default login shell for most Linux | |
| 10 | distributions. This shell and command processor should be familiar if | |
| 11 | you've used Linux (or older version of macOS) before. | |
| 14 | 12 | |
| 15 | 13 | However, bash is not the only option. There are numerous other shells |
| 16 | 14 | that exist. Here are some popular examples: |
| 17 | 15 | |
| 18 | - [zsh](https://en.wikipedia.org/wiki/Z_shell) | |
| 19 | - [fish](https://en.wikipedia.org/wiki/Fish_(Unix_shell)) | |
| 20 | - [oksh](https://github.com/ibara/oksh) | |
| 21 | - [mksh](https://wiki.gentoo.org/wiki/Mksh) | |
| 22 | - [dash](https://en.wikipedia.org/wiki/Debian_Almquist_shell) | |
| 16 | - [[https://en.wikipedia.org/wiki/Z_shell][zsh]] | |
| 17 | - [[https://en.wikipedia.org/wiki/Fish_(Unix_shell)][fish]] | |
| 18 | - [[https://github.com/ibara/oksh][oksh]] | |
| 19 | - [[https://wiki.gentoo.org/wiki/Mksh][mksh]] | |
| 20 | - [[https://en.wikipedia.org/wiki/Debian_Almquist_shell][dash]] | |
| 23 | 21 | |
| 24 | 22 | While each shell has its differences, bash is POSIX compliant and the |
| 25 | 23 | default for many Linux users. Because of this, I am going to explore a |
| 26 | program called `bash-it` below that helps bash users increase | |
| 27 | the utility of their shell without installing a completely new shell. | |
| 28 | ||
| 29 | ### Installation | |
| 24 | program called =bash-it= below that helps bash users increase the | |
| 25 | utility of their shell without installing a completely new shell. | |
| 30 | 26 | |
| 27 | ** Installation | |
| 31 | 28 | First, if bash is not already installed on your system, you can |
| 32 | [download bash from GNU](https://www.gnu.org/software/bash/) or use your | |
| 33 | package manager to install it. | |
| 29 | [[https://www.gnu.org/software/bash/][download bash from GNU]] or use | |
| 30 | your package manager to install it. | |
| 34 | 31 | |
| 35 | 32 | For example, this is how you can install bash on Fedora Linux: |
| 36 | 33 | |
| 37 | ```sh | |
| 34 | #+begin_src sh | |
| 38 | 35 | sudo dnf install bash |
| 39 | ``` | |
| 36 | #+end_src | |
| 40 | 37 | |
| 41 | If you are not using bash as your default shell, use the | |
| 42 | `chsh` command to change your shell: | |
| 38 | If you are not using bash as your default shell, use the =chsh= command | |
| 39 | to change your shell: | |
| 43 | 40 | |
| 44 | ```sh | |
| 41 | #+begin_src sh | |
| 45 | 42 | chsh |
| 46 | ``` | |
| 43 | #+end_src | |
| 47 | 44 | |
| 48 | You should see a prompt like the one below. If the brackets | |
| 49 | (`[]`) contain `bash` already, you're done, and | |
| 50 | you can simply continue by hitting the Enter key. | |
| 45 | You should see a prompt like the one below. If the brackets (=[]=) | |
| 46 | contain =bash= already, you're done, and you can simply continue by | |
| 47 | hitting the Enter key. | |
| 51 | 48 | |
| 52 | If the brackets contain another shell path (e.g. =/usr/bin/zsh=), enter | |
| 53 | the path to the bash program on your system (it's most likely located | |
| 54 | at `/usr/bin/bash`). | |
| 49 | If the brackets contain another shell path (e.g. =/usr/bin/zsh=), enter | |
| 50 | the path to the bash program on your system (it's most likely located at | |
| 51 | =/usr/bin/bash=). | |
| 55 | 52 | |
| 56 | ```sh | |
| 53 | #+begin_src sh | |
| 57 | 54 | Changing shell for <user>. |
| 58 | 55 | New shell [/usr/bin/bash]: |
| 59 | ``` | |
| 56 | #+end_src | |
| 60 | 57 | |
| 61 | 58 | You must log out or restart the machine in order for the login shell to |
| 62 | 59 | be refreshed. You can do it now or wait until you're finished |
| 63 | 60 | customizing the shell. |
| 64 | 61 | |
| 65 | ```sh | |
| 62 | #+begin_src sh | |
| 66 | 63 | sudo reboot now |
| 67 | ``` | |
| 68 | ||
| 69 | ## Bash-it | |
| 64 | #+end_src | |
| 70 | 65 | |
| 71 | As noted on the [Bash-it](https://github.com/Bash-it/bash-it) | |
| 66 | * Bash-it | |
| 67 | As noted on the [[https://github.com/Bash-it/bash-it][Bash-it]] | |
| 72 | 68 | repository: |
| 73 | 69 | |
| 74 | > Bash-it is a collection of community Bash commands and scripts for | |
| 75 | > Bash 3.2+. (And a shameless ripoff of oh-my-zsh 😃) | |
| 70 | #+begin_quote | |
| 71 | Bash-it is a collection of community Bash commands and scripts for Bash | |
| 72 | 3.2+. (And a shameless ripoff of oh-my-zsh 😃) | |
| 73 | ||
| 74 | #+end_quote | |
| 76 | 75 | |
| 77 | 76 | Bash-it makes it easy to install plugins, set up aliases for common |
| 78 | 77 | commands, and easily change the visual theme of your shell. |
| 79 | 78 | |
| 80 | ### Installation | |
| 81 | ||
| 79 | ** Installation | |
| 82 | 80 | To install the framework, simply copy the repository files and use the |
| 83 | `install.sh` script provided. If you want, you can (and | |
| 84 | should!) inspect the contents of the installation script before you run | |
| 85 | it. | |
| 81 | =install.sh= script provided. If you want, you can (and should!) inspect | |
| 82 | the contents of the installation script before you run it. | |
| 86 | 83 | |
| 87 | ```sh | |
| 84 | #+begin_src sh | |
| 88 | 85 | git clone --depth=1 https://github.com/Bash-it/bash-it.git ~/.bash_it |
| 89 | 86 | ~/.bash_it/install.sh |
| 90 | ``` | |
| 87 | #+end_src | |
| 91 | 88 | |
| 92 | 89 | If you didn't restart your session after making bash the default, and |
| 93 | 90 | are currently working within another shell, be sure to enter a bash |
| 94 | session before using `bash-it`: | |
| 91 | session before using =bash-it=: | |
| 95 | 92 | |
| 96 | ```sh | |
| 93 | #+begin_src sh | |
| 97 | 94 | bash |
| 98 | ``` | |
| 99 | ||
| 100 | ### Aliases | |
| 95 | #+end_src | |
| 101 | 96 | |
| 97 | ** Aliases | |
| 102 | 98 | Bash-it contains a number of aliases for common commands to help improve |
| 103 | 99 | efficiency in the terminal. To list all available options, use the |
| 104 | 100 | following command: |
| 105 | 101 | |
| 106 | ```sh | |
| 102 | #+begin_src sh | |
| 107 | 103 | bash-it show aliases |
| 108 | ``` | |
| 104 | #+end_src | |
| 109 | 105 | |
| 110 | 106 | This will provide you a list that looks like the following text block. |
| 111 | 107 | Within this screen, you will be able to see all available options and |
| 112 | 108 | which ones are currently enabled. |
| 113 | 109 | |
| 114 | ```txt | |
| 110 | #+begin_src txt | |
| 115 | 111 | Alias Enabled? Description |
| 116 | 112 | ag [ ] the silver searcher (ag) aliases |
| 117 | 113 | ansible [ ] ansible abbreviations |
| @@ -124,33 +120,32 @@ clipboard [ ] xclip shortcuts | ||
| 124 | 120 | composer [ ] common composer abbreviations |
| 125 | 121 | curl [x] Curl aliases for convenience. |
| 126 | 122 | ... |
| 127 | ``` | |
| 123 | #+end_src | |
| 128 | 124 | |
| 129 | 125 | To enable an alias, do: |
| 130 | 126 | |
| 131 | ```sh | |
| 127 | #+begin_src sh | |
| 132 | 128 | bash-it enable alias <alias name> [alias name]... -or- $ bash-it enable alias all |
| 133 | ``` | |
| 129 | #+end_src | |
| 134 | 130 | |
| 135 | 131 | To disable an alias, do: |
| 136 | 132 | |
| 137 | ```sh | |
| 133 | #+begin_src sh | |
| 138 | 134 | bash-it disable alias <alias name> [alias name]... -or- $ bash-it disable alias all |
| 139 | ``` | |
| 140 | ||
| 141 | ### Plugins | |
| 135 | #+end_src | |
| 142 | 136 | |
| 137 | ** Plugins | |
| 143 | 138 | Similar to aliases, plugins are available with bash-it. You can find a |
| 144 | 139 | complete list of plugins in the same way as aliases. Simply execute the |
| 145 | 140 | following: |
| 146 | 141 | |
| 147 | ```sh | |
| 142 | #+begin_src sh | |
| 148 | 143 | bash-it show plugins |
| 149 | ``` | |
| 144 | #+end_src | |
| 150 | 145 | |
| 151 | 146 | You will see the following output showing enabled and disabled plugins: |
| 152 | 147 | |
| 153 | ```txt | |
| 148 | #+begin_src txt | |
| 154 | 149 | Plugin Enabled? Description |
| 155 | 150 | alias-completion [ ] |
| 156 | 151 | autojump [ ] Autojump configuration, see https://github.com/wting/autojump for more details |
| @@ -161,82 +156,78 @@ battery [x] display info about your battery charge level | ||
| 161 | 156 | blesh [ ] load ble.sh, the Bash line editor! |
| 162 | 157 | boot2docker [ ] Helpers to get Docker setup correctly for boot2docker |
| 163 | 158 | browser [ ] render commandline output in your browser |
| 164 | ``` | |
| 159 | #+end_src | |
| 165 | 160 | |
| 166 | 161 | To enable a plugin, do: |
| 167 | 162 | |
| 168 | ```sh | |
| 163 | #+begin_src sh | |
| 169 | 164 | bash-it enable plugin <plugin name> [plugin name]... -or- $ bash-it enable plugin all |
| 170 | ``` | |
| 165 | #+end_src | |
| 171 | 166 | |
| 172 | 167 | To disable a plugin, do: |
| 173 | 168 | |
| 174 | ```sh | |
| 169 | #+begin_src sh | |
| 175 | 170 | bash-it disable plugin <plugin name> [plugin name]... -or- $ bash-it disable plugin all |
| 176 | ``` | |
| 177 | ||
| 178 | ### Themes | |
| 171 | #+end_src | |
| 179 | 172 | |
| 173 | ** Themes | |
| 180 | 174 | There are quite a few pre-defined |
| 181 | [themes](https://bash-it.readthedocs.io/en/latest/themes-list/#list-of-themes) | |
| 175 | [[https://bash-it.readthedocs.io/en/latest/themes-list/#list-of-themes][themes]] | |
| 182 | 176 | available with bash-it. |
| 183 | 177 | |
| 184 | 178 | To list all themes: |
| 185 | 179 | |
| 186 | ```sh | |
| 180 | #+begin_src sh | |
| 187 | 181 | ls ~/.bash_it/themes/ |
| 188 | ``` | |
| 182 | #+end_src | |
| 189 | 183 | |
| 190 | To use a new theme, you'll need to edit `.bashrc` and alter | |
| 191 | the `BASH_IT_THEME` variable to your desired theme. For | |
| 192 | example, I am using the `zork` theme. | |
| 184 | To use a new theme, you'll need to edit =.bashrc= and alter the | |
| 185 | =BASH_IT_THEME= variable to your desired theme. For example, I am using | |
| 186 | the =zork= theme. | |
| 193 | 187 | |
| 194 | ```sh | |
| 188 | #+begin_src sh | |
| 195 | 189 | nano ~/.bashrc |
| 196 | ``` | |
| 190 | #+end_src | |
| 197 | 191 | |
| 198 | ```sh | |
| 192 | #+begin_src sh | |
| 199 | 193 | export BASH_IT_THEME='zork' |
| 200 | ``` | |
| 194 | #+end_src | |
| 201 | 195 | |
| 202 | 196 | Once you save your changes, you just need to exit your terminal and |
| 203 | create a new one in order to see your changes to the | |
| 204 | `.bashrc` file. You can also `source` the file to | |
| 205 | see changes, but I recommend starting a completely new shell instead. | |
| 206 | ||
| 207 | ## ble.sh | |
| 208 | ||
| 209 | One big feature I was missing in Bash that both `zsh` and | |
| 210 | `fish` have is an autosuggestion feature. To explain: as you | |
| 211 | type, an autosuggestion feature in the shell will offer suggestions in a | |
| 212 | lighter font color beyond the characters already typed. Once you see the | |
| 213 | command you want, you can click the right arrow and have the shell | |
| 214 | auto-complete that line for you. | |
| 215 | ||
| 216 | Luckily, the [Bash Line Editor](https://github.com/akinomyoga/ble.sh) | |
| 197 | create a new one in order to see your changes to the =.bashrc= file. You | |
| 198 | can also =source= the file to see changes, but I recommend starting a | |
| 199 | completely new shell instead. | |
| 200 | ||
| 201 | *** ble.sh | |
| 202 | One big feature I was missing in Bash that both =zsh= and =fish= have is | |
| 203 | an autosuggestion feature. To explain: as you type, an autosuggestion | |
| 204 | feature in the shell will offer suggestions in a lighter font color | |
| 205 | beyond the characters already typed. Once you see the command you want, | |
| 206 | you can click the right arrow and have the shell auto-complete that line | |
| 207 | for you. | |
| 208 | ||
| 209 | Luckily, the [[https://github.com/akinomyoga/ble.sh][Bash Line Editor]] | |
| 217 | 210 | (ble.sh) exists! This program provides a wonderful autosuggestions |
| 218 | 211 | feature perfectly, among other features that I haven't tested yet. |
| 219 | 212 | |
| 220 | 213 | In order to install ble.sh, execute the following: |
| 221 | 214 | |
| 222 | ```sh | |
| 215 | #+begin_src sh | |
| 223 | 216 | git clone --recursive https://github.com/akinomyoga/ble.sh.git |
| 224 | 217 | make -C ble.sh install PREFIX=~/.local |
| 225 | 218 | echo 'source ~/.local/share/blesh/ble.sh' >> ~/.bashrc |
| 226 | ``` | |
| 219 | #+end_src | |
| 227 | 220 | |
| 228 | 221 | Again, exit the terminal and open a new one in order to see the |
| 229 | 222 | newly-configured shell. |
| 230 | 223 | |
| 231 | ## Restart the Session | |
| 232 | ||
| 224 | * Restart the Session | |
| 233 | 225 | Finally, as mentioned above, you'll need to restart the session to |
| 234 | 226 | ensure that your user is using bash by default. |
| 235 | 227 | |
| 236 | 228 | You will also need to exit and re-open a shell (e.g., terminal or |
| 237 | terminal tab) any time you make changes to the `.bashrc` | |
| 238 | file. | |
| 229 | terminal tab) any time you make changes to the =.bashrc= file. | |
| 239 | 230 | |
| 240 | ```sh | |
| 231 | #+begin_src sh | |
| 241 | 232 | sudo reboot now |
| 242 | ``` | |
| 233 | #+end_src | |
content/blog/2023-05-22-burnout.md → blog/burnout/index.org renamed +18 −21
| @@ -1,19 +1,17 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-05-22 | |
| 3 | title = "RE: Burnout" | |
| 4 | description = "A response to Drew DeVault's burnout post." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## RE: Burnout | |
| 8 | ||
| 9 | I recently read [Drew DeVault's post on | |
| 10 | burnout](https://drewdevault.com/2023/05/01/2023-05-01-Burnout.html) | |
| 11 | around the same time I was pulling out of a burnout rut myself earlier | |
| 12 | this month. Finally, seeing the light at the end of my burnout tunnel | |
| 13 | made me want to write my first post back on this topic. | |
| 14 | ||
| 15 | ## Busy Seasons on Busy Seasons | |
| 16 | ||
| 1 | #+title: RE: Burnout | |
| 2 | #+date: 2023-05-22 | |
| 3 | #+description: A response to Drew DeVault's burnout post. | |
| 4 | #+filetags: :personal: | |
| 5 | ||
| 6 | * RE: Burnout | |
| 7 | I recently read | |
| 8 | [[https://drewdevault.com/2023/05/01/2023-05-01-Burnout.html][Drew | |
| 9 | DeVault's post on burnout]] around the same time I was pulling out of a | |
| 10 | burnout rut myself earlier this month. Finally, seeing the light at the | |
| 11 | end of my burnout tunnel made me want to write my first post back on | |
| 12 | this topic. | |
| 13 | ||
| 14 | * Busy Seasons on Busy Seasons | |
| 17 | 15 | My career deals with busy seasons, generally driven by client demand. |
| 18 | 16 | This last year, I dealt with a harsh busy season from Aug to Oct 2022 to |
| 19 | 17 | issue a few SOC reports for the period ending 2022-09-30. Immediately |
| @@ -28,12 +26,11 @@ I have a brief break and need to focus on the 2023-09-30 SOC reports | ||
| 28 | 26 | again. While auditing and consulting always involve a busy season, this |
| 29 | 27 | is the first time I've had one last 9+ months without a break. |
| 30 | 28 | |
| 31 | While it's been tough, I have a handful of breaks pre-planned | |
| 32 | throughout this next cycle and should be able to moderate the level of | |
| 33 | commitment required for each client. | |
| 34 | ||
| 35 | ## Refocusing | |
| 29 | While it's been tough, I have a handful of breaks pre-planned throughout | |
| 30 | this next cycle and should be able to moderate the level of commitment | |
| 31 | required for each client. | |
| 36 | 32 | |
| 33 | * Refocusing | |
| 37 | 34 | Outside of work, I finally have time to work on hobbies such as this |
| 38 | 35 | website, programming, athletics, games, etc. |
| 39 | 36 | |
content/blog/2020-07-26-business-analysis.md → blog/business-analysis/index.org renamed +57 −66
| @@ -1,31 +1,28 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-07-26 | |
| 3 | title = "Algorithmically Analyzing Local Businesses" | |
| 4 | description = "Exploring and visualizing data with Python." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Background Information | |
| 1 | #+title: Algorithmically Analyzing Local Businesses | |
| 2 | #+date: 2020-07-26 | |
| 3 | #+description: Exploring and visualizing data with Python. | |
| 4 | #+filetags: :data: | |
| 8 | 5 | |
| 6 | * Background Information | |
| 9 | 7 | This project aims to help investors learn more about a random city in |
| 10 | 8 | order to determine optimal locations for business investments. The data |
| 11 | 9 | used in this project was obtained using Foursquare's developer API. |
| 12 | 10 | |
| 13 | 11 | Fields include: |
| 14 | 12 | |
| 15 | - Venue Name | |
| 16 | - Venue Category | |
| 17 | - Venue Latitude | |
| 18 | - Venue Longitude | |
| 13 | - Venue Name | |
| 14 | - Venue Category | |
| 15 | - Venue Latitude | |
| 16 | - Venue Longitude | |
| 19 | 17 | |
| 20 | 18 | There are 232 records found using the center of Lincoln as the area of |
| 21 | 19 | interest with a radius of 10,000. |
| 22 | 20 | |
| 23 | # Import the Data | |
| 24 | ||
| 21 | * Import the Data | |
| 25 | 22 | The first step is the simplest: import the applicable libraries. We will |
| 26 | 23 | be using the libraries below for this project. |
| 27 | 24 | |
| 28 | ```python | |
| 25 | #+begin_src python | |
| 29 | 26 | # Import the Python libraries we will be using |
| 30 | 27 | import pandas as pd |
| 31 | 28 | import requests |
| @@ -34,24 +31,24 @@ import math | ||
| 34 | 31 | import json |
| 35 | 32 | from pandas.io.json import json_normalize |
| 36 | 33 | from sklearn.cluster import KMeans |
| 37 | ``` | |
| 34 | #+end_src | |
| 38 | 35 | |
| 39 | 36 | To begin our analysis, we need to import the data for this project. The |
| 40 | 37 | data we are using in this project comes directly from the Foursquare |
| 41 | 38 | API. The first step is to get the latitude and longitude of the city |
| 42 | 39 | being studied (Lincoln, NE) and setting up the folium map. |
| 43 | 40 | |
| 44 | ```python | |
| 41 | #+begin_src python | |
| 45 | 42 | # Define the latitude and longitude, then map the results |
| 46 | 43 | latitude = 40.806862 |
| 47 | 44 | longitude = -96.681679 |
| 48 | 45 | map_LNK = folium.Map(location=[latitude, longitude], zoom_start=12) |
| 49 | 46 | |
| 50 | 47 | map_LNK |
| 51 | ``` | |
| 48 | #+end_src | |
| 52 | 49 | |
| 53 |  | |
| 50 | #+caption: Blank Map | |
| 51 | [[https://img.cleberg.net/blog/20200726-ibm-data-science/01_blank_map-min.png]] | |
| 55 | 52 | |
| 56 | 53 | Now that we have defined our city and created the map, we need to go get |
| 57 | 54 | the business data. The Foursquare API will limit the results to 100 per |
| @@ -59,7 +56,7 @@ API call, so we use our first API call below to determine the total | ||
| 59 | 56 | results that Foursquare has found. Since the total results are 232, we |
| 60 | 57 | perform the API fetching process three times (100 + 100 + 32 = 232). |
| 61 | 58 | |
| 62 | ```python | |
| 59 | #+begin_src python | |
| 63 | 60 | # Foursquare API credentials |
| 64 | 61 | CLIENT_ID = 'your-client-id' |
| 65 | 62 | CLIENT_SECRET = 'your-client-secret' |
| @@ -117,19 +114,18 @@ url3 = 'https://api.foursquare.com/v2/venues/explore?&client_id={}&client_secret | ||
| 117 | 114 | |
| 118 | 115 | # Fetch the final results (201 - 232) |
| 119 | 116 | results3 = requests.get(url3).json() |
| 120 | ``` | |
| 121 | ||
| 122 | # Clean the Data | |
| 117 | #+end_src | |
| 123 | 118 | |
| 119 | * Clean the Data | |
| 124 | 120 | Now that we have our data in three separate dataframes, we need to |
| 125 | 121 | combine them into a single dataframe and make sure to reset the index so |
| 126 | that we have a unique ID for each business. The `get~categorytype~` | |
| 122 | that we have a unique ID for each business. The =get~categorytype~= | |
| 127 | 123 | function below will pull the categories and name from each business's |
| 128 | 124 | entry in the Foursquare data automatically. Once all the data has been |
| 129 | labeled and combined, the results are stored in the | |
| 130 | `nearby_venues` dataframe. | |
| 125 | labeled and combined, the results are stored in the =nearby_venues= | |
| 126 | dataframe. | |
| 131 | 127 | |
| 132 | ```python | |
| 128 | #+begin_src python | |
| 133 | 129 | # This function will extract the category of the venue from the API dictionary |
| 134 | 130 | def get_category_type(row): |
| 135 | 131 | try: |
| @@ -192,18 +188,17 @@ nearby_venues3.columns = [col.split(".")[-1] for col in nearby_venues3.columns] | ||
| 192 | 188 | nearby_venues = nearby_venues.append(nearby_venues3) |
| 193 | 189 | nearby_venues = nearby_venues.reset_index(drop=True) |
| 194 | 190 | nearby_venues |
| 195 | ``` | |
| 196 | ||
| 197 |  | |
| 191 | #+end_src | |
| 199 | 192 | |
| 200 | # Visualize the Data | |
| 193 | #+caption: Clean Data | |
| 194 | [[https://img.cleberg.net/blog/20200726-ibm-data-science/02_clean_data-min.png]] | |
| 201 | 195 | |
| 196 | * Visualize the Data | |
| 202 | 197 | We now have a complete, clean data set. The next step is to visualize |
| 203 | 198 | this data onto the map we created earlier. We will be using folium's |
| 204 | `CircleMarker()` function to do this. | |
| 199 | =CircleMarker()= function to do this. | |
| 205 | 200 | |
| 206 | ```python | |
| 201 | #+begin_src python | |
| 207 | 202 | # add markers to map |
| 208 | 203 | for lat, lng, name, categories in zip(nearby_venues['lat'], nearby_venues['lng'], nearby_venues['name'], nearby_venues['categories']): |
| 209 | 204 | label = '{} ({})'.format(name, categories) |
| @@ -219,25 +214,23 @@ for lat, lng, name, categories in zip(nearby_venues['lat'], nearby_venues['lng'] | ||
| 219 | 214 | ).add_to(map_LNK) |
| 220 | 215 | |
| 221 | 216 | map_LNK |
| 222 | ``` | |
| 217 | #+end_src | |
| 223 | 218 | |
| 224 | \ | |
| 219 | ![[https://img.cleberg.net/blog/20200726-ibm-data-science/03_data_map-min.png][Initial | |
| 220 | data map]] | |
| 227 | 221 | |
| 228 | # Clustering: *k-means* | |
| 229 | ||
| 230 | To cluster the data, we will be using the *k-means* algorithm. This | |
| 222 | * Clustering: /k-means/ | |
| 223 | To cluster the data, we will be using the /k-means/ algorithm. This | |
| 231 | 224 | algorithm is iterative and will automatically make sure that data points |
| 232 | 225 | in each cluster are as close as possible to each other, while being as |
| 233 | 226 | far as possible away from other clusters. |
| 234 | 227 | |
| 235 | 228 | However, we first have to figure out how many clusters to use (defined |
| 236 | as the variable *'k'*). To do so, we will use the next two functions | |
| 237 | to calculate the sum of squares within clusters and then return the | |
| 238 | optimal number of clusters. | |
| 229 | as the variable /'k'/). To do so, we will use the next two functions to | |
| 230 | calculate the sum of squares within clusters and then return the optimal | |
| 231 | number of clusters. | |
| 239 | 232 | |
| 240 | ```python | |
| 233 | #+begin_src python | |
| 241 | 234 | # This function will return the sum of squares found in the data |
| 242 | 235 | def calculate_wcss(data): |
| 243 | 236 | wcss = [] |
| @@ -271,13 +264,13 @@ def optimal_number_of_clusters(wcss): | ||
| 271 | 264 | |
| 272 | 265 | # calculating the optimal number of clusters |
| 273 | 266 | n = optimal_number_of_clusters(sum_of_squares) |
| 274 | ``` | |
| 267 | #+end_src | |
| 275 | 268 | |
| 276 | 269 | Now that we have found that our optimal number of clusters is six, we |
| 277 | 270 | need to perform k-means clustering. When this clustering occurs, each |
| 278 | 271 | business is assigned a cluster number from 0 to 5 in the dataframe. |
| 279 | 272 | |
| 280 | ```python | |
| 273 | #+begin_src python | |
| 281 | 274 | # set number of clusters equal to the optimal number |
| 282 | 275 | kclusters = n |
| 283 | 276 | |
| @@ -286,13 +279,13 @@ kmeans = KMeans(n_clusters=kclusters, random_state=0).fit(cluster_df) | ||
| 286 | 279 | |
| 287 | 280 | # add clustering labels to dataframe |
| 288 | 281 | nearby_venues.insert(0, 'Cluster Labels', kmeans.labels_) |
| 289 | ``` | |
| 282 | #+end_src | |
| 290 | 283 | |
| 291 | 284 | Success! We now have a dataframe with clean business data, along with a |
| 292 | 285 | cluster number for each business. Now let's map the data using six |
| 293 | 286 | different colors. |
| 294 | 287 | |
| 295 | ```python | |
| 288 | #+begin_src python | |
| 296 | 289 | # create map with clusters |
| 297 | 290 | map_clusters = folium.Map(location=[latitude, longitude], zoom_start=12) |
| 298 | 291 | colors = ['#0F9D58', '#DB4437', '#4285F4', '#800080', '#ce12c0', '#171717'] |
| @@ -311,13 +304,12 @@ for lat, lng, name, categories, cluster in zip(nearby_venues['lat'], nearby_venu | ||
| 311 | 304 | fill_opacity=0.7).add_to(map_clusters) |
| 312 | 305 | |
| 313 | 306 | map_clusters |
| 314 | ``` | |
| 315 | ||
| 316 |  | |
| 307 | #+end_src | |
| 318 | 308 | |
| 319 | # Investigate Clusters | |
| 309 | #+caption: Clustered Map | |
| 310 | [[https://img.cleberg.net/blog/20200726-ibm-data-science/04_clusters-min.png]] | |
| 320 | 311 | |
| 312 | * Investigate Clusters | |
| 321 | 313 | Now that we have figured out our clusters, let's do a little more |
| 322 | 314 | analysis to provide more insight into the clusters. With the information |
| 323 | 315 | below, we can see which clusters are more popular for businesses and |
| @@ -325,23 +317,23 @@ which are less popular. The results below show us that clusters 0 | ||
| 325 | 317 | through 3 are popular, while clusters 4 and 5 are not very popular at |
| 326 | 318 | all. |
| 327 | 319 | |
| 328 | ```python | |
| 320 | #+begin_src python | |
| 329 | 321 | # Show how many venues are in each cluster |
| 330 | 322 | color_names = ['Dark Green', 'Red', 'Blue', 'Purple', 'Pink', 'Black'] |
| 331 | 323 | for x in range(0,6): |
| 332 | 324 | print("Color of Cluster", x, ":", color_names[x]) |
| 333 | 325 | print("Venues found in Cluster", x, ":", nearby_venues.loc[nearby_venues['Cluster Labels'] == x, nearby_venues.columns[:]].shape[0]) |
| 334 | 326 | print("---") |
| 335 | ``` | |
| 327 | #+end_src | |
| 336 | 328 | |
| 337 |  | |
| 329 | #+caption: Venues per Cluster | |
| 330 | [[https://img.cleberg.net/blog/20200726-ibm-data-science/05_venues_per_cluster-min.png]] | |
| 339 | 331 | |
| 340 | 332 | Our last piece of analysis is to summarize the categories of businesses |
| 341 | 333 | within each cluster. With these results, we can clearly see that |
| 342 | 334 | restaurants, coffee shops, and grocery stores are the most popular. |
| 343 | 335 | |
| 344 | ```python | |
| 336 | #+begin_src python | |
| 345 | 337 | # Calculate how many venues there are in each category |
| 346 | 338 | # Sort from largest to smallest |
| 347 | 339 | temp_df = nearby_venues.drop(columns=['name', 'lat', 'lng']) |
| @@ -361,16 +353,15 @@ with pd.option_context('display.max_rows', None, 'display.max_columns', None): | ||
| 361 | 353 | print("\n\n", "Cluster 3:", "\n", cluster3_grouped.loc[cluster3_grouped['Cluster Labels'] > 1]) |
| 362 | 354 | print("\n\n", "Cluster 4:", "\n", cluster4_grouped.loc[cluster4_grouped['Cluster Labels'] > 1]) |
| 363 | 355 | print("\n\n", "Cluster 5:", "\n", cluster5_grouped.loc[cluster5_grouped['Cluster Labels'] > 1]) |
| 364 | ``` | |
| 365 | ||
| 366 |  | |
| 356 | #+end_src | |
| 368 | 357 | |
| 369 |  | |
| 358 | #+caption: Venues per Cluster, pt. 1 | |
| 359 | [[https://img.cleberg.net/blog/20200726-ibm-data-science/06_categories_per_cluster_pt1-min.png]] | |
| 371 | 360 | |
| 372 | # Discussion | |
| 361 | #+caption: Venues per Cluster, pt. 2 | |
| 362 | [[https://img.cleberg.net/blog/20200726-ibm-data-science/07_categories_per_cluster_pt2-min.png]] | |
| 373 | 363 | |
| 364 | * Discussion | |
| 374 | 365 | In this project, we gathered location data for Lincoln, Nebraska, USA |
| 375 | 366 | and clustered the data using the k-means algorithm in order to identify |
| 376 | 367 | the unique clusters of businesses in Lincoln. Through these actions, we |
content/blog/2023-06-23-byobu.md → blog/byobu/index.org renamed +17 −20
| @@ -1,36 +1,33 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-06-23 | |
| 3 | title = "Byobu" | |
| 4 | description = "Learning about the Byobu application for terminals." | |
| 5 | +++ | |
| 1 | #+title: Byobu | |
| 2 | #+date: 2023-06-23 | |
| 3 | #+description: Learning about the Byobu application for terminals. | |
| 4 | #+filetags: :linux: | |
| 6 | 5 | |
| 7 | ## Byobu | |
| 8 | ||
| 9 | [byobu](https://www.byobu.org) is a command-line tool that allows you to | |
| 10 | use numerous screens within a single terminal emulator instance. More | |
| 11 | specifically, it's a text based window manager, using either | |
| 12 | `screen` or `tmux`. | |
| 6 | * Byobu | |
| 7 | [[https://www.byobu.org][byobu]] is a command-line tool that allows you | |
| 8 | to use numerous screens within a single terminal emulator instance. More | |
| 9 | specifically, it's a text based window manager, using either =screen= or | |
| 10 | =tmux=. | |
| 13 | 11 | |
| 14 | 12 | This post is mostly just a self-reference as I explore byobu, so I may |
| 15 | 13 | come back later and update this post with more content. |
| 16 | 14 | |
| 17 | ### Screenshot | |
| 18 | ||
| 15 | ** Screenshot | |
| 19 | 16 | Take a look below at my current multi-window set-up in byobu while I |
| 20 | 17 | write this blog post: |
| 21 | 18 | |
| 22 | 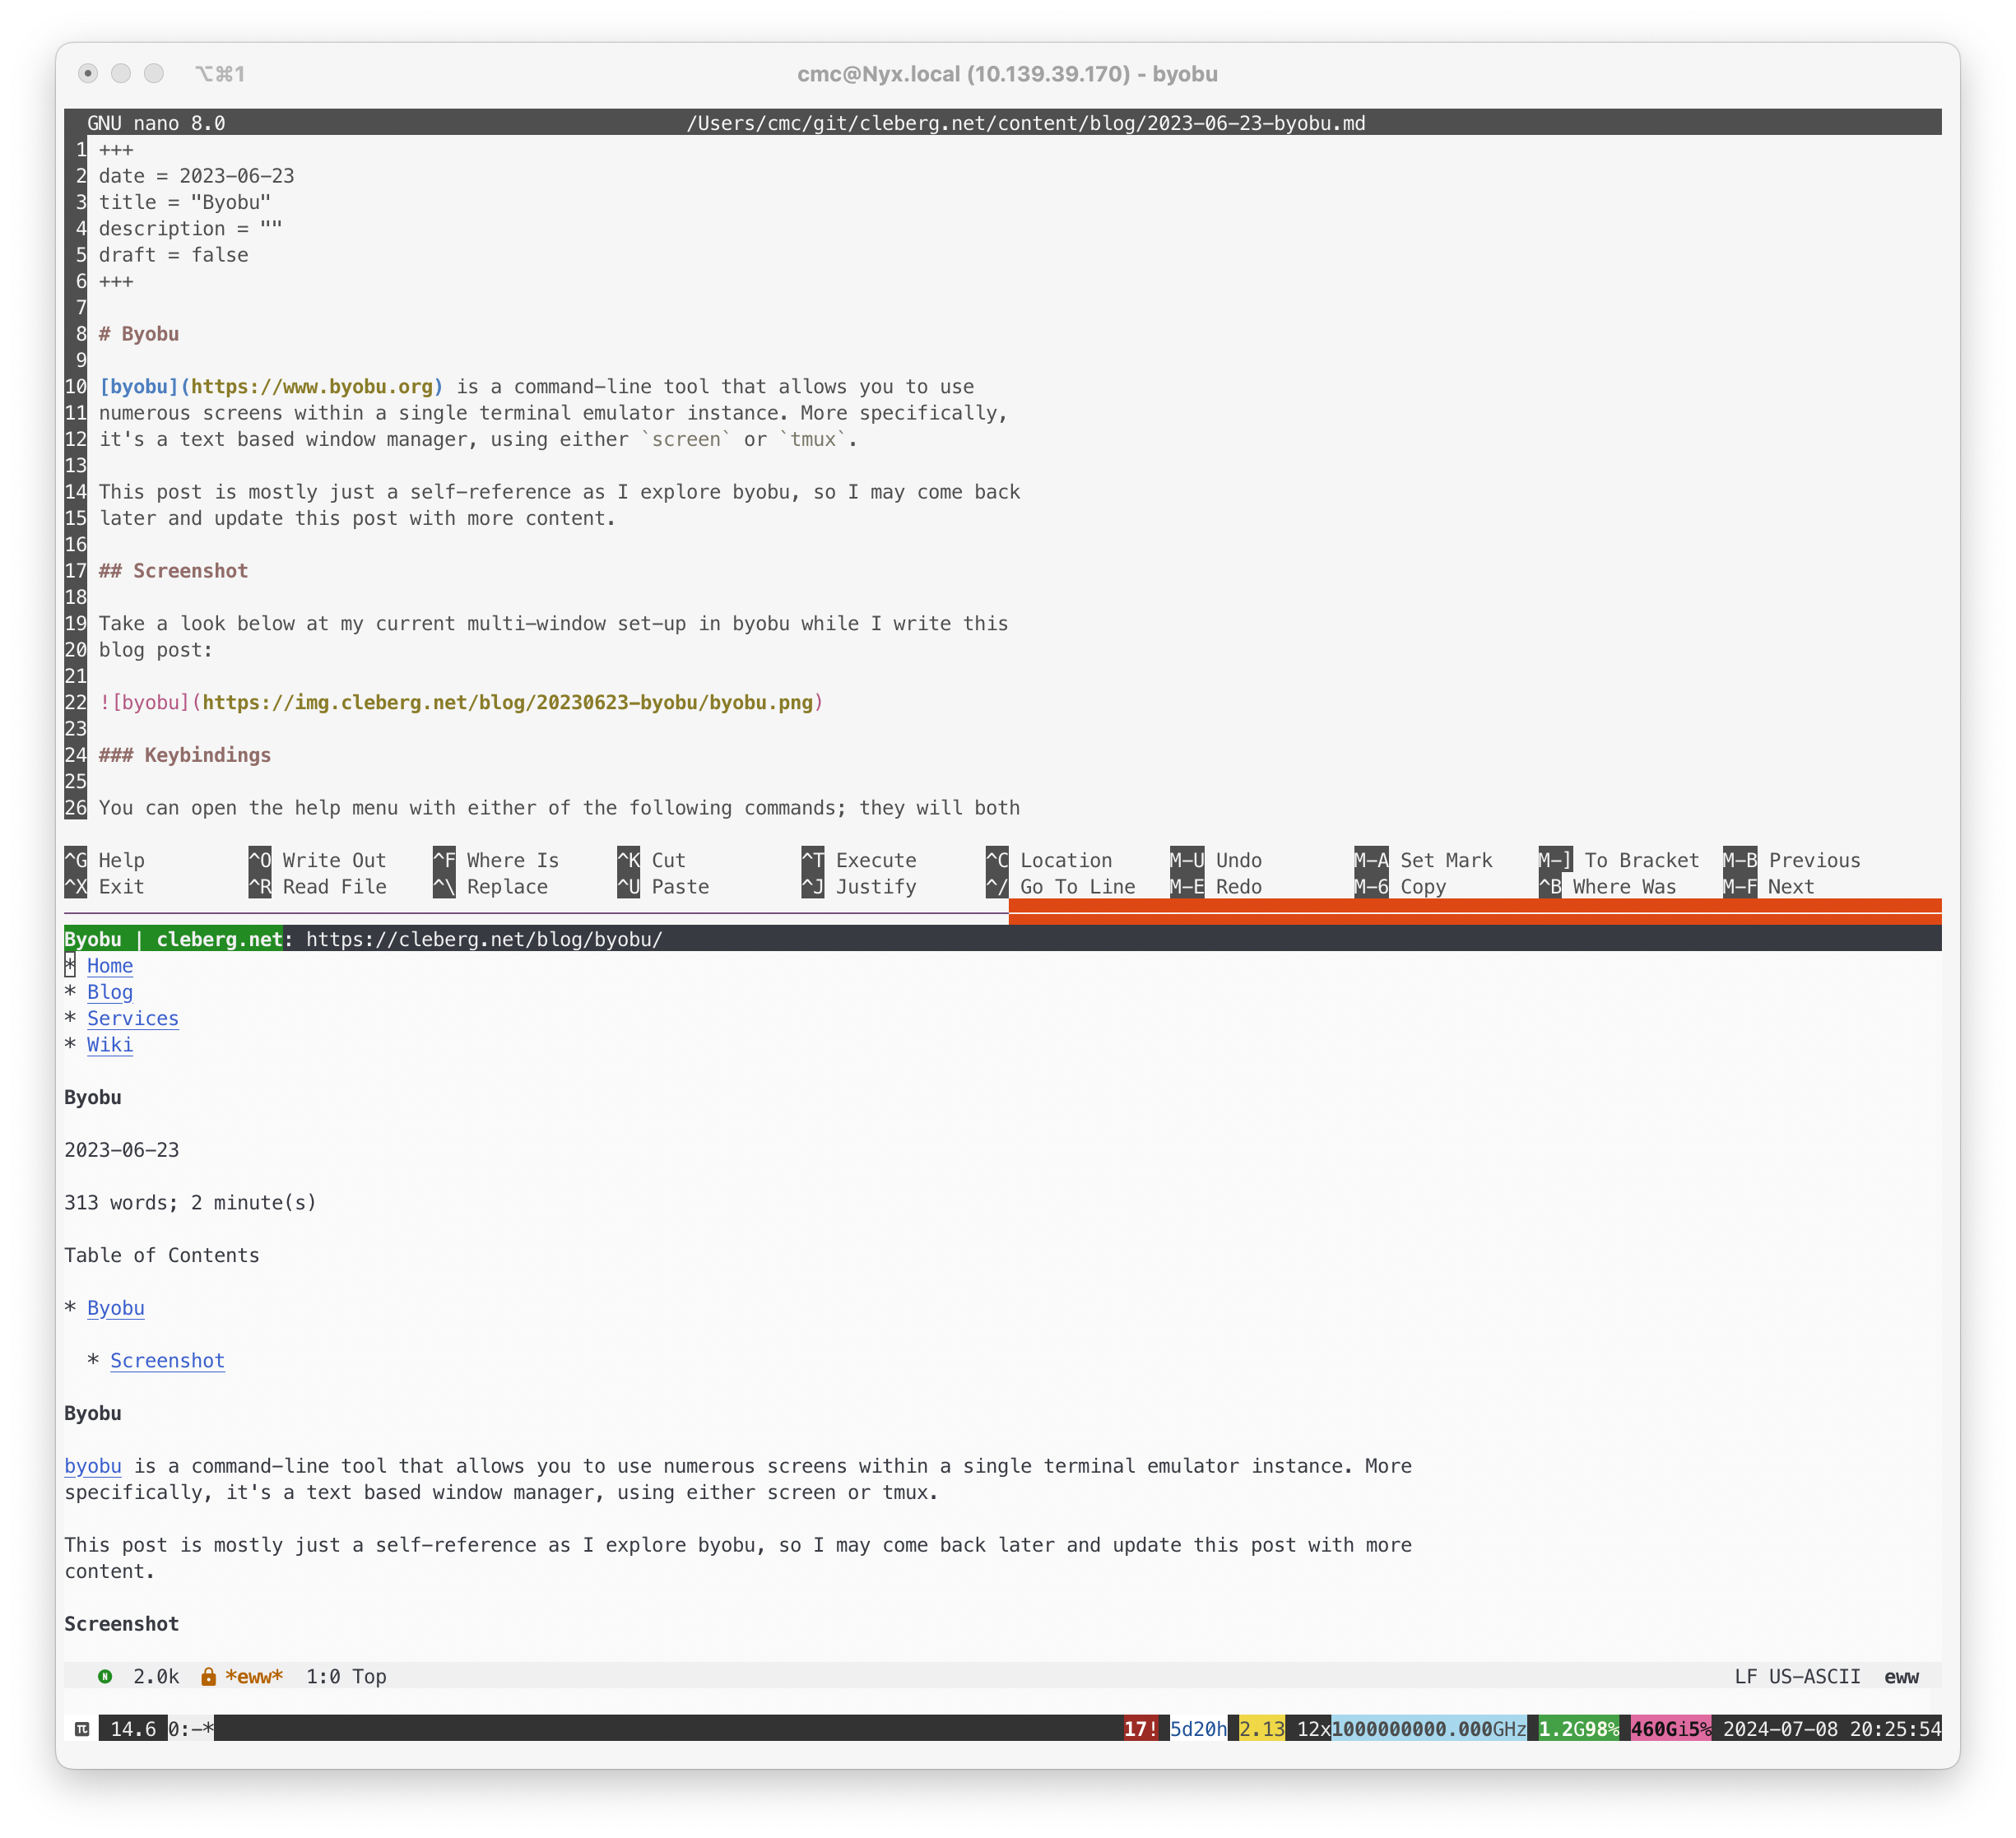 | |
| 23 | ||
| 24 | ## Keybindings | |
| 19 | #+caption: byobu | |
| 20 | [[https://img.cleberg.net/blog/20230623-byobu/byobu.png]] | |
| 25 | 21 | |
| 22 | *** Keybindings | |
| 26 | 23 | You can open the help menu with either of the following commands; they |
| 27 | 24 | will both open the same manpage: |
| 28 | 25 | |
| 29 | ```sh | |
| 26 | #+begin_src sh | |
| 30 | 27 | byobu --help |
| 31 | 28 | # or |
| 32 | 29 | man byobu |
| 33 | ``` | |
| 30 | #+end_src | |
| 34 | 31 | |
| 35 | 32 | While the manpage contains a ton of information about the functionality |
| 36 | 33 | of byobu (such as status notifications, sessions, and windows), the |
| @@ -38,7 +35,7 @@ first location to explore should be the keybindings section. | ||
| 38 | 35 | |
| 39 | 36 | The keybindings are configured as follows: |
| 40 | 37 | |
| 41 | ```txt | |
| 38 | #+begin_src txt | |
| 42 | 39 | byobu keybindings can be user defined in /usr/share/byobu/keybindings/ (or |
| 43 | 40 | within .screenrc if byobu-export was used). The common key bindings are: |
| 44 | 41 | |
| @@ -66,4 +63,4 @@ Ctrl-a R - Reload profile | ||
| 66 | 63 | Ctrl-a ! - Toggle key bindings on and off |
| 67 | 64 | Ctrl-a k - Kill the current window |
| 68 | 65 | Ctrl-a ~ - Save the current window's scrollback buffer |
| 69 | ``` | |
| 66 | #+end_src | |
content/blog/2021-05-30-changing-git-authors.md → blog/changing-git-authors/index.org renamed +16 −18
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-05-30 | |
| 3 | title = "Changing Git Authors" | |
| 4 | description = "A guide to change Git author names and emails in old commits." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Changing Git Author/Email Based on Previously Committed Email | |
| 1 | #+title: Changing Git Authors | |
| 2 | #+date: 2021-05-30 | |
| 3 | #+description: A guide to change Git author names and emails in old commits. | |
| 4 | #+filetags: :dev: | |
| 8 | 5 | |
| 6 | * Changing Git Author/Email Based on Previously Committed Email | |
| 9 | 7 | Here's the dilemma: You've been committing changes to your git |
| 10 | 8 | repository with an incorrect name or email (or multiple repositories), |
| 11 | 9 | and now you want to fix it. Luckily, there's a semi-reliable way to fix |
| @@ -15,18 +13,18 @@ of commits, so use this method only if you're okay accepting that risk. | ||
| 15 | 13 | |
| 16 | 14 | Okay, let's create the bash script: |
| 17 | 15 | |
| 18 | ```sh | |
| 16 | #+begin_src sh | |
| 19 | 17 | nano change_git_authors.sh |
| 20 | ``` | |
| 18 | #+end_src | |
| 21 | 19 | |
| 22 | 20 | The following information can be pasted directly into your bash script. |
| 23 | 21 | The only changes you need to make are to the following variables: |
| 24 | 22 | |
| 25 | - `OLD_EMAIL` | |
| 26 | - `CORRECT_NAME` | |
| 27 | - `CORRECT_EMAIL` | |
| 23 | - =OLD_EMAIL= | |
| 24 | - =CORRECT_NAME= | |
| 25 | - =CORRECT_EMAIL= | |
| 28 | 26 | |
| 29 | ```sh | |
| 27 | #+begin_src sh | |
| 30 | 28 | #!/bin/sh |
| 31 | 29 | |
| 32 | 30 | # List all sub-directories in the current directory |
| @@ -59,16 +57,16 @@ do | ||
| 59 | 57 | |
| 60 | 58 | cd .. |
| 61 | 59 | done |
| 62 | ``` | |
| 60 | #+end_src | |
| 63 | 61 | |
| 64 | 62 | Finally, save the bash script and make it executable. |
| 65 | 63 | |
| 66 | ```sh | |
| 64 | #+begin_src sh | |
| 67 | 65 | chmod a+x change_git_authors.sh |
| 68 | ``` | |
| 66 | #+end_src | |
| 69 | 67 | |
| 70 | 68 | Now you can run the script and should see the process begin. |
| 71 | 69 | |
| 72 | ```sh | |
| 70 | #+begin_src sh | |
| 73 | 71 | ./change_git_authors.sh |
| 74 | ``` | |
| 72 | #+end_src | |
content/blog/2021-12-04-cisa.md → blog/cisa/index.org renamed +75 −84
| @@ -1,21 +1,18 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-12-04 | |
| 3 | title = "I Passed the CISA!" | |
| 4 | description = "A recap of the CISA certification exam and my results." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## What is the CISA? | |
| 1 | #+title: I Passed the CISA! | |
| 2 | #+date: 2021-12-04 | |
| 3 | #+description: A recap of the CISA certification exam and my results. | |
| 4 | #+filetags: :audit: | |
| 8 | 5 | |
| 6 | * What is the CISA? | |
| 9 | 7 | For those of you lucky enough not to be knee-deep in the world of IT/IS |
| 10 | Auditing, [CISA](https://www.isaca.org/credentialing/cisa) stands for | |
| 8 | Auditing, [[https://www.isaca.org/credentialing/cisa][CISA]] stands for | |
| 11 | 9 | Certified Information Systems Auditor. This certification and exam are |
| 12 | part of ISACA's suite of certifications. As I often explain it to | |
| 13 | people like my family, it basically means you're employed to use your | |
| 14 | knowledge of information systems, regulations, common threats, risks, | |
| 15 | etc. in order to assess an organization's current control of their | |
| 16 | risk. If a risk isn't controlled (and the company doesn't want to | |
| 17 | accept the risk), an IS auditor will suggest implementing a control to | |
| 18 | address that risk. | |
| 10 | part of ISACA's suite of certifications. As I often explain it to people | |
| 11 | like my family, it basically means you're employed to use your knowledge | |
| 12 | of information systems, regulations, common threats, risks, etc. in | |
| 13 | order to assess an organization's current control of their risk. If a | |
| 14 | risk isn't controlled (and the company doesn't want to accept the risk), | |
| 15 | an IS auditor will suggest implementing a control to address that risk. | |
| 19 | 16 | |
| 20 | 17 | Now, the CISA certification itself is, in my opinion, the main |
| 21 | 18 | certification for this career. While certifications such as the CPA or |
| @@ -27,13 +24,13 @@ However, to be honest, I am a skeptic of most certifications. I | ||
| 27 | 24 | understand the value they hold in terms of how much you need to commit |
| 28 | 25 | to studying or learning on the job, as well as the market value for |
| 29 | 26 | certifications such as the CISA. But I also have known some very |
| 30 | ~~incompetent~~ *less than stellar* auditors who have CPAs, CISAs, CIAs, | |
| 27 | +incompetent+ /less than stellar/ auditors who have CPAs, CISAs, CIAs, | |
| 31 | 28 | etc. |
| 32 | 29 | |
| 33 | 30 | The same goes for most industries: if a person is good at studying, they |
| 34 | 31 | can earn the certification. However, that knowledge means nothing unless |
| 35 | you're actually able to use it in real life and perform as expected of | |
| 36 | a certification holder. The challenge comes when people are hired or | |
| 32 | you're actually able to use it in real life and perform as expected of a | |
| 33 | certification holder. The challenge comes when people are hired or | |
| 37 | 34 | connected strictly because of their certifications or resume; you need |
| 38 | 35 | to see a person work before you can assume them having a CISA means |
| 39 | 36 | they're better than someone without the CISA. |
| @@ -42,50 +39,47 @@ Okay, rant over. Certifications are generally accepted as a measuring | ||
| 42 | 39 | stick of commitment and quality of an employee, so I am accepting it |
| 43 | 40 | too. |
| 44 | 41 | |
| 45 | ## Exam Content | |
| 46 | ||
| 42 | * Exam Content | |
| 47 | 43 | The CISA is broken down into five sections, each weighted with a |
| 48 | 44 | percentage of test questions that may appear. |
| 49 | 45 | |
| 50 |  | |
| 46 | #+caption: CISA exam sections | |
| 47 | [[https://img.cleberg.net/blog/20211204-i-passed-the-cisa/cisa-exam-sections.png]] | |
| 52 | 48 | |
| 53 | 49 | Since the exam contains 150 questions, here's how those sections break |
| 54 | 50 | down: |
| 55 | 51 | |
| 56 | Exam Section Percentage of Exam Questions | |
| 57 | ----------------- -------------------- ----------- | |
| 58 | 1 21% 32 | |
| 59 | 2 17% 26 | |
| 60 | 3 12% 18 | |
| 61 | 4 23% 34 | |
| 62 | 5 27% 40 | |
| 63 | **Grand Total** **100%** **150** | |
| 64 | ||
| 65 | ## My Studying Habits | |
| 52 | | Exam Section | Percentage of Exam | Questions | | |
| 53 | |---------------+--------------------+-----------| | |
| 54 | | 1 | 21% | 32 | | |
| 55 | | 2 | 17% | 26 | | |
| 56 | | 3 | 12% | 18 | | |
| 57 | | 4 | 23% | 34 | | |
| 58 | | 5 | 27% | 40 | | |
| 59 | | *Grand Total* | *100%* | *150* | | |
| 66 | 60 | |
| 61 | * My Studying Habits | |
| 67 | 62 | This part is a little hard for me to break down into specific detail due |
| 68 | 63 | to the craziness of the last year. While I officially purchased my |
| 69 | studying materials in December 2020 and opened them to "start | |
| 70 | studying" in January 2021, I really wasn't able to study much due to | |
| 71 | the demands of my job and personal life. | |
| 64 | studying materials in December 2020 and opened them to "start studying" | |
| 65 | in January 2021, I really wasn't able to study much due to the demands | |
| 66 | of my job and personal life. | |
| 72 | 67 | |
| 73 | 68 | Let me approach this from a few different viewpoints. |
| 74 | 69 | |
| 75 | ### Study Materials | |
| 76 | ||
| 70 | ** Study Materials | |
| 77 | 71 | Let's start by discussing the study materials I purchased. I'll be |
| 78 | 72 | referring to #1 as the CRM and #2 as the QAE. |
| 79 | 73 | |
| 80 | 1. [CISA Review Manual, 27th Edition \| | |
| 81 | Print](https://store.isaca.org/s/store#/store/browse/detail/a2S4w000004KoCbEAK) | |
| 82 | 2. [[<https://store.isaca.org/s/store#/store/browse/detail/a2S4w000004KoCcEAK>][CISA | |
| 83 | Review Questions, Answers & Explanations Manual, 12th Edition \| | |
| 84 | Print]] | |
| 74 | 1. [[https://store.isaca.org/s/store#/store/browse/detail/a2S4w000004KoCbEAK][CISA | |
| 75 | Review Manual, 27th Edition | Print]] | |
| 76 | 2. [[[[https://store.isaca.org/s/store#/store/browse/detail/a2S4w000004KoCcEAK]]][CISA | |
| 77 | Review Questions, Answers & Explanations Manual, 12th Edition | | |
| 78 | Print]] | |
| 85 | 79 | |
| 86 | 80 | The CRM is an excellent source of information and could honestly be used |
| 87 | 81 | as a reference for most IS auditors as a learning reference during their |
| 88 | daily audit responsibilities. However, it is **full** of information and | |
| 82 | daily audit responsibilities. However, it is *full** of information and | |
| 89 | 83 | can be overloading if you're not good at filtering out useless |
| 90 | 84 | information while studying. |
| 91 | 85 | |
| @@ -95,10 +89,10 @@ complaint about the QAE is that each question is immediately followed | ||
| 95 | 89 | with the correct answer and explanations below it, which means I had to |
| 96 | 90 | use something to constantly cover the answers while I was studying. |
| 97 | 91 | |
| 98 | I didn't use the online database version of the QAE, but I've heard | |
| 99 | that it's easier to use than the printed book. However, it is more | |
| 100 | expensive (\$299 database vs \$129 book) which might be important if | |
| 101 | you're paying for materials yourself. | |
| 92 | I didn't use the online database version of the QAE, but I've heard that | |
| 93 | it's easier to use than the printed book. However, it is more expensive | |
| 94 | ($299 database vs $129 book) which might be important if you're paying | |
| 95 | for materials yourself. | |
| 102 | 96 | |
| 103 | 97 | In terms of question difficulty, I felt that the QAE was a good |
| 104 | 98 | representation of the actual exam. I've seen a lot of people online say |
| @@ -111,8 +105,7 @@ topics you struggle with), and use the QAE to continue practicing | ||
| 111 | 105 | exam-like questions, you should be fine. I didn't use any online |
| 112 | 106 | courses, videos, etc. - the ISACA materials are more than enough. |
| 113 | 107 | |
| 114 | ### Studying Process | |
| 115 | ||
| 108 | ** Studying Process | |
| 116 | 109 | While I was able to briefly read through sections 1 and 2 in early 2021, |
| 117 | 110 | I had to stop and take a break from February/March to September. I |
| 118 | 111 | switched jobs in September, which allowed me a lot more free time to |
| @@ -124,60 +117,59 @@ practice exam from the QAE manual and scored 70% (105/150). | ||
| 124 | 117 | |
| 125 | 118 | Here's a breakdown of my initial practice exam: |
| 126 | 119 | |
| 127 | Exam Section Incorrect Correct Grand Total Percent | |
| 128 | ----------------- ----------- --------- ------------- --------- | |
| 129 | 1 8 25 33 76% | |
| 130 | 2 5 20 25 80% | |
| 131 | 3 6 12 18 67% | |
| 132 | 4 10 23 33 70% | |
| 133 | 5 16 25 41 61% | |
| 134 | **Grand Total** **45** **105** **150** **70%** | |
| 120 | | Exam Section | Incorrect | Correct | Grand Total | Percent | | |
| 121 | |---------------+-----------+---------+-------------+---------| | |
| 122 | | 1 | 8 | 25 | 33 | 76% | | |
| 123 | | 2 | 5 | 20 | 25 | 80% | | |
| 124 | | 3 | 6 | 12 | 18 | 67% | | |
| 125 | | 4 | 10 | 23 | 33 | 70% | | |
| 126 | | 5 | 16 | 25 | 41 | 61% | | |
| 127 | | *Grand Total** | *45** | *105** | *150** | *70%** | | |
| 135 | 128 | |
| 136 | 129 | As I expected, my toughest sections were related to project management, |
| 137 | 130 | development, implementation, and security. |
| 138 | 131 | |
| 139 | 132 | This just leaves October and November. For these months, I tried to |
| 140 | 133 | practice every few days, doing 10 questions for each section, until the |
| 141 | exam. This came out to 13 practice sessions, \~140 questions per | |
| 142 | section, and \~700 questions total. | |
| 134 | exam. This came out to 13 practice sessions, ~140 questions per section, | |
| 135 | and ~700 questions total. | |
| 143 | 136 | |
| 144 | 137 | While some practice sessions were worse and some were better, the final |
| 145 | 138 | results were similar to my practice exam results. As you can see below, |
| 146 | 139 | my averages were slightly worse than my practice exam. However, I got in |
| 147 | over 700 questions of practice and, most importantly, \*I read through | |
| 140 | over 700 questions of practice and, most importantly, *I read through | |
| 148 | 141 | the explanations every time I answered incorrectly and learned from my |
| 149 | mistakes\*. | |
| 150 | ||
| 151 | Exam Section Incorrect Correct Grand Total Percent | |
| 152 | ----------------- ----------- --------- ------------- --------- | |
| 153 | 1 33 108 141 77% | |
| 154 | 2 33 109 142 77% | |
| 155 | 3 55 89 144 62% | |
| 156 | 4 52 88 140 63% | |
| 157 | 5 55 85 140 61% | |
| 158 | **Grand Total** **228** **479** **707** **68%** | |
| 142 | mistakes*. | |
| 159 | 143 | |
| 160 |  | |
| 144 | | Exam Section | Incorrect | Correct | Grand Total | Percent | | |
| 145 | |---------------+-----------+---------+-------------+---------| | |
| 146 | | 1 | 33 | 108 | 141 | 77% | | |
| 147 | | 2 | 33 | 109 | 142 | 77% | | |
| 148 | | 3 | 55 | 89 | 144 | 62% | | |
| 149 | | 4 | 52 | 88 | 140 | 63% | | |
| 150 | | 5 | 55 | 85 | 140 | 61% | | |
| 151 | | *Grand Total** | *228** | *479** | *707** | *68%** | | |
| 162 | 152 | |
| 163 | ## Results | |
| 153 | #+caption: CISA practice question results | |
| 154 | [[https://img.cleberg.net/blog/20211204-i-passed-the-cisa/cisa-practice-questions-results.png]] | |
| 164 | 155 | |
| 156 | * Results | |
| 165 | 157 | Now, how do the practice scores reflect my actual results? After all, |
| 166 | 158 | it's hard to tell how good a practice regimen is unless you see how it |
| 167 | 159 | turns out. |
| 168 | 160 | |
| 169 | Exam Section Section Name Score | |
| 170 | -------------- ------------------------------------------------------------------ --------- | |
| 171 | 1 Information Systems Auditing Process 678 | |
| 172 | 2 Governance and Management of IT 590 | |
| 173 | 3 Information Systems Acquisition, Development, and Implementation 721 | |
| 174 | 4 Information Systems Operations and Business Resilience 643 | |
| 175 | 5 Protection of Information Assets 511 | |
| 176 | **TOTAL** **616** | |
| 161 | | Exam Section | Section Name | Score | | |
| 162 | |--------------+------------------------------------------------------------------+-------| | |
| 163 | | 1 | Information Systems Auditing Process | 678 | | |
| 164 | | 2 | Governance and Management of IT | 590 | | |
| 165 | | 3 | Information Systems Acquisition, Development, and Implementation | 721 | | |
| 166 | | 4 | Information Systems Operations and Business Resilience | 643 | | |
| 167 | | 5 | Protection of Information Assets | 511 | | |
| 168 | | *TOTAL* | | *616* | | |
| 177 | 169 | |
| 178 | 170 | Now, in order to pass the CISA, you need at least 450 on a sliding scale |
| 179 | 171 | of 200-800. Personally, I really have no clue what an average CISA score |
| 180 | is. After a *very* brief look online, I can see that the high end is | |
| 172 | is. After a /very/ brief look online, I can see that the high end is | |
| 181 | 173 | usually in the low 700s. In addition, only about 50-60% of people pass |
| 182 | 174 | the exam. |
| 183 | 175 | |
| @@ -196,8 +188,7 @@ CISA topics at all, the most important part of studying is doing | ||
| 196 | 188 | practice questions. You really need to understand how to read the |
| 197 | 189 | questions critically and pick the best answer. |
| 198 | 190 | |
| 199 | ## Looking Forward | |
| 200 | ||
| 191 | * Looking Forward | |
| 201 | 192 | I am extremely happy that I was finally able to pass the CISA. Looking |
| 202 | 193 | to the future, I'm not sure what's next in terms of professional |
| 203 | 194 | learning. My current company offers internal learning courses, so I will |
content/blog/2021-03-19-clone-github-repos.md → blog/clone-github-repos/index.org renamed +42 −49
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-03-19 | |
| 3 | title = "How to Clone All Repositories from a GitHub or Sourcehut Account" | |
| 4 | description = "Learn how to clone all GitHub or Sourcehut repositories." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Cloning from GitHub | |
| 1 | #+title: How to Clone All Repositories from a GitHub or Sourcehut Account | |
| 2 | #+date: 2021-03-19 | |
| 3 | #+description: Learn how to clone all GitHub or Sourcehut repositories. | |
| 4 | #+filetags: :dev: | |
| 8 | 5 | |
| 6 | * Cloning from GitHub | |
| 9 | 7 | If you're like me and use a lot of different devices (and sometimes |
| 10 | 8 | decide to just wipe your device and start with a new OS), you probably |
| 11 | 9 | know the pain of cloning all your old code repositories down to your |
| @@ -13,47 +11,45 @@ local file system. | ||
| 13 | 11 | |
| 14 | 12 | If you're using GitHub, you can easily clone all of your code back down |
| 15 | 13 | in just seconds. First, create a bash script. I do so by opening a new |
| 16 | file in `nano`, but you can use `gedit`, | |
| 17 | `vim`, or something else: | |
| 14 | file in =nano=, but you can use =gedit=, =vim=, or something else: | |
| 18 | 15 | |
| 19 | ```sh | |
| 16 | #+begin_src sh | |
| 20 | 17 | nano clone_github_repos.sh |
| 21 | ``` | |
| 18 | #+end_src | |
| 22 | 19 | |
| 23 | 20 | Next, paste in the following information. Note that you can replace the |
| 24 | word `users` in the first line with `orgs` and | |
| 25 | type an organization's name instead of a user's name. | |
| 21 | word =users= in the first line with =orgs= and type an organization's | |
| 22 | name instead of a user's name. | |
| 26 | 23 | |
| 27 | ```sh | |
| 24 | #+begin_src sh | |
| 28 | 25 | CNTX=users; NAME=YOUR-USERNAME; PAGE=1 |
| 29 | 26 | curl "https://api.github.com/$CNTX/$NAME/repos?page=$PAGE&per_page=100" | |
| 30 | 27 | grep -e 'git_url*' | |
| 31 | 28 | cut -d \" -f 4 | |
| 32 | 29 | xargs -L1 git clone |
| 33 | ``` | |
| 30 | #+end_src | |
| 34 | 31 | |
| 35 | 32 | Finally, save the bash script and make it executable. |
| 36 | 33 | |
| 37 | ```sh | |
| 34 | #+begin_src sh | |
| 38 | 35 | chmod a+x clone_github_repos.sh |
| 39 | ``` | |
| 36 | #+end_src | |
| 40 | 37 | |
| 41 | 38 | Now you can run the script and should see the cloning process begin. |
| 42 | 39 | |
| 43 | ```sh | |
| 40 | #+begin_src sh | |
| 44 | 41 | ./clone_github_repos.sh |
| 45 | ``` | |
| 46 | ||
| 47 | ## Cloning from Sourcehut | |
| 42 | #+end_src | |
| 48 | 43 | |
| 44 | * Cloning from Sourcehut | |
| 49 | 45 | I haven't fully figured out how to directly incorporate Sourcehut's |
| 50 | 46 | GraphQL API into a bash script yet, so this one will take two steps. |
| 51 | 47 | |
| 52 | First, log-in to Sourcehut and go to their [GraphQL playground for | |
| 53 | Git](https://git.sr.ht/graphql). Next, paste the following query into | |
| 54 | the left box: | |
| 48 | First, log-in to Sourcehut and go to their | |
| 49 | [[https://git.sr.ht/graphql][GraphQL playground for Git]]. Next, paste | |
| 50 | the following query into the left box: | |
| 55 | 51 | |
| 56 | ```sh | |
| 52 | #+begin_src sh | |
| 57 | 53 | query { |
| 58 | 54 | me { |
| 59 | 55 | canonicalName |
| @@ -65,7 +61,7 @@ query { | ||
| 65 | 61 | } |
| 66 | 62 | } |
| 67 | 63 | } |
| 68 | ``` | |
| 64 | #+end_src | |
| 69 | 65 | |
| 70 | 66 | The output on the right side will give you an object of all your |
| 71 | 67 | repositories. Just grab that text and remove all the characters such as |
| @@ -74,19 +70,18 @@ space-separated values for the next step. | ||
| 74 | 70 | |
| 75 | 71 | Now let's create the bash script: |
| 76 | 72 | |
| 77 | ```sh | |
| 73 | #+begin_src sh | |
| 78 | 74 | nano clone_sourcehut_repos.sh |
| 79 | ``` | |
| 75 | #+end_src | |
| 80 | 76 | |
| 81 | 77 | Next, paste the following bash script in with the list of repositories |
| 82 | you obtained above and replace `your-username` with your | |
| 83 | username. | |
| 78 | you obtained above and replace =your-username= with your username. | |
| 84 | 79 | |
| 85 | 80 | Note that this uses the SSH-based Git cloning method |
| 86 | (e.g. =git@git...=), so you'll need to ensure you have set up Sourcehut | |
| 81 | (e.g. =git@git...=), so you'll need to ensure you have set up Sourcehut | |
| 87 | 82 | with your SSH key. |
| 88 | 83 | |
| 89 | ```sh | |
| 84 | #+begin_src sh | |
| 90 | 85 | repos=(repo1 repo2 repo3) |
| 91 | 86 | |
| 92 | 87 | # List all sub-directories in the current directory |
| @@ -95,37 +90,35 @@ do | ||
| 95 | 90 | # Clone |
| 96 | 91 | git clone git@git.sr.ht:~your-username/$repo |
| 97 | 92 | done |
| 98 | ``` | |
| 93 | #+end_src | |
| 99 | 94 | |
| 100 | 95 | Finally, save the bash script and make it executable. |
| 101 | 96 | |
| 102 | ```sh | |
| 97 | #+begin_src sh | |
| 103 | 98 | chmod a+x clone_sourcehut_repos.sh |
| 104 | ``` | |
| 99 | #+end_src | |
| 105 | 100 | |
| 106 | 101 | Now you can run the script and should see the cloning process begin. |
| 107 | 102 | |
| 108 | ```sh | |
| 103 | #+begin_src sh | |
| 109 | 104 | ./clone_sourcehut_repos.sh |
| 110 | ``` | |
| 111 | ||
| 112 | ## Moving Repositories to a New Host | |
| 105 | #+end_src | |
| 113 | 106 | |
| 107 | * Moving Repositories to a New Host | |
| 114 | 108 | Now that you have all of your code repositories cloned to your local |
| 115 | 109 | computer, you may want to change the remote host (e.g., moving from |
| 116 | 110 | GitHub to GitLab). To do this, let's create another bash script: |
| 117 | 111 | |
| 118 | ```sh | |
| 112 | #+begin_src sh | |
| 119 | 113 | nano change_remote_urls.sh |
| 120 | ``` | |
| 114 | #+end_src | |
| 121 | 115 | |
| 122 | 116 | Past the following information and be sure to change the URL information |
| 123 | 117 | to whichever host you are moving to. For this example, I am looping |
| 124 | 118 | through all of my cloned GitHub directories and changing them to |
| 125 | Sourcehut (e.g. `<YOUR_NEW_REMOTE_URL>` -\> | |
| 126 | `git@git.sr.ht:~myusername`). | |
| 119 | Sourcehut (e.g. =<YOUR_NEW_REMOTE_URL>= -> =git@git.sr.ht:~myusername=). | |
| 127 | 120 | |
| 128 | ```sh | |
| 121 | #+begin_src sh | |
| 129 | 122 | # List all sub-directories in the current directory |
| 130 | 123 | for dir in */ |
| 131 | 124 | do |
| @@ -140,16 +133,16 @@ do | ||
| 140 | 133 | # Go back to main directory |
| 141 | 134 | cd .. |
| 142 | 135 | done |
| 143 | ``` | |
| 136 | #+end_src | |
| 144 | 137 | |
| 145 | 138 | Finally, save the bash script and make it executable. |
| 146 | 139 | |
| 147 | ```sh | |
| 140 | #+begin_src sh | |
| 148 | 141 | chmod a+x change_remote_urls.sh |
| 149 | ``` | |
| 142 | #+end_src | |
| 150 | 143 | |
| 151 | 144 | Now you can run the script and should see the cloning process begin. |
| 152 | 145 | |
| 153 | ```sh | |
| 146 | #+begin_src sh | |
| 154 | 147 | ./change_remote_urls.sh |
| 155 | ``` | |
| 148 | #+end_src | |
content/blog/2022-03-23-cloudflare-dns-api.md → blog/cloudflare-dns-api/index.org renamed +44 −49
| @@ -1,41 +1,39 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-03-23 | |
| 3 | title = "Dynamic DNS with Cloudflare API" | |
| 4 | description = "Learn how to dynamically update DNS records for changing IPs with Cloudflare." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## DDNS: Dynamic DNS | |
| 8 | ||
| 9 | If you're hosting a service from a location with dynamic DNS (where | |
| 10 | your IP may change at any time), you must have a solution to update the | |
| 11 | DNS so that you can access your service even when the IP of the server | |
| 1 | #+title: Dynamic DNS with Cloudflare API | |
| 2 | #+date: 2022-03-23 | |
| 3 | #+description: Learn how to dynamically update DNS records for changing IPs with Cloudflare. | |
| 4 | #+filetags: :sysadmin: | |
| 5 | ||
| 6 | * DDNS: Dynamic DNS | |
| 7 | If you're hosting a service from a location with dynamic DNS (where your | |
| 8 | IP may change at any time), you must have a solution to update the DNS | |
| 9 | so that you can access your service even when the IP of the server | |
| 12 | 10 | changes. |
| 13 | 11 | |
| 14 | The process below uses the [Cloudflare API](https://api.cloudflare.com/) | |
| 15 | to update DNS `A` and `AAAA` records with the | |
| 16 | server's current IP. If you use another DNS provider, you will have to | |
| 17 | find a way to update your DNS (or find a way to get a static IP). | |
| 12 | The process below uses the [[https://api.cloudflare.com/][Cloudflare | |
| 13 | API]] to update DNS =A= and =AAAA= records with the server's current IP. | |
| 14 | If you use another DNS provider, you will have to find a way to update | |
| 15 | your DNS (or find a way to get a static IP). | |
| 18 | 16 | |
| 19 | First, install `jq` since we will use it in the next script: | |
| 17 | First, install =jq= since we will use it in the next script: | |
| 20 | 18 | |
| 21 | ```sh | |
| 19 | #+begin_src sh | |
| 22 | 20 | sudo apt install jq |
| 23 | ``` | |
| 21 | #+end_src | |
| 24 | 22 | |
| 25 | 23 | Next, create a location for your DDNS update scripts and open the first |
| 26 | 24 | script: |
| 27 | 25 | |
| 28 | ```sh | |
| 26 | #+begin_src sh | |
| 29 | 27 | mkdir ~/ddns |
| 30 | 28 | nano ~/ddns/update.sh |
| 31 | ``` | |
| 29 | #+end_src | |
| 32 | 30 | |
| 33 | The following `update.sh` script will take all of your | |
| 34 | domains and subdomains and check Cloudflare to see if the current | |
| 35 | `A` and `AAAA` records match your server's IP | |
| 36 | address. If not, it will update the records. | |
| 31 | The following =update.sh= script will take all of your domains and | |
| 32 | subdomains and check Cloudflare to see if the current =A= and =AAAA= | |
| 33 | records match your server's IP address. If not, it will update the | |
| 34 | records. | |
| 37 | 35 | |
| 38 | ```sh | |
| 36 | #+begin_src sh | |
| 39 | 37 | # file: update.sh |
| 40 | 38 | #!/bin/bash |
| 41 | 39 | |
| @@ -57,22 +55,20 @@ do | ||
| 57 | 55 | echo -e "\nUpdating $subdomain..." |
| 58 | 56 | zone_name=$domain dns_record=$subdomain /home/<your-username>/ddns/ddns.sh |
| 59 | 57 | done |
| 60 | ``` | |
| 58 | #+end_src | |
| 61 | 59 | |
| 62 | Next, open up the `ddns.sh` script. Paste the following into | |
| 63 | the script and update the `api_token` and `email` | |
| 64 | variables. | |
| 60 | Next, open up the =ddns.sh= script. Paste the following into the script | |
| 61 | and update the =api_token= and =email= variables. | |
| 65 | 62 | |
| 66 | ```sh | |
| 63 | #+begin_src sh | |
| 67 | 64 | nano ~/ddns/ddns.sh |
| 68 | ``` | |
| 65 | #+end_src | |
| 69 | 66 | |
| 70 | :warning: **Note**: If you want your DNS records to be proxied through | |
| 71 | Cloudflare, find and update the following snippet: | |
| 72 | `"proxied":false}"` to say `true` instead of | |
| 73 | `false`. | |
| 67 | *Note*: If you want your DNS records to be proxied through | |
| 68 | Cloudflare, find and update the following snippet: ="proxied":false}"= | |
| 69 | to say =true= instead of =false=. | |
| 74 | 70 | |
| 75 | ```sh | |
| 71 | #+begin_src sh | |
| 76 | 72 | # file: ddns.sh |
| 77 | 73 | #!/bin/bash |
| 78 | 74 | # based on https://gist.github.com/Tras2/cba88201b17d765ec065ccbedfb16d9a |
| @@ -165,31 +161,30 @@ then | ||
| 165 | 161 | else |
| 166 | 162 | echo "There is a problem with either the email or the password" |
| 167 | 163 | fi |
| 168 | ``` | |
| 164 | #+end_src | |
| 169 | 165 | |
| 170 | 166 | Once the script is saved and closed, make the scripts executable: |
| 171 | 167 | |
| 172 | ```sh | |
| 168 | #+begin_src sh | |
| 173 | 169 | chmod +x ~/ddns/ddns.sh |
| 174 | 170 | chmod +x ~/ddns/update.sh |
| 175 | ``` | |
| 171 | #+end_src | |
| 176 | 172 | |
| 177 | 173 | You can test the script by running it manually: |
| 178 | 174 | |
| 179 | ```sh | |
| 175 | #+begin_src sh | |
| 180 | 176 | ./update.sh |
| 181 | ``` | |
| 177 | #+end_src | |
| 182 | 178 | |
| 183 | To make sure the scripts run automatically, add it to the | |
| 184 | `cron` file so that it will run on a schedule. To do this, | |
| 185 | open the cron file: | |
| 179 | To make sure the scripts run automatically, add it to the =cron= file so | |
| 180 | that it will run on a schedule. To do this, open the cron file: | |
| 186 | 181 | |
| 187 | ```sh | |
| 182 | #+begin_src sh | |
| 188 | 183 | crontab -e |
| 189 | ``` | |
| 184 | #+end_src | |
| 190 | 185 | |
| 191 | 186 | In the cron file, paste the following at the bottom of the editor: |
| 192 | 187 | |
| 193 | ```sh | |
| 194 | */5 * * * * bash /home/<your_username>/ddns/update.sh | |
| 195 | ``` | |
| 188 | #+begin_src sh | |
| 189 | ,*/5 ** ** ** ** bash /home/<your_username>/ddns/update.sh | |
| 190 | #+end_src | |
content/blog/2018-11-28-cpp-compiler.md → blog/cpp-compiler/index.org renamed +39 −49
| @@ -1,12 +1,10 @@ | ||
| 1 | +++ | |
| 2 | date = 2018-11-28 | |
| 3 | title = "The C++ Compiler" | |
| 4 | description = "Learn basics about the C++ compilation process." | |
| 5 | +++ | |
| 1 | #+title: The C++ Compiler | |
| 2 | #+date: 2018-11-28 | |
| 3 | #+description: Learn basics about the C++ compilation process. | |
| 4 | #+filetags: :dev: | |
| 6 | 5 | |
| 7 | # A Brief Introduction | |
| 8 | ||
| 9 | [C++](https://en.wikipedia.org/wiki/C%2B%2B) is a general-purpose | |
| 6 | * A Brief Introduction | |
| 7 | [[https://en.wikipedia.org/wiki/C%2B%2B][C++]] is a general-purpose | |
| 10 | 8 | programming language with object-oriented, generic, and functional |
| 11 | 9 | features in addition to facilities for low-level memory manipulation. |
| 12 | 10 | |
| @@ -15,19 +13,17 @@ can be executed. There are many steps and intricacies to the compilation | ||
| 15 | 13 | process, and this post was a personal exercise to learn and remember as |
| 16 | 14 | much information as I can. |
| 17 | 15 | |
| 18 | ```cpp | |
| 16 | #+begin_src cpp | |
| 19 | 17 | #include <iostream> |
| 20 | 18 | |
| 21 | 19 | int main() |
| 22 | 20 | { |
| 23 | 21 | std::cout << "Hello, world!\n"; |
| 24 | 22 | } |
| 25 | ``` | |
| 26 | ||
| 27 | # Compilation Process | |
| 28 | ||
| 29 | ## An Overview | |
| 23 | #+end_src | |
| 30 | 24 | |
| 25 | ** Compilation Process | |
| 26 | *** An Overview | |
| 31 | 27 | Compiling C++ projects is a frustrating task most days. Seemingly |
| 32 | 28 | nonexistent errors keeping your program from successfully compiling can |
| 33 | 29 | be annoying (especially since you know you wrote it perfectly the first |
| @@ -35,50 +31,46 @@ time, right?). | ||
| 35 | 31 | |
| 36 | 32 | I'm learning more and more about C++ these days and decided to write |
| 37 | 33 | this concept down so that I can cement it even further in my own head. |
| 38 | However, C++ is not the only compiled language. Check out [the Wikipedia | |
| 39 | entry for compiled | |
| 40 | languages](https://en.wikipedia.org/wiki/Compiled_language) for more | |
| 41 | examples of compiled languages. | |
| 34 | However, C++ is not the only compiled language. Check out | |
| 35 | [[https://en.wikipedia.org/wiki/Compiled_language][the Wikipedia entry | |
| 36 | for compiled languages]] for more examples of compiled languages. | |
| 42 | 37 | |
| 43 | 38 | I'll start with a wonderful, graphical way to conceptualize the C++ |
| 44 | compiler. View [The C++ Compilation | |
| 45 | Process](https://web.archive.org/web/20190419035048/http://faculty.cs.niu.edu/~mcmahon/CS241/Notes/compile.html) | |
| 46 | by Kurt MacMahon, an NIU professor, to see the graphic and an | |
| 47 | explanation. The goal of the compilation process is to take the C++ code | |
| 48 | and produce a shared library, dynamic library, or an executable file. | |
| 49 | ||
| 50 | ## Compilation Phases | |
| 51 | ||
| 39 | compiler. View | |
| 40 | [[https://web.archive.org/web/20190419035048/http://faculty.cs.niu.edu/~mcmahon/CS241/Notes/compile.html][The | |
| 41 | C++ Compilation Process]] by Kurt MacMahon, an NIU professor, to see the | |
| 42 | graphic and an explanation. The goal of the compilation process is to | |
| 43 | take the C++ code and produce a shared library, dynamic library, or an | |
| 44 | executable file. | |
| 45 | ||
| 46 | ** Compilation Phases | |
| 52 | 47 | Let's break down the compilation process. There are four major steps to |
| 53 | 48 | compiling C++ code. |
| 54 | 49 | |
| 55 | ### Step 1 | |
| 56 | ||
| 50 | *** Step 1 | |
| 57 | 51 | The first step is to expand the source code file to meet all |
| 58 | 52 | dependencies. The C++ preprocessor includes the code from all the header |
| 59 | files, such as `#include <iostream>`. Now, what does that | |
| 60 | mean? The previous example includes the `iostream` header. | |
| 61 | This tells the computer that you want to use the `iostream` | |
| 62 | standard library, which contains classes and functions written in the | |
| 63 | core language. This specific header allows you to manipulate | |
| 64 | input/output streams. After all this, you'll end up which a temporary | |
| 65 | file that contains the expanded source code. | |
| 66 | ||
| 67 | In the example of the C++ code above, the `iostream` class | |
| 68 | would be included in the expanded code. | |
| 53 | files, such as =#include <iostream>=. Now, what does that mean? The | |
| 54 | previous example includes the =iostream= header. This tells the computer | |
| 55 | that you want to use the =iostream= standard library, which contains | |
| 56 | classes and functions written in the core language. This specific header | |
| 57 | allows you to manipulate input/output streams. After all this, you'll | |
| 58 | end up which a temporary file that contains the expanded source code. | |
| 69 | 59 | |
| 70 | ### Step 2 | |
| 60 | In the example of the C++ code above, the =iostream= class would be | |
| 61 | included in the expanded code. | |
| 71 | 62 | |
| 63 | *** Step 2 | |
| 72 | 64 | After the code is expanded, the compiler comes into play. The compiler |
| 73 | 65 | takes the C++ code and converts this code into the assembly language, |
| 74 | 66 | understood by the platform. You can see this in action if you head over |
| 75 | to the [GodBolt Compiler Explorer](https://godbolt.org), which shows C++ | |
| 76 | being converted into assembly dynamically. | |
| 67 | to the [[https://godbolt.org][GodBolt Compiler Explorer]], which shows | |
| 68 | C++ being converted into assembly dynamically. | |
| 77 | 69 | |
| 78 | For example, the `Hello, world!` code snippet above compiles | |
| 79 | into the following assembly code: | |
| 70 | For example, the =Hello, world!= code snippet above compiles into the | |
| 71 | following assembly code: | |
| 80 | 72 | |
| 81 | ```asm | |
| 73 | #+begin_src asm | |
| 82 | 74 | .LC0: |
| 83 | 75 | .string "Hello, world!\n" |
| 84 | 76 | main: |
| @@ -118,10 +110,9 @@ _GLOBAL__sub_I_main: | ||
| 118 | 110 | call __static_initialization_and_destruction_0(int, int) |
| 119 | 111 | pop rbp |
| 120 | 112 | ret |
| 121 | ``` | |
| 122 | ||
| 123 | ### Step 3 | |
| 113 | #+end_src | |
| 124 | 114 | |
| 115 | *** Step 3 | |
| 125 | 116 | Third, the assembly code generated by the compiler is assembled into the |
| 126 | 117 | object code for the platform. Essentially, this is when the compiler |
| 127 | 118 | takes the assembly code and assembles it into machine code in a binary |
| @@ -130,8 +121,7 @@ compilers will allow you to stop compilation at this step. This would be | ||
| 130 | 121 | useful for compiling each source code file separately. This saves time |
| 131 | 122 | later if a single file changes; only that file needs to be recompiled. |
| 132 | 123 | |
| 133 | ### Step 4 | |
| 134 | ||
| 124 | *** Step 4 | |
| 135 | 125 | Finally, the object code file generated by the assembler is linked |
| 136 | 126 | together with the object code files for any library functions used to |
| 137 | 127 | produce a shared library, dynamic library, or an executable file. It |
content/blog/2020-02-09-cryptography-basics.md → blog/cryptography-basics/index.org renamed +70 −77
| @@ -1,30 +1,29 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-02-09 | |
| 3 | title = "Cryptography Basics" | |
| 4 | description = "Learn about the basics of cryptography." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Similar Article Available | |
| 8 | ||
| 9 | If you haven't already, feel free to read my post on [AES | |
| 10 | Encryption](/blog/aes-encryption/). | |
| 11 | ||
| 12 | # What is Cryptography? | |
| 13 | ||
| 14 | In layman's terms, cryptography is a process that can change data from | |
| 15 | a readable format into an unreadable format (and vice-versa) through a | |
| 1 | #+title: Cryptography Basics | |
| 2 | #+date: 2020-02-09 | |
| 3 | #+description: Learn about the basics of cryptography. | |
| 4 | #+filetags: :security: | |
| 5 | ||
| 6 | * Similar Article Available | |
| 7 | If you haven't already, feel free to read my post on | |
| 8 | [[../aes-encryption/][AES Encryption]]. | |
| 9 | ||
| 10 | * What is Cryptography? | |
| 11 | In layman's terms, cryptography is a process that can change data from a | |
| 12 | readable format into an unreadable format (and vice-versa) through a | |
| 16 | 13 | series of processes and secrets. More technically, this is the Internet |
| 17 | 14 | Security Glossary's definition: |
| 18 | 15 | |
| 19 | > [Cryptography is] the mathematical science that deals with | |
| 20 | > transforming data to render its meaning unintelligible (i.e., to hide | |
| 21 | > its semantic content), prevent its undetected alteration, or prevent | |
| 22 | > its unauthorized use. If the transformation is reversible, | |
| 23 | > cryptography also deals with restoring encrypted data to an | |
| 24 | > intelligible form. | |
| 25 | > | |
| 26 | > - [Internet Security Glossary | |
| 27 | > (2000)](https://tools.ietf.org/html/rfc2828) | |
| 16 | #+begin_quote | |
| 17 | [Cryptography is] the mathematical science that deals with transforming | |
| 18 | data to render its meaning unintelligible (i.e., to hide its semantic | |
| 19 | content), prevent its undetected alteration, or prevent its unauthorized | |
| 20 | use. If the transformation is reversible, cryptography also deals with | |
| 21 | restoring encrypted data to an intelligible form. | |
| 22 | ||
| 23 | - [[https://tools.ietf.org/html/rfc2828][Internet Security Glossary | |
| 24 | (2000)]] | |
| 25 | ||
| 26 | #+end_quote | |
| 28 | 27 | |
| 29 | 28 | Cryptography cannot offer protection against the loss of data; it simply |
| 30 | 29 | offers encryption methods to protect data at-rest and data in-traffic. |
| @@ -34,25 +33,23 @@ decrypted back to plaintext). The encryption process is completed | ||
| 34 | 33 | through the use of a mathematical function that utilizes one or more |
| 35 | 34 | values called keys to encrypt or decrypt the data. |
| 36 | 35 | |
| 37 | # Key Elements of Cryptographic Systems | |
| 38 | ||
| 36 | * Key Elements of Cryptographic Systems | |
| 39 | 37 | To create or evaluate a cryptographic system, you need to know the |
| 40 | 38 | essential pieces to the system: |
| 41 | 39 | |
| 42 | - **Encryption Algorithm (Primitive):** A mathematical process that | |
| 43 | encrypts and decrypts data. | |
| 44 | - **Encryption Key:** A string of bits used within the encryption | |
| 45 | algorithm as the secret that allows successful encryption or | |
| 46 | decryption of data. | |
| 47 | - **Key Length (Size):** The maximum number of bits within the | |
| 48 | encryption key. It's important to remember that key size is | |
| 49 | regulated in many countries. | |
| 50 | - **Message Digest:** A smaller, fixed-size bit string version of the | |
| 51 | original message. This is practically infeasible to reverse, which | |
| 52 | is why it's commonly used to verify integrity. | |
| 53 | ||
| 54 | # Symmetric Systems (Secret Key Cryptography) | |
| 55 | ||
| 40 | - *Encryption Algorithm (Primitive):** A mathematical process that | |
| 41 | encrypts and decrypts data. | |
| 42 | - *Encryption Key:** A string of bits used within the encryption | |
| 43 | algorithm as the secret that allows successful encryption or | |
| 44 | decryption of data. | |
| 45 | - *Key Length (Size):** The maximum number of bits within the encryption | |
| 46 | key. It's important to remember that key size is regulated in many | |
| 47 | countries. | |
| 48 | - *Message Digest:** A smaller, fixed-size bit string version of the | |
| 49 | original message. This is practically infeasible to reverse, which is | |
| 50 | why it's commonly used to verify integrity. | |
| 51 | ||
| 52 | * Symmetric Systems (Secret Key Cryptography) | |
| 56 | 53 | Symmetric cryptography utilizes a secret, bidirectional key to perform |
| 57 | 54 | both encryption and decryption of the data. The most common |
| 58 | 55 | implementation of symmetric cryptography is the Advanced Encryption |
| @@ -76,14 +73,13 @@ key is private, it can be difficult to safely distribute keys to | ||
| 76 | 73 | communication partners. Additionally, the key cannot be used to sign |
| 77 | 74 | messages since it's necessary to keep the key private. |
| 78 | 75 | |
| 79 | # Asymmetric Systems (Public Key Cryptography) | |
| 80 | ||
| 76 | * Asymmetric Systems (Public Key Cryptography) | |
| 81 | 77 | Asymmetric cryptography utilizes two keys within the system: a secret |
| 82 | 78 | key that is privately-held and a public key that can be distributed |
| 83 | 79 | freely. The interesting aspect of asymmetric cryptography is that either |
| 84 | key can be used to encrypt the data, there's no rule that dictates | |
| 85 | which key must be used for encryption. Once one key is used to encrypt | |
| 86 | the data, only the other key can be used to decrypt the data. This means | |
| 80 | key can be used to encrypt the data, there's no rule that dictates which | |
| 81 | key must be used for encryption. Once one key is used to encrypt the | |
| 82 | data, only the other key can be used to decrypt the data. This means | |
| 87 | 83 | that if the private key encrypts the data, only the public key can |
| 88 | 84 | decrypt the data. |
| 89 | 85 | |
| @@ -103,17 +99,16 @@ with digital signatures and public keys. To combat this, applications | ||
| 103 | 99 | often use a public key infrastructure (PKI) to independently |
| 104 | 100 | authenticate the validity of signatures and keys. |
| 105 | 101 | |
| 106 | Due to the large key size and [inefficient mathematical | |
| 107 | functions](https://crypto.stackexchange.com/a/591) of asymmetric | |
| 108 | encryption, elliptical curve cryptography (ECC) is often used to | |
| 109 | increase security while using fewer resources. | |
| 110 | ||
| 111 | # Applications of Cryptographic Systems | |
| 102 | Due to the large key size and | |
| 103 | [[https://crypto.stackexchange.com/a/591][inefficient mathematical | |
| 104 | functions]] of asymmetric encryption, elliptical curve cryptography | |
| 105 | (ECC) is often used to increase security while using fewer resources. | |
| 112 | 106 | |
| 107 | * Applications of Cryptographic Systems | |
| 113 | 108 | There are quite a few implementations of cryptographic systems around |
| 114 | 109 | the world. Here are a few popular examples: |
| 115 | 110 | |
| 116 | **Transport Layer Security (TLS):** One of the most famous cryptographic | |
| 111 | *Transport Layer Security (TLS):** One of the most famous cryptographic | |
| 117 | 112 | solutions created is TLS, a session-layered or connection-layered |
| 118 | 113 | internet protocol that allows for secure communications between browsers |
| 119 | 114 | and servers. Using handshakes, peer negotiation, and authentication |
| @@ -123,12 +118,12 @@ was found in the SSL protocol in 2014. Instead of SSL, TLS can be used | ||
| 123 | 118 | with HTTP to form HTTPS and is the preferred method for modern web |
| 124 | 119 | development due to its increased security. |
| 125 | 120 | |
| 126 | **Secure Hypertext Transfer Protocol (HTTPS):** An application layer | |
| 121 | *Secure Hypertext Transfer Protocol (HTTPS):** An application layer | |
| 127 | 122 | protocol that allows for secure transport of data between servers and |
| 128 | 123 | web clients. One of the unique parts of HTTPS is that it uses a secured |
| 129 | 124 | port number instead of the default web port address. |
| 130 | 125 | |
| 131 | **Virtual Private Network (VPN):** VPNs are made to securely extend a | |
| 126 | *Virtual Private Network (VPN):** VPNs are made to securely extend a | |
| 132 | 127 | private network across public networks by utilizing an encrypted layered |
| 133 | 128 | tunneling protocol paired with an authentication method, such as |
| 134 | 129 | usernames and passwords. This technology originally allowed remote |
| @@ -136,7 +131,7 @@ employees to access their company's data but have evolved into one of | ||
| 136 | 131 | the top choices for anyone who wishes to mask their sensitive personal |
| 137 | 132 | data. |
| 138 | 133 | |
| 139 | **Internet Protocol Security (IPSec):** This protocol suite facilitates | |
| 134 | *Internet Protocol Security (IPSec):** This protocol suite facilitates | |
| 140 | 135 | communication between two or more hosts or subnets by authenticating and |
| 141 | 136 | encrypting the data packets. IPSec is used in a lot of VPNs to establish |
| 142 | 137 | the VPN connection through the transport and tunnel mode encryption |
| @@ -144,35 +139,33 @@ methods. IPSec encrypts just the data portion of packets in the | ||
| 144 | 139 | transport methods, but it encrypts both the data and headers in the |
| 145 | 140 | tunnel method (introducing an additional header for authentication). |
| 146 | 141 | |
| 147 | **Secure Shell (SSH):** SSH is another network protocol used to protect | |
| 142 | *Secure Shell (SSH):** SSH is another network protocol used to protect | |
| 148 | 143 | network services by authenticating users through a secure channel. This |
| 149 | 144 | protocol is often used for command-line (shell) functions such as remote |
| 150 | 145 | shell commands, logins, and file transfers. |
| 151 | 146 | |
| 152 | **Kerberos:** Developed by MIT, Kerberos is a computer-network | |
| 147 | *Kerberos:** Developed by MIT, Kerberos is a computer-network | |
| 153 | 148 | authentication protocol that works on the basis of tickets to allow |
| 154 | 149 | nodes communicating over a non-secure network to prove their identity to |
| 155 | 150 | one another securely. This is most commonly used in business |
| 156 | 151 | environments when used as the authentication and encryption method for |
| 157 | 152 | Windows Active Directory (AD). |
| 158 | 153 | |
| 159 | # Cybersecurity Controls | |
| 160 | ||
| 161 | If you're someone who needs solutions on how to control risks | |
| 162 | associated with utilizing a crytograhpic system, start with a few basic | |
| 163 | controls: | |
| 164 | ||
| 165 | - **Policies:** A policy on the use of cryptographic controls for | |
| 166 | protection of information is implemented and is in accordance with | |
| 167 | organizational objectives. | |
| 168 | - **Key management:** A policy on the use, protection and lifetime of | |
| 169 | cryptographic keys is implemented through the entire application | |
| 170 | lifecycle. | |
| 171 | - **Key size:** The organization has researched the optimal key size | |
| 172 | for their purposes, considering national laws, required processing | |
| 173 | power, and longevity of the solution. | |
| 174 | - **Algorithm selection:** Implemented algorithms are sufficiently | |
| 175 | appropriate for the business of the organization, robust, and align | |
| 176 | with recommended guidelines. | |
| 177 | - **Protocol configuration:** Protocols have been reviewed and | |
| 178 | configured suitable to the purpose of the business. | |
| 154 | * Cybersecurity Controls | |
| 155 | If you're someone who needs solutions on how to control risks associated | |
| 156 | with utilizing a crytograhpic system, start with a few basic controls: | |
| 157 | ||
| 158 | - *Policies:** A policy on the use of cryptographic controls for | |
| 159 | protection of information is implemented and is in accordance with | |
| 160 | organizational objectives. | |
| 161 | - *Key management:** A policy on the use, protection and lifetime of | |
| 162 | cryptographic keys is implemented through the entire application | |
| 163 | lifecycle. | |
| 164 | - *Key size:** The organization has researched the optimal key size for | |
| 165 | their purposes, considering national laws, required processing power, | |
| 166 | and longevity of the solution. | |
| 167 | - *Algorithm selection:** Implemented algorithms are sufficiently | |
| 168 | appropriate for the business of the organization, robust, and align | |
| 169 | with recommended guidelines. | |
| 170 | - *Protocol configuration:** Protocols have been reviewed and configured | |
| 171 | suitable to the purpose of the business. | |
blog/curseradio/index.org added +95
| @@ -0,0 +1,95 @@ | ||
| 1 | #+title: CurseRadio: Listening to the Radio on the Command Line | |
| 2 | #+date: 2022-07-25 | |
| 3 | #+description: Use Curse Radio to listen to radio on the command line. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * Overview | |
| 7 | While exploring some interesting Linux applications, I stumbled across | |
| 8 | [[https://github.com/chronitis/curseradio][curseradio]], a command-line | |
| 9 | radio player based on Python. | |
| 10 | ||
| 11 | This application is fantastic and incredibly easy to install, so I | |
| 12 | wanted to dedicate a post today to this app. Let's look at the features | |
| 13 | within the app and then walk through the installation process I took to | |
| 14 | get =curseradio= working. | |
| 15 | ||
| 16 | * Features | |
| 17 | #+caption: curseradio | |
| 18 | [[https://img.cleberg.net/blog/20220725-curseradio/curseradio.png]] | |
| 19 | ||
| 20 | The radio player itself is quite minimal. As you can see in the | |
| 21 | screenshot above, it contains a simple plaintext list of all available | |
| 22 | categories, which can be broken down further and further. In addition, | |
| 23 | radio shows are available for listening, alongside regular radio | |
| 24 | stations. | |
| 25 | ||
| 26 | For example, the =Sports= > =Pro Basketball= > =Shows= category contains | |
| 27 | a number of specific shows related to Professional Basketball. | |
| 28 | ||
| 29 | Aside from being able to play any of the listed stations/shows, you can | |
| 30 | make a channel your favorite by pressing =f=. It will now show up at the | |
| 31 | top of the radio player in the =Favourites= category. | |
| 32 | ||
| 33 | ** Commands/Shortcuts | |
| 34 | | Key(s) | Command | | |
| 35 | |------------+---------------------------------| | |
| 36 | | ↑, ↓ | navigate | | |
| 37 | | PgUp, PgDn | navigate quickly | | |
| 38 | | Home, End | to top/bottom | | |
| 39 | | Enter | open/close folders, play stream | | |
| 40 | | k | stop playing stream | | |
| 41 | | q | quit | | |
| 42 | | f | toggle favourite | | |
| 43 | ||
| 44 | * Installation | |
| 45 | ** Dependencies | |
| 46 | Before installing =curseradio=, a handful of system and Python packages | |
| 47 | are required. To get started, install =python3=, =pip3=, and =mpv= on | |
| 48 | your system. In this example, I'm using Fedora Linux, which uses the | |
| 49 | =dnf= package manager. You may need to adjust this if you're using a | |
| 50 | different system. | |
| 51 | ||
| 52 | #+begin_src sh | |
| 53 | sudo dnf install python3 pip3 mpv | |
| 54 | #+end_src | |
| 55 | ||
| 56 | Next, use =pip3= to install =requests=, =xdg=, and =lxml=: | |
| 57 | ||
| 58 | #+begin_src sh | |
| 59 | pip3 install requests xdg lxml | |
| 60 | #+end_src | |
| 61 | ||
| 62 | ** Repository Source Installation | |
| 63 | Once all the dependencies are installed, we can clone the source code | |
| 64 | and enter that directory: | |
| 65 | ||
| 66 | #+begin_src sh | |
| 67 | git clone https://github.com/chronitis/curseradio && cd curseradio | |
| 68 | #+end_src | |
| 69 | ||
| 70 | Once you're within the =curseradio= directory, you can install the | |
| 71 | application with the provided =setup.py= script. | |
| 72 | ||
| 73 | #+begin_src sh | |
| 74 | sudo python3 setup.py install | |
| 75 | #+end_src | |
| 76 | ||
| 77 | In my case, I ran into a few errors and needed to create the folders | |
| 78 | that curseradio wanted to use for its installation. If you don't get any | |
| 79 | errors, you can skip this and run the app. | |
| 80 | ||
| 81 | #+begin_src sh | |
| 82 | sudo mkdir /usr/local/lib/python3.10/ | |
| 83 | sudo mkdir /usr/local/lib/python3.10/site-packages/ | |
| 84 | #+end_src | |
| 85 | ||
| 86 | #+begin_src sh | |
| 87 | sudo chown -R $USER:$USER /usr/local/lib/python3.10/ | |
| 88 | #+end_src | |
| 89 | ||
| 90 | * Run the Application | |
| 91 | Once fully installed without errors, you can run the application! | |
| 92 | ||
| 93 | #+begin_src sh | |
| 94 | python3 /usr/local/bin/curseradio | |
| 95 | #+end_src | |
blog/customizing-ubuntu/index.org added +195
| @@ -0,0 +1,195 @@ | ||
| 1 | #+title: Beginner's Guide: Customizing Ubuntu | |
| 2 | #+date: 2020-05-19 | |
| 3 | #+description: A beginner's guide to customizing the Ubuntu operating system. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * More Information | |
| 7 | For inspiration on designing your *nix computer, check out the | |
| 8 | [[https://libredd.it/r/unixporn][r/unixporn]] subreddit! | |
| 9 | ||
| 10 | * Customizing Ubuntu | |
| 11 | New to Linux and want to add a personal touch to your machine? One of | |
| 12 | the best perks of Linux is that it is *extremely** customizable. You can | |
| 13 | change the styles of the windows, shell (status bars/docks), icons, | |
| 14 | fonts, terminals, and more. | |
| 15 | ||
| 16 | In this post, I'm going to go through customization on Ubuntu 20.04 | |
| 17 | (GNOME) since most new users tend to choose Ubuntu-based distros. If | |
| 18 | you've found a way to install Arch with i3-gaps, I'm assuming you know | |
| 19 | how to find more advanced tutorials out there on customizations. | |
| 20 | ||
| 21 | ** Required Tools | |
| 22 | #+caption: Gnome Tweaks | |
| 23 | [[https://img.cleberg.net/blog/20200519-customizing-ubuntu/gnome-tweaks-min.png]] | |
| 24 | ||
| 25 | Ubuntu 20.04 ships with the default desktop environment | |
| 26 | [[https://www.gnome.org/][Gnome]], which includes the handy | |
| 27 | =gnome-tweaks= tool to quickly change designs. To install this, just | |
| 28 | open your terminal and enter the following command: | |
| 29 | ||
| 30 | #+begin_src sh | |
| 31 | sudo apt install gnome-tweaks | |
| 32 | #+end_src | |
| 33 | ||
| 34 | After you've finished installing the tool, simply launch the Tweaks | |
| 35 | application, and you'll be able to access the various customization | |
| 36 | options available by default on Ubuntu. You might even like some of the | |
| 37 | pre-installed options. | |
| 38 | ||
| 39 | ** GNOME Application Themes | |
| 40 | To change the themes applied to applications in GNOME, you will need to | |
| 41 | change the Applications dropdown in the Appearance section of Tweaks. To | |
| 42 | add more themes, you will have to find your preferred theme online and | |
| 43 | follow the steps below to have it show up in the Tweaks tool. While you | |
| 44 | may find themes anywhere, one of the most popular sites for GNOME themes | |
| 45 | is [[https://www.gnome-look.org/][gnome-look.org]]. This website | |
| 46 | contains themes for applications, shells, icons, and cursors. | |
| 47 | ||
| 48 | Steps to import themes into Tweaks: | |
| 49 | ||
| 50 | 1. Download the theme. | |
| 51 | 2. These files are usually compressed (.zip, .tar.gz, .tar.xz), so you | |
| 52 | will need to extract the contents. This is easiest when opening the | |
| 53 | file explorer, right-clicking the compressed file, and choosing | |
| 54 | "Extract here." | |
| 55 | 3. Move the theme folder to =/usr/share/themes/=. You can do so with the | |
| 56 | following command: =sudo mv theme-folder/ /usr/share/themes/=. | |
| 57 | - Icons and cursors will be moved to the =/usr/share/icons/= folder. | |
| 58 | - Fonts will be moved to the =/usr/share/fonts/= folder | |
| 59 | Alternatively, you can move them to the | |
| 60 | =/usr/share/fonts/opentype/= or =/usr/share/fonts/opentype/= | |
| 61 | folders, if you have a specific font type. | |
| 62 | 4. Close tweaks if it is open. Re-open Tweaks and your new theme will be | |
| 63 | available in the Applications dropdown in the Appearance section of | |
| 64 | Tweaks. | |
| 65 | ||
| 66 | If the theme is not showing up after you've moved it into the themes | |
| 67 | folder, you may have uncompressed the folder into a sub-folder. You can | |
| 68 | check this by entering the theme folder and listing the contents: | |
| 69 | ||
| 70 | #+begin_src sh | |
| 71 | cd /usr/share/themes/Mojave-Dark && ls -la | |
| 72 | #+end_src | |
| 73 | ||
| 74 | This is an example of what the contents of your theme folder should look | |
| 75 | like. If you just see another folder there, you should move that folder | |
| 76 | up into the =/usr/share/themes/= folder. | |
| 77 | ||
| 78 | #+begin_src sh | |
| 79 | cinnamon COPYING gnome-shell gtk-2.0 gtk-3.0 index.theme metacity-1 plank xfwm4 | |
| 80 | #+end_src | |
| 81 | ||
| 82 | ** GNOME Shell Themes | |
| 83 | To change the appearance of the title bar, default dock, app menu, and | |
| 84 | other parts of the GNOME shell, you'll need to install the | |
| 85 | [[https://extensions.gnome.org/extension/19/user-themes/][user themes]] | |
| 86 | extension on [[https://extensions.gnome.org/][Gnome Extensions]]. To be | |
| 87 | able to install extensions, you will first need to install the browser | |
| 88 | extension that the website instructs you to. See this screenshot for the | |
| 89 | blue box with a link to the extension. | |
| 90 | ||
| 91 | #+caption: Gnome Extensions | |
| 92 | [[https://img.cleberg.net/blog/20200519-customizing-ubuntu/gnome-extensions-min.png]] | |
| 93 | ||
| 94 | After the browser extension is installed, you will need to install the | |
| 95 | native host connector: | |
| 96 | ||
| 97 | #+begin_src sh | |
| 98 | sudo apt install chrome-gnome-shell | |
| 99 | #+end_src | |
| 100 | ||
| 101 | Finally, you can go the | |
| 102 | [[https://extensions.gnome.org/extension/19/user-themes/][user themes]] | |
| 103 | extension page and click the installation button. This will enable the | |
| 104 | Shell option in Tweaks. Now you can move shell themes to the | |
| 105 | =/usr/share/themes= directory, using the same steps mentioned in the | |
| 106 | previous section, and enable the new theme in Tweaks. | |
| 107 | ||
| 108 | ** Icons & Cursors | |
| 109 | Icons and cursors are installed exactly the same way, so I'm grouping | |
| 110 | these together in this post. Both of these items will need to follow the | |
| 111 | same process as installing themes, except you will want to move your | |
| 112 | font folders to the =/usr/share/icons/= directory instead. | |
| 113 | ||
| 114 | ** Fonts | |
| 115 | Fonts are one of the overlooked parts of customization, but a good font | |
| 116 | can make the whole screen look different. For example, I have installed | |
| 117 | the [[https://github.com/IBM/plex/releases][IBM Plex]] fonts on my | |
| 118 | system. This follows the same process as installing themes, except you | |
| 119 | will want to move your font folders to the =/usr/share/fonts/= directory | |
| 120 | instead. | |
| 121 | ||
| 122 | ** Terminal | |
| 123 | If you spend a lot of time typing commands, you know how important the | |
| 124 | style and functionality of the terminal is. After spending a lot of time | |
| 125 | using the default GNOME terminal with | |
| 126 | [[https://en.wikipedia.org/wiki/Bash_(Unix_shell)][unix shell]], I | |
| 127 | decided to try some different options. I ended up choosing | |
| 128 | [[https://terminator-gtk3.readthedocs.io/en/latest/][Terminator]] with | |
| 129 | [[https://en.wikipedia.org/wiki/Z_shell][zsh]]. | |
| 130 | ||
| 131 | Terminator is great if you need to open multiple terminals at one time | |
| 132 | by simply right-clicking and splitting the screen into as many terminals | |
| 133 | as you want. While this project hasn't been updated in a while, | |
| 134 | [[https://github.com/gnome-terminator/terminator/issues/1][it is coming | |
| 135 | under new development]]. However, this terminal is great and I haven't | |
| 136 | experienced any errors yet. | |
| 137 | ||
| 138 | For the shell choice, I decided to choose zsh after trying it out on a | |
| 139 | fresh Manjaro installation. Zsh is great if you like to change the | |
| 140 | themes of your terminal, include icons, or add plugins. | |
| 141 | ||
| 142 | The desktop uses the | |
| 143 | [[https://github.com/zsh-users/zsh-autosuggestions][zsh-autosuggestions]] | |
| 144 | to suggest past commands as you type. In addition, it suggests | |
| 145 | corrections if you misspell a command. Lastly, it uses the =af-magic= | |
| 146 | theme, which adds dashed lines between commands, moving the user@host | |
| 147 | tag to the right side of the terminal, and changes the colors. There are | |
| 148 | plenty of plugins and themes to choose from. Just figure out what you | |
| 149 | like and add it to your =~/.zshrc= file! | |
| 150 | ||
| 151 | *** Steps to Replicate My Terminal | |
| 152 | To install zsh on Ubuntu, enter the following command into a terminal: | |
| 153 | ||
| 154 | #+begin_src sh | |
| 155 | sudo apt install zsh | |
| 156 | #+end_src | |
| 157 | ||
| 158 | Then, enter the next command to activate zsh: | |
| 159 | ||
| 160 | #+begin_src sh | |
| 161 | sudo chsh -s $(which zsh) $(whoami) | |
| 162 | #+end_src | |
| 163 | ||
| 164 | To install Terminator on Ubuntu: | |
| 165 | ||
| 166 | #+begin_src sh | |
| 167 | sudo apt install terminator | |
| 168 | #+end_src | |
| 169 | ||
| 170 | To install Oh My Zsh on Ubuntu: | |
| 171 | ||
| 172 | #+begin_src sh | |
| 173 | sh -c "$(curl -fsSL https://raw.github.com/ohmyzsh/ohmyzsh/master/tools/install.sh)" | |
| 174 | #+end_src | |
| 175 | ||
| 176 | To install zsh-autosuggestions via Oh My Zsh: | |
| 177 | ||
| 178 | #+begin_src sh | |
| 179 | git clone https://github.com/zsh-users/zsh-autosuggestions ${ZSH_CUSTOM:-~/.oh-my-zsh/custom}/plugins/zsh-autosuggestions | |
| 180 | #+end_src | |
| 181 | ||
| 182 | Then, add the following plugin wording to your =~/.zshrc= file (the | |
| 183 | default config usually has the =git= plugin activated, so just add any | |
| 184 | other plugins to the parentheses separated by a space): | |
| 185 | ||
| 186 | #+begin_src sh | |
| 187 | nano ~/.zshrc | |
| 188 | #+end_src | |
| 189 | ||
| 190 | #+begin_src sh | |
| 191 | plugins=(git zsh-autosuggestions) | |
| 192 | #+end_src | |
| 193 | ||
| 194 | Finally, you need to log out of your computer and log back in so your | |
| 195 | user shell can refresh. | |
content/blog/2022-06-22-daily-poetry.md → blog/daily-poetry/index.org renamed +69 −80
| @@ -1,17 +1,14 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-06-22 | |
| 3 | title = "Daily Plaintext Poetry via Email" | |
| 4 | description = "A small project to automatically deliver poetry to your inbox daily." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Source Code | |
| 1 | #+title: Daily Plaintext Poetry via Email | |
| 2 | #+date: 2022-06-22 | |
| 3 | #+description: A small project to automatically deliver poetry to your inbox daily. | |
| 4 | #+filetags: :selfhosting: | |
| 8 | 5 | |
| 6 | * Source Code | |
| 9 | 7 | I don't want to bury the lede here, so if you'd like to see the full |
| 10 | 8 | source code I use to email myself plaintext poems daily, visit the |
| 11 | repository: [daily-poem](https://git.sr.ht/~cmc/daily-poem/). | |
| 12 | ||
| 13 | ## My Daily Dose of Poetry | |
| 9 | repository: [[https://git.cleberg.net/daily-poem.git][daily-poem.git]]. | |
| 14 | 10 | |
| 11 | * My Daily Dose of Poetry | |
| 15 | 12 | Most of my programming projects are small, random projects that are made |
| 16 | 13 | strictly to fix some small problem I have or enhance my quality of life. |
| 17 | 14 | |
| @@ -25,47 +22,43 @@ each morning, as I know I would simply give up and stop reading daily. | ||
| 25 | 22 | Thus, I found a way to deliver poetry to myself in plain-text format, on |
| 26 | 23 | a daily basis, and scheduled to deliver automatically. |
| 27 | 24 | |
| 28 | ## Prerequisites | |
| 29 | ||
| 25 | * Prerequisites | |
| 30 | 26 | This solution uses Python and email, so the following process requires |
| 31 | 27 | the following to be installed: |
| 32 | 28 | |
| 33 | 1. An SMTP server, which can be as easy as installing | |
| 34 | `mailutils` if you're on a Debian-based distro. | |
| 35 | 2. Python (& pip!) | |
| 36 | 3. The following Python packages: `email`, | |
| 37 | `smtplib`, `json`, and `requests` | |
| 38 | ||
| 39 | ## Breaking Down the Logic | |
| 29 | 1. An SMTP server, which can be as easy as installing =mailutils= if | |
| 30 | you're on a Debian-based distro. | |
| 31 | 2. Python (& pip!) | |
| 32 | 3. The following Python packages: =email=, =smtplib=, =json=, and | |
| 33 | =requests= | |
| 40 | 34 | |
| 35 | * Breaking Down the Logic | |
| 41 | 36 | I want to break down the logic for this program, as it's quite simple |
| 42 | 37 | and informational. |
| 43 | 38 | |
| 44 | ### Required Packages | |
| 45 | ||
| 39 | ** Required Packages | |
| 46 | 40 | This program starts with a simple import of the required packages, so I |
| 47 | 41 | wanted to explain why each package is used: |
| 48 | 42 | |
| 49 | ```python | |
| 43 | #+begin_src python | |
| 50 | 44 | from email.mime.text import MIMEText # Required for translating MIMEText |
| 51 | 45 | import smtplib # Required to process the SMTP mail delivery |
| 52 | 46 | import json # Required to parse the poetry API results |
| 53 | 47 | import requests # Required to send out a request to the API |
| 54 | ``` | |
| 55 | ||
| 56 | ### Sending the API Request | |
| 48 | #+end_src | |
| 57 | 49 | |
| 50 | ** Sending the API Request | |
| 58 | 51 | Next, we need to actually send the API request. In my case, I'm calling |
| 59 | 52 | a random poem from the entire API. If you want, you can call specific |
| 60 | 53 | poems or authors from this API. |
| 61 | 54 | |
| 62 | ```python | |
| 55 | #+begin_src python | |
| 63 | 56 | json_data = requests.get('https://poetrydb.org/random').json() |
| 64 | ``` | |
| 57 | #+end_src | |
| 65 | 58 | |
| 66 | 59 | This gives us the following result in JSON: |
| 67 | 60 | |
| 68 | ```json | |
| 61 | #+begin_src json | |
| 69 | 62 | [ |
| 70 | 63 | { |
| 71 | 64 | "title": "Sonnet XXII: With Fools and Children", |
| @@ -91,40 +84,40 @@ This gives us the following result in JSON: | ||
| 91 | 84 | "linecount": "15" |
| 92 | 85 | } |
| 93 | 86 | ] |
| 94 | ``` | |
| 87 | #+end_src | |
| 95 | 88 | |
| 96 | ### Parsing the API Results | |
| 97 | ||
| 98 | In order to parse this into a readable format, we need to use the | |
| 99 | `json` package and extract the fields we want. In the example | |
| 100 | below, I am grabbing every field presented by the API. | |
| 89 | ** Parsing the API Results | |
| 90 | In order to parse this into a readable format, we need to use the =json= | |
| 91 | package and extract the fields we want. In the example below, I am | |
| 92 | grabbing every field presented by the API. | |
| 101 | 93 | |
| 102 | 94 | For the actual poem content, we need to loop over each line in the |
| 103 | `lines` variable since each line is a separate string by | |
| 104 | default. | |
| 105 | ||
| 106 | > You *could* also extract the title or author and make another call out | |
| 107 | > to the API to avoid having to build the plaintext poem with a loop, | |
| 108 | > but it just doesn't make sense to me to send multiple requests when | |
| 109 | > we can create a simple loop on our local machine to work with the data | |
| 110 | > we already have. | |
| 111 | > | |
| 112 | > For | |
| 113 | > [example](https://poetrydb.org/title/Sonnet%20XXII:%20With%20Fools%20and%20Children/lines.text), | |
| 114 | > look at the raw data response of this link to see the poem's lines | |
| 115 | > returned in plaintext. | |
| 116 | ||
| 117 | ```python | |
| 95 | =lines= variable since each line is a separate string by default. | |
| 96 | ||
| 97 | #+begin_quote | |
| 98 | You /could/ also extract the title or author and make another call out | |
| 99 | to the API to avoid having to build the plaintext poem with a loop, but | |
| 100 | it just doesn't make sense to me to send multiple requests when we can | |
| 101 | create a simple loop on our local machine to work with the data we | |
| 102 | already have. | |
| 103 | ||
| 104 | For | |
| 105 | [[https://poetrydb.org/title/Sonnet%20XXII:%20With%20Fools%20and%20Children/lines.text][example]], | |
| 106 | look at the raw data response of this link to see the poem's lines | |
| 107 | returned in plaintext. | |
| 108 | ||
| 109 | #+end_quote | |
| 110 | ||
| 111 | #+begin_src python | |
| 118 | 112 | title = json_data[0]['title'] |
| 119 | 113 | author = json_data[0]['author'] |
| 120 | 114 | line_count = json_data[0]['linecount'] |
| 121 | 115 | lines = '' |
| 122 | 116 | for line in json_data[0]['lines']: |
| 123 | 117 | lines = lines + line + "\n" |
| 124 | ``` | |
| 125 | ||
| 126 | ### Composing the Email | |
| 118 | #+end_src | |
| 127 | 119 | |
| 120 | ** Composing the Email | |
| 128 | 121 | Now that I have all the data I need, I just need to compose it into a |
| 129 | 122 | message and prepare the message metadata. |
| 130 | 123 | |
| @@ -133,43 +126,41 @@ by the author, then a blank line, and finally the full poem. This code | ||
| 133 | 126 | snippet combines that data and packages it into a MIMEText container, |
| 134 | 127 | ready to be emailed. |
| 135 | 128 | |
| 136 | ```python | |
| 129 | #+begin_src python | |
| 137 | 130 | msg_body = title + "\n" + author + "\n\n" + lines |
| 138 | 131 | msg = MIMEText(msg_body) |
| 139 | ``` | |
| 132 | #+end_src | |
| 140 | 133 | |
| 141 | 134 | Before we send the email, we need to prepare the metadata (subject, |
| 142 | 135 | from, to, etc.): |
| 143 | 136 | |
| 144 | ```python | |
| 137 | #+begin_src python | |
| 145 | 138 | sender_email = 'example@server.local' |
| 146 | 139 | recipient_emails = ['user@example.com'] |
| 147 | 140 | msg['Subject'] = 'Your Daily Poem (' + line_count + ' lines)' |
| 148 | 141 | msg['From'] = sender_email |
| 149 | 142 | msg['To'] = recipient_email |
| 150 | ``` | |
| 151 | ||
| 152 | ### Sending the Email | |
| 143 | #+end_src | |
| 153 | 144 | |
| 145 | ** Sending the Email | |
| 154 | 146 | Now that I have everything ready to be emailed, the last step is to |
| 155 | 147 | simply connect to an SMTP server and send the email out to the |
| 156 | recipients. In my case, I installed `mailutils` on Ubuntu and | |
| 157 | let my SMTP server be `localhost`. | |
| 148 | recipients. In my case, I installed =mailutils= on Ubuntu and let my | |
| 149 | SMTP server be =localhost=. | |
| 158 | 150 | |
| 159 | ```python | |
| 151 | #+begin_src python | |
| 160 | 152 | smtp_server = 'localhost' |
| 161 | 153 | s = smtplib.SMTP(smtp_server) |
| 162 | 154 | s.sendmail(sender_email, recipient_emails, msg.as_string()) |
| 163 | 155 | s.quit() |
| 164 | ``` | |
| 165 | ||
| 166 | ## The Result! | |
| 156 | #+end_src | |
| 167 | 157 | |
| 168 | Instead of including a screenshot, I've copied the contents of the | |
| 169 | email that was delivered to my inbox below since I set this process up | |
| 170 | in plaintext format. | |
| 158 | * The Result! | |
| 159 | Instead of including a screenshot, I've copied the contents of the email | |
| 160 | that was delivered to my inbox below since I set this process up in | |
| 161 | plaintext format. | |
| 171 | 162 | |
| 172 | ```txt | |
| 163 | #+begin_src txt | |
| 173 | 164 | Date: Wed, 22 Jun 2022 14:37:19 +0000 (UTC) |
| 174 | 165 | From: REDACTED |
| 175 | 166 | To: REDACTED |
| @@ -195,25 +186,23 @@ You that behold us, laugh us not to scorn; | ||
| 195 | 186 | Give Nature thanks you are not such as we. |
| 196 | 187 | Yet fools and children sometimes tell in play |
| 197 | 188 | Some, wise in show, more fools indeed than they. |
| 198 | ``` | |
| 199 | ||
| 200 | ## Scheduling the Daily Email | |
| 189 | #+end_src | |
| 201 | 190 | |
| 202 | Last, but not least, is scheduling this Python script with | |
| 203 | `crontab`. To schedule a script to run daily, you can add it | |
| 204 | to the `crontab` file. To do this, open `crontab` | |
| 205 | in editing mode: | |
| 191 | * Scheduling the Daily Email | |
| 192 | Last, but not least, is scheduling this Python script with =crontab=. To | |
| 193 | schedule a script to run daily, you can add it to the =crontab= file. To | |
| 194 | do this, open =crontab= in editing mode: | |
| 206 | 195 | |
| 207 | ```sh | |
| 196 | #+begin_src sh | |
| 208 | 197 | crontab -e |
| 209 | ``` | |
| 198 | #+end_src | |
| 210 | 199 | |
| 211 | 200 | In the file, simply paste the following snippet at the bottom of the |
| 212 | 201 | file and ensure that the file path is correctly pointing to wherever you |
| 213 | 202 | saved your Python script: |
| 214 | 203 | |
| 215 | ```config | |
| 216 | 0 8 * * * python3 /home/<your_user>/dailypoem/main.py | |
| 217 | ``` | |
| 204 | #+begin_src config | |
| 205 | 0 8 ** ** ** python3 /home/<your_user>/dailypoem/main.py | |
| 206 | #+end_src | |
| 218 | 207 | |
| 219 | 208 | We have now set up the script and scheduled it to run daily at 08:00! |
content/blog/2022-02-16-debian-and-nginx.md → blog/debian-and-nginx/index.org renamed +65 −73
| @@ -1,13 +1,11 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-02-16 | |
| 3 | title = "Migrating to a New Web Server Setup with Debian, Nginx, and Agate" | |
| 4 | description = "A retrospective on my recent server migration." | |
| 5 | +++ | |
| 1 | #+title: Migrating to a New Web Server Setup with Debian, Nginx, and Agate | |
| 2 | #+date: 2022-02-16 | |
| 3 | #+description: A retrospective on my recent server migration. | |
| 4 | #+filetags: :sysadmin: | |
| 6 | 5 | |
| 7 | ## Server OS: Debian | |
| 8 | ||
| 9 |  | |
| 6 | * Server OS: Debian | |
| 7 | #+caption: Debian + neofetch | |
| 8 | [[https://img.cleberg.net/blog/20220216-migrating-to-debian-and-nginx/neofetch.png]] | |
| 11 | 9 | |
| 12 | 10 | I've used various Linux distributions throughout the years, but I've |
| 13 | 11 | never used anything except Ubuntu for my servers. Why? I really have no |
| @@ -16,62 +14,61 @@ idea, mostly just comfort around the commands and software availability. | ||
| 16 | 14 | However, I have always wanted to try Debian as a server OS after testing |
| 17 | 15 | it out in a VM a few years ago (side-note: I'd love to try Alpine too, |
| 18 | 16 | but I always struggle with compatibility). So, I decided to launch a new |
| 19 | VPS and use [Debian](https://www.debian.org) 11 as the OS. Spoiler | |
| 17 | VPS and use [[https://www.debian.org][Debian]] 11 as the OS. Spoiler | |
| 20 | 18 | alert: it feels identical to Ubuntu for my purposes. |
| 21 | 19 | |
| 22 | 20 | I did the normal things when first launching the VPS, such as adding a |
| 23 | 21 | new user, locking down SSH, etc. If you want to see that level of |
| 24 | detail, read my other post about [How to Set Up a VPS Web | |
| 25 | Server](https://cleberg.net/blog/how-to-set-up-a-vps-web-server/). | |
| 22 | detail, read my other post about | |
| 23 | [[https://cleberg.net/blog/how-to-set-up-a-vps-web-server/][How to Set | |
| 24 | Up a VPS Web Server]]. | |
| 26 | 25 | |
| 27 | 26 | All of this has been similar, apart from small things such as the |
| 28 | 27 | location of users' home folders. No complaints at all from me - Debian |
| 29 | 28 | seems great. |
| 30 | 29 | |
| 31 | ## Web Server: Nginx | |
| 32 | ||
| 33 |  | |
| 30 | * Web Server: Nginx | |
| 31 | #+caption: Nginx status | |
| 32 | [[https://img.cleberg.net/blog/20220216-migrating-to-debian-and-nginx/nginx.png]] | |
| 35 | 33 | |
| 36 | 34 | Once I had the baseline server configuration set-up for Debian, I moved |
| 37 | on to trying out [Nginx](https://nginx.org) as my web server software. | |
| 38 | This required me to install the `nginx` and `ufw` | |
| 39 | packages, as well as setting up the initial UFW config: | |
| 35 | on to trying out [[https://nginx.org][Nginx]] as my web server software. | |
| 36 | This required me to install the =nginx= and =ufw= packages, as well as | |
| 37 | setting up the initial UFW config: | |
| 40 | 38 | |
| 41 | ```sh | |
| 39 | #+begin_src sh | |
| 42 | 40 | sudo apt install nginx ufw |
| 43 | 41 | sudo ufw allow 'Nginx Full' |
| 44 | 42 | sudo ufw allow SSH |
| 45 | 43 | sudo ufw enable |
| 46 | 44 | sudo ufw status |
| 47 | 45 | sudo systemctl status nginx |
| 48 | ``` | |
| 46 | #+end_src | |
| 49 | 47 | |
| 50 | 48 | Once I had the firewall set, I moved on to creating the directories and |
| 51 | 49 | files for my website. This is very easy and is basically the same as |
| 52 | 50 | setting up an Apache server, so no struggles here. |
| 53 | 51 | |
| 54 | ```sh | |
| 52 | #+begin_src sh | |
| 55 | 53 | sudo mkdir -p /var/www/your_domain/html |
| 56 | 54 | sudo chown -R $USER:$USER /var/www/your_domain/html |
| 57 | 55 | sudo chmod -R 755 /var/www/your_domain |
| 58 | 56 | nano /var/www/your_domain/html/index.html |
| 59 | ``` | |
| 57 | #+end_src | |
| 60 | 58 | |
| 61 | 59 | The next part, creating the Nginx configuration files, is quite a bit |
| 62 | 60 | different from Apache. First, you need to create the files in the |
| 63 | `sites-available` folder and symlink it the | |
| 64 | `sites-enabled` folder. | |
| 61 | =sites-available= folder and symlink it the =sites-enabled= folder. | |
| 65 | 62 | |
| 66 | 63 | Creating the config file for your domain: |
| 67 | 64 | |
| 68 | ```sh | |
| 65 | #+begin_src sh | |
| 69 | 66 | sudo nano /etc/nginx/sites-available/your_domain |
| 70 | ``` | |
| 67 | #+end_src | |
| 71 | 68 | |
| 72 | 69 | Default content for an Nginx config file: |
| 73 | 70 | |
| 74 | ```sh | |
| 71 | #+begin_src sh | |
| 75 | 72 | server { |
| 76 | 73 | listen 80; |
| 77 | 74 | listen [::]:80; |
| @@ -85,45 +82,43 @@ server { | ||
| 85 | 82 | try_files $uri $uri/ =404; |
| 86 | 83 | } |
| 87 | 84 | } |
| 88 | ``` | |
| 85 | #+end_src | |
| 89 | 86 | |
| 90 | 87 | Finally, symlink it together: |
| 91 | 88 | |
| 92 | ```sh | |
| 89 | #+begin_src sh | |
| 93 | 90 | sudo ln -s /etc/nginx/sites-available/your_domain /etc/nginx/sites-enabled/ |
| 94 | ``` | |
| 91 | #+end_src | |
| 95 | 92 | |
| 96 | 93 | This will make your site available to the public (as long as you have |
| 97 | `your_domain` DNS records pointed at the server's IP | |
| 98 | address)! | |
| 94 | =your_domain= DNS records pointed at the server's IP address)! | |
| 99 | 95 | |
| 100 | Next, I used [certbot](https://certbot.eff.org/) to issue an HTTPS | |
| 96 | Next, I used [[https://certbot.eff.org/][certbot]] to issue an HTTPS | |
| 101 | 97 | certificate for my domains using the following commands: |
| 102 | 98 | |
| 103 | ```sh | |
| 99 | #+begin_src sh | |
| 104 | 100 | sudo apt install snapd; sudo snap install core; sudo snap refresh core |
| 105 | 101 | sudo snap install --classic certbot |
| 106 | 102 | sudo ln -s /snap/bin/certbot /usr/bin/certbot |
| 107 | 103 | sudo certbot --nginx |
| 108 | ``` | |
| 104 | #+end_src | |
| 109 | 105 | |
| 110 | 106 | Now that certbot ran successfully and updated my Nginx config files to |
| 111 | include a `443` server block of code, I went back in and | |
| 112 | edited the config file to include security HTTP headers. This part is | |
| 113 | optional, but is recommended for security purposes; you can even test a | |
| 114 | website's HTTP header security at [Security | |
| 115 | Headers](https://securityheaders.com/). | |
| 107 | include a =443= server block of code, I went back in and edited the | |
| 108 | config file to include security HTTP headers. This part is optional, but | |
| 109 | is recommended for security purposes; you can even test a website's HTTP | |
| 110 | header security at [[https://securityheaders.com/][Security Headers]]. | |
| 116 | 111 | |
| 117 | 112 | The configuration below shows a set-up where you only want your website |
| 118 | 113 | to serve content from its own domain, except for images and scripts, |
| 119 | which may come from `nullitics.com`. All other content would | |
| 120 | be blocked from loading in a browser. | |
| 114 | which may come from =nullitics.com=. All other content would be blocked | |
| 115 | from loading in a browser. | |
| 121 | 116 | |
| 122 | ```sh | |
| 117 | #+begin_src sh | |
| 123 | 118 | sudo nano /etc/nginx/sites-available/your_domain |
| 124 | ``` | |
| 119 | #+end_src | |
| 125 | 120 | |
| 126 | ```sh | |
| 121 | #+begin_src sh | |
| 127 | 122 | server { |
| 128 | 123 | ... |
| 129 | 124 | add_header Content-Security-Policy "default-src 'none'; img-src 'self' https://nullitics.com; script-src 'self' https://nullitics.com; style-src 'self'; font-src 'self'"; |
| @@ -134,47 +129,44 @@ server { | ||
| 134 | 129 | add_header Referrer-Policy "no-referrer"; |
| 135 | 130 | ... |
| 136 | 131 | } |
| 137 | ``` | |
| 132 | #+end_src | |
| 138 | 133 | |
| 139 | ```sh | |
| 134 | #+begin_src sh | |
| 140 | 135 | sudo systemctl restart nginx |
| 141 | ``` | |
| 142 | ||
| 143 | ### Nginx vs. Apache | |
| 136 | #+end_src | |
| 144 | 137 | |
| 138 | ** Nginx vs. Apache | |
| 145 | 139 | As I stated at the beginning, my historical hesitation with trying Nginx |
| 146 | 140 | was that the differences in configuration formats scared me away from |
| 147 | 141 | leaving Apache. However, I prefer Nginx to Apache for a few reasons: |
| 148 | 142 | |
| 149 | 1. Nginx uses only one config file (`your_domain`) | |
| 150 | vs. Apache's two-file approach for HTTP vs. HTTPS | |
| 151 | (`your_domain.conf` and | |
| 152 | `your_domain-le-ssl.conf`). | |
| 153 | 2. Symlinking new configurations files and reloading Nginx are way | |
| 154 | easier than Apache's process of having to enable headers with | |
| 155 | `a2enmod mod_headers`, enable PHP with | |
| 156 | `a2enmod php` (plus any other mods you need), and then | |
| 157 | enabling sites with `a2ensite`, and THEN reloading | |
| 158 | Apache. | |
| 159 | 3. The contents of the Nginx config files seem more organized and | |
| 160 | logical with the curly-bracket approach. This is a minor reason, but | |
| 161 | everything just felt cleaner while I was installing my sites and | |
| 162 | that had a big quality of life impact on the installation for me. | |
| 143 | 1. Nginx uses only one config file (=your_domain=) vs. Apache's two-file | |
| 144 | approach for HTTP vs. HTTPS (=your_domain.conf= and | |
| 145 | =your_domain-le-ssl.conf=). | |
| 146 | 2. Symlinking new configurations files and reloading Nginx are way | |
| 147 | easier than Apache's process of having to enable headers with | |
| 148 | =a2enmod mod_headers=, enable PHP with =a2enmod php= (plus any other | |
| 149 | mods you need), and then enabling sites with =a2ensite=, and THEN | |
| 150 | reloading Apache. | |
| 151 | 3. The contents of the Nginx config files seem more organized and | |
| 152 | logical with the curly-bracket approach. This is a minor reason, but | |
| 153 | everything just felt cleaner while I was installing my sites and that | |
| 154 | had a big quality of life impact on the installation for me. | |
| 163 | 155 | |
| 164 | 156 | They're both great software packages, but Nginx just seems more |
| 165 | 157 | organized and easier to use these days. I will certainly be exploring |
| 166 | 158 | the Nginx docs to see what other fun things I can do with all of this. |
| 167 | 159 | |
| 168 | ## Gemini Server: Agate | |
| 169 | ||
| 170 |  | |
| 160 | * Gemini Server: Agate | |
| 161 | #+caption: Agate status | |
| 162 | [[https://img.cleberg.net/blog/20220216-migrating-to-debian-and-nginx/agate.png]] | |
| 172 | 163 | |
| 173 | 164 | Finally, I set up the Agate software on this server again to host my |
| 174 | 165 | Gemini server content, using Rust as I have before. You can read my |
| 175 | other post for more information on installing Agate: [Hosting a Gemini | |
| 176 | Server](https://cleberg.net/blog/hosting-a-gemini-server/). | |
| 166 | other post for more information on installing Agate: | |
| 167 | [[https://cleberg.net/blog/hosting-a-gemini-server/][Hosting a Gemini | |
| 168 | Server]]. | |
| 177 | 169 | |
| 178 | 170 | All in all, Debian + Nginx is very slick and I prefer it over my old |
| 179 | combination of Ubuntu + Apache (although it's really just Nginx \> | |
| 180 | Apache for me, since Debian seems mostly the same as Ubuntu is so far). | |
| 171 | combination of Ubuntu + Apache (although it's really just Nginx > Apache | |
| 172 | for me, since Debian seems mostly the same as Ubuntu is so far). | |
content/blog/2021-07-15-delete-gitlab-repos.md → blog/delete-gitlab-repos/index.org renamed +28 −33
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-07-15 | |
| 3 | title = "How to Delete All GitLab Repositories" | |
| 4 | description = "Learn how to delete all GitLab repositories in your account." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Background | |
| 1 | #+title: How to Delete All GitLab Repositories | |
| 2 | #+date: 2021-07-15 | |
| 3 | #+description: Learn how to delete all GitLab repositories in your account. | |
| 4 | #+filetags: :dev: | |
| 8 | 5 | |
| 6 | * Background | |
| 9 | 7 | Have you ever used GitLab to host your source code, moved to a different |
| 10 | 8 | host, and wanted to delete everything from your GitLab account? Well, |
| 11 | 9 | this post covers any scenario where you would want to delete all |
| @@ -16,37 +14,34 @@ manually delete them whenever I switch host. GitHub has a few different | ||
| 16 | 14 | tools online to delete all repositories for you, but I have not found |
| 17 | 15 | anything similar for GitLab, so I needed an alternative solution. |
| 18 | 16 | |
| 19 | ## Use a Python Script | |
| 20 | ||
| 21 | ### Requirements | |
| 22 | ||
| 17 | * Use a Python Script | |
| 18 | ** Requirements | |
| 23 | 19 | Before we look at the script, make sure you know your GitLab username. |
| 24 | Next, [create an authorization | |
| 25 | token](https://gitlab.com/-/profile/personal_access_tokens) so that the | |
| 26 | Python script can delete your repositories. Don't lose this token or | |
| 27 | else you'll need to create a new one. | |
| 28 | ||
| 29 | ### Create the Script | |
| 20 | Next, [[https://gitlab.com/-/profile/personal_access_tokens][create an | |
| 21 | authorization token]] so that the Python script can delete your | |
| 22 | repositories. Don't lose this token or else you'll need to create a new | |
| 23 | one. | |
| 30 | 24 | |
| 25 | ** Create the Script | |
| 31 | 26 | To run a Python script, you must first create it. Open a terminal and |
| 32 | 27 | enter the following commands in whichever directory you prefer to store |
| 33 | 28 | the script. You can do the same things in a file manager if you prefer. |
| 34 | 29 | |
| 35 | ```sh | |
| 30 | #+begin_src sh | |
| 36 | 31 | mkdir delete-gitlab |
| 37 | ``` | |
| 32 | #+end_src | |
| 38 | 33 | |
| 39 | ```sh | |
| 34 | #+begin_src sh | |
| 40 | 35 | cd delete-gitlab |
| 41 | ``` | |
| 36 | #+end_src | |
| 42 | 37 | |
| 43 | ```sh | |
| 38 | #+begin_src sh | |
| 44 | 39 | nano main.py |
| 45 | ``` | |
| 40 | #+end_src | |
| 46 | 41 | |
| 47 | Enter the following code into your `main.py` script. | |
| 42 | Enter the following code into your =main.py= script. | |
| 48 | 43 | |
| 49 | ```python | |
| 44 | #+begin_src python | |
| 50 | 45 | import request |
| 51 | 46 | import json |
| 52 | 47 | |
| @@ -100,16 +95,16 @@ def main(): | ||
| 100 | 95 | |
| 101 | 96 | if __name__ == "__main__": |
| 102 | 97 | main() |
| 103 | ``` | |
| 98 | #+end_src | |
| 104 | 99 | |
| 105 | Now that you have the proper information, replace `{user-id}` | |
| 106 | with your GitLab username and `{auth-token}` with the | |
| 107 | authorization token you created earlier. | |
| 100 | Now that you have the proper information, replace ={user-id}= with your | |
| 101 | GitLab username and ={auth-token}= with the authorization token you | |
| 102 | created earlier. | |
| 108 | 103 | |
| 109 | 104 | Finally, simply run the script and watch the output. You can also use |
| 110 | PyCharm Community Edition to edit and run the Python script if you | |
| 111 | don't want to work in a terminal. | |
| 105 | PyCharm Community Edition to edit and run the Python script if you don't | |
| 106 | want to work in a terminal. | |
| 112 | 107 | |
| 113 | ```sh | |
| 108 | #+begin_src sh | |
| 114 | 109 | python3 main.py |
| 115 | ``` | |
| 110 | #+end_src | |
blog/digital-minimalism/index.org added +100
| @@ -0,0 +1,100 @@ | ||
| 1 | #+title: Digital Minimalism | |
| 2 | #+date: 2023-10-04 | |
| 3 | #+description: My personal retrospective on digital minimalism. | |
| 4 | #+filetags: :personal: | |
| 5 | ||
| 6 | I've written [[/wiki/#digital-garden][a note about minimalism]] before, | |
| 7 | but I wanted to dedicate some time to reflect on digital minimalism and | |
| 8 | how I've been able to minimize the impact of digital devices in my life. | |
| 9 | ||
| 10 | #+begin_quote | |
| 11 | These changes crept up on us and happened fast, before we had a chance | |
| 12 | to step back and ask what we really wanted out of the rapid advances of | |
| 13 | the past decade. We added new technologies to the periphery of our | |
| 14 | experience for minor reasons, then woke one morning to discover that | |
| 15 | they had colonized the core of our daily life. We didn't, in other | |
| 16 | words, sign up for the digital world in which we're currently | |
| 17 | entrenched; we seem to have stumbled backward into it. | |
| 18 | ||
| 19 | /(Digital Minimalism, 2019)/ | |
| 20 | ||
| 21 | #+end_quote | |
| 22 | ||
| 23 | * The Principles of Digital Minimalism | |
| 24 | As noted in Cal Newport's book, /Digital Minimalism/, there are three | |
| 25 | main principles to digital minimalism that I tend to agree with: | |
| 26 | ||
| 27 | 1. Clutter is costly. | |
| 28 | - Digital minimalists recognize that cluttering their time and | |
| 29 | attention with too many devices, apps, and services creates an | |
| 30 | overall negative cost that can swamp the small benefits that each | |
| 31 | individual item provides in isolation. | |
| 32 | 2. Optimization is important. | |
| 33 | - Digital minimalists believe that deciding a particular technology | |
| 34 | supports something they value is only the first step. To truly | |
| 35 | extract its full potential benefit, it's necessary to think | |
| 36 | carefully about how they'll use the technology. | |
| 37 | 3. Intentionality is satisfying. | |
| 38 | - Digital minimalists derive significant satisfaction from their | |
| 39 | general commitment to being more intentional about how they engage | |
| 40 | with new technologies. This source of satisfaction is independent | |
| 41 | of the specific decisions they make and is one of the biggest | |
| 42 | reasons that minimalism tends to be immensely meaningful to its | |
| 43 | practitioners. | |
| 44 | ||
| 45 | * Taking Action | |
| 46 | In order to put the logic into practice, I've created a few new habits | |
| 47 | and continued performing old habits that are working well: | |
| 48 | ||
| 49 | ** Using Devices With Intention | |
| 50 | - I already rarely use "social media", mostly limited to forums such as | |
| 51 | Hacker News and Tildes, so I've just tweaked my behavior to stop | |
| 52 | looking for content in those places when I'm bored. | |
| 53 | - Use devices with intention. Each time I pick up a digital device, | |
| 54 | there should be an intention to use the device to improve my current | |
| 55 | situation. No more endless scrolling or searching for something to | |
| 56 | interest me. | |
| 57 | ||
| 58 | ** Prevent Distractions | |
| 59 | - Disable (most) notifications on all devices. I spent 15-30 minutes | |
| 60 | going through the notifications on my phone, watch, and computer to | |
| 61 | ensure that only a select few apps have the ability to interrupt me: | |
| 62 | Calendar, Messages, Phone, Reminders, & Signal. | |
| 63 | - Disable badges for any apps except the ones mentioned in the bullet | |
| 64 | above. | |
| 65 | - Set-up focus profiles across devices so that I can enable different | |
| 66 | modes, such as Personal when I only want to see notifications from | |
| 67 | people I care about or Do Not Disturb, where absolutely nothing can | |
| 68 | interrupt me. | |
| 69 | - Clean up my home screens. This one was quite easy as I already | |
| 70 | maintain a minimalist set-up, but I went extreme by limiting my phone | |
| 71 | to just eight apps on the home screen and four in the dock. If I need | |
| 72 | another app, I'll have to search or use the app library. | |
| 73 | - Remove the work profile from my phone. This was a tough decision as | |
| 74 | having my work profile on my device definitely makes my life easier at | |
| 75 | times, but it also has quite a negative effect when I'm "always | |
| 76 | online" and can see the notifications and team activity 24/7. I | |
| 77 | believe creating a distinct barrier between my work and personal | |
| 78 | devices will be beneficial in the end. | |
| 79 | ||
| 80 | ** Creating Alternative Activities | |
| 81 | This is the most difficult piece, as most of my hobbies and interests | |
| 82 | lie in the digital world. However, I'm making a concerted effort to put | |
| 83 | devices down unless necessary and force myself to perform other | |
| 84 | activities in the physical world instead. | |
| 85 | ||
| 86 | I've started with a few basics that are always readily available to me: | |
| 87 | ||
| 88 | - Do a chore, such as organizing or cleaning. | |
| 89 | - Read a book, study a piece of art, etc. | |
| 90 | - Exercise or get outdoors. | |
| 91 | - Participate in a hobby, such as photography, birding, disc golf, etc. | |
| 92 | - Let yourself be bored and wander into creativity. | |
| 93 | ||
| 94 | * Making Progress | |
| 95 | I'll be taking notes as I continue down this journey and hope to see | |
| 96 | positive trends. I've always been a minimalist in the physical world and | |
| 97 | it feels refreshing to filter out the clutter that has come to dominate | |
| 98 | my digital life over the years. | |
| 99 | ||
| 100 | I'm excited to see where this journey leads. | |
content/blog/2022-06-01-ditching-cloudflare.md → blog/ditching-cloudflare/index.org renamed +36 −41
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-06-01 | |
| 3 | title = "Ditching Cloudflare for Njalla" | |
| 4 | description = "A retrospective on my decision to leave Cloudflare and move to Njalla for domain registration and DNS." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Registrar | |
| 1 | #+title: Ditching Cloudflare for Njalla | |
| 2 | #+date: 2022-06-01 | |
| 3 | #+description: A retrospective on my decision to leave Cloudflare and move to Njalla for domain registration and DNS. | |
| 4 | #+filetags: :sysadmin: | |
| 8 | 5 | |
| 6 | * Registrar | |
| 9 | 7 | After spending a year or so using Cloudflare for DNS only - no proxying |
| 10 | 8 | or applications - I spent the last few months using Cloudflare Tunnels |
| 11 | 9 | and Cloudflare Access to protect my self-hosted websites and |
| @@ -15,22 +13,24 @@ However, I have never liked using Cloudflare due to their increasingly | ||
| 15 | 13 | large share of control over web traffic, as well as their business model |
| 16 | 14 | of being a MITM for all of your traffic. |
| 17 | 15 | |
| 18 | So, as of today, I have switched over to [Njalla](https://njal.la) as my | |
| 19 | registrar and DNS manager. I was able to easily transfer my domains over | |
| 20 | rapidly, with only one domain taking more than 15-30 minutes to | |
| 16 | So, as of today, I have switched over to [[https://njal.la][Njalla]] as | |
| 17 | my registrar and DNS manager. I was able to easily transfer my domains | |
| 18 | over rapidly, with only one domain taking more than 15-30 minutes to | |
| 21 | 19 | propagate. |
| 22 | 20 | |
| 23 | 21 | +I do still have two domains sitting at Cloudflare for the moment while |
| 24 | 22 | I decide if they're worth the higher rates (one domain is 30€ and the |
| 25 | 23 | other is 45€).+ |
| 26 | 24 | |
| 27 | > **Update (2022.06.03)**: I ended up transferring my final two domains | |
| 28 | > over to Njalla, clearing my Cloudflare account of personal data, and | |
| 29 | > deleting the Cloudflare account entirely. *I actually feel relieved to | |
| 30 | > have moved on to a provider I trust.* | |
| 25 | #+begin_quote | |
| 26 | *Update (2022.06.03)*: I ended up transferring my final two domains over | |
| 27 | to Njalla, clearing my Cloudflare account of personal data, and deleting | |
| 28 | the Cloudflare account entirely. /I actually feel relieved to have moved | |
| 29 | on to a provider I trust./ | |
| 31 | 30 | |
| 32 | ## DNS | |
| 31 | #+end_quote | |
| 33 | 32 | |
| 33 | * DNS | |
| 34 | 34 | As noted above, I'm using Njalla exclusively for DNS configurations on |
| 35 | 35 | my domains. |
| 36 | 36 | |
| @@ -42,48 +42,43 @@ back in one-by-one. | ||
| 42 | 42 | |
| 43 | 43 | This would be much simpler if I were able to edit the plain-text format |
| 44 | 44 | of the DNS configuration. I was able to do that at a past registrar |
| 45 | (perhaps it was [Gandi.net](https://gandi.net/)?) and it made life a lot | |
| 46 | easier. | |
| 47 | ||
| 48 | ### Dynamic DNS Updates | |
| 45 | (perhaps it was [[https://gandi.net/][Gandi.net]]?) and it made life a | |
| 46 | lot easier. | |
| 49 | 47 | |
| 50 | I have built an easy Python script to run (or set-up in | |
| 51 | `cron` to run automatically) that will check my server's | |
| 52 | IPv4 and IPv6, compare it to Njalla, and update the DNS records if they | |
| 53 | don't match. You can see the full script and process in my other post: | |
| 54 | [Updating Dynamic DNS with Njalla API](/blog/njalla-dns-api/). | |
| 48 | ** Dynamic DNS Updates | |
| 49 | I have built an easy Python script to run (or set-up in =cron= to run | |
| 50 | automatically) that will check my server's IPv4 and IPv6, compare it to | |
| 51 | Njalla, and update the DNS records if they don't match. You can see the | |
| 52 | full script and process in my other post: | |
| 53 | [[../njalla-dns-api/][Updating Dynamic DNS with Njalla API]]. | |
| 55 | 54 | |
| 56 | 55 | I haven't used this other method, but I do know that you can create |
| 57 | `Dynamic` DNS records with Njalla that [work for updating | |
| 58 | dynamic subdomains](https://njal.la/docs/ddns/). | |
| 59 | ||
| 60 | ### Njalla's DNS Tool | |
| 56 | =Dynamic= DNS records with Njalla that | |
| 57 | [[https://njal.la/docs/ddns/][work for updating dynamic subdomains]]. | |
| 61 | 58 | |
| 62 | One neat upside to Njalla is that they have a [DNS lookup | |
| 63 | tool](https://check.njal.la/dns/) that provides a lot of great | |
| 64 | information for those of you (AKA: me) who hate using the | |
| 65 | `dig` command. | |
| 59 | ** Njalla's DNS Tool | |
| 60 | One neat upside to Njalla is that they have a | |
| 61 | [[https://check.njal.la/dns/][DNS lookup tool]] that provides a lot of | |
| 62 | great information for those of you (AKA: me) who hate using the =dig= | |
| 63 | command. | |
| 66 | 64 | |
| 67 | 65 | This was very useful for monitoring a couple of my transferred domains |
| 68 | 66 | to see when the changes in nameservers, records, and DNSSEC went into |
| 69 | 67 | effect. |
| 70 | 68 | |
| 71 | ## Tunnel | |
| 72 | ||
| 69 | * Tunnel | |
| 73 | 70 | Cloudflare Tunnel is a service that acts as a reverse-proxy (hosted on |
| 74 | 71 | Cloudflare's servers) and allowed me to mask the private IP address of |
| 75 | 72 | the server hosting my various websites and apps. |
| 76 | 73 | |
| 77 | 74 | However, as I was moving away from Cloudflare, I was not able to find a |
| 78 | 75 | suitable replacement that was both inexpensive and simple. So, I simply |
| 79 | went back to hosting [my own reverse proxy with | |
| 80 | Nginx](/blog/set-up-nginx-reverse-proxy/). With the recent | |
| 81 | additions of Unifi hardware in my server/network rack, I am much more | |
| 82 | protected against spam and malicious attacks at the network edge than I | |
| 83 | was before I switched to Cloudflare. | |
| 84 | ||
| 85 | ## Access | |
| 76 | went back to hosting [[/blog/set-up-nginx-reverse-proxy/][my own reverse | |
| 77 | proxy with Nginx]]. With the recent additions of Unifi hardware in my | |
| 78 | server/network rack, I am much more protected against spam and malicious | |
| 79 | attacks at the network edge than I was before I switched to Cloudflare. | |
| 86 | 80 | |
| 81 | * Access | |
| 87 | 82 | Cloudflare Access, another app I used in combination with Cloudflare |
| 88 | 83 | Tunnel, provided an authentication screen that required you to enter |
| 89 | 84 | valid credentials before Cloudflare would forward you to the actual |
blog/dont-say-hello/index.org added +26
| @@ -0,0 +1,26 @@ | ||
| 1 | #+title: Don't Say Hello | |
| 2 | #+date: 2024-01-08 | |
| 3 | #+description: A short post describing my displeasure with cliffhanger conversations. | |
| 4 | #+filetags: :personal: | |
| 5 | ||
| 6 | I recently came back from a winter break and have started working | |
| 7 | again... only to immediately run into the dilemma of people sending me | |
| 8 | cliffhanger messages again. | |
| 9 | ||
| 10 | * No Hello | |
| 11 | A year or two ago, I discovered [[https://nohello.net/en/][no hello]] | |
| 12 | and have thought about it often since then. I've even sent it to a few | |
| 13 | people since then (who wouldn't take offense to it). | |
| 14 | ||
| 15 | I work in a fast-paced environment where efficiency is extremely | |
| 16 | valuable. Therefore, I have always held a deep displeasure for | |
| 17 | conversations where people start with "Hello" and then. | |
| 18 | ||
| 19 | I searched back through my work messages and found that I received ~50 | |
| 20 | messages from ~10 people last year from people that contained "hi", | |
| 21 | "hey", or "hello" and did not contain any indication of the purpose of | |
| 22 | the conversation. I also noticed that a few of the users were | |
| 23 | responsible for the large majority of the cliffhangers. | |
| 24 | ||
| 25 | There's no real point to this post, just a desparate request for people | |
| 26 | to please stop doing this. | |
blog/exiftool/index.org added +60
| @@ -0,0 +1,60 @@ | ||
| 1 | #+title: Stripping Image Metadata with exiftool | |
| 2 | #+date: 2022-02-17 | |
| 3 | #+description: A simple guide to remove exif data with exiftool. | |
| 4 | #+filetags: :privacy: | |
| 5 | ||
| 6 | ** Why Strip Metadata? | |
| 7 | Okay, so you want to strip metadata from your photos. Perhaps you take | |
| 8 | pictures of very rare birds, and the location metadata is a gold mine | |
| 9 | for poachers, or perhaps you're just privacy-oriented like me and prefer | |
| 10 | to strip metadata from publicly-available images. | |
| 11 | ||
| 12 | There are various components of image metadata that you may want to | |
| 13 | delete before releasing a photo to the public. Here's an incomplete list | |
| 14 | of things I could easily see just by inspecting a photo on my laptop: | |
| 15 | ||
| 16 | - Location (Latitude & Longitude) | |
| 17 | - Dimensions | |
| 18 | - Device Make & Model | |
| 19 | - Color Space | |
| 20 | - Color Profile | |
| 21 | - Focal Length | |
| 22 | - Alpha Channel | |
| 23 | - Red Eye | |
| 24 | - Metering Mode | |
| 25 | - F Number | |
| 26 | ||
| 27 | Regardless of your reasoning, I'm going to explain how I used the | |
| 28 | =exiftool= package in Linux to automatically strip metadata from all | |
| 29 | images in a directory (+ subdirectories). | |
| 30 | ||
| 31 | ** Installing =exiftool= | |
| 32 | First things first: we need to install the tool. I'm running Debian 11 | |
| 33 | on my server (Ubuntu will work the same), so the command is as simple | |
| 34 | as: | |
| 35 | ||
| 36 | #+begin_src sh | |
| 37 | sudo apt install exiftool | |
| 38 | #+end_src | |
| 39 | ||
| 40 | There are different tools that can accomplish the same thing across | |
| 41 | distributions, but I really only care to test out this one package. | |
| 42 | ||
| 43 | ** Recursively Strip Data | |
| 44 | I actually use this tool extensively to strip any photos uploaded to the | |
| 45 | website that serves all the images for my blog (=img.cleberg.net=). | |
| 46 | ||
| 47 | The following command is incredibly useful and can be modified to | |
| 48 | include any image extensions that =exiftool= supports: | |
| 49 | ||
| 50 | #+begin_src sh | |
| 51 | exiftool -r -all= -ext jpg -ext png /path/to/directory/ | |
| 52 | #+end_src | |
| 53 | ||
| 54 | See below for the results of my most recent usage of =exiftool= after I | |
| 55 | uploaded the image for this blog post. You can see that the command will | |
| 56 | let you know how many directories were scanned, how many images were | |
| 57 | updated, and how many images were unchanged. | |
| 58 | ||
| 59 | #+caption: exiftool results | |
| 60 | [[https://img.cleberg.net/blog/20220217-stripping-metadata-with-exiftool/exiftool.png]] | |
blog/exploring-hare/index.org added +169
| @@ -0,0 +1,169 @@ | ||
| 1 | #+title: Exploring the Hare Programming Language | |
| 2 | #+date: 2023-02-02 | |
| 3 | #+description: A retrospective on my first time using the Hare Programming Language. | |
| 4 | #+filetags: :dev: | |
| 5 | ||
| 6 | * A Quick Note | |
| 7 | By no means am I a professional developer, so this post will be rather | |
| 8 | short. I won't be going into depth on the specification or anything that | |
| 9 | technical. | |
| 10 | ||
| 11 | Instead, I will simply be talking about how I (a relatively basic | |
| 12 | hobbyist programmer) have been playing with Hare and what intrigues me | |
| 13 | about the language. | |
| 14 | ||
| 15 | * Hare | |
| 16 | The [[https://harelang.org][Hare]] programming language is a | |
| 17 | straightforward language that should look familiar if you've ever | |
| 18 | programmed with C, Rust, or other languages that aim to build software | |
| 19 | at the system-level. | |
| 20 | ||
| 21 | The Hare homepage states the following: | |
| 22 | ||
| 23 | #+begin_quote | |
| 24 | Hare is a systems programming language designed to be simple, stable, | |
| 25 | and robust. Hare uses a static type system, manual memory management, | |
| 26 | and minimal runtime. It is well-suited to writing operating systems, | |
| 27 | system tools, compilers, networking software, and other low-level, high | |
| 28 | performance tasks. | |
| 29 | ||
| 30 | #+end_quote | |
| 31 | ||
| 32 | I have found this all to be true while playing with it for the first | |
| 33 | time today. In the next few sections, I'm going to walk through my | |
| 34 | installation and first program. | |
| 35 | ||
| 36 | ** Installation | |
| 37 | I'm currently running Alpine Linux on my Thinkpad, so the installation | |
| 38 | was quite easy as there is a package for Hare in the =apk= repositories. | |
| 39 | ||
| 40 | #+begin_src sh | |
| 41 | doas apk add hare hare-doc | |
| 42 | #+end_src | |
| 43 | ||
| 44 | However, I was able to install Hare from scratch on Fedora Linux a short | |
| 45 | while ago, which was also very easy to do. If you need further | |
| 46 | instructions and Hare doesn't have a package on your system, take a look | |
| 47 | at the [[https://harelang.org/installation/][Hare Installation]] page. | |
| 48 | ||
| 49 | ** Creating a Test Project | |
| 50 | In order to play with the language, I created | |
| 51 | [[https://git.sr.ht/~cmc/hare-projects][hare-test]] and will be putting | |
| 52 | any of my Hare-related adventures in here. | |
| 53 | ||
| 54 | #+begin_quote | |
| 55 | *Update:** I also created a simple Hare program for creating a file from | |
| 56 | user input: | |
| 57 | [[https://git.sr.ht/~cmc/hare-projects/tree/main/item/files/files.ha][files.ha]] | |
| 58 | ||
| 59 | #+end_quote | |
| 60 | ||
| 61 | Luckily, Hare doesn't require any complex set-up tools or build | |
| 62 | environment. Once you have Hare installed, you simply need to create a | |
| 63 | file ending with =.ha= and you can run a Hare program. | |
| 64 | ||
| 65 | I created a file called =rgb.ha= in order to test out the random number | |
| 66 | generation and passing parameters between functions. | |
| 67 | ||
| 68 | #+begin_src sh | |
| 69 | nano rgb.ha | |
| 70 | #+end_src | |
| 71 | ||
| 72 | Within this file, I was able to easily import a few of the | |
| 73 | [[https://harelang.org/tutorials/stdlib/][standard library modules]]: | |
| 74 | =fmt=, =math::random=, and =datetime=. | |
| 75 | ||
| 76 | With these modules, I created two functions: | |
| 77 | ||
| 78 | 1. =main=: This function calls the =generate_rgb= function and then | |
| 79 | prints out the returned values. | |
| 80 | 2. =generate_rgb=: This function uses the current Unix epoch time to | |
| 81 | generate a pseudo-random value and uses this value to create three | |
| 82 | more random values between 0 and 255. These three numbers represent a | |
| 83 | color in RGB format. | |
| 84 | ||
| 85 | #+begin_quote | |
| 86 | *Note*: Some syntax coloring may look odd, as Zola currently doesn't | |
| 87 | have a syntax highlighting theme for Hare. Instead, I'm using the C | |
| 88 | theme, which may not be exactly accurate when coloring the code below. | |
| 89 | ||
| 90 | #+end_quote | |
| 91 | ||
| 92 | #+begin_src C | |
| 93 | use datetime; | |
| 94 | use fmt; | |
| 95 | use math::random; | |
| 96 | ||
| 97 | export fn main() void = { | |
| 98 | const rgb = generate_rgb(); | |
| 99 | fmt::printfln("RGB: ({}, {}, {})", rgb[0], rgb[1], rgb[2])!; | |
| 100 | }; | |
| 101 | ||
| 102 | fn generate_rgb() []u64 = { | |
| 103 | // Use the current Unix epoch time as the seed value | |
| 104 | let datetime = datetime::epochunix(&datetime::now()); | |
| 105 | ||
| 106 | // Generate initial pseudo-random value | |
| 107 | // You must cast the datetime from int to u64 | |
| 108 | let x = random::init(datetime: u64); | |
| 109 | ||
| 110 | // Generate RGB values between (0, 255) using pseudo-random init value | |
| 111 | let r = random::u64n(&x, 255); | |
| 112 | let g = random::u64n(&x, 255); | |
| 113 | let b = random::u64n(&x, 255); | |
| 114 | ||
| 115 | // Structure data as array and return | |
| 116 | let rgb_array: [3]u64 = [r, g, b]; | |
| 117 | return rgb_array; | |
| 118 | }; | |
| 119 | #+end_src | |
| 120 | ||
| 121 | ** Running a Program | |
| 122 | Once you have a Hare file written and ready to run, you simply need to | |
| 123 | run it: | |
| 124 | ||
| 125 | #+begin_src sh | |
| 126 | hare run file.ha | |
| 127 | #+end_src | |
| 128 | ||
| 129 | You can also compile the program into an executable: | |
| 130 | ||
| 131 | #+begin_src sh | |
| 132 | hare build -o example file.ha | |
| 133 | ./example | |
| 134 | #+end_src | |
| 135 | ||
| 136 | ** Initial Thoughts | |
| 137 | 1. Documentation Improvements Would Help | |
| 138 | ||
| 139 | While I was able to piece everything together eventually, the biggest | |
| 140 | downfall right now in Hare's documentation. For such a new project, | |
| 141 | the documentation is in a great spot. However, bare specifications | |
| 142 | don't help as much as a brief examples section would. | |
| 143 | ||
| 144 | For example, it took me a while to figure out what the =u64n= | |
| 145 | function was looking for. I could tell that it took two parameters | |
| 146 | and the second was my max value (255), but couldn't figure out what | |
| 147 | the first value should be. Eventually, I inspected the =random.ha= | |
| 148 | file in the | |
| 149 | [[https://git.sr.ht/~sircmpwn/hare/tree/master/item/math/random/random.ha][Hare | |
| 150 | source code]] and found the test suite that helped me discover that | |
| 151 | it needed an =init()= value in the form of =&var=. | |
| 152 | ||
| 153 | 2. More Basic Modules | |
| 154 | ||
| 155 | This is another point that comes from Hare being new and awaiting | |
| 156 | more contributions, but there are some basic functions that I would | |
| 157 | personally enjoy seeing in Hare, such as one to convert decimal | |
| 158 | (base 10) values to hexadecimal (base 16). | |
| 159 | ||
| 160 | If I'm feeling comfortable with my math, I may work on the list of | |
| 161 | functions I want and see if any can make it into the Hare source | |
| 162 | code. | |
| 163 | ||
| 164 | 3. Overall Thoughts | |
| 165 | ||
| 166 | Overall, I actually really enjoy Hare. It's not as tedious to get a | |
| 167 | project up and running as Rust, but it's also simpler and more | |
| 168 | user-friendly than learning C. I am going to continue playing with it | |
| 169 | and see if I can make anything of particular value. | |
content/blog/2021-01-04-fediverse.md → blog/fediverse/index.org renamed +40 −54
| @@ -1,29 +1,27 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-01-04 | |
| 3 | title = "A Simple Guide to the Fediverse" | |
| 4 | description = "Learn about the basics of the Fediverse." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## What is the Fediverse? | |
| 1 | #+title: A Simple Guide to the Fediverse | |
| 2 | #+date: 2021-01-04 | |
| 3 | #+description: Learn about the basics of the Fediverse. | |
| 4 | #+filetags: :social: | |
| 8 | 5 | |
| 6 | * What is the Fediverse? | |
| 9 | 7 | The fediverse is a federated universe of servers commonly used for |
| 10 | 8 | sharing content, like social media. So, instead of having to rely on a |
| 11 | single organization to run the server (e.g. Facebook), the fediverse is | |
| 9 | single organization to run the server (e.g. Facebook), the fediverse is | |
| 12 | 10 | a giant collection of servers across the world, owned by many people and |
| 13 | 11 | organizations. |
| 14 | 12 | |
| 15 | 13 | Take a look at this depiction of a federated network. Each server in |
| 16 | 14 | this photo is owned and run by different administrators/owners. |
| 17 | 15 | Federated networks are best explained as email servers: you have an |
| 18 | email account that exists on a server (e.g. Outlook), your friend has an | |
| 19 | account on a different server (e.g. GMail), and another friend has an | |
| 20 | account on a third server (e.g. ProtonMail). All three of you can talk | |
| 16 | email account that exists on a server (e.g. Outlook), your friend has an | |
| 17 | account on a different server (e.g. GMail), and another friend has an | |
| 18 | account on a third server (e.g. ProtonMail). All three of you can talk | |
| 21 | 19 | and communicate back and forth without having to be on the same server. |
| 22 | 20 | However, responsible email admins are there to set rules and control the |
| 23 | 21 | traffic going in/out of the server. |
| 24 | 22 | |
| 25 |  | |
| 23 | #+caption: Federated services diagram | |
| 24 | [[https://img.cleberg.net/blog/20210104-a-simple-guide-to-the-fediverse/federated-example.svg]] | |
| 27 | 25 | |
| 28 | 26 | The main objective of this architecture is to decentralize the control |
| 29 | 27 | within the internet connections. For example, if you run your own |
| @@ -36,13 +34,12 @@ This strategy is great for making sure control of the social web isn't | ||
| 36 | 34 | controlled by a single organization, but it also has some downsides. If |
| 37 | 35 | I create a Mastodon instance and get a ton of users to sign up, I can |
| 38 | 36 | shut the server down at any time. That means you're at risk of losing |
| 39 | the content you've created unless you back it up, or the server backs | |
| 40 | it up for you. Also, depending on the software used (e.g. Mastodon, | |
| 37 | the content you've created unless you back it up, or the server backs it | |
| 38 | up for you. Also, depending on the software used (e.g. Mastodon, | |
| 41 | 39 | Pixelfed, etc.), censorship may still be an issue if the server admins |
| 42 | 40 | decide they want to censor their users. Now, censorship isn't always a |
| 43 | bad thing and can even benefit the community as a whole, but you'll | |
| 44 | want to determine which servers align with your idea of proper | |
| 45 | censorship. | |
| 41 | bad thing and can even benefit the community as a whole, but you'll want | |
| 42 | to determine which servers align with your idea of proper censorship. | |
| 46 | 43 | |
| 47 | 44 | However, these are risks that we take when we sign up for any online |
| 48 | 45 | platform. Whatever your reason is for trying out federated social |
| @@ -52,55 +49,44 @@ with the increased difficulty understanding and signing up for these | ||
| 52 | 49 | platforms. Perhaps increased regulation and litigation against current |
| 53 | 50 | social media sites will push more users into the fediverse. |
| 54 | 51 | |
| 55 | ## Federated Alternatives to Popular Sites | |
| 56 | ||
| 52 | * Federated Alternatives to Popular Sites | |
| 57 | 53 | The list below is a small guide that will show you federated |
| 58 | 54 | alternatives to current popular websites. There are many more out there, |
| 59 | 55 | so go and explore: you might just find the perfect home. |
| 60 | 56 | |
| 61 | ||
| 62 | ||
| 63 | - [Lemmy](https://lemmy.ml/instances) | |
| 64 | ||
| 65 | ### Twitter/Facebook/Tumblr | |
| 66 | ||
| 67 | - [Mastodon](https://joinmastodon.org) | |
| 68 | - [Diaspora](https://diasporafoundation.org) | |
| 69 | - [Friendica](https://friendi.ca) | |
| 70 | - [GNU Social](https://gnusocial.network) | |
| 71 | - [Pleroma](https://pleroma.social) | |
| 72 | ||
| 73 | ||
| 74 | ||
| 75 | - [Pixelfed](https://pixelfed.org) | |
| 76 | ||
| 77 | ### Slack/Discord | |
| 78 | ||
| 79 | - [Matrix](https://element.io) | |
| 80 | ||
| 81 | ### Youtube/Vimeo | |
| 82 | ||
| 83 | - [Peertube](https://joinpeertube.org) | |
| 57 | ||
| 58 | - [[https://lemmy.ml/instances][Lemmy]] | |
| 84 | 59 | |
| 85 | ### Spotify/Soundcloud | |
| 60 | ** Twitter/Facebook/Tumblr | |
| 61 | - [[https://joinmastodon.org][Mastodon]] | |
| 62 | - [[https://diasporafoundation.org][Diaspora]] | |
| 63 | - [[https://friendi.ca][Friendica]] | |
| 64 | - [[https://gnusocial.network][GNU Social]] | |
| 65 | - [[https://pleroma.social][Pleroma]] | |
| 86 | 66 | |
| 87 | - [Funkwhale](https://funkwhale.audio) | |
| 67 | ||
| 68 | - [[https://pixelfed.org][Pixelfed]] | |
| 88 | 69 | |
| 89 | ### Podcasting | |
| 70 | ** Slack/Discord | |
| 71 | - [[https://element.io][Matrix]] | |
| 90 | 72 | |
| 91 | - [Pubcast](https://pubcast.pub) | |
| 73 | ** Youtube/Vimeo | |
| 74 | - [[https://joinpeertube.org][Peertube]] | |
| 92 | 75 | |
| 93 | ### Medium/Blogger | |
| 76 | ** Spotify/Soundcloud | |
| 77 | - [[https://funkwhale.audio][Funkwhale]] | |
| 94 | 78 | |
| 95 | - [WriteFreely](https://writefreely.org) | |
| 79 | ** Podcasting | |
| 80 | - [[https://pubcast.pub][Pubcast]] | |
| 96 | 81 | |
| 97 | ## Get Started | |
| 82 | ** Medium/Blogger | |
| 83 | - [[https://writefreely.org][WriteFreely]] | |
| 98 | 84 | |
| 85 | * Get Started | |
| 99 | 86 | The best way to get started is to simply sign up and learn as you go. If |
| 100 | 87 | you're comfortable signing up through a Mastodon, Pleroma, or Friendica |
| 101 | server, here is [a list of themed | |
| 102 | servers](https://fediverse.party/en/portal/servers) to choose from. If | |
| 103 | you're looking for something else, try a web search for a federated | |
| 104 | alternative to your favorite sites. | |
| 88 | server, here is [[https://fediverse.party/en/portal/servers][a list of | |
| 89 | themed servers]] to choose from. If you're looking for something else, | |
| 90 | try a web search for a federated alternative to your favorite sites. | |
| 105 | 91 | |
| 106 | 92 | Find a server that focuses on your passions and start there! |
blog/fedora-i3/index.org added +152
| @@ -0,0 +1,152 @@ | ||
| 1 | #+title: Rebooting My Love Affair with Linux | |
| 2 | #+date: 2022-06-24 | |
| 3 | #+description: A retrospective on moving from macOS to Linux. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * Leaving macOS | |
| 7 | As I noted [[../foss-macos-apps][in a recent post]], I have been | |
| 8 | planning on migrating from macOS back to a Linux-based OS. I am happy to | |
| 9 | say that I have finally completed my migration and am now stuck in the | |
| 10 | wonderful world of Linux again. | |
| 11 | ||
| 12 | My decision to leave macOS really came down to just a few important | |
| 13 | things: | |
| 14 | ||
| 15 | - Apple Security (Gatekeeper) restricting me from running any software I | |
| 16 | want. Even if you disable Gatekeeper and allow software to bypass the | |
| 17 | rest of the device installation security, you still have to repeat | |
| 18 | that process every time the allowed software is updated. | |
| 19 | - macOS sends out nearly constant connections, pings, telemetry, etc. to | |
| 20 | a myriad of mysterious Apple services. I'm not even going to dive into | |
| 21 | how many macOS apps have constant telemetry on, as well. | |
| 22 | - Lastly, I just /really/ missed the customization and freedom that | |
| 23 | comes with Linux. Being able to switch to entirely new kernel, OS, or | |
| 24 | desktop within minutes is a freedom I took for granted when I switched | |
| 25 | to macOS. | |
| 26 | ||
| 27 | Now that I've covered macOS, I'm going to move on to more exciting | |
| 28 | topics: my personal choice of OS, DE, and various customizations I'm | |
| 29 | using. | |
| 30 | ||
| 31 | * Fedora | |
| 32 | After trying a ton of distros (I think I booted and tested around 20-25 | |
| 33 | distros), I finally landed on [[https://getfedora.org/][Fedora Linux]]. | |
| 34 | I have quite a bit of experience with Fedora and enjoy the =dnf= package | |
| 35 | manager. Fedora allows me to keep up-to-date with recent software (I'm | |
| 36 | looking at you, Debian), but still provides a level of stability you | |
| 37 | don't find in every distro. | |
| 38 | ||
| 39 | In a very close second place was Arch Linux, as well as its spin-off: | |
| 40 | Garuda Linux (Garuda w/ sway is /beautiful/). Arch is great for | |
| 41 | compatibility and the massive community it has, but I have just never | |
| 42 | had the time to properly sit down and learn the methodology behind their | |
| 43 | packaging systems. | |
| 44 | ||
| 45 | Basically, everything else I tested was unacceptable in at least one way | |
| 46 | or another. Void (=glibc=) was great, but doesn't support all the | |
| 47 | software I need. Slackware worked well as a tui, but I wasn't skilled | |
| 48 | enough to get a tiling window manager (WM) working on it. | |
| 49 | ||
| 50 | ** i3 | |
| 51 | One of the reasons I settled on Fedora is that it comes with an official | |
| 52 | i3 spin. Being able to use a tiling WM, such as i3 or sway, is one of | |
| 53 | the biggest things I wanted to do as soon as I adopted Linux again. | |
| 54 | ||
| 55 | I will probably set up a dotfile repository soon, so that I don't lose | |
| 56 | any of my configurations, but nothing big has been configured thus far. | |
| 57 | ||
| 58 | The two main things I have updated in i3wm are natural scrolling and | |
| 59 | binding my brightness keys to the =brightnessctl= program. | |
| 60 | ||
| 61 | 1. Natural Scrolling | |
| 62 | ||
| 63 | You can enable natural scrolling by opening the following file: | |
| 64 | ||
| 65 | #+begin_src sh | |
| 66 | sudo nano /usr/share/X11/xorg.conf.d/40-libinput.conf | |
| 67 | #+end_src | |
| 68 | ||
| 69 | Within the =40-libinput.conf= file, find the following input sections | |
| 70 | and enable the natural scrolling option. | |
| 71 | ||
| 72 | This is the =pointer= section: | |
| 73 | ||
| 74 | #+begin_src conf | |
| 75 | Section "InputClass" | |
| 76 | Identifier "libinput pointer catchall" | |
| 77 | MatchIsPointer "on" | |
| 78 | MatchDevicePath "/dev/input/event*" | |
| 79 | Driver "libinput" | |
| 80 | Option "NaturalScrolling" "True" | |
| 81 | EndSection | |
| 82 | #+end_src | |
| 83 | ||
| 84 | This is the =touchpad= section: | |
| 85 | ||
| 86 | #+begin_src conf | |
| 87 | Section "InputClass" | |
| 88 | Identifier "libinput touchpad catchall" | |
| 89 | MatchIsTouchpad "on" | |
| 90 | MatchDevicePath "/dev/input/event*" | |
| 91 | Driver "libinput" | |
| 92 | Option "NaturalScrolling" "True" | |
| 93 | EndSection | |
| 94 | #+end_src | |
| 95 | ||
| 96 | 2. Enabling Brightness Keys | |
| 97 | ||
| 98 | Likewise, enabling brightness key functionality is as simple as | |
| 99 | binding the keys to the =brightnessctl= program. | |
| 100 | ||
| 101 | To do this, open up your i3 config file. Mine is located here: | |
| 102 | ||
| 103 | #+begin_src sh | |
| 104 | nano /home/<my-user>/.config/i3/config | |
| 105 | #+end_src | |
| 106 | ||
| 107 | #+begin_src conf | |
| 108 | # Use brightnessctl to adjust brightness. | |
| 109 | bindsym XF86MonBrightnessDown exec --no-startup-id brightnessctl --min-val=2 -q set 3%- | |
| 110 | bindsym XF86MonBrightnessUp exec --no-startup-id brightnessctl -q set 3%+ | |
| 111 | #+end_src | |
| 112 | ||
| 113 | 3. =polybar= | |
| 114 | ||
| 115 | Instead of using the default =i3status= bar, I have opted to use | |
| 116 | =polybar= instead (as you can also see in the screenshot above). | |
| 117 | ||
| 118 | My config for this menu bar is basically just the default settings | |
| 119 | with modified colors and an added battery block to quickly show me | |
| 120 | the machine's battery info. | |
| 121 | ||
| 122 | 4. =alacritty= | |
| 123 | ||
| 124 | Not much to say on this part yet, as I haven't configured it much, | |
| 125 | but I installed =alacritty= as my default terminal, and I am using | |
| 126 | =zsh= and the shell. | |
| 127 | ||
| 128 | * Software Choices | |
| 129 | Again, I'm not going to say much that I haven't said yet in other blog | |
| 130 | posts, so I'll just do a quick rundown of the apps I installed | |
| 131 | immediately after I set up the environment. | |
| 132 | ||
| 133 | Flatpak Apps: | |
| 134 | ||
| 135 | - Cryptomator | |
| 136 | - pCloud | |
| 137 | - Signal | |
| 138 | ||
| 139 | Fedora Packages: | |
| 140 | ||
| 141 | - gomuks | |
| 142 | - neomutt | |
| 143 | - neofetch | |
| 144 | - Firefox | |
| 145 | - uBlock Origin | |
| 146 | - Bitwarden | |
| 147 | - Stylus | |
| 148 | - Privacy Redirect | |
| 149 | ||
| 150 | Other: | |
| 151 | ||
| 152 | - exiftool | |
content/blog/2023-01-08-fedora-remove-login-manager.md → blog/fedora-login-manager/index.org renamed +17 −21
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-01-08 | |
| 3 | title = "How to Remove the Login Manager from Fedora i3" | |
| 4 | description = "Learn how to completely remove the login manager from Fedora i3." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Fedora i3's Login Manager | |
| 1 | #+title: How to Remove the Login Manager from Fedora i3 | |
| 2 | #+date: 2023-01-08 | |
| 3 | #+description: Learn how to completely remove the login manager from Fedora i3. | |
| 4 | #+filetags: :linux: | |
| 8 | 5 | |
| 6 | * Fedora i3's Login Manager | |
| 9 | 7 | Since I use the i3 spin of Fedora Workstation, I don't like to have a |
| 10 | 8 | login manager installed by default. As of the current version of Fedora |
| 11 | 9 | i3, the default login manager is LightDM. |
| @@ -14,31 +12,29 @@ If this is no longer the case, you can search for currently-installed | ||
| 14 | 12 | packages with the following command and see if you can identify a |
| 15 | 13 | different login manager. |
| 16 | 14 | |
| 17 | ```sh | |
| 15 | #+begin_src sh | |
| 18 | 16 | sudo dnf list installed |
| 19 | ``` | |
| 20 | ||
| 21 | ## Removing the Login Manager | |
| 17 | #+end_src | |
| 22 | 18 | |
| 19 | * Removing the Login Manager | |
| 23 | 20 | In order to remove the login manager, simply uninstall the package. |
| 24 | 21 | |
| 25 | ```sh | |
| 22 | #+begin_src sh | |
| 26 | 23 | sudo dnf remove lightdm |
| 27 | ``` | |
| 28 | ||
| 29 | ## Launching i3 Manually | |
| 24 | #+end_src | |
| 30 | 25 | |
| 26 | * Launching i3 Manually | |
| 31 | 27 | In order to launch i3 manually, you need to set up your X session |
| 32 | properly. To start, create or edit the `~/.xinitrc` file to | |
| 33 | include the following at the bottom. | |
| 28 | properly. To start, create or edit the =~/.xinitrc= file to include the | |
| 29 | following at the bottom. | |
| 34 | 30 | |
| 35 | ```config | |
| 31 | #+begin_src config | |
| 36 | 32 | exec i3 |
| 37 | ``` | |
| 33 | #+end_src | |
| 38 | 34 | |
| 39 | 35 | Now, whenever you log in to the TTY, you can launch your desktop with |
| 40 | 36 | the following command. |
| 41 | 37 | |
| 42 | ```sh | |
| 38 | #+begin_src sh | |
| 43 | 39 | startx |
| 44 | ``` | |
| 40 | #+end_src | |
blog/financial-database/index.org added +256
| @@ -0,0 +1,256 @@ | ||
| 1 | #+title: Maintaining a Personal Financial Database | |
| 2 | #+date: 2022-03-03 | |
| 3 | #+description: An example project showing to build and maintain a simple financial database. | |
| 4 | #+filetags: :personal: | |
| 5 | ||
| 6 | * Personal Financial Tracking | |
| 7 | For the last 6-ish years, I've tracked my finances in a spreadsheet. | |
| 8 | This is common practice in the business world, but any good dev will | |
| 9 | cringe at the thought of storing long-term data in a spreadsheet. A | |
| 10 | spreadsheet is not for long-term storage or as a source of data to pull | |
| 11 | data/reports. | |
| 12 | ||
| 13 | As I wanted to expand the functionality of my financial data (e.g., | |
| 14 | adding more reports), I decided to migrate the data into a database. To | |
| 15 | run reports, I would query the database and use a language like Python | |
| 16 | or Javascript to process the data, perform calculations, and visualize | |
| 17 | the data. | |
| 18 | ||
| 19 | * SQLite | |
| 20 | When choosing the type of database I wanted to use for this project, I | |
| 21 | was split between three options: | |
| 22 | ||
| 23 | 1. MySQL: The database I have the most experience with and have used for | |
| 24 | years. | |
| 25 | 2. PostgreSQL: A database I'm new to, but want to learn. | |
| 26 | 3. SQLite: A database that I've used for a couple projects and have | |
| 27 | moderate experience. | |
| 28 | ||
| 29 | I ended up choosing SQLite since it can be maintained within a single | |
| 30 | =.sqlite= file, which allows me more flexibility for storage and backup. | |
| 31 | I keep this file in my cloud storage and pull it up whenever needed. | |
| 32 | ||
| 33 | ** GUI Editing | |
| 34 | Since I didn't want to try and import 1000--1500 records into my new | |
| 35 | database via the command line, I opted to use | |
| 36 | [[https://sqlitebrowser.org/][DB Browser for SQLite (DB4S)]] as a GUI | |
| 37 | tool. This application is excellent, and I don't see myself going back | |
| 38 | to the CLI when working in this database. | |
| 39 | ||
| 40 | DB4S allows you to copy a range of cells from a spreadsheet and paste it | |
| 41 | straight into the SQL table. I used this process for all 36 accounts, | |
| 42 | 1290 account statements, and 126 pay statements. Overall, I'm guessing | |
| 43 | this took anywhere between 4--8 hours. In comparison, it probably took | |
| 44 | me 2-3 days to initially create the spreadsheet. | |
| 45 | ||
| 46 | #+caption: DB4S | |
| 47 | [[https://img.cleberg.net/blog/20220303-maintaining-a-personal-financial-database/db4s.png]] | |
| 48 | ||
| 49 | ** Schema | |
| 50 | The schema for this database is actually extremely simple and involves | |
| 51 | only three tables (for now): | |
| 52 | ||
| 53 | 1. Accounts | |
| 54 | 2. Statements | |
| 55 | 3. Payroll | |
| 56 | ||
| 57 | *Accounts* | |
| 58 | ||
| 59 | The Accounts table contains summary information about an account, such | |
| 60 | as a car loan or a credit card. By viewing this table, you can find | |
| 61 | high-level data, such as interest rate, credit line, or owner. | |
| 62 | ||
| 63 | #+begin_src sql | |
| 64 | CREATE TABLE "Accounts" ( | |
| 65 | "AccountID" INTEGER NOT NULL UNIQUE, | |
| 66 | "AccountType" TEXT, | |
| 67 | "AccountName" TEXT, | |
| 68 | "InterestRate" NUMERIC, | |
| 69 | "CreditLine" NUMERIC, | |
| 70 | "State" TEXT, | |
| 71 | "Owner" TEXT, | |
| 72 | "Co-Owner" TEXT, | |
| 73 | PRIMARY KEY("AccountID" AUTOINCREMENT) | |
| 74 | ) | |
| 75 | #+end_src | |
| 76 | ||
| 77 | *Statements* | |
| 78 | ||
| 79 | The Statements table uses the same unique identifier as the Accounts | |
| 80 | table, meaning you can join the tables to find a monthly statement for | |
| 81 | any of the accounts listed in the Accounts table. Each statement has an | |
| 82 | account ID, statement date, and total balance. | |
| 83 | ||
| 84 | #+begin_src sql | |
| 85 | CREATE TABLE "Statements" ( | |
| 86 | "StatementID" INTEGER NOT NULL UNIQUE, | |
| 87 | "AccountID" INTEGER, | |
| 88 | "StatementDate" INTEGER, | |
| 89 | "Balance" NUMERIC, | |
| 90 | PRIMARY KEY("StatementID" AUTOINCREMENT), | |
| 91 | FOREIGN KEY("AccountID") REFERENCES "Accounts"("AccountID") | |
| 92 | ) | |
| 93 | #+end_src | |
| 94 | ||
| 95 | *Payroll* | |
| 96 | ||
| 97 | The Payroll table is a separate entity, unrelated to the Accounts or | |
| 98 | Statements tables. This table contains all information you would find on | |
| 99 | a pay statement from an employer. As you change employers or obtain new | |
| 100 | perks/benefits, just add new columns to adapt to the new data. | |
| 101 | ||
| 102 | #+begin_src sql | |
| 103 | CREATE TABLE "Payroll" ( | |
| 104 | "PaycheckID" INTEGER NOT NULL UNIQUE, | |
| 105 | "PayDate" TEXT, | |
| 106 | "Payee" TEXT, | |
| 107 | "Employer" TEXT, | |
| 108 | "JobTitle" TEXT, | |
| 109 | "IncomeRegular" NUMERIC, | |
| 110 | "IncomePTO" NUMERIC, | |
| 111 | "IncomeHoliday" NUMERIC, | |
| 112 | "IncomeBonus" NUMERIC, | |
| 113 | "IncomePTOPayout" NUMERIC, | |
| 114 | "IncomeReimbursements" NUMERIC, | |
| 115 | "FringeHSA" NUMERIC, | |
| 116 | "FringeStudentLoan" NUMERIC, | |
| 117 | "Fringe401k" NUMERIC, | |
| 118 | "PreTaxMedical" NUMERIC, | |
| 119 | "PreTaxDental" NUMERIC, | |
| 120 | "PreTaxVision" NUMERIC, | |
| 121 | "PreTaxLifeInsurance" NUMERIC, | |
| 122 | "PreTax401k" NUMERIC, | |
| 123 | "PreTaxParking" NUMERIC, | |
| 124 | "PreTaxStudentLoan" NUMERIC, | |
| 125 | "PreTaxOther" NUMERIC, | |
| 126 | "TaxFederal" NUMERIC, | |
| 127 | "TaxSocial" NUMERIC, | |
| 128 | "TaxMedicare" NUMERIC, | |
| 129 | "TaxState" NUMERIC, | |
| 130 | PRIMARY KEY("PaycheckID" AUTOINCREMENT) | |
| 131 | ) | |
| 132 | #+end_src | |
| 133 | ||
| 134 | ** Python Reporting | |
| 135 | Once I created the database tables and imported all my data, the only | |
| 136 | step left was to create a process to report and visualize on various | |
| 137 | aspects of the data. | |
| 138 | ||
| 139 | In order to explore and create the reports I'm interested in, I utilized | |
| 140 | a two-part process involving Jupyter Notebooks and Python scripts. | |
| 141 | ||
| 142 | 1. Step 1: Jupyter Notebooks | |
| 143 | ||
| 144 | When I need to explore data, try different things, and re-run my code | |
| 145 | cell-by-cell, I use Jupyter Notebooks. For example, I explored the | |
| 146 | =Accounts= table until I found the following useful information: | |
| 147 | ||
| 148 | #+begin_src python | |
| 149 | import sqlite3 | |
| 150 | import pandas as pd | |
| 151 | import matplotlib | |
| 152 | ||
| 153 | # Set up database filename and connect | |
| 154 | db = "finances.sqlite" | |
| 155 | connection = sqlite3.connect(db) | |
| 156 | df = pd.read_sql_query("SELECT ** FROM Accounts", connection) | |
| 157 | ||
| 158 | # Set global matplotlib variables | |
| 159 | %matplotlib inline | |
| 160 | matplotlib.rcParams['text.color'] = 'white' | |
| 161 | matplotlib.rcParams['axes.labelcolor'] = 'white' | |
| 162 | matplotlib.rcParams['xtick.color'] = 'white' | |
| 163 | matplotlib.rcParams['ytick.color'] = 'white' | |
| 164 | matplotlib.rcParams['legend.labelcolor'] = 'black' | |
| 165 | ||
| 166 | # Display graph | |
| 167 | df.groupby(['AccountType']).sum().plot.pie(title='Credit Line by Account Type', y='CreditLine', figsize=(5,5), autopct='%1.1f%%') | |
| 168 | #+end_src | |
| 169 | ||
| 170 | 2. Step 2: Python Scripts | |
| 171 | ||
| 172 | Once I explored enough through the notebooks and had a list of | |
| 173 | reports I wanted, I moved on to create a Python project with the | |
| 174 | following structure: | |
| 175 | ||
| 176 | #+begin_src txt | |
| 177 | finance/ | |
| 178 | ├── notebooks/ | |
| 179 | │ │ ├── account_summary.ipynb | |
| 180 | │ │ ├── account_details.ipynb | |
| 181 | │ │ └── payroll.ipynb | |
| 182 | ├── public/ | |
| 183 | │ │ ├── image-01.png | |
| 184 | │ │ └── image-0X.png | |
| 185 | ├── src/ | |
| 186 | │ └── finance.sqlite | |
| 187 | ├── venv/ | |
| 188 | ├── _init.py | |
| 189 | ├── database.py | |
| 190 | ├── process.py | |
| 191 | ├── requirements.txt | |
| 192 | └── README.md | |
| 193 | #+end_src | |
| 194 | ||
| 195 | This structure allows me to: | |
| 196 | ||
| 197 | 1. Compile all required python packages into =requirements.txt= for | |
| 198 | easy installation if I move to a new machine. | |
| 199 | 2. Activate a virtual environment in =venv/= so I don't need to | |
| 200 | maintain a system-wide Python environment just for this project. | |
| 201 | 3. Keep my =notebooks/= folder to continuously explore the data as I | |
| 202 | see fit. | |
| 203 | 4. Maintain a local copy of the database in =src/= for easy access. | |
| 204 | 5. Export reports, images, HTML files, etc. to =public/=. | |
| 205 | ||
| 206 | Now, onto the differences between the code in a Jupyter Notebook and | |
| 207 | the actual Python files. To create the report in the Notebook snippet | |
| 208 | above, I created the following function inside =process.py=: | |
| 209 | ||
| 210 | #+begin_src python | |
| 211 | # Create summary pie chart | |
| 212 | def summary_data(accounts: pandas.DataFrame) -> None: | |
| 213 | accounts_01 = accounts[accounts["Owner"] == "Person01"] | |
| 214 | accounts_02 = accounts[accounts["Owner"] == "Person02"] | |
| 215 | for x in range(1, 4): | |
| 216 | if x == 1: | |
| 217 | df = accounts | |
| 218 | account_string = "All Accounts" | |
| 219 | elif x == 2: | |
| 220 | df = accounts_01 | |
| 221 | account_string = "Person01's Accounts" | |
| 222 | elif x == 3: | |
| 223 | df = accounts_02 | |
| 224 | account_string = "Person02's Accounts" | |
| 225 | print(f"Generating pie chart summary image for {account_string}...") | |
| 226 | summary_chart = ( | |
| 227 | df.groupby(["AccountType"]) | |
| 228 | .sum() | |
| 229 | .plot.pie( | |
| 230 | title=f"Credit Line by Type for {account_string}", | |
| 231 | y="CreditLine", | |
| 232 | autopct="%1.1f%%", | |
| 233 | ) | |
| 234 | ) | |
| 235 | summary_chart.figure.savefig(f"public/summary_chart_{x}.png", dpi=1200) | |
| 236 | #+end_src | |
| 237 | ||
| 238 | The result? A high-quality pie chart that is read directly by the | |
| 239 | =public/index.html= template I use. | |
| 240 | ||
| 241 | #+caption: Summary Pie Chart | |
| 242 | [[https://img.cleberg.net/blog/20220303-maintaining-a-personal-financial-database/summary_chart.png]] | |
| 243 | ||
| 244 | Other charts generated by this project include: | |
| 245 | ||
| 246 | - Charts of account balances over time. | |
| 247 | - Line chart of effective tax rate (taxes divided by taxable income). | |
| 248 | - Salary projections and error limits using past income and inflation | |
| 249 | rates. | |
| 250 | - Multi-line chart of gross income, taxable income, and net income. | |
| 251 | ||
| 252 | The best thing about this project? I can improve it at any given | |
| 253 | time, shaping it into whatever helps me the most for that time. I | |
| 254 | imagine that I will be introducing an asset tracking table soon to | |
| 255 | track the depreciating value of cars, houses, etc. Who knows what's | |
| 256 | next? | |
content/blog/2022-07-30-flac-to-opus.md → blog/flac-to-opus/index.org renamed +56 −64
| @@ -1,70 +1,65 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-07-30 | |
| 3 | title = "Recursive Command-Line FLAC to Opus Conversion" | |
| 4 | description = "Learn how to convert all FLAC files to Opus, including recursive files in subdirectories." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Converting FLAC to OPUS | |
| 1 | #+title: Recursive Command-Line FLAC to Opus Conversion | |
| 2 | #+date: 2022-07-30 | |
| 3 | #+description: Learn how to convert all FLAC files to Opus, including recursive files in subdirectories. | |
| 4 | #+filetags: :linux: | |
| 8 | 5 | |
| 6 | * Converting FLAC to OPUS | |
| 9 | 7 | I am currently rebuilding my music library from scratch so that I can |
| 10 | effectively archive all the music I own in the [FLAC file | |
| 11 | format](https://en.wikipedia.org/wiki/FLAC), a lossless audio codec. | |
| 8 | effectively archive all the music I own in the | |
| 9 | [[https://en.wikipedia.org/wiki/FLAC][FLAC file format]], a lossless | |
| 10 | audio codec. | |
| 12 | 11 | |
| 13 | 12 | However, streaming FLAC files outside the home can be difficult due to |
| 14 | 13 | the size of the files, especially if you're using a weak connection. |
| 15 | 14 | |
| 16 | 15 | So, in order to archive the music in a lossless format and still be able |
| 17 | 16 | to stream it easily, I opted to create a copy of my FLAC files in the |
| 18 | [Opus audio codec](https://en.wikipedia.org/wiki/Opus_(audio_format)). | |
| 17 | [[https://en.wikipedia.org/wiki/Opus_(audio_format)][Opus audio codec]]. | |
| 19 | 18 | This allows me to archive a quality, lossless version of the music and |
| 20 | 19 | then point my streaming service to the smaller, stream-ready version. |
| 21 | 20 | |
| 22 | ### Dependencies | |
| 23 | ||
| 24 | The process I follow utilizes the `opus-tools` package in | |
| 25 | Ubuntu. Before proceeding, install the package: | |
| 21 | ** Dependencies | |
| 22 | The process I follow utilizes the =opus-tools= package in Ubuntu. Before | |
| 23 | proceeding, install the package: | |
| 26 | 24 | |
| 27 | ```sh | |
| 25 | #+begin_src sh | |
| 28 | 26 | sudo apt install opus-tools |
| 29 | ``` | |
| 30 | ||
| 31 | If you want to use a different conversion method, such as | |
| 32 | `ffmpeg` or `avconv`, simply install that package | |
| 33 | instead. | |
| 27 | #+end_src | |
| 34 | 28 | |
| 35 | ### Conversion Process | |
| 29 | If you want to use a different conversion method, such as =ffmpeg= or | |
| 30 | =avconv=, simply install that package instead. | |
| 36 | 31 | |
| 32 | ** Conversion Process | |
| 37 | 33 | The script I'm using is stored in my home directory, but feel free to |
| 38 | 34 | create it wherever you want. It does not need to be in the same |
| 39 | 35 | directory as your music files. |
| 40 | 36 | |
| 41 | ```sh | |
| 37 | #+begin_src sh | |
| 42 | 38 | cd ~ && nano transform.sh |
| 43 | ``` | |
| 39 | #+end_src | |
| 44 | 40 | |
| 45 | 41 | Once you have your new bash script opened in an editor, go ahead and |
| 46 | 42 | paste the following logic into the script. |
| 47 | 43 | |
| 48 | You **MUST** edit the following variables in order for it to work: | |
| 44 | You *MUST* edit the following variables in order for it to work: | |
| 49 | 45 | |
| 50 | - `source`: The source directory where your FLAC files are | |
| 51 | stored. | |
| 52 | - `dest`: The destination directory where you want the | |
| 53 | resulting Opus files to be stored. | |
| 46 | - =source=: The source directory where your FLAC files are stored. | |
| 47 | - =dest=: The destination directory where you want the resulting Opus | |
| 48 | files to be stored. | |
| 54 | 49 | |
| 55 | You **MAY** want to edit the following variables to suit your needs: | |
| 50 | You *MAY* want to edit the following variables to suit your needs: | |
| 56 | 51 | |
| 57 | - `filename`: If you are converting to a file format other | |
| 58 | than Opus, you'll need to edit this so that your resulting files | |
| 59 | have the correct filename extension. | |
| 60 | - `reldir`: This variable can be edited to strip out more | |
| 61 | leading directories in the file path. As you'll see later, I ignore | |
| 62 | this for now and simply clean it up afterward. | |
| 63 | - `opusenc`: This is the actual conversion process. You may | |
| 64 | want to edit the bitrate to suit your needs. I set mine at 128 but | |
| 65 | some prefer 160 or higher. | |
| 52 | - =filename=: If you are converting to a file format other than Opus, | |
| 53 | you'll need to edit this so that your resulting files have the correct | |
| 54 | filename extension. | |
| 55 | - =reldir=: This variable can be edited to strip out more leading | |
| 56 | directories in the file path. As you'll see later, I ignore this for | |
| 57 | now and simply clean it up afterward. | |
| 58 | - =opusenc=: This is the actual conversion process. You may want to edit | |
| 59 | the bitrate to suit your needs. I set mine at 128 but some prefer 160 | |
| 60 | or higher. | |
| 66 | 61 | |
| 67 | ```sh | |
| 62 | #+begin_src sh | |
| 68 | 63 | #!/bin/bash |
| 69 | 64 | ## - The IFS takes care of spaces in file and dirnames |
| 70 | 65 | ## - your folders may vary |
| @@ -126,52 +121,49 @@ opusenc --vbr --bitrate 128 --date "$DATE" \ | ||
| 126 | 121 | ## just for testing |
| 127 | 122 | # sleep 1 |
| 128 | 123 | done |
| 129 | ``` | |
| 124 | #+end_src | |
| 130 | 125 | |
| 131 | 126 | Once you're done, simply save the file and exit your editor. Don't |
| 132 | 127 | forget to enable execution of the script: |
| 133 | 128 | |
| 134 | ```sh | |
| 129 | #+begin_src sh | |
| 135 | 130 | chmod +x transform.sh |
| 136 | ``` | |
| 131 | #+end_src | |
| 137 | 132 | |
| 138 | 133 | Finally, you may now run the script: |
| 139 | 134 | |
| 140 | ```sh | |
| 135 | #+begin_src sh | |
| 141 | 136 | ./transform.sh |
| 142 | ``` | |
| 137 | #+end_src | |
| 143 | 138 | |
| 144 | If you used `opusenc`, you'll see the conversions happen | |
| 145 | within the terminal as it progresses. You will also see variables | |
| 146 | printed if you uncommented any of the bash script's comments. | |
| 139 | If you used =opusenc=, you'll see the conversions happen within the | |
| 140 | terminal as it progresses. You will also see variables printed if you | |
| 141 | uncommented any of the bash script's comments. | |
| 147 | 142 | |
| 148 | ### Cleanup | |
| 149 | ||
| 150 | As I noted above, I didn't customize my `reldir` variable in | |
| 151 | the script, which caused my output directory to be | |
| 152 | `/mnt/music/library/archives` instead of | |
| 153 | `/mnt/music/library`. So, I moved the output up one level and | |
| 143 | ** Cleanup | |
| 144 | As I noted above, I didn't customize my =reldir= variable in the script, | |
| 145 | which caused my output directory to be =/mnt/music/library/archives= | |
| 146 | instead of =/mnt/music/library=. So, I moved the output up one level and | |
| 154 | 147 | deleted the accidental directory. |
| 155 | 148 | |
| 156 | ```sh | |
| 149 | #+begin_src sh | |
| 157 | 150 | cd /mnt/music/library |
| 158 | mv archives/* . | |
| 151 | mv archives/** . | |
| 159 | 152 | rm -rf archives |
| 160 | ``` | |
| 161 | ||
| 162 | ### Check the Resulting Size | |
| 153 | #+end_src | |
| 163 | 154 | |
| 164 | If you want to see what kind of file size savings you've gained, you | |
| 165 | can always use the `du` command to check: | |
| 155 | ** Check the Resulting Size | |
| 156 | If you want to see what kind of file size savings you've gained, you can | |
| 157 | always use the =du= command to check: | |
| 166 | 158 | |
| 167 | ```sh | |
| 159 | #+begin_src sh | |
| 168 | 160 | cd /mnt/music |
| 169 | 161 | du -h --max-depth=1 . |
| 170 | ``` | |
| 162 | #+end_src | |
| 171 | 163 | |
| 172 | 164 | In my case, my small library went from 78GB to 6.3GB! |
| 173 | 165 | |
| 174 | ```txt | |
| 166 | #+begin_src txt | |
| 175 | 167 | 78G ./archives |
| 176 | 168 | 6.3G ./library |
| 177 | ``` | |
| 169 | #+end_src | |
content/blog/2023-01-21-running-flatpak-apps-easily.md → blog/flatpak-symlinks/index.org renamed +21 −25
| @@ -1,50 +1,46 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-01-21 | |
| 3 | title = "Running Flatpak Apps with Symlinks" | |
| 4 | description = "Learn how to run Flatpak apps through menu launchers with symlinks." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Running Flatpak Apps Should Be Faster | |
| 1 | #+title: Running Flatpak Apps with Symlinks | |
| 2 | #+date: 2023-01-21 | |
| 3 | #+description: Learn how to run Flatpak apps through menu launchers with symlinks. | |
| 4 | #+filetags: :linux: | |
| 8 | 5 | |
| 6 | * Running Flatpak Apps Should Be Faster | |
| 9 | 7 | If you're like me and use Flatpak for those pesky apps that cannot run |
| 10 | 8 | on your system for one reason or another, you likely get annoyed with |
| 11 | 9 | opening a terminal and manually running the Flatpak app with the lengthy |
| 12 | `flatpak run ...` command. | |
| 10 | =flatpak run ...= command. | |
| 13 | 11 | |
| 14 | In the past, I manually created aliases in my `.zshrc` file | |
| 15 | for certain apps. For example, an alias would look like the example | |
| 16 | below. | |
| 12 | In the past, I manually created aliases in my =.zshrc= file for certain | |
| 13 | apps. For example, an alias would look like the example below. | |
| 17 | 14 | |
| 18 | 15 | This would allow me to run the command fast within the terminal, but it |
| 19 | 16 | wouldn't allow me to run it in an application launcher. |
| 20 | 17 | |
| 21 | ```sh | |
| 18 | #+begin_src sh | |
| 22 | 19 | # ~/.zshrc |
| 23 | 20 | alias librewolf = "flatpak run io.gitlab.librewolf-community" |
| 24 | ``` | |
| 21 | #+end_src | |
| 25 | 22 | |
| 26 | 23 | However, I now use a much faster and better method that integrates with |
| 27 | the tiling WMs I use and their application launchers - | |
| 28 | `dmenu` and `bemenu`. | |
| 29 | ||
| 30 | ## Creating Symlinks for Flatpak Apps | |
| 24 | the tiling WMs I use and their application launchers - =dmenu= and | |
| 25 | =bemenu=. | |
| 31 | 26 | |
| 27 | * Creating Symlinks for Flatpak Apps | |
| 32 | 28 | Let's use the example of Librewolf below. I can install the application |
| 33 | 29 | like so: |
| 34 | 30 | |
| 35 | ```sh | |
| 31 | #+begin_src sh | |
| 36 | 32 | flatpak install flathub io.gitlab.librewolf-community |
| 37 | ``` | |
| 33 | #+end_src | |
| 38 | 34 | |
| 39 | 35 | Once installed, I can create a symlink to link the flatpak app to my new |
| 40 | 36 | symlink in a location commonly included in your PATH. In this case, I |
| 41 | chose `/usr/bin`. You may need to choose a different location | |
| 42 | if `/usr/bin` isn't in your PATH. | |
| 37 | chose =/usr/bin=. You may need to choose a different location if | |
| 38 | =/usr/bin= isn't in your PATH. | |
| 43 | 39 | |
| 44 | ```sh | |
| 40 | #+begin_src sh | |
| 45 | 41 | ln -s /var/lib/flatpak/exports/bin/io.gitlab.librewolf-community /usr/bin/librewolf |
| 46 | ``` | |
| 42 | #+end_src | |
| 47 | 43 | |
| 48 | 44 | Once complete, you should be able to launch the app using the command |
| 49 | name you chose above in the symlink (`librewolf`) from a | |
| 50 | terminal or from your application launcher! | |
| 45 | name you chose above in the symlink (=librewolf=) from a terminal or | |
| 46 | from your application launcher! | |
content/blog/2021-03-28-gemini-capsule.md → blog/gemini-capsule/index.org renamed +63 −71
| @@ -1,30 +1,28 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-03-28 | |
| 3 | title = "Launching a Gemini Capsule" | |
| 4 | description = "A guide to self-hosting a Gemini capsule on your own server." | |
| 5 | +++ | |
| 1 | #+title: Launching a Gemini Capsule | |
| 2 | #+date: 2021-03-28 | |
| 3 | #+description: A guide to self-hosting a Gemini capsule on your own server. | |
| 4 | #+filetags: :dev: | |
| 6 | 5 | |
| 7 | ## What is Gemini? | |
| 8 | ||
| 9 | [Gemini](https://gemini.circumlunar.space/) is an internet protocol | |
| 6 | * What is Gemini? | |
| 7 | [[https://gemini.circumlunar.space/][Gemini]] is an internet protocol | |
| 10 | 8 | introduced in June 2019 as an alternative to HTTP(S) or Gopher. In |
| 11 | 9 | layman's terms, it's an alternative way to browse sites (called |
| 12 | 10 | capsules) that requires a special browser. Since Gemini is not |
| 13 | 11 | standardized as an internet standard, normal web browsers won't be able |
| 14 | to load a Gemini capsule. Instead, you'll need to use [a | |
| 15 | Gemini-specific | |
| 16 | browser](https://gemini.%20circumlunar.space/clients.html). | |
| 12 | to load a Gemini capsule. Instead, you'll need to use | |
| 13 | [[https://gemini.%20circumlunar.space/clients.html][a Gemini-specific | |
| 14 | browser]]. | |
| 17 | 15 | |
| 18 | 16 | The content found within a Gemini page is called |
| 19 | [Gemtext](https://gemini.circumlunar.space/docs/cheatsheet.gmi) and is | |
| 20 | *extremely* basic (on purpose). Gemini only processes the text, no media | |
| 21 | content like images. However, you're able to style 3 levels of | |
| 22 | headings, regular text, links (which will display on their own line), | |
| 23 | quotes, and an unordered list. | |
| 17 | [[https://gemini.circumlunar.space/docs/cheatsheet.gmi][Gemtext]] and is | |
| 18 | /extremely/ basic (on purpose). Gemini only processes the text, no media | |
| 19 | content like images. However, you're able to style 3 levels of headings, | |
| 20 | regular text, links (which will display on their own line), quotes, and | |
| 21 | an unordered list. | |
| 24 | 22 | |
| 25 | 23 | Here's a complete listing of valid Gemtext: |
| 26 | 24 | |
| 27 | ```txt | |
| 25 | #+begin_src txt | |
| 28 | 26 | # Heading 1 |
| 29 | 27 | ## Heading 2 |
| 30 | 28 | ### Heading 3 |
| @@ -37,14 +35,13 @@ Regular text! Lorem ipsum dolor sit amet. | ||
| 37 | 35 | > "If life were predictable it would cease to be life, and be without flavor." - Eleanor Roosevelt |
| 38 | 36 | |
| 39 | 37 | My List: |
| 40 | * Item | |
| 41 | * Item | |
| 38 | ,** Item | |
| 39 | ,** Item | |
| 42 | 40 | |
| 43 | 41 | ```Anything between three backticks will be rendered as code.``` |
| 44 | ``` | |
| 45 | ||
| 46 | ## Free Option | |
| 42 | #+end_src | |
| 47 | 43 | |
| 44 | *** Free Option | |
| 48 | 45 | There are probably numerous websites that allow you to create your |
| 49 | 46 | personal Gemini capsule, but I'm going to focus on the two sites that I |
| 50 | 47 | have personally tested. The first option below, Midnight Pub, allows you |
| @@ -54,18 +51,17 @@ second option below, Sourcehut, allows you to use a Git repository and | ||
| 54 | 51 | automatic build process to deploy your personal Gemini capsule every |
| 55 | 52 | time you push a commit. |
| 56 | 53 | |
| 57 | ### Midnight Pub - Beginner Friendly | |
| 58 | ||
| 59 | [Midnight Pub](https://midnight.pub/) is a small, virtual community | |
| 54 | ** Midnight Pub - Beginner Friendly | |
| 55 | [[https://midnight.pub/][Midnight Pub]] is a small, virtual community | |
| 60 | 56 | meant to reflect the atmosphere of wandering into a small alley pub. The |
| 61 | 57 | site is built in Gemtext and has a server-side process to convert |
| 62 | 58 | Gemtext to HTML if someone loads the site in an HTTP(S) browser. |
| 63 | 59 | |
| 64 | 60 | To create an account, you'll need to email the owner of the website to |
| 65 | 61 | obtain a key. You can find their email on the Midnight Pub homepage. |
| 66 | Once registered, head to [your account](https://midnight.pub/account) | |
| 67 | and select [manage site](https://midnight.pub/site). This is the screen | |
| 68 | where you can upload or create any files to be displayed on the | |
| 62 | Once registered, head to [[https://midnight.pub/account][your account]] | |
| 63 | and select [[https://midnight.pub/site][manage site]]. This is the | |
| 64 | screen where you can upload or create any files to be displayed on the | |
| 69 | 65 | internet. |
| 70 | 66 | |
| 71 | 67 | For example, I've created both an HTML file and a Gemini file. Remember |
| @@ -73,22 +69,19 @@ that Gemini is automatically converted to HTML on the Pub, so you don't | ||
| 73 | 69 | need an HTML version. For example, I created an HTML version to add in |
| 74 | 70 | some extra styling. |
| 75 | 71 | |
| 76 | All you need to do is create a page like `index.gmi` and use | |
| 77 | your Gemini browser to head over to your-username.midnight.pub to see | |
| 78 | the result. | |
| 72 | All you need to do is create a page like =index.gmi= and use your Gemini | |
| 73 | browser to head over to your-username.midnight.pub to see the result. | |
| 79 | 74 | |
| 80 | 75 | That's all there is to it! Easy enough, right? Let's check out a more |
| 81 | 76 | advanced version in the next section. |
| 82 | 77 | |
| 83 | ## Paid Option | |
| 84 | ||
| 78 | * Paid Option | |
| 85 | 79 | As of 2021, Sourcehut has decided to require users to have a paid |
| 86 | 80 | account in order to utilize their automated build system. For now, paid |
| 87 | accounts can be as low as \$2/month. | |
| 88 | ||
| 89 | ### Sourcehut | |
| 81 | accounts can be as low as $2/month. | |
| 90 | 82 | |
| 91 | [Sourcehut](https://sourcehut.org/) is a collection of software | |
| 83 | ** Sourcehut | |
| 84 | [[https://sourcehut.org/][Sourcehut]] is a collection of software | |
| 92 | 85 | development tools, but mostly surrounds their hosted Git repository |
| 93 | 86 | service. Simply put, it's a minimal and more private alternative to |
| 94 | 87 | services like GitHub. |
| @@ -100,43 +93,43 @@ instead. | ||
| 100 | 93 | |
| 101 | 94 | The first thing you'll need to do is create an SSH key pair, if you |
| 102 | 95 | don't already have one on your system. Once created, grab the contents |
| 103 | of `id_rsa.pub` and add it to your Sourcehut account | |
| 104 | settings - this will allow you to push and pull code changes without | |
| 105 | using a username/password. | |
| 96 | of =id_rsa.pub= and add it to your Sourcehut account settings - this | |
| 97 | will allow you to push and pull code changes without using a | |
| 98 | username/password. | |
| 106 | 99 | |
| 107 | ```sh | |
| 100 | #+begin_src sh | |
| 108 | 101 | ssh keygen |
| 109 | ``` | |
| 102 | #+end_src | |
| 110 | 103 | |
| 111 | 104 | Next up, let's create a repository with the proper name so that the |
| 112 | 105 | Sourcehut build system will know we want them to host a website for us. |
| 113 | 106 | Use the following format exactly: |
| 114 | 107 | |
| 115 | ```sh | |
| 108 | #+begin_src sh | |
| 116 | 109 | mkdir your-username.srht.site && cd your-username.srht.site |
| 117 | ``` | |
| 110 | #+end_src | |
| 118 | 111 | |
| 119 | Now that we've created the repo, let's initialize Git and add the | |
| 120 | proper remote URL. | |
| 112 | Now that we've created the repo, let's initialize Git and add the proper | |
| 113 | remote URL. | |
| 121 | 114 | |
| 122 | ```sh | |
| 115 | #+begin_src sh | |
| 123 | 116 | git init |
| 124 | ``` | |
| 117 | #+end_src | |
| 125 | 118 | |
| 126 | ```sh | |
| 119 | #+begin_src sh | |
| 127 | 120 | git remote add origin git@git.sr.ht:~your-username/your-username.srht.site |
| 128 | ``` | |
| 121 | #+end_src | |
| 129 | 122 | |
| 130 | 123 | Now that our repository is set up and configured, we will need to create |
| 131 | 124 | at least two files: |
| 132 | 125 | |
| 133 | - `index.gmi` | |
| 134 | - `.build.yml` | |
| 126 | - =index.gmi= | |
| 127 | - =.build.yml= | |
| 135 | 128 | |
| 136 | For your `.build.yml` file, use the following content and be | |
| 137 | sure to update the `site` line with your username! | |
| 129 | For your =.build.yml= file, use the following content and be sure to | |
| 130 | update the =site= line with your username! | |
| 138 | 131 | |
| 139 | ```yaml | |
| 132 | #+begin_src yaml | |
| 140 | 133 | image: alpine/latest |
| 141 | 134 | oauth: pages.sr.ht/PAGES:RW |
| 142 | 135 | environment: |
| @@ -147,39 +140,38 @@ tasks: | ||
| 147 | 140 | tar -cvz . > ../site.tar.gz |
| 148 | 141 | - upload: | |
| 149 | 142 | acurl -f https://pages.sr.ht/publish/$site -Fcontent=@site.tar.gz -Fprotocol=GEMINI |
| 150 | ``` | |
| 143 | #+end_src | |
| 151 | 144 | |
| 152 | For the `index.gmi` file, put whatever you want in there and | |
| 153 | save it. You could even just copy and paste the Gemtext cheatsheet. | |
| 145 | For the =index.gmi= file, put whatever you want in there and save it. | |
| 146 | You could even just copy and paste the Gemtext cheatsheet. | |
| 154 | 147 | |
| 155 | 148 | If you want to serve both HTML and Gemini files from this repository, |
| 156 | just add a second command to the `upload` section: | |
| 149 | just add a second command to the =upload= section: | |
| 157 | 150 | |
| 158 | ```yaml | |
| 151 | #+begin_src yaml | |
| 159 | 152 | - upload: | |
| 160 | 153 | acurl -f https://pages.sr.ht/publish/$site -Fcontent=@site.tar.gz -Fprotocol=GEMINI |
| 161 | 154 | acurl -f https://pages.sr.ht/publish/$site -Fcontent=@site.tar.gz |
| 162 | ``` | |
| 155 | #+end_src | |
| 163 | 156 | |
| 164 | 157 | Lastly, commit your changes and push them to the remote repo. |
| 165 | 158 | |
| 166 | ```sh | |
| 159 | #+begin_src sh | |
| 167 | 160 | git add .; git commit -m "initial commit"; git push --set-upstream origin HEAD |
| 168 | ``` | |
| 161 | #+end_src | |
| 169 | 162 | |
| 170 | If you've successfully created the files with the proper format, | |
| 171 | you'll see the terminal print a message that lets you know where the | |
| 172 | automatic build is taking place. For example, here's what the terminal | |
| 173 | tells me: | |
| 163 | If you've successfully created the files with the proper format, you'll | |
| 164 | see the terminal print a message that lets you know where the automatic | |
| 165 | build is taking place. For example, here's what the terminal tells me: | |
| 174 | 166 | |
| 175 | ```sh | |
| 167 | #+begin_src sh | |
| 176 | 168 | remote: Build started: |
| 177 | 169 | remote: https://builds.sr.ht/~user/job/689803 [.build.yml] |
| 178 | ``` | |
| 170 | #+end_src | |
| 179 | 171 | |
| 180 | 172 | Now that you've properly built your Sourcehut page, you can browse to |
| 181 | 173 | your-username.srht.site in a Gemini browser and view the final results. |
| 182 | 174 | Take a look at the image below for my Sourcehut Gemini capsule. |
| 183 | 175 | |
| 184 |  | |
| 176 | #+caption: Gemini page on the amfora browser | |
| 177 | [[https://img.cleberg.net/blog/20210328-launching-a-gemini-capsule/amfora.png]] | |
content/blog/2021-04-17-gemini-server.md → blog/gemini-server/index.org renamed +63 −77
| @@ -1,164 +1,150 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-04-17 | |
| 3 | title = "Hosting a Gemini Server" | |
| 4 | description = "A guide to self-hosting a Gemini web server on your own server." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Similar Article Available | |
| 1 | #+title: Hosting a Gemini Server | |
| 2 | #+date: 2021-04-17 | |
| 3 | #+description: A guide to self-hosting a Gemini web server on your own server. | |
| 4 | #+filetags: :sysadmin: | |
| 8 | 5 | |
| 6 | * Similar Article Available | |
| 9 | 7 | To read more about Gemini and ways to test out this new protocol without |
| 10 | your own server, see my previous post [Launching a Gemini | |
| 11 | Capsule](/blog/launching-a-gemini-capsule/). | |
| 12 | ||
| 13 | ## Preparation | |
| 8 | your own server, see my previous post | |
| 9 | [[../launching-a-gemini-capsule/][Launching a Gemini Capsule]]. | |
| 14 | 10 | |
| 11 | * Preparation | |
| 15 | 12 | This guide assumes you have access to a server accessible to the world |
| 16 | 13 | through a public IP address and that you own a domain name used for this |
| 17 | 14 | Gemini capsule. |
| 18 | 15 | |
| 19 | ## Getting Started with Agate | |
| 20 | ||
| 21 | We are going to use [Agate](https://github.com/mbrubeck/agate) for this | |
| 22 | tutorial. This is a basic Gemini server written in Rust. It takes very | |
| 23 | little time and maintenance to get it running. | |
| 24 | ||
| 25 | ## Install Dependencies | |
| 16 | * Getting Started with Agate | |
| 17 | We are going to use [[https://github.com/mbrubeck/agate][Agate]] for | |
| 18 | this tutorial. This is a basic Gemini server written in Rust. It takes | |
| 19 | very little time and maintenance to get it running. | |
| 26 | 20 | |
| 21 | * Install Dependencies | |
| 27 | 22 | First, you will need to install the Rust package for your system. On |
| 28 | Ubuntu, use the following commands (remember to use `sudo` if | |
| 29 | you are not the root user). The Rust installation will give you options | |
| 30 | to customize the installation; I used the default installation options. | |
| 23 | Ubuntu, use the following commands (remember to use =sudo= if you are | |
| 24 | not the root user). The Rust installation will give you options to | |
| 25 | customize the installation; I used the default installation options. | |
| 31 | 26 | |
| 32 | ```sh | |
| 27 | #+begin_src sh | |
| 33 | 28 | sudo apt update && sudo apt upgrade -y |
| 34 | 29 | curl https://sh.rustup.rs -sSf | sh |
| 35 | ``` | |
| 30 | #+end_src | |
| 36 | 31 | |
| 37 | 32 | Remember to configure your shell with the new configuration: |
| 38 | 33 | |
| 39 | ```sh | |
| 34 | #+begin_src sh | |
| 40 | 35 | source $HOME/.cargo/env |
| 41 | ``` | |
| 36 | #+end_src | |
| 42 | 37 | |
| 43 | Before we install agate, make sure you have the `gcc` package | |
| 44 | installed: | |
| 38 | Before we install agate, make sure you have the =gcc= package installed: | |
| 45 | 39 | |
| 46 | ```sh | |
| 40 | #+begin_src sh | |
| 47 | 41 | sudo apt install gcc |
| 48 | ``` | |
| 42 | #+end_src | |
| 49 | 43 | |
| 50 | 44 | Next, you'll need to install the agate executable with Rust's Cargo |
| 51 | 45 | package maintainer: |
| 52 | 46 | |
| 53 | ```sh | |
| 47 | #+begin_src sh | |
| 54 | 48 | cargo install agate |
| 55 | ``` | |
| 56 | ||
| 57 | ## Create Symlinks | |
| 49 | #+end_src | |
| 58 | 50 | |
| 51 | * Create Symlinks | |
| 59 | 52 | Once Cargo has finished installing all the required packages, symlink |
| 60 | the executable to your \$PATH. | |
| 53 | the executable to your $PATH. | |
| 61 | 54 | |
| 62 | ```sh | |
| 55 | #+begin_src sh | |
| 63 | 56 | sudo ln -s $HOME/.cargo/bin/agate /usr/local/bin/agate |
| 64 | ``` | |
| 65 | ||
| 66 | ## Using Agate's Built-In Installation Tool | |
| 57 | #+end_src | |
| 67 | 58 | |
| 59 | * Using Agate's Built-In Installation Tool | |
| 68 | 60 | If you're running Ubuntu or Debian, use the Debian installation script |
| 69 | found in Agate's GitHub repository, under the `tools/debian` | |
| 70 | folder. | |
| 61 | found in Agate's GitHub repository, under the =tools/debian= folder. | |
| 71 | 62 | |
| 72 | ```sh | |
| 63 | #+begin_src sh | |
| 73 | 64 | git clone https://github.com/mbrubeck/agate |
| 74 | 65 | cd agate/tools/debian |
| 75 | 66 | sudo ./install.sh |
| 76 | ``` | |
| 77 | ||
| 78 | ## Configure the Gemini Service | |
| 67 | #+end_src | |
| 79 | 68 | |
| 69 | * Configure the Gemini Service | |
| 80 | 70 | We have a little more to do, but since this script tries to immediately |
| 81 | 71 | run the service, it will likely fail with an exit code. Let's add our |
| 82 | 72 | finishing touches. Edit the following file and replace the hostname with |
| 83 | 73 | your desired URL. You can also change the directory where content will |
| 84 | 74 | be served. |
| 85 | 75 | |
| 86 | ```sh | |
| 76 | #+begin_src sh | |
| 87 | 77 | sudo nano /etc/systemd/system/gemini.service |
| 88 | ``` | |
| 78 | #+end_src | |
| 89 | 79 | |
| 90 | ```sh | |
| 80 | #+begin_src sh | |
| 91 | 81 | # Edit these lines to whatever you want - see the next code block for my personal configuration. |
| 92 | 82 | WorkingDirectory=/srv/gemini |
| 93 | 83 | ExecStart=agate --hostname $(uname -n) --lang en |
| 94 | ``` | |
| 84 | #+end_src | |
| 95 | 85 | |
| 96 | 86 | This is my personal config: |
| 97 | 87 | |
| 98 | ```sh | |
| 88 | #+begin_src sh | |
| 99 | 89 | WorkingDirectory=/var/gemini/ |
| 100 | 90 | ExecStart=agate --hostname gemini.example.com --lang en |
| 101 | ``` | |
| 91 | #+end_src | |
| 102 | 92 | |
| 103 | 93 | Since we've altered the systemd configuration files, we have to reload |
| 104 | 94 | the daemon. Let's do that, restart our service, and check its status. |
| 105 | 95 | |
| 106 | ```sh | |
| 96 | #+begin_src sh | |
| 107 | 97 | sudo systemctl daemon-reload |
| 108 | 98 | sudo systemctl restart gemini.service |
| 109 | 99 | sudo systemctl status gemini.service |
| 110 | ``` | |
| 111 | ||
| 112 | ## Fixing Systemd Errors | |
| 100 | #+end_src | |
| 113 | 101 | |
| 102 | * Fixing Systemd Errors | |
| 114 | 103 | If you're still getting errors, the installation process may not have |
| 115 | 104 | properly enabled the gemini service. Fix it with the following commands. |
| 116 | 105 | |
| 117 | ```sh | |
| 106 | #+begin_src sh | |
| 118 | 107 | sudo systemctl enable gemini.service |
| 119 | 108 | sudo systemctl restart gemini.service |
| 120 | 109 | sudo systemctl status gemini.service |
| 121 | ``` | |
| 122 | ||
| 123 | ## Firewall Rules | |
| 110 | #+end_src | |
| 124 | 111 | |
| 112 | * Firewall Rules | |
| 125 | 113 | Great! Our server is now functional and running. The first consideration |
| 126 | 114 | now is that you need to be able to access port 1965 on the server. If |
| 127 | 115 | you have a firewall enabled, you'll need to open that port up. |
| 128 | 116 | |
| 129 | ```sh | |
| 117 | #+begin_src sh | |
| 130 | 118 | sudo ufw allow 1965 |
| 131 | 119 | sudo ufw reload |
| 132 | ``` | |
| 133 | ||
| 134 | ## Creating Content | |
| 120 | #+end_src | |
| 135 | 121 | |
| 122 | * Creating Content | |
| 136 | 123 | Let's create the Gemini capsule. Note that wherever you set the |
| 137 | 124 | WorkingDirectory variable to earlier, Agate will expect you to put your |
| 138 | Gemini capsule contents in a sub-folder called "content." So, I place | |
| 139 | my files in "/var/gmi/content." I'm going to create that folder now | |
| 140 | and put a file in there. | |
| 125 | Gemini capsule contents in a sub-folder called "content." So, I place my | |
| 126 | files in "/var/gmi/content." I'm going to create that folder now and put | |
| 127 | a file in there. | |
| 141 | 128 | |
| 142 | ```sh | |
| 129 | #+begin_src sh | |
| 143 | 130 | sudo mkdir /var/gemini/content |
| 144 | 131 | sudo nano /var/gemini/content/index.gmi |
| 145 | ``` | |
| 132 | #+end_src | |
| 146 | 133 | |
| 147 | 134 | You can put whatever you want in the "index.gmi" file, just make sure |
| 148 | 135 | it's valid Gemtext. |
| 149 | 136 | |
| 150 | ## The Results | |
| 151 | ||
| 137 | * The Results | |
| 152 | 138 | Here are some screenshots of the Gemini page I just created in the |
| 153 | [Lagrange](https://gmi.skyjake.fi/lagrange/) browser and the | |
| 154 | [amfora](https://github.com/makeworld-the-better-one/amfora) browser. | |
| 139 | [[https://gmi.skyjake.fi/lagrange/][Lagrange]] browser and the | |
| 140 | [[https://github.com/makeworld-the-better-one/amfora][amfora]] browser. | |
| 155 | 141 | |
| 156 |  | |
| 142 | #+caption: GUI Gemini browser | |
| 143 | [[https://img.cleberg.net/blog/20210417-hosting-a-gemini-server/lagrange.png]] | |
| 158 | 144 | |
| 159 | *Lagrange* | |
| 145 | /Lagrange/ | |
| 160 | 146 | |
| 161 |  | |
| 147 | #+caption: CLI Gemini browser | |
| 148 | [[https://img.cleberg.net/blog/20210417-hosting-a-gemini-server/amfora.png]] | |
| 163 | 149 | |
| 164 | *Amfora* | |
| 150 | /Amfora/ | |
content/blog/2022-07-01-git-server.md → blog/git-server/index.org renamed +234 −271
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-07-01 | |
| 3 | title = "Self-Hosting a Personal Git Server" | |
| 4 | description = "A guide to self-hosting a Git server on your own server." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## My Approach to Self-Hosting Git | |
| 1 | #+title: Self-Hosting a Personal Git Server | |
| 2 | #+date: 2022-07-01 | |
| 3 | #+description: A guide to self-hosting a Git server on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 8 | 5 | |
| 6 | * My Approach to Self-Hosting Git | |
| 9 | 7 | I have often tried to self-host my Git repositories, but have always |
| 10 | 8 | fallen short when I tried to find a suitable web interface to show on |
| 11 | 9 | the front-end. |
| @@ -17,240 +15,223 @@ access them from anywhere. | ||
| 17 | 15 | Before I dive into the details, I want to state a high-level summary of |
| 18 | 16 | my self-hosted Git approach: |
| 19 | 17 | |
| 20 | - This method uses the `ssh://` (read & write) and | |
| 21 | `git://` (read-only) protocols for push and pull access. | |
| 22 | - For the `git://` protocol, I create a | |
| 23 | `git-daemon-export-ok` file in any repository that I | |
| 24 | want to be cloneable by anyone. | |
| 25 | - The web interface I am using (`cgit`) allows simple | |
| 26 | HTTP cloning by default. I do not disable this setting as I want | |
| 27 | beginners to be able to clone one of my repositories even if | |
| 28 | they don't know the proper method. | |
| 29 | - I am not enabling Smart HTTPS for any repositories. Updates to | |
| 30 | repositories must be pushed via SSH. | |
| 31 | - Beyond the actual repository management, I am using | |
| 32 | `cgit` for the front-end web interface. | |
| 33 | - If you use the `scan-path=<path>` configuration in | |
| 34 | the `cgitrc` configuration file to automatically find | |
| 35 | repositories, you can't exclude a repository from | |
| 36 | `cgit` if it's stored within the path that | |
| 37 | `cgit` reads. To host private repositories, you'd | |
| 38 | need to set up another directory that `cgit` can't | |
| 39 | read. | |
| 40 | ||
| 41 | ## Assumptions | |
| 42 | ||
| 18 | - This method uses the =ssh://= (read & write) and =git://= (read-only) | |
| 19 | protocols for push and pull access. | |
| 20 | - For the =git://= protocol, I create a =git-daemon-export-ok= file in | |
| 21 | any repository that I want to be cloneable by anyone. | |
| 22 | - The web interface I am using (=cgit=) allows simple HTTP cloning by | |
| 23 | default. I do not disable this setting as I want beginners to be | |
| 24 | able to clone one of my repositories even if they don't know the | |
| 25 | proper method. | |
| 26 | - I am not enabling Smart HTTPS for any repositories. Updates to | |
| 27 | repositories must be pushed via SSH. | |
| 28 | - Beyond the actual repository management, I am using =cgit= for the | |
| 29 | front-end web interface. | |
| 30 | - If you use the =scan-path=<path>= configuration in the =cgitrc= | |
| 31 | configuration file to automatically find repositories, you can't | |
| 32 | exclude a repository from =cgit= if it's stored within the path that | |
| 33 | =cgit= reads. To host private repositories, you'd need to set up | |
| 34 | another directory that =cgit= can't read. | |
| 35 | ||
| 36 | * Assumptions | |
| 43 | 37 | For the purposes of this walkthrough, I am assuming you have a URL |
| 44 | (`git.example.com`) or IP address | |
| 45 | (`207.84.26.991`) addressed to the server that you will be | |
| 46 | using to host your git repositories. | |
| 47 | ||
| 48 | ## Adding a Git User | |
| 38 | (=git.example.com=) or IP address (=207.84.26.991=) addressed to the | |
| 39 | server that you will be using to host your git repositories. | |
| 49 | 40 | |
| 41 | * Adding a Git User | |
| 50 | 42 | In order to use the SSH method associated with git, we will need to add |
| 51 | a user named `git`. If you have used the SSH method for other | |
| 52 | git hosting sites, you are probably used to the following syntax: | |
| 43 | a user named =git=. If you have used the SSH method for other git | |
| 44 | hosting sites, you are probably used to the following syntax: | |
| 53 | 45 | |
| 54 | ```sh | |
| 46 | #+begin_src sh | |
| 55 | 47 | git clone [user@]server:project.git |
| 56 | ``` | |
| 48 | #+end_src | |
| 57 | 49 | |
| 58 | The syntax above is an `scp`-like syntax for using SSH on the | |
| 59 | `git` user on the server to access your repository. | |
| 50 | The syntax above is an =scp=-like syntax for using SSH on the =git= user | |
| 51 | on the server to access your repository. | |
| 60 | 52 | |
| 61 | Let's delete any remnants of an old `git` user, if any, and | |
| 62 | create the new user account: | |
| 53 | Let's delete any remnants of an old =git= user, if any, and create the | |
| 54 | new user account: | |
| 63 | 55 | |
| 64 | ```sh | |
| 56 | #+begin_src sh | |
| 65 | 57 | sudo deluser --remove-home git |
| 66 | 58 | sudo adduser git |
| 67 | ``` | |
| 59 | #+end_src | |
| 68 | 60 | |
| 69 | ### Import Your SSH Keys to the Git User | |
| 70 | ||
| 71 | Once the `git` user is created, you will need to copy your | |
| 72 | public SSH key on your local development machine to the `git` | |
| 73 | user on the server. | |
| 61 | ** Import Your SSH Keys to the Git User | |
| 62 | Once the =git= user is created, you will need to copy your public SSH | |
| 63 | key on your local development machine to the =git= user on the server. | |
| 74 | 64 | |
| 75 | 65 | If you don't have an SSH key yet, create one with this command: |
| 76 | 66 | |
| 77 | ```sh | |
| 67 | #+begin_src sh | |
| 78 | 68 | ssh-keygen |
| 79 | ``` | |
| 69 | #+end_src | |
| 80 | 70 | |
| 81 | 71 | Once you create the key pair, the public should be saved to |
| 82 | `~/.ssh/id_rsa.pub`. | |
| 72 | =~/.ssh/id_rsa.pub=. | |
| 83 | 73 | |
| 84 | 74 | If your server still has password-based authentication available, you |
| 85 | 75 | can copy it over to your user's home directory like this: |
| 86 | 76 | |
| 87 | ```sh | |
| 77 | #+begin_src sh | |
| 88 | 78 | ssh-copy-id git@server |
| 89 | ``` | |
| 79 | #+end_src | |
| 90 | 80 | |
| 91 | 81 | Otherwise, copy it over to any user that you can access. |
| 92 | 82 | |
| 93 | ```sh | |
| 83 | #+begin_src sh | |
| 94 | 84 | scp ~/.ssh/id_rsa.pub your_user@your_server: |
| 95 | ``` | |
| 85 | #+end_src | |
| 96 | 86 | |
| 97 | Once on the server, you will need to copy the contents into the | |
| 98 | `git` user's `authorized_keys` file: | |
| 87 | Once on the server, you will need to copy the contents into the =git= | |
| 88 | user's =authorized_keys= file: | |
| 99 | 89 | |
| 100 | ```sh | |
| 90 | #+begin_src sh | |
| 101 | 91 | cat id_rsa.pub > /home/git/.ssh/authorized_keys |
| 102 | ``` | |
| 103 | ||
| 104 | ### (Optional) Disable Password-Based SSH | |
| 92 | #+end_src | |
| 105 | 93 | |
| 94 | ** (Optional) Disable Password-Based SSH | |
| 106 | 95 | If you want to lock down your server and ensure that no one can |
| 107 | 96 | authenticate in via SSH with a password, you will need to edit your SSH |
| 108 | 97 | configuration. |
| 109 | 98 | |
| 110 | ```sh | |
| 99 | #+begin_src sh | |
| 111 | 100 | sudo nano /etc/ssh/sshd_config |
| 112 | ``` | |
| 101 | #+end_src | |
| 113 | 102 | |
| 114 | 103 | Within this file, find the following settings and set them to the values |
| 115 | 104 | I am showing below: |
| 116 | 105 | |
| 117 | ```conf | |
| 106 | #+begin_src conf | |
| 118 | 107 | PermitRootLogin no |
| 119 | 108 | PasswordAuthentication no |
| 120 | 109 | AuthenticationMethods publickey |
| 121 | ``` | |
| 110 | #+end_src | |
| 122 | 111 | |
| 123 | 112 | You may have other Authentication Methods required in your personal |
| 124 | set-up, so the key here is just to ensure that | |
| 125 | `AuthenticationMethods` does not allow passwords. | |
| 126 | ||
| 127 | ## Setting up the Base Directory | |
| 113 | set-up, so the key here is just to ensure that =AuthenticationMethods= | |
| 114 | does not allow passwords. | |
| 128 | 115 | |
| 129 | Now that we have set up a `git` user to handle all transport | |
| 130 | methods, we need to set up the directory that we will be using as our | |
| 131 | base of all repositories. | |
| 116 | *** Setting up the Base Directory | |
| 117 | Now that we have set up a =git= user to handle all transport methods, we | |
| 118 | need to set up the directory that we will be using as our base of all | |
| 119 | repositories. | |
| 132 | 120 | |
| 133 | In my case, I am using `/git` as my source folder. To create | |
| 134 | this folder and assign it to the user we created, execute the following | |
| 135 | commands: | |
| 121 | In my case, I am using =/git= as my source folder. To create this folder | |
| 122 | and assign it to the user we created, execute the following commands: | |
| 136 | 123 | |
| 137 | ```sh | |
| 124 | #+begin_src sh | |
| 138 | 125 | sudo mkdir /git |
| 139 | 126 | sudo chown -R git:git /git |
| 140 | ``` | |
| 127 | #+end_src | |
| 141 | 128 | |
| 142 | ## Creating a Test Repository | |
| 129 | *** Creating a Test Repository | |
| 130 | On your server, switch over to the =git= user in order to start managing | |
| 131 | git files. | |
| 143 | 132 | |
| 144 | On your server, switch over to the `git` user in order to | |
| 145 | start managing git files. | |
| 146 | ||
| 147 | ```sh | |
| 133 | #+begin_src sh | |
| 148 | 134 | su git |
| 149 | ``` | |
| 135 | #+end_src | |
| 150 | 136 | |
| 151 | Once logged-in as the `git` user, go to your base directory | |
| 152 | and create a test repository. | |
| 137 | Once logged-in as the =git= user, go to your base directory and create a | |
| 138 | test repository. | |
| 153 | 139 | |
| 154 | ```sh | |
| 140 | #+begin_src sh | |
| 155 | 141 | cd /git |
| 156 | 142 | mkdir test.git && cd test.git |
| 157 | 143 | git init --bare |
| 158 | ``` | |
| 144 | #+end_src | |
| 159 | 145 | |
| 160 | 146 | If you want to make this repo viewable/cloneable to the public via the |
| 161 | `git://` protocol, you need to create a | |
| 162 | `git-daemon-export-ok` file inside the repository. | |
| 147 | =git://= protocol, you need to create a =git-daemon-export-ok= file | |
| 148 | inside the repository. | |
| 163 | 149 | |
| 164 | ```sh | |
| 150 | #+begin_src sh | |
| 165 | 151 | touch git-daemon-export-ok |
| 166 | ``` | |
| 167 | ||
| 168 | ## Change the Login Shell for `git` | |
| 152 | #+end_src | |
| 169 | 153 | |
| 170 | To make sure that the `git` user is only used for git | |
| 171 | operations and nothing else, you need to change the user's login shell. | |
| 172 | To do this, simply use the `chsh` command: | |
| 154 | * Change the Login Shell for =git= | |
| 155 | To make sure that the =git= user is only used for git operations and | |
| 156 | nothing else, you need to change the user's login shell. To do this, | |
| 157 | simply use the =chsh= command: | |
| 173 | 158 | |
| 174 | ```sh | |
| 159 | #+begin_src sh | |
| 175 | 160 | sudo chsh git |
| 176 | ``` | |
| 161 | #+end_src | |
| 177 | 162 | |
| 178 | The interactive prompt will ask which shell you want the | |
| 179 | `git` user to use. You must use the following value: | |
| 163 | The interactive prompt will ask which shell you want the =git= user to | |
| 164 | use. You must use the following value: | |
| 180 | 165 | |
| 181 | ```sh | |
| 166 | #+begin_src sh | |
| 182 | 167 | /usr/bin/git-shell |
| 183 | ``` | |
| 184 | ||
| 185 | Once done, no one will be able to SSH to the `git` user or | |
| 186 | execute commands other than the standard git commands. | |
| 168 | #+end_src | |
| 187 | 169 | |
| 188 | ## Opening the Firewall | |
| 170 | Once done, no one will be able to SSH to the =git= user or execute | |
| 171 | commands other than the standard git commands. | |
| 189 | 172 | |
| 173 | * Opening the Firewall | |
| 190 | 174 | Don't forget to open up ports on the device firewall and network |
| 191 | 175 | firewall if you want to access these repositories publicly. If you're |
| 192 | using default ports, forward ports `22` (ssh) and | |
| 193 | `9418` (git) from your router to your server's IP address. | |
| 176 | using default ports, forward ports =22= (ssh) and =9418= (git) from your | |
| 177 | router to your server's IP address. | |
| 194 | 178 | |
| 195 | 179 | If your server also has a firewall, ensure that the firewall allows the |
| 196 | 180 | same ports that are forwarded from the router. For example, if you use |
| 197 | `ufw`: | |
| 181 | =ufw=: | |
| 198 | 182 | |
| 199 | ```sh | |
| 183 | #+begin_src sh | |
| 200 | 184 | sudo ufw allow 22 |
| 201 | 185 | sudo ufw allow 9418 |
| 202 | ``` | |
| 186 | #+end_src | |
| 203 | 187 | |
| 204 | ### Non-Standard SSH Ports | |
| 205 | ||
| 206 | If you use a non-standard port for SSH, such as `9876`, you | |
| 207 | will need to create an SSH configuration file on your local development | |
| 208 | machine in order to connect to your server's git repositories. | |
| 188 | ** Non-Standard SSH Ports | |
| 189 | If you use a non-standard port for SSH, such as =9876=, you will need to | |
| 190 | create an SSH configuration file on your local development machine in | |
| 191 | order to connect to your server's git repositories. | |
| 209 | 192 | |
| 210 | 193 | To do this, you'll need to define your custom port on your client |
| 211 | machine in your `~/.ssh/config` file: | |
| 194 | machine in your =~/.ssh/config= file: | |
| 212 | 195 | |
| 213 | ```sh | |
| 196 | #+begin_src sh | |
| 214 | 197 | nano ~/.ssh/config |
| 215 | ``` | |
| 198 | #+end_src | |
| 216 | 199 | |
| 217 | ```conf | |
| 200 | #+begin_src conf | |
| 218 | 201 | Host git.example.com |
| 219 | 202 | # HostName can be a URL or an IP address |
| 220 | 203 | HostName git.example.com |
| 221 | 204 | Port 9876 |
| 222 | 205 | User git |
| 223 | ``` | |
| 224 | ||
| 225 | ### Testing SSH | |
| 206 | #+end_src | |
| 226 | 207 | |
| 208 | ** Testing SSH | |
| 227 | 209 | There are two main syntaxes you can use to manage git over SSH: |
| 228 | 210 | |
| 229 | - `git clone [user@]server:project.git` | |
| 230 | - `git clone ssh://[user@]server/project.git` | |
| 211 | - =git clone [user@]server:project.git= | |
| 212 | - =git clone ssh://[user@]server/project.git= | |
| 231 | 213 | |
| 232 | I prefer the first, which is an `scp`-like syntax. To test | |
| 233 | it, try to clone the test repository you set up on the server: | |
| 214 | I prefer the first, which is an =scp=-like syntax. To test it, try to | |
| 215 | clone the test repository you set up on the server: | |
| 234 | 216 | |
| 235 | ```sh | |
| 217 | #+begin_src sh | |
| 236 | 218 | git clone git@git.example.com:/git/test.git |
| 237 | ``` | |
| 238 | ||
| 239 | ## Enabling Read-Only Access | |
| 219 | #+end_src | |
| 240 | 220 | |
| 221 | * Enabling Read-Only Access | |
| 241 | 222 | If you want people to be able to clone any repository where you've |
| 242 | placed a `git-daemon-export-ok` file, you will need to start | |
| 243 | the git daemon. | |
| 223 | placed a =git-daemon-export-ok= file, you will need to start the git | |
| 224 | daemon. | |
| 244 | 225 | |
| 245 | To do this on a system with `systemd`, create a service file: | |
| 226 | To do this on a system with =systemd=, create a service file: | |
| 246 | 227 | |
| 247 | ```sh | |
| 228 | #+begin_src sh | |
| 248 | 229 | sudo nano /etc/systemd/system/git-daemon.service |
| 249 | ``` | |
| 230 | #+end_src | |
| 250 | 231 | |
| 251 | Inside the `git-daemon.service` file, paste the following: | |
| 232 | Inside the =git-daemon.service= file, paste the following: | |
| 252 | 233 | |
| 253 | ```conf | |
| 234 | #+begin_src conf | |
| 254 | 235 | [Unit] |
| 255 | 236 | Description=Start Git Daemon |
| 256 | 237 | |
| @@ -269,24 +250,23 @@ Group=git | ||
| 269 | 250 | |
| 270 | 251 | [Install] |
| 271 | 252 | WantedBy=multi-user.target |
| 272 | ``` | |
| 253 | #+end_src | |
| 273 | 254 | |
| 274 | 255 | Once created, enable and start the service: |
| 275 | 256 | |
| 276 | ```sh | |
| 257 | #+begin_src sh | |
| 277 | 258 | sudo systemctl enable git-daemon.service |
| 278 | 259 | sudo systemctl start git-daemon.service |
| 279 | ``` | |
| 260 | #+end_src | |
| 280 | 261 | |
| 281 | To clone read-only via the `git://` protocol, you can use the | |
| 282 | following syntax: | |
| 262 | To clone read-only via the =git://= protocol, you can use the following | |
| 263 | syntax: | |
| 283 | 264 | |
| 284 | ```sh | |
| 265 | #+begin_src sh | |
| 285 | 266 | git clone git://git.example.com/test.git |
| 286 | ``` | |
| 287 | ||
| 288 | ## Migrating Repositories | |
| 267 | #+end_src | |
| 289 | 268 | |
| 269 | * Migrating Repositories | |
| 290 | 270 | At this point, we have a working git server that works with both SSH and |
| 291 | 271 | read-only access. |
| 292 | 272 | |
| @@ -296,49 +276,44 @@ my new source of truth: | ||
| 296 | 276 | |
| 297 | 277 | Server: |
| 298 | 278 | |
| 299 | ```sh | |
| 279 | #+begin_src sh | |
| 300 | 280 | su git |
| 301 | 281 | mkdir /git/<REPOSITORY_NAME>.git && cd /git/<REPOSITORY_NAME>.git |
| 302 | 282 | git init --bare |
| 303 | 283 | |
| 304 | 284 | # If you want to make this repo viewable/cloneable to the public |
| 305 | 285 | touch git-daemon-export-ok |
| 306 | ``` | |
| 286 | #+end_src | |
| 307 | 287 | |
| 308 | 288 | Client: |
| 309 | 289 | |
| 310 | ```sh | |
| 290 | #+begin_src sh | |
| 311 | 291 | git clone git@<PREVIOUS_HOST>:<REPOSITORY_NAME> |
| 312 | 292 | git remote set-url origin git@git.EXAMPLE.COM:/git/<REPOSITORY_NAME>.git |
| 313 | 293 | git push |
| 314 | ``` | |
| 315 | ||
| 316 | ## Optional Web View: `cgit` | |
| 294 | #+end_src | |
| 317 | 295 | |
| 296 | * Optional Web View: =cgit= | |
| 318 | 297 | If you want a web viewer for your repositories, you can use various |
| 319 | tools, such as `gitweb`, `cgit`, or | |
| 320 | `klaus`. I chose `cgit` due to its simple | |
| 321 | interface and fairly easy set-up (compared to others). Not to mention | |
| 322 | that the [Linux kernel uses `cgit`](https://git.kernel.org/). | |
| 298 | tools, such as =gitweb=, =cgit=, or =klaus=. I chose =cgit= due to its | |
| 299 | simple interface and fairly easy set-up (compared to others). Not to | |
| 300 | mention that the [[https://git.kernel.org/][Linux kernel uses =cgit=]]. | |
| 323 | 301 | |
| 324 | ### Docker Compose | |
| 302 | ** Docker Compose | |
| 303 | Instead of using my previous method of using a =docker run= command, | |
| 304 | I've updated this section to use =docker-compose= instead for an easier | |
| 305 | installation and simpler management and configuration. | |
| 325 | 306 | |
| 326 | Instead of using my previous method of using a `docker run` | |
| 327 | command, I've updated this section to use `docker-compose` | |
| 328 | instead for an easier installation and simpler management and | |
| 329 | configuration. | |
| 330 | ||
| 331 | In order to use Docker Compose, you will set up a | |
| 332 | `docker-compose.yml` file to automatically connect resources | |
| 333 | like the repositories, `cgitrc`, and various files or folders | |
| 334 | to the `cgit` container you're creating: | |
| 307 | In order to use Docker Compose, you will set up a =docker-compose.yml= | |
| 308 | file to automatically connect resources like the repositories, =cgitrc=, | |
| 309 | and various files or folders to the =cgit= container you're creating: | |
| 335 | 310 | |
| 336 | ```sh | |
| 311 | #+begin_src sh | |
| 337 | 312 | mkdir ~/cgit && cd ~/cgit |
| 338 | 313 | nano docker-compose.yml |
| 339 | ``` | |
| 314 | #+end_src | |
| 340 | 315 | |
| 341 | ```conf | |
| 316 | #+begin_src conf | |
| 342 | 317 | # docker-compose.yml |
| 343 | 318 | version: '3' |
| 344 | 319 | |
| @@ -354,31 +329,29 @@ services: | ||
| 354 | 329 | ports: |
| 355 | 330 | - "8763:80" |
| 356 | 331 | restart: always |
| 357 | ``` | |
| 332 | #+end_src | |
| 358 | 333 | |
| 359 | 334 | Then, just start the container: |
| 360 | 335 | |
| 361 | ```sh | |
| 336 | #+begin_src sh | |
| 362 | 337 | sudo docker-compose up -d |
| 363 | ``` | |
| 338 | #+end_src | |
| 364 | 339 | |
| 365 | 340 | Once it's finished installing, you can access the site at |
| 366 | `<SERVER_IP>:8763` or use a reverse-proxy service to forward | |
| 367 | `cgit` to a URL, such as `git.example.com`. See | |
| 368 | the next section for more details on reverse proxying a URL to a local | |
| 369 | port. | |
| 370 | ||
| 371 | ### Nginx Reverse Proxy | |
| 341 | =<SERVER_IP>:8763= or use a reverse-proxy service to forward =cgit= to a | |
| 342 | URL, such as =git.example.com=. See the next section for more details on | |
| 343 | reverse proxying a URL to a local port. | |
| 372 | 344 | |
| 373 | I am using Nginx as my reverse proxy so that the `cgit` | |
| 374 | Docker container can use `git.example.com` as its URL. To do | |
| 375 | so, I simply created the following configuration file: | |
| 345 | ** Nginx Reverse Proxy | |
| 346 | I am using Nginx as my reverse proxy so that the =cgit= Docker container | |
| 347 | can use =git.example.com= as its URL. To do so, I simply created the | |
| 348 | following configuration file: | |
| 376 | 349 | |
| 377 | ```sh | |
| 350 | #+begin_src sh | |
| 378 | 351 | sudo nano /etc/nginx/sites-available/git.example.com |
| 379 | ``` | |
| 352 | #+end_src | |
| 380 | 353 | |
| 381 | ```conf | |
| 354 | #+begin_src conf | |
| 382 | 355 | server { |
| 383 | 356 | listen 80; |
| 384 | 357 | server_name git.example.com; |
| @@ -412,67 +385,65 @@ server { | ||
| 412 | 385 | include /etc/letsencrypt/options-ssl-nginx.conf; |
| 413 | 386 | ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; |
| 414 | 387 | } |
| 415 | ``` | |
| 388 | #+end_src | |
| 416 | 389 | |
| 417 | 390 | Once created, symlink it and restart the web server. |
| 418 | 391 | |
| 419 | ```sh | |
| 392 | #+begin_src sh | |
| 420 | 393 | sudo ln -s /etc/nginx/sites-available/git.example.com /etc/nginx/sites-enabled/ |
| 421 | 394 | sudo systemctl restart nginx.service |
| 422 | ``` | |
| 395 | #+end_src | |
| 423 | 396 | |
| 424 | As we can see below, my site at `git.example.com` is | |
| 425 | available and running: | |
| 397 | As we can see below, my site at =git.example.com= is available and | |
| 398 | running: | |
| 426 | 399 | |
| 427 | ### Settings Up Git Details | |
| 400 | ** Settings Up Git Details | |
| 401 | Once you have =cgit= running, you can add some small details, such as | |
| 402 | repository owners and descriptions by editing the following files within | |
| 403 | each repository. | |
| 428 | 404 | |
| 429 | Once you have `cgit` running, you can add some small details, | |
| 430 | such as repository owners and descriptions by editing the following | |
| 431 | files within each repository. | |
| 405 | Alternatively, you can use the =cgitrc= file to edit these details if | |
| 406 | you only care to edit them for the purpose of seeing them on your | |
| 407 | website. | |
| 432 | 408 | |
| 433 | Alternatively, you can use the `cgitrc` file to edit these | |
| 434 | details if you only care to edit them for the purpose of seeing them on | |
| 435 | your website. | |
| 409 | The =description= file within the repository on your server will display | |
| 410 | the description online. | |
| 436 | 411 | |
| 437 | The `description` file within the repository on your server | |
| 438 | will display the description online. | |
| 439 | ||
| 440 | ```sh | |
| 412 | #+begin_src sh | |
| 441 | 413 | cd /git/example.git |
| 442 | 414 | nano description |
| 443 | ``` | |
| 415 | #+end_src | |
| 444 | 416 | |
| 445 | You can add a `[gitweb]` block to the `config` | |
| 446 | file in order to display the owner of the repository. | |
| 417 | You can add a =[gitweb]= block to the =config= file in order to display | |
| 418 | the owner of the repository. | |
| 447 | 419 | |
| 448 | ```sh | |
| 420 | #+begin_src sh | |
| 449 | 421 | cd /git/example.git |
| 450 | 422 | nano config |
| 451 | ``` | |
| 423 | #+end_src | |
| 452 | 424 | |
| 453 | ```conf | |
| 425 | #+begin_src conf | |
| 454 | 426 | [gitweb] |
| 455 | 427 | owner = "YourName" |
| 456 | ``` | |
| 428 | #+end_src | |
| 457 | 429 | |
| 458 | 430 | Note that you can ignore the configuration within each repository and |
| 459 | simply set up this information in the `cgitrc` file, if you | |
| 460 | want to do it that way. | |
| 461 | ||
| 462 | ### Editing `cgit` | |
| 431 | simply set up this information in the =cgitrc= file, if you want to do | |
| 432 | it that way. | |
| 463 | 433 | |
| 464 | In order to edit certain items within `cgit`, you need to | |
| 465 | edit the `cgitrc` file. | |
| 434 | ** Editing =cgit= | |
| 435 | In order to edit certain items within =cgit=, you need to edit the | |
| 436 | =cgitrc= file. | |
| 466 | 437 | |
| 467 | ```sh | |
| 438 | #+begin_src sh | |
| 468 | 439 | nano ~/cgit/cgitrc |
| 469 | ``` | |
| 440 | #+end_src | |
| 470 | 441 | |
| 471 | Below is an example configuration for `cgitrc`. You can find | |
| 472 | all the configuration options within the [configuration manual] | |
| 473 | (<https://git.zx2c4.com/cgit/plain/cgitrc.5.txt>). | |
| 442 | Below is an example configuration for =cgitrc=. You can find all the | |
| 443 | configuration options within the [configuration manual] | |
| 444 | ([[https://git.zx2c4.com/cgit/plain/cgitrc.5.txt]]). | |
| 474 | 445 | |
| 475 | ```conf | |
| 446 | #+begin_src conf | |
| 476 | 447 | css=/cgit.css |
| 477 | 448 | logo=/logo.png |
| 478 | 449 | favicon=/favicon.png |
| @@ -544,111 +515,103 @@ repo.path=/git/test.git | ||
| 544 | 515 | repo.readme=:README.md |
| 545 | 516 | repo.owner=John Doe |
| 546 | 517 | repo.desc=An example repository! |
| 547 | ``` | |
| 548 | ||
| 549 | ### Final Fixes: Syntax Highlighting & README Rendering | |
| 518 | #+end_src | |
| 550 | 519 | |
| 520 | ** Final Fixes: Syntax Highlighting & README Rendering | |
| 551 | 521 | After completing my initial install and playing around with it for a few |
| 552 | 522 | days, I noticed two issues: |
| 553 | 523 | |
| 554 | 1. Syntax highlighting did not work when viewing the source code within | |
| 555 | a file. | |
| 556 | 2. The `about` tab within a repository was not rendered to | |
| 557 | HTML. | |
| 524 | 1. Syntax highlighting did not work when viewing the source code within | |
| 525 | a file. | |
| 526 | 2. The =about= tab within a repository was not rendered to HTML. | |
| 558 | 527 | |
| 559 | 528 | The following process fixes these issues. To start, let's go to the |
| 560 | `cgit` directory where we were editing our configuration file | |
| 561 | earlier. | |
| 529 | =cgit= directory where we were editing our configuration file earlier. | |
| 562 | 530 | |
| 563 | ```sh | |
| 531 | #+begin_src sh | |
| 564 | 532 | cd ~/cgit |
| 565 | ``` | |
| 533 | #+end_src | |
| 566 | 534 | |
| 567 | 535 | In here, create two folders that will hold our syntax files: |
| 568 | 536 | |
| 569 | ```sh | |
| 537 | #+begin_src sh | |
| 570 | 538 | mkdir filters && mkdir filters/html-converters && cd filters |
| 571 | ``` | |
| 539 | #+end_src | |
| 572 | 540 | |
| 573 | 541 | Next, download the default filters: |
| 574 | 542 | |
| 575 | ```sh | |
| 543 | #+begin_src sh | |
| 576 | 544 | curl https://git.zx2c4.com/cgit/plain/filters/about-formatting.sh > about-formatting.sh |
| 577 | 545 | chmod 755 about-formatting.sh |
| 578 | 546 | curl https://git.zx2c4.com/cgit/plain/filters/syntax-highlighting.py > syntax-highlighting.py |
| 579 | 547 | chmod 755 syntax-highlighting.py |
| 580 | ``` | |
| 548 | #+end_src | |
| 581 | 549 | |
| 582 | 550 | Finally, download the HTML conversion files you need. The example below |
| 583 | 551 | downloads the Markdown converter: |
| 584 | 552 | |
| 585 | ```sh | |
| 553 | #+begin_src sh | |
| 586 | 554 | cd html-converters |
| 587 | 555 | curl https://git.zx2c4.com/cgit/plain/filters/html-converters/md2html > md2html |
| 588 | 556 | chmod 755 md2html |
| 589 | ``` | |
| 557 | #+end_src | |
| 590 | 558 | |
| 591 | If you need other filters or html-converters found within [the cgit | |
| 592 | project files](https://git.zx2c4.com/cgit/tree/filters), repeat the | |
| 593 | `curl` and `chmod` process above for whichever | |
| 594 | files you need. | |
| 559 | If you need other filters or html-converters found within | |
| 560 | [[https://git.zx2c4.com/cgit/tree/filters][the cgit project files]], | |
| 561 | repeat the =curl= and =chmod= process above for whichever files you | |
| 562 | need. | |
| 595 | 563 | |
| 596 | 564 | However, formatting will not work quite yet since the Docker cgit |
| 597 | container we're using doesn't have the formatting package installed. | |
| 598 | You can install this easily by install Python 3+ and the | |
| 599 | `pygments` package: | |
| 565 | container we're using doesn't have the formatting package installed. You | |
| 566 | can install this easily by install Python 3+ and the =pygments= package: | |
| 600 | 567 | |
| 601 | ```sh | |
| 568 | #+begin_src sh | |
| 602 | 569 | # Enter the container's command line |
| 603 | 570 | sudo docker exec -it cgit bash |
| 604 | ``` | |
| 571 | #+end_src | |
| 605 | 572 | |
| 606 | ```sh | |
| 573 | #+begin_src sh | |
| 607 | 574 | # Install the necessary packages and then exit |
| 608 | 575 | yum update -y && \ |
| 609 | 576 | yum upgrade -y && \ |
| 610 | 577 | yum install python3 python3-pip -y && \ |
| 611 | 578 | pip3 install markdown pygments && \ |
| 612 | 579 | exit |
| 613 | ``` | |
| 580 | #+end_src | |
| 614 | 581 | |
| 615 | **You will need to enter the cgit docker container and re-run these | |
| 616 | `yum` commands every time you kill and restart the | |
| 617 | container!** | |
| 582 | *You will need to enter the cgit docker container and re-run these =yum= | |
| 583 | commands every time you kill and restart the container!* | |
| 618 | 584 | |
| 619 | 585 | If not done already, we need to add the following variables to our |
| 620 | `cgitrc` file in order for `cgit` to know where | |
| 621 | our filtering files are: | |
| 586 | =cgitrc= file in order for =cgit= to know where our filtering files are: | |
| 622 | 587 | |
| 623 | ```conf | |
| 588 | #+begin_src conf | |
| 624 | 589 | # Highlight source code with python pygments-based highlighter |
| 625 | 590 | source-filter=/var/www/htdocs/cgit/filters/syntax-highlighting.py |
| 626 | 591 | |
| 627 | 592 | # Format markdown, restructuredtext, manpages, text files, and html files |
| 628 | 593 | # through the right converters |
| 629 | 594 | about-filter=/var/www/htdocs/cgit/filters/about-formatting.sh |
| 630 | ``` | |
| 595 | #+end_src | |
| 631 | 596 | |
| 632 | 597 | Now you should see that syntax highlighting and README rendering to the |
| 633 | `about` tab is fixed. | |
| 634 | ||
| 635 | ### Theming | |
| 598 | =about= tab is fixed. | |
| 636 | 599 | |
| 600 | ** Theming | |
| 637 | 601 | I won't go into much detail in this section, but you can fully theme |
| 638 | your installation of `cgit` since you have access to the | |
| 639 | `cgit.css` file in your web root. This is another file you | |
| 640 | can add as a volume to the `docker-compose.yml` file if you | |
| 641 | want to edit this without entering the container's command line. | |
| 642 | ||
| 643 | ## :warning: Remember to Back Up Your Data! | |
| 602 | your installation of =cgit= since you have access to the =cgit.css= file | |
| 603 | in your web root. This is another file you can add as a volume to the | |
| 604 | =docker-compose.yml= file if you want to edit this without entering the | |
| 605 | container's command line. | |
| 644 | 606 | |
| 607 | *** :warning: Remember to Back Up Your Data! | |
| 645 | 608 | The last thing to note is that running services on your own equipment |
| 646 | 609 | means that you're assuming a level of risk that exists regarding data |
| 647 | 610 | loss, catastrophes, etc. In order to reduce the impact of any such |
| 648 | 611 | occurrence, I suggest backing up your data regularly. |
| 649 | 612 | |
| 650 | Backups can be automated via `cron`, by hooking your base | |
| 651 | directory up to a cloud provider, or even setting up hooks to push all | |
| 652 | repository info to git mirrors on other git hosts. Whatever the method, | |
| 653 | make sure that your data doesn't vanish in the event that your drives | |
| 654 | or servers fail. | |
| 613 | Backups can be automated via =cron=, by hooking your base directory up | |
| 614 | to a cloud provider, or even setting up hooks to push all repository | |
| 615 | info to git mirrors on other git hosts. Whatever the method, make sure | |
| 616 | that your data doesn't vanish in the event that your drives or servers | |
| 617 | fail. | |
content/blog/2022-07-14-gnupg.md → blog/gnupg/index.org renamed +97 −113
| @@ -1,30 +1,27 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-07-14 | |
| 3 | title = "GNU Privacy Guard (GPG)" | |
| 4 | description = "Learn how to create a PGP key with GNU Privacy Guard (GPG)." | |
| 5 | +++ | |
| 1 | #+title: GNU Privacy Guard (GPG) | |
| 2 | #+date: 2022-07-14 | |
| 3 | #+description: Learn how to create a PGP key with GNU Privacy Guard (GPG). | |
| 4 | #+filetags: :privacy: | |
| 6 | 5 | |
| 7 | ## The History of GPG | |
| 8 | ||
| 9 | [GNU Privacy Guard](https://gnupg.org/), also known as GnuPG and GPG, is | |
| 10 | a free ("free" as in both speech and beer) software that fully | |
| 11 | implements the OpenPGP Message Format documented in [RFC | |
| 12 | 4880](https://www.rfc-editor.org/rfc/rfc4880). | |
| 6 | * The History of GPG | |
| 7 | [[https://gnupg.org/][GNU Privacy Guard]], also known as GnuPG and GPG, | |
| 8 | is a free ("free" as in both speech and beer) software that fully | |
| 9 | implements the OpenPGP Message Format documented in | |
| 10 | [[https://www.rfc-editor.org/rfc/rfc4880][RFC 4880]]. | |
| 13 | 11 | |
| 14 | 12 | I won't go in-depth on the full history of the software in this post, |
| 15 | 13 | but it is important to understand that GPG is not the same as PGP |
| 16 | 14 | (Pretty Good Privacy), which is a different implementation of RFC 4880. |
| 17 | 15 | However, GPG was designed to interoperate with PGP. |
| 18 | 16 | |
| 19 | GPG was originally developed in the late 1990s by [Werner | |
| 20 | Koch](https://en.wikipedia.org/wiki/Werner_Koch) and has historically | |
| 21 | been funded generously by the German government. | |
| 22 | ||
| 23 | Now that we have all the high-level info out of the way, let's dive | |
| 24 | into the different aspects of GPG and its uses. | |
| 17 | GPG was originally developed in the late 1990s by | |
| 18 | [[https://en.wikipedia.org/wiki/Werner_Koch][Werner Koch]] and has | |
| 19 | historically been funded generously by the German government. | |
| 25 | 20 | |
| 26 | ## Encryption Algorithms | |
| 21 | Now that we have all the high-level info out of the way, let's dive into | |
| 22 | the different aspects of GPG and its uses. | |
| 27 | 23 | |
| 24 | * Encryption Algorithms | |
| 28 | 25 | GPG supports a wide range of different encryption algorithms, including |
| 29 | 26 | public-key, cipher, hash, and compression algorithms. The support for |
| 30 | 27 | these algorithms has grown since the adoption of the Libgcrypt library |
| @@ -34,7 +31,7 @@ As you will be able to see below in an example of a full key generation | ||
| 34 | 31 | with the GPG command line tool, GPG recommends the following algorithms |
| 35 | 32 | to new users: |
| 36 | 33 | |
| 37 | ```sh | |
| 34 | #+begin_src sh | |
| 38 | 35 | Please select what kind of key you want: |
| 39 | 36 | (1) RSA and RSA |
| 40 | 37 | (2) DSA and Elgamal |
| @@ -42,72 +39,66 @@ Please select what kind of key you want: | ||
| 42 | 39 | (4) RSA (sign only) |
| 43 | 40 | (9) ECC (sign and encrypt) *default* |
| 44 | 41 | (10) ECC (sign only) |
| 45 | ``` | |
| 42 | #+end_src | |
| 46 | 43 | |
| 47 | 44 | I am not doing an in-depth explanation here in order to keep the focus |
| 48 | 45 | on GPG and not encryption algorithms. If you want a deep dive into |
| 49 | 46 | cryptography or encryption algorithms, please read my other posts: |
| 50 | 47 | |
| 51 | - [AES Encryption](/blog/aes-encryption/) (2018) | |
| 52 | - [Cryptography Basics](/blog/cryptography-basics/) (2020) | |
| 53 | ||
| 54 | ### Vulnerabilities | |
| 48 | - [[../aes-encryption/][AES Encryption]] (2018) | |
| 49 | - [[../cryptography-basics/][Cryptography Basics]] (2020) | |
| 55 | 50 | |
| 51 | ** Vulnerabilities | |
| 56 | 52 | As of 2022-07-14, there are a few different vulnerabilities associated |
| 57 | 53 | with GPG or the libraries it uses: |
| 58 | 54 | |
| 59 | - GPG versions 1.0.2--1.2.3 contains a bug where "as soon as one | |
| 60 | (GPG-generated) ElGamal signature of an arbitrary message is | |
| 61 | released, one can recover the signer's private key in less than a | |
| 62 | second on a PC." | |
| 63 | ([Source](https://www.di.ens.fr/~pnguyen/pub_Ng04.htm)) | |
| 64 | - GPG versions prior to 1.4.2.1 contain a false positive signature | |
| 65 | verification bug. | |
| 66 | ([Source](https://lists.gnupg.%20org/pipermail/gnupg-announce/2006q1/000211.html)) | |
| 67 | - GPG versions prior to 1.4.2.2 cannot detect injection of unsigned | |
| 68 | data. ( | |
| 69 | [Source](https://lists.gnupg.org/pipermail/gnupg-announce/2006q1/000218.html)) | |
| 70 | - Libgcrypt, a library used by GPG, contained a bug which enabled full | |
| 71 | key recovery for RSA-1024 and some RSA-2048 keys. This was resolved | |
| 72 | in a GPG update in 2017. | |
| 73 | ([Source](https://lwn.net/Articles/727179/)) | |
| 74 | - The [ROCA | |
| 75 | Vulnerability](https://en.wikipedia.org/wiki/ROCA_vulnerability) | |
| 76 | affects RSA keys generated by YubiKey 4 tokens. | |
| 77 | ([Source](https://crocs.fi.%20muni.cz/_media/public/papers/nemec_roca_ccs17_preprint.pdf)) | |
| 78 | - The [SigSpoof Attack](https://en.wikipedia.org/wiki/SigSpoof) allows | |
| 79 | an attacker to spoof digital signatures. | |
| 80 | ([Source](https://arstechnica.%20com/information-technology/2018/06/decades-old-pgp-bug-allowed-hackers-to-spoof-just-about-anyones-signature/)) | |
| 81 | - Libgcrypt 1.9.0 contains a severe flaw related to a heap buffer | |
| 82 | overflow, fixed in Libgcrypt 1.9.1 | |
| 83 | ([Source](https://web.archive.%20org/web/20210221012505/https://www.theregister.com/2021/01/29/severe_libgcrypt_bug/)) | |
| 84 | ||
| 85 | ## Platforms | |
| 86 | ||
| 87 | Originally developed as a command-line program for *nix systems, GPG | |
| 88 | now has a wealth of front-end applications and libraries available for | |
| 55 | - GPG versions 1.0.2--1.2.3 contains a bug where "as soon as one | |
| 56 | (GPG-generated) ElGamal signature of an arbitrary message is released, | |
| 57 | one can recover the signer's private key in less than a second on a | |
| 58 | PC." ([[https://www.di.ens.fr/~pnguyen/pub_Ng04.htm][Source]]) | |
| 59 | - GPG versions prior to 1.4.2.1 contain a false positive signature | |
| 60 | verification bug. | |
| 61 | ([[https://lists.gnupg.%20org/pipermail/gnupg-announce/2006q1/000211.html][Source]]) | |
| 62 | - GPG versions prior to 1.4.2.2 cannot detect injection of unsigned | |
| 63 | data. ( | |
| 64 | [[https://lists.gnupg.org/pipermail/gnupg-announce/2006q1/000218.html][Source]]) | |
| 65 | - Libgcrypt, a library used by GPG, contained a bug which enabled full | |
| 66 | key recovery for RSA-1024 and some RSA-2048 keys. This was resolved in | |
| 67 | a GPG update in 2017. ([[https://lwn.net/Articles/727179/][Source]]) | |
| 68 | - The [[https://en.wikipedia.org/wiki/ROCA_vulnerability][ROCA | |
| 69 | Vulnerability]] affects RSA keys generated by YubiKey 4 tokens. | |
| 70 | ([[https://crocs.fi.%20muni.cz/_media/public/papers/nemec_roca_ccs17_preprint.pdf][Source]]) | |
| 71 | - The [[https://en.wikipedia.org/wiki/SigSpoof][SigSpoof Attack]] allows | |
| 72 | an attacker to spoof digital signatures. | |
| 73 | ([[https://arstechnica.%20com/information-technology/2018/06/decades-old-pgp-bug-allowed-hackers-to-spoof-just-about-anyones-signature/][Source]]) | |
| 74 | - Libgcrypt 1.9.0 contains a severe flaw related to a heap buffer | |
| 75 | overflow, fixed in Libgcrypt 1.9.1 | |
| 76 | ([[https://web.archive.%20org/web/20210221012505/https://www.theregister.com/2021/01/29/severe_libgcrypt_bug/][Source]]) | |
| 77 | ||
| 78 | *** Platforms | |
| 79 | Originally developed as a command-line program for *nix systems, GPG now | |
| 80 | has a wealth of front-end applications and libraries available for | |
| 89 | 81 | end-users. However, the most recommended programs remain the same: |
| 90 | 82 | |
| 91 | - [GnuPG](https://gnupg.org) for Linux (depending on distro) | |
| 92 | - [Gpg4win](https://gpg4win.org) for Windows | |
| 93 | - [GPGTools](https://gpgtools.org) for macOS | |
| 94 | ||
| 95 | ## Creating a Key Pair | |
| 83 | - [[https://gnupg.org][GnuPG]] for Linux (depending on distro) | |
| 84 | - [[https://gpg4win.org][Gpg4win]] for Windows | |
| 85 | - [[https://gpgtools.org][GPGTools]] for macOS | |
| 96 | 86 | |
| 87 | * Creating a Key Pair | |
| 97 | 88 | In order to create a GPG key pair, a user would first need to install |
| 98 | GPG on their system. If we're assuming that the user is on Fedora | |
| 99 | Linux, they would execute the following: | |
| 89 | GPG on their system. If we're assuming that the user is on Fedora Linux, | |
| 90 | they would execute the following: | |
| 100 | 91 | |
| 101 | ```sh | |
| 92 | #+begin_src sh | |
| 102 | 93 | sudo dnf install gpg |
| 103 | ``` | |
| 94 | #+end_src | |
| 104 | 95 | |
| 105 | 96 | Once installed, a user can create a new key pair with the following |
| 106 | 97 | command(s): |
| 107 | 98 | |
| 108 | ```sh | |
| 99 | #+begin_src sh | |
| 109 | 100 | gpg --full-generate-key |
| 110 | ``` | |
| 101 | #+end_src | |
| 111 | 102 | |
| 112 | 103 | GPG will walk the user through an interactive setup that asks for an |
| 113 | 104 | algorithm preference, expiration date, name, and email to associate with |
| @@ -116,7 +107,7 @@ this key. | ||
| 116 | 107 | See the following example key set-up for a default key generation using |
| 117 | 108 | the GnuPG command-line interface: |
| 118 | 109 | |
| 119 | ```sh | |
| 110 | #+begin_src sh | |
| 120 | 111 | gpg (GnuPG) 2.3.6; Copyright (C) 2021 Free Software Foundation, Inc. |
| 121 | 112 | This is free software: you are free to change and redistribute it. |
| 122 | 113 | There is NO WARRANTY, to the extent permitted by law. |
| @@ -168,20 +159,19 @@ pub ed25519 2022-07-14 [SC] | ||
| 168 | 159 | E955B7700FFC11EF51C2BA1FE096AACDD4C32E9C |
| 169 | 160 | uid John Doe (test key) <johndoe@example.com> |
| 170 | 161 | sub cv25519 2022-07-14 [E] |
| 171 | ``` | |
| 162 | #+end_src | |
| 172 | 163 | |
| 173 | 164 | Please note that GUI apps may differ slightly from the GPG command-line |
| 174 | 165 | interface. |
| 175 | 166 | |
| 176 | ## Common Usage | |
| 177 | ||
| 167 | * Common Usage | |
| 178 | 168 | As noted in RFC 4880, the general functions of OpenPGP are as follows: |
| 179 | 169 | |
| 180 | - digital signatures | |
| 181 | - encryption | |
| 182 | - compression | |
| 183 | - Radix-64 conversion | |
| 184 | - key management and certificate services | |
| 170 | - digital signatures | |
| 171 | - encryption | |
| 172 | - compression | |
| 173 | - Radix-64 conversion | |
| 174 | - key management and certificate services | |
| 185 | 175 | |
| 186 | 176 | From this, you can probably gather that the main use of GPG is for |
| 187 | 177 | encrypting data and/or signing the data with a key. The purpose of |
| @@ -190,8 +180,7 @@ recipient(s) can access the data. | ||
| 190 | 180 | |
| 191 | 181 | Let's explore some specific GPG use-cases. |
| 192 | 182 | |
| 193 | ||
| 194 | ||
| 183 | ||
| 195 | 184 | One of the more popular uses of GPG is to sign and/or encrypt emails. |
| 196 | 185 | With the use of a GPG keypair, you can encrypt a message, its subject, |
| 197 | 186 | and even the attachments within. |
| @@ -206,8 +195,8 @@ The second process, regarding the actual encryption of the message and | ||
| 206 | 195 | its contents, works by using a combination of the sender's keys and the |
| 207 | 196 | recipient's keys. This process may vary slightly by implementation, but |
| 208 | 197 | it most commonly uses asymmetric cryptography, also known as public-key |
| 209 | cryptography. In this version of encryption, the sender's private key | |
| 210 | to sign the message and a combination of the sender's keys and the | |
| 198 | cryptography. In this version of encryption, the sender's private key to | |
| 199 | sign the message and a combination of the sender's keys and the | |
| 211 | 200 | recipient's public key to encrypt the message. |
| 212 | 201 | |
| 213 | 202 | If two people each have their own private keys and exchange their public |
| @@ -219,61 +208,57 @@ Implementation of email encryption varies greatly between email clients, | ||
| 219 | 208 | so you will need to reference your email client's documentation to |
| 220 | 209 | ensure you are setting it up correctly for that specific client. |
| 221 | 210 | |
| 222 | ### File Encryption | |
| 223 | ||
| 211 | ** File Encryption | |
| 224 | 212 | As noted in the section above regarding emails, GPG enables users to be |
| 225 | 213 | able to send a message to each other if they are both set-up with GPG |
| 226 | 214 | keys. In this example, I am going to show how a user could send a file |
| 227 | called `example_file.txt` to another user via the | |
| 228 | recipient's email. | |
| 215 | called =example_file.txt= to another user via the recipient's email. | |
| 229 | 216 | |
| 230 | 217 | The sender would find the file they want to send and execute the |
| 231 | 218 | following command: |
| 232 | 219 | |
| 233 | ```sh | |
| 220 | #+begin_src sh | |
| 234 | 221 | gpg --encrypt --output example_file.txt.gpg --recipient \ |
| 235 | 222 | recipient@example.com example_file.txt |
| 236 | ``` | |
| 223 | #+end_src | |
| 237 | 224 | |
| 238 | 225 | Once received, the recipient can decrypt the file with the following |
| 239 | 226 | command: |
| 240 | 227 | |
| 241 | ```sh | |
| 228 | #+begin_src sh | |
| 242 | 229 | gpg --decrypt --output example_file.txt example_file.txt.gpg |
| 243 | ``` | |
| 244 | ||
| 245 | ### Ownership Signatures | |
| 230 | #+end_src | |
| 246 | 231 | |
| 232 | ** Ownership Signatures | |
| 247 | 233 | One important aspect of GPG, especially for developers, is the ability |
| 248 | 234 | to sign data without encrypting it. For example, developers often sign |
| 249 | 235 | code changes when they commit the changes back to a central repository, |
| 250 | 236 | in order to display ownership of who made the changes. This allows other |
| 251 | 237 | users to look at a code change and determine that the change was valid. |
| 252 | 238 | |
| 253 | In order to do this using [Git](https://git-scm.com), the developer | |
| 254 | simply needs to alter the `git commit` command to include the | |
| 255 | `-S` flag. Here's an example: | |
| 239 | In order to do this using [[https://git-scm.com][Git]], the developer | |
| 240 | simply needs to alter the =git commit= command to include the =-S= flag. | |
| 241 | Here's an example: | |
| 256 | 242 | |
| 257 | ```sh | |
| 243 | #+begin_src sh | |
| 258 | 244 | git commit -S -m "my commit message" |
| 259 | ``` | |
| 245 | #+end_src | |
| 260 | 246 | |
| 261 | 247 | As an expansion of the example above, Git users can configure their |
| 262 | 248 | environment with a default key to use by adding their GPG signature: |
| 263 | 249 | |
| 264 | ```sh | |
| 250 | #+begin_src sh | |
| 265 | 251 | git config --global user.signingkey XXXXXXXXXXXXXXXX |
| 266 | ``` | |
| 252 | #+end_src | |
| 267 | 253 | |
| 268 | If you're not sure what your signature is, you can find it titled | |
| 269 | `sig` in the output of this command: | |
| 254 | If you're not sure what your signature is, you can find it titled =sig= | |
| 255 | in the output of this command: | |
| 270 | 256 | |
| 271 | ```sh | |
| 257 | #+begin_src sh | |
| 272 | 258 | gpg --list-signatures |
| 273 | ``` | |
| 274 | ||
| 275 | ### File Integrity | |
| 259 | #+end_src | |
| 276 | 260 | |
| 261 | ** File Integrity | |
| 277 | 262 | When a person generates a signature for data, they are allowing users |
| 278 | 263 | the ability to verify the signature on that data in the future to ensure |
| 279 | 264 | the data has not been corrupted. This is most common with software |
| @@ -283,24 +268,23 @@ replaced with dangerous software. | ||
| 283 | 268 | |
| 284 | 269 | In order to verify signed data, a user needs to have: |
| 285 | 270 | |
| 286 | 1. The signed data | |
| 287 | 2. A signature file | |
| 288 | 3. The public GPG key of the signer | |
| 271 | 1. The signed data | |
| 272 | 2. A signature file | |
| 273 | 3. The public GPG key of the signer | |
| 289 | 274 | |
| 290 | Once the signer's public key is imported on the user's system, and | |
| 291 | they have the data and signature, they can verify the data with the | |
| 292 | following commands: | |
| 275 | Once the signer's public key is imported on the user's system, and they | |
| 276 | have the data and signature, they can verify the data with the following | |
| 277 | commands: | |
| 293 | 278 | |
| 294 | ```sh | |
| 279 | #+begin_src sh | |
| 295 | 280 | # If the signature is attached to the data |
| 296 | 281 | gpg --verify [signature-file] |
| 297 | 282 | |
| 298 | 283 | # If the signature is detached as a separate file from the data |
| 299 | 284 | gpg --verify [signature-file] [original-file] |
| 300 | ``` | |
| 301 | ||
| 302 | ## Finding Public Keys | |
| 285 | #+end_src | |
| 303 | 286 | |
| 287 | *** Finding Public Keys | |
| 304 | 288 | In order to use GPG with others, a user needs to know the other user(s) |
| 305 | 289 | keys. This is easy to do if the user knows the other user(s) in person, |
| 306 | 290 | but may be hard if the relationship is strictly digital. Luckily, there |
| @@ -309,5 +293,5 @@ social pages if they have them. | ||
| 309 | 293 | |
| 310 | 294 | Otherwise, the best option is to use a keyserver, such as: |
| 311 | 295 | |
| 312 | - [pgp.mit.edu](https://pgp.mit.edu) | |
| 313 | - [keys.openpgp.org](https://keys.openpgp.org) | |
| 296 | - [[https://pgp.mit.edu][pgp.mit.edu]] | |
| 297 | - [[https://keys.openpgp.org][keys.openpgp.org]] | |
content/blog/2023-06-08-goaccess-geoip.md → blog/goaccess-geoip/index.org renamed +27 −32
| @@ -1,48 +1,44 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-06-08 | |
| 3 | title = "Inspecting Nginx Logs with GoAccess and MaxMind GeoIP Data" | |
| 4 | description = "Learn how to use GoAccess and MaxMind to evaluate visitors to your web server." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Overview | |
| 8 | ||
| 9 | [GoAccess](https://goaccess.io/) is an open source real-time web log | |
| 10 | analyzer and interactive viewer that runs in a terminal in \*nix systems | |
| 1 | #+title: Inspecting Nginx Logs with GoAccess and MaxMind GeoIP Data | |
| 2 | #+date: 2023-06-08 | |
| 3 | #+description: Learn how to use GoAccess and MaxMind to evaluate visitors to your web server. | |
| 4 | #+filetags: :sysadmin: | |
| 5 | ||
| 6 | * Overview | |
| 7 | [[https://goaccess.io/][GoAccess]] is an open source real-time web log | |
| 8 | analyzer and interactive viewer that runs in a terminal in *nix systems | |
| 11 | 9 | or through your browser. |
| 12 | 10 | |
| 13 | ## Installation | |
| 14 | ||
| 15 | To start, you'll need to install GoAccess for your OS. Here's an | |
| 16 | example for Debian-based distros: | |
| 11 | * Installation | |
| 12 | To start, you'll need to install GoAccess for your OS. Here's an example | |
| 13 | for Debian-based distros: | |
| 17 | 14 | |
| 18 | ```sh | |
| 15 | #+begin_src sh | |
| 19 | 16 | sudo apt install goaccess |
| 20 | ``` | |
| 17 | #+end_src | |
| 21 | 18 | |
| 22 | 19 | Next, find any number of the MaxMind GeoIP database files on GitHub or |
| 23 | 20 | another file hosting website. We're going to use P3TERX's version in |
| 24 | 21 | this example: |
| 25 | 22 | |
| 26 | ```sh | |
| 23 | #+begin_src sh | |
| 27 | 24 | wget https://github.com/P3TERX/GeoLite.mmdb/raw/download/GeoLite2-City.mmdb |
| 28 | ``` | |
| 25 | #+end_src | |
| 29 | 26 | |
| 30 | 27 | Be sure to save this file in an easy to remember location! |
| 31 | 28 | |
| 32 | ## Usage | |
| 33 | ||
| 29 | * Usage | |
| 34 | 30 | In order to utilize the full capabilities of GoAccess and MMDB, start |
| 35 | 31 | with the command template below and customize as necessary. This will |
| 36 | 32 | export an HTML view of the GoAccess dashboard, showing all relevant |
| 37 | 33 | information related to that site's access log. You can also omit the |
| 38 | `-o output.html` parameter if you prefer to view the data | |
| 39 | within the CLI instead of creating an HTML file. | |
| 34 | =-o output.html= parameter if you prefer to view the data within the CLI | |
| 35 | instead of creating an HTML file. | |
| 40 | 36 | |
| 41 | 37 | With the addition of the GeoIP Database parameter, section |
| 42 | `16 - Geo Location` will be added with the various countries | |
| 43 | that are associated with the collected IP addresses. | |
| 38 | =16 - Geo Location= will be added with the various countries that are | |
| 39 | associated with the collected IP addresses. | |
| 44 | 40 | |
| 45 | ```sh | |
| 41 | #+begin_src sh | |
| 46 | 42 | zcat /var/log/nginx/example.access.log.*.gz | goaccess \ |
| 47 | 43 | --geoip-database=/home/user/GeoLite2-City.mmdb \ |
| 48 | 44 | --date-format=%d/%b/%Y \ |
| @@ -50,20 +46,19 @@ zcat /var/log/nginx/example.access.log.*.gz | goaccess \ | ||
| 50 | 46 | --log-format=COMBINED \ |
| 51 | 47 | -o output.html \ |
| 52 | 48 | /var/log/nginx/example.access.log - |
| 53 | ``` | |
| 54 | ||
| 55 | ### Example Output | |
| 49 | #+end_src | |
| 56 | 50 | |
| 51 | ** Example Output | |
| 57 | 52 | See below for an example of the HTML output: |
| 58 | 53 | |
| 59 |  | |
| 54 | #+caption: GoAccess HTML | |
| 55 | [[https://img.cleberg.net/blog/20230608-goaccess/goaccess-dashboard.png]] | |
| 61 | 56 | |
| 62 | 57 | You can also see the GeoIP card created by the integration of the |
| 63 | 58 | MaxMind database information. |
| 64 | 59 | |
| 65 |  | |
| 60 | #+caption: GoAccess GeoIP | |
| 61 | [[https://img.cleberg.net/blog/20230608-goaccess/goaccess-geoip.png]] | |
| 67 | 62 | |
| 68 | 63 | That's all there is to it! Informational data is provided in an |
| 69 | 64 | organized fashion with minimal effort. |
blog/graphene-os/index.org added +154
| @@ -0,0 +1,154 @@ | ||
| 1 | #+title: Installing Graphene OS on the Pixel 6 Pro | |
| 2 | #+date: 2022-09-21 | |
| 3 | #+description: A retrospective on the successful command-line installation of Graphene OS on a Pixel 6 Pro. | |
| 4 | #+filetags: :privacy: | |
| 5 | ||
| 6 | * Introduction | |
| 7 | After using iOS for a couple of years, I finally took the plunge and | |
| 8 | purchased a Pixel 6 Pro in order to test and use [GrapheneOS] | |
| 9 | ([[https://grapheneos.org]]). | |
| 10 | ||
| 11 | The installation process was rather quick once you have the tools and | |
| 12 | files you need. Overall, it can be done in just a few minutes. | |
| 13 | ||
| 14 | * Gathering Tools & Files | |
| 15 | ** Android Tools | |
| 16 | First, in order to interact with the device, we will need the | |
| 17 | [[https://developer.android.com/studio/releases/platform-tools.html][Android | |
| 18 | platform tools]]. Find the Linux download and save the ZIP folder to | |
| 19 | your preferred location. | |
| 20 | ||
| 21 | Once we've downloaded the files, we will need to unzip them, enter the | |
| 22 | directory, and move the necessary executables to a central location, | |
| 23 | such as =/usr/bin/=. For this installation, we only need the =fastboot= | |
| 24 | and =adb= executables. | |
| 25 | ||
| 26 | #+begin_src sh | |
| 27 | cd ~/Downloads | |
| 28 | #+end_src | |
| 29 | ||
| 30 | #+begin_src sh | |
| 31 | unzip platform-tools_r33.0.3-linux.zip | |
| 32 | cd platform-tools | |
| 33 | sudo mv fastboot /usr/bin/ | |
| 34 | sudo mv adb /usr/bin | |
| 35 | #+end_src | |
| 36 | ||
| 37 | ** GrapheneOS Files | |
| 38 | Next, we need the [[https://grapheneos.org/releases][GrapheneOS files]] | |
| 39 | for our device and model. For example, the Pixel 6 Pro is codenamed | |
| 40 | =raven= on the release page. | |
| 41 | ||
| 42 | Once we have the links, let's download them to our working directory: | |
| 43 | ||
| 44 | #+begin_src sh | |
| 45 | curl -O https://releases.grapheneos.org/factory.pub | |
| 46 | curl -0 https://releases.grapheneos.org/raven-factory-2022091400.zip | |
| 47 | curl -0 https://releases.grapheneos.org/raven-factory-2022091400.zip.sig | |
| 48 | #+end_src | |
| 49 | ||
| 50 | 1. Validate Integrity | |
| 51 | ||
| 52 | In order to validate the integrity of the downloaded files, we will | |
| 53 | need the =signify= package and Graphene's =factory.pub= file. | |
| 54 | ||
| 55 | #+begin_src sh | |
| 56 | sudo dnf install signify | |
| 57 | #+end_src | |
| 58 | ||
| 59 | #+begin_src sh | |
| 60 | curl -O https://releases.grapheneos.org/factory.pub | |
| 61 | #+end_src | |
| 62 | ||
| 63 | Then we can validate the files and ensure that no data was corrupted | |
| 64 | or modified before it was saved to our device. | |
| 65 | ||
| 66 | #+begin_src sh | |
| 67 | signify -Cqp factory.pub -x raven-factory-2022091400.zip.sig && echo verified | |
| 68 | #+end_src | |
| 69 | ||
| 70 | 2. Unzip Files | |
| 71 | ||
| 72 | Once the files are verified, we can unzip the Graphene image and | |
| 73 | enter the directory: | |
| 74 | ||
| 75 | #+begin_src sh | |
| 76 | unzip raven-factory-2022091400.zip && cd raven-factory-2022091400 | |
| 77 | #+end_src | |
| 78 | ||
| 79 | * Installation Process | |
| 80 | ** Enable Developer Debugging & OEM Unlock | |
| 81 | Before we can actually flash anything to the phone, we will need to | |
| 82 | enable OEM Unlocking, as well as either USB Debugging or Wireless | |
| 83 | Debugging, depending on which method we will be using. | |
| 84 | ||
| 85 | To start, enable developer mode by going to =Settings= > =About= and | |
| 86 | tapping =Build Number= seven (7) times. You may need to enter your PIN | |
| 87 | to enable this mode. | |
| 88 | ||
| 89 | Once developer mode is enabled, go to =Settings= > =System= > | |
| 90 | =Devloper Options= and enable OEM Unlocking, as well as USB or Wireless | |
| 91 | Debugging. In my case, I chose USB Debugging and performed all actions | |
| 92 | via USB cable. | |
| 93 | ||
| 94 | Once these options are enabled, plug the phone into the computer and | |
| 95 | execute the following command: | |
| 96 | ||
| 97 | #+begin_src sh | |
| 98 | adb devices | |
| 99 | #+end_src | |
| 100 | ||
| 101 | If an unauthorized error occurs, make sure the USB mode on the phone is | |
| 102 | changed from charging to something like "File Transfer" or "PTP." You | |
| 103 | can find the USB mode in the notification tray. | |
| 104 | ||
| 105 | ** Reboot Device | |
| 106 | Once we have found the device via =adb=, we can either boot into the | |
| 107 | bootloader interface by holding the volume down button while the phone | |
| 108 | reboots or by executing the following command: | |
| 109 | ||
| 110 | #+begin_src sh | |
| 111 | adb reboot bootloader | |
| 112 | #+end_src | |
| 113 | ||
| 114 | ** Unlock the Bootloader | |
| 115 | The phone will reboot and load the bootloader screen upon startup. At | |
| 116 | this point, we are ready to start the actual flashing of GrapheneOS onto | |
| 117 | the device. | |
| 118 | ||
| 119 | *NOTE*: In my situation, I needed to use =sudo= with every =fastboot= | |
| 120 | command, but not with =adb= commands. I am not sure if this is standard | |
| 121 | or a Fedora quirk, but I'm documenting my commands verbatim in this | |
| 122 | post. | |
| 123 | ||
| 124 | First, we start by unlocking the bootloader so that we can load other | |
| 125 | ROMs: | |
| 126 | ||
| 127 | #+begin_src sh | |
| 128 | sudo fastboot flashing unlock | |
| 129 | #+end_src | |
| 130 | ||
| 131 | ** Flashing Factory Images | |
| 132 | Once the phone is unlocked, we can flash it with the =flash-all.sh= | |
| 133 | script found inside the =raven-factory-2022091400= folder we entered | |
| 134 | earlier: | |
| 135 | ||
| 136 | #+begin_src sh | |
| 137 | sudo ./flash-all.sh | |
| 138 | #+end_src | |
| 139 | ||
| 140 | This process should take a few minutes and will print informational | |
| 141 | messages as things progress. Avoid doing anything on the phone while | |
| 142 | this process is operating. | |
| 143 | ||
| 144 | ** Lock the Bootloader | |
| 145 | If everything was successful, the phone should reboot a few times and | |
| 146 | finally land back on the bootloader screen. At this point, we can | |
| 147 | re-lock the bootloader to enable full verified boot and protect the | |
| 148 | device from unwanted flashing or erasure of data. | |
| 149 | ||
| 150 | #+begin_src sh | |
| 151 | sudo fastboot flashing lock | |
| 152 | #+end_src | |
| 153 | ||
| 154 | Once done, the device will be wiped and ready for a fresh set-up! | |
content/blog/2020-09-25-happiness-map.md → blog/happiness-map/index.org renamed +60 −68
| @@ -1,52 +1,48 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-09-25 | |
| 3 | title = "Data Visualization: World Choropleth Map of Happiness" | |
| 4 | description = "Exploring and visualizing data with Python." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Background Information | |
| 1 | #+title: Data Visualization: World Choropleth Map of Happiness | |
| 2 | #+date: 2020-09-25 | |
| 3 | #+description: Exploring and visualizing data with Python. | |
| 4 | #+filetags: :data: | |
| 8 | 5 | |
| 6 | * Background Information | |
| 9 | 7 | The dataset (obtained from |
| 10 | [Kaggle](https://www.kaggle.com/unsdsn/world-happiness)) used in this | |
| 8 | [[https://www.kaggle.com/unsdsn/world-happiness][Kaggle]]) used in this | |
| 11 | 9 | article contains a list of countries around the world, their happiness |
| 12 | 10 | rankings and scores, as well as other national scoring measures. |
| 13 | 11 | |
| 14 | 12 | Fields include: |
| 15 | 13 | |
| 16 | - Overall rank | |
| 17 | - Country or region | |
| 18 | - GDP per capita | |
| 19 | - Social support | |
| 20 | - Healthy life expectancy | |
| 21 | - Freedom to make life choices | |
| 22 | - Generosity | |
| 23 | - Perceptions of corruption | |
| 14 | - Overall rank | |
| 15 | - Country or region | |
| 16 | - GDP per capita | |
| 17 | - Social support | |
| 18 | - Healthy life expectancy | |
| 19 | - Freedom to make life choices | |
| 20 | - Generosity | |
| 21 | - Perceptions of corruption | |
| 24 | 22 | |
| 25 | There are 156 records. Since there are \~195 countries in the world, we | |
| 23 | There are 156 records. Since there are ~195 countries in the world, we | |
| 26 | 24 | can see that around 40 countries will be missing from this dataset. |
| 27 | 25 | |
| 28 | # Install Packages | |
| 29 | ||
| 30 | As always, run the `install` command for all packages needed | |
| 31 | to perform analysis. | |
| 26 | * Install Packages | |
| 27 | As always, run the =install= command for all packages needed to perform | |
| 28 | analysis. | |
| 32 | 29 | |
| 33 | ```python | |
| 30 | #+begin_src python | |
| 34 | 31 | !pip install folium geopandas matplotlib numpy pandas |
| 35 | ``` | |
| 36 | ||
| 37 | # Import the Data | |
| 32 | #+end_src | |
| 38 | 33 | |
| 34 | * Import the Data | |
| 39 | 35 | We only need a couple packages to create a choropleth map. We will use |
| 40 | [Folium](https://python-visualization.github.io/folium/), which provides | |
| 41 | map visualizations in Python. We will also use geopandas and pandas to | |
| 42 | wrangle our data before we put it on a map. | |
| 36 | [[https://python-visualization.github.io/folium/][Folium]], which | |
| 37 | provides map visualizations in Python. We will also use geopandas and | |
| 38 | pandas to wrangle our data before we put it on a map. | |
| 43 | 39 | |
| 44 | ```python | |
| 40 | #+begin_src python | |
| 45 | 41 | # Import the necessary Python packages |
| 46 | 42 | import folium |
| 47 | 43 | import geopandas as gpd |
| 48 | 44 | import pandas as pd |
| 49 | ``` | |
| 45 | #+end_src | |
| 50 | 46 | |
| 51 | 47 | To get anything to show up on a map, we need a file that will specify |
| 52 | 48 | the boundaries of each country. Luckily, GeoJSON files exist (for free!) |
| @@ -57,38 +53,37 @@ GeoPandas will take this data and load it into a dataframe so that we | ||
| 57 | 53 | can easily match it to the data we're trying to analyze. Let's look at |
| 58 | 54 | the GeoJSON dataframe: |
| 59 | 55 | |
| 60 | ```python | |
| 56 | #+begin_src python | |
| 61 | 57 | # Load the GeoJSON data with geopandas |
| 62 | 58 | geo_data = gpd.read_file('https://raw.githubusercontent.com/datasets/geo-countries/master/data/countries.geojson') |
| 63 | 59 | geo_data.head() |
| 64 | ``` | |
| 60 | #+end_src | |
| 65 | 61 | |
| 66 |  | |
| 62 | #+caption: GeoJSON Dataframe | |
| 63 | [[https://img.cleberg.net/blog/20200925-world-choropleth-map/geojson_df.png]] | |
| 68 | 64 | |
| 69 | Next, let's load the data from the Kaggle dataset. I've downloaded | |
| 70 | this file, so update the file path if you have it somewhere else. After | |
| 65 | Next, let's load the data from the Kaggle dataset. I've downloaded this | |
| 66 | file, so update the file path if you have it somewhere else. After | |
| 71 | 67 | loading, let's take a look at this dataframe: |
| 72 | 68 | |
| 73 | ```python | |
| 69 | #+begin_src python | |
| 74 | 70 | # Load the world happiness data with pandas |
| 75 | 71 | happy_data = pd.read_csv(r'~/Downloads/world_happiness_data_2019.csv') |
| 76 | 72 | happy_data.head() |
| 77 | ``` | |
| 78 | ||
| 79 |  | |
| 73 | #+end_src | |
| 81 | 74 | |
| 82 | # Clean the Data | |
| 75 | #+caption: Happiness Dataframe | |
| 76 | [[https://img.cleberg.net/blog/20200925-world-choropleth-map/happiness_df.png]] | |
| 83 | 77 | |
| 78 | * Clean the Data | |
| 84 | 79 | Some countries need to be renamed, or they will be lost when you merge |
| 85 | 80 | the happiness and GeoJSON dataframes. This is something I discovered |
| 86 | 81 | when the map below showed empty countries. I searched both data frames |
| 87 | 82 | for the missing countries to see the naming differences. Any countries |
| 88 | that do not have records in the `happy_data` df will not show | |
| 89 | up on the map. | |
| 83 | that do not have records in the =happy_data= df will not show up on the | |
| 84 | map. | |
| 90 | 85 | |
| 91 | ```python | |
| 86 | #+begin_src python | |
| 92 | 87 | # Rename some countries to match our GeoJSON data |
| 93 | 88 | |
| 94 | 89 | # Rename USA |
| @@ -106,38 +101,36 @@ happy_data.at[republic_congo_index, 'Country or region'] = 'Republic of Congo' | ||
| 106 | 101 | # Rename the DRC |
| 107 | 102 | democratic_congo_index = happy_data.index[happy_data['Country or region'] == 'Congo (Kinshasa)'] |
| 108 | 103 | happy_data.at[democratic_congo_index, 'Country or region'] = 'Democratic Republic of the Congo' |
| 109 | ``` | |
| 110 | ||
| 111 | # Merge the Data | |
| 104 | #+end_src | |
| 112 | 105 | |
| 106 | * Merge the Data | |
| 113 | 107 | Now that we have clean data, we need to merge the GeoJSON data with the |
| 114 | happiness data. Since we've stored them both in dataframes, we just | |
| 115 | need to call the `.merge()` function. | |
| 108 | happiness data. Since we've stored them both in dataframes, we just need | |
| 109 | to call the =.merge()= function. | |
| 116 | 110 | |
| 117 | 111 | We will also rename a couple columns, just so that they're a little |
| 118 | 112 | easier to use when we create the map. |
| 119 | 113 | |
| 120 | ```python | |
| 114 | #+begin_src python | |
| 121 | 115 | # Merge the two previous dataframes into a single geopandas dataframe |
| 122 | 116 | merged_df = geo_data.merge(happy_data,left_on='ADMIN', right_on='Country or region') |
| 123 | 117 | |
| 124 | 118 | # Rename columns for ease of use |
| 125 | 119 | merged_df = merged_df.rename(columns = {'ADMIN':'GeoJSON_Country'}) |
| 126 | 120 | merged_df = merged_df.rename(columns = {'Country or region':'Country'}) |
| 127 | ``` | |
| 128 | ||
| 129 |  | |
| 121 | #+end_src | |
| 131 | 122 | |
| 132 | # Create the Map | |
| 123 | #+caption: Merged Dataframe | |
| 124 | [[https://img.cleberg.net/blog/20200925-world-choropleth-map/merged_df.png]] | |
| 133 | 125 | |
| 126 | * Create the Map | |
| 134 | 127 | The data is finally ready to be added to a map. The code below shows the |
| 135 | 128 | simplest way to find the center of the map and create a Folium map |
| 136 | 129 | object. The important part is to remember to reference the merged |
| 137 | 130 | dataframe for our GeoJSON data and value data. The columns specify which |
| 138 | 131 | geo data and value data to use. |
| 139 | 132 | |
| 140 | ```python | |
| 133 | #+begin_src python | |
| 141 | 134 | # Assign centroids to map |
| 142 | 135 | x_map = merged_df.centroid.x.mean() |
| 143 | 136 | y_map = merged_df.centroid.y.mean() |
| @@ -161,21 +154,20 @@ folium.Choropleth( | ||
| 161 | 154 | smooth_factor=0, |
| 162 | 155 | highlight=True |
| 163 | 156 | ).add_to(world_map) |
| 164 | ``` | |
| 157 | #+end_src | |
| 165 | 158 | |
| 166 | 159 | Let's look at the resulting map. |
| 167 | 160 | |
| 168 |  | |
| 170 | ||
| 171 | # Create a Tooltip on Hover | |
| 161 | #+caption: Choropleth Map | |
| 162 | [[https://img.cleberg.net/blog/20200925-world-choropleth-map/map.png]] | |
| 172 | 163 | |
| 164 | * Create a Tooltip on Hover | |
| 173 | 165 | Now that we have a map set up, we could stop. However, I want to add a |
| 174 | 166 | tooltip so that I can see more information about each country. The |
| 175 | `tooltip_data` code below will show a popup on hover with all | |
| 176 | the data fields shown. | |
| 167 | =tooltip_data= code below will show a popup on hover with all the data | |
| 168 | fields shown. | |
| 177 | 169 | |
| 178 | ```python | |
| 170 | #+begin_src python | |
| 179 | 171 | # Adding labels to map |
| 180 | 172 | style_function = lambda x: {'fillColor': '#ffffff', |
| 181 | 173 | 'color':'#000000', |
| @@ -216,10 +208,10 @@ folium.LayerControl().add_to(world_map) | ||
| 216 | 208 | |
| 217 | 209 | # Display the map |
| 218 | 210 | world_map |
| 219 | ``` | |
| 211 | #+end_src | |
| 220 | 212 | |
| 221 | 213 | The final image below will show you what the tooltip looks like whenever |
| 222 | 214 | you hover over a country. |
| 223 | 215 | |
| 224 |  | |
| 216 | #+caption: Choropleth Map Tooltip | |
| 217 | [[https://img.cleberg.net/blog/20200925-world-choropleth-map/tooltip_map.png]] | |
content/blog/2020-05-03-homelab.md → blog/homelab/index.org renamed +55 −71
| @@ -1,60 +1,55 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-05-03 | |
| 3 | title = "An Inside Look at My Homelab" | |
| 4 | description = "A retrospective on the first iteration of my home lab." | |
| 5 | +++ | |
| 6 | ||
| 7 | # What is a Homelab? | |
| 1 | #+title: An Inside Look at My Homelab | |
| 2 | #+date: 2020-05-03 | |
| 3 | #+description: A retrospective on the first iteration of my home lab. | |
| 4 | #+filetags: :sysadmin: | |
| 8 | 5 | |
| 6 | * What is a Homelab? | |
| 9 | 7 | Starting as a developer, I have largely stayed away from hardware-based |
| 10 | 8 | hobbies (other than building a gaming desktop). However, as the |
| 11 | 9 | quarantine for COVID-19 stretches out further and further, I found |
| 12 | 10 | myself bored and in search of new hobbies. After spending the last few |
| 13 | months browsing the [r/homelab](https://www.reddit.com/r/homelab/) | |
| 11 | months browsing the [[https://www.reddit.com/r/homelab/][r/homelab]] | |
| 14 | 12 | subreddit, I decided it was time to jump in and try things out for |
| 15 | 13 | myself. |
| 16 | 14 | |
| 17 | 15 | Since I am a beginner and just recently graduated from college, |
| 18 | 16 | everything I've done so far in my homelab is fairly low-budget. |
| 19 | 17 | |
| 20 | # Hardware | |
| 21 | ||
| 22 |  | |
| 18 | * Hardware | |
| 19 | #+caption: HomeLab Diagram | |
| 20 | [[https://img.cleberg.net/blog/20200503-homelab/homelab-min.png]] | |
| 24 | 21 | |
| 25 | ## Raspberry Pi 4 | |
| 26 | ||
| 27 | Luckily, I had actually purchased a [Raspberry Pi | |
| 28 | 4](https://www.raspberrypi.org/products/raspberry-pi-4-model-b/) before | |
| 29 | the quarantine started so that I could try to keep Plex Media Center | |
| 30 | running, even while my desktop computer was turned off. I started here, | |
| 31 | using the Pi to hold Plex and Pi-hole until I grew tired with the slow | |
| 32 | performance. | |
| 22 | *** Raspberry Pi 4 | |
| 23 | Luckily, I had actually purchased a | |
| 24 | [[https://www.raspberrypi.org/products/raspberry-pi-4-model-b/][Raspberry | |
| 25 | Pi 4]] before the quarantine started so that I could try to keep Plex | |
| 26 | Media Center running, even while my desktop computer was turned off. I | |
| 27 | started here, using the Pi to hold Plex and Pi-hole until I grew tired | |
| 28 | with the slow performance. | |
| 33 | 29 | |
| 34 | 30 | Here are the specifications for the Pi 4: |
| 35 | 31 | |
| 36 | - Broadcom BCM2711, Quad core Cortex-A72 (ARM v8) 64-bit SoC @ 1.5GHz | |
| 37 | - 4GB LPDDR4-3200 SDRAM | |
| 38 | - Gigabit Ethernet | |
| 39 | - H.265 (4kp60 decode), H264 (1080p60 decode, 1080p30 encode) | |
| 40 | - 64 GB MicroSD Card | |
| 41 | ||
| 42 | ## Dell Optiplex 5040 | |
| 32 | - Broadcom BCM2711, Quad core Cortex-A72 (ARM v8) 64-bit SoC @ 1.5GHz | |
| 33 | - 4GB LPDDR4-3200 SDRAM | |
| 34 | - Gigabit Ethernet | |
| 35 | - H.265 (4kp60 decode), H264 (1080p60 decode, 1080p30 encode) | |
| 36 | - 64 GB MicroSD Card | |
| 43 | 37 | |
| 38 | ** Dell Optiplex 5040 | |
| 44 | 39 | Since I wasn't happy with the Pi as my main server, I turned to |
| 45 | Craigslist. I know a lot of other homelabbers use Ebay, but I can't | |
| 46 | seem to ever trust it enough to purchase items on there. So I used | |
| 47 | Craigslist and found a Dell Optiplex 5040 desktop computer on sale for | |
| 48 | \$90. While this computer might be underpowered, it was one of the few | |
| 49 | computers under \$100 that was available during quarantine. | |
| 40 | Craigslist. I know a lot of other homelabbers use Ebay, but I can't seem | |
| 41 | to ever trust it enough to purchase items on there. So I used Craigslist | |
| 42 | and found a Dell Optiplex 5040 desktop computer on sale for $90. While | |
| 43 | this computer might be underpowered, it was one of the few computers | |
| 44 | under $100 that was available during quarantine. | |
| 50 | 45 | |
| 51 | 46 | Here are the specifications for the Dell Optiplex 5040: |
| 52 | 47 | |
| 53 | - Intel Core i3 6100 | |
| 54 | - 8GB RAM DDR3 | |
| 55 | - Intel HD Graphics | |
| 56 | - Gigabit Ethernet | |
| 57 | - 500GB Hard Drive | |
| 48 | - Intel Core i3 6100 | |
| 49 | - 8GB RAM DDR3 | |
| 50 | - Intel HD Graphics | |
| 51 | - Gigabit Ethernet | |
| 52 | - 500GB Hard Drive | |
| 58 | 53 | |
| 59 | 54 | While this hardware would be awful for a work computer or a gaming rig, |
| 60 | 55 | it turned out to be wonderful for my server purposes. The only |
| @@ -63,36 +58,34 @@ power for a single 4k video transcode at a time. I haven't tested more | ||
| 63 | 58 | than three 1080p streams at a time, but the maximum amount of streams |
| 64 | 59 | I've ever actually used is two. |
| 65 | 60 | |
| 66 | ## WD easystore 10TB & 8TB | |
| 67 | ||
| 61 | ** WD easystore 10TB & 8TB | |
| 68 | 62 | Application storage and temporary files are stored on the internal hard |
| 69 | 63 | drive of the server, but all media files (movies, tv, games, books, etc) |
| 70 | 64 | are stored externally on my WD easystore hard drive. Creating auto-boot |
| 71 | configurations in the `/etc/fstab` file on my server allows | |
| 72 | the hard drives to automatically mount whenever I need to restart my | |
| 73 | server. | |
| 65 | configurations in the =/etc/fstab= file on my server allows the hard | |
| 66 | drives to automatically mount whenever I need to restart my server. | |
| 74 | 67 | |
| 75 | > Update: In March 2022, I shucked the hard drives out of their external | |
| 76 | > cases, put some Kapton tape on the third power pin to prevent power | |
| 77 | > shutdowns, and stuck them inside my server tower using internal SATA | |
| 78 | > cables. | |
| 68 | #+begin_quote | |
| 69 | Update: In March 2022, I shucked the hard drives out of their external | |
| 70 | cases, put some Kapton tape on the third power pin to prevent power | |
| 71 | shutdowns, and stuck them inside my server tower using internal SATA | |
| 72 | cables. | |
| 79 | 73 | |
| 80 | ## Netgear Unmanaged Switch | |
| 74 | #+end_quote | |
| 81 | 75 | |
| 76 | ** Netgear Unmanaged Switch | |
| 82 | 77 | To manage all the ethernet cords used by my homelab, my desktop, and my |
| 83 | 78 | living room media center, I purchased an 8-port gigabit ethernet switch |
| 84 | for \$50 at my local computer store. This is probably much more than I | |
| 79 | for $50 at my local computer store. This is probably much more than I | |
| 85 | 80 | should have spent on an unmanaged switch, but I am comfortable with the |
| 86 | 81 | choice. |
| 87 | 82 | |
| 88 | ## TP-Link Managed Switch | |
| 89 | ||
| 83 | ** TP-Link Managed Switch | |
| 90 | 84 | Since I use the unmanaged switch to group all living room devices |
| 91 | 85 | together, I use the managed switch to configure VLANs and secure my |
| 92 | 86 | network. |
| 93 | 87 | |
| 94 | ## Arris TM1602A Modem & Sagecom Fast 5280 Router | |
| 95 | ||
| 88 | ** Arris TM1602A Modem & Sagecom Fast 5280 Router | |
| 96 | 89 | My default modem and router, provided by my ISP, are fairly standard. |
| 97 | 90 | The Arris modem supports DOCSIS 3.0, which is something that I |
| 98 | 91 | definitely wanted as a minimum. The Sagecom router is also standard, no |
| @@ -100,23 +93,19 @@ fancy bells or whistles. However, it does support DHCP and DHCPv6, which | ||
| 100 | 93 | is something you can use to route all household traffic through a |
| 101 | 94 | pi-hole or firewall. |
| 102 | 95 | |
| 103 | ## TP-Link EAP | |
| 104 | ||
| 96 | ** TP-Link EAP | |
| 105 | 97 | In order to gain better control over the network, I use my own wireless |
| 106 | 98 | access point instead of the one included in the Sagecom router above. |
| 107 | 99 | Now I can control and organize all of my ethernet connections through |
| 108 | 100 | the VLANs on the managed switch and wireless connections through the |
| 109 | 101 | VLANS on the EAP. |
| 110 | 102 | |
| 111 | ## Generic Printer | |
| 112 | ||
| 103 | ** Generic Printer | |
| 113 | 104 | The last piece to my homelab is a standard wireless printer. Nothing |
| 114 | 105 | special here. |
| 115 | 106 | |
| 116 | # Software | |
| 117 | ||
| 118 | ## Ubuntu Server 20.04 | |
| 119 | ||
| 107 | * Software | |
| 108 | ** Ubuntu Server 20.04 | |
| 120 | 109 | While the 20.04 version of Ubuntu was just released, I always like to |
| 121 | 110 | experiment with new features (and I don't mind breaking my system - it |
| 122 | 111 | just gives me more experience learning how to fix things). So, I have |
| @@ -124,31 +113,27 @@ Ubuntu Server 20.04 installed on the Dell Optiplex server and Ubuntu | ||
| 124 | 113 | Server 19.10 installed on the Raspberry Pi. Once I find an acceptable |
| 125 | 114 | use for the Pi, I will most likely switch the operating system. |
| 126 | 115 | |
| 127 | ## Docker | |
| 128 | ||
| 129 | I am *very* new to Docker, but I have had a lot of fun playing with it | |
| 116 | ** Docker | |
| 117 | I am /very/ new to Docker, but I have had a lot of fun playing with it | |
| 130 | 118 | so far. Docker is used to create containers that can hold all the |
| 131 | 119 | contents of a system without interfering with other software on the same |
| 132 | 120 | system. So far, I have successfully installed pi-hole, GitLab, Gogs, and |
| 133 | 121 | Nextcloud in containers. However, I opted to delete all of those so that |
| 134 | 122 | I can reconfigure them more professionally at a later time. |
| 135 | 123 | |
| 136 | ## Plex Media Server | |
| 137 | ||
| 124 | ** Plex Media Server | |
| 138 | 125 | Plex is a media center software that allows you to organize your movies, |
| 139 | 126 | TV shows, music, photos, and videos automatically. It will even download |
| 140 | 127 | metadata for you so that you can easily browse these collections. |
| 141 | 128 | |
| 142 | ## Pi-hole | |
| 143 | ||
| 129 | ** Pi-hole | |
| 144 | 130 | Pi-hole is an alternative ad-blocker that runs at the DNS level, |
| 145 | 131 | allowing you to block traffic when it hits your network, so that you can |
| 146 | 132 | reject any traffic you deem to be bad. Pi-hole uses blacklists and |
| 147 | 133 | whitelists to decide which traffic block and, luckily, there are a lot |
| 148 | 134 | of pre-made lists out there on Reddit, GitHub, etc. |
| 149 | 135 | |
| 150 | ## Nextcloud | |
| 151 | ||
| 136 | ** Nextcloud | |
| 152 | 137 | While I had trouble with the Docker version of Nextcloud, I was very |
| 153 | 138 | successful when setting up the snap version. Using this, I was able to |
| 154 | 139 | map Nextcloud to a subdomain of a domain I own in Namecheap. |
| @@ -156,8 +141,7 @@ Additionally, Nextcloud has an integration with Let's Encrypt that | ||
| 156 | 141 | allows me to issue certificates automatically to any new domain I |
| 157 | 142 | authorize. |
| 158 | 143 | |
| 159 | ## Webmin | |
| 160 | ||
| 144 | ** Webmin | |
| 161 | 145 | To monitor my servers, and the processes running on them, I use the |
| 162 | 146 | Webmin dashboard. This was fairly painless to set up, and I currently |
| 163 | 147 | access it straight through the server's IP address. In the future, I |
blog/index.org added +141
| @@ -0,0 +1,141 @@ | ||
| 1 | #+title: Blog | |
| 2 | #+options: toc:nil | |
| 3 | ||
| 4 | Use =Ctrl + F= to search blog post titles for keywords. | |
| 5 | ||
| 6 | * TODO Create RSS Feed | |
| 7 | ||
| 8 | * 2024 | |
| 9 | ||
| 10 | - 2024-02-26 [[./org-blog/][Blogging in Org-Mode]] | |
| 11 | - 2024-02-21 [[./self-hosting-otter-wiki/][Self-Hosting An Otter Wiki]] | |
| 12 | - 2024-02-13 [[./ubuntu-emergency-mode/][Stuck in Ubuntu's Emergency Mode? Try Fixing the Fstab File]] | |
| 13 | - 2024-02-06 [[./zfs/][How to Create a ZFS Pool on Ubuntu Linux]] | |
| 14 | - 2024-01-27 [[./tableau-dashboard/][Data Visualization: Mapping Omaha Crime Data with Tableau]] | |
| 15 | - 2024-01-26 [[./audit-dashboard/][Building an Audit Status Dashboard]] | |
| 16 | - 2024-01-13 [[./local-llm/][Running Local LLMs on macOS and iOS]] | |
| 17 | - 2024-01-09 [[./macos-customization/][Customizing macOS]] | |
| 18 | - 2024-01-08 [[./dont-say-hello/][Don't Say Hello]] | |
| 19 | ||
| 20 | * 2023 | |
| 21 | ||
| 22 | - 2023-12-03 [[./unifi-nextdns/][How to Install NextDNS on the Unifi Dream Machine]] | |
| 23 | - 2023-11-08 [[./scli/][Installing scli on Alpine Linux (musl)]] | |
| 24 | - 2023-10-17 [[./self-hosting-anonymousoverflow/][Self-Hosting AnonymousOverflow]] | |
| 25 | - 2023-10-15 [[./alpine-ssh-hardening/][SSH Hardening for Alpine Linux]] | |
| 26 | - 2023-10-11 [[./self-hosting-authelia/][Self-Hosting Authelia]] | |
| 27 | - 2023-10-04 [[./digital-minimalism/][Digital Minimalism]] | |
| 28 | - 2023-09-19 [[./audit-sql-scripts/][Useful SQL Scripts for Auditing Logical Access]] | |
| 29 | - 2023-09-15 [[./self-hosting-gitweb/][Self-Hosting GitWeb via Nginx]] | |
| 30 | - 2023-08-18 [[./agile-auditing/][Agile Auditing: An Introduction]] | |
| 31 | - 2023-07-19 [[./plex-transcoder-errors/][How to Avoid Plex Error: 'Conversion failed. The transcoder failed to start up.']] | |
| 32 | - 2023-07-12 [[./wireguard-lan/][Enable LAN Access in Mullvad Wireguard Conf Files]] | |
| 33 | - 2023-06-30 [[./self-hosting-voyager/][Self-Hosting Voyager - A Lemmy Web Client]] | |
| 34 | - 2023-06-28 [[./backblaze-b2/][Getting Started with Backblaze B2 Cloud Storage]] | |
| 35 | - 2023-06-23 [[./self-hosting-convos/][Self-Hosting Convos IRC Web Client]] | |
| 36 | - 2023-06-23 [[./byobu/][Byobu]] | |
| 37 | - 2023-06-20 [[./audit-review-template/][Audit Testing Review Template]] | |
| 38 | - 2023-06-18 [[./unifi-ip-blocklist/][Block IP Addresses and Subnets with Unifi Network Firewall]] | |
| 39 | - 2023-06-08 [[./goaccess-geoip/][Inspecting Nginx Logs with GoAccess and MaxMind GeoIP Data]] | |
| 40 | - 2023-06-08 [[./self-hosting-baikal/][Self-Hosting Baikal Server (CalDAV & CardDAV)]] | |
| 41 | - 2023-05-22 [[./burnout/][RE: Burnout]] | |
| 42 | - 2023-02-02 [[./exploring-hare/][Exploring the Hare Programming Language]] | |
| 43 | - 2023-01-28 [[./self-hosting-wger/][Self-Hosting Wger Workout Manager]] | |
| 44 | - 2023-01-23 [[./random-wireguard/][Connecting to a Random Mullvad Wireguard Host on Boot]] | |
| 45 | - 2023-01-21 [[./flatpak-symlinks/][Running Flatpak Apps with Symlinks]] | |
| 46 | - 2023-01-08 [[./fedora-login-manager/][How to Remove the Login Manager from Fedora i3]] | |
| 47 | - 2023-01-05 [[./mass-unlike-tumblr-posts/][How to Easily Mass Unlike Tumblr Posts with Javascript]] | |
| 48 | - 2023-01-03 [[./recent-website-changes/][Recent Website Changes]] | |
| 49 | ||
| 50 | * 2022 | |
| 51 | ||
| 52 | - 2022-12-23 [[./alpine-desktop/][Alpine Linux as a Desktop OS]] | |
| 53 | - 2022-12-17 [[./st/][Simple Terminal]] | |
| 54 | - 2022-12-07 [[./nginx-wildcard-redirect/][Redirect Nginx Subdomains & Trailing Content with Regex]] | |
| 55 | - 2022-12-01 [[./nginx-compression/][Enable GZIP Compression in Nginx]] | |
| 56 | - 2022-11-29 [[./nginx-referrer-ban-list/][Creating a Referrer Ban List in Nginx]] | |
| 57 | - 2022-11-27 [[./server-build/][Building a Custom Rack-Mounted Server]] | |
| 58 | - 2022-11-11 [[./nginx-tmp-errors/][Fixing Permission Errors in /var/lib/nginx]] | |
| 59 | - 2022-10-30 [[./linux-display-manager/][How to Disable or Change the Display Manager on Void Linux]] | |
| 60 | - 2022-10-22 [[./alpine-linux/][Alpine Linux: My New Server OS]] | |
| 61 | - 2022-10-04 [[./syncthing/][Syncthing: A Minimal Self-Hosted Cloud Storage Solution]] | |
| 62 | - 2022-10-04 [[./mtp-linux/][How to Mount an MTP Mobile Device on Fedora Linux]] | |
| 63 | - 2022-09-21 [[./graphene-os/][Installing Graphene OS on the Pixel 6 Pro]] | |
| 64 | - 2022-09-17 [[./serenity-os/][Serenity OS: Testing Out a Unique System]] | |
| 65 | - 2022-08-31 [[./privacy-com-changes/][Concerning Changes on Privacy.com]] | |
| 66 | - 2022-03-23 [[./cloudflare-dns-api/][Dynamic DNS with Cloudflare API]] | |
| 67 | - 2022-07-31 [[./bash-it/][Upgrade Bash with Bash-It & Ble.sh]] | |
| 68 | - 2022-07-30 [[./flac-to-opus/][Recursive Command-Line FLAC to Opus Conversion]] | |
| 69 | - 2022-07-25 [[./curseradio/][CurseRadio: Listening to the Radio on the Command Line]] | |
| 70 | - 2022-07-14 [[./gnupg/][GNU Privacy Guard (GPG)]] | |
| 71 | - 2022-07-01 [[./git-server/][Self-Hosting a Personal Git Server]] | |
| 72 | - 2022-06-24 [[./fedora-i3/][Rebooting My Love Affair with Linux]] | |
| 73 | - 2022-06-22 [[./daily-poetry/][Daily Plaintext Poetry via Email]] | |
| 74 | - 2022-06-16 [[./terminal-lifestyle/][A Terminal Lifestyle]] | |
| 75 | - 2022-06-07 [[./self-hosting-freshrss/][Self-Hosting FreshRSS]] | |
| 76 | - 2022-06-01 [[./ditching-cloudflare/][Ditching Cloudflare for Njalla]] | |
| 77 | - 2022-04-09 [[./pinetime/][PineTime: An Open-Source Smart Watch]] | |
| 78 | - 2022-04-02 [[./nginx-reverse-proxy/][Set-Up a Reverse Proxy with Nginx]] | |
| 79 | - 2022-03-26 [[./ssh-mfa/][Enable TOTP MFA for SSH]] | |
| 80 | - 2022-03-24 [[./server-hardening/][Hardening a Public-Facing Home Server]] | |
| 81 | - 2022-03-23 [[./nextcloud-on-ubuntu/][Nextcloud on Ubuntu]] | |
| 82 | - 2022-03-08 [[./plex-migration/][Migrating Plex to a New Server (& Nvidia Transcoding)]] | |
| 83 | - 2022-03-03 [[./financial-database/][Maintaining a Personal Financial Database]] | |
| 84 | - 2022-03-02 [[./reliable-notes/][Easy, Reliable Note-Taking]] | |
| 85 | - 2022-02-22 [[./tuesday/][Tuesday]] | |
| 86 | - 2022-02-20 [[./nginx-caching/][Caching Static Content with Nginx]] | |
| 87 | - 2022-02-17 [[./exiftool/][Stripping Image Metadata with exiftool]] | |
| 88 | - 2022-02-16 [[./debian-and-nginx/][Migrating to a New Web Server Setup with Debian, Nginx, and Agate]] | |
| 89 | - 2022-02-10 [[./leaving-the-office/][Leaving Office-Based Work in the Past]] | |
| 90 | - 2022-02-10 [[./njalla-dns-api/][Dynamic DNS with Njalla API]] | |
| 91 | ||
| 92 | * 2021 | |
| 93 | ||
| 94 | - 2021-12-04 [[./cisa/][I Passed the CISA!]] | |
| 95 | - 2021-10-09 [[./apache-redirect/][Apache Redirect HTML Files to a Directory]] | |
| 96 | - 2021-08-25 [[./audit-sampling/][Audit Sampling with Python]] | |
| 97 | - 2021-07-15 [[./delete-gitlab-repos/][How to Delete All GitLab Repositories]] | |
| 98 | - 2021-05-30 [[./changing-git-authors/][Changing Git Authors]] | |
| 99 | - 2021-04-28 [[./photography/][Jumping Back Into Photography]] | |
| 100 | - 2021-04-23 [[./php-comment-system/][Roll Your Own Static Commenting System in PHP]] | |
| 101 | - 2021-04-17 [[./gemini-server/][Hosting a Gemini Server]] | |
| 102 | - 2021-03-30 [[./vps-web-server/][How to Set Up a VPS Web Server]] | |
| 103 | - 2021-03-28 [[./vaporwave-vs-outrun/][Vaporwave vs Outrun]] | |
| 104 | - 2021-03-28 [[./gemini-capsule/][Launching a Gemini Capsule]] | |
| 105 | - 2021-03-19 [[./clone-github-repos/][How to Clone All Repositories from a GitHub or Sourcehut Account]] | |
| 106 | - 2021-02-19 [[./macos/][macOS: Testing Out A New OS]] | |
| 107 | - 2021-01-04 [[./fediverse/][A Simple Guide to the Fediverse]] | |
| 108 | - 2021-01-07 [[./ufw/][Secure Your Network with the Uncomplicated Firewall (ufw)]] | |
| 109 | - 2021-01-01 [[./seum/][SEUM: Speedrunners from Hell]] | |
| 110 | ||
| 111 | * 2020 | |
| 112 | ||
| 113 | - 2020-12-29 [[./zork/][Zork: Let's Explore a Classic]] | |
| 114 | - 2020-12-27 [[./website-redesign/][Redesigning My Website: The 5 KB Result]] | |
| 115 | - 2020-12-28 [[./neon-drive/][Neon Drive: A Nostalgic 80s Arcade Racing Game]] | |
| 116 | - 2020-10-12 [[./mediocrity/][On the Pursuit of Mediocrity]] | |
| 117 | - 2020-09-25 [[./happiness-map/][Data Visualization: World Choropleth Map of Happiness]] | |
| 118 | - 2020-09-22 [[./internal-audit/][What is Internal Audit?]] | |
| 119 | - 2020-09-01 [[./visual-recognition/][IBM Watson Visual Recognition]] | |
| 120 | - 2020-08-29 [[./php-auth-flow/][PHP Authentication Flow]] | |
| 121 | - 2020-08-22 [[./redirect-github-pages/][Redirect GitHub Pages from Subdomain to the Top-Level Domain]] | |
| 122 | - 2020-07-26 [[./business-analysis/][Algorithmically Analyzing Local Businesses]] | |
| 123 | - 2020-07-20 [[./video-game-sales/][Data Exploration: Video Game Sales]] | |
| 124 | - 2020-05-19 [[./customizing-ubuntu/][Beginner's Guide: Customizing Ubuntu]] | |
| 125 | - 2020-05-03 [[./homelab/][An Inside Look at My Homelab]] | |
| 126 | - 2020-03-25 [[./session-manager/][Session Private Messenger]] | |
| 127 | - 2020-02-09 [[./cryptography-basics/][Cryptography Basics]] | |
| 128 | - 2020-01-26 [[./steam-on-ntfs/][Linux Gaming Tweak: Steam on NTFS Drives]] | |
| 129 | - 2020-01-25 [[./linux-software/][Linux Software]] | |
| 130 | ||
| 131 | * 2019 | |
| 132 | ||
| 133 | - 2019-12-16 [[./password-security//][Password Security]] | |
| 134 | - 2019-12-03 [[./the-ansoff-matrix//][The Ansoff Matrix]] | |
| 135 | - 2019-09-09 [[./audit-analytics//][Data Analysis in Auditing]] | |
| 136 | - 2019-01-07 [[./useful-css//][Useful CSS Snippets]] | |
| 137 | ||
| 138 | * 2018 | |
| 139 | ||
| 140 | - 2018-12-08 [[./aes-encryption//][AES Encryption]] | |
| 141 | - 2018-11-28 [[./cpp-compiler//][The C++ Compiler]] | |
content/blog/2020-09-22-internal-audit.md → blog/internal-audit/index.org renamed +54 −70
| @@ -1,33 +1,32 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-09-22 | |
| 3 | title = "What is Internal Audit?" | |
| 4 | description = "Learn about the Internal Audit function and their purpose." | |
| 5 | +++ | |
| 1 | #+title: What is Internal Audit? | |
| 2 | #+date: 2020-09-22 | |
| 3 | #+description: Learn about the Internal Audit function and their purpose. | |
| 4 | #+filetags: :audit: | |
| 6 | 5 | |
| 7 |  | |
| 9 | ||
| 10 | # Definitions | |
| 6 | #+caption: Internal Audit Overview | |
| 7 | [[https://img.cleberg.net/blog/20200922-what-is-internal-audit/internal-audit-overview.jpg]] | |
| 11 | 8 | |
| 9 | * Definitions | |
| 12 | 10 | One of the many reasons that Internal Audit needs such thorough |
| 13 | 11 | explaining to non-auditors is that Internal Audit can serve many |
| 14 | 12 | purposes, depending on the organization's size and needs. However, the |
| 15 | 13 | Institute of Internal Auditors (IIA) defines Internal Auditing as: |
| 16 | 14 | |
| 17 | > Internal auditing is an independent, objective assurance and | |
| 18 | > consulting activity designed to add value and improve an | |
| 19 | > organization's operations. It helps an organization accomplish its | |
| 20 | > objectives by bringing a systematic, disciplined approach to evaluate | |
| 21 | > and improve the effectiveness of risk management, control, and | |
| 22 | > governance processes. | |
| 15 | #+begin_quote | |
| 16 | Internal auditing is an independent, objective assurance and consulting | |
| 17 | activity designed to add value and improve an organization's operations. | |
| 18 | It helps an organization accomplish its objectives by bringing a | |
| 19 | systematic, disciplined approach to evaluate and improve the | |
| 20 | effectiveness of risk management, control, and governance processes. | |
| 23 | 21 | |
| 24 | However, this definition uses quite a few terms that aren't clear | |
| 25 | unless the reader already has a solid understanding of the auditing | |
| 26 | profession. To further explain, the following is a list of definitions | |
| 27 | that can help supplement understanding of internal auditing. | |
| 22 | #+end_quote | |
| 28 | 23 | |
| 29 | ## Independent | |
| 24 | However, this definition uses quite a few terms that aren't clear unless | |
| 25 | the reader already has a solid understanding of the auditing profession. | |
| 26 | To further explain, the following is a list of definitions that can help | |
| 27 | supplement understanding of internal auditing. | |
| 30 | 28 | |
| 29 | ** Independent | |
| 31 | 30 | Independence is the freedom from conditions that threaten the ability of |
| 32 | 31 | the internal audit activity to carry out internal audit responsibilities |
| 33 | 32 | in an unbiased manner. To achieve the degree of independence necessary |
| @@ -38,8 +37,7 @@ dual-reporting relationship. Threats to independence must be managed at | ||
| 38 | 37 | the individual auditor, engagement, functional, and organizational |
| 39 | 38 | levels. |
| 40 | 39 | |
| 41 | ## Objective | |
| 42 | ||
| 40 | ** Objective | |
| 43 | 41 | Objectivity is an unbiased mental attitude that allows internal auditors |
| 44 | 42 | to perform engagements in such a manner that they believe in their work |
| 45 | 43 | product and that no quality compromises are made. Objectivity requires |
| @@ -47,8 +45,7 @@ that internal auditors do not subordinate their judgment on audit | ||
| 47 | 45 | matters to others. Threats to objectivity must be managed at the |
| 48 | 46 | individual auditor, engagement, functional, and organizational levels. |
| 49 | 47 | |
| 50 | ## Assurance | |
| 51 | ||
| 48 | ** Assurance | |
| 52 | 49 | Assurance services involve the internal auditor's objective assessment |
| 53 | 50 | of evidence to provide opinions or conclusions regarding an entity, |
| 54 | 51 | operation, function, process, system, or other subject matters. The |
| @@ -59,8 +56,7 @@ operation, function, process, system, or other subject - (the process | ||
| 59 | 56 | owner), (2) the person or group making the assessment - (the internal |
| 60 | 57 | auditor), and (3) the person or group using the assessment - (the user). |
| 61 | 58 | |
| 62 | ## Consulting | |
| 63 | ||
| 59 | ** Consulting | |
| 64 | 60 | Consulting services are advisory in nature and are generally performed |
| 65 | 61 | at the specific request of an engagement client. The nature and scope of |
| 66 | 62 | the consulting engagement are subject to agreement with the engagement |
| @@ -70,23 +66,21 @@ person or group seeking and receiving the advice (the engagement | ||
| 70 | 66 | client). When performing consulting services, the internal auditor |
| 71 | 67 | should maintain objectivity and not assume management responsibility. |
| 72 | 68 | |
| 73 | ## Governance, Risk Management, & Compliance (GRC) | |
| 74 | ||
| 69 | ** Governance, Risk Management, & Compliance (GRC) | |
| 75 | 70 | The integrated collection of capabilities that enable an organization to |
| 76 | 71 | reliably achieve objectives, address uncertainty and act with integrity. |
| 77 | 72 | |
| 78 | # Audit Charter & Standards | |
| 79 | ||
| 80 | First, it's important to note that not every organization needs | |
| 81 | internal auditors. In fact, it's unwise for an organization to hire | |
| 82 | internal auditors unless they have regulatory requirements for auditing | |
| 83 | and have the capital to support the department. Internal audit is a cost | |
| 84 | center that can only affect revenue indirectly. | |
| 73 | * Audit Charter & Standards | |
| 74 | First, it's important to note that not every organization needs internal | |
| 75 | auditors. In fact, it's unwise for an organization to hire internal | |
| 76 | auditors unless they have regulatory requirements for auditing and have | |
| 77 | the capital to support the department. Internal audit is a cost center | |
| 78 | that can only affect revenue indirectly. | |
| 85 | 79 | |
| 86 | 80 | Once an organization determines the need for internal assurance |
| 87 | 81 | services, they will hire a Chief Audit Executive and create the audit |
| 88 | charter. This charter is a document, approved by the company's | |
| 89 | governing body, that will define internal audit's purpose, authority, | |
| 82 | charter. This charter is a document, approved by the company's governing | |
| 83 | body, that will define internal audit's purpose, authority, | |
| 90 | 84 | responsibility, and position within the organization. Fortunately, the |
| 91 | 85 | IIA has model charters available to IIA members for those developing or |
| 92 | 86 | improving their charter. |
| @@ -101,21 +95,20 @@ assurance. Finally, additional standards such as FASB, GAAP, and | ||
| 101 | 95 | industry-specific standards are used when performing internal audit |
| 102 | 96 | work. |
| 103 | 97 | |
| 104 | # Three Lines of Defense | |
| 105 | ||
| 106 | [The IIA](https://theiia.org) released the original Three Lines of | |
| 98 | * Three Lines of Defense | |
| 99 | [[https://theiia.org][The IIA]] released the original Three Lines of | |
| 107 | 100 | Defense model in 2013, but have released an updated version in 2020. |
| 108 | 101 | Here is what the Three Lines of Defense model has historically looked |
| 109 | 102 | like: |
| 110 | 103 | |
| 111 | 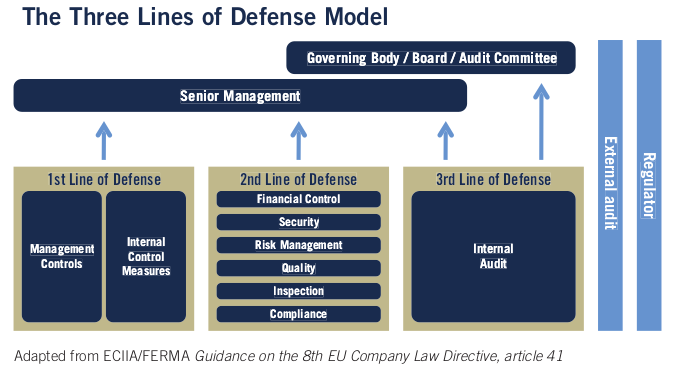 | |
| 104 | #+caption: 2013 Three Lines of Defense Model | |
| 105 | [[https://img.cleberg.net/blog/20200922-what-is-internal-audit/three_lines_model.png]] | |
| 113 | 106 | |
| 114 | 107 | I won't go into depth about the changes made to the model in this |
| 115 | 108 | article. Instead, let's take a look at the most current model. |
| 116 | 109 | |
| 117 | 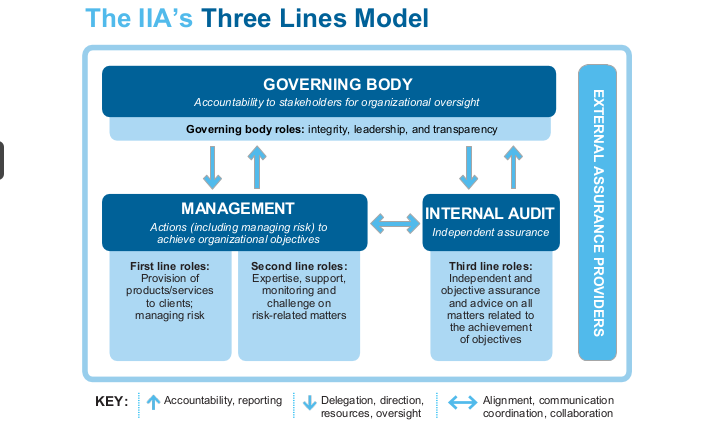 | |
| 110 | #+caption: 2020 Three Lines of Defense Model | |
| 111 | [[https://img.cleberg.net/blog/20200922-what-is-internal-audit/updated_three_lines_model.png]] | |
| 119 | 112 | |
| 120 | 113 | The updated model forgets the strict idea of areas performing their own |
| 121 | 114 | functions or line of defense. Instead of talking about management, risk, |
| @@ -126,10 +119,10 @@ Looking at this model from an auditing perspective shows us that | ||
| 126 | 119 | auditors will need to align, communicate, and collaborate with |
| 127 | 120 | management, including business area managers and chief officers, as well |
| 128 | 121 | as reporting to the governing body. The governing body will instruct |
| 129 | internal audit *functionally* on their goals and track their progress | |
| 122 | internal audit /functionally/ on their goals and track their progress | |
| 130 | 123 | periodically. |
| 131 | 124 | |
| 132 | However, the internal audit department will report *administratively* to | |
| 125 | However, the internal audit department will report /administratively/ to | |
| 133 | 126 | a chief officer in the company for the purposes of collaboration, |
| 134 | 127 | direction, and assistance with the business. Note that in most |
| 135 | 128 | situations, the governing body is the audit committee on the company's |
| @@ -139,22 +132,20 @@ The result of this structure is that internal audit is an independent | ||
| 139 | 132 | and objective function that can provide assurance over the topics they |
| 140 | 133 | audit. |
| 141 | 134 | |
| 142 | # Audit Process | |
| 143 | ||
| 135 | * Audit Process | |
| 144 | 136 | A normal audit will generally follow the same process, regardless of the |
| 145 | 137 | topic. However, certain special projects or abnormal business areas may |
| 146 | 138 | call for changes to the audit process. The audit process is not set in |
| 147 | 139 | stone, it's simply a set of best practices so that audits can be |
| 148 | 140 | performed consistently. |
| 149 | 141 | |
| 150 | 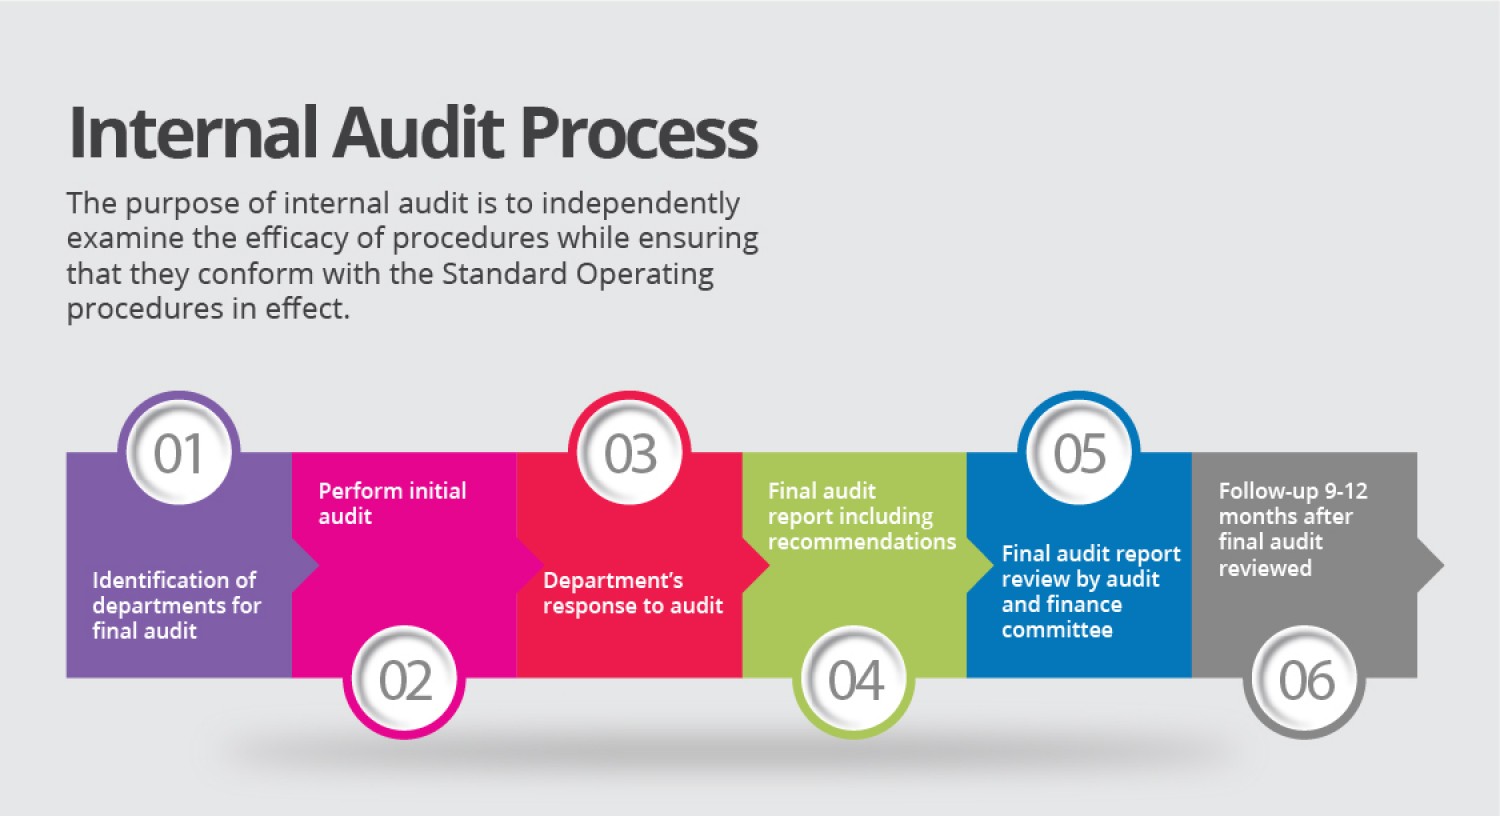 | |
| 142 | #+caption: The Internal Audit Process | |
| 143 | [[https://img.cleberg.net/blog/20200922-what-is-internal-audit/internal-audit-process.jpg]] | |
| 152 | 144 | |
| 153 | 145 | While different organizations may tweak the process, it will generally |
| 154 | 146 | follow this flow: |
| 155 | 147 | |
| 156 | ## 1. Risk Assessment | |
| 157 | ||
| 148 | ** 1. Risk Assessment | |
| 158 | 149 | The risk assessment part of the process has historically been performed |
| 159 | 150 | annually, but many organizations have moved to performing this process |
| 160 | 151 | much more frequently. In fact, some organizations are moving to an agile |
| @@ -168,8 +159,7 @@ Once a risk assessment has been documented, the audit department has a | ||
| 168 | 159 | prioritized list of risks that can be audited. This is usually in the |
| 169 | 160 | form of auditable entities, such as business areas or departments. |
| 170 | 161 | |
| 171 | ## 2. Planning | |
| 172 | ||
| 162 | ** 2. Planning | |
| 173 | 163 | During the planning phase of an audit, auditors will meet with the |
| 174 | 164 | business area to discuss the various processes, controls, and risks |
| 175 | 165 | applicable to the business. This helps the auditors determine the scope |
| @@ -177,8 +167,7 @@ limits for the audit, as well as timing and subject-matter experts. | ||
| 177 | 167 | Certain documents will be created in this phase that will be used to |
| 178 | 168 | keep the audit on-track an in-scope as it goes forward. |
| 179 | 169 | |
| 180 | ## 3. Testing | |
| 181 | ||
| 170 | ** 3. Testing | |
| 182 | 171 | The testing phase, also known as fieldwork or execution, is where |
| 183 | 172 | internal auditors will take the information they've discovered and test |
| 184 | 173 | it against regulations, industry standards, company rules, best |
| @@ -192,8 +181,7 @@ well as compared against regulations such as the Equal Employment | ||
| 192 | 181 | Opportunity (EEO), American with Disabilities Act, and National Labor |
| 193 | 182 | Relations Act. |
| 194 | 183 | |
| 195 | ## 4. Reporting | |
| 196 | ||
| 184 | ** 4. Reporting | |
| 197 | 185 | Once all the tests have been completed, the audit will enter the |
| 198 | 186 | reporting phase. This is when the audit team will conclude on the |
| 199 | 187 | evidence they've collected, interviews they've held, and any opinions |
| @@ -204,16 +192,14 @@ opportunity to respond to the report and submit an action plan and time | ||
| 204 | 192 | frame. These responses become part of the final report which is |
| 205 | 193 | distributed to the appropriate level of administration. |
| 206 | 194 | |
| 207 | ## 5. Follow-Up | |
| 208 | ||
| 195 | ** 5. Follow-Up | |
| 209 | 196 | After audits have been completed and management has formed action plans |
| 210 | 197 | and time frames for audit issues, internal audit will follow up once |
| 211 | 198 | that due date has arrived. In most cases, the follow-up will simply |
| 212 | 199 | consist of a meeting to discuss how the action plan has been completed |
| 213 | 200 | and to request documentation to prove it. |
| 214 | 201 | |
| 215 | # Audit Department Structure | |
| 216 | ||
| 202 | * Audit Department Structure | |
| 217 | 203 | While an internal audit department is most often thought of as a team of |
| 218 | 204 | full-time employees, there are actually many different ways in which a |
| 219 | 205 | department can be structured. As the world becomes more digital and |
| @@ -230,12 +216,11 @@ large organizations, but organizations tend to rotate lower-level audit | ||
| 230 | 216 | staff instead of managers. This helps prevent any significant knowledge |
| 231 | 217 | loss as auditors rotate out to business areas. |
| 232 | 218 | |
| 233 | # Consulting | |
| 234 | ||
| 219 | * Consulting | |
| 235 | 220 | Consulting is not an easy task at any organization, especially for a |
| 236 | 221 | department that can have negative perceptions within the organization as |
| 237 | the "compliance police." However, once an internal audit department | |
| 238 | has delivered value to organization, adding consulting to their suite of | |
| 222 | the "compliance police." However, once an internal audit department has | |
| 223 | delivered value to organization, adding consulting to their suite of | |
| 239 | 224 | services is a smart move. In most cases, Internal Audit can insert |
| 240 | 225 | themselves into a consulting role without affecting the process of |
| 241 | 226 | project management at the company. This means that internal audit can |
| @@ -243,10 +228,9 @@ add objective assurance and opinions to business areas as they develop | ||
| 243 | 228 | new processes, instead of coming in periodically to audit an area and |
| 244 | 229 | file issues that could have been fixed at the beginning. |
| 245 | 230 | |
| 246 | # Data Science & Data Analytics | |
| 247 | ||
| 248 |  | |
| 231 | * Data Science & Data Analytics | |
| 232 | #+caption: Data Science Skill Set | |
| 233 | [[https://img.cleberg.net/blog/20200922-what-is-internal-audit/data-science-skillset.png]] | |
| 250 | 234 | |
| 251 | 235 | One major piece of the internal audit function in the modern world is |
| 252 | 236 | data science. While the process is data science, most auditors will |
content/blog/2022-02-10-leaving-the-office.md → blog/leaving-the-office/index.org renamed +54 −56
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-02-10 | |
| 3 | title = "Leaving Office-Based Work in the Past" | |
| 4 | description = "My thoughts on the current surge of remote work and what that means for full-time office-based roles." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## The Working World is Changing | |
| 1 | #+title: Leaving Office-Based Work in the Past | |
| 2 | #+date: 2022-02-10 | |
| 3 | #+description: My thoughts on the current surge of remote work and what that means for full-time office-based roles. | |
| 4 | #+filetags: :audit: | |
| 8 | 5 | |
| 6 | * The Working World is Changing | |
| 9 | 7 | There has been a trend for the past few years of companies slowly |
| 10 | 8 | realizing that the pandemic is not just a temporary state that will go |
| 11 | 9 | away eventually and let everything return to the way it was before. In |
| @@ -23,10 +21,8 @@ I decided to take a look back at my relatively short career so far and | ||
| 23 | 21 | compare the positive and negative effects of the different work |
| 24 | 22 | environments I've been in. |
| 25 | 23 | |
| 26 | ## In-Person Offices | |
| 27 | ||
| 28 | ### Retail Internship | |
| 29 | ||
| 24 | * In-Person Offices | |
| 25 | ** Retail Internship | |
| 30 | 26 | I started my first job as a management intern at a busy retail pharmacy, |
| 31 | 27 | working my 40-hour weeks on my feet. As these retail stores don't |
| 32 | 28 | believe in resting or sitting down, you can guarantee that you will |
| @@ -42,10 +38,9 @@ However, if you are able to operate a retail store with a limited crew | ||
| 42 | 38 | and provide enough comfort and support, I believe these jobs could be |
| 43 | 39 | both comfortable and efficient. |
| 44 | 40 | |
| 45 | ### Semi-Private Cubicles | |
| 46 | ||
| 47 |  | |
| 41 | ** Semi-Private Cubicles | |
| 42 | #+caption: Semi-Private Cubicles | |
| 43 | [[https://img.cleberg.net/blog/20220210-leaving-office-based-work-in-the-past/private_cubicles.png]] | |
| 49 | 44 | |
| 50 | 45 | After about a year, I was able to find another internship - this time, |
| 51 | 46 | it was in my field of interest: internal auditing. This was for a life |
| @@ -60,8 +55,8 @@ formed into cubicles that house 4 desks/employees. These "pods" of | ||
| 60 | 55 | 4-person cubicles are linked throughout each floor of the headquarters |
| 61 | 56 | (except the sales people, who had that open-floor concept going on). The |
| 62 | 57 | walls of the cubicle were tall and provided a lot of privacy and |
| 63 | sound-proofing, except when I used the standing desk feature (I'm over | |
| 64 | 6 feet tall, so probably not an issue for most people). | |
| 58 | sound-proofing, except when I used the standing desk feature (I'm over 6 | |
| 59 | feet tall, so probably not an issue for most people). | |
| 65 | 60 | |
| 66 | 61 | I loved this environment, it allowed me to focus on my work with minimal |
| 67 | 62 | distractions, but also allowed easy access, so I could spin around in my |
| @@ -69,10 +64,9 @@ chair and chat with my friends without leaving my chair. This is the | ||
| 69 | 64 | closest I've been to a home office environment (which is my personal |
| 70 | 65 | favorite, as I'll get to later in this post). |
| 71 | 66 | |
| 72 | ### Semi-Open Floor Concept | |
| 73 | ||
| 74 |  | |
| 67 | ** Semi-Open Floor Concept | |
| 68 | #+caption: Semi-Open Floor Concept | |
| 69 | [[https://img.cleberg.net/blog/20220210-leaving-office-based-work-in-the-past/semi_open_office.png]] | |
| 76 | 70 | |
| 77 | 71 | When I shifted to my first full-time internal audit job out of college, |
| 78 | 72 | I was working at a company that was headquartered on a floor in a |
| @@ -80,8 +74,8 @@ downtown high-rise building. The company was only about 20 years old | ||
| 80 | 74 | when I worked there and were trying a lot of new things to attract young |
| 81 | 75 | talent, one of which was a semi-open floor concept for the office. My |
| 82 | 76 | department worked just around the hallway corner from the executive |
| 83 | offices and used that "modern" layout young tech companies started | |
| 84 | using in the 2000s/2010s. | |
| 77 | offices and used that "modern" layout young tech companies started using | |
| 78 | in the 2000s/2010s. | |
| 85 | 79 | |
| 86 | 80 | Each desk was brief, and you could look most coworkers in the face |
| 87 | 81 | without moving from your chair, I hated this so much. Directly to my |
| @@ -97,17 +91,15 @@ conversation would be constant throughout the day while you try to work. | ||
| 97 | 91 | For someone like me, who needs silence to get work done, that was a |
| 98 | 92 | non-starter. |
| 99 | 93 | |
| 100 | ### Hotel Office Concept | |
| 101 | ||
| 102 |  | |
| 94 | ** Hotel Office Concept | |
| 95 | #+caption: Hotel Office Concept | |
| 96 | [[https://img.cleberg.net/blog/20220210-leaving-office-based-work-in-the-past/hotel_desks.png]] | |
| 104 | 97 | |
| 105 | 98 | I currently work for a company remotely (for now) and travel to the |
| 106 | 99 | office every once in a while for events and to help coach the staff |
| 107 | 100 | underneath me. The office I visit uses the hotel desk concept, where you |
| 108 | need to check in at a touch screen when you enter the office and | |
| 109 | "rent" a desk for the day. The same goes for offices and meeting | |
| 110 | rooms. | |
| 101 | need to check in at a touch screen when you enter the office and "rent" | |
| 102 | a desk for the day. The same goes for offices and meeting rooms. | |
| 111 | 103 | |
| 112 | 104 | These desks are flat-top only and do not have any walls at all. In |
| 113 | 105 | addition, they're stacked with one row of 4 desks facing another row of |
| @@ -125,10 +117,9 @@ Luckily, you can rent offices with doors that offer quiet and privacy, | ||
| 125 | 117 | which can be very nice if you have a lot of meetings or webinars on a |
| 126 | 118 | certain day. |
| 127 | 119 | |
| 128 | ## Home Office | |
| 129 | ||
| 130 |  | |
| 120 | * Home Office | |
| 121 | #+caption: Home Office | |
| 122 | [[https://img.cleberg.net/blog/20220210-leaving-office-based-work-in-the-past/home_office.png]] | |
| 132 | 123 | |
| 133 | 124 | Okay, now let's finally get to the home office concept. I have worked |
| 134 | 125 | from home for a little over two years at this point, across three |
| @@ -140,11 +131,13 @@ These things might not apply to you, and that's fine. Everyone has a | ||
| 140 | 131 | different situation, and I really don't think you'll know what works |
| 141 | 132 | until you try. |
| 142 | 133 | |
| 143 | ### Tip #1 | |
| 144 | ||
| 134 | ** Tip #1 | |
| 145 | 135 | Let's start with my top rule for a home office: |
| 146 | 136 | |
| 147 | > If you live with others, working in a shared space is not effective. | |
| 137 | #+begin_quote | |
| 138 | If you live with others, working in a shared space is not effective. | |
| 139 | ||
| 140 | #+end_quote | |
| 148 | 141 | |
| 149 | 142 | It just does not work. If you have another person sleeping in your |
| 150 | 143 | bedroom, it is difficult to manage your work schedule with their |
| @@ -157,12 +150,14 @@ likely won't work either. Distractions will come far more frequently: | ||
| 157 | 150 | televisions, cooking, cleaning, deliveries, etc. If you're like me, |
| 158 | 151 | you'll end up playing a game instead of actually doing any work. |
| 159 | 152 | |
| 160 | ### Tip #2 | |
| 161 | ||
| 153 | ** Tip #2 | |
| 162 | 154 | Okay, the second thing I've discovered that works for me: |
| 163 | 155 | |
| 164 | > Use the pomodoro method (or something similar) to balance work tasks | |
| 165 | > with personal tasks. | |
| 156 | #+begin_quote | |
| 157 | Use the pomodoro method (or something similar) to balance work tasks | |
| 158 | with personal tasks. | |
| 159 | ||
| 160 | #+end_quote | |
| 166 | 161 | |
| 167 | 162 | I use a very casual version of the pomodoro method where I will work for |
| 168 | 163 | 1-2 hours (usually set in strict intervals like 1, 1.5, 2 hours) and |
| @@ -176,13 +171,15 @@ clothes in the washer, get the mail, etc. If you're in a convenient | ||
| 176 | 171 | location, this usually gives time for things like getting groceries (as |
| 177 | 172 | long as you're not a slow shopper). |
| 178 | 173 | |
| 179 | ### Tip #3 | |
| 180 | ||
| 174 | ** Tip #3 | |
| 181 | 175 | While I listed this one as number three, I don't think I'd accomplish |
| 182 | 176 | anything without it: |
| 183 | 177 | |
| 184 | > Document everything: even things you didn't before - such as task | |
| 185 | > lists and notes from casual calls or meetings. | |
| 178 | #+begin_quote | |
| 179 | Document everything: even things you didn't before - such as task lists | |
| 180 | and notes from casual calls or meetings. | |
| 181 | ||
| 182 | #+end_quote | |
| 186 | 183 | |
| 187 | 184 | I've noticed that staying in an office gave me more constant reminders |
| 188 | 185 | of outstanding tasks or facts I had learned in a conversation. |
| @@ -196,11 +193,13 @@ has improved my retention immensely. Beyond helping my mental | ||
| 196 | 193 | recollection, it has saved me numerous times when I need to do a keyword |
| 197 | 194 | search for some topic that was discussed 6+ months ago. |
| 198 | 195 | |
| 199 | ### Tip #4 | |
| 200 | ||
| 196 | ** Tip #4 | |
| 201 | 197 | Okay, last one for now. |
| 202 | 198 | |
| 203 | > Keep your work area clean. | |
| 199 | #+begin_quote | |
| 200 | Keep your work area clean. | |
| 201 | ||
| 202 | #+end_quote | |
| 204 | 203 | |
| 205 | 204 | This one is straightforward, but I know some people struggle with |
| 206 | 205 | cleanliness or may not believe it makes a difference. Trust me, keeping |
| @@ -211,8 +210,8 @@ Just think about it, you walk into your home office and see a clean desk | ||
| 211 | 210 | with a laptop, dock, monitors, keyboard, mouse, and a notepad with a pen |
| 212 | 211 | on top. |
| 213 | 212 | |
| 214 | Now imagine the opposite, there's an office with the same equipment, | |
| 215 | but there are clothes hanging on the chair, empty drink bottles, candy | |
| 213 | Now imagine the opposite, there's an office with the same equipment, but | |
| 214 | there are clothes hanging on the chair, empty drink bottles, candy | |
| 216 | 215 | wrappers and dirty plates. This can take both a mental and emotional |
| 217 | 216 | toll by bringing constant disarray and stress into your working |
| 218 | 217 | environment. |
| @@ -220,12 +219,11 @@ environment. | ||
| 220 | 219 | Just keep things clean each day, and you won't need to do any big |
| 221 | 220 | cleaning days to recover. |
| 222 | 221 | |
| 223 | ## My Preferences | |
| 224 | ||
| 222 | * My Preferences | |
| 225 | 223 | I've talked about the different environments I've worked in and |
| 226 | 224 | expressed some honest thoughts on pros or cons to each, but what do I |
| 227 | prefer? Well, if you're reading along, you should be able to tell that | |
| 228 | I much prefer a home office above all else. | |
| 225 | prefer? Well, if you're reading along, you should be able to tell that I | |
| 226 | much prefer a home office above all else. | |
| 229 | 227 | |
| 230 | 228 | Being able to control my own day and allot my time as needed has brought |
| 231 | 229 | a calmness to my life and has allowed me to maximize each day. I feel |
| @@ -238,5 +236,5 @@ my work done. | ||
| 238 | 236 | |
| 239 | 237 | Cubicles are good! I agree with Alice (from the comic Dilbert): |
| 240 | 238 | |
| 241 |  | |
| 239 | #+caption: Dilbert comic strip | |
| 240 | [[https://img.cleberg.net/blog/20220210-leaving-office-based-work-in-the-past/dilbert_120109.png]] | |
blog/linux-display-manager/index.org added +72
| @@ -0,0 +1,72 @@ | ||
| 1 | #+title: How to Disable or Change the Display Manager on Void Linux | |
| 2 | #+date: 2022-10-30 | |
| 3 | #+description: Learn how to remove or modify the display manager on Void Linux. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * Display Manager Services | |
| 7 | In order to change the | |
| 8 | [[https://en.wikipedia.org/wiki/Display_manager][display manager]] on | |
| 9 | Void Linux - or any other Linux distro - you need to identify the | |
| 10 | currently enabled display manager. | |
| 11 | ||
| 12 | ** Disabling the Current Display Manager | |
| 13 | Void Linux only has one ISO available for download with a pre-built | |
| 14 | display manager at the time of this post: the XFCE ISO. If you've | |
| 15 | installed this version, the pre-assigned display manager is =lxdm=. If | |
| 16 | you installed another display manager, replace =lxdm= in the following | |
| 17 | command with the display manager you have installed. | |
| 18 | ||
| 19 | To disable =lxdm=, simply remove the service symlink: | |
| 20 | ||
| 21 | #+begin_src sh | |
| 22 | sudo rm /var/service/lxdm | |
| 23 | #+end_src | |
| 24 | ||
| 25 | ** Enabling a New Display Manager | |
| 26 | If you want to enable a new display manager, you can do so after =lxdm= | |
| 27 | is disabled. Make sure to replace =<new_display_manager>= with your new | |
| 28 | DM, such as =gdm=, =xdm=, etc. | |
| 29 | ||
| 30 | #+begin_src sh | |
| 31 | sudo ln -s /etc/sv/<new_display_manager> /var/service | |
| 32 | #+end_src | |
| 33 | ||
| 34 | * Set Up =.xinitrc= | |
| 35 | Depending on your setup, you may need to create a few X files, such as | |
| 36 | =~/.xinitrc=. For my personal set-up, I created this file to launch the | |
| 37 | i3wm as my desktop. | |
| 38 | ||
| 39 | #+begin_src sh | |
| 40 | nano ~/.xinitrc | |
| 41 | #+end_src | |
| 42 | ||
| 43 | #+begin_src sh | |
| 44 | #!/bin/sh | |
| 45 | ||
| 46 | exec i3 | |
| 47 | #+end_src | |
| 48 | ||
| 49 | If you run a desktop other than i3, simply replace =i3= with the shell | |
| 50 | command that launches that desktop. | |
| 51 | ||
| 52 | * Set Up Your Shell Profile | |
| 53 | Finally, in order to automatically launch an X session upon login, you | |
| 54 | will need to edit the =.bash_profile= (bash) or =.zprofile= (zsh) files | |
| 55 | for your shell: | |
| 56 | ||
| 57 | #+begin_src sh | |
| 58 | nano ~/.zprofile | |
| 59 | #+end_src | |
| 60 | ||
| 61 | Add the following snippet to the end of the shell profile file. This | |
| 62 | will execute the =startx= command upon login. | |
| 63 | ||
| 64 | #+begin_src sh | |
| 65 | if [ -z "${DISPLAY}" ] && [ "${XDG_VTNR}" -eq 1 ]; then | |
| 66 | exec startx | |
| 67 | fi | |
| 68 | #+end_src | |
| 69 | ||
| 70 | Alternatively, you can ignore this step and simply choose to manually | |
| 71 | execute =startx= upon login. This can be useful if you have issues with | |
| 72 | your desktop or like to manually launch different desktops by choice. | |
content/blog/2020-01-25-linux-software.md → blog/linux-software/index.org renamed +123 −127
| @@ -1,172 +1,169 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-01-25 | |
| 3 | title = "Linux Software" | |
| 4 | description = "A look at some useful Linux applications." | |
| 5 | +++ | |
| 6 | ||
| 7 | # GUI Applications | |
| 8 | ||
| 9 | ## Etcher | |
| 10 | ||
| 11 |  | |
| 12 | ||
| 13 | [Etcher](https://www.balena.io/etcher/) is a quick and easy way to burn | |
| 14 | ISO images to CDs and USB devices. There are two different ways you can | |
| 15 | install this program. First, you can navigate to the [official | |
| 16 | website](https://www.balena.io/etcher/) and download the AppImage file, | |
| 17 | which can run without installation. | |
| 1 | #+title: Linux Software | |
| 2 | #+date: 2020-01-25 | |
| 3 | #+description: A look at some useful Linux applications. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * GUI Applications | |
| 7 | ** Etcher | |
| 8 | #+caption: Etcher Screenshot | |
| 9 | [[https://img.cleberg.net/blog/20200125-the-best-linux-software/etcher.png]] | |
| 10 | ||
| 11 | [[https://www.balena.io/etcher/][Etcher]] is a quick and easy way to | |
| 12 | burn ISO images to CDs and USB devices. There are two different ways you | |
| 13 | can install this program. First, you can navigate to the | |
| 14 | [[https://www.balena.io/etcher/][official website]] and download the | |
| 15 | AppImage file, which can run without installation. | |
| 18 | 16 | |
| 19 | 17 | However, AppImage files are not executable by default, so you'll either |
| 20 | 18 | need to right-click to open the properties of the file and click the |
| 21 | "Allow executing file as program" box in the Permissions tab or use | |
| 22 | the following command: | |
| 19 | "Allow executing file as program" box in the Permissions tab or use the | |
| 20 | following command: | |
| 23 | 21 | |
| 24 | ```sh | |
| 22 | #+begin_src sh | |
| 25 | 23 | chmod u+x FILE_NAME |
| 26 | ``` | |
| 24 | #+end_src | |
| 27 | 25 | |
| 28 | 26 | If you don't like AppImage files or just prefer repositories, you can |
| 29 | use the following commands to add the author's repository and install | |
| 30 | it through the command-line only. | |
| 27 | use the following commands to add the author's repository and install it | |
| 28 | through the command-line only. | |
| 31 | 29 | |
| 32 | 30 | First, you'll have to echo the repo and write it to a list file: |
| 33 | 31 | |
| 34 | ```sh | |
| 32 | #+begin_src sh | |
| 35 | 33 | echo "deb https://deb.etcher.io stable etcher" | sudo tee /etc/apt/sources.list.d/balena-etcher.list |
| 36 | ``` | |
| 34 | #+end_src | |
| 37 | 35 | |
| 38 | 36 | Next, add the application keys to Ubuntu's keyring: |
| 39 | 37 | |
| 40 | ```sh | |
| 38 | #+begin_src sh | |
| 41 | 39 | sudo apt-key adv --keyserver keyserver.ubuntu.com --recv-keys 379CE192D401AB61 |
| 42 | ``` | |
| 40 | #+end_src | |
| 43 | 41 | |
| 44 | 42 | Finally, update the repositories and install the app. |
| 45 | 43 | |
| 46 | ```sh | |
| 44 | #+begin_src sh | |
| 47 | 45 | sudo apt update && sudo apt install balena-etcher-electron |
| 48 | ``` | |
| 46 | #+end_src | |
| 49 | 47 | |
| 50 | 48 | Using Arch, Manjaro, or another distro using the AUR? Use this command |
| 51 | 49 | instead: |
| 52 | 50 | |
| 53 | ```sh | |
| 51 | #+begin_src sh | |
| 54 | 52 | sudo pacman -S etcher |
| 55 | ``` | |
| 56 | ||
| 57 | ## Atom | |
| 53 | #+end_src | |
| 58 | 54 | |
| 59 |  | |
| 55 | ** Atom | |
| 56 | #+caption: Atom Screenshot | |
| 57 | [[https://img.cleberg.net/blog/20200125-the-best-linux-software/atom.png]] | |
| 60 | 58 | |
| 61 | [Atom](https://atom.io) is the self-proclaimed "hackable text editor | |
| 62 | for the 21st century". This text editor is made by GitHub, [now owned | |
| 63 | by | |
| 64 | Microsoft](https://news.microsoft.com/2018/06/04/microsoft-to-acquire-github-for-7-5-billion/), | |
| 65 | and has some of the best add-ons available to customize the layout and | |
| 66 | abilities of the app. | |
| 59 | [[https://atom.io][Atom]] is the self-proclaimed "hackable text editor | |
| 60 | for the 21st century". This text editor is made by GitHub, | |
| 61 | [[https://news.microsoft.com/2018/06/04/microsoft-to-acquire-github-for-7-5-billion/][now | |
| 62 | owned by Microsoft]], and has some of the best add-ons available to | |
| 63 | customize the layout and abilities of the app. | |
| 67 | 64 | |
| 68 | 65 | First, add the Atom repository to your sources. |
| 69 | 66 | |
| 70 | ```sh | |
| 67 | #+begin_src sh | |
| 71 | 68 | sudo add-apt-repository ppa:webupd8team/atom |
| 72 | ``` | |
| 69 | #+end_src | |
| 73 | 70 | |
| 74 | 71 | Next, update your package listings and install atom. |
| 75 | 72 | |
| 76 | ```sh | |
| 73 | #+begin_src sh | |
| 77 | 74 | sudo apt update && sudo apt install atom |
| 78 | ``` | |
| 75 | #+end_src | |
| 79 | 76 | |
| 80 | 77 | If you have issues updating your packages with the Atom repository, |
| 81 | 78 | you'll need to use the snap package described below instead of the |
| 82 | 79 | repository. To remove the repository we just added, use this command: |
| 83 | 80 | |
| 84 | ```sh | |
| 81 | #+begin_src sh | |
| 85 | 82 | sudo add-apt-repository -r ppa:webupd8team/atom |
| 86 | ``` | |
| 83 | #+end_src | |
| 87 | 84 | |
| 88 | 85 | You can also install Atom as a snap package, but it must be installed |
| 89 | with the `--classic` flag. A [full explanation is | |
| 90 | available](https://language-bash.com/blog/how-to-snap-introducing-classic-confinement) | |
| 91 | if you'd like to read more about why you need the classic flag. | |
| 86 | with the =--classic= flag. A | |
| 87 | [[https://language-bash.com/blog/how-to-snap-introducing-classic-confinement][full | |
| 88 | explanation is available]] if you'd like to read more about why you need | |
| 89 | the classic flag. | |
| 92 | 90 | |
| 93 | ```sh | |
| 91 | #+begin_src sh | |
| 94 | 92 | snap install atom --classic |
| 95 | ``` | |
| 93 | #+end_src | |
| 96 | 94 | |
| 97 | 95 | Using Arch, Manjaro, or another distro using the AUR? Use this command |
| 98 | 96 | instead: |
| 99 | 97 | |
| 100 | ```sh | |
| 98 | #+begin_src sh | |
| 101 | 99 | sudo pacman -S atom |
| 102 | ``` | |
| 103 | ||
| 104 | --- | |
| 100 | #+end_src | |
| 105 | 101 | |
| 106 | ## Visual Studio Code | |
| 102 | ** Visual Studio Code | |
| 103 | #+caption: Visual Studio Code Code | |
| 104 | [[https://img.cleberg.net/blog/20200125-the-best-linux-software/vscode.png]] | |
| 107 | 105 | |
| 108 |  | |
| 109 | ||
| 110 | [Visual Studio Code](https://code.visualstudio.com) is yet another | |
| 106 | [[https://code.visualstudio.com][Visual Studio Code]] is yet another | |
| 111 | 107 | fantastic choice for programming on Linux, especially if you need those |
| 112 | 108 | extra add-ons to spice up your late-night coding sessions. The theme |
| 113 | 109 | used in the screenshot is |
| 114 | [Mars](https://marketplace.visualstudio.com/items?itemName=EliverLara.mars) | |
| 115 | by theme creator [Eliver Lara](https://github.com/EliverLara), who makes | |
| 116 | a ton of great themes for VS Code, Atom, and various Linux desktop | |
| 110 | [[https://marketplace.visualstudio.com/items?itemName=EliverLara.mars][Mars]] | |
| 111 | by theme creator [[https://github.com/EliverLara][Eliver Lara]], who | |
| 112 | makes a ton of great themes for VS Code, Atom, and various Linux desktop | |
| 117 | 113 | environments. |
| 118 | 114 | |
| 119 | To install VS Code, you'll need to download the `.deb` file from the | |
| 115 | To install VS Code, you'll need to download the =.deb= file from the | |
| 120 | 116 | official website. Once you've downloaded the file, either double-click |
| 121 | 117 | it to install through the Software Center or run the following command: |
| 122 | 118 | |
| 123 | ```sh | |
| 119 | #+begin_src sh | |
| 124 | 120 | sudo dpkg -i FILE_NAME.deb |
| 125 | ``` | |
| 121 | #+end_src | |
| 126 | 122 | |
| 127 | 123 | You can also install VS Code as a snap package, but it must be installed |
| 128 | with the `--classic` flag. A [full explanation is | |
| 129 | available](https://language-bash.com/blog/how-to-snap-introducing-classic-confinement) | |
| 130 | if you'd like to read more about why you need the classic flag. | |
| 124 | with the =--classic= flag. A | |
| 125 | [[https://language-bash.com/blog/how-to-snap-introducing-classic-confinement][full | |
| 126 | explanation is available]] if you'd like to read more about why you need | |
| 127 | the classic flag. | |
| 131 | 128 | |
| 132 | ```sh | |
| 129 | #+begin_src sh | |
| 133 | 130 | snap install code --classic |
| 134 | ``` | |
| 131 | #+end_src | |
| 135 | 132 | |
| 136 | 133 | Using Arch, Manjaro, or another distro using the AUR? Use these commands |
| 137 | 134 | instead: |
| 138 | 135 | |
| 139 | ```sh | |
| 136 | #+begin_src sh | |
| 140 | 137 | sudo pacman -S yay binutils make gcc pkg-config fakeroot yay -S visual-studio-code-bin |
| 141 | ``` | |
| 142 | ||
| 143 | ## GNOME Tweaks | |
| 138 | #+end_src | |
| 144 | 139 | |
| 145 |  | |
| 140 | ** GNOME Tweaks | |
| 141 | #+caption: Gnome Tweaks Screenshot | |
| 142 | [[https://img.cleberg.net/blog/20200125-the-best-linux-software/gnome-tweaks.png]] | |
| 146 | 143 | |
| 147 | [Gnome Tweaks](https://gitlab.gnome.org/GNOME/gnome-tweaks) is the | |
| 144 | [[https://gitlab.gnome.org/GNOME/gnome-tweaks][Gnome Tweaks]] is the | |
| 148 | 145 | ultimate tool to use if you want to customize your GNOME desktop |
| 149 | 146 | environment. This is how you can switch application themes (GTK), shell |
| 150 | 147 | themes, icons, fonts, and more. To install GNOME Tweaks on Ubuntu, you |
| 151 | 148 | just need to install the official package. |
| 152 | 149 | |
| 153 | ```sh | |
| 150 | #+begin_src sh | |
| 154 | 151 | sudo apt install gnome-tweaks |
| 155 | ``` | |
| 152 | #+end_src | |
| 156 | 153 | |
| 157 | 154 | If you've installed Manjaro or Arch with Gnome, you should have the |
| 158 | tweak tool pre-installed. If you're on Fedora, this tool is available | |
| 159 | as an official package: | |
| 155 | tweak tool pre-installed. If you're on Fedora, this tool is available as | |
| 156 | an official package: | |
| 160 | 157 | |
| 161 | ```sh | |
| 158 | #+begin_src sh | |
| 162 | 159 | sudo dnf install gnome-tweaks |
| 163 | ``` | |
| 164 | ||
| 165 | ## Steam | |
| 160 | #+end_src | |
| 166 | 161 | |
| 167 |  | |
| 162 | ** Steam | |
| 163 | #+caption: Steam Screenshot | |
| 164 | [[https://img.cleberg.net/blog/20200125-the-best-linux-software/steam.png]] | |
| 168 | 165 | |
| 169 | [Steam](https://steampowered.com) is one of the most popular gaming | |
| 166 | [[https://steampowered.com][Steam]] is one of the most popular gaming | |
| 170 | 167 | libraries for computers and is one of the main reasons that many people |
| 171 | 168 | have been able to switch to Linux in recent years, thanks to Steam |
| 172 | 169 | Proton, which makes it easier to play games not officially created for |
| @@ -175,21 +172,21 @@ Linux platforms. | ||
| 175 | 172 | To install Steam on Ubuntu, you just need to install the official |
| 176 | 173 | package. |
| 177 | 174 | |
| 178 | ```sh | |
| 175 | #+begin_src sh | |
| 179 | 176 | sudo apt install steam-installer |
| 180 | ``` | |
| 177 | #+end_src | |
| 181 | 178 | |
| 182 | For Arch-based systems, you'll simply need to install the | |
| 183 | `steam` package. However, this requires that you enable the | |
| 184 | `multilib` source. To do so, use the following command: | |
| 179 | For Arch-based systems, you'll simply need to install the =steam= | |
| 180 | package. However, this requires that you enable the =multilib= source. | |
| 181 | To do so, use the following command: | |
| 185 | 182 | |
| 186 | ```sh | |
| 183 | #+begin_src sh | |
| 187 | 184 | sudo nano /etc/pacman.conf |
| 188 | ``` | |
| 185 | #+end_src | |
| 189 | 186 | |
| 190 | Now, scroll down and uncomment the `multilib` section. | |
| 187 | Now, scroll down and uncomment the =multilib= section. | |
| 191 | 188 | |
| 192 | ```config | |
| 189 | #+begin_src config | |
| 193 | 190 | # Before: |
| 194 | 191 | #[multilib] |
| 195 | 192 | #Include = /etc/pacman.d/mirrorlist |
| @@ -197,24 +194,23 @@ Now, scroll down and uncomment the `multilib` section. | ||
| 197 | 194 | # After: |
| 198 | 195 | [multilib] |
| 199 | 196 | Include = /etc/pacman.d/mirrorlist |
| 200 | ``` | |
| 197 | #+end_src | |
| 201 | 198 | |
| 202 | 199 | Finally, install the program: |
| 203 | 200 | |
| 204 | ```sh | |
| 201 | #+begin_src sh | |
| 205 | 202 | sudo pacman -S steam |
| 206 | ``` | |
| 203 | #+end_src | |
| 207 | 204 | |
| 208 | [Problem Launching Steam Games? Click | |
| 209 | Here.](./2020-01-26-steam-on-ntfs-drives.html) | |
| 205 | [[./2020-01-26-steam-on-ntfs-drives.html][Problem Launching Steam Games? | |
| 206 | Click Here.]] | |
| 210 | 207 | |
| 211 | # Command-Line Packages | |
| 208 | * Command-Line Packages | |
| 209 | ** neofetch | |
| 210 | #+caption: Neofetch Screenshot | |
| 211 | [[https://img.cleberg.net/blog/20200125-the-best-linux-software/neofetch.png]] | |
| 212 | 212 | |
| 213 | ## neofetch | |
| 214 | ||
| 215 |  | |
| 216 | ||
| 217 | [Neofetch](https://github.com/dylanaraps/neofetch) is a customizable | |
| 213 | [[https://github.com/dylanaraps/neofetch][Neofetch]] is a customizable | |
| 218 | 214 | tool used in the command-line to show system information. This is |
| 219 | 215 | exceptionally useful if you want to see your system's information |
| 220 | 216 | quickly without the clutter of some resource-heavy GUI apps. |
| @@ -222,54 +218,54 @@ quickly without the clutter of some resource-heavy GUI apps. | ||
| 222 | 218 | This is an official package if you're running Ubuntu 17.04 or later, so |
| 223 | 219 | simply use the following command: |
| 224 | 220 | |
| 225 | ```sh | |
| 221 | #+begin_src sh | |
| 226 | 222 | sudo apt install neofetch |
| 227 | ``` | |
| 223 | #+end_src | |
| 228 | 224 | |
| 229 | 225 | If you're running Ubuntu 16.10 or earlier, you'll have to use a series |
| 230 | 226 | of commands: |
| 231 | 227 | |
| 232 | ```sh | |
| 228 | #+begin_src sh | |
| 233 | 229 | sudo add-apt-repository ppa:dawidd0811/neofetch; sudo apt update; sudo apt install neofetch |
| 234 | ``` | |
| 230 | #+end_src | |
| 235 | 231 | |
| 236 | 232 | Using Arch, Manjaro, or another distro using the AUR? Use this command |
| 237 | 233 | instead: |
| 238 | 234 | |
| 239 | ```sh | |
| 235 | #+begin_src sh | |
| 240 | 236 | sudo pacman -S neofetch |
| 241 | ``` | |
| 242 | ||
| 243 | ## yt-dlp | |
| 237 | #+end_src | |
| 244 | 238 | |
| 245 |  | |
| 239 | ** yt-dlp | |
| 240 | #+caption: yt-dlp Screenshot | |
| 241 | [[https://img.cleberg.net/blog/20200125-the-best-linux-software/yt-dlp.png]] | |
| 246 | 242 | |
| 247 | [yt-dlp](https://github.com/yt-dlp/yt-dlp) is an extremely handy | |
| 243 | [[https://github.com/yt-dlp/yt-dlp][yt-dlp]] is an extremely handy | |
| 248 | 244 | command-line tool that allows you to download video or audio files from |
| 249 | 245 | various websites, such as YouTube. There are a ton of different options |
| 250 | when running this package, so be sure to run `yt-dlp --help` first to | |
| 246 | when running this package, so be sure to run =yt-dlp --help= first to | |
| 251 | 247 | look through everything you can do (or give up and search for the best |
| 252 | 248 | config online). |
| 253 | 249 | |
| 254 | While this shouldn't be a problem for most users, yt-dlp requires | |
| 255 | Python 2.6, 2.7, or 3.2+ to work correctly, so install Python if you | |
| 256 | don't have it already. You can check to see if you have Python | |
| 257 | installed by running: | |
| 250 | While this shouldn't be a problem for most users, yt-dlp requires Python | |
| 251 | 2.6, 2.7, or 3.2+ to work correctly, so install Python if you don't have | |
| 252 | it already. You can check to see if you have Python installed by | |
| 253 | running: | |
| 258 | 254 | |
| 259 | ```sh | |
| 255 | #+begin_src sh | |
| 260 | 256 | python -V |
| 261 | ``` | |
| 257 | #+end_src | |
| 262 | 258 | |
| 263 | 259 | To get the youtube-dl package, simply curl the URL and output the |
| 264 | 260 | results. |
| 265 | 261 | |
| 266 | ```sh | |
| 262 | #+begin_src sh | |
| 267 | 263 | sudo curl -L https://github.com/yt-dlp/yt-dlp/releases/latest/download/yt-dlp -o /usr/local/bin/yt-dlp |
| 268 | ``` | |
| 264 | #+end_src | |
| 269 | 265 | |
| 270 | 266 | Finally, make the file executable so that it can be run from the |
| 271 | 267 | command-line. |
| 272 | 268 | |
| 273 | ```sh | |
| 269 | #+begin_src sh | |
| 274 | 270 | sudo chmod a+rx /usr/local/bin/yt-dlp |
| 275 | ``` | |
| 271 | #+end_src | |
blog/local-llm/index.org added +108
| @@ -0,0 +1,108 @@ | ||
| 1 | #+title: Running Local LLMs on macOS and iOS | |
| 2 | #+date: 2024-01-13 | |
| 3 | #+description: Finding some useful applications for running local LLMs on macOS and iOS. | |
| 4 | #+filetags: :apple: | |
| 5 | ||
| 6 | * Requirements | |
| 7 | I've recently started playing with large language models (LLMs), mostly | |
| 8 | in the popular chatbot form, as part of my job and have decided to see | |
| 9 | if there's a consistent and reliable way to interact with these models | |
| 10 | on Apple devices without sacrificing privacy or requiring in-depth | |
| 11 | technical setup. | |
| 12 | ||
| 13 | My requirements for this test: | |
| 14 | ||
| 15 | - Open source platform | |
| 16 | - On-device model files | |
| 17 | - Minimal required configuration | |
| 18 | - Preferably pre-built, but a simple build process is acceptable | |
| 19 | ||
| 20 | I tested a handful of apps and have summarized my favorite (so far) for | |
| 21 | macOS and iOS below. | |
| 22 | ||
| 23 | #+begin_quote | |
| 24 | TL;DR - Here are the two that met my requirements and I have found the | |
| 25 | easiest to install and use so far: | |
| 26 | ||
| 27 | #+end_quote | |
| 28 | ||
| 29 | - macOS: [[https://ollama.ai/][Ollama]] | |
| 30 | - iOS : [[https://llmfarm.site/][LLM Farm]] | |
| 31 | ||
| 32 | * macOS | |
| 33 | [[https://ollama.ai/][Ollama]] is a simple Go application for macOS and | |
| 34 | Linux that can run various LLMs locally. | |
| 35 | ||
| 36 | For macOS, you can download the pplication on the | |
| 37 | [[https://ollama.ai/download/mac][Ollama download page]] and install it | |
| 38 | by unzipping the =Ollama.app= file and moving it to the =Applications= | |
| 39 | folder. | |
| 40 | ||
| 41 | If you prefer the command line, you can run these commands after the | |
| 42 | download finished: | |
| 43 | ||
| 44 | #+begin_src sh | |
| 45 | cd ~/Downloads && \ | |
| 46 | unzip Ollama-darwin.zip && \ | |
| 47 | mv ~/Downloads/Ollama.app /Applications/ | |
| 48 | #+end_src | |
| 49 | ||
| 50 | After running the app, the app will ask you to open a terminal and run | |
| 51 | the default =llama2= model, which will open an interactive chat session | |
| 52 | in the terminal. You can startfully using the application at this point. | |
| 53 | ||
| 54 | #+caption: Ollama | |
| 55 | [[https://img.cleberg.net/blog/20240113-local-llm/ollama.png]] | |
| 56 | ||
| 57 | If you don't want to use the default =llama2= model, you can download | |
| 58 | and run additional models found on the | |
| 59 | [[https://ollama.ai/library][Models]] page. | |
| 60 | ||
| 61 | To see the information for the currently-used model, you can run the | |
| 62 | =/show info= command in the chat. | |
| 63 | ||
| 64 | #+caption: Model Info | |
| 65 | [[https://img.cleberg.net/blog/20240113-local-llm/ollama_info.png]] | |
| 66 | ||
| 67 | ** Community Integrations | |
| 68 | I highly recommend browsing the | |
| 69 | [[https://github.com/jmorganca/ollama#community-integrations][Community | |
| 70 | Integrations]] section of the project to see how you would prefer to | |
| 71 | extend Ollama beyond a simple command-line interface. There are options | |
| 72 | for APIs, browser UIs, advanced terminal configurations, and more. | |
| 73 | ||
| 74 | #+caption: Ollama SwiftUI | |
| 75 | [[https://img.cleberg.net/blog/20240113-local-llm/ollama-swiftui.png]] | |
| 76 | ||
| 77 | * iOS | |
| 78 | While there are a handful of decent macOS options, it was quite | |
| 79 | difficult to find an iOS app that offered an open source platform | |
| 80 | without an extensive configuration and building process. I found LLM | |
| 81 | Farm to be decent enough in quality to sit at the top of my list - | |
| 82 | however, it's definitely not user friendly enough for me to consider | |
| 83 | using it on a daily basis. | |
| 84 | ||
| 85 | [[https://llmfarm.site/][LLM Farm]] is available on TestFlight, so | |
| 86 | there's no manual build process required. However, you can view the | |
| 87 | [[https://github.com/guinmoon/LLMFarm][LLMFarm repository]] if you wish. | |
| 88 | ||
| 89 | The caveat is that you will have to manually download the model files | |
| 90 | from the links in the | |
| 91 | [[https://github.com/guinmoon/LLMFarm/blob/main/models.md][models.md]] | |
| 92 | file to your iPhone to use the app - there's currently no option in the | |
| 93 | app to reach out and grab the latest version of any supported model. | |
| 94 | ||
| 95 | Once you have a file downloaded, you simply create a new chat and select | |
| 96 | the downloaded model file and ensure the inference matches the | |
| 97 | requirement in the =models.md= file. | |
| 98 | ||
| 99 | See below for a test of the ORCA Mini v3 model: | |
| 100 | ||
| 101 | | Chat List | Chat | | |
| 102 | |------------------------------------------------------------------------+------------------------------------------------------------------| | |
| 103 | | [[https://img.cleberg.net/blog/20240113-local-llm/llm_farm_chats.png]] | [[https://img.cleberg.net/blog/20240113-local-llm/llm_farm.png]] | | |
| 104 | ||
| 105 | [[https://github.com/AugustDev/enchanted][Enchanted]] is also an iOS for | |
| 106 | private AI models, but it requires a public-facing Ollama API, which did | |
| 107 | not meet my "on device requirement." Nonetheless, it's an interesting | |
| 108 | looking app and I will likely set it up to test soon. | |
blog/macos-customization/index.org added +170
| @@ -0,0 +1,170 @@ | ||
| 1 | #+title: Customizing macOS | |
| 2 | #+date: 2024-01-09 | |
| 3 | #+description: Learn how to customize macOS beyond the standard, built-in options provided by Apple. | |
| 4 | #+filetags: :apple: | |
| 5 | ||
| 6 | I have been using macOS more than Linux lately, so I wrote this post to | |
| 7 | describe some simple options to customize macOS beyond the normal | |
| 8 | built-in settings menu. | |
| 9 | ||
| 10 | While not all-encompassing, the options below should be a good start for | |
| 11 | anyone looking to dive down the rabbit hole. | |
| 12 | ||
| 13 | * Basics | |
| 14 | ** Package Management | |
| 15 | To install a lot of software on macOS, you will need | |
| 16 | [[https://brew.sh/][Homebrew]]. You can use their installation script to | |
| 17 | get started. Simply open the =Terminal= application and paste the | |
| 18 | following snippet: | |
| 19 | ||
| 20 | #+begin_src sh | |
| 21 | /bin/bash -c "$(curl -fsSL https://raw.githubusercontent.com/Homebrew/install/HEAD/install.sh)" | |
| 22 | #+end_src | |
| 23 | ||
| 24 | This will allow you to easily install and manage applications and other | |
| 25 | software easily through the =brew= command. | |
| 26 | ||
| 27 | ** Terminal | |
| 28 | If you're serious about customizing your macOS system, I highly | |
| 29 | recommend installing a terminal emulator that you like and if you're not | |
| 30 | comfortable on the command line yet, start learning. A lot of | |
| 31 | customization options require you to edit hidden files, which is easiest | |
| 32 | in a terminal. | |
| 33 | ||
| 34 | There are options like iTerm2, Kitty, Alacritty, Hyper, Warp, or the | |
| 35 | built-in Terminal app. | |
| 36 | ||
| 37 | I use [[https://iterm2.com/][iTerm2]], which can be installed with | |
| 38 | Homebrew: | |
| 39 | ||
| 40 | #+begin_src sh | |
| 41 | brew install iterm2 | |
| 42 | #+end_src | |
| 43 | ||
| 44 | #+caption: iTerm2 | |
| 45 | [[https://img.cleberg.net/blog/20240109-macos-customization/iterm2.png]] | |
| 46 | ||
| 47 | To install color schemes, such as the Dracula scheme shown in the | |
| 48 | screenshot above, you visit [[https://iterm2colorschemes.com/][iTerm | |
| 49 | Themes]] and follow their installation instructions to install any of | |
| 50 | the themes. | |
| 51 | ||
| 52 | * Desktop | |
| 53 | ** Window Management | |
| 54 | [[https://github.com/koekeishiya/yabai][yabai]] is a tiling window | |
| 55 | manager for macOS. While other window managers exist, I found that most | |
| 56 | of them struggled to create logical layouts and to allow me to easily | |
| 57 | move windows around the screen. | |
| 58 | ||
| 59 | Some advanced settings for yabai are only available if partially disable | |
| 60 | System Integrity Protection (SIP). However, I chose not to do this and | |
| 61 | it hasn't affected my basic usage of yabai at all. | |
| 62 | ||
| 63 | Refer to the | |
| 64 | [[https://github.com/koekeishiya/yabai/wiki/Installing-yabai-(latest-release)][yabai | |
| 65 | wiki]] for installation instructions. You will need to ensure that yabai | |
| 66 | is allowed to access the accessibility and screen recording APIs. | |
| 67 | ||
| 68 | You can see a basic three-pane layout atuomatically configured by yabai | |
| 69 | for me as I opened the windows below. | |
| 70 | ||
| 71 | #+caption: yabai window manager | |
| 72 | [[https://img.cleberg.net/blog/20240109-macos-customization/yabai.png]] | |
| 73 | ||
| 74 | ** Keyboard Shortcuts | |
| 75 | [[https://github.com/koekeishiya/skhd][skhd]] is a simple hotkey daemon | |
| 76 | that allows you to define hotkeys in a file for usage on your system. | |
| 77 | ||
| 78 | Installation is simple: | |
| 79 | ||
| 80 | #+begin_src sh | |
| 81 | brew install koekeishiya/formulae/skhd | |
| 82 | skhd --start-service | |
| 83 | #+end_src | |
| 84 | ||
| 85 | After installation, be sure to allow =skhd= access to the accessibility | |
| 86 | API in the macOS privacy settings. | |
| 87 | ||
| 88 | You can configure your hotkeys in the =~/.config/skhd/skhdrc= file: | |
| 89 | ||
| 90 | #+begin_src sh | |
| 91 | nano ~/.config/skhd/skhdrc | |
| 92 | #+end_src | |
| 93 | ||
| 94 | For example, I have hotkeys to open my browser and terminal: | |
| 95 | ||
| 96 | #+begin_src conf | |
| 97 | # Terminal | |
| 98 | cmd - return : /Applications/iTerm.app/Contents/MacOS/iTerm2 | |
| 99 | ||
| 100 | # Browser | |
| 101 | cmd + shift - return : /Applications/LibreWolf.app/Contents/MacOS/librewolf | |
| 102 | #+end_src | |
| 103 | ||
| 104 | ** Widgets | |
| 105 | [[https://github.com/felixhageloh/uebersicht/][uebersicht]] is a handy | |
| 106 | desktop-based widget tool with a plethora of community-made widgets | |
| 107 | available in the [[https://tracesof.net/uebersicht-widgets/][widgets | |
| 108 | gallery]]. You can also write your own widgets with this tool. | |
| 109 | ||
| 110 | To install, simply download the latest release from the | |
| 111 | [[https://tracesof.net/uebersicht/][uebersicht website]] and copy it to | |
| 112 | the Applications folder. | |
| 113 | ||
| 114 | See below for an example of the | |
| 115 | [[https://tracesof.net/uebersicht-widgets/#Mond][Mond]] widget in | |
| 116 | action. | |
| 117 | ||
| 118 | #+caption: uebersicht desktop widgets | |
| 119 | [[https://img.cleberg.net/blog/20240109-macos-customization/uebersicht.png]] | |
| 120 | ||
| 121 | ** Status Bar | |
| 122 | [[https://github.com/FelixKratz/SketchyBar][SketchyBar]] is a | |
| 123 | customizable replacement for the macOS status or menu bar. | |
| 124 | ||
| 125 | You can browse a discussion where various users shared their | |
| 126 | [[https://github.com/FelixKratz/SketchyBar/discussions/47?sort=top][configurations]] | |
| 127 | for inspiration or to copy their dotfiles. | |
| 128 | ||
| 129 | See below for a quick (& slightly broken) copy of | |
| 130 | [[https://github.com/zer0yu/dotfiles][zer0yu's]] SketchyBar | |
| 131 | configuration. | |
| 132 | ||
| 133 | #+caption: SketchyBar | |
| 134 | [[https://img.cleberg.net/blog/20240109-macos-customization/sketchybar.png]] | |
| 135 | ||
| 136 | ** Dock | |
| 137 | The easiest way to customize the dock is to install | |
| 138 | [[https://ubarapp.com/][uBar]], which uses a Windows-like menu bar as | |
| 139 | the default style. | |
| 140 | ||
| 141 | However, the built-in macOS dock cannot be disabled and can only be set | |
| 142 | to "always hidden". This can be annoying as it will pop out any time | |
| 143 | your mouse cursor passes closely to the dock edge of the screen. Because | |
| 144 | of this, I simply use the built-in dock instead of customizing it with | |
| 145 | third-party software. | |
| 146 | ||
| 147 | Regardless, see below for the default installation style of uBar. | |
| 148 | ||
| 149 | #+caption: uBar | |
| 150 | [[https://img.cleberg.net/blog/20240109-macos-customization/ubar.png]] | |
| 151 | ||
| 152 | ** Application Icons | |
| 153 | You can also customize the icon of any application in macOS, which will | |
| 154 | show up in Finder, the Dock, Launchpad, search results, etc. I recommend | |
| 155 | using [[https://macosicons.com/][macOSicons]] to download icons you | |
| 156 | want, and then apply them by following this process. | |
| 157 | ||
| 158 | 1. Open the Finder application. | |
| 159 | 2. Navigate to the =Applications= folder. | |
| 160 | 3. Right-click an application of your choice, and select =Get Info=. | |
| 161 | 4. Drag the image you downloaded on top of the application's icon at the | |
| 162 | top of information window (you will see a green "plus" symbol when | |
| 163 | you're hovering over it). | |
| 164 | 5. Release the new icon on top of the old icon and it will update! | |
| 165 | ||
| 166 | You can see an example of me dragging a new =signal.icns= file onto my | |
| 167 | Signal.app information window to update it below: | |
| 168 | ||
| 169 | #+caption: replace macOS icons | |
| 170 | [[https://img.cleberg.net/blog/20240109-macos-customization/replace_icon.png]] | |
content/blog/2021-02-19-macos.md → blog/macos/index.org renamed +83 −97
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-02-19 | |
| 3 | title = "macOS: Testing Out A New OS" | |
| 4 | description = "A retrospective on my migration from Linux to macOS." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Diving into macOS | |
| 1 | #+title: macOS: Testing Out A New OS | |
| 2 | #+date: 2021-02-19 | |
| 3 | #+description: A retrospective on my migration from Linux to macOS. | |
| 4 | #+filetags: :apple: | |
| 8 | 5 | |
| 6 | * Diving into macOS | |
| 9 | 7 | After spending nearly 15 years working with Windows and 8 years on |
| 10 | 8 | Linux, I have experienced macOS for the first time. By chance, my spouse |
| 11 | 9 | happened to buy a new MacBook and gifted me their 2013 model. Of course, |
| @@ -14,22 +12,21 @@ around for gaming needs, but over the past week I've found myself using | ||
| 14 | 12 | the MacBook more and more for things that don't require gaming specs or |
| 15 | 13 | advanced dev tools. |
| 16 | 14 | |
| 17 | ## Initial Thoughts | |
| 18 | ||
| 15 | * Initial Thoughts | |
| 19 | 16 | Before I move on to the technical aspects of my set-up, I want to take |
| 20 | 17 | some time and express my thoughts on the overall OS. |
| 21 | 18 | |
| 22 |  | |
| 19 | #+caption: macOS Desktop | |
| 20 | [[https://img.cleberg.net/blog/20210219-macos-testing-out-a-new-os/macos-desktop.png]] | |
| 24 | 21 | |
| 25 | 22 | As expected, the initial computer setup is a breeze with Mac's guided |
| 26 | 23 | GUI installer. |
| 27 | 24 | |
| 28 | 25 | The desktop itself reminds me of GNOME more than anything else I've |
| 29 | seen: even Pantheon from [ElementaryOS](https://elementary.io/), which | |
| 26 | seen: even Pantheon from [[https://elementary.io/][ElementaryOS]], which | |
| 30 | 27 | people commonly refer to as the closest Linux distro to macOS. The |
| 31 | 28 | desktop toolbar is great and far surpasses the utility of the GNOME |
| 32 | toolbar due to the fact that the extensions and icons *actually work*. I | |
| 29 | toolbar due to the fact that the extensions and icons /actually work/. I | |
| 33 | 30 | launch macOS and immediately see my shortcuts for Tresorit, Bitwarden, |
| 34 | 31 | and Mullvad pop up as the computer loads. |
| 35 | 32 | |
| @@ -41,7 +38,7 @@ can't stand items taking up precious screen space if I'm not currently | ||
| 41 | 38 | using them. On that same note, it's taking me some time to get use to |
| 42 | 39 | the fact that I have to manually quit an app or else it will still stay |
| 43 | 40 | open/active in the dock, even if I've closed out all windows for that |
| 44 | app (e.g. Firefox). | |
| 41 | app (e.g. Firefox). | |
| 45 | 42 | |
| 46 | 43 | Overall, I'm having a lot of fun and for users who spend a large |
| 47 | 44 | majority of their time performing basic tasks like web browsing, |
| @@ -51,8 +48,7 @@ The rest of this post explains the technicalities of how I set up my CLI | ||
| 51 | 48 | environment to make me feel more at-home, similar to the environments I |
| 52 | 49 | set up on Fedora, Ubuntu, etc. |
| 53 | 50 | |
| 54 | ## Making it Feel Like Home | |
| 55 | ||
| 51 | * Making it Feel Like Home | |
| 56 | 52 | If you're someone who uses Linux primarily, no doubt your first thought |
| 57 | 53 | when booting macOS will be the same as mine was: "Where is the terminal |
| 58 | 54 | and how do I set up my favorite utilities?" |
| @@ -60,155 +56,145 @@ and how do I set up my favorite utilities?" | ||
| 60 | 56 | Luckily, macOS hasn't completely hidden away the development tools from |
| 61 | 57 | the average user. You can easily find the Terminal app in the Launchpad |
| 62 | 58 | area, but it's probably not what you're used to. I was surprised (and |
| 63 | happy) to see that the default shell is `zsh`, the shell I | |
| 64 | use on all of my Linux distros. However, the commands are not the same - | |
| 65 | even the ones you may think are native to the shell. Commands like | |
| 66 | `dir` do not exist, so other native commands like | |
| 67 | `ls -la` or `pwd` are more useful here. | |
| 59 | happy) to see that the default shell is =zsh=, the shell I use on all of | |
| 60 | my Linux distros. However, the commands are not the same - even the ones | |
| 61 | you may think are native to the shell. Commands like =dir= do not exist, | |
| 62 | so other native commands like =ls -la= or =pwd= are more useful here. | |
| 68 | 63 | |
| 69 | 64 | With only a few minutes of installing and tweaking a few packages, I was |
| 70 | 65 | able to recreate a terminal environment that I feel very comfortable |
| 71 | 66 | using. See the image below for a preview of the iTerm2 app with a split |
| 72 | 67 | view between my macOS desktop shell and an SSH session into my server. |
| 73 | 68 | |
| 74 |  | |
| 75 | ||
| 76 | ## Xcode | |
| 69 | #+caption: iTerm2 | |
| 70 | [[https://img.cleberg.net/blog/20210219-macos-testing-out-a-new-os/iterm2.png]] | |
| 77 | 71 | |
| 78 | My first step was to search the web for any hints on how to get | |
| 79 | `zsh` back up to the state I like, with extensions, themes, | |
| 80 | etc. My first step was to install the CLI tools for | |
| 81 | [Xcode](https://developer.apple.com/xcode/), Apple's suite of | |
| 72 | * Xcode | |
| 73 | My first step was to search the web for any hints on how to get =zsh= | |
| 74 | back up to the state I like, with extensions, themes, etc. My first step | |
| 75 | was to install the CLI tools for | |
| 76 | [[https://developer.apple.com/xcode/][Xcode]], Apple's suite of | |
| 82 | 77 | development tools. |
| 83 | 78 | |
| 84 | ```sh | |
| 79 | #+begin_src sh | |
| 85 | 80 | sudo xcode-select -r |
| 86 | ``` | |
| 81 | #+end_src | |
| 87 | 82 | |
| 88 | ```sh | |
| 83 | #+begin_src sh | |
| 89 | 84 | sudo xcode-select --install |
| 90 | ``` | |
| 85 | #+end_src | |
| 91 | 86 | |
| 92 | ## Homebrew | |
| 93 | ||
| 94 | Next up is to install [Homebrew](https://brew.sh), a nifty package | |
| 87 | * Homebrew | |
| 88 | Next up is to install [[https://brew.sh][Homebrew]], a nifty package | |
| 95 | 89 | manager for macOS. |
| 96 | 90 | |
| 97 | ```sh | |
| 91 | #+begin_src sh | |
| 98 | 92 | /bin/bash -c "$(curl -fsSL https://raw.githubusercontent.com/Homebrew/install/HEAD/install.sh)" |
| 99 | ``` | |
| 93 | #+end_src | |
| 100 | 94 | |
| 101 | 95 | I ran into a permission error when installing Homebrew: |
| 102 | 96 | |
| 103 | ```sh | |
| 97 | #+begin_src sh | |
| 104 | 98 | Error: Failed to link all completions, docs and manpages: |
| 105 | 99 | Permission denied @ rb_file_s_symlink - (../../../Homebrew/completions/zsh/_brew, /usr/local/share/zsh/site-functions/_brew) |
| 106 | 100 | Failed during: /usr/local/bin/brew update --force --quiet |
| 107 | ``` | |
| 101 | #+end_src | |
| 108 | 102 | |
| 109 | 103 | I found that the following permission modification worked like a charm. |
| 110 | 104 | However, I noted that some users online discussed the fact that this |
| 111 | 105 | solution may not work if your system has multiple users who use |
| 112 | 106 | Homebrew. |
| 113 | 107 | |
| 114 | ```sh | |
| 108 | #+begin_src sh | |
| 115 | 109 | sudo chown -R $(whoami) $(brew --prefix)/* |
| 116 | ``` | |
| 110 | #+end_src | |
| 117 | 111 | |
| 118 | 112 | Next up is to ensure Homebrew is updated and cleaned. |
| 119 | 113 | |
| 120 | ```sh | |
| 114 | #+begin_src sh | |
| 121 | 115 | brew update |
| 122 | ``` | |
| 116 | #+end_src | |
| 123 | 117 | |
| 124 | ```sh | |
| 118 | #+begin_src sh | |
| 125 | 119 | brew cleanup |
| 126 | ``` | |
| 127 | ||
| 128 | ## iTerm2 | |
| 120 | #+end_src | |
| 129 | 121 | |
| 122 | * iTerm2 | |
| 130 | 123 | Now that I've installed the basic utilities for development, I moved |
| 131 | 124 | onto installing iTerm2, a much better terminal than the default. |
| 132 | 125 | |
| 133 | ```sh | |
| 126 | #+begin_src sh | |
| 134 | 127 | brew install --cask iterm2 |
| 135 | ``` | |
| 128 | #+end_src | |
| 136 | 129 | |
| 137 | I also used the `Make iTerm2 Default Term` and | |
| 138 | `Install Shell Integration` options in the iTerm2 application | |
| 139 | menu to make sure I don't run into any issues later on with different | |
| 140 | terminals. | |
| 130 | I also used the =Make iTerm2 Default Term= and | |
| 131 | =Install Shell Integration= options in the iTerm2 application menu to | |
| 132 | make sure I don't run into any issues later on with different terminals. | |
| 141 | 133 | |
| 142 | We will also install `zsh` so we can use it in iTerm2. | |
| 134 | We will also install =zsh= so we can use it in iTerm2. | |
| 143 | 135 | |
| 144 | ```sh | |
| 136 | #+begin_src sh | |
| 145 | 137 | brew install zsh |
| 146 | ``` | |
| 147 | ||
| 148 | ## Oh-My-Zsh | |
| 138 | #+end_src | |
| 149 | 139 | |
| 150 | I've shown the great aspects of [Oh My Zsh](https://ohmyz.sh) in other | |
| 151 | blog posts, so I'll skip over that speech for now. Simply install it | |
| 152 | and run an update. | |
| 140 | * Oh-My-Zsh | |
| 141 | I've shown the great aspects of [[https://ohmyz.sh][Oh My Zsh]] in other | |
| 142 | blog posts, so I'll skip over that speech for now. Simply install it and | |
| 143 | run an update. | |
| 153 | 144 | |
| 154 | ```sh | |
| 145 | #+begin_src sh | |
| 155 | 146 | sh -c "$(curl -fsSL https://raw.githubusercontent.com/robbyrussell/oh-my-zsh/master/tools/install.sh)" |
| 156 | ``` | |
| 147 | #+end_src | |
| 157 | 148 | |
| 158 | ```sh | |
| 149 | #+begin_src sh | |
| 159 | 150 | omz update |
| 160 | ``` | |
| 151 | #+end_src | |
| 161 | 152 | |
| 162 | 153 | Finally, restart the iTerm2 application to ensure all changes go into |
| 163 | 154 | effect. |
| 164 | 155 | |
| 165 | ## Oh-My-Zsh Themes | |
| 166 | ||
| 156 | * Oh-My-Zsh Themes | |
| 167 | 157 | Let's change the theme of the terminal to make it a little more |
| 168 | 158 | friendly. |
| 169 | 159 | |
| 170 | ```sh | |
| 160 | #+begin_src sh | |
| 171 | 161 | open ~/.zshrc |
| 172 | ``` | |
| 162 | #+end_src | |
| 173 | 163 | |
| 174 | 164 | The third section of this file should contain a line like the code |
| 175 | below. Change that theme to [any theme you | |
| 176 | want](https://github.com/ohmyzsh/ohmyzsh/wiki/Themes), save the file, | |
| 177 | and exit. | |
| 165 | below. Change that theme to | |
| 166 | [[https://github.com/ohmyzsh/ohmyzsh/wiki/Themes][any theme you want]], | |
| 167 | save the file, and exit. | |
| 178 | 168 | |
| 179 | ```sh | |
| 169 | #+begin_src sh | |
| 180 | 170 | ZSH_THEME="af-magic" |
| 181 | ``` | |
| 182 | ||
| 183 | After changing the `.zshrc` file, you'll need to close your | |
| 184 | terminal and re-open it to see the changes. Optionally, just open a new | |
| 185 | tab if you're using iTerm2, and you'll see the new shell config. | |
| 171 | #+end_src | |
| 186 | 172 | |
| 187 | ## Oh-My-Zsh Plugins | |
| 173 | After changing the =.zshrc= file, you'll need to close your terminal and | |
| 174 | re-open it to see the changes. Optionally, just open a new tab if you're | |
| 175 | using iTerm2, and you'll see the new shell config. | |
| 188 | 176 | |
| 189 | Of course, my customization of `zsh` would not be complete | |
| 190 | without | |
| 191 | [zsh-autosuggestions](https://github.com/zsh-users/zsh-autosuggestions). | |
| 192 | This will bring up commands you've run in the past as you type them. | |
| 193 | For example, if you've run `ssh user@192.168.1.99` before, | |
| 194 | the terminal will show this command as soon as you start typing it | |
| 195 | (e.g. =zsh u=), and you can hit the right arrow to autocomplete the | |
| 196 | command. | |
| 177 | * Oh-My-Zsh Plugins | |
| 178 | Of course, my customization of =zsh= would not be complete without | |
| 179 | [[https://github.com/zsh-users/zsh-autosuggestions][zsh-autosuggestions]]. | |
| 180 | This will bring up commands you've run in the past as you type them. For | |
| 181 | example, if you've run =ssh user@192.168.1.99= before, the terminal will | |
| 182 | show this command as soon as you start typing it (e.g. =zsh u=), and you | |
| 183 | can hit the right arrow to autocomplete the command. | |
| 197 | 184 | |
| 198 | ```sh | |
| 185 | #+begin_src sh | |
| 199 | 186 | git clone https://github.com/zsh-users/zsh-autosuggestions ${ZSH_CUSTOM:-~/.oh-my-zsh/custom}/plugins/zsh-autosuggestions |
| 200 | ``` | |
| 187 | #+end_src | |
| 201 | 188 | |
| 202 | ```sh | |
| 189 | #+begin_src sh | |
| 203 | 190 | open ~/.zshrc |
| 204 | ``` | |
| 191 | #+end_src | |
| 205 | 192 | |
| 206 | ```sh | |
| 193 | #+begin_src sh | |
| 207 | 194 | # Scroll down the script and edit this line to add zsh-autosuggestions |
| 208 | 195 | plugins=(git zsh-autosuggestions) |
| 209 | ``` | |
| 196 | #+end_src | |
| 210 | 197 | |
| 211 | Remember: After changing the `.zshrc` file, you'll need to | |
| 212 | close your terminal and re-open it to see the changes. Optionally, just | |
| 213 | open a new tab if you're using iTerm2, and you'll see the new shell | |
| 214 | config. | |
| 198 | Remember: After changing the =.zshrc= file, you'll need to close your | |
| 199 | terminal and re-open it to see the changes. Optionally, just open a new | |
| 200 | tab if you're using iTerm2, and you'll see the new shell config. | |
content/blog/2023-01-05-mass-unlike-tumblr-posts.md → blog/mass-unlike-tumblr-posts/index.org renamed +34 −41
| @@ -1,18 +1,15 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-01-05 | |
| 3 | title = "How to Easily Mass Unlike Tumblr Posts with Javascript" | |
| 4 | description = "Learn how to unlike Tumblr posts en masse in the browser." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## The Dilemma | |
| 1 | #+title: How to Easily Mass Unlike Tumblr Posts with Javascript | |
| 2 | #+date: 2023-01-05 | |
| 3 | #+description: Learn how to unlike Tumblr posts en masse in the browser. | |
| 4 | #+filetags: :dev: | |
| 8 | 5 | |
| 6 | * The Dilemma | |
| 9 | 7 | The dilemma I had was pretty simple: I wanted to unlike all the posts I |
| 10 | 8 | have liked on Tumblr so that I could follow a new focus on blogs and |
| 11 | 9 | start fresh. Otherwise, Tumblr will keep recommending content based on |
| 12 | 10 | your previous likes. |
| 13 | 11 | |
| 14 | ## The Solution | |
| 15 | ||
| 12 | * The Solution | |
| 16 | 13 | I searched the web for a while and noted that most solutions referenced |
| 17 | 14 | Tumblr setting and dashboard pages that no longer exist. Additionally, I |
| 18 | 15 | did not want to install a third party extension to do this, as some |
| @@ -22,13 +19,12 @@ Luckily, I used Javascript for a while a few years ago and figured it | ||
| 22 | 19 | would be easy enough to script a solution, as long as Tumblr had a |
| 23 | 20 | system for the unlike buttons. |
| 24 | 21 | |
| 25 | ### Identifying Unlike Buttons | |
| 26 | ||
| 22 | ** Identifying Unlike Buttons | |
| 27 | 23 | Tumblr's unlike buttons are structured as you can see in the following |
| 28 | code block. All unlike buttons have an `aria-label` with a | |
| 29 | value of `Unlike`. | |
| 24 | code block. All unlike buttons have an =aria-label= with a value of | |
| 25 | =Unlike=. | |
| 30 | 26 | |
| 31 | ```html | |
| 27 | #+begin_src html | |
| 32 | 28 | <button class="TRX6J" aria-label="Unlike"> |
| 33 | 29 | <span class="EvhBA B1Z5w ztpfZ" tabindex="-1"> |
| 34 | 30 | <svg xmlns="http://www.w3.org/2000/svg" height="21" width="23" |
| @@ -37,56 +33,53 @@ value of `Unlike`. | ||
| 37 | 33 | </svg> |
| 38 | 34 | </span> |
| 39 | 35 | </button> |
| 40 | ``` | |
| 36 | #+end_src | |
| 41 | 37 | |
| 42 | ### Running a Script to Unlike All Likes | |
| 43 | ||
| 44 | To run this script, you will need to load the [Likes \| | |
| 45 | Tumblr](https://www.tumblr.com/likes) page while logged in to your | |
| 46 | account. | |
| 38 | ** Running a Script to Unlike All Likes | |
| 39 | To run this script, you will need to load the | |
| 40 | [[https://www.tumblr.com/likes][Likes | Tumblr]] page while logged in to | |
| 41 | your account. | |
| 47 | 42 | |
| 48 | 43 | Further, be sure to scroll down to the bottom and force Tumblr to load |
| 49 | 44 | more posts so that this script unlikes more posts at a time. |
| 50 | 45 | |
| 51 | 46 | Once you are logged in and the page is loaded, open the Developer Tools |
| 52 | and be sure you're on the "Console" tab. It should look something | |
| 53 | like this (this is in Firefox, Chromium should be similar): | |
| 47 | and be sure you're on the "Console" tab. It should look something like | |
| 48 | this (this is in Firefox, Chromium should be similar): | |
| 54 | 49 | |
| 55 |  | |
| 50 | #+caption: Firefox Dev !Tools | |
| 51 | [[https:///img.cleberg.net/blog/20230105-mass-unlike-tumblr-posts/dev_console.png]] | |
| 57 | 52 | |
| 58 | 53 | All you need to do is paste the following snippet into the dev console. |
| 59 | This code will collect all unlike buttons (`elements`) and | |
| 60 | then click each button to unlike it. | |
| 54 | This code will collect all unlike buttons (=elements=) and then click | |
| 55 | each button to unlike it. | |
| 61 | 56 | |
| 62 | Optionally, you can comment-out the line | |
| 63 | `elements[i].click();` and uncomment the | |
| 64 | `console.log()` lines to simply print out information without | |
| 65 | performing any actions. This can be useful to debug issues or confirm | |
| 66 | that the code below isn't doing anything you don't want it to. | |
| 57 | Optionally, you can comment-out the line =elements[i].click();= and | |
| 58 | uncomment the =console.log()= lines to simply print out information | |
| 59 | without performing any actions. This can be useful to debug issues or | |
| 60 | confirm that the code below isn't doing anything you don't want it to. | |
| 67 | 61 | |
| 68 | ```javascript | |
| 62 | #+begin_src javascript | |
| 69 | 63 | const elements = document.querySelectorAll('[aria-label="Unlike"]'); |
| 70 | 64 | // console.log(elements); // 👉 [button] |
| 71 | ||
| 65 | ||
| 72 | 66 | for (let i=0; i < elements.length; i++) { |
| 73 | 67 | // console.log(elements[i]); |
| 74 | 68 | elements[i].click(); |
| 75 | 69 | } |
| 76 | ``` | |
| 77 | ||
| 78 | ## Results | |
| 70 | #+end_src | |
| 79 | 71 | |
| 80 | The results were quick for my situation, as it unliked \~200 posts | |
| 81 | within 2-3 seconds. I am not sure how this will perform on larger sets | |
| 82 | of likes (or if Tumblr has a limit to unliking posts). | |
| 72 | * Results | |
| 73 | The results were quick for my situation, as it unliked ~200 posts within | |
| 74 | 2-3 seconds. I am not sure how this will perform on larger sets of likes | |
| 75 | (or if Tumblr has a limit to unliking posts). | |
| 83 | 76 | |
| 84 | 77 | You can see the below screenshot showing that I pasted the snippet into |
| 85 | 78 | the console, pressed Enter, and then the posts are automatically |
| 86 | 79 | unliked. |
| 87 | 80 | |
| 88 |  | |
| 81 | #+caption: Script !Results | |
| 82 | [[https:///img.cleberg.net/blog/20230105-mass-unlike-tumblr-posts/script_results.png]] | |
| 90 | 83 | |
| 91 | 84 | Thinking about this further, I would bet that this would be fairly |
| 92 | 85 | simple to package into a browser add-on so that users could install the |
content/blog/2020-10-12-mediocrity.md → blog/mediocrity/index.org renamed +47 −45
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-10-12 | |
| 3 | title = "On the Pursuit of Mediocrity" | |
| 4 | description = "Musings on mediocrity." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Perfect is the Enemy of Good | |
| 1 | #+title: On the Pursuit of Mediocrity | |
| 2 | #+date: 2020-10-12 | |
| 3 | #+description: Musings on mediocrity. | |
| 4 | #+filetags: :personal: | |
| 8 | 5 | |
| 6 | * Perfect is the Enemy of Good | |
| 9 | 7 | As the saying goes, "the best is the enemy of the good." As we strive |
| 10 | 8 | for perfection, we often fail to realize the implications of such an |
| 11 | 9 | undertaking. Attempting to reach perfection is often unrealistic. Even |
| @@ -15,36 +13,37 @@ burned the bridges that would have allowed us to reach a lesser yet | ||
| 15 | 13 | still superb solution. |
| 16 | 14 | |
| 17 | 15 | Philosophers throughout history have inspected this plight from many |
| 18 | viewpoints. Greek mythology speaks of the [golden | |
| 19 | mean](https://en.wikipedia.org/wiki/Golden_mean_(philosophy)), which | |
| 20 | uses the story of Icarus to illustrate that sometimes "the middle | |
| 16 | viewpoints. Greek mythology speaks of the | |
| 17 | [[https://en.wikipedia.org/wiki/Golden_mean_(philosophy)][golden mean]], | |
| 18 | which uses the story of Icarus to illustrate that sometimes "the middle | |
| 21 | 19 | course" is the best solution. In this story, Daedalus, a famous artist |
| 22 | 20 | of his time, built feathered wings for himself and his son so that they |
| 23 | 21 | might escape the clutches of King Minos. Daedalus warns his beloved son |
| 24 | whom he loved so much to "fly the middle course", between the sea | |
| 25 | spray and the sun's heat. Icarus did not heed his father; he flew up | |
| 26 | and up until the sun melted the wax off his wings. For not heeding the | |
| 27 | middle course, he fell into the sea and drowned. | |
| 28 | ||
| 29 | More recently, management scholars have explored the [Pareto | |
| 30 | principle](https://en.wikipedia.org/wiki/Pareto_principle) and found | |
| 31 | that as we increase the frequency of something, or strive to perform | |
| 32 | actions to achieve some form of perfection, we run into [diminishing | |
| 33 | returns](https://en.wikipedia.org/wiki/Diminishing_returns). | |
| 34 | ||
| 35 | Even further, Harold Demsetz is noted as coining the term [the Nirvana | |
| 36 | fallacy](https://en.wikipedia.org/wiki/Nirvana_fallacy) in 1969, which | |
| 37 | shows the fallacy of comparing actual things with unrealistic, idealized | |
| 38 | alternatives. This is another trap that we may fall into, where we are | |
| 39 | constantly thinking of the ultimate solutions to problems, when | |
| 40 | something more realistic needs to be considered. | |
| 22 | whom he loved so much to "fly the middle course", between the sea spray | |
| 23 | and the sun's heat. Icarus did not heed his father; he flew up and up | |
| 24 | until the sun melted the wax off his wings. For not heeding the middle | |
| 25 | course, he fell into the sea and drowned. | |
| 26 | ||
| 27 | More recently, management scholars have explored the | |
| 28 | [[https://en.wikipedia.org/wiki/Pareto_principle][Pareto principle]] and | |
| 29 | found that as we increase the frequency of something, or strive to | |
| 30 | perform actions to achieve some form of perfection, we run into | |
| 31 | [[https://en.wikipedia.org/wiki/Diminishing_returns][diminishing | |
| 32 | returns]]. | |
| 33 | ||
| 34 | Even further, Harold Demsetz is noted as coining the term | |
| 35 | [[https://en.wikipedia.org/wiki/Nirvana_fallacy][the Nirvana fallacy]] | |
| 36 | in 1969, which shows the fallacy of comparing actual things with | |
| 37 | unrealistic, idealized alternatives. This is another trap that we may | |
| 38 | fall into, where we are constantly thinking of the ultimate solutions to | |
| 39 | problems, when something more realistic needs to be considered. | |
| 41 | 40 | |
| 42 | 41 | Over and over throughout history, we've found that perfection is often |
| 43 | 42 | unrealistic and unachievable. However, we push ourselves and our peers |
| 44 | to "give 100%" or "go the extra mile," while it may be that the | |
| 45 | better course is to give a valuable level of effort while considering | |
| 46 | the effects of further effort on the outcome. Working harder does not | |
| 47 | always help us achieve loftier goals. | |
| 43 | to "give 100%" or "go the extra mile," while it may be that the better | |
| 44 | course is to give a valuable level of effort while considering the | |
| 45 | effects of further effort on the outcome. Working harder does not always | |
| 46 | help us achieve loftier goals. | |
| 48 | 47 | |
| 49 | 48 | This has presented itself to me most recently during my time studying at |
| 50 | 49 | my university. I was anxious and feeling the stresses of my courses, |
| @@ -53,8 +52,10 @@ how well I was doing at school and my level of effort at work. One day, | ||
| 53 | 52 | I happened to be talking to my father when he said something simple that |
| 54 | 53 | hit home: |
| 55 | 54 | |
| 56 | > All you can do is show up and do your best. Worrying about the | |
| 57 | > outcomes won't affect the outcome itself. | |
| 55 | #+begin_quote | |
| 56 | All you can do is show up and do your best. Worrying about the outcomes | |
| 57 | won't affect the outcome itself. | |
| 58 | #+end_quote | |
| 58 | 59 | |
| 59 | 60 | The thought was extremely straightforward and uncomplicated, yet it was |
| 60 | 61 | something that I had lost sight of during my stress-filled years at |
| @@ -63,8 +64,7 @@ quote every time I get anxious or stressed. It helps to stop and think | ||
| 63 | 64 | "Can I do anything to affect the outcome, or am I simply worrying over |
| 64 | 65 | something I can't change?" |
| 65 | 66 | |
| 66 | # When Mediocrity Isn't Enough | |
| 67 | ||
| 67 | * When Mediocrity Isn't Enough | |
| 68 | 68 | One problem with the philosophies presented in this post is that they |
| 69 | 69 | are implemented far too often in situations where mediocrity simply |
| 70 | 70 | isn't adequate. For example, let's take a look at digital user data, |
| @@ -73,21 +73,23 @@ cybersecurity auditor in the United States, I have found that most | ||
| 73 | 73 | companies are concerned more with compliance than any actual safeguards |
| 74 | 74 | over the privacy or protection of user data. Other than companies who |
| 75 | 75 | have built their reputation on privacy and security, most companies will |
| 76 | use [satisficing](https://en.wikipedia.org/wiki/Satisficing) as their | |
| 76 | use [[https://en.wikipedia.org/wiki/Satisficing][satisficing]] as their | |
| 77 | 77 | primary decision-making strategy around user data. |
| 78 | 78 | |
| 79 | > Satisficing is a decision-making strategy or cognitive heuristic that | |
| 80 | > entails searching through the available alternatives until an | |
| 81 | > acceptability threshold is met. | |
| 79 | #+begin_quote | |
| 80 | Satisficing is a decision-making strategy or cognitive heuristic that | |
| 81 | entails searching through the available alternatives until an | |
| 82 | acceptability threshold is met. | |
| 83 | #+end_quote | |
| 82 | 84 | |
| 83 | 85 | This means that each decision will be met with certain possible |
| 84 | 86 | solutions until one of the solutions meets their minimum acceptable |
| 85 | 87 | standards. For companies that deal with user data, the |
| 86 | 88 | minimum-acceptable standards come from three areas: |
| 87 | 89 | |
| 88 | 1. Laws and regulations | |
| 89 | 2. Competitive pressure | |
| 90 | 3. Risk of monetary or reputation loss | |
| 90 | 1. Laws and regulations | |
| 91 | 2. Competitive pressure | |
| 92 | 3. Risk of monetary or reputation loss | |
| 91 | 93 | |
| 92 | 94 | Working with project management or auditing, the primary concern here is |
| 93 | 95 | the risk of legal ramifications. Since the primary risk comes from laws |
| @@ -110,9 +112,9 @@ measure of how well a company or manager is performing, so we often | ||
| 110 | 112 | don't think about our responsibilities beyond these basic standards. |
| 111 | 113 | |
| 112 | 114 | Not all situations demand excellence, but I believe that applying any |
| 113 | philosophy as a broad stroke across one's life can be a mistake. We | |
| 114 | must be able to think critically about what we are doing as we do it and | |
| 115 | ask ourselves a few questions. Have I done everything I can in this | |
| 115 | philosophy as a broad stroke across one's life can be a mistake. We must | |
| 116 | be able to think critically about what we are doing as we do it and ask | |
| 117 | ourselves a few questions. Have I done everything I can in this | |
| 116 | 118 | situation? Is mediocrity an acceptable outcome, or should we strive for |
| 117 | 119 | perfection, even if we can't attain it? |
| 118 | 120 | |
content/blog/2022-10-04-mtp-linux.md → blog/mtp-linux/index.org renamed +28 −35
| @@ -1,16 +1,14 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-10-04 | |
| 3 | title = "How to Mount an MTP Mobile Device on Fedora Linux" | |
| 4 | description = "Learn how to mount an MTP mobile device on Fedora Linux." | |
| 5 | +++ | |
| 1 | #+title: How to Mount an MTP Mobile Device on Fedora Linux | |
| 2 | #+date: 2022-10-04 | |
| 3 | #+description: Learn how to mount an MTP mobile device on Fedora Linux. | |
| 4 | #+filetags: :linux: | |
| 6 | 5 | |
| 7 | 6 | I recently ran into trouble attempting to mount my GrapheneOS phone to |
| 8 | my laptop running Fedora Linux via the [Media Transfer | |
| 9 | Protocol](https://en.wikipedia.org/wiki/Media_transfer_protocol) (MTP) | |
| 10 | and discovered a simple and effective solution. | |
| 11 | ||
| 12 | ## Use a USB 3.0 Port | |
| 7 | my laptop running Fedora Linux via the | |
| 8 | [[https://en.wikipedia.org/wiki/Media_transfer_protocol][Media Transfer | |
| 9 | Protocol]] (MTP) and discovered a simple and effective solution. | |
| 13 | 10 | |
| 11 | * Use a USB 3.0 Port | |
| 14 | 12 | First, ensure that the device was plugged in to the laptop through a USB |
| 15 | 13 | 3.0 port, if possible. From a brief glance online, it seems that USB 2.0 |
| 16 | 14 | ports may cause issues with dropped connections over MTP. This is purely |
| @@ -18,63 +16,58 @@ anecdotal since I don't have any evidence to link showing that USB 2.0 | ||
| 18 | 16 | causes issues, but I can confirm that switching to a USB 3.0 port seemed |
| 19 | 17 | to cut out most of my issues. |
| 20 | 18 | |
| 21 | ## Switch USB Preferences to MTP | |
| 22 | ||
| 19 | * Switch USB Preferences to MTP | |
| 23 | 20 | Secondly, you need to ensure that the phone's USB preferences/mode is |
| 24 | 21 | changed to MTP or File Transfer once the phone is plugged in. Other |
| 25 | 22 | modes will not allow you to access the phone's file system. |
| 26 | 23 | |
| 27 | ## Install `jmtpfs` | |
| 28 | ||
| 29 | Next, I used the `jmtpfs` package to mount my phone to my | |
| 30 | laptop. There are other packages that exist, but this one worked | |
| 31 | perfectly for me. On Fedora Linux, you can install it like this: | |
| 24 | * Install =jmtpfs= | |
| 25 | Next, I used the =jmtpfs= package to mount my phone to my laptop. There | |
| 26 | are other packages that exist, but this one worked perfectly for me. On | |
| 27 | Fedora Linux, you can install it like this: | |
| 32 | 28 | |
| 33 | ```sh | |
| 29 | #+begin_src sh | |
| 34 | 30 | sudo dnf install jmtpfs -y |
| 35 | ``` | |
| 36 | ||
| 37 | ## Create a Mount Point | |
| 31 | #+end_src | |
| 38 | 32 | |
| 33 | * Create a Mount Point | |
| 39 | 34 | Once you have the package installed, you just need to create a folder |
| 40 | for the device to use as a mount point. In my case, I used | |
| 41 | `/mnt/pixel`: | |
| 35 | for the device to use as a mount point. In my case, I used =/mnt/pixel=: | |
| 42 | 36 | |
| 43 | ```sh | |
| 37 | #+begin_src sh | |
| 44 | 38 | sudo mkdir /mnt/pixel |
| 45 | 39 | sudo chown -R $USER:$USER /mnt/pixel |
| 46 | ``` | |
| 47 | ||
| 48 | ## Mount & Access the Phone's File System | |
| 40 | #+end_src | |
| 49 | 41 | |
| 42 | * Mount & Access the Phone's File System | |
| 50 | 43 | Finally, plug-in and mount the device, and you should be able to see all |
| 51 | 44 | storage (internal and external) inside your new folder! |
| 52 | 45 | |
| 53 | ```sh | |
| 46 | #+begin_src sh | |
| 54 | 47 | jmtpfs /mnt/pixel |
| 55 | ``` | |
| 48 | #+end_src | |
| 56 | 49 | |
| 57 | 50 | The output should look something like this: |
| 58 | 51 | |
| 59 | ```sh | |
| 52 | #+begin_src sh | |
| 60 | 53 | Device 0 (VID=18d1 and PID=4ee1) is a Google Inc Nexus/Pixel (MTP). |
| 61 | 54 | Android device detected, assigning default bug flags |
| 62 | ``` | |
| 55 | #+end_src | |
| 63 | 56 | |
| 64 | 57 | Now you are mounted and can do anything you'd like with the device's |
| 65 | 58 | files: |
| 66 | 59 | |
| 67 | ```sh | |
| 60 | #+begin_src sh | |
| 68 | 61 | cd /mnt/pixel |
| 69 | 62 | ls -lha |
| 70 | ``` | |
| 63 | #+end_src | |
| 71 | 64 | |
| 72 | 65 | From here, you will be able to see any internal or external storage |
| 73 | 66 | available on the device: |
| 74 | 67 | |
| 75 | ```sh | |
| 68 | #+begin_src sh | |
| 76 | 69 | total 0 |
| 77 | 70 | drwxr-xr-x. 3 user user 0 Jan 1 1970 . |
| 78 | 71 | drwxr-xr-x. 1 root root 10 Oct 4 13:29 .. |
| 79 | 72 | drwxr-xr-x. 16 user user 0 Apr 21 4426383 'Internal shared storage' |
| 80 | ``` | |
| 73 | #+end_src | |
blog/neon-drive/index.org added +93
| @@ -0,0 +1,93 @@ | ||
| 1 | #+title: Neon Drive: A Nostalgic 80s Arcade Racing Game | |
| 2 | #+date: 2020-12-28 | |
| 3 | #+description: A video game review for Neon Drive. | |
| 4 | #+filetags: :gaming: | |
| 5 | ||
| 6 | * Game Description | |
| 7 | [[https://store.steampowered.com/app/433910/Neon_Drive/][Neon Drive]] | |
| 8 | presents itself as a simple arcade-style game inspired by the arcade | |
| 9 | race games of the 1980s, yet it has managed to take up hours of my life | |
| 10 | without much effort. The game description, directly from the Steam page, | |
| 11 | is intriguing enough to entice anyone who's been looking for a good | |
| 12 | arcade racing game: | |
| 13 | ||
| 14 | #+begin_quote | |
| 15 | Neon Drive is a slick retro-futuristic arcade game that will make your | |
| 16 | brain melt. You've been warned. From beautiful cityscapes and ocean | |
| 17 | roads to exploding enemy spaceships, Neon Drive has it all. | |
| 18 | ||
| 19 | #+end_quote | |
| 20 | ||
| 21 | * Gameplay | |
| 22 | The game holds true to the | |
| 23 | [[https://en.wikipedia.org/wiki/Retrofuturism][retro-futurism]] style, | |
| 24 | including chrome female robots, pixelated arcade machines, and | |
| 25 | [[https://teddit.net/r/outrun/][outrun]] aesthetics. | |
| 26 | ||
| 27 | Each level of the game is shown as a separate arcade machine. Each | |
| 28 | arcade machine lets you play on Normal, Hard, Insane, Practice, and Free | |
| 29 | Run. To beat each arcade, you must reach the end of the level without | |
| 30 | crashing your car into the various obstacles on the course. Basic levels | |
| 31 | let you move left or right to avoid blocks in the road. Later levels put | |
| 32 | you through other tests, such as dodging traffic or blasting asteroids. | |
| 33 | ||
| 34 | The game uses synthwave music to keep you on track to make the correct | |
| 35 | moves by timing the beats of the songs to the correct moves on the | |
| 36 | screen. It reminds me of the early Guitar Hero games, as well as mobile | |
| 37 | apps like VOEZ - repetition and staying on-beat is the only way to win. | |
| 38 | ||
| 39 | * In-Game Screenshots | |
| 40 | Taking a look at the main menu, you can see that Neon Drive plays into | |
| 41 | every stereotype you can think of around retro-futuristic, synthwave | |
| 42 | arcades (in a good way). | |
| 43 | ||
| 44 | #+caption: Neon Drive Menu | |
| 45 | [[https://img.cleberg.net/blog/20201228-neon-drive/neon_drive_menu.png]] | |
| 46 | ||
| 47 | Once you get into the first level, we see that the choice of car fits | |
| 48 | right in with the stereotypical cars of the 80s, like the | |
| 49 | [[https://en.wikipedia.org/wiki/DMC_DeLorean][DeLorean]] or the | |
| 50 | [[https://en.wikipedia.org/wiki/Ferrari_F40][Ferrari F40]]. Each new | |
| 51 | level comes with new color schemes and cars, so you should never get | |
| 52 | tired of the aesthetic. | |
| 53 | ||
| 54 | #+caption: Neon Drive Race | |
| 55 | [[https://img.cleberg.net/blog/20201228-neon-drive/neon_drive_race.png]] | |
| 56 | ||
| 57 | Personally, I love the orange and blue colors used in level 2: | |
| 58 | ||
| 59 | #+caption: Level 2 | |
| 60 | [[https://img.cleberg.net/blog/20201228-neon-drive/neon_drive_level_2.png]] | |
| 61 | ||
| 62 | If you're the competitive type and getting 100% on all arcade machines | |
| 63 | isn't enough, there are leaderboards for the regular part of the game, | |
| 64 | and the endurance game mode. | |
| 65 | ||
| 66 | #+caption: Leaderboard | |
| 67 | [[https://img.cleberg.net/blog/20201228-neon-drive/neon_drive_leaderboard.png]] | |
| 68 | ||
| 69 | * Other Suggestions | |
| 70 | Neon Drive sits nicely within the well-founded cult genre of Outrun. | |
| 71 | Other games that I've enjoyed in this same spectrum are: | |
| 72 | ||
| 73 | - [[https://store.steampowered.com/app/233270/Far_Cry_3__Blood_Dragon/][Far | |
| 74 | Cry 3: Blood Dragon]] | |
| 75 | - [[https://store.steampowered.com/app/1239690/Retrowave/][Retrowave]] | |
| 76 | - [[https://store.steampowered.com/app/732810/Slipstream/][Slipstream]] | |
| 77 | ||
| 78 | Although these games aren't necessarily in the same genre, they do have | |
| 79 | aspects that place them close enough to interest gamers that enjoyed | |
| 80 | Neon Drive: | |
| 81 | ||
| 82 | - [[https://store.steampowered.com/app/311800/Black_Ice/][Black Ice]] | |
| 83 | - [[https://store.steampowered.com/app/746850/Cloudpunk/][Cloudpunk]] | |
| 84 | - [[https://store.steampowered.com/app/1222680/Need_for_Speed_Heat/][Need | |
| 85 | for Speed: Heat]] | |
| 86 | - [[https://store.steampowered.com/app/1019310/VirtuaVerse/][VirtuaVerse]] | |
| 87 | ||
| 88 | Of course, if all you really care about is the arcade aspect of these | |
| 89 | games, you can check out the | |
| 90 | [[https://store.steampowered.com/app/400020/Atari_Vault/][Atari Vault]] | |
| 91 | or any of the other classic games sold on Steam by companies like Namco, | |
| 92 | Atari. For something like Nintendo, you'd have to settle for buying used | |
| 93 | classic consoles or delve into the world of emulation. | |
content/blog/2022-03-23-nextcloud-on-ubuntu.md → blog/nextcloud-on-ubuntu/index.org renamed +58 −68
| @@ -1,83 +1,77 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-03-23 | |
| 3 | title = "Installing Nextcloud on Ubuntu" | |
| 4 | description = "A guide to self-hosting the NextCloud application on your own server." | |
| 5 | +++ | |
| 1 | #+title: Nextcloud on Ubuntu | |
| 2 | #+date: 2022-03-23 | |
| 3 | #+description: A guide to self-hosting the NextCloud application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 6 | 5 | |
| 7 | ## What is Nextcloud? | |
| 8 | ||
| 9 | [Nextcloud](https://nextcloud.com/) is a self-hosted solution for | |
| 6 | * What is Nextcloud? | |
| 7 | [[https://nextcloud.com/][Nextcloud]] is a self-hosted solution for | |
| 10 | 8 | storage, communications, editing, calendar, contacts, and more. |
| 11 | 9 | |
| 12 | 10 | This tutorial assumes that you have an Ubuntu server and a domain name |
| 13 | 11 | configured to point toward the server. |
| 14 | 12 | |
| 15 | ## Install Dependencies | |
| 16 | ||
| 13 | * Install Dependencies | |
| 17 | 14 | To start, you will need to install the packages that Nextcloud requires: |
| 18 | 15 | |
| 19 | ```sh | |
| 16 | #+begin_src sh | |
| 20 | 17 | sudo apt install apache2 mariadb-server libapache2-mod-php7.4 |
| 21 | 18 | sudo apt install php7.4-gd php7.4-mysql php7.4-curl php7.4-mbstring php7.4-intl |
| 22 | 19 | sudo apt install php7.4-gmp php7.4-bcmath php-imagick php7.4-xml php7.4-zip |
| 23 | ``` | |
| 20 | #+end_src | |
| 24 | 21 | |
| 25 | ## Set Up MySQL | |
| 22 | * Set Up MySQL | |
| 23 | Next, you will need to log in to MySQL as the =root= user of the | |
| 24 | machine. | |
| 26 | 25 | |
| 27 | Next, you will need to log in to MySQL as the `root` user of | |
| 28 | the machine. | |
| 29 | ||
| 30 | ```sh | |
| 26 | #+begin_src sh | |
| 31 | 27 | sudo mysql -uroot -p |
| 32 | ``` | |
| 28 | #+end_src | |
| 33 | 29 | |
| 34 | 30 | Once you've logged in, you must create a new user so that Nextcloud can |
| 35 | manage the database. You will also create a `nextcloud` | |
| 36 | database and assign privileges: | |
| 31 | manage the database. You will also create a =nextcloud= database and | |
| 32 | assign privileges: | |
| 37 | 33 | |
| 38 | ```sql | |
| 34 | #+begin_src sql | |
| 39 | 35 | CREATE USER 'username'@'localhost' IDENTIFIED BY 'password'; |
| 40 | 36 | CREATE DATABASE IF NOT EXISTS nextcloud CHARACTER SET utf8mb4 COLLATE utf8mb4_general_ci; |
| 41 | GRANT ALL PRIVILEGES ON nextcloud.* TO 'username'@'localhost'; | |
| 37 | GRANT ALL PRIVILEGES ON nextcloud.** TO 'username'@'localhost'; | |
| 42 | 38 | FLUSH PRIVILEGES; |
| 43 | 39 | quit; |
| 44 | ``` | |
| 45 | ||
| 46 | ## Download & Install Nextcloud | |
| 40 | #+end_src | |
| 47 | 41 | |
| 48 | To download Nextcloud, go the [Nextcloud downloads | |
| 49 | page](https://nextcloud.com/install/#instructions-server), click on | |
| 50 | `Archive File` and right-click the big blue button to copy | |
| 51 | the link. | |
| 42 | * Download & Install Nextcloud | |
| 43 | To download Nextcloud, go the | |
| 44 | [[https://nextcloud.com/install/#instructions-server][Nextcloud | |
| 45 | downloads page]], click on =Archive File= and right-click the big blue | |
| 46 | button to copy the link. | |
| 52 | 47 | |
| 53 | 48 | Then, go to your server and enter the following commands to download, |
| 54 | 49 | unzip, and move the files to your destination directory. This example |
| 55 | uses `example.com` as the destination, but you can put it | |
| 56 | wherever you want to server your files from. | |
| 50 | uses =example.com= as the destination, but you can put it wherever you | |
| 51 | want to server your files from. | |
| 57 | 52 | |
| 58 | ```sh | |
| 53 | #+begin_src sh | |
| 59 | 54 | wget https://download.nextcloud.com/server/releases/nextcloud-23.0.3.zip |
| 60 | 55 | sudo apt install unzip |
| 61 | 56 | unzip nextcloud-23.0.3.zip |
| 62 | 57 | sudo cp -r nextcloud /var/www/example.com |
| 63 | ``` | |
| 64 | ||
| 65 | ## Configure the Apache Web Server | |
| 58 | #+end_src | |
| 66 | 59 | |
| 60 | * Configure the Apache Web Server | |
| 67 | 61 | Now that the database is set up and Nextcloud is installed, you need to |
| 68 | 62 | set up the Apache configuration files to tell the server how to handle |
| 69 | requests for `example.com/nextcloud`. | |
| 63 | requests for =example.com/nextcloud=. | |
| 70 | 64 | |
| 71 | 65 | First, open the following file in the editor: |
| 72 | 66 | |
| 73 | ```sh | |
| 67 | #+begin_src sh | |
| 74 | 68 | sudo nano /etc/apache2/sites-available/nextcloud.conf |
| 75 | ``` | |
| 69 | #+end_src | |
| 76 | 70 | |
| 77 | 71 | Once the editor is open, paste the following information in. Then, save |
| 78 | 72 | and close the file. |
| 79 | 73 | |
| 80 | ```config | |
| 74 | #+begin_src config | |
| 81 | 75 | <VirtualHost *:80> |
| 82 | 76 | DocumentRoot /var/www/example.com |
| 83 | 77 | ServerName example.com |
| @@ -96,74 +90,70 @@ and close the file. | ||
| 96 | 90 | </IfModule> |
| 97 | 91 | </Directory> |
| 98 | 92 | </VirtualHost> |
| 99 | ``` | |
| 93 | #+end_src | |
| 100 | 94 | |
| 101 | 95 | Once the file is saved, enable it with Apache: |
| 102 | 96 | |
| 103 | ```sh | |
| 97 | #+begin_src sh | |
| 104 | 98 | sudo a2ensite nextcloud.conf |
| 105 | ``` | |
| 99 | #+end_src | |
| 106 | 100 | |
| 107 | 101 | Next, enable the Apache mods required by Nextcloud: |
| 108 | 102 | |
| 109 | ```sh | |
| 103 | #+begin_src sh | |
| 110 | 104 | sudo a2enmod rewrite headers env dir mime |
| 111 | ``` | |
| 105 | #+end_src | |
| 112 | 106 | |
| 113 | 107 | Finally, restart Apache. If any errors arise, you must solve those |
| 114 | 108 | before continuing. |
| 115 | 109 | |
| 116 | ```sh | |
| 110 | #+begin_src sh | |
| 117 | 111 | sudo systemctl restart apache2 |
| 118 | ``` | |
| 112 | #+end_src | |
| 119 | 113 | |
| 120 | 114 | For the app to work, you must have the correct file permissions on your |
| 121 | `nextcloud` directory. Set the owner to be | |
| 122 | `www-data`: | |
| 115 | =nextcloud= directory. Set the owner to be =www-data=: | |
| 123 | 116 | |
| 124 | ```sh | |
| 117 | #+begin_src sh | |
| 125 | 118 | sudo chown -R www-data:www-data /var/www/example.com/nextcloud/ |
| 126 | ``` | |
| 127 | ||
| 128 | ## DNS | |
| 119 | #+end_src | |
| 129 | 120 | |
| 121 | * DNS | |
| 130 | 122 | If you do not have a static IP address, you will need to update your DNS |
| 131 | 123 | settings (at your DNS provider) whenever your dynamic IP address |
| 132 | 124 | changes. |
| 133 | 125 | |
| 134 | 126 | For an example on how I do that with Cloudflare, see my other post: |
| 135 | [Updating Dynamic DNS with Cloudflare | |
| 136 | API](/blog/updating-dynamic-dns-with-cloudflare-api/) | |
| 137 | ||
| 138 | ## Certbot | |
| 127 | [[../updating-dynamic-dns-with-cloudflare-api/][Updating Dynamic DNS | |
| 128 | with Cloudflare API]] | |
| 139 | 129 | |
| 130 | * Certbot | |
| 140 | 131 | If you want to serve Nextcloud from HTTPS rather than plain HTTP, use |
| 141 | 132 | the following commands to issue Let's Encrypt SSL certificates: |
| 142 | 133 | |
| 143 | ```sh | |
| 134 | #+begin_src sh | |
| 144 | 135 | sudo apt install snapd |
| 145 | 136 | sudo snap install core |
| 146 | 137 | sudo snap refresh core |
| 147 | 138 | sudo snap install --classic certbot |
| 148 | 139 | sudo ln -s /snap/bin/certbot /usr/bin/certbot |
| 149 | 140 | sudo certbot --apache |
| 150 | ``` | |
| 151 | ||
| 152 | ## Results | |
| 141 | #+end_src | |
| 153 | 142 | |
| 143 | * Results | |
| 154 | 144 | Voilà! You're all done and should be able to access Nextcloud from your |
| 155 | 145 | domain or IP address. |
| 156 | 146 | |
| 157 | 147 | See the screenshots below for the dashboard and a settings page on my |
| 158 | instance of Nextcloud, using the `Breeze Dark` theme I | |
| 159 | installed from the Apps page. | |
| 148 | instance of Nextcloud, using the =Breeze Dark= theme I installed from | |
| 149 | the Apps page. | |
| 160 | 150 | |
| 161 |  | |
| 151 | #+caption: Nextcloud Dashboard | |
| 152 | [[https://img.cleberg.net/blog/20220323-installing-nextcloud-on-ubuntu/nextcloud_dashboard.png]] | |
| 163 | 153 | |
| 164 | *Figure 01: Nextcloud Dashboard* | |
| 154 | /Figure 01: Nextcloud Dashboard/ | |
| 165 | 155 | |
| 166 |  | |
| 156 | #+caption: Nextcloud Settings | |
| 157 | [[https://img.cleberg.net/blog/20220323-installing-nextcloud-on-ubuntu/nextcloud_settings.png]] | |
| 168 | 158 | |
| 169 | *Figure 02: Nextcloud Security Settings* | |
| 159 | /Figure 02: Nextcloud Security Settings/ | |
blog/nginx-caching/index.org added +68
| @@ -0,0 +1,68 @@ | ||
| 1 | #+title: Caching Static Content with Nginx | |
| 2 | #+date: 2022-02-20 | |
| 3 | #+description: Learn how to enable the static content cache in Nginx. | |
| 4 | #+filetags: :nginx: | |
| 5 | ||
| 6 | * Update Your Nginx Config to Cache Static Files | |
| 7 | If you run a website on Nginx that serves static content (i.e., content | |
| 8 | that is not dynamic and changing with interactions from the user), you | |
| 9 | would likely benefit from caching that content on the client-side. If | |
| 10 | you're used to Apache and looking for the Nginx equivalent, this post | |
| 11 | should help. | |
| 12 | ||
| 13 | Luckily, setting up the cache is as easy as identifying the file types | |
| 14 | you want to cache and determining the expiration length. To include more | |
| 15 | file types, simply use the bar separator (=|=) and type the new file | |
| 16 | extension you want to include. | |
| 17 | ||
| 18 | #+begin_src config | |
| 19 | server { | |
| 20 | ... | |
| 21 | ||
| 22 | location ~** .(css|js|jpg|jpeg|gif|png|ico)$ { | |
| 23 | expires 30d; | |
| 24 | } | |
| 25 | ||
| 26 | ... | |
| 27 | } | |
| 28 | #+end_src | |
| 29 | ||
| 30 | I have seen some people who prefer to set =expires= as =365d= or even | |
| 31 | =max=, but that is only for stable, infrequently changing websites. As | |
| 32 | my site often changes (i.e., I'm never content with my website), I need | |
| 33 | to know that my readers are seeing the new content without waiting too | |
| 34 | long. | |
| 35 | ||
| 36 | So, I went ahead and set the expiration date at =30d=, which is short | |
| 37 | enough to refresh for readers but long enough that clients/browsers | |
| 38 | won't be re-requesting the static files too often, hopefully resulting | |
| 39 | in faster loading times, as images should be the only thing slowing down | |
| 40 | my site. | |
| 41 | ||
| 42 | * Testing Results | |
| 43 | To test my changes to the Nginx configuration, I used the | |
| 44 | [[https://addons.mozilla.org/en-US/firefox/addon/http-header-live/][HTTP | |
| 45 | Header Live]] extension on my Gecko browser and used the sidebar to | |
| 46 | inspect the headers of a recent image from my blog. | |
| 47 | ||
| 48 | In the image below, you can see that the =Cache-Control= header is now | |
| 49 | present and set to 2592000, which is 30 days represented in seconds (30 | |
| 50 | days _ 24 hours/day _ 60 minutes/hour ** 60 seconds/minute = 2,592,000 | |
| 51 | seconds). | |
| 52 | ||
| 53 | The =Expires= field is now showing 22 March 2022, which is 30 days from | |
| 54 | the day of this post, 20 February 2022. | |
| 55 | ||
| 56 | #+caption: Image Headers | |
| 57 | [[https://img.cleberg.net/blog/20220220-caching-static-content-with-nginx/image_headers.png]] | |
| 58 | ||
| 59 | * Caveats | |
| 60 | Remember that this caching system is *client-side*, which means that | |
| 61 | content is only cached for as long as a client allows it. For example, | |
| 62 | my browser purges all caches, data, etc. upon exit, so this caching | |
| 63 | policy will only work as long as my browser remains open and running. | |
| 64 | ||
| 65 | If you need to test updates to your site, you'll need to clear the cache | |
| 66 | to see updates for any file extension you configured. This can often be | |
| 67 | done with the =Shift + F5= or =Ctrl + F5= key combinations in most | |
| 68 | browsers. | |
blog/nginx-compression/index.org added +73
| @@ -0,0 +1,73 @@ | ||
| 1 | #+title: Enable GZIP Compression in Nginx | |
| 2 | #+date: 2022-12-01 | |
| 3 | #+description: Learn how to enable compression in Nginx. | |
| 4 | #+filetags: :nginx: | |
| 5 | ||
| 6 | * Text Compression | |
| 7 | Text compression allows a web server to serve text-based resources | |
| 8 | faster than uncompressed data. This can speed up things like First | |
| 9 | Contentful Paint, Tie to Interactive, and Speed Index. | |
| 10 | ||
| 11 | * Enable Nginx Compression with gzip | |
| 12 | In order to enable text compression on Nginx, we need to enable it | |
| 13 | within the configuration file: | |
| 14 | ||
| 15 | #+begin_src sh | |
| 16 | nano /etc/nginx/nginx.conf | |
| 17 | #+end_src | |
| 18 | ||
| 19 | Within the =http= block, find the section that shows something like the | |
| 20 | block below. This is the default gzip configuration I found in my | |
| 21 | =nginx.conf= file on Alpine Linux 3.17. Yours may look slightly | |
| 22 | different, just make sure that you're not creating any duplicate gzip | |
| 23 | options. | |
| 24 | ||
| 25 | #+begin_src conf | |
| 26 | # Enable gzipping of responses. | |
| 27 | #gzip on; | |
| 28 | ||
| 29 | # Set the Vary HTTP header as defined in the RFC 2616. Default is 'off'. | |
| 30 | gzip_vary on; | |
| 31 | #+end_src | |
| 32 | ||
| 33 | Remove the default gzip lines and replace them with the following: | |
| 34 | ||
| 35 | #+begin_src conf | |
| 36 | # Enable gzipping of responses. | |
| 37 | gzip on; | |
| 38 | gzip_vary on; | |
| 39 | gzip_min_length 10240; | |
| 40 | gzip_proxied expired no-cache no-store private auth; | |
| 41 | gzip_types text/plain text/css text/xml text/javascript application/x-javascript application/xml; | |
| 42 | gzip_disable "MSIE [1-6]"; | |
| 43 | #+end_src | |
| 44 | ||
| 45 | * Explanations of ngx_{httpgzipmodule} Options | |
| 46 | Each of the lines above enables a different aspect of the gzip response | |
| 47 | for Nginx. Here are the full explanations: | |
| 48 | ||
| 49 | - =gzip= -- Enables or disables gzipping of responses. | |
| 50 | - =gzip_vary= -- Enables or disables inserting the "Vary: | |
| 51 | Accept-Encoding" response header field if the directives gzip, | |
| 52 | gzip_{static}, or gunzip are active. | |
| 53 | - =gzip_min_length= -- Sets the minimum length of a response that will | |
| 54 | be gzipped. The length is determined only from the "Content-Length" | |
| 55 | response header field. | |
| 56 | - =gzip_proxied= -- Enables or disables gzipping of responses for | |
| 57 | proxied requests depending on the request and response. The fact that | |
| 58 | the request is proxied is determined by the presence of the "Via" | |
| 59 | request header field. | |
| 60 | - =gzip_types= -- Enables gzipping of responses for the specified MIME | |
| 61 | types in addition to "text/html". The special value “*” matches any | |
| 62 | MIME type (0.8.29). Responses with the "text/html" type are always | |
| 63 | compressed. | |
| 64 | - =gzip_disable= -- Disables gzipping of responses for requests with | |
| 65 | "User-Agent" header fields matching any of the specified regular | |
| 66 | expressions. | |
| 67 | - The special mask "msie6" (0.7.12) corresponds to the regular | |
| 68 | expression "MSIE [4-6].", but works faster. Starting from version | |
| 69 | 0.8.11, "MSIE 6.0; ... SV1" is excluded from this mask. | |
| 70 | ||
| 71 | More information on these directives and their options can be found on | |
| 72 | the [[https://nginx.org/en/docs/http/ngx_http_gzip_module.html][Module | |
| 73 | ngx_{httpgzipmodule}]] page in Nginx's documentation. | |
content/blog/2022-11-29-nginx-referrer-ban-list.md → blog/nginx-referrer-ban-list/index.org renamed +46 −53
| @@ -1,25 +1,23 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-11-29 | |
| 3 | title = "Creating a Referrer Ban List in Nginx" | |
| 4 | description = "Learn how to create a ban list for referring sites in Nginx." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Creating the Ban List | |
| 1 | #+title: Creating a Referrer Ban List in Nginx | |
| 2 | #+date: 2022-11-29 | |
| 3 | #+description: Learn how to create a ban list for referring sites in Nginx. | |
| 4 | #+filetags: :nginx: | |
| 8 | 5 | |
| 6 | * Creating the Ban List | |
| 9 | 7 | In order to ban list referral domains or websites with Nginx, you need |
| 10 | 8 | to create a ban list file. The file below will accept regexes for |
| 11 | 9 | different domains or websites you wish to block. |
| 12 | 10 | |
| 13 | 11 | First, create the file in your nginx directory: |
| 14 | 12 | |
| 15 | ```sh | |
| 13 | #+begin_src sh | |
| 16 | 14 | doas nano /etc/nginx/banlist.conf |
| 17 | ``` | |
| 15 | #+end_src | |
| 18 | 16 | |
| 19 | 17 | Next, paste the following contents in and fill out the regexes with |
| 20 | 18 | whichever domains you're blocking. |
| 21 | 19 | |
| 22 | ```conf | |
| 20 | #+begin_src conf | |
| 23 | 21 | # /etc/nginx/banlist.conf |
| 24 | 22 | |
| 25 | 23 | map $http_referer $bad_referer { |
| @@ -30,21 +28,20 @@ map $http_referer $bad_referer { | ||
| 30 | 28 | # Put regexes for undesired referrers here |
| 31 | 29 | "~news.ycombinator.com" 1; |
| 32 | 30 | } |
| 33 | ``` | |
| 34 | ||
| 35 | ## Configuring Nginx | |
| 31 | #+end_src | |
| 36 | 32 | |
| 33 | * Configuring Nginx | |
| 37 | 34 | In order for the ban list to work, Nginx needs to know it exists and how |
| 38 | to handle it. For this, edit the `nginx.conf` file. | |
| 35 | to handle it. For this, edit the =nginx.conf= file. | |
| 39 | 36 | |
| 40 | ```sh | |
| 37 | #+begin_src sh | |
| 41 | 38 | doas nano /etc/nginx/nginx.conf |
| 42 | ``` | |
| 39 | #+end_src | |
| 43 | 40 | |
| 44 | Within this file, find the `http` block and add your ban list | |
| 45 | file location to the end of the block. | |
| 41 | Within this file, find the =http= block and add your ban list file | |
| 42 | location to the end of the block. | |
| 46 | 43 | |
| 47 | ```conf | |
| 44 | #+begin_src conf | |
| 48 | 45 | # /etc/nginx/nginx.conf |
| 49 | 46 | |
| 50 | 47 | http { |
| @@ -53,30 +50,28 @@ http { | ||
| 53 | 50 | # Include ban list |
| 54 | 51 | include /etc/nginx/banlist.conf; |
| 55 | 52 | } |
| 56 | ``` | |
| 57 | ||
| 58 | ## Enabling the Ban List | |
| 53 | #+end_src | |
| 59 | 54 | |
| 55 | * Enabling the Ban List | |
| 60 | 56 | Finally, we need to take action when a bad referral site is found. To do |
| 61 | 57 | so, edit the configuration file for your website. For example, I have |
| 62 | all website configuration files in the `http.d` directory. | |
| 63 | You may have them in the `sites-available` directory on some | |
| 64 | distributions. | |
| 58 | all website configuration files in the =http.d= directory. You may have | |
| 59 | them in the =sites-available= directory on some distributions. | |
| 65 | 60 | |
| 66 | ```sh | |
| 61 | #+begin_src sh | |
| 67 | 62 | doas nano /etc/nginx/http.d/example.com.conf |
| 68 | ``` | |
| 63 | #+end_src | |
| 69 | 64 | |
| 70 | Within each website's configuration file, edit the `server` | |
| 71 | blocks that are listening to ports 80 and 443 and create a check for the | |
| 72 | `$bad_referrer` variable we created in the ban list file. | |
| 65 | Within each website's configuration file, edit the =server= blocks that | |
| 66 | are listening to ports 80 and 443 and create a check for the | |
| 67 | =$bad_referrer= variable we created in the ban list file. | |
| 73 | 68 | |
| 74 | If a matching site is found, you can return any [HTTP Status | |
| 75 | Code](https://en.wikipedia.org/wiki/List_of_HTTP_status_codes) you want. | |
| 76 | Code 403 (Forbidden) is logical in this case since you are preventing a | |
| 77 | client connection due to a banned domain. | |
| 69 | If a matching site is found, you can return any | |
| 70 | [[https://en.wikipedia.org/wiki/List_of_HTTP_status_codes][HTTP Status | |
| 71 | Code]] you want. Code 403 (Forbidden) is logical in this case since you | |
| 72 | are preventing a client connection due to a banned domain. | |
| 78 | 73 | |
| 79 | ```conf | |
| 74 | #+begin_src conf | |
| 80 | 75 | server { |
| 81 | 76 | ... |
| 82 | 77 | |
| @@ -87,42 +82,40 @@ server { | ||
| 87 | 82 | |
| 88 | 83 | ... |
| 89 | 84 | } |
| 90 | ``` | |
| 91 | ||
| 92 | ## Restart Nginx | |
| 85 | #+end_src | |
| 93 | 86 | |
| 87 | * Restart Nginx | |
| 94 | 88 | Lastly, restart Nginx to enable all changes made. |
| 95 | 89 | |
| 96 | ```sh | |
| 90 | #+begin_src sh | |
| 97 | 91 | doas rc-service nginx restart |
| 98 | ``` | |
| 99 | ||
| 100 | ## Testing Results | |
| 92 | #+end_src | |
| 101 | 93 | |
| 94 | * Testing Results | |
| 102 | 95 | In order to test the results, let's curl the contents of our site. To |
| 103 | 96 | start, I'll curl the site normally: |
| 104 | 97 | |
| 105 | ```sh | |
| 98 | #+begin_src sh | |
| 106 | 99 | curl https://cleberg.net |
| 107 | ``` | |
| 100 | #+end_src | |
| 108 | 101 | |
| 109 | 102 | The HTML contents of the page come back successfully: |
| 110 | 103 | |
| 111 | ```html | |
| 104 | #+begin_src html | |
| 112 | 105 | <!doctype html>...</html> |
| 113 | ``` | |
| 106 | #+end_src | |
| 114 | 107 | |
| 115 | 108 | Next, let's include a banned referrer: |
| 116 | 109 | |
| 117 | ```sh | |
| 110 | #+begin_src sh | |
| 118 | 111 | curl --referer https://news.ycombinator.com https://cleberg.net |
| 119 | ``` | |
| 112 | #+end_src | |
| 120 | 113 | |
| 121 | This time, I'm met with a 403 Forbidden response page. That means we | |
| 122 | are successful and any clients being referred from a banned domain will | |
| 123 | be met with this same response code. | |
| 114 | This time, I'm met with a 403 Forbidden response page. That means we are | |
| 115 | successful and any clients being referred from a banned domain will be | |
| 116 | met with this same response code. | |
| 124 | 117 | |
| 125 | ```html | |
| 118 | #+begin_src html | |
| 126 | 119 | <html> |
| 127 | 120 | <head><title>403 Forbidden</title></head> |
| 128 | 121 | <body> |
| @@ -130,4 +123,4 @@ be met with this same response code. | ||
| 130 | 123 | <hr><center>nginx</center> |
| 131 | 124 | </body> |
| 132 | 125 | </html> |
| 133 | ``` | |
| 126 | #+end_src | |
content/blog/2022-04-02-nginx-reverse-proxy.md → blog/nginx-reverse-proxy/index.org renamed +97 −111
| @@ -1,43 +1,40 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-04-02 | |
| 3 | title = "Set-Up a Reverse Proxy with Nginx" | |
| 4 | description = "Learn how to set-up an Nginx reverse proxy from scratch." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## What is a Reverse Proxy? | |
| 1 | #+title: Set-Up a Reverse Proxy with Nginx | |
| 2 | #+date: 2022-04-02 | |
| 3 | #+description: Learn how to set-up an Nginx reverse proxy from scratch. | |
| 4 | #+filetags: :nginx: | |
| 8 | 5 | |
| 6 | * What is a Reverse Proxy? | |
| 9 | 7 | A reverse proxy is a server that is placed between local servers or |
| 10 | 8 | services and clients/users (e.g., the internet). The reverse proxy |
| 11 | 9 | intercepts all requests from clients at the network edge and uses its |
| 12 | 10 | configuration files to determine where each request should be sent. |
| 13 | 11 | |
| 14 | ### A Brief Example | |
| 15 | ||
| 12 | ** A Brief Example | |
| 16 | 13 | For example, let's say that I run three servers in my home: |
| 17 | 14 | |
| 18 | - Server~01~ (`example.com`) | |
| 19 | - Server~02~ (`service01.example.com`) | |
| 20 | - Server~03~ (`service02.example.com`) | |
| 15 | - Server_{01} (=example.com=) | |
| 16 | - Server_{02} (=service01.example.com=) | |
| 17 | - Server_{03} (=service02.example.com=) | |
| 21 | 18 | |
| 22 | 19 | I also run a reverse proxy in my home that intercepts all public |
| 23 | 20 | traffic: |
| 24 | 21 | |
| 25 | - Reverse Proxy | |
| 22 | - Reverse Proxy | |
| 26 | 23 | |
| 27 | Assume that I have a domain name (`example.com`) that allows | |
| 28 | clients to request websites or services from my home servers. | |
| 24 | Assume that I have a domain name (=example.com=) that allows clients to | |
| 25 | request websites or services from my home servers. | |
| 29 | 26 | |
| 30 | 27 | In this case, the reverse proxy will intercept all traffic from |
| 31 | `example.com` that enters my network and determine if the | |
| 32 | client is requesting valid data, based on my configuration. | |
| 28 | =example.com= that enters my network and determine if the client is | |
| 29 | requesting valid data, based on my configuration. | |
| 33 | 30 | |
| 34 | If the user is requesting `example.com` and my configuration | |
| 35 | files say that Server~01~ holds that data, Nginx will send the user to | |
| 36 | Server~01~. If I were to change the configuration so that | |
| 37 | `example.com` is routed to Server~02~, that same user would | |
| 38 | be sent to Server~02~ instead. | |
| 31 | If the user is requesting =example.com= and my configuration files say | |
| 32 | that Server_{01} holds that data, Nginx will send the user to | |
| 33 | Server_{01}. If I were to change the configuration so that =example.com= | |
| 34 | is routed to Server_{02}, that same user would be sent to Server_{02} | |
| 35 | instead. | |
| 39 | 36 | |
| 40 | ```txt | |
| 37 | #+begin_src txt | |
| 41 | 38 | ┌──────┐ ┌───────────┐ |
| 42 | 39 | │ User │─┐ ┌──► Server_01 │ |
| 43 | 40 | └──────┘ │ │ └───────────┘ |
| @@ -47,140 +44,130 @@ be sent to Server~02~ instead. | ||
| 47 | 44 | ┌──────┐ │ │ ┌───────────┐ |
| 48 | 45 | │ User │─┘ └──► Server_03 │ |
| 49 | 46 | └──────┘ └───────────┘ |
| 50 | ``` | |
| 51 | ||
| 52 | ## Reverse Proxy Options | |
| 47 | #+end_src | |
| 53 | 48 | |
| 49 | * Reverse Proxy Options | |
| 54 | 50 | There are a lot of options when it comes to reverse proxy servers, so |
| 55 | I'm just going to list a few of the options I've heard recommended | |
| 56 | over the last few years: | |
| 51 | I'm just going to list a few of the options I've heard recommended over | |
| 52 | the last few years: | |
| 57 | 53 | |
| 58 | - [Nginx](https://nginx.com) | |
| 59 | - [Caddy](https://caddyserver.com) | |
| 60 | - [Traefik](https://traefik.io/) | |
| 61 | - [HAProxy](https://www.haproxy.org/) | |
| 62 | - [Squid](https://ubuntu.com/server/docs/proxy-servers-squid) | |
| 54 | - [[https://nginx.com][Nginx]] | |
| 55 | - [[https://caddyserver.com][Caddy]] | |
| 56 | - [[https://traefik.io/][Traefik]] | |
| 57 | - [[https://www.haproxy.org/][HAProxy]] | |
| 58 | - [[https://ubuntu.com/server/docs/proxy-servers-squid][Squid]] | |
| 63 | 59 | |
| 64 | 60 | In this post, we will be using Nginx as our reverse proxy, running on |
| 65 | 61 | Ubuntu Server 20.04.4 LTS. |
| 66 | 62 | |
| 67 | ## Nginx Reverse Proxy Example | |
| 68 | ||
| 69 | ### Local Applications | |
| 70 | ||
| 63 | * Nginx Reverse Proxy Example | |
| 64 | ** Local Applications | |
| 71 | 65 | You may be like me and have a lot of applications running on your local |
| 72 | 66 | network that you'd like to expose publicly with a domain. |
| 73 | 67 | |
| 74 | 68 | In my case, I have services running in multiple Docker containers within |
| 75 | 69 | a single server and want a way to visit those services from anywhere |
| 76 | with a URL. For example, on my local network, [Dashy](https://dashy.to) | |
| 77 | runs through port 4000 (`localhost:4000`) and [Uptime | |
| 78 | Kuma](https://github.com/louislam/uptime-kuma) runs through port 3001 | |
| 79 | (`localhost:3001`). | |
| 70 | with a URL. For example, on my local network, | |
| 71 | [[https://dashy.to][Dashy]] runs through port 4000 (=localhost:4000=) | |
| 72 | and [[https://github.com/louislam/uptime-kuma][Uptime Kuma]] runs | |
| 73 | through port 3001 (=localhost:3001=). | |
| 80 | 74 | |
| 81 | 75 | In order to expose these services to the public, I will need to do the |
| 82 | 76 | following: |
| 83 | 77 | |
| 84 | 1. Set up DNS records for a domain or subdomain (one per service) to | |
| 85 | point toward the IP address of the server. | |
| 86 | 2. Open up the server network's HTTP and HTTPS ports (80 & 443) so | |
| 87 | that the reverse proxy can accept traffic and determine where to | |
| 88 | send it. | |
| 89 | 3. Install the reverse proxy software. | |
| 90 | 4. Configure the reverse proxy to recognize which service should get | |
| 91 | traffic from any of the domains or subdomains. | |
| 78 | 1. Set up DNS records for a domain or subdomain (one per service) to | |
| 79 | point toward the IP address of the server. | |
| 80 | 2. Open up the server network's HTTP and HTTPS ports (80 & 443) so that | |
| 81 | the reverse proxy can accept traffic and determine where to send it. | |
| 82 | 3. Install the reverse proxy software. | |
| 83 | 4. Configure the reverse proxy to recognize which service should get | |
| 84 | traffic from any of the domains or subdomains. | |
| 92 | 85 | |
| 93 | ### Step 1: DNS Configuration | |
| 86 | ** Step 1: DNS Configuration | |
| 87 | To start, update your DNS configuration so that you have an =A= record | |
| 88 | for each domain or subdomain. | |
| 94 | 89 | |
| 95 | To start, update your DNS configuration so that you have an | |
| 96 | `A` record for each domain or subdomain. | |
| 90 | The =A= records should point toward the public IP address of the server. | |
| 91 | If you don't know the public IP address, log in to the server and run | |
| 92 | the following command: | |
| 97 | 93 | |
| 98 | The `A` records should point toward the public IP address of | |
| 99 | the server. If you don't know the public IP address, log in to the | |
| 100 | server and run the following command: | |
| 101 | ||
| 102 | ```sh | |
| 94 | #+begin_src sh | |
| 103 | 95 | curl ifconfig.co |
| 104 | ``` | |
| 96 | #+end_src | |
| 105 | 97 | |
| 106 | In the DNS example below, `xxx.xxx.xxx.xxx` is the public IP | |
| 107 | address of the server. | |
| 98 | In the DNS example below, =xxx.xxx.xxx.xxx= is the public IP address of | |
| 99 | the server. | |
| 108 | 100 | |
| 109 | ```config | |
| 101 | #+begin_src config | |
| 110 | 102 | example.com A xxx.xxx.xxx.xxx |
| 111 | 103 | uptime.example.com A xxx.xxx.xxx.xxx |
| 112 | 104 | dashy.example.com A xxx.xxx.xxx.xxx |
| 113 | 105 | www CNAME example.com |
| 114 | ``` | |
| 115 | ||
| 116 | Finally, ensure the DNS has propagated correctly with [DNS | |
| 117 | Checker](https://dnschecker.org) by entering your domains or subdomains | |
| 118 | in the search box and ensuring the results are showing the correct IP | |
| 119 | address. | |
| 106 | #+end_src | |
| 120 | 107 | |
| 121 | ### Step 2: Open Network Ports | |
| 108 | Finally, ensure the DNS has propagated correctly with | |
| 109 | [[https://dnschecker.org][DNS Checker]] by entering your domains or | |
| 110 | subdomains in the search box and ensuring the results are showing the | |
| 111 | correct IP address. | |
| 122 | 112 | |
| 113 | ** Step 2: Open Network Ports | |
| 123 | 114 | This step will be different depending on which router you have in your |
| 124 | 115 | home. If you're not sure, try to visit |
| 125 | [192.168.1.1](http://192.168.1.1) in your browser. Login credentials are | |
| 126 | usually written on a sticker somewhere on your modem/router. | |
| 116 | [[http://192.168.1.1][192.168.1.1]] in your browser. Login credentials | |
| 117 | are usually written on a sticker somewhere on your modem/router. | |
| 127 | 118 | |
| 128 | 119 | Once you're able to log in to your router, find the Port Forwarding |
| 129 | settings. You will need to forward ports `80` and | |
| 130 | `443` to whichever machine is running the reverse proxy. | |
| 120 | settings. You will need to forward ports =80= and =443= to whichever | |
| 121 | machine is running the reverse proxy. | |
| 131 | 122 | |
| 132 | 123 | In my case, the table below shows the port-forwarding rules I've |
| 133 | created. In this table, `xxx.xxx.xxx.xxx` is the local device | |
| 134 | IP of the reverse proxy server, it will probably be an IP between | |
| 135 | `192.168.1.1` and `192.168.1.255`. | |
| 124 | created. In this table, =xxx.xxx.xxx.xxx= is the local device IP of the | |
| 125 | reverse proxy server, it will probably be an IP between =192.168.1.1= | |
| 126 | and =192.168.1.255=. | |
| 136 | 127 | |
| 137 | NAME FROM PORT DEST PORT/IP ENABLED | |
| 138 | ------- ------ ------ ----------------- --------- | |
| 139 | HTTP \* 80 xxx.xxx.xxx.xxx TRUE | |
| 140 | HTTPS \* 443 xxx.xxx.xxx.xxx TRUE | |
| 128 | | NAME | FROM | PORT | DEST PORT/IP | ENABLED | | |
| 129 | |-------+------+------+-----------------+---------| | |
| 130 | | HTTP | ** | 80 | xxx.xxx.xxx.xxx | TRUE | | |
| 131 | | HTTPS | ** | 443 | xxx.xxx.xxx.xxx | TRUE | | |
| 141 | 132 | |
| 142 | 133 | Once configured, these rules will direct all web traffic to your reverse |
| 143 | 134 | proxy. |
| 144 | 135 | |
| 145 | ### Step 3: Nginx Installation | |
| 146 | ||
| 136 | ** Step 3: Nginx Installation | |
| 147 | 137 | To install Nginx, simply run the following command: |
| 148 | 138 | |
| 149 | ```sh | |
| 139 | #+begin_src sh | |
| 150 | 140 | sudo apt install nginx |
| 151 | ``` | |
| 141 | #+end_src | |
| 152 | 142 | |
| 153 | If you have a firewall enabled, open up ports `80` and | |
| 154 | `443` on your server so that Nginx can accept web traffic | |
| 155 | from the router. | |
| 143 | If you have a firewall enabled, open up ports =80= and =443= on your | |
| 144 | server so that Nginx can accept web traffic from the router. | |
| 156 | 145 | |
| 157 | For example, if you want to use `ufw` for web traffic and | |
| 158 | SSH, run the following commands: | |
| 146 | For example, if you want to use =ufw= for web traffic and SSH, run the | |
| 147 | following commands: | |
| 159 | 148 | |
| 160 | ```sh | |
| 149 | #+begin_src sh | |
| 161 | 150 | sudo ufw allow 'Nginx Full' |
| 162 | 151 | sudo ufw allow SSH |
| 163 | 152 | sudo ufw enable |
| 164 | ``` | |
| 165 | ||
| 166 | ### Step 4: Nginx Configuration | |
| 153 | #+end_src | |
| 167 | 154 | |
| 155 | ** Step 4: Nginx Configuration | |
| 168 | 156 | Now that we have domains pointing toward the server, the only step left |
| 169 | 157 | is to configure the reverse proxy to direct traffic from domains to |
| 170 | 158 | local services. |
| 171 | 159 | |
| 172 | 160 | To start, you'll need to create a configuration file for each domain in |
| 173 | `/etc/nginx/sites-available/`. They will look identical | |
| 174 | except for the `server_name` variable and the | |
| 175 | `proxy_pass` port. | |
| 161 | =/etc/nginx/sites-available/=. They will look identical except for the | |
| 162 | =server_name= variable and the =proxy_pass= port. | |
| 176 | 163 | |
| 177 | 164 | Dashy: |
| 178 | 165 | |
| 179 | ```sh | |
| 166 | #+begin_src sh | |
| 180 | 167 | nano /etc/nginx/sites-available/dashy.example.com |
| 181 | ``` | |
| 168 | #+end_src | |
| 182 | 169 | |
| 183 | ```config | |
| 170 | #+begin_src config | |
| 184 | 171 | server { |
| 185 | 172 | listen 80; |
| 186 | 173 | server_name dashy.example.com; |
| @@ -189,15 +176,15 @@ server { | ||
| 189 | 176 | proxy_pass http://localhost:4000; |
| 190 | 177 | } |
| 191 | 178 | } |
| 192 | ``` | |
| 179 | #+end_src | |
| 193 | 180 | |
| 194 | 181 | Uptime: |
| 195 | 182 | |
| 196 | ```sh | |
| 183 | #+begin_src sh | |
| 197 | 184 | nano /etc/nginx/sites-available/uptime.example.com |
| 198 | ``` | |
| 185 | #+end_src | |
| 199 | 186 | |
| 200 | ```config | |
| 187 | #+begin_src config | |
| 201 | 188 | server { |
| 202 | 189 | listen 80; |
| 203 | 190 | server_name uptime.example.com; |
| @@ -206,29 +193,28 @@ server { | ||
| 206 | 193 | proxy_pass http://localhost:3001; |
| 207 | 194 | } |
| 208 | 195 | } |
| 209 | ``` | |
| 196 | #+end_src | |
| 210 | 197 | |
| 211 | 198 | Once the configuration files are created, you will need to enable them |
| 212 | with the `symlink` command: | |
| 199 | with the =symlink= command: | |
| 213 | 200 | |
| 214 | ```sh | |
| 201 | #+begin_src sh | |
| 215 | 202 | sudo ln -s /etc/nginx/sites-available/dashy.example.com /etc/nginx/sites-enabled/ |
| 216 | ``` | |
| 203 | #+end_src | |
| 217 | 204 | |
| 218 | 205 | Voilà! Your local services should now be available through their URLs. |
| 219 | 206 | |
| 220 | ## HTTPS with Certbot | |
| 221 | ||
| 207 | * HTTPS with Certbot | |
| 222 | 208 | If you've followed along, you'll notice that your services are only |
| 223 | 209 | available via HTTP (not HTTPS). |
| 224 | 210 | |
| 225 | 211 | If you want to enable HTTPS for your new domains, you will need to |
| 226 | 212 | generate SSL/TLS certificates for them. The easiest way to generate |
| 227 | certificates on Nginx is [Certbot](https://certbot.eff.org): | |
| 213 | certificates on Nginx is [[https://certbot.eff.org][Certbot]]: | |
| 228 | 214 | |
| 229 | ```sh | |
| 215 | #+begin_src sh | |
| 230 | 216 | sudo apt install snapd; sudo snap install core; sudo snap refresh core |
| 231 | 217 | sudo snap install --classic certbot |
| 232 | 218 | sudo ln -s /snap/bin/certbot /usr/bin/certbot |
| 233 | 219 | sudo certbot --nginx |
| 234 | ``` | |
| 220 | #+end_src | |
content/blog/2022-11-11-nginx-tmp-errors.md → blog/nginx-tmp-errors/index.org renamed +31 −35
| @@ -1,14 +1,12 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-11-11 | |
| 3 | title = "Fixing Permission Errors in /var/lib/nginx" | |
| 4 | description = "Learn how to fix permission errors related to the Nginx temporary file storage." | |
| 5 | +++ | |
| 1 | #+title: Fixing Permission Errors in /var/lib/nginx | |
| 2 | #+date: 2022-11-11 | |
| 3 | #+description: Learn how to fix permission errors related to the Nginx temporary file storage. | |
| 4 | #+filetags: :nginx: | |
| 6 | 5 | |
| 7 | *This is a brief post so that I personally remember the solution as it | |
| 8 | has occurred multiple times for me.* | |
| 9 | ||
| 10 | ## The Problem | |
| 6 | /This is a brief post so that I personally remember the solution as it | |
| 7 | has occurred multiple times for me./ | |
| 11 | 8 | |
| 9 | * The Problem | |
| 12 | 10 | After migrating to a new server OS, I started receiving quite a few |
| 13 | 11 | permission errors like the one below. These popped up for various |
| 14 | 12 | different websites I'm serving via Nginx on this server, but did not |
| @@ -16,46 +14,44 @@ prevent the website from loading. | ||
| 16 | 14 | |
| 17 | 15 | I found the errors in the standard log file: |
| 18 | 16 | |
| 19 | ```sh | |
| 17 | #+begin_src sh | |
| 20 | 18 | cat /var/log/nginx/error.log |
| 21 | ``` | |
| 19 | #+end_src | |
| 22 | 20 | |
| 23 | ```sh | |
| 21 | #+begin_src sh | |
| 24 | 22 | 2022/11/11 11:30:34 [crit] 8970#8970: *10 open() "/var/lib/nginx/tmp/proxy/3/00/0000000003" failed (13: Permission denied) while reading upstream, client: 169.150.203.10, server: cyberchef.example.com, request: "GET /assets/main.css HTTP/2.0", upstream: "http://127.0.0.1:8111/assets/main.css", host: "cyberchef.example.com", referrer: "https://cyberchef.example.com/" |
| 25 | ``` | |
| 23 | #+end_src | |
| 26 | 24 | |
| 27 | You can see that the error is `13: Permission denied` and it | |
| 28 | occurs in the `/var/lib/nginx/tmp/` directory. In my case, I | |
| 29 | had thousands of errors where Nginx was denied permission to read/write | |
| 30 | files in this directory. | |
| 25 | You can see that the error is =13: Permission denied= and it occurs in | |
| 26 | the =/var/lib/nginx/tmp/= directory. In my case, I had thousands of | |
| 27 | errors where Nginx was denied permission to read/write files in this | |
| 28 | directory. | |
| 31 | 29 | |
| 32 | 30 | So how do I fix it? |
| 33 | 31 | |
| 34 | ## The Solution | |
| 35 | ||
| 36 | In order to resolve the issue, I had to ensure the | |
| 37 | `/var/lib/nginx` directory is owned by Nginx. Mine was owned | |
| 38 | by the `www` user and Nginx was not able to read or write | |
| 39 | files within that directory. This prevented Nginx from caching temporary | |
| 40 | files. | |
| 32 | * The Solution | |
| 33 | In order to resolve the issue, I had to ensure the =/var/lib/nginx= | |
| 34 | directory is owned by Nginx. Mine was owned by the =www= user and Nginx | |
| 35 | was not able to read or write files within that directory. This | |
| 36 | prevented Nginx from caching temporary files. | |
| 41 | 37 | |
| 42 | ```sh | |
| 38 | #+begin_src sh | |
| 43 | 39 | # Alpine Linux |
| 44 | 40 | doas chown -R nginx:nginx /var/lib/nginx |
| 45 | 41 | |
| 46 | 42 | # Other Distros |
| 47 | 43 | sudo chown -R nginx:nginx /var/lib/nginx |
| 48 | ``` | |
| 44 | #+end_src | |
| 49 | 45 | |
| 50 | You *may* also be able to change the `proxy_temp_path` in | |
| 51 | your Nginx config, but I did not try this. Here's a suggestion I found | |
| 52 | online that may work if the above solution does not: | |
| 46 | You /may/ also be able to change the =proxy_temp_path= in your Nginx | |
| 47 | config, but I did not try this. Here's a suggestion I found online that | |
| 48 | may work if the above solution does not: | |
| 53 | 49 | |
| 54 | ```sh | |
| 50 | #+begin_src sh | |
| 55 | 51 | nano /etc/nginx/http.d/example.com.conf |
| 56 | ``` | |
| 52 | #+end_src | |
| 57 | 53 | |
| 58 | ```conf | |
| 54 | #+begin_src conf | |
| 59 | 55 | server { |
| 60 | 56 | ... |
| 61 | 57 | |
| @@ -65,15 +61,15 @@ server { | ||
| 65 | 61 | |
| 66 | 62 | ... |
| 67 | 63 | } |
| 68 | ``` | |
| 64 | #+end_src | |
| 69 | 65 | |
| 70 | 66 | Finally, restart Nginx and your server should be able to cache temporary |
| 71 | 67 | files again. |
| 72 | 68 | |
| 73 | ```sh | |
| 69 | #+begin_src sh | |
| 74 | 70 | # Alpine Linux (OpenRC) |
| 75 | 71 | doas rc-service nginx restart |
| 76 | 72 | |
| 77 | 73 | # Other Distros (systemd) |
| 78 | 74 | sudo systemctl restart nginx |
| 79 | ``` | |
| 75 | #+end_src | |
content/blog/2022-12-07-nginx-wildcard-redirect.md → blog/nginx-wildcard-redirect/index.org renamed +30 −36
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-12-07 | |
| 3 | title = "Redirect Nginx Subdomains & Trailing Content with Regex" | |
| 4 | description = "A simple Nginx configuration to redirect all subdomains and trailing content." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Problem | |
| 1 | #+title: Redirect Nginx Subdomains & Trailing Content with Regex | |
| 2 | #+date: 2022-12-07 | |
| 3 | #+description: A simple Nginx configuration to redirect all subdomains and trailing content. | |
| 4 | #+filetags: :nginx: | |
| 8 | 5 | |
| 6 | * Problem | |
| 9 | 7 | I recently migrated domains and replaced the old webpage with a simple |
| 10 | 8 | info page with instructions to users on how to edit their bookmarks and |
| 11 | 9 | URLs to get to the page they were seeking. |
| @@ -13,13 +11,12 @@ URLs to get to the page they were seeking. | ||
| 13 | 11 | This was not ideal as it left the work up to the user and may have |
| 14 | 12 | caused friction for users who accessed my RSS feed. |
| 15 | 13 | |
| 16 | ## Solution | |
| 17 | ||
| 14 | * Solution | |
| 18 | 15 | Instead, I finally found a solution that allows me to redirect both |
| 19 | 16 | subdomains AND trailing content. For example, both of these URLs now |
| 20 | 17 | redirect properly using the logic I'll explain below: |
| 21 | 18 | |
| 22 | ```txt | |
| 19 | #+begin_src txt | |
| 23 | 20 | # Example 1 - Simple base domain redirect with trailing content |
| 24 | 21 | https://domain1.com/blog/alpine-linux/ -> https://domain2.com/blog/alpine-linux/ |
| 25 | 22 | |
| @@ -27,23 +24,22 @@ https://domain1.com/blog/alpine-linux/ -> https://domain2.com/blog/alpine-linux/ | ||
| 27 | 24 | https://libreddit.domain1.com/r/history/comments/7z8cbg/new_discovery_mode_turns_video_game_assassins/ |
| 28 | 25 | -> |
| 29 | 26 | https://libreddit.domain2.com/r/history/comments/7z8cbg/new_discovery_mode_turns_video_game_assassins/ |
| 30 | ``` | |
| 27 | #+end_src | |
| 31 | 28 | |
| 32 | 29 | Go ahead, try the URLs if you want to test them. |
| 33 | 30 | |
| 34 | ### Nginx Config | |
| 35 | ||
| 31 | ** Nginx Config | |
| 36 | 32 | To make this possible. I needed to configure a proper redirect scheme in |
| 37 | 33 | my Nginx configuration. |
| 38 | 34 | |
| 39 | ```sh | |
| 35 | #+begin_src sh | |
| 40 | 36 | doas nano /etc/nginx/http.d/domain1.conf |
| 41 | ``` | |
| 37 | #+end_src | |
| 42 | 38 | |
| 43 | 39 | Within this file, I had one block configured to redirect HTTP requests |
| 44 | 40 | to HTTPS for the base domain and all subdomains. |
| 45 | 41 | |
| 46 | ```conf | |
| 42 | #+begin_src conf | |
| 47 | 43 | server { |
| 48 | 44 | listen [::]:80; |
| 49 | 45 | listen 80; |
| @@ -59,14 +55,14 @@ server { | ||
| 59 | 55 | |
| 60 | 56 | return 404; |
| 61 | 57 | } |
| 62 | ``` | |
| 58 | #+end_src | |
| 63 | 59 | |
| 64 | For the base domain, I have another `server` block dedicated | |
| 65 | to redirecting all base domain requests. You can see that the | |
| 66 | `rewrite` line is instructing Nginx to gather all trailing | |
| 67 | content and append it to the new `domain2.com` URL. | |
| 60 | For the base domain, I have another =server= block dedicated to | |
| 61 | redirecting all base domain requests. You can see that the =rewrite= | |
| 62 | line is instructing Nginx to gather all trailing content and append it | |
| 63 | to the new =domain2.com= URL. | |
| 68 | 64 | |
| 69 | ```conf | |
| 65 | #+begin_src conf | |
| 70 | 66 | server { |
| 71 | 67 | listen [::]:443 ssl http2; |
| 72 | 68 | listen 443 ssl http2; |
| @@ -78,23 +74,21 @@ server { | ||
| 78 | 74 | ssl_certificate /etc/letsencrypt/live/domain1.com/fullchain.pem; |
| 79 | 75 | ssl_certificate_key /etc/letsencrypt/live/domain1.com/privkey.pem; |
| 80 | 76 | } |
| 81 | ``` | |
| 77 | #+end_src | |
| 82 | 78 | |
| 83 | 79 | Finally, the tricky part is figuring out how to tell Nginx to redirect |
| 84 | 80 | while keeping both a subdomain and trailing content intact. I found that |
| 85 | the easiest way to do this is to give it a `server` block of | |
| 86 | its own. | |
| 81 | the easiest way to do this is to give it a =server= block of its own. | |
| 87 | 82 | |
| 88 | Within this block, we need to do some regex on the | |
| 89 | `server_name` line before we can rewrite anything. This | |
| 90 | creates a variable called `subdomain`. | |
| 83 | Within this block, we need to do some regex on the =server_name= line | |
| 84 | before we can rewrite anything. This creates a variable called | |
| 85 | =subdomain=. | |
| 91 | 86 | |
| 92 | Once the server gets to the `rewrite` line, it pulls the | |
| 93 | `subdomain` variable from above and uses it on the new | |
| 94 | `domain2.com` domain before appending the trailing content | |
| 95 | (`$request_uri`). | |
| 87 | Once the server gets to the =rewrite= line, it pulls the =subdomain= | |
| 88 | variable from above and uses it on the new =domain2.com= domain before | |
| 89 | appending the trailing content (=$request_uri=). | |
| 96 | 90 | |
| 97 | ```conf | |
| 91 | #+begin_src conf | |
| 98 | 92 | server { |
| 99 | 93 | listen [::]:443 ssl http2; |
| 100 | 94 | listen 443 ssl http2; |
| @@ -106,14 +100,14 @@ server { | ||
| 106 | 100 | ssl_certificate /etc/letsencrypt/live/domain1.com/fullchain.pem; |
| 107 | 101 | ssl_certificate_key /etc/letsencrypt/live/domain1.com/privkey.pem; |
| 108 | 102 | } |
| 109 | ``` | |
| 103 | #+end_src | |
| 110 | 104 | |
| 111 | 105 | That's all there is to it. With this, I simply restarted Nginx and |
| 112 | 106 | watched the redirections work in-action. |
| 113 | 107 | |
| 114 | ```sh | |
| 108 | #+begin_src sh | |
| 115 | 109 | doas rc-service nginx restart |
| 116 | ``` | |
| 110 | #+end_src | |
| 117 | 111 | |
| 118 | 112 | Looking back on it, I wish I had done this sooner. Who knows how many |
| 119 | 113 | people went looking for my sites or bookmarks and gave up when they saw |
content/blog/2022-06-04-njalla-dns-api.md → blog/njalla-dns-api/index.org renamed +55 −67
| @@ -1,15 +1,13 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-02-10 | |
| 3 | title = "Dynamic DNS with Njalla API" | |
| 4 | description = "Learn how to dynamically update DNS records for changing IPs with Njalla." | |
| 5 | +++ | |
| 1 | #+title: Dynamic DNS with Njalla API | |
| 2 | #+date: 2022-02-10 | |
| 3 | #+description: Learn how to dynamically update DNS records for changing IPs with Njalla. | |
| 4 | #+filetags: :sysadmin: | |
| 6 | 5 | |
| 7 | ## Njalla's API | |
| 8 | ||
| 9 | As noted in my recent post about [switching to Njalla from | |
| 10 | Cloudflare](/blog/ditching-cloudflare/), I was searching for a | |
| 11 | way to replace my very easy-to-use bash script to [update Cloudflare's | |
| 12 | DNS via their API](/blog/cloudflare-dns-api/). | |
| 6 | * Njalla's API | |
| 7 | As noted in my recent post about [[/blog/ditching-cloudflare/][switching | |
| 8 | to Njalla from Cloudflare]], I was searching for a way to replace my | |
| 9 | very easy-to-use bash script to [[/blog/cloudflare-dns-api/][update | |
| 10 | Cloudflare's DNS via their API]]. | |
| 13 | 11 | |
| 14 | 12 | To reiterate what I said in those posts, this is a common necessity for |
| 15 | 13 | those of us who have non-static IP addresses that can change at any |
| @@ -22,88 +20,81 @@ update their domain's DNS records if it changes. | ||
| 22 | 20 | This post explains how to use Python to update Njalla's DNS records |
| 23 | 21 | whenever a machine's public IP address changes. |
| 24 | 22 | |
| 25 | ### Creating a Token | |
| 26 | ||
| 23 | ** Creating a Token | |
| 27 | 24 | To use Njalla's API, you will first need to create a token that will be |
| 28 | 25 | used to authenticate you every time you call the API. Luckily, this is |
| 29 | 26 | very easy to do if you have an account with Njalla. |
| 30 | 27 | |
| 31 | Simply go the [API Settings](https://njal.la/settings/api/) page and | |
| 32 | click the `Add Token` button. Next, enter a name for the | |
| 33 | token and click `Add`. | |
| 28 | Simply go the [[https://njal.la/settings/api/][API Settings]] page and | |
| 29 | click the =Add Token= button. Next, enter a name for the token and click | |
| 30 | =Add=. | |
| 34 | 31 | |
| 35 | Finally, click the `Manage` button next to your newly created | |
| 36 | token and copy the `API Token` field. | |
| 37 | ||
| 38 | ### Finding the Correct API Request | |
| 32 | Finally, click the =Manage= button next to your newly created token and | |
| 33 | copy the =API Token= field. | |
| 39 | 34 | |
| 35 | ** Finding the Correct API Request | |
| 40 | 36 | Once you have a token, you're ready to call the Njalla API for any |
| 41 | 37 | number of requests. For a full listing of available requests, see the |
| 42 | [Njalla API Documentation](https://njal.la/api/). | |
| 38 | [[https://njal.la/api/][Njalla API Documentation]]. | |
| 43 | 39 | |
| 44 | For this demo, we are using the `list-records` and | |
| 45 | `edit-record` requests. | |
| 40 | For this demo, we are using the =list-records= and =edit-record= | |
| 41 | requests. | |
| 46 | 42 | |
| 47 | The `list-records` request requires the following payload to | |
| 48 | be sent when calling the API: | |
| 43 | The =list-records= request requires the following payload to be sent | |
| 44 | when calling the API: | |
| 49 | 45 | |
| 50 | ```txt | |
| 46 | #+begin_src txt | |
| 51 | 47 | params: { |
| 52 | 48 | domain: string |
| 53 | 49 | } |
| 54 | ``` | |
| 50 | #+end_src | |
| 55 | 51 | |
| 56 | The `edit-record` request requires the following payload to | |
| 57 | be sent when calling the API: | |
| 52 | The =edit-record= request requires the following payload to be sent when | |
| 53 | calling the API: | |
| 58 | 54 | |
| 59 | ```txt | |
| 55 | #+begin_src txt | |
| 60 | 56 | params: { |
| 61 | 57 | domain: string |
| 62 | 58 | id: int |
| 63 | 59 | content: string |
| 64 | 60 | } |
| 65 | ``` | |
| 66 | ||
| 67 | ## Server Set-Up | |
| 61 | #+end_src | |
| 68 | 62 | |
| 63 | * Server Set-Up | |
| 69 | 64 | To create this script, we will be using Python. By default, I use Python |
| 70 | 65 | 3 on my servers, so please note that I did not test this in Python 2, |
| 71 | 66 | and I do not know if Python 2 will work for this. |
| 72 | 67 | |
| 73 | ### Creating the Script | |
| 74 | ||
| 68 | ** Creating the Script | |
| 75 | 69 | First, find a suitable place to create your script. Personally, I just |
| 76 | create a directory called `ddns` in my home directory: | |
| 70 | create a directory called =ddns= in my home directory: | |
| 77 | 71 | |
| 78 | ```sh | |
| 72 | #+begin_src sh | |
| 79 | 73 | mkdir ~/ddns |
| 80 | ``` | |
| 74 | #+end_src | |
| 81 | 75 | |
| 82 | 76 | Next, create a Python script file: |
| 83 | 77 | |
| 84 | ```sh | |
| 78 | #+begin_src sh | |
| 85 | 79 | nano ~/ddns/ddns.py |
| 86 | ``` | |
| 80 | #+end_src | |
| 87 | 81 | |
| 88 | 82 | The following code snippet is quite long, so I won't go into depth on |
| 89 | 83 | each part. However, I suggest you read through the entire script before |
| 90 | 84 | running it; it is quite simple and contains comments to help explain |
| 91 | 85 | each code block. |
| 92 | 86 | |
| 93 | :warning: **Note**: You will need to update the following variables for | |
| 87 | :warning: *Note*: You will need to update the following variables for | |
| 94 | 88 | this to work: |
| 95 | 89 | |
| 96 | - `token`: This is the Njalla API token you created | |
| 97 | earlier. | |
| 98 | - `user_domain`: This is the top-level domain you want to | |
| 99 | modify. | |
| 100 | - `include_subdomains`: Set this to `True` if | |
| 101 | you also want to modify subdomains found under the TLD. | |
| 102 | - `subdomains`: If `include_subdomains` = | |
| 103 | `True`, you can include your list of subdomains to be | |
| 104 | modified here. | |
| 105 | ||
| 106 | ```python | |
| 90 | - =token=: This is the Njalla API token you created earlier. | |
| 91 | - =user_domain=: This is the top-level domain you want to modify. | |
| 92 | - =include_subdomains=: Set this to =True= if you also want to modify | |
| 93 | subdomains found under the TLD. | |
| 94 | - =subdomains=: If =include_subdomains= = =True=, you can include your | |
| 95 | list of subdomains to be modified here. | |
| 96 | ||
| 97 | #+begin_src python | |
| 107 | 98 | #!/usr/bin/python |
| 108 | 99 | # -*- coding: utf-8 -*- |
| 109 | 100 | # Import Python modules |
| @@ -182,30 +173,27 @@ for record in data['records']: | ||
| 182 | 173 | 'does not match Njalla's value of', |
| 183 | 174 | record['content'], '. Updating...') |
| 184 | 175 | update_record(user_domain, record['id'], ipv6) |
| 185 | ``` | |
| 186 | ||
| 187 | ### Running the Script | |
| 176 | #+end_src | |
| 188 | 177 | |
| 178 | ** Running the Script | |
| 189 | 179 | Once you've created the script and are ready to test it, run the |
| 190 | 180 | following command: |
| 191 | 181 | |
| 192 | ```sh | |
| 182 | #+begin_src sh | |
| 193 | 183 | python3 ~/ddns/ddns.py |
| 194 | ``` | |
| 195 | ||
| 196 | ### Setting the Script to Run Automatically | |
| 184 | #+end_src | |
| 197 | 185 | |
| 198 | To make sure the scripts run automatically, add it to the | |
| 199 | `cron` file so that it will run on a schedule. To do this, | |
| 200 | open the `cron` file: | |
| 186 | ** Setting the Script to Run Automatically | |
| 187 | To make sure the scripts run automatically, add it to the =cron= file so | |
| 188 | that it will run on a schedule. To do this, open the =cron= file: | |
| 201 | 189 | |
| 202 | ```sh | |
| 190 | #+begin_src sh | |
| 203 | 191 | crontab -e |
| 204 | ``` | |
| 192 | #+end_src | |
| 205 | 193 | |
| 206 | 194 | In the cron file, paste the following at the bottom of the editor in |
| 207 | 195 | order to check the IP every five minutes: |
| 208 | 196 | |
| 209 | ```sh | |
| 210 | */5 * * * * python3 /home/<your_username>/ddns/ddns.py | |
| 211 | ``` | |
| 197 | #+begin_src sh | |
| 198 | ,*/5 ** ** ** ** python3 /home/<your_username>/ddns/ddns.py | |
| 199 | #+end_src | |
blog/org-blog/index.org added +71
| @@ -0,0 +1,71 @@ | ||
| 1 | #+title: Blogging in Org-Mode | |
| 2 | #+date: 2024-02-26 | |
| 3 | #+description: A guide to blogging with org-mode, no third-party tools required. | |
| 4 | #+filetags: :dev: | |
| 5 | ||
| 6 | * TODO Write a post on emacs first? | |
| 7 | ||
| 8 | - Could write-up my Doom Emacs config and workflow first, then reference here. | |
| 9 | ||
| 10 | * TODO Configure Emacs | |
| 11 | ||
| 12 | #+begin_src sh | |
| 13 | emacs -nw | |
| 14 | #+end_src | |
| 15 | ||
| 16 | =SPC f f= ---> =~/.doom.d/config.el= | |
| 17 | ||
| 18 | #+begin_src lisp | |
| 19 | ;; org-publish | |
| 20 | (require 'ox-publish) | |
| 21 | ||
| 22 | (setq org-publish-project-alist | |
| 23 | `(("blog" | |
| 24 | :base-directory "~/Source/cleberg.net/" | |
| 25 | :base-extension "org" | |
| 26 | :recursive t | |
| 27 | :publishing-directory "~/Source/cleberg.net/public/" | |
| 28 | :publishing-function org-html-publish-to-html | |
| 29 | ;; HTML5 | |
| 30 | :html-doctype "html5" | |
| 31 | :html-html5-fancy t | |
| 32 | ;; Disable some Org's HTML defaults | |
| 33 | :html-head-include-scripts nil | |
| 34 | :html-head-include-default-style nil | |
| 35 | :section-numbers nil | |
| 36 | :with-title nil | |
| 37 | ;; Generate sitemap | |
| 38 | :auto-sitemap t | |
| 39 | :sitemap-filename "sitemap.org" | |
| 40 | ;; Customize HTML output | |
| 41 | :html-divs ((preamble "header" "preamble") | |
| 42 | (content "main" "content") | |
| 43 | (postamble "footer" "postamble")) | |
| 44 | :html-head "<link rel='stylesheet' href='/styles.css' type='text/css'>" | |
| 45 | :html-preamble "<nav class='site-nav' aria-label='site-nav' role='navigation'> | |
| 46 | <ul> | |
| 47 | <li><a href='/'>Home</a></li> | |
| 48 | <li><a href='/blog/'>Blog</a></li> | |
| 49 | <li><a href='/services/'>Services</a></li> | |
| 50 | <li><a href='/wiki/'>Wiki</a></li> | |
| 51 | </ul></nav> | |
| 52 | <h1>%t</h1> | |
| 53 | <time datetime='%d'>%d</time>" | |
| 54 | :html-postamble " | |
| 55 | <p>Last build: %T</p> | |
| 56 | <p>Created with %c</p>" | |
| 57 | ) | |
| 58 | ||
| 59 | ("static" | |
| 60 | :base-directory "~/Source/cleberg.net/static/" | |
| 61 | :base-extension "css\\|txt\\|jpg\\|gif\\|png" | |
| 62 | :recursive t | |
| 63 | :publishing-directory "~/Source/cleberg.net/public/" | |
| 64 | :publishing-function org-publish-attachment) | |
| 65 | ||
| 66 | ("cleberg.net" :components ("blog" "static")))) | |
| 67 | #+end_src | |
| 68 | ||
| 69 | * TODO Build Process | |
| 70 | ||
| 71 | * TODO Deploy Process | |
blog/password-security/index.org added +121
| @@ -0,0 +1,121 @@ | ||
| 1 | #+title: Password Security | |
| 2 | #+date: 2019-12-16 | |
| 3 | #+description: Password security basics. | |
| 4 | #+filetags: :security: | |
| 5 | ||
| 6 | * Users | |
| 7 | ** Why Does It Matter? | |
| 8 | Information security, including passwords and identities, has become one | |
| 9 | of the most important digital highlights of the last decade. With | |
| 10 | [[https://www.usatoday.com/story/money/2018/12/28/data-breaches-2018-billions-hit-growing-number-cyberattacks/2413411002/][billions | |
| 11 | of people affected by data breaches each year]], there's a greater need | |
| 12 | to introduce strong information security systems. If you think you've | |
| 13 | been part of a breach, or you want to check and see, you can use | |
| 14 | [[https://haveibeenpwned.com/][Have I Been Pwned]] to see if your email | |
| 15 | has been involved in any public breaches. Remember that there's a | |
| 16 | possibility that a company experienced a breach and did not report it to | |
| 17 | anyone. | |
| 18 | ||
| 19 | ** How Do I Protect Myself? | |
| 20 | The first place to start with any personal security check-up is to | |
| 21 | gather a list of all the different websites, apps, or programs that | |
| 22 | require you to have login credentials. Optionally, once you know where | |
| 23 | your information is being stored, you can sort the list from the | |
| 24 | most-important items such as banks or government logins to less | |
| 25 | important items such as your favorite meme site. You will want to ensure | |
| 26 | that your critical logins are secure before getting to the others. | |
| 27 | ||
| 28 | Once you think you have a good idea of all your different authentication | |
| 29 | methods, I recommend using a password manager such as | |
| 30 | [[https://bitwarden.com/][Bitwarden]]. Using a password manager allows | |
| 31 | you to automatically save your logins, create randomized passwords, and | |
| 32 | transfer passwords across devices. However, you'll need to memorize your | |
| 33 | "vault password" that allows you to open the password manager. It's | |
| 34 | important to make this something hard to guess since it would allow | |
| 35 | anyone who has it to access every password you've stored in there. | |
| 36 | ||
| 37 | Personally, I recommend using a | |
| 38 | [[https://en.wikipedia.org/wiki/Passphrase][passphrase]] instead of a | |
| 39 | [[https://en.wikipedia.org/wiki/Password][password]] for your vault | |
| 40 | password. Instead of using a string of characters (whether random or | |
| 41 | simple), use a phrase and add in symbols and a number. For example, your | |
| 42 | vault password could be =Racing-Alphabet-Gourd-Parrot3=. Swap the | |
| 43 | symbols out for whichever symbol you want, move the number around, and | |
| 44 | fine-tune the passphrase until you are confident that you can remember | |
| 45 | it whenever necessary. | |
| 46 | ||
| 47 | Once you've stored your passwords, make sure you continually check up on | |
| 48 | your account and make sure you aren't following bad password practices. | |
| 49 | Krebs on Security has a great | |
| 50 | [[https://krebsonsecurity.com/password-dos-and-donts/][blog post on | |
| 51 | password recommendations]]. Any time that a data breach happens, make | |
| 52 | sure you check to see if you were included, and if you need to reset any | |
| 53 | account passwords. | |
| 54 | ||
| 55 | * Developers | |
| 56 | ** What Are the Basic Requirements? | |
| 57 | When developing any password-protected application, there are a few | |
| 58 | basic rules that anyone should follow even if they do not follow any | |
| 59 | official guidelines such as NIST. The foremost practice is to require | |
| 60 | users to use passwords that are at least 8 characters and cannot easily | |
| 61 | be guessed. This sounds extremely simple, but it requires quite a few | |
| 62 | different strategies. First, the application should check the potential | |
| 63 | passwords against a dictionary of insecure passwords such =password=, | |
| 64 | =1234abc=, or =application_name=. | |
| 65 | ||
| 66 | Next, the application should offer guidance on the strength of passwords | |
| 67 | being entered during enrollment. Further, NIST officially recommends | |
| 68 | *not** implementing any composition rules that make passwords hard to | |
| 69 | remember (e.g. passwords with letters, numbers, and special characters) | |
| 70 | and instead encouraging the use of long pass phrases which can include | |
| 71 | spaces. It should be noted that to be able to keep spaces within | |
| 72 | passwords, all unicode characters should be supported, and passwords | |
| 73 | should not be truncated. | |
| 74 | ||
| 75 | ** What Does NIST Recommend? | |
| 76 | The National Institute of Standards and Technology | |
| 77 | ([[https://www.nist.gov][NIST]]) in the US Department of Commerce | |
| 78 | regularly publishes information around information security and digital | |
| 79 | identity guidelines. Recently, NIST published | |
| 80 | [[https://pages.nist.gov/800-63-3/sp800-63b.html][Special Publication | |
| 81 | 800-63b]]: Digital Identity Guidelines and Authentication and Lifecycle | |
| 82 | Management. | |
| 83 | ||
| 84 | #+begin_quote | |
| 85 | A Memorized Secret authenticator - commonly referred to as a password | |
| 86 | or, if numeric, a PIN - is a secret value intended to be chosen and | |
| 87 | memorized by the user. Memorized secrets need to be of sufficient | |
| 88 | complexity and secrecy that it would be impractical for an attacker to | |
| 89 | guess or otherwise discover the correct secret value. A memorized secret | |
| 90 | is something you know. | |
| 91 | ||
| 92 | - NIST Special Publication 800-63B | |
| 93 | #+end_quote | |
| 94 | ||
| 95 | NIST offers a lot of guidance on passwords, but I'm going to highlight | |
| 96 | just a few of the important factors: | |
| 97 | ||
| 98 | - Require passwords to be a minimum of 8 characters (6 characters if | |
| 99 | randomly generated and be generated using an approved random bit | |
| 100 | generator). | |
| 101 | - Compare potential passwords against a list that contains values known | |
| 102 | to be commonly-used, expected, or compromised. | |
| 103 | - Offer guidance on password strength, such as a strength meter. | |
| 104 | - Implement a rate-limiting mechanism to limit the number of failed | |
| 105 | authentication attempts for each user account. | |
| 106 | - Do not require composition rules for passwords and do not require | |
| 107 | passwords to be changed periodically (unless compromised). | |
| 108 | - Allow pasting of user identification and passwords to facilitate the | |
| 109 | use of password managers. | |
| 110 | - Allow users to view the password as it is being entered. | |
| 111 | - Use secure forms of communication and storage, including salting and | |
| 112 | hashing passwords using a one-way key derivation function. | |
| 113 | ||
| 114 | NIST offers further guidance on other devices that require specific | |
| 115 | security policies, querying for passwords, and more. All the information | |
| 116 | discussed so far comes from | |
| 117 | [[https://pages.nist.gov/800-63-3/sp800-63b.html][NIST SP800-63b]] but | |
| 118 | NIST offers a lot of information on digital identities, enrollment, | |
| 119 | identity proofing, authentication, lifecycle management, federation, and | |
| 120 | assertions in the total [[https://pages.nist.gov/800-63-3/][NIST | |
| 121 | SP800-63 Digital Identity Guidelines]]. | |
content/blog/2021-04-28-photography.md → blog/photography/index.org renamed +30 −34
| @@ -1,68 +1,64 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-04-28 | |
| 3 | title = "Jumping Back Into Photography" | |
| 4 | description = "Some thoughts on photography." | |
| 5 | +++ | |
| 1 | #+title: Jumping Back Into Photography | |
| 2 | #+date: 2021-04-28 | |
| 3 | #+description: Some thoughts on photography. | |
| 4 | #+filetags: :personal: | |
| 6 | 5 | |
| 7 | ## Why Photography? | |
| 8 | ||
| 9 | I've often wondered why photography is as enticing as it is. You can | |
| 10 | see billions of people around the world taking photographs every single | |
| 6 | * Why Photography? | |
| 7 | I've often wondered why photography is as enticing as it is. You can see | |
| 8 | billions of people around the world taking photographs every single | |
| 11 | 9 | moment of the day. New technology often boasts about their photographic |
| 12 | 10 | capabilities, especially smartphones. I would even assume that we live |
| 13 | 11 | in a world where there is never a moment in which a photograph is not |
| 14 | 12 | being taken somewhere on Earth. |
| 15 | 13 | |
| 16 | 14 | As for myself, I would simply say that I enjoy preserving a memory in |
| 17 | physical (or digital) form. I've never had the best memory when it | |
| 18 | comes to recalling details of places and people gone by, so it helps to | |
| 19 | have a frame of reference lying around. | |
| 15 | physical (or digital) form. I've never had the best memory when it comes | |
| 16 | to recalling details of places and people gone by, so it helps to have a | |
| 17 | frame of reference lying around. | |
| 20 | 18 | |
| 21 | 19 | Regardless of the reason, I think most people would agree that you |
| 22 | 20 | simply cannot have too many hobbies. |
| 23 | 21 | |
| 24 | ## Older Cameras | |
| 25 | ||
| 22 | * Older Cameras | |
| 26 | 23 | I started playing around with the idea of photography when my family |
| 27 | 24 | purchased a Fujifilm camera for family-specific events. I don't recall |
| 28 | 25 | the specific model, but I do recall it was a point-and-shoot camera |
| 29 | 26 | without an interchangeable lens. However, it was of great value to |
| 30 | someone, like myself, who couldn't afford any other camera. I took | |
| 31 | about 10,000 shots with that camera over a 3-5 year span. Most notably, | |
| 32 | all of my trips to California were documented through this camera. | |
| 27 | someone, like myself, who couldn't afford any other camera. I took about | |
| 28 | 10,000 shots with that camera over a 3-5 year span. Most notably, all of | |
| 29 | my trips to California were documented through this camera. | |
| 33 | 30 | |
| 34 | 31 | When possible, I would borrow my sister's camera, which is a Sony |
| 35 | 32 | SLT-A58. This camera was great and allowed for some of my best early |
| 36 | 33 | shots, especially those taken in Utah's and Nevada's parks. |
| 37 | 34 | |
| 38 | ## My Current Kit | |
| 39 | ||
| 35 | * My Current Kit | |
| 40 | 36 | I've finally come to a point in my life where I have the disposable |
| 41 | 37 | income to invest in a solid photography kit. I played around with the |
| 42 | 38 | idea of a lot of different cameras, different types, new vs used, etc. |
| 43 | Finally, I settled on the [Sony α7 | |
| 44 | III](https://en.wikipedia.org/wiki/Sony_%CE%B17_III). This camera is | |
| 45 | mirror-less and uses a full-frame image sensor at 24 megapixels. I | |
| 46 | don't create large prints, and I am mostly focused on preserving | |
| 47 | memories in high quality for the next 5-10 years with this camera, so | |
| 48 | the specifications here are just perfect for me. | |
| 39 | Finally, I settled on the | |
| 40 | [[https://en.wikipedia.org/wiki/Sony_%CE%B17_III][Sony α7 III]]. This | |
| 41 | camera is mirror-less and uses a full-frame image sensor at 24 | |
| 42 | megapixels. I don't create large prints, and I am mostly focused on | |
| 43 | preserving memories in high quality for the next 5-10 years with this | |
| 44 | camera, so the specifications here are just perfect for me. | |
| 49 | 45 | |
| 50 | 46 | For lenses, I decided to buy two lenses that could carry me through most |
| 51 | 47 | situations: |
| 52 | 48 | |
| 53 | - [Vario-Tessar T\* FE 24-70 mm F4 ZA | |
| 54 | OSS](https://electronics.sony.com/imaging/lenses/full-frame-e-mount/p/sel2470z) | |
| 55 | - [Tamron 70-300mm f4.5-6.3 Di III | |
| 56 | RXD](https://www.tamron-usa.com/product/lenses/a047.html) | |
| 49 | - [[https://electronics.sony.com/imaging/lenses/full-frame-e-mount/p/sel2470z][Vario-Tessar | |
| 50 | T** FE 24-70 mm F4 ZA OSS]] | |
| 51 | - [[https://www.tamron-usa.com/product/lenses/a047.html][Tamron 70-300mm | |
| 52 | f4.5-6.3 Di III RXD]] | |
| 57 | 53 | |
| 58 | In addition, I grabbed a couple [HGX Prime | |
| 59 | 67mm](https://www.promaster.com/Product/6725) protection filters for the | |
| 60 | lenses. | |
| 54 | In addition, I grabbed a couple | |
| 55 | [[https://www.promaster.com/Product/6725][HGX Prime 67mm]] protection | |
| 56 | filters for the lenses. | |
| 61 | 57 | |
| 62 | 58 | As I delve further into photography and pick up more skills, I will most |
| 63 | 59 | likely go back and grab a lens with a higher f-stop value, such as |
| 64 | f/1.8. I toyed with the idea of grabbing a 50 mm at `f/1.8`, | |
| 65 | but decided to keep things in a reasonable price range instead. | |
| 60 | f/1.8. I toyed with the idea of grabbing a 50 mm at =f/1.8=, but decided | |
| 61 | to keep things in a reasonable price range instead. | |
| 66 | 62 | |
| 67 | 63 | Finally, I made sure to buy a photography-specific backpack with a rain |
| 68 | 64 | guard, and the zipper on the back panel, to protect the equipment while |
content/blog/2020-08-29-php-auth-flow.md → blog/php-auth-flow/index.org renamed +35 −42
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-08-29 | |
| 3 | title = "PHP Authentication Flow" | |
| 4 | description = "Learn how to establish and maintain a basic user authentication flow in PHP." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Introduction | |
| 1 | #+title: PHP Authentication Flow | |
| 2 | #+date: 2020-08-29 | |
| 3 | #+description: Learn how to establish and maintain a basic user authentication flow in PHP. | |
| 4 | #+filetags: :dev: | |
| 8 | 5 | |
| 6 | * Introduction | |
| 9 | 7 | When creating websites that will allow users to create accounts, the |
| 10 | 8 | developer always needs to consider the proper authentication flow for |
| 11 | 9 | their app. For example, some developers will utilize an API for |
| @@ -17,7 +15,7 @@ problem of copying and pasting the code from their library's | ||
| 17 | 15 | documentation. For example, here's the code I use to authenticate users |
| 18 | 16 | with the Tumblr OAuth API for my Tumblr client, Vox Populi: |
| 19 | 17 | |
| 20 | ```php | |
| 18 | #+begin_src php | |
| 21 | 19 | // Start the session |
| 22 | 20 | session_start(); |
| 23 | 21 | |
| @@ -38,7 +36,7 @@ $client = new Tumblr\API\Client( | ||
| 38 | 36 | $token, |
| 39 | 37 | $token_secret |
| 40 | 38 | ); |
| 41 | ``` | |
| 39 | #+end_src | |
| 42 | 40 | |
| 43 | 41 | However, developers creating authentication flows from scratch will need |
| 44 | 42 | to think carefully about when to make sure a web page will check the |
| @@ -47,8 +45,7 @@ user's authenticity. | ||
| 47 | 45 | In this article, we're going to look at a simple authentication flow |
| 48 | 46 | using a MySQL database and PHP. |
| 49 | 47 | |
| 50 | # Creating User Accounts | |
| 51 | ||
| 48 | * Creating User Accounts | |
| 52 | 49 | The beginning to any type of user authentication is to create a user |
| 53 | 50 | account. This process can take many formats, but the simplest is to |
| 54 | 51 | accept user input from a form (e.g., username and password) and send it |
| @@ -56,10 +53,10 @@ over to your database. For example, here's a snippet that shows how to | ||
| 56 | 53 | get username and password parameters that would come when a user submits |
| 57 | 54 | a form to your PHP script. |
| 58 | 55 | |
| 59 | **Note**: Ensure that your password column is large enough to hold the | |
| 56 | *Note*: Ensure that your password column is large enough to hold the | |
| 60 | 57 | hashed value (at least 60 characters or longer). |
| 61 | 58 | |
| 62 | ```php | |
| 59 | #+begin_src php | |
| 63 | 60 | // Get the values from the URL |
| 64 | 61 | $username = $_POST['username']; |
| 65 | 62 | $raw_password = $_POST['password']; |
| @@ -92,15 +89,14 @@ if ($conn->query($sql) === TRUE) { | ||
| 92 | 89 | } |
| 93 | 90 | |
| 94 | 91 | $conn->close(); |
| 95 | ``` | |
| 96 | ||
| 97 | # Validate Returning Users | |
| 92 | #+end_src | |
| 98 | 93 | |
| 94 | ** Validate Returning Users | |
| 99 | 95 | To be able to verify that a returning user has a valid username and |
| 100 | 96 | password in your database is as simple as having users fill out a form |
| 101 | 97 | and comparing their inputs to your database. |
| 102 | 98 | |
| 103 | ```php | |
| 99 | #+begin_src php | |
| 104 | 100 | // Query the database for username and password |
| 105 | 101 | // ... |
| 106 | 102 | |
| @@ -111,42 +107,40 @@ if(password_verify($password_input, $hashed_password)) { | ||
| 111 | 107 | |
| 112 | 108 | // Else, Redirect them back to the login page. |
| 113 | 109 | ... |
| 114 | ``` | |
| 110 | #+end_src | |
| 115 | 111 | |
| 116 | # Storing Authentication State | |
| 112 | * Storing Authentication State | |
| 113 | Once you've created the user's account, now you're ready to initialize | |
| 114 | the user's session. *You will need to do this on every page you load | |
| 115 | while the user is logged in.** To do so, simply enter the following code | |
| 116 | snippet: | |
| 117 | 117 | |
| 118 | Once you've created the user's account, now you're ready to | |
| 119 | initialize the user's session. **You will need to do this on every page | |
| 120 | you load while the user is logged in.** To do so, simply enter the | |
| 121 | following code snippet: | |
| 122 | ||
| 123 | ```php | |
| 118 | #+begin_src php | |
| 124 | 119 | session_start(); |
| 125 | ``` | |
| 120 | #+end_src | |
| 126 | 121 | |
| 127 | 122 | Once you've initialized the session, the next step is to store the |
| 128 | 123 | session in a cookie so that you can access it later. |
| 129 | 124 | |
| 130 | ```php | |
| 125 | #+begin_src php | |
| 131 | 126 | setcookie(session_name()); |
| 132 | ``` | |
| 127 | #+end_src | |
| 133 | 128 | |
| 134 | 129 | Now that the session name has been stored, you'll be able to check if |
| 135 | 130 | there's an active session whenever you load a page. |
| 136 | 131 | |
| 137 | ```php | |
| 132 | #+begin_src php | |
| 138 | 133 | if(isset(session_name())) { |
| 139 | 134 | // The session is active |
| 140 | 135 | } |
| 141 | ``` | |
| 142 | ||
| 143 | # Removing User Authentication | |
| 136 | #+end_src | |
| 144 | 137 | |
| 138 | ** Removing User Authentication | |
| 145 | 139 | The next logical step is to give your users the option to log out once |
| 146 | 140 | they are done using your application. This can be tricky in PHP since a |
| 147 | 141 | few of the standard ways do not always work. |
| 148 | 142 | |
| 149 | ```php | |
| 143 | #+begin_src php | |
| 150 | 144 | // Initialize the session. |
| 151 | 145 | // If you are using session_name("something"), don't forget it now! |
| 152 | 146 | session_start(); |
| @@ -178,18 +172,17 @@ session_write_close(); | ||
| 178 | 172 | // Go back to sign-in page |
| 179 | 173 | header('Location: https://example.com/logged-out/'); |
| 180 | 174 | die(); |
| 181 | ``` | |
| 182 | ||
| 183 | # Wrapping Up | |
| 175 | #+end_src | |
| 184 | 176 | |
| 177 | * Wrapping Up | |
| 185 | 178 | Now you should be ready to begin your authentication programming with |
| 186 | 179 | PHP. You can create user accounts, create sessions for users across |
| 187 | 180 | different pages of your site, and then destroy the user data when |
| 188 | 181 | they're ready to leave. |
| 189 | 182 | |
| 190 | For more information on this subject, I recommend reading the [PHP | |
| 191 | Documentation](https://www.php.net/). Specifically, you may want to look | |
| 192 | at [HTTP Authentication with | |
| 193 | PHP](https://www.php.net/manual/en/features.http-auth.php), [session | |
| 194 | handling](https://www.php.net/manual/en/book.session.php), and | |
| 195 | [hash](https://www.php.net/manual/en/function.hash.php). | |
| 183 | For more information on this subject, I recommend reading the | |
| 184 | [[https://www.php.net/][PHP Documentation]]. Specifically, you may want | |
| 185 | to look at [[https://www.php.net/manual/en/features.http-auth.php][HTTP | |
| 186 | Authentication with PHP]], | |
| 187 | [[https://www.php.net/manual/en/book.session.php][session handling]], | |
| 188 | and [[https://www.php.net/manual/en/function.hash.php][hash]]. | |
content/blog/2021-04-23-php-comment-system.md → blog/php-comment-system/index.org renamed +84 −95
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-04-23 | |
| 3 | title = "Roll Your Own Static Commenting System in PHP" | |
| 4 | description = "A simple guide to creating a commenting system in PHP." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## The Terrible-ness of Commenting Systems | |
| 1 | #+title: Roll Your Own Static Commenting System in PHP | |
| 2 | #+date: 2021-04-23 | |
| 3 | #+description: A simple guide to creating a commenting system in PHP. | |
| 4 | #+filetags: :dev: | |
| 8 | 5 | |
| 6 | * The Terrible-ness of Commenting Systems | |
| 9 | 7 | The current state of affairs regarding interactive comment systems is, |
| 10 | 8 | well, terrible. It is especially awful if you're a privacy conscious |
| 11 | 9 | person who does not generally load third-party scripts or frames on the |
| @@ -16,24 +14,23 @@ something that should be standard. | ||
| 16 | 14 | |
| 17 | 15 | Of course, there are some really terrible options: |
| 18 | 16 | |
| 19 | - Facebook Comments | |
| 20 | - Discourse | |
| 17 | - Facebook Comments | |
| 18 | - Discourse | |
| 21 | 19 | |
| 22 | 20 | There are some options that are better but still use too many scripts, |
| 23 | 21 | frames, or social integrations on your web page that could impact some |
| 24 | 22 | users: |
| 25 | 23 | |
| 26 | - Disqus | |
| 27 | - Isso | |
| 28 | - Remark42 | |
| 24 | - Disqus | |
| 25 | - Isso | |
| 26 | - Remark42 | |
| 29 | 27 | |
| 30 | 28 | Lastly, I looked into a few unique ways of generating blog comments, |
| 31 | 29 | such as using Twitter threads or GitHub issues to automatically post |
| 32 | 30 | issues. However, these both rely on external third-party sites that I |
| 33 | 31 | don't currently use. |
| 34 | 32 | |
| 35 | ## Stay Static with Server-Side Comments | |
| 36 | ||
| 33 | * Stay Static with Server-Side Comments | |
| 37 | 34 | The main issue for my personal use-case is that my blog is completely, |
| 38 | 35 | 100% static. I use PHP on the back-end but website visitors only see |
| 39 | 36 | HTML and a single CSS file. No external javascript and no embedded |
| @@ -41,15 +38,14 @@ frames. | ||
| 41 | 38 | |
| 42 | 39 | So, how do we keep a site static and still allow users to interact with |
| 43 | 40 | blog posts? The key actually pretty simple - I'm already using PHP, so |
| 44 | why not rely on the classic HTML `<form>` and a PHP script to | |
| 45 | save the comments somewhere? As it turns out, this was a perfect | |
| 46 | solution for me. | |
| 41 | why not rely on the classic HTML =<form>= and a PHP script to save the | |
| 42 | comments somewhere? As it turns out, this was a perfect solution for me. | |
| 47 | 43 | |
| 48 | 44 | The second issue for my personal use-case is that I am trying to keep |
| 49 | 45 | the contents of my website accessible over time, as described by |
| 50 | @brandur, in his post entitled [Blog with Markdown + Git, and degrade | |
| 51 | gracefully through | |
| 52 | time](https://brandur.org/fragments/graceful-degradation-time) . | |
| 46 | [cite/t:@brandur], in his post entitled | |
| 47 | [[https://brandur.org/fragments/graceful-degradation-time][Blog with | |
| 48 | Markdown + Git, and degrade gracefully through time]] . | |
| 53 | 49 | |
| 54 | 50 | This means I cannot rely on a database for comments, since I do not rely |
| 55 | 51 | on a database for any other part of my websites. |
| @@ -59,35 +55,34 @@ that future readers will be able to see the source data long after I'm | ||
| 59 | 55 | gone, or the website has gone offline. However, I still haven't |
| 60 | 56 | committed any images served on my blog to Git, as I'm not entirely sold |
| 61 | 57 | on Git LFS yet - for now, images can be found at |
| 62 | [img.cleberg.net](https://img.cleberg.net). | |
| 58 | [[https://img.cleberg.net][img.cleberg.net]]. | |
| 63 | 59 | |
| 64 | 60 | Saving my comments back to the Git repository ensures that another |
| 65 | 61 | aspect of my site will degrade gracefully. |
| 66 | 62 | |
| 67 | ## Create a Comment Form | |
| 68 | ||
| 63 | * Create a Comment Form | |
| 69 | 64 | Okay, let's get started. The first step is to create an HTML form that |
| 70 | 65 | users can see and utilize to submit comments. This is fairly easy and |
| 71 | 66 | can be changed depending on your personal preferences. |
| 72 | 67 | |
| 73 | 68 | Take a look at the code block below for the form I currently use. Note |
| 74 | that `<current-url>` is replaced automatically in PHP with | |
| 75 | the current post's URL, so that my PHP script used later will know | |
| 76 | which blog post the comment is related to. | |
| 69 | that =<current-url>= is replaced automatically in PHP with the current | |
| 70 | post's URL, so that my PHP script used later will know which blog post | |
| 71 | the comment is related to. | |
| 77 | 72 | |
| 78 | 73 | The form contains the following structure: |
| 79 | 74 | |
| 80 | 1. `<form>` - This is the form and will determine which PHP | |
| 81 | script to send the comment to. | |
| 82 | 2. `<section hidden>` - This section is hidden from the user | |
| 83 | and is used to ensure that we know which blog post sent the comment. | |
| 84 | 3. `<section>` Display Name (Optional) - Used to accept a | |
| 85 | display name, if entered. | |
| 86 | 4. `<section>` Comment (Required) - Used to accept the | |
| 87 | user's full comment. Markdown is allowed. | |
| 88 | 5. `<button>` - A button to submit the form. | |
| 89 | ||
| 90 | ```html | |
| 75 | 1. =<form>= - This is the form and will determine which PHP script to | |
| 76 | send the comment to. | |
| 77 | 2. =<section hidden>= - This section is hidden from the user and is used | |
| 78 | to ensure that we know which blog post sent the comment. | |
| 79 | 3. =<section>= Display Name (Optional) - Used to accept a display name, | |
| 80 | if entered. | |
| 81 | 4. =<section>= Comment (Required) - Used to accept the user's full | |
| 82 | comment. Markdown is allowed. | |
| 83 | 5. =<button>= - A button to submit the form. | |
| 84 | ||
| 85 | #+begin_src html | |
| 91 | 86 | <form action="/comment.php" method="POST"> |
| 92 | 87 | <h3>Leave a Comment</h3> |
| 93 | 88 | <section hidden> |
| @@ -127,32 +122,30 @@ The form contains the following structure: | ||
| 127 | 122 | </section> |
| 128 | 123 | <button type="submit">Submit</button> |
| 129 | 124 | </form> |
| 130 | ``` | |
| 131 | ||
| 132 | ## Handle Comments via POST | |
| 125 | #+end_src | |
| 133 | 126 | |
| 127 | * Handle Comments via POST | |
| 134 | 128 | Now that we have a form and can submit comments, we need to create a PHP |
| 135 | 129 | script so that the server can fetch the comment data and save it. Make |
| 136 | sure your PHP script name matches the name you entered in the | |
| 137 | `action` field in your form. | |
| 138 | ||
| 139 | See the code block below for the contents of my `comment.php` | |
| 140 | script. We perform the following tasks in this script: | |
| 141 | ||
| 142 | 1. Grab the POST data from the HTML form. | |
| 143 | 2. Sanitize the comment data with `htmlentities`. | |
| 144 | 3. Set the display name to `Anonymous` if it was left blank. | |
| 145 | 4. Create a PHP object that combines all of this data. | |
| 146 | 5. Check if our destination file `comments.json` exists. | |
| 147 | 6. If so, convert the PHP object to JSON and save it to the file. | |
| 148 | 7. If the `comments.json` file does not exist, the script | |
| 149 | will exit with an error. You can alter this to ensure it creates the | |
| 150 | script, but my source code includes the file by default, so it will | |
| 151 | always exist. | |
| 152 | 8. Finally, send the user back to the `#comments` section of | |
| 153 | the blog post they just read. | |
| 154 | ||
| 155 | ```php | |
| 130 | sure your PHP script name matches the name you entered in the =action= | |
| 131 | field in your form. | |
| 132 | ||
| 133 | See the code block below for the contents of my =comment.php= script. We | |
| 134 | perform the following tasks in this script: | |
| 135 | ||
| 136 | 1. Grab the POST data from the HTML form. | |
| 137 | 2. Sanitize the comment data with =htmlentities=. | |
| 138 | 3. Set the display name to =Anonymous= if it was left blank. | |
| 139 | 4. Create a PHP object that combines all of this data. | |
| 140 | 5. Check if our destination file =comments.json= exists. | |
| 141 | 6. If so, convert the PHP object to JSON and save it to the file. | |
| 142 | 7. If the =comments.json= file does not exist, the script will exit with | |
| 143 | an error. You can alter this to ensure it creates the script, but my | |
| 144 | source code includes the file by default, so it will always exist. | |
| 145 | 8. Finally, send the user back to the =#comments= section of the blog | |
| 146 | post they just read. | |
| 147 | ||
| 148 | #+begin_src php | |
| 156 | 149 | // Get the content sent from the comment form |
| 157 | 150 | $comment = htmlentities($_POST['userContent']); |
| 158 | 151 | $post_url = $_POST['postURL']; |
| @@ -187,33 +180,32 @@ if (file_exists($file_name)) { | ||
| 187 | 180 | |
| 188 | 181 | // Send the user back |
| 189 | 182 | header('Location: ' . $post_url . '#comments'); |
| 190 | ``` | |
| 183 | #+end_src | |
| 191 | 184 | |
| 192 | If you're using Apache, make sure the `www-data` user on | |
| 193 | your server has the correct permissions to your website directory or | |
| 194 | else it will not be able to write to `comments.json`. | |
| 185 | If you're using Apache, make sure the =www-data= user on your server has | |
| 186 | the correct permissions to your website directory or else it will not be | |
| 187 | able to write to =comments.json=. | |
| 195 | 188 | |
| 196 | ```sh | |
| 189 | #+begin_src sh | |
| 197 | 190 | chgrp -R www-data /path/to/website/ |
| 198 | 191 | chmod -R g+w comments.json |
| 199 | ``` | |
| 200 | ||
| 201 | ## Display User Comments | |
| 192 | #+end_src | |
| 202 | 193 | |
| 194 | * Display User Comments | |
| 203 | 195 | Now that we can submit comments, and they are saved to the |
| 204 | `comments.json` file, let's make sure we can show those | |
| 205 | comments in each blog post. | |
| 196 | =comments.json= file, let's make sure we can show those comments in each | |
| 197 | blog post. | |
| 206 | 198 | |
| 207 | 199 | The code block below shows the function I use to decode my |
| 208 | `comments.json` file, check if the comments apply to the | |
| 209 | current post, and then display them. | |
| 200 | =comments.json= file, check if the comments apply to the current post, | |
| 201 | and then display them. | |
| 210 | 202 | |
| 211 | This piece of code should **really** be inside a function (or at least | |
| 212 | in an organized PHP workflow). Don't just copy-and-paste and expect it | |
| 213 | to work. You need to at least supply a `$query` variable | |
| 214 | depending on the page visited. | |
| 203 | This piece of code should *really** be inside a function (or at least in | |
| 204 | an organized PHP workflow). Don't just copy-and-paste and expect it to | |
| 205 | work. You need to at least supply a =$query= variable depending on the | |
| 206 | page visited. | |
| 215 | 207 | |
| 216 | ```php | |
| 208 | #+begin_src php | |
| 217 | 209 | $query = 'your-blog-post.html'; |
| 218 | 210 | |
| 219 | 211 | // Load saved comments |
| @@ -245,32 +237,29 @@ foreach ($comments as $comment) { | ||
| 245 | 237 | } |
| 246 | 238 | |
| 247 | 239 | echo $comment_section; |
| 248 | ``` | |
| 249 | ||
| 250 | ## Bonus: Create a 'Recent Comments' Page | |
| 240 | #+end_src | |
| 251 | 241 | |
| 242 | * Bonus: Create a 'Recent Comments' Page | |
| 252 | 243 | Finally, the last part of my current system is to create a Recent |
| 253 | 244 | Comments page so that I can easily check-in on my blog and moderate any |
| 254 | spam. As an alternative, you could use PHP's `mail()` | |
| 255 | function to email you for each blog comment. | |
| 245 | spam. As an alternative, you could use PHP's =mail()= function to email | |
| 246 | you for each blog comment. | |
| 256 | 247 | |
| 257 | 248 | The code to do this is literally the same code as the previous section, |
| 258 | 249 | I just make sure it is printed when someone visits |
| 259 | `https://example.com/comments/`. | |
| 260 | ||
| 261 | ## Possible Enhancements | |
| 250 | =https://example.com/comments/=. | |
| 262 | 251 | |
| 252 | * Possible Enhancements | |
| 263 | 253 | This comment system is by no means a fully-developed system. I have |
| 264 | 254 | noted a few possible enhancements here that I may implement in the |
| 265 | 255 | future: |
| 266 | 256 | |
| 267 | - Create a secure moderator page with user authentication at | |
| 268 | `https://blog.example.com/mod/`. This page could have the | |
| 269 | option to edit or delete any comment found in | |
| 270 | `comments.json`. | |
| 271 | - Create a temporary file, such as `pending_comments.json`, | |
| 272 | that will store newly-submitted comments and won't display on blog | |
| 273 | posts until approved by a moderator. | |
| 274 | - Create a `/modlog/` page with a chronological log, | |
| 275 | showing which moderator approved which comments and why certain | |
| 276 | comments were rejected. | |
| 257 | - Create a secure moderator page with user authentication at | |
| 258 | =https://blog.example.com/mod/=. This page could have the option to | |
| 259 | edit or delete any comment found in =comments.json=. | |
| 260 | - Create a temporary file, such as =pending_comments.json=, that will | |
| 261 | store newly-submitted comments and won't display on blog posts until | |
| 262 | approved by a moderator. | |
| 263 | - Create a =/modlog/= page with a chronological log, showing which | |
| 264 | moderator approved which comments and why certain comments were | |
| 265 | rejected. | |
content/blog/2022-04-09-pinetime.md → blog/pinetime/index.org renamed +59 −70
| @@ -1,44 +1,39 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-04-09 | |
| 3 | title = "PineTime: An Open-Source Smart Watch" | |
| 4 | description = "Playing with the PineTime smart watch." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## PineTime Product Information | |
| 8 | ||
| 9 | ### Overview | |
| 10 | ||
| 11 | The [PineTime](https://www.pine64.org/pinetime/) is an open-source | |
| 12 | smartwatch, created by [PINE64](https://www.pine64.org). Originally | |
| 1 | #+title: PineTime: An Open-Source Smart Watch | |
| 2 | #+date: 2022-04-09 | |
| 3 | #+description: Playing with the PineTime smart watch. | |
| 4 | #+filetags: :hardware: | |
| 5 | ||
| 6 | * PineTime Product Information | |
| 7 | ** Overview | |
| 8 | The [[https://www.pine64.org/pinetime/][PineTime]] is an open-source | |
| 9 | smartwatch, created by [[https://www.pine64.org][PINE64]]. Originally | |
| 13 | 10 | announced in September 2019, this ARM-based watch is a fantastic option |
| 14 | 11 | for users who want the benefits of a modern smartwatch with the backing |
| 15 | 12 | of open-source components and software. |
| 16 | 13 | |
| 17 | ### Product Specifications | |
| 14 | ** Product Specifications | |
| 15 | I won't dive into too many details that you can find on | |
| 16 | [[https://www.pine64.org/pinetime/][the product page]], but I wanted to | |
| 17 | point out the prices for each watch and the primary functions: | |
| 18 | 18 | |
| 19 | I won't dive into too many details that you can find on [the product | |
| 20 | page](https://www.pine64.org/pinetime/), but I wanted to point out the | |
| 21 | prices for each watch and the primary functions: | |
| 19 | 1. Price: | |
| 22 | 20 | |
| 23 | 1. Price: | |
| 21 | - $26.99 (Sealed) | |
| 22 | - $24.99 (Dev Kit) | |
| 23 | - $51.98 (One Sealed + One Dev Kit) | |
| 24 | 24 | |
| 25 | - \$26.99 (Sealed) | |
| 26 | - \$24.99 (Dev Kit) | |
| 27 | - \$51.98 (One Sealed + One Dev Kit) | |
| 25 | 2. Primary Functionality: | |
| 28 | 26 | |
| 29 | 2. Primary Functionality: | |
| 30 | ||
| 31 | - Clock (+ Smartphone Sync) | |
| 32 | - Pedometer | |
| 33 | - Heart Rate Monitor | |
| 34 | - Sleep Monitor | |
| 35 | - Calories burned | |
| 36 | - Messaging | |
| 37 | - Smartphone Notifications | |
| 38 | - Media Controls | |
| 39 | ||
| 40 | ## Unboxing | |
| 27 | - Clock (+ Smartphone Sync) | |
| 28 | - Pedometer | |
| 29 | - Heart Rate Monitor | |
| 30 | - Sleep Monitor | |
| 31 | - Calories burned | |
| 32 | - Messaging | |
| 33 | - Smartphone Notifications | |
| 34 | - Media Controls | |
| 41 | 35 | |
| 36 | * Unboxing | |
| 42 | 37 | Now, my PineTime was ordered on 2022-02-17, shipped on 2022-02-22, and |
| 43 | 38 | was delivered on 2022-03-23. With the current delays on shipping times |
| 44 | 39 | around the world (and the semiconductor shortage), a month for delivery |
| @@ -51,31 +46,29 @@ USB wall adapter). | ||
| 51 | 46 | The watch itself was able to turn on immediately when I pulled it out of |
| 52 | 47 | the box, but the battery was depleted and required charging right away. |
| 53 | 48 | |
| 54 |  | |
| 56 | ||
| 57 | ## Software | |
| 58 | ||
| 59 | ### Watch OS: InfiniTime | |
| 49 | #+caption: PineTime Box Contents | |
| 50 | [[https://img.cleberg.net/blog/20220409-pinetime-smart-watch/pinetime_box_contents.png]] | |
| 60 | 51 | |
| 52 | * Software | |
| 53 | ** Watch OS: InfiniTime | |
| 61 | 54 | While turning on the watch for the first time, some of the main design |
| 62 | 55 | choices you can see in the watch OS, |
| 63 | [InfiniTime](https://wiki.pine64.org/wiki/InfiniTime), are: | |
| 56 | [[https://wiki.pine64.org/wiki/InfiniTime][InfiniTime]], are: | |
| 64 | 57 | |
| 65 | - A square bezel, not too thin against the sides of the watch. | |
| 66 | - A simple, rubber band. | |
| 67 | - Basic font and screen pixel design. | |
| 68 | - Swipe gestures to access other screens. | |
| 58 | - A square bezel, not too thin against the sides of the watch. | |
| 59 | - A simple, rubber band. | |
| 60 | - Basic font and screen pixel design. | |
| 61 | - Swipe gestures to access other screens. | |
| 69 | 62 | |
| 70 |  | |
| 63 | #+caption: PineTime Screens | |
| 64 | [[https://img.cleberg.net/blog/20220409-pinetime-smart-watch/pinetime.png]] | |
| 72 | 65 | |
| 73 | 66 | The OS itself is fantastic in terms of functionality for me. It does |
| 74 | 67 | exactly what a smartwatch should do - track time, steps, heart rates, |
| 75 | 68 | and connect to another smart device, without being overly burdensome to |
| 76 | 69 | the user. |
| 77 | 70 | |
| 78 | My only gripe so far is that it's *really* difficult to swipe to | |
| 71 | My only gripe so far is that it's /really/ difficult to swipe to | |
| 79 | 72 | different screens, such as pulling down the notification tray. I'm not |
| 80 | 73 | sure if this is an OS or hardware issue, but it makes it quite hard to |
| 81 | 74 | quickly move around the screens. |
| @@ -86,46 +79,43 @@ accidentally turn on the screen. With other watches, I absolutely hated | ||
| 86 | 79 | not being able to turn off the raise-to-wake or wave features (i.e., |
| 87 | 80 | blinding myself while wearing a watch at night because I moved my arm). |
| 88 | 81 | |
| 89 | ### iOS App: InfiniLink | |
| 90 | ||
| 82 | ** iOS App: InfiniLink | |
| 91 | 83 | Since I am using iOS as my primary mobile device OS, I am using the |
| 92 | [InfiniLink](https://github.com/xan-m/InfiniLink) app to connect my | |
| 84 | [[https://github.com/xan-m/InfiniLink][InfiniLink]] app to connect my | |
| 93 | 85 | watch. |
| 94 | 86 | |
| 95 | 87 | This app provides the following for PineTime owners: |
| 96 | 88 | |
| 97 | - Firmware updates | |
| 98 | - Steps | |
| 99 | - Charts | |
| 100 | - Notifications | |
| 89 | - Firmware updates | |
| 90 | - Steps | |
| 91 | - Charts | |
| 92 | - Notifications | |
| 101 | 93 | |
| 102 | 94 | I mashed up a few screenshots to show off the home page, menu, firmware |
| 103 | 95 | update, and notification test screens: |
| 104 | 96 | |
| 105 |  | |
| 97 | #+caption: InfiniLink Home | |
| 98 | [[https://img.cleberg.net/blog/20220409-pinetime-smart-watch/infinilink_home.png]] | |
| 107 | 99 | |
| 108 | 100 | Another big feature of InfiniLink is the ability to track pedometer |
| 109 | 101 | steps in a collection of beautiful graphs, with the option to change |
| 110 | 102 | your step goal and add in manual steps. |
| 111 | 103 | |
| 112 |  | |
| 104 | #+caption: InfiniLink Steps | |
| 105 | [[https://img.cleberg.net/blog/20220409-pinetime-smart-watch/infinilink_steps.png]] | |
| 114 | 106 | |
| 115 | 107 | Finally, there are charts to display the battery percentage and heart |
| 116 | 108 | rates over time. This area also comes with an option to clear data. |
| 117 | 109 | |
| 118 |  | |
| 120 | ||
| 121 | ## Final Thoughts | |
| 122 | ||
| 123 | ### Pros | |
| 110 | #+caption: InfiniLink Charts | |
| 111 | [[https://img.cleberg.net/blog/20220409-pinetime-smart-watch/infinilink_charts.png]] | |
| 124 | 112 | |
| 113 | * Final Thoughts | |
| 114 | ** Pros | |
| 125 | 115 | After wearing my watch for a few weeks, I have mostly positive thoughts |
| 126 | 116 | about the watch so far. In the past, I have owned smartwatches by |
| 127 | FitBit, Fossil, Apple, etc. - **but I prefer the PineTime over all of | |
| 128 | those watches**. | |
| 117 | FitBit, Fossil, Apple, etc. - *but I prefer the PineTime over all of | |
| 118 | those watches*. | |
| 129 | 119 | |
| 130 | 120 | The PineTime strips out all the unnecessary features and performs the |
| 131 | 121 | functions that it provides effectively and efficiently. |
| @@ -133,12 +123,11 @@ functions that it provides effectively and efficiently. | ||
| 133 | 123 | The battery life is amazing on this device. By default, the watch seems |
| 134 | 124 | to last anywhere from a few days to a week before dying. |
| 135 | 125 | |
| 136 | And of course, it's open source and backed by some of the most | |
| 137 | dedicated enthusiasts and developers I've seen. Watching the Matrix | |
| 138 | channel, forums, and website have been exciting to see. | |
| 139 | ||
| 140 | ### Cons | |
| 126 | And of course, it's open source and backed by some of the most dedicated | |
| 127 | enthusiasts and developers I've seen. Watching the Matrix channel, | |
| 128 | forums, and website have been exciting to see. | |
| 141 | 129 | |
| 130 | ** Cons | |
| 142 | 131 | If I had to complain about anything, it would simply be the small bugs |
| 143 | 132 | in some features that can be contributed to the companion apps more than |
| 144 | 133 | the watch itself. |
blog/plex-migration/index.org added +230
| @@ -0,0 +1,230 @@ | ||
| 1 | #+title: Migrating Plex to a New Server (& Nvidia Transcoding) | |
| 2 | #+date: 2022-03-08 | |
| 3 | #+description: A retrospective on migrating Plex between servers and enabling Nvidia GPU transcoding. | |
| 4 | #+filetags: :selfhosting: | |
| 5 | ||
| 6 | * Migration Phases | |
| 7 | I recently decided to migrate my server from an old OptiPlex desktop | |
| 8 | machine to a custom-built tower with better hardware in every category. | |
| 9 | In order to do this, I would need to properly migrate a full Plex | |
| 10 | installation. | |
| 11 | ||
| 12 | The second part of this migration is that the new server uses an Nvidia | |
| 13 | GPU and does not have any integrated graphics, which requires extra work | |
| 14 | for installation, but provides much better hardware transcoding options | |
| 15 | for Plex. | |
| 16 | ||
| 17 | Therefore, I have broken this migration down into three phases: | |
| 18 | ||
| 19 | 1. Configure the New Server | |
| 20 | 2. Migrate Plex Data & Devices | |
| 21 | 3. Configure GPU Transcoding | |
| 22 | ||
| 23 | * Phase 1: Configure the New Server | |
| 24 | ** Choosing an OS | |
| 25 | In order to migrate Plex to my new server, I first needed to choose an | |
| 26 | appropriate operating system (OS) and install it on the machine. Given | |
| 27 | that I have encountered numerous issues installing other Linux | |
| 28 | distributions properly with Nvidia graphics, I chose | |
| 29 | [[https://ubuntu.com/download/server][Ubuntu Server]]. | |
| 30 | ||
| 31 | The first step is to create a bootable USB with Ubuntu Server. This is | |
| 32 | easy with [[https://www.balena.io/etcher/][Etcher]], an app that runs on | |
| 33 | many different platforms. Just download the Ubuntu Server =.iso= image, | |
| 34 | launch Etcher, and install the =.iso= on the USB. | |
| 35 | ||
| 36 | Once the USB is created, insert it into my server, reboot, and click | |
| 37 | =Esc= (or any of the =F1-12= keys) until the BIOS menu appears. Finally, | |
| 38 | launch the USB boot drive. | |
| 39 | ||
| 40 | ** Booting with Nvidia | |
| 41 | In order to install Ubuntu Server with an Nvidia Graphics card (and no | |
| 42 | integrated graphics on this device for some reason), you'll have to | |
| 43 | configure the boot menu to allow different graphics drivers to be | |
| 44 | loaded. | |
| 45 | ||
| 46 | When booting from the USB, the machine will launch the initial | |
| 47 | installation menu. From this menu, type =e= to view the default command | |
| 48 | options that come with the device - it's a good idea to take a photo of | |
| 49 | this screen, so you can enter these commands on the next screen (along | |
| 50 | with adding support for Nvidia). | |
| 51 | ||
| 52 | Finally, type =Ctrl + C= to enter the command line. From this command | |
| 53 | line, enter the commands found on the =e= screen. *Remember to add | |
| 54 | =nomodeset= to the =linux ...= line so that your Nvidia device will | |
| 55 | display the installation screens properly!* | |
| 56 | ||
| 57 | Here's an example of the commands I pulled from the =e= screen and | |
| 58 | entered on the command line. | |
| 59 | ||
| 60 | #+begin_src sh | |
| 61 | setparams 'Install Ubuntu Server' | |
| 62 | setgfxpayload=keep | |
| 63 | linux /casper/vmlinuz quiet nomodeset --- | |
| 64 | initrd /casper/initrd | |
| 65 | boot | |
| 66 | #+end_src | |
| 67 | ||
| 68 | #+caption: Ubuntu Server Installation 01 | |
| 69 | [[https://img.cleberg.net/blog/20220308-plex-media-server-migration/ubuntu_server_installation_01.png]] | |
| 70 | ||
| 71 | #+caption: Ubuntu Server Installation 02 | |
| 72 | [[https://img.cleberg.net/blog/20220308-plex-media-server-migration/ubuntu_server_installation_02.png]] | |
| 73 | ||
| 74 | Once the machine is rebooted, enter the =e= screen again and add | |
| 75 | =nomodeset= to the =linux ...= line again and press =Ctrl + X= to save | |
| 76 | the boot options. | |
| 77 | ||
| 78 | The machine is now fully installed and can properly display on an | |
| 79 | external display using the Nvidia GPU. | |
| 80 | ||
| 81 | Always remember to update and upgrade on a new installation: | |
| 82 | ||
| 83 | #+begin_src sh | |
| 84 | sudo apt update; sudo apt upgrade -y; sudo apt autoremove -y | |
| 85 | #+end_src | |
| 86 | ||
| 87 | * Phase 2: Migrate Plex Data & Devices | |
| 88 | This phase uses the great Plex article on migrations | |
| 89 | ([[https://support.plex.tv/articles/201370363-move-an-install-to-another-system/][Move | |
| 90 | an Installation to Another System]]) and adds a bit more information to | |
| 91 | help with commands and context. | |
| 92 | ||
| 93 | ** Terminology | |
| 94 | *Source:** The original server that is being replaced.\\ | |
| 95 | *Destination:** The new server.\\ | |
| 96 | *Client:** Any application that can be used to modify settings for both | |
| 97 | source/destination. | |
| 98 | ||
| 99 | ** Step 01: [Client] Update Settings | |
| 100 | Open up a Plex app and /disable/ the =Account= > =Library= > | |
| 101 | =Empty trash automatically after every scan= preference for the source | |
| 102 | server. | |
| 103 | ||
| 104 | ** Step 02: [Destination] Install Plex | |
| 105 | Open up the [[https://www.plex.tv/media-server-downloads/][Plex Media | |
| 106 | Server download page]] and copy the link for the appropriate platform. | |
| 107 | ||
| 108 | Execute the following commands on the destination server to install | |
| 109 | Plex: | |
| 110 | ||
| 111 | #+begin_src sh | |
| 112 | wget <url> | |
| 113 | sudo dpkg -i <filename> | |
| 114 | sudo systemctl stop plexmediaserver.service | |
| 115 | #+end_src | |
| 116 | ||
| 117 | ** Step 03: [Source] Stop Plex & Migrate Data | |
| 118 | First, stop the Plex service so that no data is created or modified | |
| 119 | during the migration. | |
| 120 | ||
| 121 | #+begin_src sh | |
| 122 | sudo systemctl stop plexmediaserver.service | |
| 123 | #+end_src | |
| 124 | ||
| 125 | Next, copy the data to the new server. To find where the Plex data | |
| 126 | directory is located, Plex has another excellent article available: | |
| 127 | [[https://support.plex.tv/articles/202915258-where-is-the-plex-media-server-data-directory-located/][Where | |
| 128 | is the Plex Media Server data directory located?]]. | |
| 129 | ||
| 130 | There are many ways to copy the data to the new server and will largely | |
| 131 | depend on the size of the folder being copied. Personally, my data | |
| 132 | folder was ~23GB and I opted to simply use the =scp= command to copy the | |
| 133 | files over SSH. | |
| 134 | ||
| 135 | This process was throttled by the old server's slow HDD and ports and | |
| 136 | took approximately 90 minutes to complete. In comparison, moving the | |
| 137 | data from the new server's =home/user/= directory to the | |
| 138 | =/var/.../Plex Media Server= directory took 2-3 minutes. | |
| 139 | ||
| 140 | #+begin_src sh | |
| 141 | scp -r "/var/lib/plexmediaserver/Library/Application Support/Plex Media Server" your_user@xxx.xxx.xxx.xxx:"'/path/to/destination/'" | |
| 142 | #+end_src | |
| 143 | ||
| 144 | ** Step 04: [Destination] Update File Permissions | |
| 145 | In case you move the data directory to a common area on the new server, | |
| 146 | it will have to be moved to the proper location before Plex can function | |
| 147 | properly: | |
| 148 | ||
| 149 | #+begin_src sh | |
| 150 | mv "Plex Media Server" /var/lib/plexmediaserver/Library/Application Support/ | |
| 151 | #+end_src | |
| 152 | ||
| 153 | To ensure permissions were retained properly, the server will need to | |
| 154 | show that all files and folders in the data directory are owned by | |
| 155 | =plex:plex= (or whichever user is running the Plex application). | |
| 156 | ||
| 157 | #+begin_src sh | |
| 158 | sudo chown -R plex:plex "/var/lib/plexmediaserver/Library/Application Support/Plex Media Server" | |
| 159 | #+end_src | |
| 160 | ||
| 161 | Finally, start the service and check the status. | |
| 162 | ||
| 163 | #+begin_src sh | |
| 164 | sudo systemctl start plexmediaserver.service | |
| 165 | sudo systemctl status plexmediaserver.service | |
| 166 | #+end_src | |
| 167 | ||
| 168 | ** Step 05: [Client] Update Libraries & Metadata | |
| 169 | The first step - now that the new server is up and running - is to sign | |
| 170 | out of the client and sign back in. Once this is done, update any | |
| 171 | library locations, if necessary. This was unnecessary in my case since I | |
| 172 | simply moved my storage drives from the source server to the destination | |
| 173 | server. | |
| 174 | ||
| 175 | Next, perform the following actions in the client: | |
| 176 | ||
| 177 | 1. On the left sidebar, click =More= > Three-Dot Menu > | |
| 178 | =Scan Library Files= | |
| 179 | 2. /Enable/ the =Account= > =Library= > | |
| 180 | =Empty trash automatically after every scan= preference for the | |
| 181 | source server. | |
| 182 | 3. On the left sidebar, click =More= > Three-Dot Menu > =Manage Server= | |
| 183 | > =Empty Trash= | |
| 184 | 4. On the left sidebar, click =More= > Three-Dot Menu > =Manage Server= | |
| 185 | > =Clean Bundles= | |
| 186 | 5. On the left sidebar, click =More= > Three-Dot Menu > =Manage Server= | |
| 187 | > =Optimize Database= | |
| 188 | ||
| 189 | Finally, double-check the Remote Access settings to make sure no changes | |
| 190 | have caused issues with accessing the server from outside the network. | |
| 191 | ||
| 192 | In my case, I use a single port forwarding rule in my router and needed | |
| 193 | to update the Local LAN IP Address to the new server IP address. | |
| 194 | ||
| 195 | #+caption: Router port forwarding | |
| 196 | [[https://img.cleberg.net/blog/20220308-plex-media-server-migration/port_forwarding.png]] | |
| 197 | ||
| 198 | * Phase 3: Configure GPU Transcoding | |
| 199 | The final piece to the migration is enabling hardware transcoding so | |
| 200 | that Plex can fully utilize the new Nvidia GPU available in the server. | |
| 201 | The first step is to install Nvidia graphics drivers. This process may | |
| 202 | take a few minutes, but the commands are pretty simple: | |
| 203 | ||
| 204 | #+begin_src sh | |
| 205 | sudo add-apt-repository ppa:graphics-drivers/ppa | |
| 206 | sudo apt update | |
| 207 | sudo apt-get install ubuntu-drivers-common | |
| 208 | sudo ubuntu-drivers autoinstall | |
| 209 | #+end_src | |
| 210 | ||
| 211 | Finally, reboot so that the changes are loaded: | |
| 212 | ||
| 213 | #+begin_src sh | |
| 214 | sudo reboot now | |
| 215 | #+end_src | |
| 216 | ||
| 217 | To ensure that the Nvidia graphics drivers are working properly, run the | |
| 218 | following command to view the available GPUs, statistics, and processes: | |
| 219 | ||
| 220 | #+begin_src sh | |
| 221 | sudo nvidia-smi | |
| 222 | #+end_src | |
| 223 | ||
| 224 | #+caption: nvidia-smi | |
| 225 | [[https://img.cleberg.net/blog/20220308-plex-media-server-migration/nvidia_smi.png]] | |
| 226 | ||
| 227 | Finally, enable hardware transcoding settings in the Plex application: | |
| 228 | ||
| 229 | #+caption: Plex transcoding settings | |
| 230 | [[https://img.cleberg.net/blog/20220308-plex-media-server-migration/plex_transcoding.png]] | |
content/blog/2023-07-19-plex-transcoder-errors.md → blog/plex-transcoder-errors/index.org renamed +27 −33
| @@ -1,63 +1,57 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-07-19 | |
| 3 | title = "How to Avoid Plex Error: 'Conversion failed. The transcoder failed to start up.'" | |
| 4 | description = "Learn how to avoid Plex conversion errors caused by subtitles." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Plex Transcoder Error | |
| 1 | #+title: How to Avoid Plex Error: 'Conversion failed. The transcoder failed to start up.' | |
| 2 | #+date: 2023-07-19 | |
| 3 | #+description: Learn how to avoid Plex conversion errors caused by subtitles. | |
| 4 | #+filetags: :sysadmin: | |
| 8 | 5 | |
| 6 | * Plex Transcoder Error | |
| 9 | 7 | Occasionally, you may see an error in your Plex client that references a |
| 10 | 8 | failure with the transcoder conversion process. The specific error |
| 11 | 9 | wording is: |
| 12 | 10 | |
| 13 | ```txt | |
| 11 | #+begin_src txt | |
| 14 | 12 | Conversion failed. The transcoder failed to start up. |
| 15 | ``` | |
| 16 | ||
| 17 | ## Debugging the Cause | |
| 13 | #+end_src | |
| 18 | 14 | |
| 19 | In order to get a better look at what is causing the error, I'm going | |
| 20 | to observe the Plex console while the error occurs. To do this, open the | |
| 21 | Plex web client, go to `Settings` > `Manage` > | |
| 22 | `Console`. Now, try to play the title again and watch to see | |
| 23 | which errors occur. | |
| 15 | * Debugging the Cause | |
| 16 | In order to get a better look at what is causing the error, I'm going to | |
| 17 | observe the Plex console while the error occurs. To do this, open the | |
| 18 | Plex web client, go to =Settings= > =Manage= > =Console=. Now, try to | |
| 19 | play the title again and watch to see which errors occur. | |
| 24 | 20 | |
| 25 | 21 | In my case, you can see the errors below are related to a subtitle file |
| 26 | (`.srt`) causing the transcoder to crash. | |
| 22 | (=.srt=) causing the transcoder to crash. | |
| 27 | 23 | |
| 28 | ```txt | |
| 24 | #+begin_src txt | |
| 29 | 25 | Jul 19, 2023 16:49:34.945 [140184571120440] Error — Couldn't find the file to stream: /movies/Movie Title (2021)/Movie Title (2021).srt |
| 30 | 26 | Jul 19, 2023 16:49:34.947 [140184532732728] Error — [Req#7611/Transcode/42935159-67C1-4192-9336-DDC6F7BC9330] Error configuring transcoder: TPU: Failed to download sub-stream to temporary file |
| 31 | 27 | Jul 19, 2023 16:49:35.225 [140184532732728] Warning — [Req#760d/Transcode] Got a request to stop a transcode session without a valid session GUID. |
| 32 | 28 | Jul 19, 2023 16:49:45.561 [140184532732728] Info — [Req#7648] AutoUpdate: no updates available |
| 33 | 29 | Jul 19, 2023 16:51:23.402 [140184510081848] Info — Library section 1 (Movies) will be updated because of a change in "/movies/Movie Title (2021)/Movie Title (2021).srt" |
| 34 | ``` | |
| 35 | ||
| 36 | ## Solving the Error | |
| 30 | #+end_src | |
| 37 | 31 | |
| 32 | * Solving the Error | |
| 38 | 33 | In my case, I simply removed the subtitle file because it was not |
| 39 | 34 | critical to keep. You may also avoid this by turning off subtitles if |
| 40 | 35 | you don't want to delete the file. |
| 41 | 36 | |
| 42 | ```sh | |
| 37 | #+begin_src sh | |
| 43 | 38 | rm -rf "/movies/Movie Title (2021)/Movie Title (2021).srt" |
| 44 | ``` | |
| 39 | #+end_src | |
| 45 | 40 | |
| 46 | 41 | Once the subtitle is removed from the directory or subtitles are turned |
| 47 | 42 | off, try to play the title again. At this point, it should play without |
| 48 | 43 | error. If not, reopen or refresh your Plex client and the Plex server: |
| 49 | 44 | |
| 50 | ```sh | |
| 45 | #+begin_src sh | |
| 51 | 46 | sudo systemctl restart plexmediaserver.service |
| 52 | ``` | |
| 53 | ||
| 54 | ## Related Discussion | |
| 55 | ||
| 56 | Looking at [a related Plex forum | |
| 57 | post](https://forums.plex.tv/t/subtitles-crashing-plex-transcoder-samsung-q80-tv-with-or-without-hardware-transcode/741441/2), | |
| 58 | it seems that `.srt` subtitles are the core issue here. | |
| 59 | However, Plex does not seem to have a resolution that fixes these | |
| 60 | errors. | |
| 47 | #+end_src | |
| 48 | ||
| 49 | * Related Discussion | |
| 50 | Looking at | |
| 51 | [[https://forums.plex.tv/t/subtitles-crashing-plex-transcoder-samsung-q80-tv-with-or-without-hardware-transcode/741441/2][a | |
| 52 | related Plex forum post]], it seems that =.srt= subtitles are the core | |
| 53 | issue here. However, Plex does not seem to have a resolution that fixes | |
| 54 | these errors. | |
| 61 | 55 | |
| 62 | 56 | Unfortunately, I would suggest converting subtitle formats, burning the |
| 63 | 57 | subtitles into the title, or simply removing subtitles when they cause |
content/blog/2022-08-31-privacy.com-changes.md → blog/privacy-com-changes/index.org renamed +30 −34
| @@ -1,24 +1,21 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-08-31 | |
| 3 | title = "Concering Changes on Privacy.com" | |
| 4 | description = "My thoughts on Privacy.com changing from a prepaid model to a credit charge model." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Privacy.com Changes Their Terms | |
| 1 | #+title: Concerning Changes on Privacy.com | |
| 2 | #+date: 2022-08-31 | |
| 3 | #+description: My thoughts on Privacy.com changing from a prepaid model to a credit charge model. | |
| 4 | #+filetags: :privacy: | |
| 8 | 5 | |
| 6 | * Privacy.com Changes Their Terms | |
| 9 | 7 | Recently, Privacy.com reached out to their customers regarding a change |
| 10 | 8 | in their terms of use. Further, all customers are required to agree to |
| 11 | 9 | the changes in order to continue using their accounts. |
| 12 | 10 | |
| 13 | [You can view the new cardholder agreement | |
| 14 | here](https://privacy.com/commercial-cardholder-agreement). | |
| 11 | [[https://privacy.com/commercial-cardholder-agreement][You can view the | |
| 12 | new cardholder agreement here]]. | |
| 15 | 13 | |
| 16 | 14 | When you log in, you'll be greeted with a pop-up window asking you to |
| 17 | 15 | review and agree to the new terms of use. You will also not be able to |
| 18 | 16 | open any new cards until the terms are agreed to. |
| 19 | 17 | |
| 20 | ### Changing from a "Prepaid Debit" Model to a "Charge Card" Model | |
| 21 | ||
| 18 | ** Changing from a "Prepaid Debit" Model to a "Charge Card" Model | |
| 22 | 19 | The actual content of the changes is interesting. While the historical |
| 23 | 20 | model of using Privacy.com was akin to prepaid debit cards, the new |
| 24 | 21 | model is very similar to a credit card (they use the term "charge |
| @@ -27,7 +24,7 @@ card"). | ||
| 27 | 24 | I have used Privacy.com for 1-2 years, and the process was always that |
| 28 | 25 | you would create a single-use or merchant-locked card. This card could |
| 29 | 26 | be used for any dollar limit you set and would immediately draw the |
| 30 | funds from whatever funding source you connected, e.g. PayPal account or | |
| 27 | funds from whatever funding source you connected, e.g. PayPal account or | |
| 31 | 28 | a bank account. |
| 32 | 29 | |
| 33 | 30 | The benefit this service provides with a premium account is masking the |
| @@ -37,15 +34,14 @@ charges through Privacy.com and set the merchant as one of their pre-set | ||
| 37 | 34 | options, such as "Smiley's Corner Store" or "NSA Gift Shop." |
| 38 | 35 | |
| 39 | 36 | The new model still works with a bank account as a funding source, but |
| 40 | the model is changed so that you get a "line of credit" set according | |
| 41 | to a 14-day billing cycle. It seems that Privacy.com will now allow | |
| 42 | charges to be incurred without being immediately paid. | |
| 43 | ||
| 44 | ### Daily Payments and Available Credit | |
| 37 | the model is changed so that you get a "line of credit" set according to | |
| 38 | a 14-day billing cycle. It seems that Privacy.com will now allow charges | |
| 39 | to be incurred without being immediately paid. | |
| 45 | 40 | |
| 41 | ** Daily Payments and Available Credit | |
| 46 | 42 | Instead of paying as charges are incurred, you must make a "Daily |
| 47 | Payment" and your "Available Credit" will be locked until you make | |
| 48 | that payment. There are also "End of Billing Cycle Payments" that are | |
| 43 | Payment" and your "Available Credit" will be locked until you make that | |
| 44 | payment. There are also "End of Billing Cycle Payments" that are | |
| 49 | 45 | assigned a due date. |
| 50 | 46 | |
| 51 | 47 | Further, Privacy.com will decline charges that would cause you to exceed |
| @@ -53,18 +49,20 @@ your Available Credit or Credit Limit. | ||
| 53 | 49 | |
| 54 | 50 | One particular interesting section states the following: |
| 55 | 51 | |
| 56 | > YOUR OBLIGATION TO PAY US BACK FOR ALL CARD TRANSACTIONS AND OTHER | |
| 57 | > OBLIGATIONS YOU INCUR IS SECURED BY THE SECURED ACCOUNT. IF YOU DO NOT | |
| 58 | > PAY US BACK FOR ANY AMOUNT YOU OWE US WHEN YOUR PAYMENTS ARE DUE, WE | |
| 59 | > WILL EXERCISE OUR INTEREST AND DEBIT THE SECURED ACCOUNT, AND YOU WILL | |
| 60 | > LOSE THE MONEY IN THE SECURED ACCOUNT. SEE SECTION 8: SECURITY | |
| 61 | > AGREEMENT FOR MORE INFORMATION. | |
| 52 | #+begin_quote | |
| 53 | YOUR OBLIGATION TO PAY US BACK FOR ALL CARD TRANSACTIONS AND OTHER | |
| 54 | OBLIGATIONS YOU INCUR IS SECURED BY THE SECURED ACCOUNT. IF YOU DO NOT | |
| 55 | PAY US BACK FOR ANY AMOUNT YOU OWE US WHEN YOUR PAYMENTS ARE DUE, WE | |
| 56 | WILL EXERCISE OUR INTEREST AND DEBIT THE SECURED ACCOUNT, AND YOU WILL | |
| 57 | LOSE THE MONEY IN THE SECURED ACCOUNT. SEE SECTION 8: SECURITY AGREEMENT | |
| 58 | FOR MORE INFORMATION. | |
| 62 | 59 | |
| 63 | ### Personal Information | |
| 60 | #+end_quote | |
| 64 | 61 | |
| 62 | ** Personal Information | |
| 65 | 63 | Now that Privacy.com is more of a financial institution, they are |
| 66 | obligated to comply with the [know your | |
| 67 | customer](https://en.wikipedia.org/wiki/Know_your_customer) | |
| 64 | obligated to comply with the | |
| 65 | [[https://en.wikipedia.org/wiki/Know_your_customer][know your customer]] | |
| 68 | 66 | guidelines/laws. |
| 69 | 67 | |
| 70 | 68 | I did not proceed with the change to my Privacy.com account, but I have |
| @@ -73,13 +71,11 @@ to be submitted, such as SSN. I am not aware of all new personal | ||
| 73 | 71 | information required or if the funding source is now required to only be |
| 74 | 72 | a bank account. |
| 75 | 73 | |
| 76 | ### Fees | |
| 77 | ||
| 74 | ** Fees | |
| 78 | 75 | Luckily, the fees section did not change much. The subscription fees for |
| 79 | 76 | a premium account are still the only fees. |
| 80 | 77 | |
| 81 | ## My Thoughts | |
| 82 | ||
| 78 | * My Thoughts | |
| 83 | 79 | Personally, I wiped my personal information from my account and then |
| 84 | 80 | permanently deleted it when I heard about these changes. I have no |
| 85 | 81 | interest in yet another method of credit lending offered by private |
| @@ -93,6 +89,6 @@ This type of change toward a "buy it now, pay us later" model is | ||
| 93 | 89 | concerning, and I will be watching Privacy.com to see if they further |
| 94 | 90 | their interests in the credit model as time goes on. |
| 95 | 91 | |
| 96 | Could we see them start charging interest, fees, etc.? I'm not sure, | |
| 97 | but this change does not inspire confidence in their mission as a | |
| 92 | Could we see them start charging interest, fees, etc.? I'm not sure, but | |
| 93 | this change does not inspire confidence in their mission as a | |
| 98 | 94 | privacy-focused company. |
content/blog/2023-01-23-random-mullvad-wireguard.md → blog/random-wireguard/index.org renamed +41 −45
| @@ -1,17 +1,16 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-01-23 | |
| 3 | title = "Connecting to a Random Mullvad Wireguard Host on Boot" | |
| 4 | description = "Learn how to connect to a random Mullvad Wireguard host on boot." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Mullvad Wireguard | |
| 1 | #+title: Connecting to a Random Mullvad Wireguard Host on Boot | |
| 2 | #+date: 2023-01-23 | |
| 3 | #+description: Learn how to connect to a random Mullvad Wireguard host on boot. | |
| 4 | #+filetags: :linux: | |
| 8 | 5 | |
| 6 | * Mullvad Wireguard | |
| 9 | 7 | If you're using an OS that does not support one of Mullvad's apps, |
| 10 | 8 | you're likely using the Wireguard configuration files instead. |
| 11 | 9 | |
| 12 | If not, the first step is to visit Mullvad's [Wireguard configuration | |
| 13 | files](https://mullvad.net/en/account/#/wireguard-config) page and | |
| 14 | download a ZIP of the configuration files you want to use. | |
| 10 | If not, the first step is to visit Mullvad's | |
| 11 | [[https://mullvad.net/en/account/#/wireguard-config][Wireguard | |
| 12 | configuration files]] page and download a ZIP of the configuration files | |
| 13 | you want to use. | |
| 15 | 14 | |
| 16 | 15 | Personally, I downloaded all configuration files across the world and |
| 17 | 16 | chose my connections using the script below. |
| @@ -19,32 +18,31 @@ chose my connections using the script below. | ||
| 19 | 18 | Once the files are downloaded, unzip them and move them to your |
| 20 | 19 | preferred location: |
| 21 | 20 | |
| 22 | ```sh | |
| 21 | #+begin_src sh | |
| 23 | 22 | cd Downloads |
| 24 | 23 | unzip mullvad_wireguard_linux_all_all.zip |
| 25 | 24 | mkdir ~/mullvad && mv ~/Downloads/*.conf ~/mullvad/ |
| 26 | ``` | |
| 27 | ||
| 28 | ## Creating a Script to Connect to a Random Host | |
| 25 | #+end_src | |
| 29 | 26 | |
| 27 | *** Creating a Script to Connect to a Random Host | |
| 30 | 28 | Once you have a folder of Wireguard configuration files from Mullvad, |
| 31 | 29 | you can create a script to randomly connect to any one of the locations. |
| 32 | 30 | |
| 33 | Start by creating a shell script - mine is called `vpn.sh`. | |
| 31 | Start by creating a shell script - mine is called =vpn.sh=. | |
| 34 | 32 | |
| 35 | ```sh | |
| 33 | #+begin_src sh | |
| 36 | 34 | nano ~/vpn.sh |
| 37 | ``` | |
| 35 | #+end_src | |
| 38 | 36 | |
| 39 | 37 | Within this script, you can paste the following info. Note that I |
| 40 | specify `us-*` in my script, which means that it will only | |
| 41 | consider US-based VPN locations. You can alter this or simply change it | |
| 42 | `*` to consider all locations. | |
| 38 | specify =us-*= in my script, which means that it will only consider | |
| 39 | US-based VPN locations. You can alter this or simply change it =*= to | |
| 40 | consider all locations. | |
| 43 | 41 | |
| 44 | ```sh | |
| 42 | #+begin_src sh | |
| 45 | 43 | #!/bin/sh |
| 46 | 44 | |
| 47 | ls /home/$USER/mullvad/us-* |sort -R |tail -n 1 |while read file; do | |
| 45 | ls /home/$USER/mullvad/us-** |sort -R |tail -n 1 |while read file; do | |
| 48 | 46 | # Replace `doas` with `sudo` if your machine uses `sudo`, |
| 49 | 47 | # or remove `doas` if users don't need to su to run wg-quick |
| 50 | 48 | doas wg-quick up $file; |
| @@ -52,19 +50,19 @@ ls /home/$USER/mullvad/us-* |sort -R |tail -n 1 |while read file; do | ||
| 52 | 50 | printf "\n\nPrinting new IP info:\n" |
| 53 | 51 | curl https://am.i.mullvad.net/connected |
| 54 | 52 | done |
| 55 | ``` | |
| 53 | #+end_src | |
| 56 | 54 | |
| 57 | 55 | Once you've modified the script to your liking, add executable |
| 58 | 56 | permissions and run the script: |
| 59 | 57 | |
| 60 | ```sh | |
| 58 | #+begin_src sh | |
| 61 | 59 | chmod +x ~/vpn.sh |
| 62 | 60 | ~/vpn.sh |
| 63 | ``` | |
| 61 | #+end_src | |
| 64 | 62 | |
| 65 | 63 | The output should look like the following: |
| 66 | 64 | |
| 67 | ```txt | |
| 65 | #+begin_src txt | |
| 68 | 66 | doas (user@host) password: |
| 69 | 67 | |
| 70 | 68 | # ... The script will process all of the iptables and wg commands here |
| @@ -73,44 +71,42 @@ Created Mullvad wireguard connection with file: /home/user/mullvad/us-nyc-wg-210 | ||
| 73 | 71 | |
| 74 | 72 | Printing new IP info: |
| 75 | 73 | You are connected to Mullvad (server country-city-wg-num). Your IP address is 12.345.678.99 |
| 76 | ``` | |
| 74 | #+end_src | |
| 77 | 75 | |
| 78 | 76 | That's all there is to it. You can see your new location and IP via the |
| 79 | `printf` and `curl` commands included in the | |
| 80 | script. | |
| 81 | ||
| 82 | You can also go to the [Connection Check \| | |
| 83 | Mullvad](https://mullvad.net/en/check/) page to see if you are fully | |
| 84 | connected to Mullvad and if any leaks exist. | |
| 77 | =printf= and =curl= commands included in the script. | |
| 85 | 78 | |
| 86 |  | |
| 79 | You can also go to the [[https://mullvad.net/en/check/][Connection Check | |
| 80 | | Mullvad]] page to see if you are fully connected to Mullvad and if any | |
| 81 | leaks exist. | |
| 88 | 82 | |
| 89 | ## Disconnecting from the Wireguard Connection | |
| 83 | #+caption: Mullvad Connection Check | |
| 84 | [[https://img.cleberg.net/blog/20230123-random-mullvad-wireguard/mullvad_check.png]] | |
| 90 | 85 | |
| 86 | * Disconnecting from the Wireguard Connection | |
| 91 | 87 | If you forget which connection you're using, you can execute the |
| 92 | 88 | following command to see where Wireguard is currently connected: |
| 93 | 89 | |
| 94 | ```sh | |
| 90 | #+begin_src sh | |
| 95 | 91 | wg show |
| 96 | ``` | |
| 92 | #+end_src | |
| 97 | 93 | |
| 98 | 94 | This command will show you the Wireguard interfaces and should output a |
| 99 | connection like so: `interface: us-lax-wg-104`. | |
| 95 | connection like so: =interface: us-lax-wg-104=. | |
| 100 | 96 | |
| 101 | 97 | Once you have this, just disconnect using that files' full path: |
| 102 | 98 | |
| 103 | ```sh | |
| 99 | #+begin_src sh | |
| 104 | 100 | wg-quick down /home/user/mullvad/us-lax-wg-104.conf |
| 105 | ``` | |
| 101 | #+end_src | |
| 106 | 102 | |
| 107 | 103 | I have a TODO item on figuring out how to easily export an environment |
| 108 | variable that contains the configuration file's full name, so that I | |
| 109 | can just execute the following: | |
| 104 | variable that contains the configuration file's full name, so that I can | |
| 105 | just execute the following: | |
| 110 | 106 | |
| 111 | ```sh | |
| 107 | #+begin_src sh | |
| 112 | 108 | # Ideal situation if I can export the $file variable to the environment |
| 113 | 109 | wg-quick down $file |
| 114 | ``` | |
| 110 | #+end_src | |
| 115 | 111 | |
| 116 | 112 | If you have an idea on how to do this, email me! |
content/blog/2023-01-03-recent-website-changes.md → blog/recent-website-changes/index.org renamed +31 −42
| @@ -1,43 +1,36 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-01-03 | |
| 3 | title = "Recent Website Changes" | |
| 4 | description = "A retrospective of recent changes to my website." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## The State of This Website | |
| 1 | #+title: Recent Website Changes | |
| 2 | #+date: 2023-01-03 | |
| 3 | #+description: A retrospective of recent changes to my website. | |
| 4 | #+filetags: :dev: | |
| 8 | 5 | |
| 6 | * The State of This Website | |
| 9 | 7 | Over the years, this website has changed URLs, styles, content focus, |
| 10 | 8 | and much more. However, it seems that I am never done, as I am yet again |
| 11 | 9 | changing this page to fit my current needs and wants. |
| 12 | 10 | |
| 13 | While this site was already minimal (\~12kb), it contained a lot of | |
| 11 | While this site was already minimal (~12kb), it contained a lot of | |
| 14 | 12 | disorganized content and some poorly chosen color schemes. |
| 15 | 13 | |
| 16 | 14 | The recent updates attempt to fix these items while focusing on what I |
| 17 | 15 | truly care about here: the content within each page. |
| 18 | 16 | |
| 19 | ## Recent Changes | |
| 20 | ||
| 17 | * Recent Changes | |
| 21 | 18 | I've made quite a few changes to the style of this website today, both |
| 22 | 19 | in the CSS and in the HTML. |
| 23 | 20 | |
| 24 | 21 | Here are some of the key takeaways from today's changes: |
| 25 | 22 | |
| 26 | 1. Reduce the width of the website from `60em` to | |
| 27 | `40em`. | |
| 28 | 2. Remove breadcrumb navigation and replaced with a simple "Return | |
| 29 | Home" link when visiting anything other than the homepage. | |
| 30 | 3. Remove syntax highlighting from code blocks. CSS now loads from a | |
| 31 | single file. | |
| 32 | 4. Move blog posts on the homepage to the top, pushing tertiary content | |
| 33 | down. | |
| 34 | 5. Update font-family from `monospace` to | |
| 35 | `sans-serif` for readability. | |
| 36 | ||
| 37 | ## Future Focus | |
| 38 | ||
| 39 | ### Accessibility | |
| 40 | ||
| 23 | 1. Reduce the width of the website from =60em= to =40em=. | |
| 24 | 2. Remove breadcrumb navigation and replaced with a simple "Return Home" | |
| 25 | link when visiting anything other than the homepage. | |
| 26 | 3. Remove syntax highlighting from code blocks. CSS now loads from a | |
| 27 | single file. | |
| 28 | 4. Move blog posts on the homepage to the top, pushing tertiary content | |
| 29 | down. | |
| 30 | 5. Update font-family from =monospace= to =sans-serif= for readability. | |
| 31 | ||
| 32 | * Future Focus | |
| 33 | ** Accessibility | |
| 41 | 34 | My main focus amidst all the changes this past year was accessibility. I |
| 42 | 35 | tried to improve the accessibility of all pages on this site as well as |
| 43 | 36 | I know how. For example, I added aria labels to identify different |
| @@ -46,8 +39,7 @@ navigation menus in November. | ||
| 46 | 39 | I want to continue this in 2023 and learn more about the accessibility |
| 47 | 40 | features I can utilize to help those who may need them. |
| 48 | 41 | |
| 49 | ### Content First | |
| 50 | ||
| 42 | ** Content First | |
| 51 | 43 | Beyond accessibility, I am making a concerted effort to bring the |
| 52 | 44 | content of this site to the forefront and push the tertiary information |
| 53 | 45 | (e.g., About Me, Services, etc.) down below the content. |
| @@ -56,30 +48,27 @@ Further, I want to review and edit previous blog posts for grammar, | ||
| 56 | 48 | accuracy, dead links, and more. Where necessary, I may even add a blurb |
| 57 | 49 | at the top of old posts that are no longer accurate or helpful. |
| 58 | 50 | |
| 59 | ### Style | |
| 60 | ||
| 51 | ** Style | |
| 61 | 52 | As always, I will be searching for ways to reduce distractions and bring |
| 62 | 53 | a minimalistic approach to this site. While there are certainly more |
| 63 | drastic measures I could take, such as making this a [Shinobi | |
| 64 | Website](https://shinobi.bt.ht) or a [No CSS | |
| 65 | Website](https://nocss.club), I prefer to keep some modern features | |
| 66 | here. | |
| 54 | drastic measures I could take, such as making this a | |
| 55 | [[https://shinobi.bt.ht][Shinobi Website]] or a [[https://nocss.club][No | |
| 56 | CSS Website]], I prefer to keep some modern features here. | |
| 67 | 57 | |
| 68 | 58 | Two ideas have been floating around in my head, but I am not sure how I |
| 69 | 59 | feel about these approaches yet: |
| 70 | 60 | |
| 71 | 1. Going all-in with Emacs org-mode and creating a script to | |
| 72 | auto-publish all my blog posts from org-mode to plain HTML files and | |
| 73 | then letting my CSS style it after the fact. | |
| 74 | 2. Focus on publishing for Gemini or Gopher and then utilize a | |
| 75 | conversion program to translate the pages to HTML. | |
| 76 | ||
| 77 | ## Looking Back | |
| 61 | 1. Going all-in with Emacs org-mode and creating a script to | |
| 62 | auto-publish all my blog posts from org-mode to plain HTML files and | |
| 63 | then letting my CSS style it after the fact. | |
| 64 | 2. Focus on publishing for Gemini or Gopher and then utilize a | |
| 65 | conversion program to translate the pages to HTML. | |
| 78 | 66 | |
| 67 | * Looking Back | |
| 79 | 68 | As I sit here and finalize the changes, as well as this post, I am happy |
| 80 | 69 | with the current state of this website. It's certainly a long way from |
| 81 | my first attempts (parallax background images, anyone?) and it's good | |
| 82 | to see the progress. | |
| 70 | my first attempts (parallax background images, anyone?) and it's good to | |
| 71 | see the progress. | |
| 83 | 72 | |
| 84 | 73 | I can only hope and work hard to ensure that I make more meaningful |
| 85 | 74 | progress by this time next year. |
blog/redirect-github-pages/index.org added +120
| @@ -0,0 +1,120 @@ | ||
| 1 | #+title: Redirect GitHub Pages from Subdomain to the Top-Level Domain | |
| 2 | #+date: 2020-08-22 | |
| 3 | #+description: Learn how to redirect Github pages to the TLD. | |
| 4 | #+filetags: :sysadmin: | |
| 5 | ||
| 6 | * Short answer | |
| 7 | ** Step 1 | |
| 8 | Add a new file CNAME to your GitHub Pages repository containing only one | |
| 9 | line: your top-level domain name. E.g.: =example.com= | |
| 10 | ||
| 11 | ** Step 2 | |
| 12 | [Optional] but highly recommended | |
| 13 | ||
| 14 | 2.1: Remove all other top-level records (prefixed with @) of type A from | |
| 15 | your DNS configuration. | |
| 16 | ||
| 17 | 2.2: Remove a CNAME record for the second-level domain www if it is | |
| 18 | present. | |
| 19 | ||
| 20 | ** Step 3 | |
| 21 | Add these 5 entries to the very top of your DNS configuration: | |
| 22 | ||
| 23 | #+begin_src txt | |
| 24 | @ A 185.199.108.153 | |
| 25 | @ A 185.199.109.153 | |
| 26 | @ A 185.199.110.153 | |
| 27 | @ A 185.199.111.153 | |
| 28 | www CNAME your_github_username.github.io. | |
| 29 | #+end_src | |
| 30 | ||
| 31 | Replace =your_github_username= with your actual GitHub username. | |
| 32 | ||
| 33 | ** Step 4 | |
| 34 | Wait for your DNS changes to propagate. DNS changes aren't effective | |
| 35 | immediately. They can take up to a full day to propagate. | |
| 36 | ||
| 37 | * Long answer | |
| 38 | This issue has two sides. One is the DNS configuration itself. Another | |
| 39 | one is the way GitHub Pages will forward HTTP requests. | |
| 40 | ||
| 41 | We need to know a few things to understand what GitHub is trying to say | |
| 42 | in their documentation. | |
| 43 | ||
| 44 | ** DNS Entry Types | |
| 45 | There are two types of DNS records which interest us: CNAME and A. | |
| 46 | ||
| 47 | =A= is also known as =Apex= or sometimes as =root entry=. It forwards | |
| 48 | requests to a specified fixed IP address. =CNAME= entry forwards | |
| 49 | requests to a specified URL (actual valid plain text URL, not an IP | |
| 50 | address). | |
| 51 | ||
| 52 | ** DNS Load balancing | |
| 53 | GitHub has one central URL address which accepts all DNS requests for | |
| 54 | GitHub Pages: =http://username.github.io=. That URL is resolved to | |
| 55 | different IP addresses based on your geographical location. Website | |
| 56 | hosted on GitHub Pages is a simple collection of =HTML=, =CSS= and =JS= | |
| 57 | files. GitHub distributes these files to different servers across the | |
| 58 | globe. So that when your browser sends a request from Europe, it | |
| 59 | receives data from a server in Europe. The same is valid for the | |
| 60 | requests from Asia and the USA. | |
| 61 | ||
| 62 | ** What GitHub is trying to say | |
| 63 | Since =A= records in DNS must contain IP addresses, and they must be | |
| 64 | either =185.199.108.153= or =185.199.109.153= or =185.199.110.153= or | |
| 65 | =185.199.111.153=, there is no way to forward requests to a server | |
| 66 | located somewhere in Europe or Asia. Your website hosted at GitHub Pages | |
| 67 | will be downloaded from a central GitHub Pages server. There is a minor | |
| 68 | risk that if GitHub Pages DNS servers (=x.x.x.153=) are down for some | |
| 69 | reason, all custom domains which use fixed GitHub Pages IP addresses | |
| 70 | will not be accessible (their DNS requests will not be resolvable). | |
| 71 | ||
| 72 | That is why GitHub strongly suggests to either use a second-level domain | |
| 73 | for your GitHub Pages (e.g. =blog.example.com=) or use a DNS service | |
| 74 | provider that supports a record type =ALIAS= that acts as =A= record but | |
| 75 | forwards request to a URL address (e.g. =username.github.io=) instead of | |
| 76 | a fixed IP address. | |
| 77 | ||
| 78 | ** How GitHub Pages treats HTTP requests | |
| 79 | After a DNS request for =your_github_username.github.io= is resolved | |
| 80 | into an IP address, e.g. =185.199.108.153= your browser sends an HTTP | |
| 81 | request to that server with an HTTP header =Host=. Below are =curl= | |
| 82 | examples that load the same website (these examples might not work if | |
| 83 | you are behind a proxy server): | |
| 84 | ||
| 85 | #+begin_src sh | |
| 86 | curl --header "Host: your_github_username.github.io" http://185.199.108.153/ | |
| 87 | curl --header "Host: www.example.com" http://185.199.108.153/ | |
| 88 | curl --header "Host: example.com" http://185.199.108.153/ | |
| 89 | #+end_src | |
| 90 | ||
| 91 | This way GitHub Pages servers know which user website to serve. | |
| 92 | ||
| 93 | #+begin_quote | |
| 94 | GitHub Pages server will automatically redirect HTTP requests to the | |
| 95 | top-level domain if your =CNAME= file contains =example.com= but | |
| 96 | =www.example.com= is requested. | |
| 97 | ||
| 98 | The same is valid if your =CNAME= file contains =www.example.com= but | |
| 99 | the header =Host= in the =HTTP= request contains =example.com=. | |
| 100 | #+end_quote | |
| 101 | ||
| 102 | ** Why can't I add a =CNAME= record entry that accepts a top-level request (=@=) to my DNS configuration? | |
| 103 | Quote from the GitHub Pages documentation: | |
| 104 | ||
| 105 | #+begin_quote | |
| 106 | Warning: Do not create a CNAME record for your custom apex domain! Doing | |
| 107 | so may cause issues with other services, such as email, on that domain. | |
| 108 | #+end_quote | |
| 109 | ||
| 110 | ** References: | |
| 111 | 1. [[https://docs.github.com/en/github/working-with-github-pages/configuring-a-custom-domain-for-your-github-pages-site][Setting | |
| 112 | up a custom domain with GitHub Pages]] | |
| 113 | 2. [[https://docs.github.com/en/github/working-with-github-pages/troubleshooting-custom-domains-and-github-pages][My | |
| 114 | custom domain isn't working]] | |
| 115 | 3. [[https://serverfault.com/questions/589370/cannot-access-my-github-pages-website-by-ip-address][Cannot | |
| 116 | access my GitHub Pages website by IP Address]] | |
| 117 | 4. [[https://stackoverflow.com/questions/23375422/how-do-i-set-up-github-pages-to-redirect-dns-requests-from-a-subdomain-e-g-www][How | |
| 118 | do I set up GitHub Pages to redirect DNS requests from a subdomain | |
| 119 | (e.g. www) to the top-level domain (TLD, Apex record)?]] | |
| 120 | ||
content/blog/2022-03-02-note-taking.md → blog/reliable-notes/index.org renamed +49 −49
| @@ -1,16 +1,17 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-03-02 | |
| 3 | title = "Easy, Reliable Note-Taking" | |
| 4 | description = "My personal preferences to ensure notes are clear, portable, and long-lasting." | |
| 5 | +++ | |
| 1 | #+title: Easy, Reliable Note-Taking | |
| 2 | #+date: 2022-03-02 | |
| 3 | #+description: My personal preferences to ensure notes are clear, portable, and long-lasting. | |
| 4 | #+filetags: :personal: | |
| 6 | 5 | |
| 7 | ## Choosing Durable File Formats | |
| 6 | * Choosing Durable File Formats | |
| 8 | 7 | |
| 9 | > TL;DR: Write in a format that can be easily rendered and read in | |
| 10 | > plain-text mode (e.g., `.txt`, `.md`, etc.). | |
| 8 | #+begin_quote | |
| 9 | TL;DR: Write in a format that can be easily rendered and read in | |
| 10 | plain-text mode (e.g., =.txt=, =.md=, etc.). | |
| 11 | #+end_quote | |
| 11 | 12 | |
| 12 | As I've written more and more over the years, I've found that my love | |
| 13 | of note-taking is always growing. Everything I learn or need to remember | |
| 13 | As I've written more and more over the years, I've found that my love of | |
| 14 | note-taking is always growing. Everything I learn or need to remember | |
| 14 | 15 | can be written down in a note and saved digitally, with no cost to |
| 15 | 16 | myself. Unlike paper copies that need physical storage space, digital |
| 16 | 17 | files simply need space on your local disk or cloud storage, which is |
| @@ -22,8 +23,8 @@ styling. This meant that I had to go through each note during migration | ||
| 22 | 23 | and edit the file to look presentable again. |
| 23 | 24 | |
| 24 | 25 | For the last year or two, I have written everything exclusively in |
| 25 | [Markdown](https://en.wikipedia.org/wiki/Markdown) format. Small notes, | |
| 26 | long-form writings, and even these blog posts are all written in | |
| 26 | [[https://en.wikipedia.org/wiki/Markdown][Markdown]] format. Small | |
| 27 | notes, long-form writings, and even these blog posts are all written in | |
| 27 | 28 | Markdown. |
| 28 | 29 | |
| 29 | 30 | Why Markdown? While I do appreciate the simplicity of plain-text files |
| @@ -31,19 +32,18 @@ without any formatting, I often need visual cues such as heading and | ||
| 31 | 32 | code blocks to keep my thoughts straight. Markdown provides a minimal |
| 32 | 33 | set of styling indicators for me to style my notes without adding any |
| 33 | 34 | proprietary, embedded data into the files. If I want a top-level |
| 34 | heading, I simply add a hash (`#`) before the line. An added | |
| 35 | bonus is that even if a system doesn't understand Markdown, it will | |
| 36 | render it as plain-text and I can read it just as easily. | |
| 35 | heading, I simply add a hash (=#=) before the line. An added bonus is | |
| 36 | that even if a system doesn't understand Markdown, it will render it as | |
| 37 | plain-text and I can read it just as easily. | |
| 37 | 38 | |
| 38 | 39 | For example, here's how TextEdit on macOS will open and display a |
| 39 | 40 | Markdown file in plain-text, since it does contain any features to |
| 40 | 41 | preview Markdown as HTML: |
| 41 | 42 | |
| 42 |  | |
| 44 | ||
| 45 | ## Saving & Syncing Files | |
| 43 | #+caption: Plain Text Markdown | |
| 44 | [[https://img.cleberg.net/blog/20220302-easy-reliable-note-taking/plain_markdown.png]] | |
| 46 | 45 | |
| 46 | ** Saving & Syncing Files | |
| 47 | 47 | In order to read and edit my notes across platforms, I use my personal |
| 48 | 48 | cloud storage through Tresorit due to its native integration with macOS |
| 49 | 49 | and iOS file managers. In addition, Tresorit works well on Debian-based |
| @@ -59,19 +59,17 @@ me to sync anything manually or kick-off a sync job to update my files. | ||
| 59 | 59 | This means that I can edit on mobile, and it takes about 5-10 seconds to |
| 60 | 60 | see the changes on desktop. |
| 61 | 61 | |
| 62 | ### Version Control with Git | |
| 63 | ||
| 62 | *** Version Control with Git | |
| 64 | 63 | A different approach I've contemplated is storing my notes and |
| 65 | 64 | attachments is using a hosted Git repository to track changes to the |
| 66 | 65 | files. However, I don't want to rely on an external service that could |
| 67 | 66 | potentially see into my data, even if the repository is private. |
| 68 | 67 | |
| 69 | I might just do `git init` locally and then commit my changes | |
| 70 | each time I write or update a note, but that seems to be a lot of work | |
| 71 | just for tracking changes - which I don't necessarily care to know. | |
| 72 | ||
| 73 | ### Backups! | |
| 68 | I might just do =git init= locally and then commit my changes each time | |
| 69 | I write or update a note, but that seems to be a lot of work just for | |
| 70 | tracking changes - which I don't necessarily care to know. | |
| 74 | 71 | |
| 72 | *** Backups! | |
| 75 | 73 | One small addition to the storage/sync conversation is the idea of |
| 76 | 74 | backups. Personally, I manually create periodic backups of my entire |
| 77 | 75 | cloud storage, compress it into an archive, and store it on my home |
| @@ -81,12 +79,15 @@ To improve my workflow, I am going to be exploring options to | ||
| 81 | 79 | automatically compress the mounted cloud directory and send it over to |
| 82 | 80 | my server on a set schedule. |
| 83 | 81 | |
| 84 | ## Writing on Desktop | |
| 82 | ** Writing on Desktop | |
| 85 | 83 | |
| 86 | > **Update (06.14.22)**: Since writing this post, I have reverted to | |
| 87 | > simply keeping my `notes` folder open and opening notes | |
| 88 | > individually in TextEdit for a more minimal and relaxing writing | |
| 89 | > experience on the desktop. | |
| 84 | #+begin_quote | |
| 85 | *Update (06.14.22)*: Since writing this post, I have reverted to simply | |
| 86 | keeping my =notes= folder open and opening notes individually in | |
| 87 | TextEdit for a more minimal and relaxing writing experience on the | |
| 88 | desktop. | |
| 89 | ||
| 90 | #+end_quote | |
| 90 | 91 | |
| 91 | 92 | The bulk of my writing occurs in a desktop environment, with a full |
| 92 | 93 | keyboard layout and wide screen. I don't illustrate with a smart pen, I |
| @@ -94,31 +95,30 @@ rarely use embedded images, and I love being able to see all of my | ||
| 94 | 95 | notes/directories in a sidebar. |
| 95 | 96 | |
| 96 | 97 | With this simple set of requirements, I chose |
| 97 | [Obsidian](https://obsidian.md) as my desktop text editor. Obsidian has | |
| 98 | some in-depth tools like a graph view, command palette, mentions, etc., | |
| 99 | but I've found that using it as a simple Markdown editor is incredibly | |
| 100 | easy and straightforward. | |
| 98 | [[https://obsidian.md][Obsidian]] as my desktop text editor. Obsidian | |
| 99 | has some in-depth tools like a graph view, command palette, mentions, | |
| 100 | etc., but I've found that using it as a simple Markdown editor is | |
| 101 | incredibly easy and straightforward. | |
| 101 | 102 | |
| 102 | 103 | Here's an example of how my Markdown notes look when opened in |
| 103 | 104 | plain-text mode: |
| 104 | 105 | |
| 105 |  | |
| 107 | ||
| 108 | Here's the "live preview" version, where the Markdown is rendered | |
| 109 | into its HTML format: | |
| 106 | #+caption: Obsidian Markdown Source Mode | |
| 107 | [[https://img.cleberg.net/blog/20220302-easy-reliable-note-taking/obsidian_source_mode.png]] | |
| 110 | 108 | |
| 111 |  | |
| 109 | Here's the "live preview" version, where the Markdown is rendered into | |
| 110 | its HTML format: | |
| 113 | 111 | |
| 114 | ### Programming on Desktop | |
| 112 | #+caption: Obsidian Markdown Live Preview | |
| 113 | [[https://img.cleberg.net/blog/20220302-easy-reliable-note-taking/obsidian_live_preview.png]] | |
| 115 | 114 | |
| 115 | *** Programming on Desktop | |
| 116 | 116 | While I was writing this, I realized I should specify that I don't use |
| 117 | 117 | the same editor for writing notes and for writing code. For programming |
| 118 | purposes, I use [VSCodium](https://vscodium.com) as my development IDE. | |
| 119 | ||
| 120 | ## Writing on Mobile | |
| 118 | purposes, I use [[https://vscodium.com][VSCodium]] as my development | |
| 119 | IDE. | |
| 121 | 120 | |
| 121 | ** Writing on Mobile | |
| 122 | 122 | Personally, I write very little on mobile, except when needing to take |
| 123 | 123 | important notes on-the-go. Any long-form writing, journals, etc. are |
| 124 | 124 | done at home, where I always have my laptop available. |
| @@ -126,9 +126,9 @@ done at home, where I always have my laptop available. | ||
| 126 | 126 | I wanted a simple and foolproof editor for iOS, preferably open-source. |
| 127 | 127 | After a long journey of testing the few (& terrible) open-source iOS |
| 128 | 128 | note-taking apps, I finally found a phenomenal one: |
| 129 | [Runestone](https://github.com/simonbs/runestone). This app is fantastic | |
| 130 | for note-taking, has plenty of optional features, and integrates | |
| 131 | natively with the iOS file manager. | |
| 129 | [[https://github.com/simonbs/runestone][Runestone]]. This app is | |
| 130 | fantastic for note-taking, has plenty of optional features, and | |
| 131 | integrates natively with the iOS file manager. | |
| 132 | 132 | |
| 133 | 133 | This app opens the iOS file manager and allows you to click any file you |
| 134 | 134 | want, opens it up in an editor, and lets me save and close out of that |
blog/scli/index.org added +145
| @@ -0,0 +1,145 @@ | ||
| 1 | #+title: Installing scli on Alpine Linux (musl) | |
| 2 | #+date: 2023-11-08 | |
| 3 | #+description: Learn how to properly configure scli for musl-based systems. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | [[https://github.com/isamert/scli][scli]] is a command-line tool that | |
| 7 | allows you to connect to your Signal messenger account. This program | |
| 8 | utilizes a two-pane display that shows you chats on the left and the | |
| 9 | focused conversation on the right. | |
| 10 | ||
| 11 | This guide will show you how to install =scli= and its dependencies on | |
| 12 | Alpine Linux, which requires some extra work due to musl. | |
| 13 | ||
| 14 | If you're using a non-musl system, you can likely following the =scli= | |
| 15 | README and download the packaged binaries for an easier installation | |
| 16 | process. | |
| 17 | ||
| 18 | * Dependencies | |
| 19 | In order to use =scli=, you need a few dependencies: | |
| 20 | ||
| 21 | - =openjdk17-jre= - Used as a dependency for the =signal-cli= tool. | |
| 22 | Version may vary. | |
| 23 | - =signal-cli= - Used as the backbone of the =scli= tool. | |
| 24 | - =findutils= - Replaces the standard Busybox version of =xargs=. | |
| 25 | - =urwid= - A console user interface library for Python. | |
| 26 | - =urwid-readline= - For GNU emacs-like keybinds on the input line. | |
| 27 | - =qrencode= - Displays a QR code in the terminal to link the device | |
| 28 | using your phone. Not necessary if you're only linking on desktop and | |
| 29 | can copy/paste the connection URL. | |
| 30 | ||
| 31 | Let's start by installing the packages available via Alpine's | |
| 32 | repositories. Be sure to install the latest version of =openjdk=. If you | |
| 33 | run into Java-related issues, uninstall =openjdk= and install an older | |
| 34 | version. | |
| 35 | ||
| 36 | #+begin_src sh | |
| 37 | doas apk add openjdk17-jre findutils qrencode | |
| 38 | #+end_src | |
| 39 | ||
| 40 | Next, let's install =signal-cli=. Be sure to export the version of | |
| 41 | =signal-cli= that you want. I use version =0.12.4= below, but that may | |
| 42 | be outdated by the time you're reading this. | |
| 43 | ||
| 44 | #+begin_src sh | |
| 45 | export VERSION="0.12.4" | |
| 46 | wget https://github.com/AsamK/signal-cli/releases/download/v"${VERSION}"/signal-cli-"${VERSION}".tar.gz | |
| 47 | doas tar xf signal-cli-"${VERSION}".tar.gz -C /opt | |
| 48 | doas ln -sf /opt/signal-cli-${VERSION}"/bin/signal/cli /usr/local/bin | |
| 49 | #+end_src | |
| 50 | ||
| 51 | Finally, install the =urwid= packages using the Python packaging | |
| 52 | utility. | |
| 53 | ||
| 54 | #+begin_src sh | |
| 55 | pip3 install urwid urwid-readline | |
| 56 | #+end_src | |
| 57 | ||
| 58 | * Installation | |
| 59 | Now that we have all of the dependencies we need, we can install =scli=. | |
| 60 | Start by simply cloning the repository. | |
| 61 | ||
| 62 | #+begin_src sh | |
| 63 | git clone https://github.com/isamert/scli | |
| 64 | #+end_src | |
| 65 | ||
| 66 | When I cloned this repository on 2023-11-08, I found a bug in the logic | |
| 67 | that required a fix. You must edit the =scli= file and replace the one | |
| 68 | instance of =RLIMIT_OFILE= with =RLIMIT_NOFILE=. | |
| 69 | ||
| 70 | #+begin_src sh | |
| 71 | cd scli | |
| 72 | nano scli | |
| 73 | #+end_src | |
| 74 | ||
| 75 | Once complete, you can move this program to anywhere on your =$PATH=. I | |
| 76 | chose the following directory. | |
| 77 | ||
| 78 | #+begin_src sh | |
| 79 | doas mv scli /usr/local/bin/scli | |
| 80 | #+end_src | |
| 81 | ||
| 82 | * Initial Setup | |
| 83 | Now that everything is installed, we can login and configure the client. | |
| 84 | Start by generating a connection link. | |
| 85 | ||
| 86 | #+begin_src sh | |
| 87 | signal-cli link -n "YOUR-DEVICE-NICKNAME" | tee >(xargs -L 1 qrencode -t utf8) | |
| 88 | #+end_src | |
| 89 | ||
| 90 | This will generate a connection link and related QR code for you to use | |
| 91 | to link the devices together. Once complete, *wait patiently** for the | |
| 92 | connection process to finish. | |
| 93 | ||
| 94 | Once it completes, it will exit and return you to the prompt. From here, | |
| 95 | you need to perform an initial =receive= command to start things off. | |
| 96 | The =USERNAME= variable should be your phone number, such as | |
| 97 | =+15551237890=. | |
| 98 | ||
| 99 | #+begin_src sh | |
| 100 | signal-cli -u USERNAME receive | |
| 101 | #+end_src | |
| 102 | ||
| 103 | Also be sure to test the daemon to ensure it works properly. If no | |
| 104 | errors occur, it's working. If you run into errors because you're not | |
| 105 | running a DBUS session, see my notes below. | |
| 106 | ||
| 107 | #+begin_src sh | |
| 108 | signal-cli -u USERNAME daemon | |
| 109 | #+end_src | |
| 110 | ||
| 111 | Once the initial reception is complete, you are ready to use =scli=. | |
| 112 | ||
| 113 | This process will differ depending on your desktop environment (DE). If | |
| 114 | you are running a DE, you likely have a DBUS session running already and | |
| 115 | can simply launch the program. | |
| 116 | ||
| 117 | However, if you're like me and running your computer straight on the TTY | |
| 118 | without a DE, you'll need to start a DBUS session for this program. | |
| 119 | ||
| 120 | #+begin_src sh | |
| 121 | # If you're not running a DBUS session yet, you need to start one for scli | |
| 122 | dbus-run-session -- scli | |
| 123 | ||
| 124 | # OR - If you're already running a DBUS session, simply run scli | |
| 125 | scli | |
| 126 | #+end_src | |
| 127 | ||
| 128 | * Configuration | |
| 129 | Lastly, there are a number of configuration options that you can pass | |
| 130 | via the command or in the =~/.config/sclirc= file. See the Github README | |
| 131 | for more information on configuration options. | |
| 132 | ||
| 133 | #+begin_src sh | |
| 134 | nano ~/.config/sclirc | |
| 135 | #+end_src | |
| 136 | ||
| 137 | #+begin_src conf | |
| 138 | # ~/.config/sclirc | |
| 139 | ||
| 140 | wrap-at = 80 | |
| 141 | enable-notifications = true | |
| 142 | #+end_src | |
| 143 | ||
| 144 | That's it! Following this guide, I have a functional =scli= program that | |
| 145 | successfully sends messages to my contacts and myself! | |
content/blog/2023-10-17-self-hosting-anonymousoverflow.md → blog/self-hosting-anonymousoverflow/index.org renamed +27 −33
| @@ -1,35 +1,30 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-10-17 | |
| 3 | title = "Self-Hosting AnonymousOverflow" | |
| 4 | description = "A guide to self-hosting the AnonymousOverflow application on your own server." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Overview | |
| 1 | #+title: Self-Hosting AnonymousOverflow | |
| 2 | #+date: 2023-10-17 | |
| 3 | #+description: A guide to self-hosting the AnonymousOverflow application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 8 | 5 | |
| 6 | * Overview | |
| 9 | 7 | I recently launched an instance of AnonymousOverflow at |
| 10 | [ao.cleberg.net](https://ao.cleberg.net) and wanted to write a brief | |
| 8 | [[https://ao.cleberg.net][ao.cleberg.net]] and wanted to write a brief | |
| 11 | 9 | post on how easy it is to install with Docker Compose and Nginx. |
| 12 | 10 | |
| 13 | 11 | This guide uses Ubuntu server, Docker Compose, and Nginx as a reverse |
| 14 | 12 | proxy. |
| 15 | 13 | |
| 16 | ## Installation | |
| 17 | ||
| 18 | ### Docker Compose | |
| 19 | ||
| 14 | * Installation | |
| 15 | ** Docker Compose | |
| 20 | 16 | To install AnonymousOverflow, start by creating a directory for the |
| 21 | application and create its `docker-compose.yml` file. | |
| 17 | application and create its =docker-compose.yml= file. | |
| 22 | 18 | |
| 23 | ```sh | |
| 19 | #+begin_src sh | |
| 24 | 20 | mkdir ~/anonymousoverflow && cd ~/anonymousoverflow |
| 25 | 21 | nano docker-compose.yml |
| 26 | ``` | |
| 22 | #+end_src | |
| 27 | 23 | |
| 28 | 24 | Within this file, paste the following information. Be sure to change the |
| 29 | `APP_URL`, `JWT_SIGNING_SECRET`, and | |
| 30 | `ports` to match your needs. | |
| 25 | =APP_URL=, =JWT_SIGNING_SECRET=, and =ports= to match your needs. | |
| 31 | 26 | |
| 32 | ```yaml | |
| 27 | #+begin_src yaml | |
| 33 | 28 | version: '3' |
| 34 | 29 | |
| 35 | 30 | services: |
| @@ -42,32 +37,30 @@ services: | ||
| 42 | 37 | ports: |
| 43 | 38 | - '9380:8080' |
| 44 | 39 | restart: 'always' |
| 45 | ``` | |
| 40 | #+end_src | |
| 46 | 41 | |
| 47 | 42 | Save and exit the file when complete. You can now launch the container |
| 48 | 43 | and access it via your local network. |
| 49 | 44 | |
| 50 | ```sh | |
| 45 | #+begin_src sh | |
| 51 | 46 | sudo docker-compose up -d |
| 52 | ``` | |
| 53 | ||
| 54 | ### Nginx Reverse Proxy | |
| 47 | #+end_src | |
| 55 | 48 | |
| 49 | ** Nginx Reverse Proxy | |
| 56 | 50 | If you want to access this service outside the local network, I |
| 57 | 51 | recommend using Nginx as a reverse proxy. |
| 58 | 52 | |
| 59 | 53 | Let's start by creating a configuration file. |
| 60 | 54 | |
| 61 | ```sh | |
| 55 | #+begin_src sh | |
| 62 | 56 | sudo nano /etc/nginx/sites-available/ao |
| 63 | ``` | |
| 57 | #+end_src | |
| 64 | 58 | |
| 65 | 59 | Within this file, paste the following content and repace |
| 66 | `ao.example.com` with your URL. You may need to update the | |
| 67 | SSL certificate statements if your certificates are in a different | |
| 68 | location. | |
| 60 | =ao.example.com= with your URL. You may need to update the SSL | |
| 61 | certificate statements if your certificates are in a different location. | |
| 69 | 62 | |
| 70 | ```conf | |
| 63 | #+begin_src conf | |
| 71 | 64 | server { |
| 72 | 65 | if ($host ~ ^[^.]+\.cleberg\.net$) { |
| 73 | 66 | return 301 https://$host$request_uri; |
| @@ -119,15 +112,16 @@ server { | ||
| 119 | 112 | proxy_buffers 64 256k; |
| 120 | 113 | } |
| 121 | 114 | } |
| 122 | ``` | |
| 115 | #+end_src | |
| 123 | 116 | |
| 124 | 117 | Save and exit the file when complete. On Ubuntu, you will need to |
| 125 | 118 | symlink the configuration file before it will be recognized by Nginx. |
| 126 | 119 | Once complete, simply restart the web server. |
| 127 | 120 | |
| 128 | ```sh | |
| 121 | #+begin_src sh | |
| 129 | 122 | sudo ln -s /etc/nginx/sites-available/ao /etc/nginx/sites-enabled/ao |
| 130 | 123 | sudo systemctl restart nginx.service |
| 131 | ``` | |
| 124 | #+end_src | |
| 132 | 125 | |
| 133 | The website will now be available publicly. Visit [my instance](https://ao.cleberg.net) for an example. | |
| 126 | The website will now be available publicly. Visit | |
| 127 | [[https://ao.cleberg.net][my instance]] for an example. | |
content/blog/2023-10-11-self-hosting-authelia.md → blog/self-hosting-authelia/index.org renamed +84 −98
| @@ -1,12 +1,10 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-10-11 | |
| 3 | title = "Self-Hosting Authelia" | |
| 4 | description = "A guide to self-hosting the Authelia application on your own server." | |
| 5 | +++ | |
| 1 | #+title: Self-Hosting Authelia | |
| 2 | #+date: 2023-10-11 | |
| 3 | #+description: A guide to self-hosting the Authelia application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 6 | 5 | |
| 7 | ## Overview | |
| 8 | ||
| 9 | [Authelia](https://www.authelia.com/) is an open-source authentication | |
| 6 | * Overview | |
| 7 | [[https://www.authelia.com/][Authelia]] is an open-source authentication | |
| 10 | 8 | service that allows you to place a portal between end users on the |
| 11 | 9 | internet and self-hosted services on your server. |
| 12 | 10 | |
| @@ -15,42 +13,38 @@ authentication for any such user before allowing them to access a | ||
| 15 | 13 | specific service on your domain. |
| 16 | 14 | |
| 17 | 15 | This guide will walk through a standard installation of Authelia for |
| 18 | `example.com`, using `auth.example.com` as | |
| 19 | Authelia's authentication domain and `teddit.example.com` as | |
| 20 | the website we want to protect behind the authentication portal. | |
| 21 | ||
| 22 | ## Prerequisites | |
| 16 | =example.com=, using =auth.example.com= as Authelia's authentication | |
| 17 | domain and =teddit.example.com= as the website we want to protect behind | |
| 18 | the authentication portal. | |
| 23 | 19 | |
| 20 | * Prerequisites | |
| 24 | 21 | This guide assumes you have the following already set-up: |
| 25 | 22 | |
| 26 | - A registered domain with DNS pointing to your server. | |
| 27 | - A subdomain for Authelia (`auth.example.com`) and a | |
| 28 | subdomain to protect via Authelia (`app.example.com`). | |
| 29 | - A working Nginx web server. | |
| 30 | - Docker and docker-compose installed. | |
| 31 | ||
| 32 | ## Installation | |
| 23 | - A registered domain with DNS pointing to your server. | |
| 24 | - A subdomain for Authelia (=auth.example.com=) and a subdomain to | |
| 25 | protect via Authelia (=app.example.com=). | |
| 26 | - A working Nginx web server. | |
| 27 | - Docker and docker-compose installed. | |
| 33 | 28 | |
| 29 | * Installation | |
| 34 | 30 | This guide will walk through each installation step one-by-one, starting |
| 35 | 31 | with the container and finishing by cleaning up external access via an |
| 36 | 32 | Nginx reverse proxy. |
| 37 | 33 | |
| 38 | ### Docker-Compose | |
| 39 | ||
| 34 | ** Docker-Compose | |
| 40 | 35 | To start, create a directory for Authelia and create a |
| 41 | `docker-compose.yml` file. | |
| 36 | =docker-compose.yml= file. | |
| 42 | 37 | |
| 43 | ```sh | |
| 38 | #+begin_src sh | |
| 44 | 39 | mkdir ~/authelia |
| 45 | 40 | nano ~/authelia/docker-compose.yml |
| 46 | ``` | |
| 41 | #+end_src | |
| 47 | 42 | |
| 48 | 43 | Within this file, paste the following content. If you prefer a different |
| 49 | 44 | local port, modify the port on the left side of the colon on the |
| 50 | `9091:9091` line. Be sure to modify the `TZ` | |
| 51 | variable to your timezone. | |
| 45 | =9091:9091= line. Be sure to modify the =TZ= variable to your timezone. | |
| 52 | 46 | |
| 53 | ```yml | |
| 47 | #+begin_src yml | |
| 54 | 48 | version: '3.3' |
| 55 | 49 | |
| 56 | 50 | services: |
| @@ -63,55 +57,52 @@ services: | ||
| 63 | 57 | - 9091:9091 |
| 64 | 58 | environment: |
| 65 | 59 | - TZ=America/Chicago |
| 66 | ``` | |
| 60 | #+end_src | |
| 67 | 61 | |
| 68 | 62 | Start the container with docker-compose: |
| 69 | 63 | |
| 70 | ```sh | |
| 64 | #+begin_src sh | |
| 71 | 65 | sudo docker-compose up -d |
| 72 | ``` | |
| 66 | #+end_src | |
| 73 | 67 | |
| 74 | 68 | After the first start, the container will automatically exit and require |
| 75 | 69 | you to modify the app's configuration files before continuing. Read on |
| 76 | 70 | to learn more. |
| 77 | 71 | |
| 78 | ### Authelia Configuration | |
| 79 | ||
| 72 | ** Authelia Configuration | |
| 80 | 73 | To configure Authelia before we restart the container, we need to open |
| 81 | the `config` directory and modify the files. Start by editing | |
| 82 | the `configuration.yml` file, where all of Authelia's | |
| 83 | settings are stored. | |
| 74 | the =config= directory and modify the files. Start by editing the | |
| 75 | =configuration.yml= file, where all of Authelia's settings are stored. | |
| 84 | 76 | |
| 85 | 77 | My personal preference is to copy the original configuration file to a |
| 86 | 78 | backup file and edit a fresh copy. |
| 87 | 79 | |
| 88 | ```sh | |
| 80 | #+begin_src sh | |
| 89 | 81 | sudo cp ~/authelia/config/configuration.yml ~/authelia/config/configuration.yml.bk |
| 90 | 82 | sudo nano ~/authelia/config/configuration.yml |
| 91 | ``` | |
| 83 | #+end_src | |
| 92 | 84 | |
| 93 | Within the blank `configuration.yml` file, paste the | |
| 94 | following information. You will need to make quite a few updates, so be | |
| 95 | sure to read each line carefully and modify as necessary. | |
| 85 | Within the blank =configuration.yml= file, paste the following | |
| 86 | information. You will need to make quite a few updates, so be sure to | |
| 87 | read each line carefully and modify as necessary. | |
| 96 | 88 | |
| 97 | 89 | The major required changes are: |
| 98 | 90 | |
| 99 | - Any instances of `example.com` should be replaced by your | |
| 100 | domain. | |
| 101 | - `jwt_secret` - Use the `pwgen 40 1` command to | |
| 102 | generate a secret for yourself. | |
| 103 | - `access_control` - Set the Authelia domain to bypass | |
| 104 | here, as well as any subdomains you want to protect. | |
| 105 | - `session` > `secret` - Use the | |
| 106 | `pwgen 40 1` command to generate a secret for yourself. | |
| 107 | - `regulation` - Set the variables here to restrict login | |
| 108 | attempts and bans. | |
| 109 | - `storage` > `encryption_key` - Use the | |
| 110 | `pwgen 40 1` command to generate a secret for yourself. | |
| 111 | - `smtp` - If you have access to an SMTP service, set up | |
| 112 | the information here to active outgoing emails. | |
| 113 | ||
| 114 | ```yml | |
| 91 | - Any instances of =example.com= should be replaced by your domain. | |
| 92 | - =jwt_secret= - Use the =pwgen 40 1= command to generate a secret for | |
| 93 | yourself. | |
| 94 | - =access_control= - Set the Authelia domain to bypass here, as well as | |
| 95 | any subdomains you want to protect. | |
| 96 | - =session= > =secret= - Use the =pwgen 40 1= command to generate a | |
| 97 | secret for yourself. | |
| 98 | - =regulation= - Set the variables here to restrict login attempts and | |
| 99 | bans. | |
| 100 | - =storage= > =encryption_key= - Use the =pwgen 40 1= command to | |
| 101 | generate a secret for yourself. | |
| 102 | - =smtp= - If you have access to an SMTP service, set up the information | |
| 103 | here to active outgoing emails. | |
| 104 | ||
| 105 | #+begin_src yml | |
| 115 | 106 | # yamllint disable rule:comments-indentation |
| 116 | 107 | --- |
| 117 | 108 | ############################################################################### |
| @@ -200,26 +191,25 @@ notifier: | ||
| 200 | 191 | skip_verify: false |
| 201 | 192 | minimum_version: TLS1.2 |
| 202 | 193 | ... |
| 203 | ``` | |
| 204 | ||
| 205 | ### Authelia Users | |
| 194 | #+end_src | |
| 206 | 195 | |
| 196 | ** Authelia Users | |
| 207 | 197 | Next, create the users file for authentication. |
| 208 | 198 | |
| 209 | ```sh | |
| 199 | #+begin_src sh | |
| 210 | 200 | sudo nano ~/authelia/config/users_database.yml |
| 211 | ``` | |
| 201 | #+end_src | |
| 212 | 202 | |
| 213 | 203 | Within the file, you will need to create an entry for each user that |
| 214 | needs access to Authelia. The `my_username` entry will be the | |
| 215 | username used on the login page. | |
| 204 | needs access to Authelia. The =my_username= entry will be the username | |
| 205 | used on the login page. | |
| 216 | 206 | |
| 217 | To generate the password, go to [Argon2 Hash | |
| 218 | Generator](https://argon2.online), generate a random salt, and make sure | |
| 219 | the rest of the settings match the `authentication_backend` | |
| 220 | section of `configuration.yml` file. | |
| 207 | To generate the password, go to [[https://argon2.online][Argon2 Hash | |
| 208 | Generator]], generate a random salt, and make sure the rest of the | |
| 209 | settings match the =authentication_backend= section of | |
| 210 | =configuration.yml= file. | |
| 221 | 211 | |
| 222 | ```yaml | |
| 212 | #+begin_src yaml | |
| 223 | 213 | users: |
| 224 | 214 | my_username: |
| 225 | 215 | displayname: "My User" |
| @@ -230,32 +220,30 @@ users: | ||
| 230 | 220 | groups: |
| 231 | 221 | - admins |
| 232 | 222 | - dev |
| 233 | ``` | |
| 223 | #+end_src | |
| 234 | 224 | |
| 235 | 225 | Once the app is configured, restart the container from scratch. |
| 236 | 226 | |
| 237 | ```sh | |
| 227 | #+begin_src sh | |
| 238 | 228 | cd ~/authelia |
| 239 | 229 | sudo docker-compose down && sudo docker-compose up -d |
| 240 | ``` | |
| 241 | ||
| 242 | ### Nginx: Authelia Domain | |
| 230 | #+end_src | |
| 243 | 231 | |
| 232 | ** Nginx: Authelia Domain | |
| 244 | 233 | Once the container is running and configured, the final step is to |
| 245 | 234 | configure external access to the server via Nginx reverse proxy. |
| 246 | 235 | |
| 247 | 236 | Start by creating the Authelia domain. |
| 248 | 237 | |
| 249 | ```sh | |
| 238 | #+begin_src sh | |
| 250 | 239 | sudo nano /etc/nginx/sites-available/auth |
| 251 | ``` | |
| 240 | #+end_src | |
| 252 | 241 | |
| 253 | 242 | Within this file, paste the following information and be sure to update |
| 254 | `example.com` to your domain. Make sure the | |
| 255 | `$upstream_authelia` variable matches the location of your | |
| 256 | Authelia container. | |
| 243 | =example.com= to your domain. Make sure the =$upstream_authelia= | |
| 244 | variable matches the location of your Authelia container. | |
| 257 | 245 | |
| 258 | ```conf | |
| 246 | #+begin_src conf | |
| 259 | 247 | server { |
| 260 | 248 | if ($host ~ ^[^.]+\.example\.com$) { |
| 261 | 249 | return 301 https://$host$request_uri; |
| @@ -307,30 +295,29 @@ server { | ||
| 307 | 295 | } |
| 308 | 296 | |
| 309 | 297 | } |
| 310 | ``` | |
| 298 | #+end_src | |
| 311 | 299 | |
| 312 | 300 | Next, symlink the file and restart Nginx. If there are errors, be sure |
| 313 | 301 | to resolve those before moving on. |
| 314 | 302 | |
| 315 | ```sh | |
| 303 | #+begin_src sh | |
| 316 | 304 | sudo ln -s /etc/nginx/sites-available/auth /etc/nginx/sites-enabled/auth |
| 317 | 305 | sudo systemctl restart nginx.service |
| 318 | ``` | |
| 319 | ||
| 320 | ### Nginx: Protected Domain(s) | |
| 306 | #+end_src | |
| 321 | 307 | |
| 308 | ** Nginx: Protected Domain(s) | |
| 322 | 309 | Now that Authelia is accessible externally, you need to configure the |
| 323 | 310 | domain you intend to protect with Authelia. In this example, I'm |
| 324 | protecting `teddit.example.com`. | |
| 311 | protecting =teddit.example.com=. | |
| 325 | 312 | |
| 326 | 313 | Similar to the process above, paste the content and update the relevant |
| 327 | 314 | variables. |
| 328 | 315 | |
| 329 | ```sh | |
| 316 | #+begin_src sh | |
| 330 | 317 | sudo nano /etc/nginx/sites-available/teddit |
| 331 | ``` | |
| 318 | #+end_src | |
| 332 | 319 | |
| 333 | ```conf | |
| 320 | #+begin_src conf | |
| 334 | 321 | server { |
| 335 | 322 | if ($host ~ ^[^.]+\.example\.com$) { |
| 336 | 323 | return 301 https://$host$request_uri; |
| @@ -432,26 +419,25 @@ server { | ||
| 432 | 419 | proxy_buffers 64 256k; |
| 433 | 420 | } |
| 434 | 421 | } |
| 435 | ``` | |
| 422 | #+end_src | |
| 436 | 423 | |
| 437 | 424 | Same as before, symlink the file and restart Nginx. |
| 438 | 425 | |
| 439 | ```sh | |
| 426 | #+begin_src sh | |
| 440 | 427 | sudo ln -s /etc/nginx/sites-available/teddit /etc/nginx/sites-enabled/teddit |
| 441 | 428 | sudo systemctl restart nginx.service |
| 442 | ``` | |
| 443 | ||
| 444 | ## Results | |
| 429 | #+end_src | |
| 445 | 430 | |
| 431 | * Results | |
| 446 | 432 | When visiting the protected domain, you will now be redirected to your |
| 447 | 433 | authentication domain and presented with the Authelia login portal. |
| 448 | 434 | |
| 449 |  | |
| 435 | #+caption: Authelia Portal | |
| 436 | [[https://img.cleberg.net/blog/20231010-authelia/authelia_portal.png]] | |
| 451 | 437 | |
| 452 | 438 | Once you've successfully authenticated, you can visit your |
| 453 | 439 | authentication domain directly and see that you're currently |
| 454 | 440 | authenticated to any domain protected by Authelia. |
| 455 | 441 | |
| 456 |  | |
| 442 | #+caption: Authelia Success | |
| 443 | [[https://img.cleberg.net/blog/20231010-authelia/authelia_success.png]] | |
content/blog/2023-06-08-self-hosting-baikal-server.md → blog/self-hosting-baikal/index.org renamed +48 −57
| @@ -1,34 +1,30 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-06-08 | |
| 3 | title = "Self-Hosting Baikal Server (CalDAV & CardDAV)" | |
| 4 | description = "A guide to self-hosting the Baikal application on your own server." | |
| 5 | +++ | |
| 1 | #+title: Self-Hosting Baikal Server (CalDAV & CardDAV) | |
| 2 | #+date: 2023-06-08 | |
| 3 | #+description: A guide to self-hosting the Baikal application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 6 | 5 | |
| 7 | ## What is Baikal? | |
| 8 | ||
| 9 | [Baikal](https://sabre.io/baikal/) is a lightweight CalDAV + CardDAV | |
| 6 | * What is Baikal? | |
| 7 | [[https://sabre.io/baikal/][Baikal]] is a lightweight CalDAV + CardDAV | |
| 10 | 8 | server that you can self-host on your own machine. While I have tried (& |
| 11 | 9 | failed) to get this CalDAV + CardDAV server running before, it was quite |
| 12 | 10 | easy this time. Not really sure what I did differently this time, but |
| 13 | 11 | I'm documenting my process here to ensure I don't forget. |
| 14 | 12 | |
| 15 | ## Installation | |
| 16 | ||
| 17 | First, create a folder on your server and open a | |
| 18 | `docker-compose.yml` file for editing: | |
| 13 | * Installation | |
| 14 | First, create a folder on your server and open a =docker-compose.yml= | |
| 15 | file for editing: | |
| 19 | 16 | |
| 20 | ```sh | |
| 17 | #+begin_src sh | |
| 21 | 18 | mkdir baikal && cd baikal |
| 22 | 19 | nano docker-compose.yml |
| 23 | ``` | |
| 20 | #+end_src | |
| 24 | 21 | |
| 25 | 22 | Within this file, you'll need to paste the information below. You can |
| 26 | customize the `ports` section to use any port on your server | |
| 27 | to pass through to port 80 in the container. You can also edit the | |
| 28 | `volumes` section to use docker volumes instead of local | |
| 29 | folders. | |
| 23 | customize the =ports= section to use any port on your server to pass | |
| 24 | through to port 80 in the container. You can also edit the =volumes= | |
| 25 | section to use docker volumes instead of local folders. | |
| 30 | 26 | |
| 31 | ```conf | |
| 27 | #+begin_src conf | |
| 32 | 28 | version: "2" |
| 33 | 29 | services: |
| 34 | 30 | baikal: |
| @@ -39,45 +35,41 @@ services: | ||
| 39 | 35 | volumes: |
| 40 | 36 | - ./config:/var/www/baikal/config |
| 41 | 37 | - ./data:/var/www/baikal/Specific |
| 42 | ``` | |
| 38 | #+end_src | |
| 43 | 39 | |
| 44 | 40 | Once finished with editing, save and close the file. Then, launch the |
| 45 | 41 | docker container: |
| 46 | 42 | |
| 47 | ```sh | |
| 43 | #+begin_src sh | |
| 48 | 44 | sudo docker-compose up -d |
| 49 | ``` | |
| 50 | ||
| 51 | ## Intial Setup | |
| 45 | #+end_src | |
| 52 | 46 | |
| 47 | * Intial Setup | |
| 53 | 48 | As long as no issues came up when starting the container, you should be |
| 54 | able to visit the server's set-up page at | |
| 55 | `http://<server_ip>:<port>`. The application will ask you to | |
| 56 | create an administrator account and choose the database type for your | |
| 57 | storage. Personally, I opted to use SQLite. | |
| 49 | able to visit the server's set-up page at =http://<server_ip>:<port>=. | |
| 50 | The application will ask you to create an administrator account and | |
| 51 | choose the database type for your storage. Personally, I opted to use | |
| 52 | SQLite. | |
| 58 | 53 | |
| 59 | 54 | Make sure the administrator credentials are adequate to protect against |
| 60 | 55 | common attacks. |
| 61 | 56 | |
| 62 | ## Creating Users | |
| 63 | ||
| 64 | Once you've set up the application, you will be greeted by the | |
| 65 | Dashboard page, which will show the version of the app, status of the | |
| 57 | * Creating Users | |
| 58 | Once you've set up the application, you will be greeted by the Dashboard | |
| 59 | page, which will show the version of the app, status of the | |
| 66 | 60 | admin/CalDAV/CardDAV services, and the number of users, calendars, |
| 67 | 61 | events, address books, and contacts. |
| 68 | 62 | |
| 69 |  | |
| 63 | #+caption: Baikal Dashboard | |
| 64 | [[https://img.cleberg.net/blog/20230608-baikal/baikal-dashboard.png]] | |
| 71 | 65 | |
| 72 | To create a new user, navigate to the `Users and resources` | |
| 73 | page. This process is as simple as entering a username, password, and | |
| 74 | email. | |
| 66 | To create a new user, navigate to the =Users and resources= page. This | |
| 67 | process is as simple as entering a username, password, and email. | |
| 75 | 68 | |
| 76 | 69 | Once a user has been created, you can create any number of calendars and |
| 77 | 70 | address books for user, as well as inspect their information. |
| 78 | 71 | |
| 79 | ## Setting Up a Public URL | |
| 80 | ||
| 72 | * Setting Up a Public URL | |
| 81 | 73 | Once your application is working locally, you can open access remotely |
| 82 | 74 | via a URL by using a reverse-proxy like Nginx. |
| 83 | 75 | |
| @@ -87,15 +79,15 @@ point a domain name to the server hosting Baikal. | ||
| 87 | 79 | Start by navigating to your web server's configuration directory and |
| 88 | 80 | create a new file for this application. |
| 89 | 81 | |
| 90 | ```sh | |
| 82 | #+begin_src sh | |
| 91 | 83 | cd /etc/nginx/sites-available/ |
| 92 | 84 | nano dav |
| 93 | ``` | |
| 85 | #+end_src | |
| 94 | 86 | |
| 95 | 87 | Within this file, paste in the configuration from below and change |
| 96 | `dav.example.com` to match the URL you'll be using. | |
| 88 | =dav.example.com= to match the URL you'll be using. | |
| 97 | 89 | |
| 98 | ```conf | |
| 90 | #+begin_src conf | |
| 99 | 91 | server { |
| 100 | 92 | if ($host ~ ^[^.]+\.example\.com$) { |
| 101 | 93 | return 301 https://$host$request_uri; |
| @@ -125,35 +117,34 @@ server { | ||
| 125 | 117 | include /etc/letsencrypt/options-ssl-nginx.conf; |
| 126 | 118 | ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; |
| 127 | 119 | } |
| 128 | ``` | |
| 120 | #+end_src | |
| 129 | 121 | |
| 130 | 122 | For Nginx on Ubuntu, you'll need to symlink the configuration file to |
| 131 | the `sites-enabled` directory and then restart Nginx. | |
| 123 | the =sites-enabled= directory and then restart Nginx. | |
| 132 | 124 | |
| 133 | ```sh | |
| 125 | #+begin_src sh | |
| 134 | 126 | sudo ln -s /etc/nginx/sites-available/dav /etc/nginx/sites-enabled/dav |
| 135 | 127 | sudo systemctl restart nginx.service |
| 136 | ``` | |
| 128 | #+end_src | |
| 137 | 129 | |
| 138 | 130 | At this point, the Baikal server should be available over the internet |
| 139 | 131 | at the URL configured above! |
| 140 | 132 | |
| 141 | ## Configuring Clients | |
| 142 | ||
| 133 | * Configuring Clients | |
| 143 | 134 | Lastly, configuring clients and applications is essential to making sure |
| 144 | 135 | the DAV server is being fully utilized. |
| 145 | 136 | |
| 146 | You can also use the `Users and resources` page to inspect a | |
| 147 | user's personal link to their calendars and address books by clicking | |
| 148 | the info (i) button. It will show a URI like | |
| 149 | `/dav.php/calendars/your-user/default/`. | |
| 137 | You can also use the =Users and resources= page to inspect a user's | |
| 138 | personal link to their calendars and address books by clicking the info | |
| 139 | (i) button. It will show a URI like | |
| 140 | =/dav.php/calendars/your-user/default/=. | |
| 150 | 141 | |
| 151 | 142 | However, I found that the following URL works for most applications: |
| 152 | `/dav.php/principals/your-user/`. | |
| 143 | =/dav.php/principals/your-user/=. | |
| 153 | 144 | |
| 154 | I used the `principals` URL above for Thunderbird (calendar, | |
| 155 | tasks, and contacts), as well as iOS (calendar, tasks, and contacts) and | |
| 156 | everything works flawlessly so far. | |
| 145 | I used the =principals= URL above for Thunderbird (calendar, tasks, and | |
| 146 | contacts), as well as iOS (calendar, tasks, and contacts) and everything | |
| 147 | works flawlessly so far. | |
| 157 | 148 | |
| 158 | 149 | Syncing is quick between the server and clients, and I haven't seen any |
| 159 | 150 | disruptions in the service or data integrity. |
content/blog/2023-06-23-self-hosting-convos-irc.md → blog/self-hosting-convos/index.org renamed +62 −68
| @@ -1,43 +1,39 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-06-23 | |
| 3 | title = "Self-Hosting Convos IRC Web Client" | |
| 4 | description = "A guide to self-hosting the Convos application on your own server." | |
| 5 | +++ | |
| 1 | #+title: Self-Hosting Convos IRC Web Client | |
| 2 | #+date: 2023-06-23 | |
| 3 | #+description: A guide to self-hosting the Convos application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 6 | 5 | |
| 7 | ## Convos | |
| 8 | ||
| 9 | [Convos](https://convos.chat/) is an always-online web client for IRC. | |
| 6 | * Convos | |
| 7 | [[https://convos.chat/][Convos]] is an always-online web client for IRC. | |
| 10 | 8 | It has a few features that made it attractive to me as a self-hosted |
| 11 | 9 | option: |
| 12 | 10 | |
| 13 | - Extremely simple Docker Compose installation method. | |
| 14 | - Runs in the background and monitors chats even while you're not | |
| 15 | logged in. | |
| 16 | - Neatly organized sidebar for conversation and client settings. | |
| 17 | - Ability to connect to different hosts and create profiles for hosts. | |
| 18 | - By default, registration is closed to the public. You can enable | |
| 19 | public registration on the Settings page or generate invitation | |
| 20 | links on the Users page. | |
| 21 | - Customization of the client theme, organization name and URL, admin | |
| 22 | email, and video service. | |
| 23 | ||
| 24 | ## Docker Installation | |
| 25 | ||
| 26 | To install Convos, simply create a directory and a | |
| 27 | `docker-compose.yml` file: | |
| 28 | ||
| 29 | ```sh | |
| 11 | - Extremely simple Docker Compose installation method. | |
| 12 | - Runs in the background and monitors chats even while you're not logged | |
| 13 | in. | |
| 14 | - Neatly organized sidebar for conversation and client settings. | |
| 15 | - Ability to connect to different hosts and create profiles for hosts. | |
| 16 | - By default, registration is closed to the public. You can enable | |
| 17 | public registration on the Settings page or generate invitation links | |
| 18 | on the Users page. | |
| 19 | - Customization of the client theme, organization name and URL, admin | |
| 20 | email, and video service. | |
| 21 | ||
| 22 | * Docker Installation | |
| 23 | To install Convos, simply create a directory and a =docker-compose.yml= | |
| 24 | file: | |
| 25 | ||
| 26 | #+begin_src sh | |
| 30 | 27 | mkdir ~/convos && cd ~/convos |
| 31 | 28 | nano docker-compose.yml |
| 32 | ``` | |
| 29 | #+end_src | |
| 33 | 30 | |
| 34 | With the `docker-compose.yml` file open, paste the | |
| 35 | configuration below into the file. You can customize the host port to be | |
| 36 | something unique, such as `21897:3000`. You can also change | |
| 37 | the `data` folder to be a docker volume instead, if you | |
| 38 | prefer. | |
| 31 | With the =docker-compose.yml= file open, paste the configuration below | |
| 32 | into the file. You can customize the host port to be something unique, | |
| 33 | such as =21897:3000=. You can also change the =data= folder to be a | |
| 34 | docker volume instead, if you prefer. | |
| 39 | 35 | |
| 40 | ```config | |
| 36 | #+begin_src config | |
| 41 | 37 | version: '3' |
| 42 | 38 | |
| 43 | 39 | services: |
| @@ -50,33 +46,31 @@ services: | ||
| 50 | 46 | environment: |
| 51 | 47 | - CONVOS_REVERSE_PROXY=1 |
| 52 | 48 | restart: always |
| 53 | ``` | |
| 49 | #+end_src | |
| 54 | 50 | |
| 55 | Save the `docker-compose.yml` file and bring the container | |
| 56 | up: | |
| 51 | Save the =docker-compose.yml= file and bring the container up: | |
| 57 | 52 | |
| 58 | ```sh | |
| 53 | #+begin_src sh | |
| 59 | 54 | sudo docker-compose up -d |
| 60 | ``` | |
| 55 | #+end_src | |
| 61 | 56 | |
| 62 | At this point, Convos is available at `<server_ip>:3000` but | |
| 63 | not available to the public. | |
| 64 | ||
| 65 | ## Nginx Reverse Proxy | |
| 57 | At this point, Convos is available at =<server_ip>:3000= but not | |
| 58 | available to the public. | |
| 66 | 59 | |
| 60 | * Nginx Reverse Proxy | |
| 67 | 61 | If you're using Nginx, you can create a configuration file for the |
| 68 | 62 | convos application. Start by opening the file: |
| 69 | 63 | |
| 70 | ```sh | |
| 64 | #+begin_src sh | |
| 71 | 65 | nano /etc/nginx/sites-available/convos |
| 72 | ``` | |
| 66 | #+end_src | |
| 73 | 67 | |
| 74 | 68 | Within the nginx configuration file, paste the following content and be |
| 75 | sure to update `convos.example.com` to match your domain and | |
| 76 | `127.0.0.1:3000` to match the port you opened in the | |
| 77 | `docker-compose.yml` file. | |
| 69 | sure to update =convos.example.com= to match your domain and | |
| 70 | =127.0.0.1:3000= to match the port you opened in the | |
| 71 | =docker-compose.yml= file. | |
| 78 | 72 | |
| 79 | ```config | |
| 73 | #+begin_src config | |
| 80 | 74 | # Host and port where convos is running |
| 81 | 75 | upstream convos_upstream { server 127.0.0.1:3000; } |
| 82 | 76 | |
| @@ -114,53 +108,53 @@ server { | ||
| 114 | 108 | include /etc/letsencrypt/options-ssl-nginx.conf; |
| 115 | 109 | ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; |
| 116 | 110 | } |
| 117 | ``` | |
| 111 | #+end_src | |
| 118 | 112 | |
| 119 | Once the file is saved, link it to the `sites-enabled` | |
| 120 | directory and restart Nginx. | |
| 113 | Once the file is saved, link it to the =sites-enabled= directory and | |
| 114 | restart Nginx. | |
| 121 | 115 | |
| 122 | ```sh | |
| 116 | #+begin_src sh | |
| 123 | 117 | sudo ln -s /etc/nginx/sites-available/convos /etc/nginx/sites-enabled/convos |
| 124 | 118 | sudo systemctl restart nginx.service |
| 125 | ``` | |
| 126 | ||
| 127 | ## Screenshots | |
| 119 | #+end_src | |
| 128 | 120 | |
| 121 | * Screenshots | |
| 129 | 122 | See the screenshots below for an example of the Convos homepage and an |
| 130 | 123 | excerpt of the chat screen. |
| 131 | 124 | |
| 132 | 125 | There are numerous themes to choose from; the theme shown in the images |
| 133 | 126 | below is Dracula. |
| 134 | 127 | |
| 135 |  | |
| 136 | ||
| 137 |  | |
| 128 | #+caption: Convos Home | |
| 129 | [[https://img.cleberg.net/blog/20230623-convos/convos_home.png]] | |
| 138 | 130 | |
| 139 | ## Registering a Nickname | |
| 131 | #+caption: Convos Chat | |
| 132 | [[https://img.cleberg.net/blog/20230623-convos/convos_chat.png]] | |
| 140 | 133 | |
| 134 | * Registering a Nickname | |
| 141 | 135 | Hop into the server channel so that you can message NickServ. In the |
| 142 | 136 | case of Convos, the default sever is libera.chat. Simply click the |
| 143 | `libera` conversation at the top of the sidebar to open it. | |
| 144 | Once the chat is open, you can claim a nickname by typing: | |
| 137 | =libera= conversation at the top of the sidebar to open it. Once the | |
| 138 | chat is open, you can claim a nickname by typing: | |
| 145 | 139 | |
| 146 | ```txt | |
| 140 | #+begin_src txt | |
| 147 | 141 | /nick <nick> |
| 148 | ``` | |
| 142 | #+end_src | |
| 149 | 143 | |
| 150 | If the nickname is available, and you'd like to register the nickname | |
| 151 | to yourself, you'll need to type another command: | |
| 144 | If the nickname is available, and you'd like to register the nickname to | |
| 145 | yourself, you'll need to type another command: | |
| 152 | 146 | |
| 153 | ```txt | |
| 147 | #+begin_src txt | |
| 154 | 148 | /msg NickServ REGISTER |
| 155 | 149 | <password> <email> |
| 156 | ``` | |
| 150 | #+end_src | |
| 157 | 151 | |
| 158 | 152 | On libera.chat, the server will send a confirmation email with a command |
| 159 | 153 | that you must message in IRC to verify registration of the nickname: |
| 160 | 154 | |
| 161 | ```txt | |
| 155 | #+begin_src txt | |
| 162 | 156 | /msg NickServ VERIFY REGISTER <nick> <verification_code> |
| 163 | ``` | |
| 157 | #+end_src | |
| 164 | 158 | |
| 165 | 159 | Once entered, the server should confirm registration of the nickname to |
| 166 | 160 | the supplied email with the password specified. |
content/blog/2022-06-07-freshrss.md → blog/self-hosting-freshrss/index.org renamed +90 −112
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-06-07 | |
| 3 | title = "Self-Hosting FreshRSS" | |
| 4 | description = "A guide to self-hosting the FreshRSS application on your own server." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Why RSS? | |
| 1 | #+title: Self-Hosting FreshRSS | |
| 2 | #+date: 2022-06-07 | |
| 3 | #+description: A guide to self-hosting the FreshRSS application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 8 | 5 | |
| 6 | * Why RSS? | |
| 9 | 7 | After noticing that I have collected 50+ blogs as bookmarks, I decided |
| 10 | 8 | to migrate back to using RSS feeds to stay up-to-date with my favorite |
| 11 | 9 | websites. Using RSS allows me to read all of these posts in a single app |
| @@ -16,56 +14,49 @@ However, I ran into one issue: syncing subscriptions and read/unread | ||
| 16 | 14 | posts across devices. Since I want to be able to easily read on both |
| 17 | 15 | mobile and desktop, I decided to look for a self-hosted RSS solution. |
| 18 | 16 | |
| 19 | Thus, I found [FreshRSS](https://www.freshrss.org/) and was able to | |
| 17 | Thus, I found [[https://www.freshrss.org/][FreshRSS]] and was able to | |
| 20 | 18 | successfully install it on my server in about 30 minutes. |
| 21 | 19 | |
| 22 | ## Documentation | |
| 23 | ||
| 24 | While it's certainly not robust, the [FreshRSS | |
| 25 | documentation](https://freshrss.github.io/FreshRSS/) is helpful for | |
| 26 | figuring out basic information about the service. | |
| 20 | * Documentation | |
| 21 | While it's certainly not robust, the | |
| 22 | [[https://freshrss.github.io/FreshRSS/][FreshRSS documentation]] is | |
| 23 | helpful for figuring out basic information about the service. | |
| 27 | 24 | |
| 28 | 25 | However, I wanted to install this service as a Docker container and |
| 29 | stumbled across the [Docker | |
| 30 | README](https://github.com/FreshRSS/FreshRSS/tree/edge/Docker) within | |
| 31 | the GitHub repository. | |
| 26 | stumbled across the | |
| 27 | [[https://github.com/FreshRSS/FreshRSS/tree/edge/Docker][Docker README]] | |
| 28 | within the GitHub repository. | |
| 32 | 29 | |
| 33 | 30 | This README was the documentation I actually needed. However, as you'll |
| 34 | see below, I still had to manually edit one file | |
| 35 | (`config.php`) to access the API externally via my RSS apps. | |
| 36 | ||
| 37 | ## Installation | |
| 38 | ||
| 39 | ### DNS | |
| 31 | see below, I still had to manually edit one file (=config.php=) to | |
| 32 | access the API externally via my RSS apps. | |
| 40 | 33 | |
| 34 | * Installation | |
| 35 | ** DNS | |
| 41 | 36 | The first step, as required by any external web service, was assigning a |
| 42 | domain name to use. I chose to use a subdomain, like | |
| 43 | `rss.example.com`. | |
| 37 | domain name to use. I chose to use a subdomain, like =rss.example.com=. | |
| 44 | 38 | |
| 45 | To assign this, I created an `A` record in my DNS settings | |
| 46 | with the IPv4 address of the server and an `AAAA` record with | |
| 47 | the IPv6 address of the server. Note: assigning an IPv6 | |
| 48 | (`AAAA`) record is optional, but I like to enable IPV6 for my | |
| 49 | services. | |
| 39 | To assign this, I created an =A= record in my DNS settings with the IPv4 | |
| 40 | address of the server and an =AAAA= record with the IPv6 address of the | |
| 41 | server. Note: assigning an IPv6 (=AAAA=) record is optional, but I like | |
| 42 | to enable IPV6 for my services. | |
| 50 | 43 | |
| 51 | ```config | |
| 44 | #+begin_src config | |
| 52 | 45 | rss.example.com A xxx.xxx.xxx.xxx |
| 53 | 46 | rss.example.com AAAA xxxx:xxxx: ... :xxxx |
| 54 | ``` | |
| 55 | ||
| 56 | ### Docker | |
| 47 | #+end_src | |
| 57 | 48 | |
| 58 | I initially tried to set up a `docker-compose.yml` file with | |
| 59 | a `.env` file because I prefer to have a file I can look back | |
| 60 | at later to see how I initially started the container, but it simply | |
| 61 | wouldn't work for me. I'm not sure why, but I assume I wasn't telling | |
| 62 | `docker-compose` where the `.env` file was. | |
| 49 | ** Docker | |
| 50 | I initially tried to set up a =docker-compose.yml= file with a =.env= | |
| 51 | file because I prefer to have a file I can look back at later to see how | |
| 52 | I initially started the container, but it simply wouldn't work for me. | |
| 53 | I'm not sure why, but I assume I wasn't telling =docker-compose= where | |
| 54 | the =.env= file was. | |
| 63 | 55 | |
| 64 | Regardless, I chose to simply run the service with | |
| 65 | `docker run`. See the following command for my | |
| 66 | `docker run` configuration: | |
| 56 | Regardless, I chose to simply run the service with =docker run=. See the | |
| 57 | following command for my =docker run= configuration: | |
| 67 | 58 | |
| 68 | ```sh | |
| 59 | #+begin_src sh | |
| 69 | 60 | sudo docker run -d --restart unless-stopped --log-opt max-size=10m \ |
| 70 | 61 | -p 8080:80 \ |
| 71 | 62 | -e TZ=America/Chicago \ |
| @@ -74,44 +65,40 @@ sudo docker run -d --restart unless-stopped --log-opt max-size=10m \ | ||
| 74 | 65 | -v freshrss_extensions:/var/www/FreshRSS/extensions \ |
| 75 | 66 | --name freshrss \ |
| 76 | 67 | freshrss/freshrss |
| 77 | ``` | |
| 68 | #+end_src | |
| 78 | 69 | |
| 79 | 70 | This started the container successfully and allowed me to visit the |
| 80 | FreshRSS instance at `localhost:8080`. | |
| 81 | ||
| 82 | ### Fresh RSS Set-Up | |
| 71 | FreshRSS instance at =localhost:8080=. | |
| 83 | 72 | |
| 84 | I **HIGHLY** suggest that you set up your user account prior to exposing | |
| 73 | ** Fresh RSS Set-Up | |
| 74 | I *HIGHLY** suggest that you set up your user account prior to exposing | |
| 85 | 75 | this service to the public. It's unlikely that someone is trying to |
| 86 | access the exact domain or IP/port you're assigning here, but as soon | |
| 87 | as you expose this service, the first person to open the URL will be | |
| 88 | able to create the admin user. | |
| 76 | access the exact domain or IP/port you're assigning here, but as soon as | |
| 77 | you expose this service, the first person to open the URL will be able | |
| 78 | to create the admin user. | |
| 89 | 79 | |
| 90 | In order to set up your FreshRSS service, open the | |
| 91 | `localhost:8080` URL in your browser (you may need to use a | |
| 92 | local IP instead of `localhost` if you're accessing the page | |
| 93 | from a different machine on the network - e.g., | |
| 94 | `192.168.1.20:8080`). | |
| 80 | In order to set up your FreshRSS service, open the =localhost:8080= URL | |
| 81 | in your browser (you may need to use a local IP instead of =localhost= | |
| 82 | if you're accessing the page from a different machine on the network - | |
| 83 | e.g., =192.168.1.20:8080=). | |
| 95 | 84 | |
| 96 | 85 | Once the page loads, set up your default user with a strong username and |
| 97 | 86 | password. You may also choose to configure other settings prior to |
| 98 | 87 | exposing this service. |
| 99 | 88 | |
| 100 | ### Nginx Reverse-Proxy | |
| 101 | ||
| 89 | ** Nginx Reverse-Proxy | |
| 102 | 90 | In order to access this service outside my home, I needed to set up a |
| 103 | reverse-proxy to connect `localhost:8080` to | |
| 104 | `rss.example.com`. | |
| 91 | reverse-proxy to connect =localhost:8080= to =rss.example.com=. | |
| 105 | 92 | |
| 106 | 93 | First, I created a new Nginx configuration file: |
| 107 | 94 | |
| 108 | ```sh | |
| 95 | #+begin_src sh | |
| 109 | 96 | sudo nano /etc/nginx/sites-available/rss.example.com |
| 110 | ``` | |
| 97 | #+end_src | |
| 111 | 98 | |
| 112 | 99 | Within the config file, I pasted the following code: |
| 113 | 100 | |
| 114 | ```config | |
| 101 | #+begin_src config | |
| 115 | 102 | upstream freshrss { |
| 116 | 103 | server 127.0.0.1:8080; |
| 117 | 104 | keepalive 64; |
| @@ -140,87 +127,79 @@ server { | ||
| 140 | 127 | proxy_pass_header Authorization; |
| 141 | 128 | } |
| 142 | 129 | } |
| 143 | ``` | |
| 130 | #+end_src | |
| 144 | 131 | |
| 145 | 132 | Finally, restart Nginx and you will be able to access your service via |
| 146 | 133 | HTTP: |
| 147 | 134 | |
| 148 | ```sh | |
| 135 | #+begin_src sh | |
| 149 | 136 | sudo systemctl restart nginx.service |
| 150 | ``` | |
| 151 | ||
| 152 | ### HTTPS | |
| 137 | #+end_src | |
| 153 | 138 | |
| 139 | ** HTTPS | |
| 154 | 140 | However, I don't want to access my RSS feeds via HTTP. I want it |
| 155 | 141 | available only via HTTPS. In order to do this, I ran the |
| 156 | [certbot](https://certbot.eff.org/) program to generate SSL certificates | |
| 157 | for me: | |
| 142 | [[https://certbot.eff.org/][certbot]] program to generate SSL | |
| 143 | certificates for me: | |
| 158 | 144 | |
| 159 | ```sh | |
| 145 | #+begin_src sh | |
| 160 | 146 | sudo certbot --nginx |
| 161 | ``` | |
| 147 | #+end_src | |
| 162 | 148 | |
| 163 | 149 | This process will automatically generate an SSL certificate for you and |
| 164 | 150 | modify the Nginx configuration file to include a redirect from HTTP to |
| 165 | 151 | HTTPS. |
| 166 | 152 | |
| 167 | ## Post-Installation Fixes | |
| 168 | ||
| 153 | * Post-Installation Fixes | |
| 169 | 154 | At this point, we have a functional FreshRSS website, available from |
| 170 | 155 | anywhere and secured with HTTPS. However, attempting to connect this |
| 171 | 156 | service to an RSS app resulted in many errors regarding unavailable URLs |
| 172 | 157 | and incorrect credentials. |
| 173 | 158 | |
| 174 | ### API Set-Up | |
| 175 | ||
| 176 | First, you need to open your user profile in FreshRSS | |
| 177 | (`Settings` > `Profile`) and set an API password | |
| 178 | in the field at the bottom. This is the password you will need to | |
| 179 | provide to your RSS apps. | |
| 159 | ** API Set-Up | |
| 160 | First, you need to open your user profile in FreshRSS (=Settings= > | |
| 161 | =Profile=) and set an API password in the field at the bottom. This is | |
| 162 | the password you will need to provide to your RSS apps. | |
| 180 | 163 | |
| 181 | 164 | Once that is set and saved, click the link below the API password field |
| 182 | 165 | to open the API check tool. It should look something like |
| 183 | `https://localhost:8080/api/` or | |
| 184 | `https://rss.example.com/api/`. | |
| 166 | =https://localhost:8080/api/= or =https://rss.example.com/api/=. | |
| 185 | 167 | |
| 186 | Within this page, you *should* see your correct external URL and | |
| 187 | "PASS" at the bottom of each API type. This would mean everything is | |
| 188 | set up correctly, and you can now move on and login to any RSS apps that | |
| 168 | Within this page, you /should/ see your correct external URL and "PASS" | |
| 169 | at the bottom of each API type. This would mean everything is set up | |
| 170 | correctly, and you can now move on and login to any RSS apps that | |
| 189 | 171 | support self-hosted options. |
| 190 | 172 | |
| 191 | 173 | In my case, the URL showed an internal URL and I had a warning that the |
| 192 | `base_url` variable may be misconfigured. If this is the | |
| 193 | case, see the next section for a fix. | |
| 194 | ||
| 195 | ### Base URL Fix | |
| 174 | =base_url= variable may be misconfigured. If this is the case, see the | |
| 175 | next section for a fix. | |
| 196 | 176 | |
| 197 | In order to fix the `base_url` for the API, I opened up my | |
| 198 | docker container with the following command: | |
| 177 | ** Base URL Fix | |
| 178 | In order to fix the =base_url= for the API, I opened up my docker | |
| 179 | container with the following command: | |
| 199 | 180 | |
| 200 | ```sh | |
| 181 | #+begin_src sh | |
| 201 | 182 | sudo docker exec -it freshrss bash |
| 202 | ``` | |
| 183 | #+end_src | |
| 203 | 184 | |
| 204 | 185 | Within this container, update the packages and install an editor: |
| 205 | 186 | |
| 206 | ```sh | |
| 187 | #+begin_src sh | |
| 207 | 188 | apt-get update |
| 208 | 189 | apt-get install nano |
| 209 | ``` | |
| 190 | #+end_src | |
| 210 | 191 | |
| 211 | Finally, open up `config.php` in the `data` | |
| 212 | directory: | |
| 192 | Finally, open up =config.php= in the =data= directory: | |
| 213 | 193 | |
| 214 | ```sh | |
| 194 | #+begin_src sh | |
| 215 | 195 | nano data/config.php |
| 216 | ``` | |
| 196 | #+end_src | |
| 217 | 197 | |
| 218 | Within `config.php`, you will need to update the | |
| 219 | `base_url` variable and update it to match your external URL. | |
| 220 | In my case, I simply commented-out the incorrect URL with | |
| 221 | `//` and added the correct one on a new line: | |
| 198 | Within =config.php=, you will need to update the =base_url= variable and | |
| 199 | update it to match your external URL. In my case, I simply commented-out | |
| 200 | the incorrect URL with =//= and added the correct one on a new line: | |
| 222 | 201 | |
| 223 | ```php | |
| 202 | #+begin_src php | |
| 224 | 203 | <?php |
| 225 | 204 | return array ( |
| 226 | 205 | ... |
| @@ -229,26 +208,25 @@ In my case, I simply commented-out the incorrect URL with | ||
| 229 | 208 | ... |
| 230 | 209 | ) |
| 231 | 210 | > |
| 232 | ``` | |
| 211 | #+end_src | |
| 233 | 212 | |
| 234 | You can now exit the file with `Ctrl + x`, press | |
| 235 | `y` to save the file, and then click `Enter` to | |
| 236 | keep the same file name. | |
| 213 | You can now exit the file with =Ctrl + x=, press =y= to save the file, | |
| 214 | and then click =Enter= to keep the same file name. | |
| 237 | 215 | |
| 238 | 216 | Finally, just exit out of the docker container: |
| 239 | 217 | |
| 240 | ```sh | |
| 218 | #+begin_src sh | |
| 241 | 219 | exit |
| 242 | ``` | |
| 220 | #+end_src | |
| 243 | 221 | |
| 244 | 222 | Next, just restart the container: |
| 245 | 223 | |
| 246 | ```sh | |
| 224 | #+begin_src sh | |
| 247 | 225 | sudo docker restart freshrss |
| 248 | ``` | |
| 226 | #+end_src | |
| 249 | 227 | |
| 250 | 228 | Voilà! Your API check should now "PASS" and you should be able to use |
| 251 | 229 | one of the API URLs in your RSS apps. |
| 252 | 230 | |
| 253 | In my case, I use [NetNewsWire](https://netnewswire.com) on my desktop | |
| 231 | In my case, I use [[https://netnewswire.com][NetNewsWire]] on my desktop | |
| 254 | 232 | and phone. |
content/blog/2023-09-15-gitweb.md → blog/self-hosting-gitweb/index.org renamed +23 −28
| @@ -1,15 +1,12 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-09-15 | |
| 3 | title = "GitWeb via Nginx" | |
| 4 | description = "A guide to self-hosting GitWeb using the Nginx web server." | |
| 5 | +++ | |
| 1 | #+title: Self-Hosting GitWeb via Nginx | |
| 2 | #+date: 2023-09-15 | |
| 3 | #+description: A guide to self-hosting GitWeb using the Nginx web server. | |
| 4 | #+filetags: :selfhosting: | |
| 6 | 5 | |
| 7 | ## Overview | |
| 8 | ||
| 9 | [GitWeb](https://git-scm.com/book/en/v2/Git-on-the-Server-GitWeb) is a | |
| 6 | * Overview | |
| 7 | [[https://git-scm.com/book/en/v2/Git-on-the-Server-GitWeb][GitWeb]] is a | |
| 10 | 8 | simple web-based visualizer for git repositories. By default, GitWeb |
| 11 | will only run with the `lighttpd` or `webrick` web | |
| 12 | servers. | |
| 9 | will only run with the =lighttpd= or =webrick= web servers. | |
| 13 | 10 | |
| 14 | 11 | However, this guide will show you how to keep GitWeb running in the |
| 15 | 12 | background and display information for all repositories in a chosen |
| @@ -17,25 +14,24 @@ directory. | ||
| 17 | 14 | |
| 18 | 15 | See below for the final result: |
| 19 | 16 | |
| 20 |  | |
| 21 | ||
| 22 | ## Install Dependencies | |
| 17 | #+caption: Gitweb | |
| 18 | [[https://img.cleberg.net/blog/20230915-gitweb/gitweb.png]] | |
| 23 | 19 | |
| 20 | * Install Dependencies | |
| 24 | 21 | To start, you'll need install the following packages: |
| 25 | 22 | |
| 26 | ```sh | |
| 23 | #+begin_src sh | |
| 27 | 24 | sudo apt install git gitweb fcgiwrap nginx |
| 28 | ``` | |
| 29 | ||
| 30 | ## Configure Nginx | |
| 25 | #+end_src | |
| 31 | 26 | |
| 27 | * Configure Nginx | |
| 32 | 28 | Once installed, create an Nginx configuration file. |
| 33 | 29 | |
| 34 | ```sh | |
| 30 | #+begin_src sh | |
| 35 | 31 | sudo nano /etc/nginx/sites-available/git.example.com |
| 36 | ``` | |
| 32 | #+end_src | |
| 37 | 33 | |
| 38 | ```conf | |
| 34 | #+begin_src conf | |
| 39 | 35 | server { |
| 40 | 36 | listen 80; |
| 41 | 37 | server_name example.com; |
| @@ -54,24 +50,23 @@ server { | ||
| 54 | 50 | index index.cgi; |
| 55 | 51 | } |
| 56 | 52 | } |
| 57 | ``` | |
| 53 | #+end_src | |
| 58 | 54 | |
| 59 | 55 | To make the configuration active, you need to symlink it and then |
| 60 | 56 | restart Nginx. |
| 61 | 57 | |
| 62 | ```sh | |
| 58 | #+begin_src sh | |
| 63 | 59 | sudo ln -s /etc/nginx/sites-available/git.example.com /etc/nginx/sites-enabled/git.example.com |
| 64 | 60 | sudo systemctl restart nginx.service |
| 65 | ``` | |
| 61 | #+end_src | |
| 66 | 62 | |
| 67 | 63 | The GitWeb application should now be available via the URL you set in |
| 68 | 64 | the Nginx configuration above. |
| 69 | 65 | |
| 70 | ## Customize GitWeb | |
| 71 | ||
| 66 | * Customize GitWeb | |
| 72 | 67 | If you need to, you can customize many things about Gitweb by editing |
| 73 | the [gitweb.conf](https://git-scm.com/docs/gitweb.conf) file. | |
| 68 | the [[https://git-scm.com/docs/gitweb.conf][gitweb.conf]] file. | |
| 74 | 69 | |
| 75 | ```sh | |
| 70 | #+begin_src sh | |
| 76 | 71 | sudo nano /etc/gitweb.conf |
| 77 | ``` | |
| 72 | #+end_src | |
content/blog/2022-11-07-matrix-synapse.md → blog/self-hosting-matrix/index.org renamed +69 −81
| @@ -1,106 +1,98 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-11-07 | |
| 3 | title = "Self-Hosting Matrix Synapse on Alpine Linux" | |
| 4 | description = "A guide to self-hosting the Matrix Synapse application on your own server." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Synpase | |
| 1 | #+title: Self-Hosting Matrix Synapse on Alpine Linux | |
| 2 | #+date: 2022-11-07 | |
| 3 | #+description: A guide to self-hosting the Matrix Synapse application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 8 | 5 | |
| 6 | * Synpase | |
| 9 | 7 | If you're reading this, you likely know that |
| 10 | [Synapse](https://github.com/matrix-org/synapse/) is a popular | |
| 11 | [Matrix](https://matrix.org/) home server software that allows users to | |
| 12 | run their own Matrix home server. | |
| 8 | [[https://github.com/matrix-org/synapse/][Synapse]] is a popular | |
| 9 | [[https://matrix.org/][Matrix]] home server software that allows users | |
| 10 | to run their own Matrix home server. | |
| 13 | 11 | |
| 14 | 12 | This post is a short guide describing how I was able to get Synapse |
| 15 | 13 | working in a minimally-usable state on Alpine Linux. |
| 16 | 14 | |
| 17 | ## Installation Process | |
| 18 | ||
| 19 | ### Dependencies | |
| 20 | ||
| 15 | * Installation Process | |
| 16 | ** Dependencies | |
| 21 | 17 | First, since there is no Alpine-specific package for Synapse, we need to |
| 22 | 18 | ensure that Alpine has the required dependencies for the Python-based |
| 23 | 19 | installation method. |
| 24 | 20 | |
| 25 | ```sh | |
| 21 | #+begin_src sh | |
| 26 | 22 | doas apk -U update |
| 27 | 23 | doas apk add python3 py3-virtualenv |
| 28 | ``` | |
| 24 | #+end_src | |
| 29 | 25 | |
| 30 | 26 | Next, we need to set up a Python virtual environment for Synapse: |
| 31 | 27 | |
| 32 | ```sh | |
| 28 | #+begin_src sh | |
| 33 | 29 | mkdir -p ~/synapse && cd ~/synapse |
| 34 | 30 | virtualenv -p python3 ~/synapse/env |
| 35 | 31 | source ~/synapse/env/bin/activate |
| 36 | 32 | pip install --upgrade pip |
| 37 | 33 | pip install --upgrade setuptools |
| 38 | 34 | pip install matrix-synapse |
| 39 | ``` | |
| 40 | ||
| 41 | ### Running Synapse | |
| 35 | #+end_src | |
| 42 | 36 | |
| 37 | ** Running Synapse | |
| 43 | 38 | Once installed, running Synapse is easy. Simply execute the following |
| 44 | command, replacing `example.com` with the domain name that | |
| 45 | will be used with this home server. This will generate the configuration | |
| 46 | files needed to run the server. | |
| 39 | command, replacing =example.com= with the domain name that will be used | |
| 40 | with this home server. This will generate the configuration files needed | |
| 41 | to run the server. | |
| 47 | 42 | |
| 48 | ```sh | |
| 43 | #+begin_src sh | |
| 49 | 44 | python -m synapse.app.homeserver \ |
| 50 | 45 | --server-name example.com \ |
| 51 | 46 | --config-path homeserver.yaml \ |
| 52 | 47 | --generate-config \ |
| 53 | 48 | --report-stats=no |
| 54 | ``` | |
| 49 | #+end_src | |
| 55 | 50 | |
| 56 | 51 | Once the configuration is generated, we can start up the Synapse server: |
| 57 | 52 | |
| 58 | ```sh | |
| 53 | #+begin_src sh | |
| 59 | 54 | synctl start |
| 60 | ``` | |
| 55 | #+end_src | |
| 61 | 56 | |
| 62 | ### Configuring Synapse | |
| 57 | ** Configuring Synapse | |
| 58 | To make any change to Synapse, we need to edit the =YAML= configuration | |
| 59 | file: | |
| 63 | 60 | |
| 64 | To make any change to Synapse, we need to edit the `YAML` | |
| 65 | configuration file: | |
| 66 | ||
| 67 | ```sh | |
| 61 | #+begin_src sh | |
| 68 | 62 | nano ~/synapse/homeserver.yaml |
| 69 | ``` | |
| 63 | #+end_src | |
| 70 | 64 | |
| 71 | For now, we just need to ensure the `server_name` is | |
| 72 | accurate. However, there are a lot of other configuration options found | |
| 73 | in the [Configuring | |
| 74 | Synapse](https://matrix-org.github.io/synapse/develop/usage/configuration/config_documentation.html) | |
| 75 | documentation that can be enabled/disabled at any point. | |
| 65 | For now, we just need to ensure the =server_name= is accurate. However, | |
| 66 | there are a lot of other configuration options found in the | |
| 67 | [[https://matrix-org.github.io/synapse/develop/usage/configuration/config_documentation.html][Configuring | |
| 68 | Synapse]] documentation that can be enabled/disabled at any point. | |
| 76 | 69 | |
| 77 | ```yaml | |
| 70 | #+begin_src yaml | |
| 78 | 71 | server_name: "example.com" |
| 79 | ``` | |
| 72 | #+end_src | |
| 80 | 73 | |
| 81 | 74 | Make sure to restart Synapse when you make changes to the configuration: |
| 82 | 75 | |
| 83 | ```sh | |
| 76 | #+begin_src sh | |
| 84 | 77 | synctl restart |
| 85 | ``` | |
| 86 | ||
| 87 | ### Nginx Reverse-Proxy | |
| 78 | #+end_src | |
| 88 | 79 | |
| 80 | ** Nginx Reverse-Proxy | |
| 89 | 81 | To ensure that Synapse is reachable from the public, we need to connect |
| 90 | 82 | our domain to the Synapse server. In my case, I use a Nginx |
| 91 | 83 | reverse-proxy for this purpose. |
| 92 | 84 | |
| 93 | 85 | To use Nginx, we need to create a reverse-proxy configuration file: |
| 94 | 86 | |
| 95 | ```sh | |
| 87 | #+begin_src sh | |
| 96 | 88 | doas nano /etc/nginx/http.d/example.com.conf |
| 97 | ``` | |
| 89 | #+end_src | |
| 98 | 90 | |
| 99 | If you already have TLS certificates for this domain | |
| 100 | (`example.com`), you can simply use the SSL configuration and | |
| 101 | point toward your TLS certificates. | |
| 91 | If you already have TLS certificates for this domain (=example.com=), | |
| 92 | you can simply use the SSL configuration and point toward your TLS | |
| 93 | certificates. | |
| 102 | 94 | |
| 103 | ```conf | |
| 95 | #+begin_src conf | |
| 104 | 96 | server { |
| 105 | 97 | listen 443 ssl http2; |
| 106 | 98 | listen [::]:443 ssl http2; |
| @@ -139,15 +131,15 @@ server { | ||
| 139 | 131 | listen 80; |
| 140 | 132 | return 404; |
| 141 | 133 | } |
| 142 | ``` | |
| 134 | #+end_src | |
| 143 | 135 | |
| 144 | 136 | If you need to generate TLS certificates (I recommend |
| 145 | [Certbot](https://certbot.eff.org/)), you'll need a more minimal Nginx | |
| 137 | [[https://certbot.eff.org/][Certbot]]), you'll need a more minimal Nginx | |
| 146 | 138 | conf file before you can use the TLS-enabled example above. Instead, use |
| 147 | 139 | this configuration file during the Certbot certificate generation |
| 148 | 140 | process: |
| 149 | 141 | |
| 150 | ```conf | |
| 142 | #+begin_src conf | |
| 151 | 143 | server { |
| 152 | 144 | server_name example.com; |
| 153 | 145 | location / { |
| @@ -155,64 +147,60 @@ server { | ||
| 155 | 147 | } |
| 156 | 148 | listen 80; |
| 157 | 149 | } |
| 158 | ``` | |
| 150 | #+end_src | |
| 159 | 151 | |
| 160 | 152 | Once you're done editing the Nginx conf file, restart Nginx: |
| 161 | 153 | |
| 162 | ```sh | |
| 154 | #+begin_src sh | |
| 163 | 155 | doas rc-service nginx restart |
| 164 | ``` | |
| 156 | #+end_src | |
| 165 | 157 | |
| 166 | If you still need to generate TLS certificates, run `certbot` | |
| 167 | now and obtain the certificates. Certbot will ask if you want to use a | |
| 168 | webroot or spin up a temporary web server. I **highly** recommend using | |
| 169 | the temporary web server due to the many issues with using a webroot. | |
| 158 | If you still need to generate TLS certificates, run =certbot= now and | |
| 159 | obtain the certificates. Certbot will ask if you want to use a webroot | |
| 160 | or spin up a temporary web server. I *highly** recommend using the | |
| 161 | temporary web server due to the many issues with using a webroot. | |
| 170 | 162 | |
| 171 | 163 | You will need to stop Nginx in order to user the temporary web server |
| 172 | 164 | option with Certbot: |
| 173 | 165 | |
| 174 | ```sh | |
| 166 | #+begin_src sh | |
| 175 | 167 | # Stop Nginx so certbot can spin up a temp webserver for cert generation |
| 176 | 168 | doas rc-service nginx stop |
| 177 | 169 | doas certbot certonly -v |
| 178 | 170 | doas rc-service nginx start |
| 179 | ``` | |
| 171 | #+end_src | |
| 180 | 172 | |
| 181 | ### Open Firewall & Router Ports | |
| 182 | ||
| 183 | If you use a firewall on the server, open the `8448` port for | |
| 184 | discovery and federation, as well as the normal web server ports if | |
| 185 | you're using a reverse proxy. If you want additional services, such as | |
| 186 | voice calls, you will need to read the Synapse documentation to see | |
| 187 | which ports need to be opened for those features. | |
| 173 | ** Open Firewall & Router Ports | |
| 174 | If you use a firewall on the server, open the =8448= port for discovery | |
| 175 | and federation, as well as the normal web server ports if you're using a | |
| 176 | reverse proxy. If you want additional services, such as voice calls, you | |
| 177 | will need to read the Synapse documentation to see which ports need to | |
| 178 | be opened for those features. | |
| 188 | 179 | |
| 189 | 180 | Here's an example of the Universal Firewall (UFW) software: |
| 190 | 181 | |
| 191 | ```sh | |
| 182 | #+begin_src sh | |
| 192 | 183 | # Matrix port |
| 193 | 184 | doas ufw allow 8448 |
| 194 | 185 | # Standard web server ports |
| 195 | 186 | doas ufw allow "Nginx Full" |
| 196 | ``` | |
| 197 | ||
| 198 | Remember to forward any Synapse ports, such as `8448`, | |
| 199 | `80`, and `443`, in your Router from the internet | |
| 200 | to your server's IP address. | |
| 187 | #+end_src | |
| 201 | 188 | |
| 202 | ### Adding Matrix Users | |
| 189 | Remember to forward any Synapse ports, such as =8448=, =80=, and =443=, | |
| 190 | in your Router from the internet to your server's IP address. | |
| 203 | 191 | |
| 192 | ** Adding Matrix Users | |
| 204 | 193 | Finally, if you didn't enable public registration in the |
| 205 | `homeserver.yaml` file, you can manually create users via the | |
| 194 | =homeserver.yaml= file, you can manually create users via the | |
| 206 | 195 | command-line: |
| 207 | 196 | |
| 208 | ```sh | |
| 197 | #+begin_src sh | |
| 209 | 198 | cd ~/synapse |
| 210 | 199 | register_new_matrix_user -c homeserver.yaml |
| 211 | ``` | |
| 200 | #+end_src | |
| 212 | 201 | |
| 213 | 202 | Remember that the format for federated Matrix usernames is |
| 214 | `@username:example.com` when logging in to client | |
| 215 | applications. | |
| 203 | =@username:example.com= when logging in to client applications. | |
| 216 | 204 | |
| 217 | 205 | Once Synapse is running, and you have a username, you are ready to log |
| 218 | 206 | in to a Matrix client and start sending messages, joining rooms, and |
blog/self-hosting-otter-wiki/index.org added +135
| @@ -0,0 +1,135 @@ | ||
| 1 | #+title: Self-Hosting An Otter Wiki | |
| 2 | #+date: <2024-02-21> | |
| 3 | #+description: Learn how to easily self-host An Otter Wiki. | |
| 4 | #+filetags: :selfhosting: | |
| 5 | ||
| 6 | * An Otter Wiki | |
| 7 | [[https://otterwiki.com/][An Otter Wiki]] is an easy to use wiki | |
| 8 | software that takes almost no effort to set up and maintain. | |
| 9 | ||
| 10 | * Installation | |
| 11 | To install An Otter Wiki, I'm going to use Docker Compose to create the | |
| 12 | container and then use Nginx as a reverse proxy to allow external access | |
| 13 | via a subdomain I own. | |
| 14 | ||
| 15 | ** Docker Compose | |
| 16 | Start by creating a directory for the container's files. | |
| 17 | ||
| 18 | #+begin_src sh | |
| 19 | mkdir ~/otterwiki | |
| 20 | #+end_src | |
| 21 | ||
| 22 | Next, create the =docker-compose.yml= file to define the container's | |
| 23 | parameters. | |
| 24 | ||
| 25 | #+begin_src sh | |
| 26 | nano ~/otterwiki/docker-compose.yml | |
| 27 | #+end_src | |
| 28 | ||
| 29 | Within the file, paste the following content. You can read the project's | |
| 30 | documentation if you want to further override or customize the | |
| 31 | container. | |
| 32 | ||
| 33 | #+begin_src conf | |
| 34 | version: '3' | |
| 35 | services: | |
| 36 | otterwiki: | |
| 37 | image: redimp/otterwiki:2 | |
| 38 | restart: unless-stopped | |
| 39 | # Internal port must be assigned to port 80 | |
| 40 | # External port can be customized | |
| 41 | ports: | |
| 42 | - 8337:80 | |
| 43 | volumes: | |
| 44 | - ./app-data:/app-data | |
| 45 | #+end_src | |
| 46 | ||
| 47 | Once the file is saved and closed, you can launch the container. | |
| 48 | ||
| 49 | #+begin_src sh | |
| 50 | cd ~/otterwiki | |
| 51 | sudo docker-compose up -d | |
| 52 | #+end_src | |
| 53 | ||
| 54 | The container is now available at =localhost:8337=. Next, we will use | |
| 55 | Nginx to serve this app externally. | |
| 56 | ||
| 57 | ** Nginx | |
| 58 | To access the app externally, let's set up a reverse proxy. I'll start | |
| 59 | by creating the Nginx configuration file for my wiki. | |
| 60 | ||
| 61 | #+begin_src sh | |
| 62 | sudo nano /etc/nginx/sites-available/wiki | |
| 63 | #+end_src | |
| 64 | ||
| 65 | Within the file, I have saved the following content. This assumes you | |
| 66 | already have a TLS/SSL cert to use with this subdomain. If not, simply | |
| 67 | remove the =ssl_*= variables, remove the =80= server block, and change | |
| 68 | the =443= server block to =80= to serve the app without SSL. | |
| 69 | ||
| 70 | #+begin_src conf | |
| 71 | server { | |
| 72 | if ($host ~ ^[^.]+\.example\.com$) { | |
| 73 | return 301 https://$host$request_uri; | |
| 74 | } | |
| 75 | ||
| 76 | listen [::]:80; | |
| 77 | listen 80; | |
| 78 | server_name wiki.example.com; | |
| 79 | return 404; | |
| 80 | } | |
| 81 | ||
| 82 | server { | |
| 83 | listen [::]:443 ssl http2; | |
| 84 | listen 443 ssl http2; | |
| 85 | server_name wiki.example.com; | |
| 86 | access_log /var/log/nginx/wiki.access.log; | |
| 87 | error_log /var/log/nginx/wiki.error.log; | |
| 88 | ||
| 89 | ssl_certificate /etc/letsencrypt/live/example.com/fullchain.pem; | |
| 90 | ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem; | |
| 91 | include /etc/letsencrypt/options-ssl-nginx.conf; | |
| 92 | ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; | |
| 93 | ||
| 94 | location / { | |
| 95 | set $upstream_wiki http://127.0.0.1:8337; | |
| 96 | proxy_pass $upstream_wiki; | |
| 97 | ||
| 98 | proxy_set_header Host $http_host; | |
| 99 | proxy_set_header X-Real-IP $remote_addr; | |
| 100 | proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for; | |
| 101 | proxy_set_header X-Forwarded-Host $http_host; | |
| 102 | } | |
| 103 | } | |
| 104 | #+end_src | |
| 105 | ||
| 106 | Save and close the configuration file. On Nginx, we need to symlink the | |
| 107 | file to enable it. | |
| 108 | ||
| 109 | #+begin_src sh | |
| 110 | sudo ln -s /etc/nginx/sites-available/wiki /etc/nginx/sites-enabled/wiki | |
| 111 | #+end_src | |
| 112 | ||
| 113 | Once enabled, restart the Nginx server to start serving the app | |
| 114 | externally. | |
| 115 | ||
| 116 | #+begin_src sh | |
| 117 | sudo systemctl restart nginx.service | |
| 118 | #+end_src | |
| 119 | ||
| 120 | * Screenshots | |
| 121 | In the screenshot below, you can see the initial launch screen for An | |
| 122 | Otter Wiki. Start by creating your admin account and configure the app | |
| 123 | as necessary. | |
| 124 | ||
| 125 | #+caption: An Otter Wiki - Initial Screen | |
| 126 | [[https://img.cleberg.net/blog/20240221-otterwiki/otterwiki.png]] | |
| 127 | ||
| 128 | You can also see the default editing screen for creating and editing | |
| 129 | pages. It's as easy as typing Markdown and hitting the save button. | |
| 130 | ||
| 131 | #+caption: An Otter Wiki - Editing Screen | |
| 132 | [[https://img.cleberg.net/blog/20240221-otterwiki/otterwiki-edit.png]] | |
| 133 | ||
| 134 | Overall, I like An Otter Wiki and will be looking forward to seeing how | |
| 135 | much use I get out of it going forward. | |
content/blog/2023-06-30-self-hosting-voyager-lemmy-client.md → blog/self-hosting-voyager/index.org renamed +41 −48
| @@ -1,55 +1,50 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-06-30 | |
| 3 | title = "Self-Hosting Voyager - A Lemmy Web Client" | |
| 4 | description = "A guide to self-hosting the Voyager application on your own server." | |
| 5 | +++ | |
| 1 | #+title: Self-Hosting Voyager - A Lemmy Web Client | |
| 2 | #+date: 2023-06-30 | |
| 3 | #+description: A guide to self-hosting the Voyager application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 6 | 5 | |
| 7 | ## Installation Guide | |
| 8 | ||
| 9 | [Voyager](https://github.com/aeharding/voyager) is a mobile-first Lemmy | |
| 10 | web client, based on iOS design standards. It follows very closely to | |
| 11 | Apollo's design. | |
| 6 | * Installation Guide | |
| 7 | [[https://github.com/aeharding/voyager][Voyager]] is a mobile-first | |
| 8 | Lemmy web client, based on iOS design standards. It follows very closely | |
| 9 | to Apollo's design. | |
| 12 | 10 | |
| 13 | 11 | This post is a guide showing how I was able to build and launch my own |
| 14 | 12 | instance of Voyager via Docker Compose. |
| 15 | 13 | |
| 16 | ### Clone the Repository | |
| 17 | ||
| 14 | ** Clone the Repository | |
| 18 | 15 | Start by cloning the repository and entering it: |
| 19 | 16 | |
| 20 | ```sh | |
| 17 | #+begin_src sh | |
| 21 | 18 | git clone https://github.com/aeharding/voyager |
| 22 | 19 | cd voyager |
| 23 | ``` | |
| 24 | ||
| 25 | ### Build the Image | |
| 20 | #+end_src | |
| 26 | 21 | |
| 22 | ** Build the Image | |
| 27 | 23 | With this repository, you can build the image yourself without any |
| 28 | 24 | further configuration. When complete, it'll give you the image ID for |
| 29 | 25 | you to run. |
| 30 | 26 | |
| 31 | ```sh | |
| 27 | #+begin_src sh | |
| 32 | 28 | sudo docker build . |
| 33 | 29 | # Successfully built 5f00723cb5be |
| 34 | ``` | |
| 30 | #+end_src | |
| 35 | 31 | |
| 36 | 32 | With the image ID above, you can run the container and pass the |
| 37 | requested port `5314` through or use a custom port, if you | |
| 38 | wish. | |
| 33 | requested port =5314= through or use a custom port, if you wish. | |
| 39 | 34 | |
| 40 | You can also set the `CUSTOM_LEMMY_SERVERS` environment | |
| 41 | variable if you want to add to the default suggested login servers. This | |
| 42 | must be set with a comma separated list of suggested servers. The first | |
| 43 | instance in the list will be the default view for logged-out users. | |
| 35 | You can also set the =CUSTOM_LEMMY_SERVERS= environment variable if you | |
| 36 | want to add to the default suggested login servers. This must be set | |
| 37 | with a comma separated list of suggested servers. The first instance in | |
| 38 | the list will be the default view for logged-out users. | |
| 44 | 39 | |
| 45 | I will be using a `docker-compose.yml` file to run this | |
| 46 | container, instead of a `docker run` command. | |
| 40 | I will be using a =docker-compose.yml= file to run this container, | |
| 41 | instead of a =docker run= command. | |
| 47 | 42 | |
| 48 | ```sh | |
| 43 | #+begin_src sh | |
| 49 | 44 | nano docker-compose.yml |
| 50 | ``` | |
| 45 | #+end_src | |
| 51 | 46 | |
| 52 | ```conf | |
| 47 | #+begin_src conf | |
| 53 | 48 | version: "2" |
| 54 | 49 | services: |
| 55 | 50 | voyager: |
| @@ -59,30 +54,29 @@ services: | ||
| 59 | 54 | - "<custom_port>:5314" |
| 60 | 55 | environment: |
| 61 | 56 | - CUSTOM_LEMMY_SERVERS=lemmy.dbzer0.com,lemmy.world,lemmy.ml,beehaw.org |
| 62 | ``` | |
| 57 | #+end_src | |
| 63 | 58 | |
| 64 | ```sh | |
| 59 | #+begin_src sh | |
| 65 | 60 | sudo docker-compose up -d |
| 66 | ``` | |
| 61 | #+end_src | |
| 67 | 62 | |
| 68 | 63 | The web app will now be available at the following address: |
| 69 | `<machine_ip>:<custom_port>`. If you are running it on your | |
| 70 | local device, try `localhost:<custom_port>`. | |
| 71 | ||
| 72 | ### Reverse Proxy | |
| 64 | =<machine_ip>:<custom_port>=. If you are running it on your local | |
| 65 | device, try =localhost:<custom_port>=. | |
| 73 | 66 | |
| 74 | If you want to visit this app via an external URL or domain name, | |
| 75 | you'll need to set up a reverse proxy. The example below uses Nginx as | |
| 76 | a reverse proxy. | |
| 67 | ** Reverse Proxy | |
| 68 | If you want to visit this app via an external URL or domain name, you'll | |
| 69 | need to set up a reverse proxy. The example below uses Nginx as a | |
| 70 | reverse proxy. | |
| 77 | 71 | |
| 78 | 72 | Simply create the configuration file, paste the contents below, save the |
| 79 | 73 | file, symlink the file, and restart Nginx. |
| 80 | 74 | |
| 81 | ```sh | |
| 75 | #+begin_src sh | |
| 82 | 76 | sudo nano /etc/nginx/sites-available/voyager |
| 83 | ``` | |
| 77 | #+end_src | |
| 84 | 78 | |
| 85 | ```conf | |
| 79 | #+begin_src conf | |
| 86 | 80 | server { |
| 87 | 81 | if ($host ~ ^[^.]+\.example\.com$) { |
| 88 | 82 | return 301 https://$host$request_uri; |
| @@ -112,15 +106,14 @@ server { | ||
| 112 | 106 | include /etc/letsencrypt/options-ssl-nginx.conf; |
| 113 | 107 | ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; |
| 114 | 108 | } |
| 115 | ``` | |
| 109 | #+end_src | |
| 116 | 110 | |
| 117 | ```sh | |
| 111 | #+begin_src sh | |
| 118 | 112 | sudo ln sudo ln -s /etc/nginx/sites-available/voyager /etc/nginx/sites-enabled/voyager |
| 119 | 113 | sudo systemctl restart nginx.service |
| 120 | ``` | |
| 114 | #+end_src | |
| 121 | 115 | |
| 122 | The site will now be available at the `server_name` you | |
| 123 | specified above! | |
| 116 | The site will now be available at the =server_name= you specified above! | |
| 124 | 117 | |
| 125 | 118 | You can visit my instance at |
| 126 | [voyager.cleberg.net](https://voyager.cleberg.net) for an example. | |
| 119 | [[https://voyager.cleberg.net][voyager.cleberg.net]] for an example. | |
content/blog/2023-01-28-self-hosting-wger-workout-manager.md → blog/self-hosting-wger/index.org renamed +59 −69
| @@ -1,106 +1,97 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-01-28 | |
| 3 | title = "Self-Hosting Wger Workout Manager" | |
| 4 | description = "A guide to self-hosting the Wger application on your own server." | |
| 5 | +++ | |
| 1 | #+title: Self-Hosting Wger Workout Manager | |
| 2 | #+date: 2023-01-28 | |
| 3 | #+description: A guide to self-hosting the Wger application on your own server. | |
| 4 | #+filetags: :selfhosting: | |
| 6 | 5 | |
| 7 | ## Wger: The Self-Hosted Workout Manager | |
| 8 | ||
| 9 | [Wger Workout Manager](https://wger.de) is a fitness tracking tool for | |
| 6 | * Wger: The Self-Hosted Workout Manager | |
| 7 | [[https://wger.de][Wger Workout Manager]] is a fitness tracking tool for | |
| 10 | 8 | those who enjoy self-hosting their data. You can also register an |
| 11 | 9 | account on their main website if you'd prefer to try without |
| 12 | 10 | self-hosting. |
| 13 | 11 | |
| 14 | ### Features | |
| 15 | ||
| 12 | ** Features | |
| 16 | 13 | I didn't see a full listing of features anywhere, so I compiled this |
| 17 | 14 | list of my own after installing wger: |
| 18 | 15 | |
| 19 | 1. Dashboard | |
| 16 | 1. Dashboard | |
| 20 | 17 | |
| 21 | - Dashboard view of Workout Schedule, Nutrition Plan, Weight | |
| 22 | Graph, & last 5 Weight Logs | |
| 18 | - Dashboard view of Workout Schedule, Nutrition Plan, Weight Graph, & | |
| 19 | last 5 Weight Logs | |
| 23 | 20 | |
| 24 | 2. Training | |
| 21 | 2. Training | |
| 25 | 22 | |
| 26 | - Workout Log | |
| 27 | - Workout Schedule | |
| 28 | - Calendar (shows weight logs and Bad/Neutral/Good days) | |
| 29 | - Gallery (shows images you upload) | |
| 30 | - Workout templates | |
| 31 | - Public templates | |
| 32 | - Exercises | |
| 23 | - Workout Log | |
| 24 | - Workout Schedule | |
| 25 | - Calendar (shows weight logs and Bad/Neutral/Good days) | |
| 26 | - Gallery (shows images you upload) | |
| 27 | - Workout templates | |
| 28 | - Public templates | |
| 29 | - Exercises | |
| 33 | 30 | |
| 34 | 3. Nutrition | |
| 31 | 3. Nutrition | |
| 35 | 32 | |
| 36 | - Nutrition plans | |
| 37 | - BMI calculator | |
| 38 | - Daily calories calculator | |
| 39 | - Ingredient overview | |
| 33 | - Nutrition plans | |
| 34 | - BMI calculator | |
| 35 | - Daily calories calculator | |
| 36 | - Ingredient overview | |
| 40 | 37 | |
| 41 | 4. Body Weight | |
| 38 | 4. Body Weight | |
| 42 | 39 | |
| 43 | - Weight overview | |
| 44 | ||
| 45 | ### Documentation | |
| 40 | - Weight overview | |
| 46 | 41 | |
| 42 | ** Documentation | |
| 47 | 43 | In order to self-host wger, I opted to use the Docker version of the |
| 48 | 44 | application. You can read the README within the |
| 49 | [wger-project/docker](https://github.com/wger-project/docker) project on | |
| 50 | GitHub for information and installation instructions. | |
| 51 | ||
| 52 | ### Installation | |
| 45 | [[https://github.com/wger-project/docker][wger-project/docker]] project | |
| 46 | on GitHub for information and installation instructions. | |
| 53 | 47 | |
| 48 | ** Installation | |
| 54 | 49 | To start the installation, I created a folder for wger and started |
| 55 | 50 | creating the three necessary files: |
| 56 | 51 | |
| 57 | ```sh | |
| 52 | #+begin_src sh | |
| 58 | 53 | mkdir ~/wger && mkdir ~/wger/config |
| 59 | 54 | touch ~/wger/docker-compose.yml && \ |
| 60 | 55 | touch ~/wger/config/prod.env && \ |
| 61 | 56 | touch ~/wger/config/nginx.conf |
| 62 | ``` | |
| 57 | #+end_src | |
| 63 | 58 | |
| 64 | 59 | Once you have the folders and files created, you will need to copy the |
| 65 | contents of the `docker-compose.yml`, `prod.env`, | |
| 66 | and `nginx.conf` from the GitHub link above. | |
| 60 | contents of the =docker-compose.yml=, =prod.env=, and =nginx.conf= from | |
| 61 | the GitHub link above. | |
| 67 | 62 | |
| 68 | 63 | A few notes to explain the changes I made to the default files: |
| 69 | 64 | |
| 70 | - I updated the `ALLOW_REGISTRAION` variable in | |
| 71 | `prod.env` to `False` after I created an | |
| 72 | account via my LAN connection, **before** I connected this app to a | |
| 73 | publicly-available domain. | |
| 74 | - I uncommented and updated `CSRF_TRUSTED_ORIGINS` to be | |
| 75 | equal to the public version of this app: | |
| 76 | `https://wger.example.com`. | |
| 77 | - I updated the port within `docker-compose.yml`, within | |
| 78 | the `nginx` block. The port I updated this to will be | |
| 79 | reflected in my nginx configuration file on the server (NOT the wger | |
| 80 | nginx.conf file). | |
| 81 | ||
| 82 | ### Deploy | |
| 65 | - I updated the =ALLOW_REGISTRAION= variable in =prod.env= to =False= | |
| 66 | after I created an account via my LAN connection, *before** I connected | |
| 67 | this app to a publicly-available domain. | |
| 68 | - I uncommented and updated =CSRF_TRUSTED_ORIGINS= to be equal to the | |
| 69 | public version of this app: =https://wger.example.com=. | |
| 70 | - I updated the port within =docker-compose.yml=, within the =nginx= | |
| 71 | block. The port I updated this to will be reflected in my nginx | |
| 72 | configuration file on the server (NOT the wger nginx.conf file). | |
| 83 | 73 | |
| 74 | ** Deploy | |
| 84 | 75 | Once all files are created and modified to your needs, simply start the |
| 85 | 76 | container. |
| 86 | 77 | |
| 87 | ```sh | |
| 78 | #+begin_src sh | |
| 88 | 79 | docker-compose up -d |
| 89 | ``` | |
| 80 | #+end_src | |
| 90 | 81 | |
| 91 | 82 | You can now visit the website on your LAN by going to |
| 92 | `localhost:YOUR_PORT` or by the server's IP, if you're not | |
| 93 | on the same machine that is running the container. | |
| 83 | =localhost:YOUR_PORT= or by the server's IP, if you're not on the same | |
| 84 | machine that is running the container. | |
| 94 | 85 | |
| 95 | 86 | If you wish to connect this app to a public domain name, you'll need to |
| 96 | point an `A` DNS record from the domain to your server's | |
| 97 | public IP. You'll then need to create a configuration file for | |
| 98 | whichever web server or reverse proxy you're using. | |
| 87 | point an =A= DNS record from the domain to your server's public IP. | |
| 88 | You'll then need to create a configuration file for whichever web server | |
| 89 | or reverse proxy you're using. | |
| 99 | 90 | |
| 100 | 91 | Wger's README suggests the following reverse proxy configuration for |
| 101 | 92 | Nginx: |
| 102 | 93 | |
| 103 | ```conf | |
| 94 | #+begin_src conf | |
| 104 | 95 | upstream wger { |
| 105 | 96 | # This port should match the port in the `nginx` block of docker-compose.yml |
| 106 | 97 | # If the container is running on this same machine, replace this with |
| @@ -127,16 +118,15 @@ server { | ||
| 127 | 118 | ssl_certificate /path/to/https/certificate.crt; |
| 128 | 119 | ssl_certificate_key /path/to/https/certificate.key; |
| 129 | 120 | } |
| 130 | ``` | |
| 131 | ||
| 132 | ## Thoughts on Wger | |
| 121 | #+end_src | |
| 133 | 122 | |
| 134 | I'm still playing around with the app itself, but it seems to be a | |
| 135 | solid all-around workout manager, weight log, and food log. | |
| 123 | * Thoughts on Wger | |
| 124 | I'm still playing around with the app itself, but it seems to be a solid | |
| 125 | all-around workout manager, weight log, and food log. | |
| 136 | 126 | |
| 137 | 127 | I like that the weight log graph is fluid and updates quickly. You can |
| 138 | also import or export data in CSV format if you'd like to move your | |
| 139 | data elsewhere. | |
| 128 | also import or export data in CSV format if you'd like to move your data | |
| 129 | elsewhere. | |
| 140 | 130 | |
| 141 | 131 | The workout manager is slightly odd, as it requires you to enter sets |
| 142 | 132 | and reps for each exercise when you enter it into the plan. Then, when |
| @@ -146,8 +136,8 @@ actually performed, in terms of reps and weight. | ||
| 146 | 136 | I haven't tried the food log yet and I likely will not, at least for a |
| 147 | 137 | while. I have no need for a food log or calorie tracker at the moment. |
| 148 | 138 | |
| 149 | ### Screenshot Example | |
| 150 | ||
| 139 | ** Screenshot Example | |
| 151 | 140 | You can see an example of a dashboard with placeholder data here: |
| 152 | 141 | |
| 153 |  | |
| 142 | #+caption: wger dashboard | |
| 143 | [[https://img.cleberg.net/blog/20230128-wger/wger.png]] | |
content/blog/2022-09-17-serenity-os.md → blog/serenity-os/index.org renamed +52 −53
| @@ -1,12 +1,10 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-09-17 | |
| 3 | title = "Serenity OS: Testing Out a Unique System" | |
| 4 | description = "A quick look at the Serenity operating system." | |
| 5 | +++ | |
| 1 | #+title: Serenity OS: Testing Out a Unique System | |
| 2 | #+date: 2022-09-17 | |
| 3 | #+description: A quick look at the Serenity operating system. | |
| 4 | #+filetags: :dev: | |
| 6 | 5 | |
| 7 | ## Overview | |
| 8 | ||
| 9 | [SerenityOS](https://serenityos.org) is a unique operating system (OS) | |
| 6 | * Overview | |
| 7 | [[https://serenityos.org][SerenityOS]] is a unique operating system (OS) | |
| 10 | 8 | that I have seen pop up in my news feed a few times over the last few |
| 11 | 9 | years, but I have never had time to test it out until now. |
| 12 | 10 | |
| @@ -16,42 +14,42 @@ to my youth. | ||
| 16 | 14 | |
| 17 | 15 | Per their website: |
| 18 | 16 | |
| 19 | > A graphical Unix-like operating system for desktop computers! | |
| 20 | > | |
| 21 | > SerenityOS is a love letter to '90s user interfaces with a custom | |
| 22 | > Unix-like core. It flatters with sincerity by stealing beautiful ideas | |
| 23 | > from various other systems. | |
| 24 | > | |
| 25 | > Roughly speaking, the goal is a marriage between the aesthetic of | |
| 26 | > late-1990s productivity software and the power-user accessibility of | |
| 27 | > late-2000s *nix. | |
| 28 | > | |
| 29 | > This is a system by us, for us, based on the things we like. | |
| 17 | #+begin_quote | |
| 18 | A graphical Unix-like operating system for desktop computers! | |
| 19 | ||
| 20 | SerenityOS is a love letter to '90s user interfaces with a custom | |
| 21 | Unix-like core. It flatters with sincerity by stealing beautiful ideas | |
| 22 | from various other systems. | |
| 23 | ||
| 24 | Roughly speaking, the goal is a marriage between the aesthetic of | |
| 25 | late-1990s productivity software and the power-user accessibility of | |
| 26 | late-2000s *nix. | |
| 30 | 27 | |
| 31 | ## Building | |
| 28 | This is a system by us, for us, based on the things we like. | |
| 32 | 29 | |
| 33 | Your first question may be "Where's the iso?" and the answer is... | |
| 34 | there are none. SerenityOS does not provide pre-built images for | |
| 35 | testing. You must build the images yourself. This seems intentionally to | |
| 36 | limit participation to only those who are truly interested enough to | |
| 37 | learn how to build the OS. | |
| 30 | #+end_quote | |
| 38 | 31 | |
| 39 | ### Clone | |
| 32 | * Building | |
| 33 | Your first question may be "Where's the iso?" and the answer is... there | |
| 34 | are none. SerenityOS does not provide pre-built images for testing. You | |
| 35 | must build the images yourself. This seems intentionally to limit | |
| 36 | participation to only those who are truly interested enough to learn how | |
| 37 | to build the OS. | |
| 40 | 38 | |
| 39 | ** Clone | |
| 41 | 40 | In order to get started, you'll need to clone the source repository: |
| 42 | 41 | |
| 43 | ```sh | |
| 42 | #+begin_src sh | |
| 44 | 43 | git clone https://github.com/SerenityOS/serenity && cd serenity |
| 45 | ``` | |
| 44 | #+end_src | |
| 46 | 45 | |
| 47 | ### Build | |
| 48 | ||
| 49 | Note that I followed the [Build | |
| 50 | Instructions](https://github.com/SerenityOS/serenity/blob/master/Documentation/BuildInstructions.md) | |
| 51 | in the SerenityOS repository as of commit | |
| 52 | `660d2b53b1206e868d5470eee80b5e62d7e30da7`. Things may have | |
| 53 | changed since my installation, and you should double-check the | |
| 54 | instructions first. | |
| 46 | ** Build | |
| 47 | Note that I followed the | |
| 48 | [[https://github.com/SerenityOS/serenity/blob/master/Documentation/BuildInstructions.md][Build | |
| 49 | Instructions]] in the SerenityOS repository as of commit | |
| 50 | =660d2b53b1206e868d5470eee80b5e62d7e30da7=. Things may have changed | |
| 51 | since my installation, and you should double-check the instructions | |
| 52 | first. | |
| 55 | 53 | |
| 56 | 54 | Regardless, I want to repeat my steps here to illustrate any errors or |
| 57 | 55 | differing commands I needed to run in order to build and run SerenityOS. |
| @@ -59,58 +57,59 @@ differing commands I needed to run in order to build and run SerenityOS. | ||
| 59 | 57 | Since I am running Fedora, I needed to install these packages in order |
| 60 | 58 | to build the OS images: |
| 61 | 59 | |
| 62 | ```sh | |
| 60 | #+begin_src sh | |
| 63 | 61 | sudo dnf install texinfo binutils-devel curl cmake mpfr-devel libmpc-devel gmp-devel e2fsprogs ninja-build patch ccache rsync @"C Development Tools and Libraries" @Virtualization |
| 64 | ``` | |
| 62 | #+end_src | |
| 65 | 63 | |
| 66 | Next, make sure you're inside the `serenity` directory | |
| 67 | created earlier during the git cloning process and process to build the | |
| 68 | toolchain: | |
| 64 | Next, make sure you're inside the =serenity= directory created earlier | |
| 65 | during the git cloning process and process to build the toolchain: | |
| 69 | 66 | |
| 70 | ```sh | |
| 67 | #+begin_src sh | |
| 71 | 68 | Meta/serenity.sh rebuild-toolchain |
| 72 | ``` | |
| 69 | #+end_src | |
| 73 | 70 | |
| 74 | 71 | Once the toolchain is built, you can Build and run the OS! |
| 75 | 72 | |
| 76 | ```sh | |
| 73 | #+begin_src sh | |
| 77 | 74 | Meta/serenity.sh run |
| 78 | ``` | |
| 75 | #+end_src | |
| 79 | 76 | |
| 80 | 77 | After this process is completed, the image should run automatically and |
| 81 | 78 | launch. |
| 82 | 79 | |
| 83 | ## Issues | |
| 84 | ||
| 80 | * Issues | |
| 85 | 81 | I played around in SerenityOS for an hour or two in order to see what I |
| 86 | 82 | could do and had a lot of fun with it. The only issue I ran into was a |
| 87 | 83 | lack of working internet. I didn't try very hard, but I could tell that |
| 88 | 84 | the main network link wasn't connecting to my Fedora host properly. |
| 89 | 85 | |
| 90 | ## Screenshots | |
| 91 | ||
| 86 | * Screenshots | |
| 92 | 87 | The initial launch of the image displays the SerenityOS desktop, with a |
| 93 | 88 | simple terminal already launched: |
| 94 | 89 | |
| 95 |  | |
| 90 | #+caption: SerenityOS Terminal | |
| 91 | [[https://img.cleberg.net/blog/20220917-serenityos/initial_launch.png]] | |
| 96 | 92 | |
| 97 | 93 | Here you can see the Fire application (literally just shows fire |
| 98 | 94 | burning), a browser with the local Serenity Browser page loaded, and a |
| 99 | 95 | text editor. |
| 100 | 96 | |
| 101 |  | |
| 97 | #+caption: SerenityOS Fire | |
| 98 | [[https://img.cleberg.net/blog/20220917-serenityos/basic_apps.png]] | |
| 102 | 99 | |
| 103 | 100 | I also poked around the system utilities and found most tools you'd |
| 104 | 101 | expect to find within a standard desktop. |
| 105 | 102 | |
| 106 |  | |
| 103 | #+caption: SerenityOS System Monitor | |
| 104 | [[https://img.cleberg.net/blog/20220917-serenityos/system_monitor.png]] | |
| 107 | 105 | |
| 108 | 106 | Lastly, I noted that the default desktop contains numerous pre-defined |
| 109 | 107 | themes to choose from. This is a small piece, but it's actually |
| 110 | 108 | wonderful to see desktop developers consider theming directly out of the |
| 111 | 109 | box rather than using an addon-based mentality. |
| 112 | 110 | |
| 113 |  | |
| 111 | #+caption: SerenityOS Themes | |
| 112 | [[https://img.cleberg.net/blog/20220917-serenityos/themes.png]] | |
| 114 | 113 | |
| 115 | 114 | I didn't take a screenshot of the other pre-installed games, but I did |
| 116 | 115 | spend nearly 30 minutes playing Solitaire before remembering that I was |
content/blog/2022-11-27-server-build.md → blog/server-build/index.org renamed +45 −51
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-11-27 | |
| 3 | title = "Building a Custom Rack-Mounted Server" | |
| 4 | description = "A retrospective on building my own rack-mounted server." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## The Dilemma | |
| 1 | #+title: Building a Custom Rack-Mounted Server | |
| 2 | #+date: 2022-11-27 | |
| 3 | #+description: A retrospective on building my own rack-mounted server. | |
| 4 | #+filetags: :hardware: | |
| 8 | 5 | |
| 6 | * The Dilemma | |
| 9 | 7 | For years, I have been using desktops and a Raspberry Pi as the backbone |
| 10 | 8 | of my homelab. I have always wanted to move toward a single dedicated |
| 11 | 9 | server that could handle all of my tasks, but was often put off by the |
| @@ -21,32 +19,31 @@ After returning the R720XD, I decided that I wanted to build my own | ||
| 21 | 19 | server with modern, consumer-grade PC components. This time, I am very |
| 22 | 20 | happy with the results of my server. |
| 23 | 21 | |
| 24 | ## Components | |
| 25 | ||
| 22 | * Components | |
| 26 | 23 | I'll start by listing all the components I used for this server build: |
| 27 | 24 | |
| 28 | - **Case**: [Rosewill RSV-R4100U 4U Server Chassis Rackmount | |
| 29 | Case](https://www.rosewill.com/rosewill-rsv-r4100u-black/p/9SIA072GJ92825) | |
| 30 | - **Motherboard**: [NZXT B550](https://nzxt.com/product/n7-b550) | |
| 31 | - **CPU**: AMD Ryzen 7 5700G with Radeon Graphics | |
| 32 | - **GPU**: N/A - I specifically chose one of the few AMD CPUs that | |
| 33 | support onboard graphics. | |
| 34 | - **RAM**: 64GB RAM (2x32GB) *Max of 128GB RAM on this motherboard* | |
| 35 | - **Boot Drive**: Western Digital 500GB M.2 NVME SSD | |
| 36 | - **HDD Bay**: | |
| 37 | - 10TB WD White *(shucked, moved from previous server)* | |
| 38 | - 8TB WD White *(shucked, moved from previous server)* | |
| 39 | - 2 x 8TB WD Red Plus *(Black Friday lined up perfectly with this | |
| 40 | build, so I grabbed two of these)* | |
| 41 | - **PSU**: Corsair RM850 PSU | |
| 42 | - **Extras**: | |
| 43 | - Corsair TM3Q Thermal Paste | |
| 44 | - Noctua 120mm fan *(replacement for front case fan)* | |
| 45 | - 2 x Noctua 80mm fans *(replacement for rear case fans)* | |
| 46 | - CableMatters 6Gbps SATA Cables | |
| 47 | ||
| 48 | ## Building the Server | |
| 49 | ||
| 25 | - *Case*: | |
| 26 | [[https://www.rosewill.com/rosewill-rsv-r4100u-black/p/9SIA072GJ92825][Rosewill | |
| 27 | RSV-R4100U 4U Server Chassis Rackmount Case]] | |
| 28 | - *Motherboard*: [[https://nzxt.com/product/n7-b550][NZXT B550]] | |
| 29 | - *CPU*: AMD Ryzen 7 5700G with Radeon Graphics | |
| 30 | - *GPU*: N/A - I specifically chose one of the few AMD CPUs that support | |
| 31 | onboard graphics. | |
| 32 | - *RAM*: 64GB RAM (2x32GB) /Max of 128GB RAM on this motherboard/ | |
| 33 | - *Boot Drive*: Western Digital 500GB M.2 NVME SSD | |
| 34 | - *HDD Bay*: | |
| 35 | - 10TB WD White /(shucked, moved from previous server)/ | |
| 36 | - 8TB WD White /(shucked, moved from previous server)/ | |
| 37 | - 2 x 8TB WD Red Plus /(Black Friday lined up perfectly with this | |
| 38 | build, so I grabbed two of these)/ | |
| 39 | - *PSU*: Corsair RM850 PSU | |
| 40 | - *Extras*: | |
| 41 | - Corsair TM3Q Thermal Paste | |
| 42 | - Noctua 120mm fan /(replacement for front case fan)/ | |
| 43 | - 2 x Noctua 80mm fans /(replacement for rear case fans)/ | |
| 44 | - CableMatters 6Gbps SATA Cables | |
| 45 | ||
| 46 | * Building the Server | |
| 50 | 47 | This took quite a while for me to build (in my opinion of time), |
| 51 | 48 | totaling around 3 hours from start to finish. The case has some peculiar |
| 52 | 49 | construction, so you have to completely remove the ODD & HDD cages to |
| @@ -55,8 +52,8 @@ install the motherboard and other components first. | ||
| 55 | 52 | Now, I've never built a computer of any kind before, so I was quite |
| 56 | 53 | nervous. Personally, the only challenging part was getting the CPU |
| 57 | 54 | cooler to screw into the motherboard without sliding the thermal paste |
| 58 | around too much underneath. I'm still not entirely sure if I did a | |
| 59 | great job of it, but nothing's broken yet. | |
| 55 | around too much underneath. I'm still not entirely sure if I did a great | |
| 56 | job of it, but nothing's broken yet. | |
| 60 | 57 | |
| 61 | 58 | The main components were all fine and simple. However, installing the |
| 62 | 59 | hard drives is slightly tedious as I need to power off the server and |
| @@ -68,15 +65,13 @@ used to in other machines. | ||
| 68 | 65 | Seeing that the cases with hot-swap bays were 3-4x the price, I'm okay |
| 69 | 66 | dealing with the tedium of removing the cage to install new drives. |
| 70 | 67 | |
| 71 | ## Software | |
| 72 | ||
| 68 | * Software | |
| 73 | 69 | I'm not going to dive into the software as I have done so in other |
| 74 | 70 | recent posts. However, I wanted to note that I am using Alpine Linux on |
| 75 | 71 | this server and hosting most services inside Docker. No virtual machines |
| 76 | 72 | (VMs) and very few bare-metal services. |
| 77 | 73 | |
| 78 | ## The Results | |
| 79 | ||
| 74 | * The Results | |
| 80 | 75 | How did my build turn out? Well, after migrating my other servers and |
| 81 | 76 | their services over, I found that my server is blazing fast. The |
| 82 | 77 | heaviest of my applications, Plex, is handled with ease. Even 4k |
| @@ -86,8 +81,7 @@ I am very happy with the results and will likely continue to improve on | ||
| 86 | 81 | this server as the years go by rather than buying another used server |
| 87 | 82 | online. |
| 88 | 83 | |
| 89 | ### Mistakes I Made | |
| 90 | ||
| 84 | ** Mistakes I Made | |
| 91 | 85 | This post wouldn't be complete unless I wrote about the mistakes I made |
| 92 | 86 | while building. The only real mistake I made beyond a "whoops I dropped |
| 93 | 87 | a screw" related to airflow and fan direction. |
| @@ -96,19 +90,19 @@ While installing the two new hard drives that showed up on 2022-11-30 | ||
| 96 | 90 | and getting ready to install the case in my rack, I noticed that the |
| 97 | 91 | hard drive temperatures were quite high. |
| 98 | 92 | |
| 99 | I used the `smartctl` command for each of my drives | |
| 100 | (`/dev/sda` through `/dev/sdd`): | |
| 93 | I used the =smartctl= command for each of my drives (=/dev/sda= through | |
| 94 | =/dev/sdd=): | |
| 101 | 95 | |
| 102 | ```sh | |
| 96 | #+begin_src sh | |
| 103 | 97 | doas smartctl -a /dev/sda | grep Temperature_Celsius |
| 104 | ``` | |
| 98 | #+end_src | |
| 105 | 99 | |
| 106 | The results were unusual - all four drives were idling at ~44-46 | |
| 107 | degrees Celsius. The only drive that was cooler was my 10TB drive, which | |
| 108 | was at 38 degrees Celsius. I noted that this 10TB drive was also closest | |
| 109 | to the case fan. | |
| 100 | The results were unusual - all four drives were idling at ~44-46 degrees | |
| 101 | Celsius. The only drive that was cooler was my 10TB drive, which was at | |
| 102 | 38 degrees Celsius. I noted that this 10TB drive was also closest to the | |
| 103 | case fan. | |
| 110 | 104 | |
| 111 | ```sh | |
| 105 | #+begin_src sh | |
| 112 | 106 | ID# ATTRIBUTE_NAME FLAG VALUE WORST THRESH TYPE UPDATED WHEN_FAILED RAW_VALUE |
| 113 | 107 | # /dev/sda |
| 114 | 108 | 194 Temperature_Celsius 0x0002 147 147 000 Old_age Always - 44 (Min/Max 22/46) |
| @@ -118,7 +112,7 @@ ID# ATTRIBUTE_NAME FLAG VALUE WORST THRESH TYPE UPDATED WHEN_ | ||
| 118 | 112 | 194 Temperature_Celsius 0x0002 144 144 000 Old_age Always - 45 (Min/Max 19/61) |
| 119 | 113 | # /dev/sdd |
| 120 | 114 | 194 Temperature_Celsius 0x0002 171 171 000 Old_age Always - 38 (Min/Max 14/56) |
| 121 | ``` | |
| 115 | #+end_src | |
| 122 | 116 | |
| 123 | 117 | After looking to see if I could fit more fans into the case, I noticed |
| 124 | 118 | that the 120mm fan used for intake from the front of the case was |
| @@ -130,7 +124,7 @@ dropped immediately! They are now idling at ~31-33 degrees Celsius. A | ||
| 130 | 124 | single fan spinning the wrong way caused my drives to idle 10-15 degrees |
| 131 | 125 | higher than they should have. |
| 132 | 126 | |
| 133 | ```sh | |
| 127 | #+begin_src sh | |
| 134 | 128 | ID# ATTRIBUTE_NAME FLAG VALUE WORST THRESH TYPE UPDATED WHEN_FAILED RAW_VALUE |
| 135 | 129 | # /dev/sda |
| 136 | 130 | 194 Temperature_Celsius 0x0002 209 209 000 Old_age Always - 31 (Min/Max 14/56) |
| @@ -140,7 +134,7 @@ ID# ATTRIBUTE_NAME FLAG VALUE WORST THRESH TYPE UPDATED WHEN_ | ||
| 140 | 134 | 194 Temperature_Celsius 0x0002 203 203 000 Old_age Always - 32 (Min/Max 21/48) |
| 141 | 135 | # /dev/sdd |
| 142 | 136 | 194 Temperature_Celsius 0x0002 196 196 000 Old_age Always - 33 (Min/Max 22/46) |
| 143 | ``` | |
| 137 | #+end_src | |
| 144 | 138 | |
| 145 | 139 | This was a silly error to make, but I'm glad I found it today before I |
| 146 | 140 | screwed the case into the rack and made things a lot more tedious to |
blog/server-hardening/index.org added +334
| @@ -0,0 +1,334 @@ | ||
| 1 | #+title: Hardening a Public-Facing Home Server | |
| 2 | #+date: 2022-03-24 | |
| 3 | #+description: Learn some basic techniques to harden a home server and network. | |
| 4 | #+filetags: :security: | |
| 5 | ||
| 6 | * Post Updates | |
| 7 | ||
| 8 | #+begin_quote | |
| 9 | After reviewing this post today (2022-10-04), I noticed quite a few gaps | |
| 10 | in my write-up and wanted to add a few things, even though this blog is | |
| 11 | really just a retrospective and knowledge dump for myself. I left things | |
| 12 | intact and simply crossed them out (+like this+) for posterity. | |
| 13 | #+end_quote | |
| 14 | ||
| 15 | * Planning Data Flows & Security | |
| 16 | ** My Personal Data Flow | |
| 17 | #+begin_src txt | |
| 18 | ┌───────┐ ┌─────────────────┐ | |
| 19 | ┌──► VLAN1 ├───► Private Devices │ | |
| 20 | │ └───────┘ └─────────────────┘ | |
| 21 | ┌──────────┐ ┌────────┐ ┌──────────┐ ┌────────┐ │ | |
| 22 | │ Internet ├───► Router ├───► Firewall ├───► Switch ├──┤ | |
| 23 | └──────────┘ └────────┘ └──────────┘ └────────┘ │ | |
| 24 | │ ┌───────┐ ┌───────────────┐ | |
| 25 | └──► VLAN2 ├───► Public Server │ | |
| 26 | └───────┘ └───────────────┘ | |
| 27 | #+end_src | |
| 28 | ||
| 29 | ** Thought Process | |
| 30 | To serve content from your home server and harden your security posture, | |
| 31 | you have to think about the transport of data from =server= to =client=. | |
| 32 | ||
| 33 | Let's start with the actual server itself. Think about the following: | |
| 34 | ||
| 35 | - Do I have a firewall enabled? Do I need to update this to allow new | |
| 36 | ports or IPs? | |
| 37 | - Do I have an IPS/IDS that may prevent outside traffic? | |
| 38 | - Do I have any other security software installed? | |
| 39 | - Are the services hosted inside Docker containers, behind a reverse | |
| 40 | proxy, or virtualized? If so, are they configured to allow outside | |
| 41 | traffic? | |
| 42 | ||
| 43 | Once the data leaves the server, where does it go? In my case, it goes | |
| 44 | to a managed switch. In this case, I asked the following: | |
| 45 | ||
| 46 | - What configurations is the switch using? | |
| 47 | - Am I using VLANs? | |
| 48 | - Yes, I am using 802.1Q VLANs. | |
| 49 | - Are the VLANs configured properly? | |
| 50 | - Yes, as shown in the Switch section below, I have a | |
| 51 | separate VLAN to allow outside traffic to and from the server alone. | |
| 52 | No other devices, except for a service port, and in that VLAN. | |
| 53 | ||
| 54 | At this point, the data has been processed through the switch. Where | |
| 55 | does it go next? In my case, it's pretty simple: it goes to the | |
| 56 | router/modem device. | |
| 57 | ||
| 58 | - Does my ISP block any ports that I need? | |
| 59 | - This is an important step that a lot of people run into when | |
| 60 | self-hosting at home. Use an online port-checker tool for your IP or | |
| 61 | call your ISP if you think ports are blocked. | |
| 62 | - Is there a router firewall? | |
| 63 | - Yes, I checked that it's configured to allow the ports I need to run | |
| 64 | my services publicly. Common web servers and reverse proxies require | |
| 65 | ports 80 and 443, but other services like media servers or games can | |
| 66 | require unique ports, so be sure to check the documentation for your | |
| 67 | service(s). | |
| 68 | - Are there any other settings affecting inbound/outbound traffic? | |
| 69 | - Schedules or access blocks | |
| 70 | - Static Routing | |
| 71 | - QoS | |
| 72 | - Port Forwarding | |
| 73 | - DMZ Hosting | |
| 74 | - Remote Management (this can sometimes mess with services that also | |
| 75 | require the use of ports 80 and 443) | |
| 76 | ||
| 77 | Once the data leaves my router, it goes to the upstream ISP and can be | |
| 78 | accessed publicly. | |
| 79 | ||
| 80 | *** Server | |
| 81 | +The services I run on my server are installed straight into the OS, | |
| 82 | without any use of Docker or VMs, so I don't need any extra application | |
| 83 | configuration to make them accessible to the outside world.+ | |
| 84 | ||
| 85 | As of 2022-10-04, the paragraph above is no longer true as I now run a | |
| 86 | reverse proxy with Nginx and host many services inside Docker. However, | |
| 87 | it doesn't change anything regarding this post as I still just need to | |
| 88 | open ports 80 & 443 and create the necessary website configuration | |
| 89 | files. | |
| 90 | ||
| 91 | When creating new services - either installed directly on bare metal or | |
| 92 | within something like Docker - I ensure that I read through the | |
| 93 | documentation thoroughly to understand a few key things: - What network | |
| 94 | activities should this app perform (if any)? Using which ports and | |
| 95 | protocols? - Does this app require any commands/services to be run as | |
| 96 | =root=? - Does this app log errors, authentication failures/successes, | |
| 97 | or anything else that would be useful for an investigation? | |
| 98 | ||
| 99 | For extra security, I use limit all incoming connections to SSH | |
| 100 | connections through my server firewall (=ufw=) and disable common SSH | |
| 101 | settings. After all of that, I use =fail2ban= as a preventative measure | |
| 102 | against brute-force login attempts. | |
| 103 | ||
| 104 | As another piece of security, you can randomize your SSH port to ensure | |
| 105 | that random scanners or attackers can't easily try to force their way | |
| 106 | into your network. For example, you can edit the port rules in your | |
| 107 | server to block all connection requests to port =22= but forward all | |
| 108 | remote connections from port =12345= to your server's port =22=. Then | |
| 109 | you just need to SSH to your network via your randomized port. | |
| 110 | ||
| 111 | ** =ufw= | |
| 112 | To see how to configure =ufw=, see my other post: | |
| 113 | [[../secure-your-network-with-the-uncomplicated-firewall/][Secure | |
| 114 | Your Network with the Uncomplicated Firewall]]. | |
| 115 | ||
| 116 | The general notion with an on-device firewall is that you want to deny | |
| 117 | all incoming connections by default and then selectively open certain | |
| 118 | ports for services or users that you know need access. | |
| 119 | ||
| 120 | If you know that you will only be logging into this server from a | |
| 121 | certain set or list of IPs, you can always set the firewall to only | |
| 122 | allow connections to port 22 from those IPs. | |
| 123 | ||
| 124 | For a quick start to only allow SSH connections to the server, use this: | |
| 125 | ||
| 126 | #+begin_src sh | |
| 127 | sudo ufw default deny incoming | |
| 128 | sudo ufw default allow outgoing | |
| 129 | sudo ufw allow 22 | |
| 130 | sudo ufw enable | |
| 131 | #+end_src | |
| 132 | ||
| 133 | #+caption: ufw | |
| 134 | [[https://img.cleberg.net/blog/20220324-hardening-a-public-facing-home-server/ufw.png]] | |
| 135 | ||
| 136 | ** =ssh= | |
| 137 | 1. Using SSH Keys | |
| 138 | ||
| 139 | First, make sure you have an SSH keypair generated on the device(s) | |
| 140 | that you'll be using to log in to the server. If you don't have an | |
| 141 | SSH key, run this command: | |
| 142 | ||
| 143 | #+begin_src sh | |
| 144 | ssh-keygen | |
| 145 | #+end_src | |
| 146 | ||
| 147 | Now that we have an SSH key, copy it to the server with the following | |
| 148 | command, which will ask for the user's password before accepting the | |
| 149 | key: | |
| 150 | ||
| 151 | #+begin_src sh | |
| 152 | ssh-copy-id my_user@my_server | |
| 153 | #+end_src | |
| 154 | ||
| 155 | If you have multiple keys, you'll need to specify which to use. After | |
| 156 | it's complete, =ssh= back into the server as that user and make sure | |
| 157 | it doesn't ask for a password. | |
| 158 | ||
| 159 | 2. Disable Password & Root Authentication | |
| 160 | ||
| 161 | Now that we can access the server without a password, we will disable | |
| 162 | password authentication and disable anyone from using =ssh= to login | |
| 163 | as =root=. | |
| 164 | ||
| 165 | To do this, open the =sshd_config= file: | |
| 166 | ||
| 167 | #+begin_src sh | |
| 168 | sudo nano /etc/ssh/sshd_config | |
| 169 | #+end_src | |
| 170 | ||
| 171 | You'll need to update the parameters to the values below. If one of | |
| 172 | these rules is commented-out or doesn't exist, create the rule at the | |
| 173 | bottom of the file. | |
| 174 | ||
| 175 | #+begin_src config | |
| 176 | PermitRootLogin no | |
| 177 | PasswordAuthentication no | |
| 178 | PubkeyAuthentication yes | |
| 179 | #+end_src | |
| 180 | ||
| 181 | Finally, restart the =ssh= service: | |
| 182 | ||
| 183 | #+begin_src sh | |
| 184 | sudo systemctl restart sshd.service | |
| 185 | #+end_src | |
| 186 | ||
| 187 | To test that everything's working so far, open ANOTHER terminal and | |
| 188 | try logging in as =root= over SSH. It is very important that you keep | |
| 189 | your current SSH session open and test with an additional session, or | |
| 190 | you will lock yourself out at some point and will need to use a | |
| 191 | recovery method (e.g., hooking monitor up to home server) to get | |
| 192 | yourself back in. | |
| 193 | ||
| 194 | 3. Enable MFA for =ssh= | |
| 195 | ||
| 196 | This part is optional, but I highly recommend it. So far, we've | |
| 197 | ensured that no one can log into our user on the server without using | |
| 198 | our secret key, and we've ensured that no one can log in remotely as | |
| 199 | =root=. Next, you can enable MFA authentication for =ssh= | |
| 200 | connections. | |
| 201 | ||
| 202 | This process involves editing a couple files and installing an MFA | |
| 203 | package, so I will not include all the details in this post. To see | |
| 204 | how to configure MFA for =ssh=, see my other post: | |
| 205 | [[../enable-totp-mfa-for-ssh/][Enabling MFA for SSH]]. | |
| 206 | ||
| 207 | #+caption: SSH MFA | |
| 208 | [[https://img.cleberg.net/blog/20220324-hardening-a-public-facing-home-server/ssh_mfa.png]] | |
| 209 | ||
| 210 | ** =fail2ban= | |
| 211 | I haven't written a post on how I use =fail2ban=, but it's quite simple. | |
| 212 | I use the default =sshd= jail, but you can always create new jails for | |
| 213 | respective applications or ports. For example, if you use Nginx as your | |
| 214 | web server, you can use the =nginx-http-auth= jail. | |
| 215 | ||
| 216 | In order to get it up and running, use the following commands: | |
| 217 | ||
| 218 | #+begin_src sh | |
| 219 | sudo apt install fail2ban | |
| 220 | sudo fail2ban-client start sshd | |
| 221 | sudo fail2ban-client status sshd | |
| 222 | #+end_src | |
| 223 | ||
| 224 | This should be used as a last-resort defense and shouldn't be a | |
| 225 | replacement for the security measures mentioned above. | |
| 226 | ||
| 227 | #+caption: fail2ban | |
| 228 | [[https://img.cleberg.net/blog/20220324-hardening-a-public-facing-home-server/fail2ban.png]] | |
| 229 | ||
| 230 | * Switch | |
| 231 | Between the router and any local devices is my managed switch, which is | |
| 232 | used to create VLANs. The example below shows how I would isolate the | |
| 233 | VLANs if I were starting to host a single service at home. | |
| 234 | ||
| 235 | ** 802.1Q VLAN Configuration | |
| 236 | In this configuration, port 8 is the public server that needs to be | |
| 237 | accessed from the outside. Port 23 is my 'dedicated service port' for | |
| 238 | this server. In order to SSH to this server, I need to plug my laptop | |
| 239 | into port 23 or else I cannot SSH. Otherwise, I'd need to hook up a | |
| 240 | monitor and keyboard directly to the server to manage it. | |
| 241 | ||
| 242 | | VLAN ID | VLAN Name | Member Ports | Tagged Ports | Untagged Ports | | |
| 243 | |---------+-----------+--------------+--------------+----------------| | |
| 244 | | 1 | Default | 1-24 | | 1-24 | | |
| 245 | | 2 | Server | 1,8,23 | | 1,8,23 | | |
| 246 | ||
| 247 | ** 802.1Q VLAN PVID Setting | |
| 248 | Once the VLAN is created, I simply add the =VLAN ID= of =2= as the | |
| 249 | =PVID= for any related ports (in this case, see that ports =8= and =23= | |
| 250 | have a PVID of =2=). | |
| 251 | ||
| 252 | | Port | PVID | | |
| 253 | |------+------| | |
| 254 | | 1 | 1 | | |
| 255 | | 2 | 1 | | |
| 256 | | 3 | 1 | | |
| 257 | | 4 | 1 | | |
| 258 | | 5 | 1 | | |
| 259 | | 6 | 1 | | |
| 260 | | 7 | 1 | | |
| 261 | | 8 | 2 | | |
| 262 | | 9 | 1 | | |
| 263 | | 10 | 1 | | |
| 264 | | 11 | 1 | | |
| 265 | | 12 | 1 | | |
| 266 | | 13 | 1 | | |
| 267 | | 14 | 1 | | |
| 268 | | 15 | 1 | | |
| 269 | | 16 | 1 | | |
| 270 | | 17 | 1 | | |
| 271 | | 18 | 1 | | |
| 272 | | 19 | 1 | | |
| 273 | | 20 | 1 | | |
| 274 | | 21 | 1 | | |
| 275 | | 22 | 1 | | |
| 276 | | 23 | 2 | | |
| 277 | | 24 | 1 | | |
| 278 | ||
| 279 | * Router | |
| 280 | On my router, the configuration was as easy as opening the firewall | |
| 281 | settings and unblocking the ports I needed for my services (e.g., | |
| 282 | HTTP/S, Plex, SSH, MySQL, etc.). | |
| 283 | ||
| 284 | +Since I'm relying on an ISP-provided modem/router combo for now (not by | |
| 285 | choice), I do not use any other advanced settings on my router that | |
| 286 | would inhibit any valid traffic to these services.+ | |
| 287 | ||
| 288 | The paragraph above regarding the ISP-owned router is no longer accurate | |
| 289 | as I now use the Ubiquiti Unifi Dream Machine Pro as my router. Within | |
| 290 | this router, I enabled port forwarding/firewall rules, segregate the | |
| 291 | network based on the device, and enable traffic restrictions (e.g., | |
| 292 | silently drop traffic from certain countries and threat categories). | |
| 293 | ||
| 294 | If you have the option with your ISP, I recommend using a personal | |
| 295 | router with software that you are familiar with so that you can explore | |
| 296 | all the options available to you. | |
| 297 | ||
| 298 | * Physical Security | |
| 299 | One large piece of self-hosting that people generally don't discuss | |
| 300 | online is physical security. However, physical security is very | |
| 301 | important for everyone who hosts a server like this. Exactly /how/ | |
| 302 | important it is depends on the server use/purpose. | |
| 303 | ||
| 304 | If you self-host customer applications that hold protected data (HIPAA, | |
| 305 | GDPR, COPPA, etc.), then physical security is extremely important and | |
| 306 | cannot be ignored. If you simply host a blog and some hobby sites, then | |
| 307 | it's a relatively minor consideration, but one you still need to think | |
| 308 | about. | |
| 309 | ||
| 310 | ** Location | |
| 311 | The first consideration is quite simple: location. - Is the server | |
| 312 | within a property you own or housed on someone else's property? - Is it | |
| 313 | nearby (in your house, in your work office, in your neighbor's garage, | |
| 314 | in a storage unit, etc.)? - Do you have 24/7 access to the server? - Are | |
| 315 | there climate considerations, such as humidity, fires, tornadoes, | |
| 316 | monsoons? - Do you have emergency equipment nearby in case of emergency? | |
| 317 | ||
| 318 | ** Hardware Ownership | |
| 319 | Secondly, consider the hardware itself: - Do you own the server in its | |
| 320 | entirety? - Are any other users able to access the server, even if your | |
| 321 | data/space is segregated? - If you're utilizing a third party, do they | |
| 322 | have any documentation to show responsibility? This could be a SOC 1/2/3 | |
| 323 | report, ISO compliance report, internal security/safety documentation. | |
| 324 | ||
| 325 | ** Physical Controls | |
| 326 | Regardless of who owns the hardware, ensure that there are adequate | |
| 327 | safeguards in place, if necessary. These usually don't apply to small | |
| 328 | home servers and are usually covered already if you're utilizing a third | |
| 329 | party. | |
| 330 | ||
| 331 | These can include: - Server bezel locks - Server room locks - physical, | |
| 332 | digital, or biometric authentication - Security cameras - Raised | |
| 333 | floors/lowered ceilings with proper guards/gates in-place within the | |
| 334 | floors or ceilings - Security personnel - Log sheets and/or guest badges | |
content/blog/2020-03-25-session-messenger.md → blog/session-manager/index.org renamed +62 −70
| @@ -1,32 +1,31 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-03-25 | |
| 3 | title = "Session Private Messenger" | |
| 4 | description = "Exploring the Session Private Messenger application." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Privacy Warning | |
| 1 | #+title: Session Private Messenger | |
| 2 | #+date: 2020-03-25 | |
| 3 | #+description: Exploring the Session Private Messenger application. | |
| 4 | #+filetags: :privacy: | |
| 8 | 5 | |
| 6 | * Privacy Warning | |
| 9 | 7 | The company behind Session (Loki Foundation) is from Australia. If you |
| 10 | 8 | didn't know, Australia has introduced |
| 11 | [legislation](https://parlinfo.aph.gov.au/parlInfo/download/legislation/bills/r6195_aspassed/toc_pdf/18204b01.pdf) | |
| 9 | [[https://parlinfo.aph.gov.au/parlInfo/download/legislation/bills/r6195_aspassed/toc_pdf/18204b01.pdf][legislation]] | |
| 12 | 10 | mandating companies comply with government requests to build backdoor |
| 13 | access into applications. For more information, read my article on [AES | |
| 14 | Encryption](./2020-01-25-aes-encryption.html). | |
| 15 | ||
| 16 | # About Session | |
| 17 | ||
| 18 | [Session](https://getsession.org) is a private, cross-platform messaging | |
| 19 | app from the [Loki Foundation](https://loki.foundation). As someone who | |
| 20 | has spent years looking for quality alternatives to major messaging | |
| 21 | apps, I was excited when I first heard about Session. Reading through | |
| 22 | [Session's white paper](https://arxiv.org/pdf/2002.04609.pdf), you can | |
| 23 | learn the technologies behind the Session app. Part of the security of | |
| 24 | Session comes from the Signal protocol, which was forked as the origin | |
| 25 | of Session. | |
| 26 | ||
| 27 | > Session is an end-to-end encrypted messenger that removes sensitive | |
| 28 | > metadata collection, and is designed for people who want privacy and | |
| 29 | > freedom from any forms of surveillance. | |
| 11 | access into applications. For more information, read my article on | |
| 12 | [[./2020-01-25-aes-encryption.html][AES Encryption]]. | |
| 13 | ||
| 14 | * About Session | |
| 15 | [[https://getsession.org][Session]] is a private, cross-platform | |
| 16 | messaging app from the [[https://loki.foundation][Loki Foundation]]. As | |
| 17 | someone who has spent years looking for quality alternatives to major | |
| 18 | messaging apps, I was excited when I first heard about Session. Reading | |
| 19 | through [[https://arxiv.org/pdf/2002.04609.pdf][Session's white paper]], | |
| 20 | you can learn the technologies behind the Session app. Part of the | |
| 21 | security of Session comes from the Signal protocol, which was forked as | |
| 22 | the origin of Session. | |
| 23 | ||
| 24 | #+begin_quote | |
| 25 | Session is an end-to-end encrypted messenger that removes sensitive | |
| 26 | metadata collection, and is designed for people who want privacy and | |
| 27 | freedom from any forms of surveillance. | |
| 28 | #+end_quote | |
| 30 | 29 | |
| 31 | 30 | In general, this app promises security through end-to-end encryption, |
| 32 | 31 | decentralized onion routing, and private identities. The biggest change |
| @@ -39,90 +38,83 @@ ID. | ||
| 39 | 38 | Since Session's website and white paper describe the details of |
| 40 | 39 | Session's security, I'm going to focus on using the app in this post. |
| 41 | 40 | |
| 42 | # Features | |
| 43 | ||
| 41 | * Features | |
| 44 | 42 | Since most people are looking for an alternative to a popular chat app, |
| 45 | 43 | I am going to list out the features that Session has so that you are |
| 46 | 44 | able to determine if the app would suit your needs: |
| 47 | 45 | |
| 48 | - Multiple device linking (via QR code or ID) | |
| 49 | - App locking via device screen lock, password, or fingerprint | |
| 50 | - Screenshot blocking | |
| 51 | - Incognito keyboard | |
| 52 | - Read receipts and typing indicators | |
| 53 | - Mobile notification customization | |
| 54 | - Old message deletion and conversation limit | |
| 55 | - Backups | |
| 56 | - Recovery phrase | |
| 57 | - Account deletion, including ID, messages, sessions, and contacts | |
| 58 | ||
| 59 | # Downloads | |
| 60 | ||
| 46 | - Multiple device linking (via QR code or ID) | |
| 47 | - App locking via device screen lock, password, or fingerprint | |
| 48 | - Screenshot blocking | |
| 49 | - Incognito keyboard | |
| 50 | - Read receipts and typing indicators | |
| 51 | - Mobile notification customization | |
| 52 | - Old message deletion and conversation limit | |
| 53 | - Backups | |
| 54 | - Recovery phrase | |
| 55 | - Account deletion, including ID, messages, sessions, and contacts | |
| 56 | ||
| 57 | * Downloads | |
| 61 | 58 | I have tested this app on Ubuntu 19.10, Android 10, macOS Monterey, and |
| 62 | 59 | iOS 15. All apps have worked well without many issues. |
| 63 | 60 | |
| 64 | 61 | Below is a brief overview of the Session app on Linux. To get this app, |
| 65 | you'll need to go to the [Downloads](https://getsession.org/download/) | |
| 62 | you'll need to go to the [[https://getsession.org/download/][Downloads]] | |
| 66 | 63 | page and click to link to the operating system you're using. |
| 67 | 64 | |
| 68 | 65 | For Linux, it will download an AppImage that you'll need to enable with |
| 69 | 66 | the following command: |
| 70 | 67 | |
| 71 | ```sh | |
| 68 | #+begin_src sh | |
| 72 | 69 | sudo chmod u+x session-messenger-desktop-linux-x86_64-1.0.5.AppImage |
| 73 | ``` | |
| 74 | ||
| 75 |  | |
| 70 | #+end_src | |
| 77 | 71 | |
| 78 | # Creating an Account | |
| 72 | #+caption: Session Download Options | |
| 73 | [[https://img.cleberg.net/blog/20200325-session-private-messenger/session_downloads.png]] | |
| 79 | 74 | |
| 80 | Once you've installed the app, simply run the app and create your | |
| 81 | unique Session ID. It will look something like this: | |
| 82 | `05af1835afdd63c947b47705867501d6373f486aa1ae05b1f2f3fcd24570eba608`. | |
| 75 | * Creating an Account | |
| 76 | Once you've installed the app, simply run the app and create your unique | |
| 77 | Session ID. It will look something like this: | |
| 78 | =05af1835afdd63c947b47705867501d6373f486aa1ae05b1f2f3fcd24570eba608=. | |
| 83 | 79 | |
| 84 | 80 | You'll need to set a display name and, optionally, a password. If you |
| 85 | 81 | set a password, you will need to enter it every time you open the app. |
| 86 | 82 | |
| 87 |  | |
| 89 | ||
| 90 |  | |
| 83 | #+caption: Session Login (Linux) | |
| 84 | [[https://img.cleberg.net/blog/20200325-session-private-messenger/session_linux_login.png]] | |
| 92 | 85 | |
| 93 |  | |
| 86 | #+caption: Session Login (macOS) | |
| 87 | [[https://img.cleberg.net/blog/20200325-session-private-messenger/session_macos_login.png]] | |
| 95 | 88 | |
| 96 | # Start Messaging | |
| 89 | #+caption: Password Authentication | |
| 90 | [[https://img.cleberg.net/blog/20200325-session-private-messenger/session_password_authentication.png]] | |
| 97 | 91 | |
| 92 | * Start Messaging | |
| 98 | 93 | Once you've created your account and set up your profile details, the |
| 99 | 94 | next step is to start messaging other people. To do so, you'll need to |
| 100 | 95 | share your Session ID with other people. From this point, it's fairly |
| 101 | 96 | straightforward and acts like any other messaging app, so I won't dive |
| 102 | 97 | into much detail here. |
| 103 | 98 | |
| 104 | ## macOS | |
| 105 | ||
| 106 |  | |
| 99 | ** macOS | |
| 100 | #+caption: macOS Conversations | |
| 101 | [[https://img.cleberg.net/blog/20200325-session-private-messenger/session_macos_conversations.png]] | |
| 108 | 102 | |
| 109 | 103 | One key feature to note is that the desktop application now provides a |
| 110 | 104 | helpful pop-up box explaining the process that Session uses to hide your |
| 111 | 105 | IP address: |
| 112 | 106 | |
| 113 |  | |
| 115 | ||
| 116 | ## iOS | |
| 107 | #+caption: IP Address Help Box | |
| 108 | [[https://img.cleberg.net/blog/20200325-session-private-messenger/session_ip.png]] | |
| 117 | 109 | |
| 110 | ** iOS | |
| 118 | 111 | The mobile app is quite simple and effective, giving you all the |
| 119 | 112 | standard mobile messaging options you'd expect. |
| 120 | 113 | |
| 121 |  | |
| 123 | ||
| 124 | # Potential Issues | |
| 114 | #+caption: iOS App | |
| 115 | [[https://img.cleberg.net/blog/20200325-session-private-messenger/session_ios.png]] | |
| 125 | 116 | |
| 117 | * Potential Issues | |
| 126 | 118 | I've discovered one annoying issue that would prevent from using this |
| 127 | 119 | app regularly. On a mobile device, there have been issues with receiving |
| 128 | 120 | messages on time. Even with battery optimization disabled and no network |
content/blog/2021-01-01-seum.md → blog/seum/index.org renamed +43 −43
| @@ -1,27 +1,25 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-01-01 | |
| 3 | title = "SEUM: Speedrunners from Hell" | |
| 4 | description = "A video game review for SEUM: Speedrunners from Hell." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Game Description {#game-description id="809DA4E6-4E0D-4179-B8FF-6C9E767EC74D"} | |
| 8 | ||
| 9 | [SEUM: Speedrunners from | |
| 10 | Hell](https://store.steampowered.com/app/457210/SEUM_Speedrunners_from_Hell/) | |
| 11 | is an incredibly fast-paced mashup of a puzzle game and a free-running | |
| 12 | game. Created by [Pine Studio](https://pinestudio.co) in early 2016 and | |
| 13 | first released as a [demo on | |
| 14 | GameJolt](https://gamejolt.com/games/seum-speedrunners-from-hell-demo/154868), | |
| 15 | this game was successfully green-lit on Steam and has amassed a cult | |
| 16 | following on multiple consoles. | |
| 1 | #+title: SEUM: Speedrunners from Hell | |
| 2 | #+date: 2021-01-01 | |
| 3 | #+description: A video game review for SEUM: Speedrunners from Hell. | |
| 4 | #+filetags: :gaming: | |
| 5 | ||
| 6 | * Game Description | |
| 7 | [[https://store.steampowered.com/app/457210/SEUM_Speedrunners_from_Hell/][SEUM: | |
| 8 | Speedrunners from Hell]] is an incredibly fast-paced mashup of a puzzle | |
| 9 | game and a free-running game. Created by [[https://pinestudio.co][Pine | |
| 10 | Studio]] in early 2016 and first released as a | |
| 11 | [[https://gamejolt.com/games/seum-speedrunners-from-hell-demo/154868][demo | |
| 12 | on GameJolt]], this game was successfully green-lit on Steam and has | |
| 13 | amassed a cult following on multiple consoles. | |
| 17 | 14 | |
| 18 | 15 | Here's the game description straight from the developers: |
| 19 | 16 | |
| 20 | > Like a bastard child of Quake 3 and Super Meat Boy, SEUM: Speedrunners | |
| 21 | > from Hell is truly hardcore and focuses on speed and fast reaction. | |
| 22 | ||
| 23 | ## Story {#story id="BF401145-763D-4399-922B-7D73322B5B40"} | |
| 17 | #+begin_quote | |
| 18 | Like a bastard child of Quake 3 and Super Meat Boy, SEUM: Speedrunners | |
| 19 | from Hell is truly hardcore and focuses on speed and fast reaction. | |
| 20 | #+end_quote | |
| 24 | 21 | |
| 22 | * Story | |
| 25 | 23 | SEUM does a great job setting the stage when you open the game for the |
| 26 | 24 | first time, playing an animated video in the form of comic book images. |
| 27 | 25 | You see Marty, the protagonist, sitting around drinking his beer as |
| @@ -33,10 +31,10 @@ use all the powers in the game. | ||
| 33 | 31 | Check out the screenshot below for one of the first panels of the |
| 34 | 32 | storyline: |
| 35 | 33 | |
| 36 |  | |
| 37 | ||
| 38 | ## Gameplay {#gameplay id="A55CB1AF-E818-4CA7-BF69-E8141369C269"} | |
| 34 | #+caption: SEUM Story | |
| 35 | [[https://img.cleberg.net/blog/20210101-seum/seum_story.png]] | |
| 39 | 36 | |
| 37 | * Gameplay | |
| 40 | 38 | To accomplish each level, you will need to get to the final blue portal |
| 41 | 39 | under a certain time limit. You can beat a level by getting to the |
| 42 | 40 | portal before the time meter runs out or "Dominate" a level by beating |
| @@ -49,44 +47,46 @@ to go through any existing orange portals, light all yellow beacons, | ||
| 49 | 47 | avoid things like fireballs and blades, or use any satanic power orbs |
| 50 | 48 | lying around. These special abilities include: |
| 51 | 49 | |
| 52 | - Gravity | |
| 53 | - Teleport | |
| 54 | - Rewind | |
| 55 | - Spawn platform | |
| 56 | - Roar (DLC) | |
| 57 | - Rocket (DLC) | |
| 58 | - Shadow world (DLC) | |
| 50 | - Gravity | |
| 51 | - Teleport | |
| 52 | - Rewind | |
| 53 | - Spawn platform | |
| 54 | - Roar (DLC) | |
| 55 | - Rocket (DLC) | |
| 56 | - Shadow world (DLC) | |
| 59 | 57 | |
| 60 | 58 | For the main storyline, there are nine floors to beat. Each floor |
| 61 | 59 | contains nine regular levels, one boss level, and one bonus level; |
| 62 | although you don't technically need to beat all levels to advance to | |
| 63 | the next floor. | |
| 64 | ||
| 65 |  | |
| 60 | although you don't technically need to beat all levels to advance to the | |
| 61 | next floor. | |
| 67 | 62 | |
| 68 | ## In-Game Screenshots {#in-game-screenshots id="C779F008-4C8A-4BA4-AA31-60A1BF5A3EE3"} | |
| 63 | #+caption: SEUM Floor Menu | |
| 64 | [[https://img.cleberg.net/blog/20210101-seum/seum_floor.png]] | |
| 69 | 65 | |
| 66 | * In-Game Screenshots | |
| 70 | 67 | The main menu gives you plenty of options for tuning your system, |
| 71 | 68 | playing main levels, playing the DLC, or exploring the other game modes. |
| 72 | 69 | |
| 73 |  | |
| 70 | #+caption: SEUM Main Menu | |
| 71 | [[https://img.cleberg.net/blog/20210101-seum/seum_menu.png]] | |
| 75 | 72 | |
| 76 | 73 | Once you enter a level, you can look around and strategize before |
| 77 | 74 | starting. Clicking any button will start the menu, and you'll have to |
| 78 | 75 | restart if you die. One of the great things about SEUM is that it has |
| 79 | great keyboard shortcuts. You can quickly smash `R` to | |
| 80 | restart the level or `M` to return to the level menu. | |
| 76 | great keyboard shortcuts. You can quickly smash =R= to restart the level | |
| 77 | or =M= to return to the level menu. | |
| 81 | 78 | |
| 82 |  | |
| 79 | #+caption: SEUM Level | |
| 80 | [[https://img.cleberg.net/blog/20210101-seum/seum_level.png]] | |
| 83 | 81 | |
| 84 | 82 | Once you're able to win a level, you'll see the high scores and can |
| 85 | 83 | watch replays of the best scores. |
| 86 | 84 | |
| 87 |  | |
| 85 | #+caption: SEUM Win | |
| 86 | [[https://img.cleberg.net/blog/20210101-seum/seum_win.png]] | |
| 88 | 87 | |
| 89 | 88 | Each regular level contains a beer in a disguised location that may take |
| 90 | 89 | some out-of-the-box thinking. |
| 91 | 90 | |
| 92 |  | |
| 91 | #+caption: SEUM Beer | |
| 92 | [[https://img.cleberg.net/blog/20210101-seum/seum_beer.png]] | |
content/blog/2022-03-26-ssh-mfa.md → blog/ssh-mfa/index.org renamed +61 −70
| @@ -1,83 +1,78 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-03-26 | |
| 3 | title = "Enable TOTP MFA for SSH" | |
| 4 | description = "Learn how to enable timed one-time passcodes for SSH." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Why Do I Need MFA for SSH? | |
| 1 | #+title: Enable TOTP MFA for SSH | |
| 2 | #+date: 2022-03-26 | |
| 3 | #+description: Learn how to enable timed one-time passcodes for SSH. | |
| 4 | #+filetags: :security: | |
| 8 | 5 | |
| 6 | * Why Do I Need MFA for SSH? | |
| 9 | 7 | If you are a sysadmin of a server anywhere (that includes at home!), you |
| 10 | 8 | may want an added layer of protection against intruders. This is not a |
| 11 | 9 | replacement for other security measures, such as: |
| 12 | 10 | |
| 13 | - Disable root SSH | |
| 14 | - Disable SSH password authentication | |
| 15 | - Allow only certain users to login via SSH | |
| 16 | - Allow SSH only from certain IPs | |
| 11 | - Disable root SSH | |
| 12 | - Disable SSH password authentication | |
| 13 | - Allow only certain users to login via SSH | |
| 14 | - Allow SSH only from certain IPs | |
| 17 | 15 | |
| 18 | 16 | However, MFA can be added as an additional security measure to ensure |
| 19 | 17 | that your server is protected. This is especially important if you need |
| 20 | 18 | to allow password authentication for SSH. |
| 21 | 19 | |
| 22 | 20 | For more guidance on server security measures, see my other post: |
| 23 | [Hardening a Public-Facing Home | |
| 24 | Server](/blog/hardening-a-public-facing-home-server/). | |
| 25 | ||
| 26 | ## Install MFA PAM Module | |
| 21 | [[../hardening-a-public-facing-home-server/][Hardening a | |
| 22 | Public-Facing Home Server]]. | |
| 27 | 23 | |
| 24 | * Install MFA PAM Module | |
| 28 | 25 | PAM, which stands for Pluggable Authentication Module, is an |
| 29 | 26 | authentication infrastructure used on Linux systems to authenticate a |
| 30 | 27 | user. In order to use this technology, let's install the |
| 31 | `libpam-google-authenticator` package: | |
| 28 | =libpam-google-authenticator= package: | |
| 32 | 29 | |
| 33 | ```sh | |
| 30 | #+begin_src sh | |
| 34 | 31 | sudo apt-get update |
| 35 | ``` | |
| 32 | #+end_src | |
| 36 | 33 | |
| 37 | ```sh | |
| 34 | #+begin_src sh | |
| 38 | 35 | sudo apt-get install libpam-google-authenticator |
| 39 | ``` | |
| 40 | ||
| 41 | ## Initialize the PAM Module | |
| 42 | ||
| 43 | ### Interactive Method | |
| 36 | #+end_src | |
| 44 | 37 | |
| 38 | * Initialize the PAM Module | |
| 39 | ** Interactive Method | |
| 45 | 40 | Once the package is installed, initialize it and following the |
| 46 | 41 | interactive prompts to generate your OTP or TOTP: |
| 47 | 42 | |
| 48 | ```sh | |
| 43 | #+begin_src sh | |
| 49 | 44 | google-authenticator |
| 50 | ``` | |
| 45 | #+end_src | |
| 51 | 46 | |
| 52 | 47 | If you are not sure how to answer, read the prompts carefully and think |
| 53 | 48 | about having to how each situation would affect your normal login |
| 54 | 49 | attempts. If you are still not sure, use my default responses below. |
| 55 | 50 | |
| 56 | ```txt | |
| 51 | #+begin_src txt | |
| 57 | 52 | OUTPUT |
| 58 | 53 | |
| 59 | 54 | Do you want authentication tokens to be time-based (y/n) y |
| 60 | ``` | |
| 55 | #+end_src | |
| 61 | 56 | |
| 62 | 57 | At this point, use an authenticator app somewhere one of your devices to |
| 63 | 58 | scan the QR code. Any future login attempts after our upcoming |
| 64 | 59 | configuration changes will require that TOTP. |
| 65 | 60 | |
| 66 | ```txt | |
| 61 | #+begin_src txt | |
| 67 | 62 | OUTPUT |
| 68 | 63 | |
| 69 | 64 | Do you want me to update your "/home/user/.google_authenticator" file? (y/n) y |
| 70 | ``` | |
| 65 | #+end_src | |
| 71 | 66 | |
| 72 | ```txt | |
| 67 | #+begin_src txt | |
| 73 | 68 | OUTPUT |
| 74 | 69 | |
| 75 | 70 | Do you want to disallow multiple uses of the same authentication |
| 76 | 71 | token? This restricts you to one login about every 30s, but it increases |
| 77 | 72 | your chances to notice or even prevent man-in-the-middle attacks (y/n) y |
| 78 | ``` | |
| 73 | #+end_src | |
| 79 | 74 | |
| 80 | ```txt | |
| 75 | #+begin_src txt | |
| 81 | 76 | OUTPUT |
| 82 | 77 | |
| 83 | 78 | By default, a new token is generated every 30 seconds by the mobile app. |
| @@ -90,30 +85,29 @@ code, the next code) to 17 permitted codes (the 8 previous codes, the current | ||
| 90 | 85 | code, and the 8 next codes). This will permit for a time skew of up to 4 minutes |
| 91 | 86 | between client and server. |
| 92 | 87 | Do you want to do so? (y/n) n |
| 93 | ``` | |
| 88 | #+end_src | |
| 94 | 89 | |
| 95 | ```txt | |
| 90 | #+begin_src txt | |
| 96 | 91 | OUTPUT |
| 97 | 92 | |
| 98 | 93 | If the computer that you are logging into isn't hardened against brute-force |
| 99 | 94 | login attempts, you can enable rate-limiting for the authentication module. |
| 100 | 95 | By default, this limits attackers to no more than 3 login attempts every 30s. |
| 101 | 96 | Do you want to enable rate-limiting? (y/n) y |
| 102 | ``` | |
| 103 | ||
| 104 | ### Non-Interactive Method | |
| 97 | #+end_src | |
| 105 | 98 | |
| 99 | ** Non-Interactive Method | |
| 106 | 100 | If you need to do this quickly, know your responses to the prompts, or |
| 107 | 101 | are setting this up for numerous users, the non-interactive method can |
| 108 | 102 | be much faster: |
| 109 | 103 | |
| 110 | ```sh | |
| 104 | #+begin_src sh | |
| 111 | 105 | google-authenticator -t -d -f -r 3 -R 30 -w 3 |
| 112 | ``` | |
| 106 | #+end_src | |
| 113 | 107 | |
| 114 | 108 | The options referenced above are as follows: |
| 115 | 109 | |
| 116 | ```txt | |
| 110 | #+begin_src txt | |
| 117 | 111 | google-authenticator [<options>] |
| 118 | 112 | -h, --help Print this message |
| 119 | 113 | -c, --counter-based Set up counter-based (HOTP) verification |
| @@ -133,66 +127,63 @@ google-authenticator [<options>] | ||
| 133 | 127 | -w, --window-size=W Set window of concurrently valid codes |
| 134 | 128 | -W, --minimal-window Disable window of concurrently valid codes |
| 135 | 129 | -e, --emergency-codes=N Number of emergency codes to generate |
| 136 | ``` | |
| 130 | #+end_src | |
| 137 | 131 | |
| 138 | 132 | This fully configures the authenticator, saves it to a file, and then |
| 139 | 133 | outputs the secret key, QR code, and recovery codes. (If you add the |
| 140 | flag `-q`, then there won't be any output). If you use this | |
| 141 | command in an automated fashion, make sure your script captures the | |
| 142 | secret key and/or recovery codes and makes them available to the user. | |
| 143 | ||
| 144 | ## PAM Configuration Settings | |
| 134 | flag =-q=, then there won't be any output). If you use this command in | |
| 135 | an automated fashion, make sure your script captures the secret key | |
| 136 | and/or recovery codes and makes them available to the user. | |
| 145 | 137 | |
| 138 | * PAM Configuration Settings | |
| 146 | 139 | Once you've enabled the T/OTP and have it saved to an MFA app on your |
| 147 | phone or other device, open the PAM `sshd` file: | |
| 140 | phone or other device, open the PAM =sshd= file: | |
| 148 | 141 | |
| 149 | ```sh | |
| 142 | #+begin_src sh | |
| 150 | 143 | sudo nano /etc/pam.d/sshd |
| 151 | ``` | |
| 144 | #+end_src | |
| 152 | 145 | |
| 153 | 146 | You need to do two things in this file. First, add the following lines |
| 154 | 147 | to the bottom of the file: |
| 155 | 148 | |
| 156 | ```config | |
| 149 | #+begin_src config | |
| 157 | 150 | auth required pam_google_authenticator.so nullok |
| 158 | 151 | auth required pam_permit.so |
| 159 | ``` | |
| 152 | #+end_src | |
| 160 | 153 | |
| 161 | 154 | Second, comment-out the following line near the top of the file. |
| 162 | 155 | |
| 163 | 156 | If you leave this line uncommented, every SSH login attempt will ask for |
| 164 | 157 | the following three authentication factors: |
| 165 | 158 | |
| 166 | 1. Publickey | |
| 167 | 2. Password | |
| 168 | 3. T/OTP code | |
| 159 | 1. Publickey | |
| 160 | 2. Password | |
| 161 | 3. T/OTP code | |
| 169 | 162 | |
| 170 | ```config | |
| 163 | #+begin_src config | |
| 171 | 164 | #@include common-auth |
| 172 | ``` | |
| 173 | ||
| 174 | ## SSH Configuration Settings | |
| 165 | #+end_src | |
| 175 | 166 | |
| 176 | Finally, edit the `sshd_config` file again: | |
| 167 | * SSH Configuration Settings | |
| 168 | Finally, edit the =sshd_config= file again: | |
| 177 | 169 | |
| 178 | ```sh | |
| 170 | #+begin_src sh | |
| 179 | 171 | sudo nano /etc/ssh/sshd_config |
| 180 | ``` | |
| 172 | #+end_src | |
| 181 | 173 | |
| 182 | You'll need to change `ChallengeResponseAuthentication` to | |
| 183 | yes and add the `AuthenticationMethods` line to the bottom of | |
| 184 | the file. | |
| 174 | You'll need to change =ChallengeResponseAuthentication= to yes and add | |
| 175 | the =AuthenticationMethods= line to the bottom of the file. | |
| 185 | 176 | |
| 186 | ```config | |
| 177 | #+begin_src config | |
| 187 | 178 | ChallengeResponseAuthentication yes |
| 188 | 179 | AuthenticationMethods publickey,password publickey,keyboard-interactive |
| 189 | ``` | |
| 180 | #+end_src | |
| 190 | 181 | |
| 191 | Finally, restart the `ssh` service: | |
| 182 | Finally, restart the =ssh= service: | |
| 192 | 183 | |
| 193 | ```sh | |
| 184 | #+begin_src sh | |
| 194 | 185 | sudo systemctl restart sshd.service |
| 195 | ``` | |
| 186 | #+end_src | |
| 196 | 187 | |
| 197 | 188 | The next time you log in, you should be greeted with a verification code |
| 198 | 189 | request! |
blog/st/index.org added +87
| @@ -0,0 +1,87 @@ | ||
| 1 | #+title: Simple Terminal | |
| 2 | #+date: 2022-12-17 | |
| 3 | #+description: Instructions for building simple terminal on Fedora. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * st | |
| 7 | [[https://st.suckless.org][st]] standards for Simple Terminal, a simple | |
| 8 | terminal implementation for X made by the | |
| 9 | [[https://suckless.org][suckless]] team. | |
| 10 | ||
| 11 | This post walks through the dependencies needed and process to build and | |
| 12 | install =st= on Fedora Workstation. | |
| 13 | ||
| 14 | ** Obtain Files | |
| 15 | To start, obtain the source files for =st= via =git clone=. | |
| 16 | ||
| 17 | #+begin_src sh | |
| 18 | mkdir ~/suckless && cd ~/suckless | |
| 19 | git clone https://git.suckless.org/st && cd st | |
| 20 | #+end_src | |
| 21 | ||
| 22 | ** Dependencies | |
| 23 | Once you have the files and are in the =st= directory, ensure the | |
| 24 | following packages are installed. | |
| 25 | ||
| 26 | #+begin_src sh | |
| 27 | sudo dnf update && sudo dnf upgrade | |
| 28 | sudo dnf install gcc patch libX11-devel libXft-devel | |
| 29 | #+end_src | |
| 30 | ||
| 31 | ** Building | |
| 32 | Before building, ensure that you read the README file. | |
| 33 | ||
| 34 | #+begin_src sh | |
| 35 | cat README | |
| 36 | #+end_src | |
| 37 | ||
| 38 | Once you've read the instructions, open the =config.mk= file and ensure | |
| 39 | it matches your setup. If you're not sure, leave the default options | |
| 40 | within the file. | |
| 41 | ||
| 42 | Finally, you can build =st= with the following command. Ensure you run | |
| 43 | as root (e.g., =sudo=) or else you may not end up with a usable | |
| 44 | application file. | |
| 45 | ||
| 46 | #+begin_src sh | |
| 47 | sudo make clean install | |
| 48 | #+end_src | |
| 49 | ||
| 50 | ** Customization (Patches) | |
| 51 | Note that customizing =st= requires you to modify the source files or to | |
| 52 | download one of the [[https://st.suckless.org/patches/][available | |
| 53 | patches]] for suckless.org. | |
| 54 | ||
| 55 | If you've already installed =st= and want to customize or install a | |
| 56 | patch, start by uninstalling the current program. | |
| 57 | ||
| 58 | #+begin_src sh | |
| 59 | cd ~/suckless/st | |
| 60 | sudo make uninstall | |
| 61 | #+end_src | |
| 62 | ||
| 63 | Next, grab the =<path>.diff= file from the page of the patch you chose. | |
| 64 | For example, I will be using the | |
| 65 | [[https://st.suckless.org/patches/defaultfontsize/][defaultfontsize]] | |
| 66 | patch in the below example. | |
| 67 | ||
| 68 | #+begin_src sh | |
| 69 | wget https://st.suckless.org/patches/defaultfontsize/st-defaultfontsize-20210225-4ef0cbd.diff | |
| 70 | #+end_src | |
| 71 | ||
| 72 | Once the file is downloaded inside the =st= folder, apply the patch and | |
| 73 | re-install the program. You may need to install the =patch= command if | |
| 74 | you don't have it installed already (you should have installed it | |
| 75 | above). | |
| 76 | ||
| 77 | #+begin_src sh | |
| 78 | patch -i st-defaultfontsize-20210225-4ef0cbd.diff | |
| 79 | sudo make clean install | |
| 80 | #+end_src | |
| 81 | ||
| 82 | Once installed, you can use the default font size patch to launch =st= | |
| 83 | with any font size you wish: | |
| 84 | ||
| 85 | #+begin_src sh | |
| 86 | st -z 16 | |
| 87 | #+end_src | |
blog/steam-on-ntfs/index.org added +93
| @@ -0,0 +1,93 @@ | ||
| 1 | #+title: Linux Gaming Tweak: Steam on NTFS Drives | |
| 2 | #+date: 2020-01-26 | |
| 3 | #+description: Learn how to fix Steam NTFS issues on Linux. | |
| 4 | #+filetags: :gaming:linux: | |
| 5 | ||
| 6 | * Auto-Mount Steam Drives | |
| 7 | #+caption: Steam Screenshot | |
| 8 | [[https://img.cleberg.net/blog/20200125-the-best-linux-software/steam.png]] | |
| 9 | ||
| 10 | If you want to see how to install Steam on Linux, see my other post: | |
| 11 | [[../linux-software/][Linux Software]]. | |
| 12 | ||
| 13 | Are you having trouble launching games, even though they've installed | |
| 14 | correctly? This may happen if you're storing your games on an | |
| 15 | NTFS-formatted drive. This shouldn't be an issue if you're storing your | |
| 16 | games on the same drive that Steam is on, but some gamers prefer to put | |
| 17 | Steam on their main drive and game files on another SSD or HDD. | |
| 18 | ||
| 19 | To fix this problem, you'll need to try a few things. First, you'll need | |
| 20 | to install the =ntfs-3g= package, which is meant for better | |
| 21 | interoperability with Linux. | |
| 22 | ||
| 23 | #+begin_src sh | |
| 24 | sudo apt install ntfs-3g | |
| 25 | #+end_src | |
| 26 | ||
| 27 | Next, you should set up the =/etc/fstab= file to automatically mount | |
| 28 | your drives on boot. To automatically mount your drives when the | |
| 29 | computer boots up, you'll have to create the folders you want to mount | |
| 30 | your drive to first. I store mine in the =/mnt= folder using names that | |
| 31 | I'll recognize, but you can create your folders wherever you want. | |
| 32 | ||
| 33 | #+begin_src sh | |
| 34 | mkdir /path/to/folder | |
| 35 | #+end_src | |
| 36 | ||
| 37 | For example: | |
| 38 | ||
| 39 | #+begin_src sh | |
| 40 | mkdir /mnt/steam_library | |
| 41 | #+end_src | |
| 42 | ||
| 43 | To automatically mount drives upon system boot, you will need to collect | |
| 44 | a few items. The UUID is the identification number connected to | |
| 45 | whichever drive you're using to store Steam games. | |
| 46 | ||
| 47 | Drives are usually labeled similar to =/dev/nvme0n1p1= or =/dev/sda1=, | |
| 48 | so you'll need to find the line in the output of the command below that | |
| 49 | correlates to your drive and copy the UUID over to the =/etc/fstab= | |
| 50 | file. | |
| 51 | ||
| 52 | #+begin_src sh | |
| 53 | sudo blkid | grep UUID= | |
| 54 | #+end_src | |
| 55 | ||
| 56 | Next, you'll need your =uid= and =gid=. To find these, run the following | |
| 57 | command: | |
| 58 | ||
| 59 | #+begin_src sh | |
| 60 | id -u && id -g | |
| 61 | #+end_src | |
| 62 | ||
| 63 | Now that you have collected the necessary information, open the | |
| 64 | =/etc/fstab= file: | |
| 65 | ||
| 66 | #+begin_src sh | |
| 67 | sudo nano /etc/fstab | |
| 68 | #+end_src | |
| 69 | ||
| 70 | Each drive you want to mount on boot should have its own line in the | |
| 71 | =/etc/fstab= file that looks similar to this: | |
| 72 | ||
| 73 | #+begin_src config | |
| 74 | UUID=B64E53824E5339F7 /mnt/steam_library ntfs-3g uid=1000,gid=1000 0 0 | |
| 75 | #+end_src | |
| 76 | ||
| 77 | Now all you need to do is unmount your drive and re-mount it. You can | |
| 78 | unmount the drive by doing this (be sure to use the correct drive name | |
| 79 | here): | |
| 80 | ||
| 81 | #+begin_src sh | |
| 82 | sudo umount /dev/sdxX | |
| 83 | #+end_src | |
| 84 | ||
| 85 | You can re-mount all your drives by executing the following: | |
| 86 | ||
| 87 | #+begin_src sh | |
| 88 | sudo mount -a | |
| 89 | #+end_src | |
| 90 | ||
| 91 | If you don't know what your drive name is, or you're nervous about | |
| 92 | unmounting and re-mounting, simply reboot your computer, and it will be | |
| 93 | done for you automatically. | |
content/blog/2022-10-20-syncthing.md → blog/syncthing/index.org renamed +82 −91
| @@ -1,70 +1,66 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-10-04 | |
| 3 | title = "Syncthing: A Minimal Self-Hosted Cloud Storage Solution" | |
| 4 | description = "" | |
| 5 | +++ | |
| 6 | ||
| 7 | ## An Overview of Syncthing | |
| 1 | #+title: Syncthing: A Minimal Self-Hosted Cloud Storage Solution | |
| 2 | #+date: 2022-10-04 | |
| 3 | #+description: An overview of how you can use Syncthing as a minimal alternative to cloud storage. | |
| 4 | #+filetags: :selfhosting: | |
| 8 | 5 | |
| 6 | * An Overview of Syncthing | |
| 9 | 7 | If you've been looking around the self-hosted cloud storage space for a |
| 10 | 8 | while, you've undoubtedly run into someone suggesting |
| 11 | [Syncthing](https://syncthing.net) as an option. However, it is an | |
| 9 | [[https://syncthing.net][Syncthing]] as an option. However, it is an | |
| 12 | 10 | unusual alternative for those users out there who are used to having a |
| 13 | centralized cloud server that serves as the "controller" of the data | |
| 14 | and interacts with clients on devices to fetch files. | |
| 11 | centralized cloud server that serves as the "controller" of the data and | |
| 12 | interacts with clients on devices to fetch files. | |
| 15 | 13 | |
| 16 | 14 | This post is a walkthrough of the Syncthing software, how I set up my |
| 17 | 15 | personal storage, and some pros and cons of using the software. |
| 18 | 16 | |
| 19 | ## Installing Syncthing | |
| 20 | ||
| 17 | * Installing Syncthing | |
| 21 | 18 | To install Syncthing, visit the |
| 22 | [Downloads](https://syncthing.net/downloads/) page or install via your | |
| 19 | [[https://syncthing.net/downloads/][Downloads]] page or install via your | |
| 23 | 20 | device's package manager. |
| 24 | 21 | |
| 25 | ### Server & Desktop | |
| 26 | ||
| 22 | ** Server & Desktop | |
| 27 | 23 | You can install Syncthing on servers and desktops via the Downloads page |
| 28 | 24 | linked above or via the command-line. |
| 29 | 25 | |
| 30 | 26 | For Debian-based distros: |
| 31 | 27 | |
| 32 | ```sh | |
| 28 | #+begin_src sh | |
| 33 | 29 | sudo apt install syncthing |
| 34 | ``` | |
| 30 | #+end_src | |
| 35 | 31 | |
| 36 | 32 | For Fedora-based distros: |
| 37 | 33 | |
| 38 | ```sh | |
| 34 | #+begin_src sh | |
| 39 | 35 | sudo dnf install syncthing |
| 40 | ``` | |
| 41 | ||
| 42 | ### Mobile | |
| 36 | #+end_src | |
| 43 | 37 | |
| 38 | ** Mobile | |
| 44 | 39 | Syncthing for Android is available on |
| 45 | [F-Droid](https://f-droid.org/packages/com.nutomic.syncthingandroid/) | |
| 46 | and [Google | |
| 47 | Play](https://play.google.com/store/apps/details?id=com.nutomic.syncthingandroid). | |
| 48 | Syncthing does not have an official iOS client, but there is a | |
| 49 | third-party client called [Möbius | |
| 50 | Sync](https://apps.apple.com/us/app/m%C3%B6bius-sync/id1539203216). | |
| 51 | ||
| 52 | ## How Does Syncthing Work? | |
| 53 | ||
| 40 | [[https://f-droid.org/packages/com.nutomic.syncthingandroid/][F-Droid]] | |
| 41 | and | |
| 42 | [[https://play.google.com/store/apps/details?id=com.nutomic.syncthingandroid][Google | |
| 43 | Play]]. Syncthing does not have an official iOS client, but there is a | |
| 44 | third-party client called | |
| 45 | [[https://apps.apple.com/us/app/m%C3%B6bius-sync/id1539203216][Möbius | |
| 46 | Sync]]. | |
| 47 | ||
| 48 | * How Does Syncthing Work? | |
| 54 | 49 | To start, I wanted to include the main marketing blurb from their |
| 55 | 50 | website: |
| 56 | 51 | |
| 57 | > Syncthing is a continuous file synchronization program. It | |
| 58 | > synchronizes files between two or more computers in real time, safely | |
| 59 | > protected from prying eyes. Your data is your data alone, and you | |
| 60 | > deserve to choose where it is stored, whether it is shared with some | |
| 61 | > third party, and how it's transmitted over the internet. | |
| 52 | #+begin_quote | |
| 53 | Syncthing is a continuous file synchronization program. It synchronizes | |
| 54 | files between two or more computers in real time, safely protected from | |
| 55 | prying eyes. Your data is your data alone, and you deserve to choose | |
| 56 | where it is stored, whether it is shared with some third party, and how | |
| 57 | it's transmitted over the internet. | |
| 58 | #+end_quote | |
| 62 | 59 | |
| 63 | 60 | Let's break this apart and add in some other details to help explain |
| 64 | 61 | what exactly Syncthing does in order to sync files between devices. |
| 65 | 62 | |
| 66 | ### Local Syncthing Server(s) | |
| 67 | ||
| 63 | ** Local Syncthing Server(s) | |
| 68 | 64 | Syncthing syncs files between multiple devices by creating a local |
| 69 | 65 | server on each device. These local servers handle a few different |
| 70 | 66 | things, such as watching files and directories for changes, hosting an |
| @@ -72,40 +68,37 @@ administrative GUI website, and authenticating with connected devices. | ||
| 72 | 68 | |
| 73 | 69 | You can also start, stop, and restart the Syncthing server via the |
| 74 | 70 | command-line or web dashboard. If you're running Syncthing on a device |
| 75 | with `systemd`, you can use the following commands: | |
| 71 | with =systemd=, you can use the following commands: | |
| 76 | 72 | |
| 77 | ```sh | |
| 73 | #+begin_src sh | |
| 78 | 74 | sudo systemctl start syncthing@username.service |
| 79 | 75 | sudo systemctl restart syncthing@username.service |
| 80 | 76 | sudo systemctl stop syncthing@username.service |
| 81 | ``` | |
| 82 | ||
| 83 | ### Syncthing Dashboard | |
| 77 | #+end_src | |
| 84 | 78 | |
| 79 | ** Syncthing Dashboard | |
| 85 | 80 | This biggest part of Syncthing is the admin GUI website that runs on |
| 86 | 81 | each device (note that mobile devices will use the Syncthing app rather |
| 87 | 82 | than the web GUI). The admin GUI is available through the web browser on |
| 88 | 83 | the local device that is running Syncthing - simply go to |
| 89 | `http://localhost:8384` or | |
| 90 | `http://127.0.0.1:8384`. This web page is the place where you | |
| 91 | will change settings, add/modify synced files, and add/modify connected | |
| 92 | devices. | |
| 84 | =http://localhost:8384= or =http://127.0.0.1:8384=. This web page is the | |
| 85 | place where you will change settings, add/modify synced files, and | |
| 86 | add/modify connected devices. | |
| 93 | 87 | |
| 94 | 88 | Here's an example web GUI dashboard: |
| 95 | 89 | |
| 96 |  | |
| 98 | ||
| 99 | ### Remote Devices | |
| 90 | #+caption: Syncthing Dashboard | |
| 91 | [[https://img.cleberg.net/blog/20221020-syncthing/syncthing_gui.png]] | |
| 100 | 92 | |
| 93 | ** Remote Devices | |
| 101 | 94 | A cloud storage solution wouldn't be very useful if you aren't able to |
| 102 | 95 | share data among various devices. Syncthing does this by sharing Device |
| 103 | 96 | IDs to connect servers, and then by manually sharing Folders with |
| 104 | 97 | devices that have been connected. |
| 105 | 98 | |
| 106 | 99 | For instance, if you have a laptop running Syncthing and then install |
| 107 | the Syncthing mobile app on a phone, you could scan the laptop's QR | |
| 108 | code for Device ID and then accept the authentication on the laptop's | |
| 100 | the Syncthing mobile app on a phone, you could scan the laptop's QR code | |
| 101 | for Device ID and then accept the authentication on the laptop's | |
| 109 | 102 | dashboard. Next, you can use either device to select a folder for |
| 110 | 103 | sharing and dictating which device should send, receive, or both. |
| 111 | 104 | |
| @@ -114,8 +107,7 @@ which can add devices from the introducer to the device list, for | ||
| 114 | 107 | mutually shared folders. You can also configure Auto Accept, |
| 115 | 108 | compression, rate limits, and more settings per device. |
| 116 | 109 | |
| 117 | ## My Personal Cloud Storage Set-up | |
| 118 | ||
| 110 | * My Personal Cloud Storage Set-up | |
| 119 | 111 | Personally, I use a model similar to a traditional cloud storage |
| 120 | 112 | service. I have a "centralized" server running 24/7 that acts as an |
| 121 | 113 | Introducer for my Syncthing network. I think of this as my main storage |
| @@ -129,50 +121,49 @@ network, both running intermittently as they are not powered-on 24/7. | ||
| 129 | 121 | The initial set-up of the software was easy enough, but data transfer |
| 130 | 122 | rates were incredibly slow for me due to the Wi-Fi. Instead, I plugged |
| 131 | 123 | my laptop into the ethernet network that my server is on and manually |
| 132 | copied my folders over to the server with `scp`. Once | |
| 133 | complete, Syncthing validated that all files were there and not missing, | |
| 134 | and it did not need to transfer any data through the WAN. | |
| 124 | copied my folders over to the server with =scp=. Once complete, | |
| 125 | Syncthing validated that all files were there and not missing, and it | |
| 126 | did not need to transfer any data through the WAN. | |
| 135 | 127 | |
| 136 | 128 | As slow as the transfer was going, this probably saved me a few days of |
| 137 | 129 | waiting for my ~100GB sync. |
| 138 | 130 | |
| 139 | ## Pros & Cons | |
| 140 | ||
| 141 | I've put together a short list of pros and cons for Syncthing. I | |
| 142 | thought about my experiences with Nextcloud, WebDAV, proprietary | |
| 143 | services (Google Drive, iCloud, etc.), and privacy-focused cloud | |
| 144 | solutions (pCloud, Tresorit, etc.). | |
| 145 | ||
| 146 | **Pros:** | |
| 147 | ||
| 148 | - I've faced no data loss at all through my two-month trial run. | |
| 149 | - No third-parties store your data on their servers. | |
| 150 | - You have full control over your data and can take your data and | |
| 151 | leave at any time. | |
| 152 | - It's possible to encrypt client-side easily with software like | |
| 153 | Cryptomator. | |
| 154 | - No proprietary clients or mounted volumes, just plain files and | |
| 155 | folders. | |
| 156 | ||
| 157 | **Cons:** | |
| 158 | ||
| 159 | - The learning curve is steeper than traditional cloud services and is | |
| 160 | focused on a technical audience. | |
| 161 | - If a device needs to modify files in a Folder, the devices will need | |
| 162 | to sync ALL files from the folder, which may be large. To avoid size | |
| 163 | restraints, split large folders into smaller folders for syncing. | |
| 164 | - Syncing can be slow due to the clients/servers initially connecting | |
| 165 | or re-connecting after sleeping. | |
| 166 | - Multiple personal devices are required and require the user to own | |
| 167 | or rent them as no third-party servers are involved in the storage | |
| 168 | of data. | |
| 169 | ||
| 170 | Overall, I've had a great experience with Syncthing so far. I've had | |
| 171 | no data loss, syncing has been quick and easy when changes are made to | |
| 131 | * Pros & Cons | |
| 132 | I've put together a short list of pros and cons for Syncthing. I thought | |
| 133 | about my experiences with Nextcloud, WebDAV, proprietary services | |
| 134 | (Google Drive, iCloud, etc.), and privacy-focused cloud solutions | |
| 135 | (pCloud, Tresorit, etc.). | |
| 136 | ||
| 137 | *Pros:* | |
| 138 | ||
| 139 | - I've faced no data loss at all through my two-month trial run. | |
| 140 | - No third-parties store your data on their servers. | |
| 141 | - You have full control over your data and can take your data and leave | |
| 142 | at any time. | |
| 143 | - It's possible to encrypt client-side easily with software like | |
| 144 | Cryptomator. | |
| 145 | - No proprietary clients or mounted volumes, just plain files and | |
| 146 | folders. | |
| 147 | ||
| 148 | *Cons:* | |
| 149 | ||
| 150 | - The learning curve is steeper than traditional cloud services and is | |
| 151 | focused on a technical audience. | |
| 152 | - If a device needs to modify files in a Folder, the devices will need | |
| 153 | to sync ALL files from the folder, which may be large. To avoid size | |
| 154 | restraints, split large folders into smaller folders for syncing. | |
| 155 | - Syncing can be slow due to the clients/servers initially connecting or | |
| 156 | re-connecting after sleeping. | |
| 157 | - Multiple personal devices are required and require the user to own or | |
| 158 | rent them as no third-party servers are involved in the storage of | |
| 159 | data. | |
| 160 | ||
| 161 | Overall, I've had a great experience with Syncthing so far. I've had no | |
| 162 | data loss, syncing has been quick and easy when changes are made to | |
| 172 | 163 | files, device connections are reliable, and I love the freedom of |
| 173 | 164 | controlling the clients and servers as I choose. |
| 174 | 165 | |
| 175 | 166 | Not to mention that I appreciate that I - or someone else - could pull |
| 176 | the Syncthing [source code](https://github.com/syncthing) and continue | |
| 167 | the Syncthing [[https://github.com/syncthing][source code]] and continue | |
| 177 | 168 | development/support if the Syncthing Foundation decides to stop |
| 178 | 169 | developing the software or sells the business. |
blog/tableau-dashboard/index.org added +156
| @@ -0,0 +1,156 @@ | ||
| 1 | #+title: Data Visualization: Mapping Omaha Crime Data with Tableau | |
| 2 | #+date: 2024-01-27 | |
| 3 | #+description: Learn how to utilize Tableau Public to build a dashboard to map crimes across Omaha. | |
| 4 | #+filetags: :data: | |
| 5 | ||
| 6 | In this project, I am going to show you how to use Tableau Public for | |
| 7 | free to create simple dashboards. | |
| 8 | ||
| 9 | I will be creating simple visuals from an Omaha crime data set and | |
| 10 | combining them to create the dashboard below. You can view this | |
| 11 | dashboard interactively online here: | |
| 12 | [[https://public.tableau.com/app/profile/c.c7042/viz/OmahaCrimeData2015-2023/OmahaCrimeData2015-2023#1][Omaha | |
| 13 | Crime Data (2015 - 2023)]]. | |
| 14 | ||
| 15 | #+caption: Tableau Dashboard | |
| 16 | [[https://img.cleberg.net/blog/20240127-tableau-dashboard/dashboard.png]] | |
| 17 | ||
| 18 | * Gather the Data | |
| 19 | You can download incident data from the Omaha Police Department on their | |
| 20 | [[https://police.cityofomaha.org/crime-information/incident-data-download][Incident | |
| 21 | Data Download]] page. They currently have files for the years 2015 | |
| 22 | through 2023. | |
| 23 | ||
| 24 | Each file will be downloaded as a CSV file, approximately 3 MB - 8 MB. | |
| 25 | ||
| 26 | * Clean and Transform the Data | |
| 27 | I have used Python to combine the files into a single CSV file, as well | |
| 28 | as adding a custom =datetime= column. You could do this step in any | |
| 29 | software you prefer, but I prefer Python as its free, easy to use, and | |
| 30 | has a plethora of support resources online. | |
| 31 | ||
| 32 | Start by opening a terminal, navigating to your Downloads directory, and | |
| 33 | creating a python script. | |
| 34 | ||
| 35 | #+begin_src sh | |
| 36 | cd ~/Downloads | |
| 37 | nano data_processing.py | |
| 38 | #+end_src | |
| 39 | ||
| 40 | Within the Python script, paste the following: | |
| 41 | ||
| 42 | #+begin_src python | |
| 43 | # Import modules | |
| 44 | import pandas as pd | |
| 45 | import glob | |
| 46 | import os | |
| 47 | ||
| 48 | # Import the data | |
| 49 | path = r"~/Downloads/*.csv" | |
| 50 | files = glob.glob(path) | |
| 51 | ||
| 52 | list = [] | |
| 53 | ||
| 54 | for file in files: | |
| 55 | df_tmp = pd.read_csv(file) | |
| 56 | li.append(df_tmp) | |
| 57 | ||
| 58 | df = pd.concat(list, axis=0, ignore_index=True) | |
| 59 | ||
| 60 | # Create a combined datetime column | |
| 61 | df["datetime"] = pd.to_datetime( | |
| 62 | df["date"] + " " + df["time"], | |
| 63 | format="%m/%d/%Y %H:%M:%S" | |
| 64 | ) | |
| 65 | df.head() | |
| 66 | ||
| 67 | # Export the combined data | |
| 68 | df.to_csv(r"~/Downloads/combined_incidents.csv") | |
| 69 | #+end_src | |
| 70 | ||
| 71 | Once pasted, save and close the file. You can execute the file like so: | |
| 72 | ||
| 73 | #+begin_src sh | |
| 74 | python3 data_processing.py | |
| 75 | #+end_src | |
| 76 | ||
| 77 | After this, you should have a combined data file that contains all | |
| 78 | incidents between 2015 and 2023. Mine was approximately 55 MB. | |
| 79 | ||
| 80 | * Tableau Public | |
| 81 | [[https://public.tableau.com/][Tableau Public]] is a free-to-use web | |
| 82 | application that allows you to create visualizations by uploading data | |
| 83 | sources. Note that there's no way to keep the data and visualizations | |
| 84 | private, so don't upload anything private. | |
| 85 | ||
| 86 | After creating an account, you can click the =Create= > =Web Authoring= | |
| 87 | link to create your first visualization. | |
| 88 | ||
| 89 | #+caption: Create Button | |
| 90 | [[https://img.cleberg.net/blog/20240127-tableau-dashboard/create_button.png]] | |
| 91 | ||
| 92 | ** Upload the Data | |
| 93 | Once you've opened your first project, Tableau will ask you to connect | |
| 94 | to your data. For this project, click the =Upload from computer= button | |
| 95 | and select the CSV file previously combined in the step above. | |
| 96 | ||
| 97 | #+caption: Connect Data | |
| 98 | [[https://img.cleberg.net/blog/20240127-tableau-dashboard/connect_data.png]] | |
| 99 | ||
| 100 | Once connected, you can refresh the preview of the data with the | |
| 101 | =Refresh Data Source= button in the toolbar. | |
| 102 | ||
| 103 | #+caption: Data Preview | |
| 104 | [[https://img.cleberg.net/blog/20240127-tableau-dashboard/data_preview.png]] | |
| 105 | ||
| 106 | If you need to edit any of the data types, column names, etc., you can | |
| 107 | do so now. Once complete, generate an extract so that you can start | |
| 108 | creating visualizations. | |
| 109 | ||
| 110 | ** Create Visualizations | |
| 111 | To start, create a worksheet in the toolbar at the bottom of the screen. | |
| 112 | ||
| 113 | Within this screen, select a column from the =Data= side bar on the left | |
| 114 | and drag it into the =Columns= or =Rows= area of the canvas. | |
| 115 | ||
| 116 | See below for the map visualization. You can recreate this by adding the | |
| 117 | following fields: | |
| 118 | ||
| 119 | - =Columns=: Lon | |
| 120 | - =Rows=: Lat | |
| 121 | - =Marks=: | |
| 122 | - Description | |
| 123 | - Datetime | |
| 124 | - =Filters=: Datetime | |
| 125 | ||
| 126 | #+caption: Worksheet Editing | |
| 127 | [[https://img.cleberg.net/blog/20240127-tableau-dashboard/worksheet_edit.png]] | |
| 128 | ||
| 129 | You can repeat this process for each visualization you want to create. | |
| 130 | Explore your options by dragging data fields to different areas and by | |
| 131 | opening the field options to explore what operations can be performed on | |
| 132 | different data types (e.g., average, count, etc.). | |
| 133 | ||
| 134 | ** Create Dashboard | |
| 135 | To create a dashboard, click the button on the toolbar at the bottom of | |
| 136 | the screen. Within the dashboard, drag each sheet from the left side bar | |
| 137 | onto the dashboard canvas. | |
| 138 | ||
| 139 | #+caption: Dashboard Editing | |
| 140 | [[https://img.cleberg.net/blog/20240127-tableau-dashboard/dashboard_edit.png]] | |
| 141 | ||
| 142 | ** Formatting | |
| 143 | You can explore a ton of different formatting options throughout the | |
| 144 | worksheets and dashboard. Specifically for maps, you can alter the map | |
| 145 | layers, background, and visible features through the =Map= menu in the | |
| 146 | top file menu of the editing screen. | |
| 147 | ||
| 148 | In the finished dashboard below, I opted for a dark mode with a map that | |
| 149 | showed county lines and city names. | |
| 150 | ||
| 151 | There's a ton of other options available to be used in a dashboard like | |
| 152 | this, but this project shows a quick preview of what you can do in | |
| 153 | Tableau Public. | |
| 154 | ||
| 155 | #+caption: Tableau Dashboard | |
| 156 | [[https://img.cleberg.net/blog/20240127-tableau-dashboard/dashboard.png]] | |
content/blog/2022-06-16-terminal-lifestyle.md → blog/terminal-lifestyle/index.org renamed +84 −88
| @@ -1,25 +1,23 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-06-16 | |
| 3 | title = "A Terminal Lifestyle" | |
| 4 | description = "Explaining how I live my digital life mostly in the console/terminal." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Text-Based Simplicity | |
| 1 | #+title: A Terminal Lifestyle | |
| 2 | #+date: 2022-06-16 | |
| 3 | #+description: Explaining how I live my digital life mostly in the console/terminal. | |
| 4 | #+filetags: :linux: | |
| 8 | 5 | |
| 6 | * Text-Based Simplicity | |
| 9 | 7 | I've detailed my views on web-based minimalism and related topics in |
| 10 | 8 | other posts throughout the years; e.g., JavaScript/CSS bloat slowing |
| 11 | 9 | down websites that are essentially a text document. However, I have |
| 12 | 10 | never really expanded beyond talking about the web and describing how I |
| 13 | 11 | focus on minimizing distractions in other digital environments. |
| 14 | 12 | |
| 15 | This post is going to set the baseline for how I *try* to live my | |
| 13 | This post is going to set the baseline for how I /try/ to live my | |
| 16 | 14 | digital life. It does not necessarily get into my physical life, which |
| 17 | 15 | is often harder to control and contain all the noise in our modern |
| 18 | 16 | world. |
| 19 | 17 | |
| 20 | 18 | While there are new things to do every day in our digital world, I find |
| 21 | 19 | that keeping a core set of values and interests can ground you and keep |
| 22 | you mindful of *why* you are participating in the digital world. For | |
| 20 | you mindful of /why/ you are participating in the digital world. For | |
| 23 | 21 | example, if - at your core - you have no interest in what strangers |
| 24 | 22 | think about random topics, it would be unwise to start participating in |
| 25 | 23 | social media. However, I am someone who has been dragged in by effective |
| @@ -30,12 +28,11 @@ I won't dive much further into explaining the philosophy of all this, | ||
| 30 | 28 | but I will link a few helpful articles that may pique your interest if |
| 31 | 29 | you're in search of more meaningful experiences: |
| 32 | 30 | |
| 33 | - [Mindfulness](https://en.wikipedia.org/wiki/Mindfulness) | |
| 34 | - [Minimalism](https://en.wikipedia.org/wiki/Minimalism) | |
| 35 | - [Stoicism](https://en.wikipedia.org/wiki/Stoicism) | |
| 36 | ||
| 37 | ## Living Life in the Terminal | |
| 31 | - [[https://en.wikipedia.org/wiki/Mindfulness][Mindfulness]] | |
| 32 | - [[https://en.wikipedia.org/wiki/Minimalism][Minimalism]] | |
| 33 | - [[https://en.wikipedia.org/wiki/Stoicism][Stoicism]] | |
| 38 | 34 | |
| 35 | * Living Life in the Terminal | |
| 39 | 36 | My personal approach to reducing digital distractions and increasing my |
| 40 | 37 | focus on the task at hand is to use a terminal for as much as I possibly |
| 41 | 38 | can. |
| @@ -43,12 +40,12 @@ can. | ||
| 43 | 40 | Most days, this means that I have a few tabs open constantly in my |
| 44 | 41 | terminal: |
| 45 | 42 | |
| 46 | 1. A web browser | |
| 47 | 2. A chat client | |
| 48 | 3. An email client | |
| 49 | 4. An RSS feed reader | |
| 50 | 5. A local shell for navigating my computer's files | |
| 51 | 6. A remote shell for managing servers and other machines | |
| 43 | 1. A web browser | |
| 44 | 2. A chat client | |
| 45 | 3. An email client | |
| 46 | 4. An RSS feed reader | |
| 47 | 5. A local shell for navigating my computer's files | |
| 48 | 6. A remote shell for managing servers and other machines | |
| 52 | 49 | |
| 53 | 50 | Beyond this, I rarely open other tabs or GUI applications, unless |
| 54 | 51 | absolutely necessary. If you look, you may be surprised what can be |
| @@ -57,56 +54,55 @@ accomplished in the terminal. | ||
| 57 | 54 | For example, I have moved my music and entertainment downloads to the |
| 58 | 55 | terminal, along with my device VPN connections. I am exploring options |
| 59 | 56 | for moving my RSS subscriptions to something like |
| 60 | [Newsboat](https://newsboat.org/), so that I can read my daily articles | |
| 61 | without all the fuss. | |
| 57 | [[https://newsboat.org/][Newsboat]], so that I can read my daily | |
| 58 | articles without all the fuss. | |
| 62 | 59 | |
| 63 | 60 | Now that we have some examples out of the way, let's dive into the |
| 64 | 61 | specifics. |
| 65 | 62 | |
| 66 | ### Browsing the Web | |
| 67 | ||
| 68 | I'm going to start off with a hard topic for those who prefer to live | |
| 69 | in the terminal: web browsing. This task is made hard mostly by websites | |
| 63 | ** Browsing the Web | |
| 64 | I'm going to start off with a hard topic for those who prefer to live in | |
| 65 | the terminal: web browsing. This task is made hard mostly by websites | |
| 70 | 66 | and web apps that require JavaScript to run. The other difficult part is |
| 71 | that if you're using a text-based browser, that means images won't | |
| 72 | load (hopefully that's obvious). | |
| 67 | that if you're using a text-based browser, that means images won't load | |
| 68 | (hopefully that's obvious). | |
| 73 | 69 | |
| 74 | I am using [Lynx](https://lynx.invisible-island.net), a text-based | |
| 70 | I am using [[https://lynx.invisible-island.net][Lynx]], a text-based | |
| 75 | 71 | browser that runs quickly and easily in the terminal. Lynx allows me to |
| 76 | browser most websites by simply typing `g` and then typing in | |
| 77 | the URL I want. | |
| 72 | browser most websites by simply typing =g= and then typing in the URL I | |
| 73 | want. | |
| 78 | 74 | |
| 79 |  | |
| 75 | #+caption: Lynx | |
| 76 | [[https://img.cleberg.net/blog/20220616-terminal-lifestyle/lynx.png]] | |
| 80 | 77 | |
| 81 | If you need a search engine while in Lynx, I recommend [DuckDuckGo | |
| 82 | (Lite)](https://lite.duckduckgo.com/lite/), which allows you to search | |
| 83 | the web using their text-only interface. | |
| 78 | If you need a search engine while in Lynx, I recommend | |
| 79 | [[https://lite.duckduckgo.com/lite/][DuckDuckGo (Lite)]], which allows | |
| 80 | you to search the web using their text-only interface. | |
| 84 | 81 | |
| 85 |  | |
| 82 | #+caption: DuckDuckGo !Lite | |
| 83 | [[https://img.cleberg.net/blog/20220616-terminal-lifestyle/ddg.png]] | |
| 87 | 84 | |
| 88 | 85 | Eventually, you will run into websites that don't work (or are just too |
| 89 | ugly and messy) in a text-only mode, and you'll be forced to switch | |
| 90 | over to a GUI browser to look at that site. Personally, I don't mind | |
| 91 | this as it doesn't happen as often as I thought it would. | |
| 86 | ugly and messy) in a text-only mode, and you'll be forced to switch over | |
| 87 | to a GUI browser to look at that site. Personally, I don't mind this as | |
| 88 | it doesn't happen as often as I thought it would. | |
| 92 | 89 | |
| 93 | 90 | The only time I need to do this is when I want to browse an |
| 94 | 91 | image/video-focused webpage or if I need to log in to a site, and it |
| 95 | doesn't support a text-only login page. For example, I am able to | |
| 96 | easily log in to [Sourcehut](https://sr.ht) in lynx. | |
| 97 | ||
| 98 | ### Chatting with Friends | |
| 92 | doesn't support a text-only login page. For example, I am able to easily | |
| 93 | log in to [[https://sr.ht][Sourcehut]] in lynx. | |
| 99 | 94 | |
| 95 | ** Chatting with Friends | |
| 100 | 96 | After web browsing activities, my main form of terminal communication is |
| 101 | Matrix. I use the [gomuks](https://docs.mau.fi/gomuks/) client | |
| 97 | Matrix. I use the [[https://docs.mau.fi/gomuks/][gomuks]] client | |
| 102 | 98 | currently. |
| 103 | 99 | |
| 104 | 100 | This was incredibly easy to install on macOS (but I will need to see if |
| 105 | 101 | it'll be just as easy on Linux when my new laptop arrives): |
| 106 | 102 | |
| 107 | ```sh | |
| 103 | #+begin_src sh | |
| 108 | 104 | brew install gomuks |
| 109 | ``` | |
| 105 | #+end_src | |
| 110 | 106 | |
| 111 | 107 | Once you launch gomuks, it will sync and require your username and |
| 112 | 108 | password to login. After doing so, the only problem I ran into was |
| @@ -114,102 +110,102 @@ verifying my gomuks client so that I could participate in rooms with | ||
| 114 | 110 | E2EE. |
| 115 | 111 | |
| 116 | 112 | Finally, I was able to verify the session by opening the Element desktop |
| 117 | app (I assume you can do this in the browser and mobile app too, but | |
| 118 | I'm not sure) and manually verifying myself with this process: | |
| 113 | app (I assume you can do this in the browser and mobile app too, but I'm | |
| 114 | not sure) and manually verifying myself with this process: | |
| 119 | 115 | |
| 120 | 1. Open the Element desktop app | |
| 121 | 2. Open a room I was a member of | |
| 122 | 3. Open the `Room Info` pane | |
| 123 | 4. Open the `People` menu and search for myself | |
| 124 | 5. Click on my profile name | |
| 125 | 6. Click on the session link under the `Security` section | |
| 126 | and follow the prompts to manually verify the session | |
| 116 | 1. Open the Element desktop app | |
| 117 | 2. Open a room I was a member of | |
| 118 | 3. Open the =Room Info= pane | |
| 119 | 4. Open the =People= menu and search for myself | |
| 120 | 5. Click on my profile name | |
| 121 | 6. Click on the session link under the =Security= section and follow the | |
| 122 | prompts to manually verify the session | |
| 127 | 123 | |
| 128 | 124 | Overall, I like gomuks and am able to enjoy all the features I was using |
| 129 | 125 | in Element. The only hiccup I have occurred is manually downloading |
| 130 | 126 | images to view them, which can be annoying. |
| 131 | 127 | |
| 132 |  | |
| 133 | ||
| 134 | ||
| 128 | #+caption: gomuks | |
| 129 | [[https://img.cleberg.net/blog/20220616-terminal-lifestyle/gomuks.png]] | |
| 135 | 130 | |
| 131 | ||
| 136 | 132 | Moving email to the terminal has been the hardest of the tasks for me. |
| 137 | 133 | Unlike web browsing, where I can simply decide to not look at a website |
| 138 | 134 | that does not work in the terminal, I cannot simply ignore emails sent |
| 139 | 135 | to me. |
| 140 | 136 | |
| 141 | Personally, I am experimenting with [neomutt](https://neomutt.org/) as a | |
| 142 | potential email client. | |
| 137 | Personally, I am experimenting with [[https://neomutt.org/][neomutt]] as | |
| 138 | a potential email client. | |
| 143 | 139 | |
| 144 | However, this requires a **TON** of configuration and tweaking to get | |
| 140 | However, this requires a *TON** of configuration and tweaking to get | |
| 145 | 141 | right. Even when I was able to set up neomutt, configure my email |
| 146 | 142 | account, and customize a few personal preferences, a lot of emails still |
| 147 | 143 | do not display correctly (mostly due to HTML and images). |
| 148 | 144 | |
| 149 | I won't get into the details of configuring `neomutt`; I | |
| 150 | mostly followed this blog post: [Email in the Terminal: Configuring | |
| 151 | Neomutt](https://gideonwolfe.com/posts/workflow/neomutt/intro/). | |
| 145 | I won't get into the details of configuring =neomutt=; I mostly followed | |
| 146 | this blog post: | |
| 147 | [[https://gideonwolfe.com/posts/workflow/neomutt/intro/][Email in the | |
| 148 | Terminal: Configuring Neomutt]]. | |
| 152 | 149 | |
| 153 | 150 | Finally, I have yet to figure out how to connect my GPG keys to |
| 154 | `neomutt`, but that's a problem for another day. | |
| 155 | ||
| 156 | ### RSS Feed Reader | |
| 151 | =neomutt=, but that's a problem for another day. | |
| 157 | 152 | |
| 158 | I have just started using [Newsboat](https://newsboat.org/) to read | |
| 153 | ** RSS Feed Reader | |
| 154 | I have just started using [[https://newsboat.org/][Newsboat]] to read | |
| 159 | 155 | articles in my terminal and have found quick success with it. |
| 160 | 156 | |
| 161 | 157 | I'll show you a quick screenshot first: |
| 162 | 158 | |
| 163 |  | |
| 159 | #+caption: Newsboat | |
| 160 | [[https://img.cleberg.net/blog/20220616-terminal-lifestyle/newsboat.png]] | |
| 164 | 161 | |
| 165 | 162 | The configuration was super easy for this app; I simply installed the |
| 166 | 163 | app, created a file for URLs, and imported my OPML subscriptions that I |
| 167 | 164 | had exported out of my old feed reader: |
| 168 | 165 | |
| 169 | ```sh | |
| 166 | #+begin_src sh | |
| 170 | 167 | brew install newsboat |
| 171 | ``` | |
| 168 | #+end_src | |
| 172 | 169 | |
| 173 | ```sh | |
| 170 | #+begin_src sh | |
| 174 | 171 | touch ~/.newsboat/urls |
| 175 | ``` | |
| 172 | #+end_src | |
| 176 | 173 | |
| 177 | ```sh | |
| 174 | #+begin_src sh | |
| 178 | 175 | newsboat -i=my_subscriptions.opml |
| 179 | ``` | |
| 180 | ||
| 181 | ### Writing & Programming | |
| 176 | #+end_src | |
| 182 | 177 | |
| 178 | ** Writing & Programming | |
| 183 | 179 | Unfortunately, the weak link in my terminal-based environment right now |
| 184 | 180 | is my grasp of the possibilities of editing files within a shell. |
| 185 | 181 | |
| 186 | 182 | I am used to the easy extensions found in VSCodium and Kate, so I am |
| 187 | 183 | slowly learning how to mold the default editing tools to my needs. |
| 188 | Currently, this means I am using `nano` with the following | |
| 184 | Currently, this means I am using =nano= with the following | |
| 189 | 185 | configuration: |
| 190 | 186 | |
| 191 | ```config | |
| 187 | #+begin_src config | |
| 192 | 188 | set breaklonglines |
| 193 | 189 | set autoindent |
| 194 | 190 | set linenumbers |
| 195 | 191 | set tabstospaces |
| 196 | 192 | set tabsize 2 |
| 197 | 193 | set fill 80 |
| 198 | ``` | |
| 194 | #+end_src | |
| 199 | 195 | |
| 200 | 196 | This configuration allows nano to automatically hard-wrap lines at 80 |
| 201 | 197 | characters, autoindent the wrapped lines (if the previous line was |
| 202 | 198 | indented), use 2 spaces per tab, and display line numbers within each |
| 203 | 199 | file I open. |
| 204 | 200 | |
| 205 | I am currently looking to see if `vim` or `emacs` | |
| 206 | would be more useful for my current needs, but I'm not in any rush, so | |
| 207 | I don't expect to find an answer anytime soon. | |
| 201 | I am currently looking to see if =vim= or =emacs= would be more useful | |
| 202 | for my current needs, but I'm not in any rush, so I don't expect to find | |
| 203 | an answer anytime soon. | |
| 208 | 204 | |
| 209 | 205 | With my current life demands, I am not programming at the moment and |
| 210 | 206 | have not explored the best terminal set-up for programming. However, I |
| 211 | have seen many peers find success configuring `vim` and | |
| 212 | `emacs`, so that's where I will start when I pick my | |
| 213 | projects back up. | |
| 207 | have seen many peers find success configuring =vim= and =emacs=, so | |
| 208 | that's where I will start when I pick my projects back up. | |
| 214 | 209 | |
| 215 |  | |
| 210 | #+caption: nano | |
| 211 | [[https://img.cleberg.net/blog/20220616-terminal-lifestyle/nano.png]] | |
blog/the-ansoff-matrix/index.org added +140
| @@ -0,0 +1,140 @@ | ||
| 1 | #+title: The Ansoff Matrix | |
| 2 | #+date: 2019-12-03 | |
| 3 | #+description: Learn about the Ansoff Matrix, a strategic management tool. | |
| 4 | #+filetags: :business: | |
| 5 | ||
| 6 | * Overview | |
| 7 | As the world of business evolves, managers must approach business | |
| 8 | planning and strategy with a contemporary mindset. According to Dess, | |
| 9 | McNamara, Eisner, and Lee, managers must be willing to adapt to the | |
| 10 | modern business environment by going beyond "'incremental management', | |
| 11 | whereby they view their job as making a series of small, minor changes | |
| 12 | to improve the efficiency of the firm's operations"[fn:1]. | |
| 13 | ||
| 14 | One reason that strategic management is crucial is because most | |
| 15 | businesses that fail in the United States each year fail due to a lack | |
| 16 | of strategic focus or direction[fn:2]. The rate of failure for | |
| 17 | businesses with poor strategies shows that strategic planning and | |
| 18 | management are crucial to a business's strength and longevity, injecting | |
| 19 | the critical factors of growth and direction into a company's business | |
| 20 | plan. | |
| 21 | ||
| 22 | One of the most significant strategic planning and management frameworks | |
| 23 | that companies can use is the | |
| 24 | [[https://en.wikipedia.org/wiki/Ansoff_matrix][Ansoff Matrix]]. While | |
| 25 | this framework has unique purposes and use-cases, it can effectively | |
| 26 | help an organization grow and compete. Specifically, the Ansoff matrix | |
| 27 | is one of the most effective frameworks for companies who want to focus | |
| 28 | on increasing sales revenue or profitability[fn:3]. | |
| 29 | ||
| 30 | This framework uses a two-by-two figure to show the four strategic | |
| 31 | options for companies to use in this framework: market penetration, | |
| 32 | market development, product development, and diversification (see | |
| 33 | *Figure 1*). The x-axis of the matrix focuses on the firm's markets and | |
| 34 | also determines if the firm is looking to enter new markets or innovate | |
| 35 | in its current markets. The y-axis of the matrix focuses on the firm's | |
| 36 | products and determines if the firm wants to pursue strategies around | |
| 37 | their existing products or explore new products. | |
| 38 | ||
| 39 | #+caption: The Ansoff Matrix by JaisonAbeySabu, Own work, CC BY-SA 3.0 | |
| 40 | [[https://img.cleberg.net/blog/20191203-the-ansoff-matrix/ansoff_matrix-min.png]] | |
| 41 | ||
| 42 | * Strategic Options | |
| 43 | ** Market Penetration | |
| 44 | The most straightforward strategy in the Ansoff matrix is to focus on | |
| 45 | existing products in existing markets, also known as market | |
| 46 | penetration[fn:4]. Companies such as Coca-Cola have used market | |
| 47 | penetration successfully by investing a lot of money to get further | |
| 48 | value out of their current markets. Coca-Cola does this by introducing | |
| 49 | new features such as Christmas-themed bottles, personal names on the | |
| 50 | bottles, and other marketing schemes. | |
| 51 | ||
| 52 | ** Market Development | |
| 53 | Market development extends existing products into new markets in an | |
| 54 | attempt to increase the number of buyers. One interesting way that | |
| 55 | Coca-Cola used this strategy comes from the stigma that Diet Coke is a | |
| 56 | woman's drink[fn:5]. Coca-Cola introduced Coca-Cola Zero, which | |
| 57 | contained the same nutritional content as Diet Coke, but was packaged in | |
| 58 | a dark black can to appear more "manly"[fn:6]. | |
| 59 | ||
| 60 | ** Product Development | |
| 61 | Product development uses existing markets to introduce new products so | |
| 62 | that the firm can better meet customer needs[fn:7]. The extreme end of | |
| 63 | diversification is home to companies such as Johnson & Johnson, a | |
| 64 | healthcare company that has developed a business portfolio of more than | |
| 65 | 60,000 different products[fn:8]. Johnson & Johnson's dedication to | |
| 66 | continuous diversification has led them to a balance sheet rating of | |
| 67 | "AAA", industry recognition for diversification, and increases in their | |
| 68 | investor dividends for 57 consecutive years[fn:9]. | |
| 69 | ||
| 70 | ** Related Diversification | |
| 71 | Diversification, the final strategy of the Ansoff Matrix, is more | |
| 72 | difficult than the others since it involves exploring both new markets | |
| 73 | and new products. Related diversification is a diversification strategy | |
| 74 | that closely relates to the firm's core business. Coca-Cola's best | |
| 75 | example of related diversification is its acquisition of Glaceau and | |
| 76 | Vitamin Water, which expanded their drinking lines of business[fn:10]. | |
| 77 | ||
| 78 | ** Unrelated Diversification | |
| 79 | Unrelated diversification is a diversification strategy that does not | |
| 80 | really relate to the firm's core business but still diversifies their | |
| 81 | business portfolio. A good example of this would be a coffee company who | |
| 82 | has decided to enter the market for bicycle sales. The main purpose of | |
| 83 | this strategy is to an extremely diverse company that will not go | |
| 84 | bankrupt if one market goes through difficult times. However, this | |
| 85 | requires a lot of independent skills and heavy investments since the | |
| 86 | company most likely cannot easily transfer knowledge between the markets | |
| 87 | they compete in. | |
| 88 | ||
| 89 | * Requirements for Success | |
| 90 | To use the Ansoff Matrix framework, managers need to formulate corporate | |
| 91 | goals and objectives. Without goals and direction, management frameworks | |
| 92 | do not present much practical utility. Further, the Ansoff Matrix | |
| 93 | requires the managers involved to make tactical decisions and create a | |
| 94 | path for the company to take toward their goals. Lastly, both the Ansoff | |
| 95 | Matrix needs to consider both internal and external perspectives | |
| 96 | throughout the strategy formulation process. | |
| 97 | ||
| 98 | One interesting probability is that companies will be using multiple | |
| 99 | strategic planning and management frameworks at the same time. While | |
| 100 | this may sound like it could crowd the management process, there are | |
| 101 | numerous reasons to do so. For example, the Ansoff Matrix and the | |
| 102 | Balanced Scorecard are relatively popular, and they cover entirely | |
| 103 | different parts of a company's strategy. Using the results from the | |
| 104 | Balanced Scorecard could inform a company of the potential product and | |
| 105 | market demands, such as from customer or supplier survey results, to | |
| 106 | help the company determine which Ansoff Matrix strategy to pursue. | |
| 107 | However, a combined approach at this level would require mature | |
| 108 | frameworks and focused managers who are able to strategize at a high | |
| 109 | level. | |
| 110 | ||
| 111 | Lastly, it should be noted that the author of the Ansoff matrix, Igor | |
| 112 | Ansoff, often used the term | |
| 113 | [[https://en.wikipedia.org/wiki/Analysis_paralysis][paralysis by | |
| 114 | analysis]] to explain the mistake of companies who overuse analysis and | |
| 115 | spend too much time planning. Companies need to understand the utility | |
| 116 | of a strategic management framework while ensuring that the company is | |
| 117 | poised to execute as efficiently as they have planned. | |
| 118 | ||
| 119 | * Footnotes | |
| 120 | ||
| 121 | [fn:1] Dess, G. G., McNamara, G., Eisner, A. B., Lee, S. H. (2019). Strategic management: Text & cases, ninth edition. New York, NY: McGraw-Hill Education. | |
| 122 | ||
| 123 | [fn:2] Juneja, P. (n.d.). Benefits of strategic management. Management Study Guide. Retrieved from [[https://www.managementstudyguide.com/strategic-management-benefits.htm]]. | |
| 124 | ||
| 125 | [fn:3] Meldrum M., McDonald M. (1995) The Ansoff matrix. In: Key Marketing Concepts. London: Palgrave. | |
| 126 | ||
| 127 | [fn:4] Meldrum M., McDonald M. (1995) The Ansoff matrix. In: Key Marketing Concepts. London: Palgrave. | |
| 128 | ||
| 129 | [fn:5] Oakley, T. (2015). Coca-Cola: The Ansoff matrix. The Marketing Agenda. Retrieved from [[https://themarketingagenda.com/2015/03/28/coca-cola-ansoff-matrix/]]. | |
| 130 | ||
| 131 | [fn:6] Oakley, T. (2015). Coca-Cola: The Ansoff matrix. The Marketing Agenda. Retrieved from [[https://themarketingagenda.com/2015/03/28/coca-cola-ansoff-matrix/]]. | |
| 132 | ||
| 133 | [fn:7] Oakley, T. (2015). Coca-Cola: The Ansoff matrix. The Marketing Agenda. Retrieved from [[https://themarketingagenda.com/2015/03/28/coca-cola-ansoff-matrix/]]. | |
| 134 | ||
| 135 | [fn:8] Lemke, T. (2019). The most diversified companies in the stock market. The balance. Retrieved from [[https://www.thebalance.com/the-most-diversified-companies-in-the-stock-market-4169730]]. | |
| 136 | ||
| 137 | [fn:9] Johnson & Johnson. (2018). 2018 Investor Fact Sheet. [PDF file]. Retrieved from [[http://www.investor.jnj.com/_document/2018-investor-fact-sheet-4-19'id=0000016a-5681-d475-a17f-d78db54a0000][http://www.investor.jnj.com/_document/2018-investor-fact-sheet-4-19'id=0000016a-5681-d475-a17f-d78db54a0000]]. | |
| 138 | ||
| 139 | [fn:10] Oakley, T. (2015). Coca-Cola: The Ansoff matrix. The Marketing Agenda. Retrieved from [[https://themarketingagenda.com/2015/03/28/coca-cola-ansoff-matrix/]]. | |
| 140 | ||
blog/tuesday/index.org added +37
| @@ -0,0 +1,37 @@ | ||
| 1 | #+title: Tuesday | |
| 2 | #+date: 2022-02-22 | |
| 3 | #+description: 2-22-22 || 22-2-22 | |
| 4 | #+filetags: :personal: | |
| 5 | ||
| 6 | * Tuesday, Twosday | |
| 7 | I'm taking a break from my usual technology-related posts and writing | |
| 8 | about something a little more enjoyable today. | |
| 9 | ||
| 10 | Today is Tuesday, February 22nd, 2022. Today is 02-22-2022. Today is | |
| 11 | Twosday. | |
| 12 | ||
| 13 | Let's look at everything that fell in place today: | |
| 14 | ||
| 15 | 1. Written in the =m-dd-yy= or =dd-m-yy= formats, today is 2-22-22 or | |
| 16 | 22-2-22, which is a neat little palindrome in either format. (The | |
| 17 | last ubiquitous six-digit palindrome was 1-11-11.) | |
| 18 | 2. Today is Tuesday, which is why everyone is using the nickname Twosday | |
| 19 | to call out these similarities. | |
| 20 | 3. Falling on Tuesday means today is the 2nd day of the week (for most | |
| 21 | cultures. For the US, it's the 3rd day of the week since we start on | |
| 22 | Sunday). | |
| 23 | 4. The only culture I could find with a connection to a =2= is that some | |
| 24 | Slavic languages derived their version of Tuesday from the Old Church | |
| 25 | Slavonic word =въторъ=, meaning "the second." | |
| 26 | 5. Written in the classic monospaced, digital font (think of digital | |
| 27 | clocks from the 80s/90s), there is nice symmetry to the numbers | |
| 28 | ([[https://img.cleberg.net/blog/20220222-tuesday/digital_font.png][view | |
| 29 | the image here]]!). | |
| 30 | 6. This one isn't naturally-occurring, but it seems people around the | |
| 31 | world are celebrating the day. For example, a group is putting | |
| 32 | together | |
| 33 | [[[[https://www.eventbrite.com/e/2-22-22-a-collective-wedding-ceremony-at-the-state-capitol-tickets-211434605597]]][a | |
| 34 | wedding of 222 couples at the California State Capitol in | |
| 35 | Sacramento]], concluding at exactly 2:22 PM. These couples will | |
| 36 | record their marriage dates as 2-22-22 2:22 PM. Tickets were on sale | |
| 37 | for $222.22. | |
blog/ubuntu-emergency-mode/index.org added +69
| @@ -0,0 +1,69 @@ | ||
| 1 | #+title: Stuck in Ubuntu's Emergency Mode? Try Fixing the Fstab File | |
| 2 | #+date: 2024-02-13 | |
| 3 | #+description: Learn how to fix a missing disk issue that can lock you in Ubuntu's emergency mode. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * The Problem | |
| 7 | I recently [[../zfs/][migrated my hard drives to a ZFS pool]] and | |
| 8 | found myself stuck in Ubuntu's emergency mode after the first reboot I | |
| 9 | performed after creating the ZFS pool. | |
| 10 | ||
| 11 | My server was stuck in the boot process and showed the following error | |
| 12 | on the screen: | |
| 13 | ||
| 14 | #+begin_src txt | |
| 15 | You are in emergency mode. | |
| 16 | After logging in, type "journalctl -xb" to view system logs, | |
| 17 | "systemctl reboot" to reboot, "systemctl default" | |
| 18 | or ^D to try again to boot into default mode". | |
| 19 | #+end_src | |
| 20 | ||
| 21 | After rebooting the server and watching the logs scroll on a monitor, I | |
| 22 | noticed the root cause was related to a very long search for certain | |
| 23 | drives. I kept seeing errors like this: | |
| 24 | ||
| 25 | #+begin_src txt | |
| 26 | [ TIME ] Timed out waiting of device dev-disk-by/[disk-uuid] | |
| 27 | #+end_src | |
| 28 | ||
| 29 | I realized that I had not removed the =/etc/fstab= references that asked | |
| 30 | Ubuntu to mount two disks on boot, but I had recently changed those | |
| 31 | disks to be part of my ZFS pool instead. Therefore, Ubuntu was trying to | |
| 32 | identify and mount a disk that was not available. | |
| 33 | ||
| 34 | Now that we have an idea of the issue, let's move to solution. | |
| 35 | ||
| 36 | * The Solution | |
| 37 | In order to fix the issue, I waited until I was allowed to type the root | |
| 38 | user's password, and then I executed the following command: | |
| 39 | ||
| 40 | #+begin_src sh | |
| 41 | nano /etc/fstab | |
| 42 | #+end_src | |
| 43 | ||
| 44 | Within the =fstab= file, I needed to comment/remove the following lines | |
| 45 | at the bottom of the file. You can comment-out a line by prepending a | |
| 46 | =#= symbol at the beginning of the line. You can also delete the line | |
| 47 | entirely. | |
| 48 | ||
| 49 | #+begin_src conf | |
| 50 | # What it looked like when running into the issue: | |
| 51 | UUID=B64E53824E5339F7 /mnt/white-01 ntfs-3g uid=1000,gid=1000 0 0 | |
| 52 | UUID=E69867E59867B32B /mnt/white-02 ntfs-3g uid=1000,gid=1000 0 0 | |
| 53 | ||
| 54 | # What I changed it to, in order to fix the issue: | |
| 55 | # UUID=B64E53824E5339F7 /mnt/white-01 ntfs-3g uid=1000,gid=1000 0 0 | |
| 56 | # UUID=E69867E59867B32B /mnt/white-02 ntfs-3g uid=1000,gid=1000 0 0 | |
| 57 | #+end_src | |
| 58 | ||
| 59 | Once removing the lines above from the =/etc/fstab= file, save and exit | |
| 60 | the file by hitting the =Ctrl= + =x= key combo. | |
| 61 | ||
| 62 | You can now hit =Ctrl= + =D= to continue, or reboot: | |
| 63 | ||
| 64 | #+begin_src sh | |
| 65 | systemctl reboot | |
| 66 | #+end_src | |
| 67 | ||
| 68 | Once rebooted, I was able to watch the machine boot properly and launch | |
| 69 | to the TTY login screen without errors! | |
content/blog/2021-01-07-ufw.md → blog/ufw/index.org renamed +76 −86
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-01-07 | |
| 3 | title = "Secure Your Network with the Uncomplicated Firewall" | |
| 4 | description = "A simple guide to the UFW." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Uncomplicated Firewall | |
| 1 | #+title: Secure Your Network with the Uncomplicated Firewall (ufw) | |
| 2 | #+date: 2021-01-07 | |
| 3 | #+description: A simple guide to the UFW. | |
| 4 | #+filetags: :sysadmin: | |
| 8 | 5 | |
| 6 | * Uncomplicated Firewall | |
| 9 | 7 | Uncomplicated Firewall, also known as ufw, is a convenient and |
| 10 | 8 | beginner-friendly way to enforce OS-level firewall rules. For those who |
| 11 | 9 | are hosting servers or any device that is accessible to the world (i.e., |
| @@ -15,147 +13,140 @@ implemented and active. | ||
| 15 | 13 | Ufw is available by default in all Ubuntu installations after 8.04 LTS. |
| 16 | 14 | For other distributions, you can look to install ufw or check if there |
| 17 | 15 | are alternative firewalls installed already. There are usually |
| 18 | alternatives available, such as Fedora's `firewall` and the | |
| 19 | package available on most distributions: `iptables`. Ufw is | |
| 20 | considered a beginner-friendly front-end to iptables. | |
| 16 | alternatives available, such as Fedora's =firewall= and the package | |
| 17 | available on most distributions: =iptables=. Ufw is considered a | |
| 18 | beginner-friendly front-end to iptables. | |
| 21 | 19 | |
| 22 | [Gufw](https://gufw.org) is available as a graphical user interface | |
| 20 | [[https://gufw.org][Gufw]] is available as a graphical user interface | |
| 23 | 21 | (GUI) application for users who are uncomfortable setting up a firewall |
| 24 | 22 | through a terminal. |
| 25 | 23 | |
| 26 |  | |
| 27 | ||
| 28 | ## Getting Help | |
| 24 | #+caption: Gufw Screenshot | |
| 25 | [[https://img.cleberg.net/blog/20210107-secure-your-network-with-the-uncomplicated-firewall/gufw.png]] | |
| 29 | 26 | |
| 27 | * Getting Help | |
| 30 | 28 | If you need help figuring out commands, remember that you can run the |
| 31 | `--help` flag to get a list of options. | |
| 29 | =--help= flag to get a list of options. | |
| 32 | 30 | |
| 33 | ```sh | |
| 31 | #+begin_src sh | |
| 34 | 32 | sudo ufw --help |
| 35 | ``` | |
| 36 | ||
| 37 | ## Set Default State | |
| 33 | #+end_src | |
| 38 | 34 | |
| 35 | * Set Default State | |
| 39 | 36 | The proper way to run a firewall is to set a strict default state and |
| 40 | 37 | slowly open up ports that you want to allow. This helps prevent anything |
| 41 | 38 | malicious from slipping through the cracks. The following command |
| 42 | 39 | prevents all incoming traffic (other than the rules we specify later), |
| 43 | 40 | but you can also set this for outgoing connections, if necessary. |
| 44 | 41 | |
| 45 | ```sh | |
| 42 | #+begin_src sh | |
| 46 | 43 | sudo ufw default deny incoming |
| 47 | ``` | |
| 44 | #+end_src | |
| 48 | 45 | |
| 49 | 46 | You should also allow outgoing traffic if you want to allow the device |
| 50 | 47 | to communicate back to you or other parties. For example, media servers |
| 51 | 48 | like Plex need to be able to send out data related to streaming the |
| 52 | 49 | media. |
| 53 | 50 | |
| 54 | ```sh | |
| 51 | #+begin_src sh | |
| 55 | 52 | sudo ufw default allow outgoing |
| 56 | ``` | |
| 53 | #+end_src | |
| 57 | 54 | |
| 58 | ## Adding Port Rules | |
| 55 | * Adding Port Rules | |
| 56 | Now that we've disabled all incoming traffic by default, we need to open | |
| 57 | up some ports (or else no traffic would be able to come in). If you need | |
| 58 | to be able to =ssh= into the machine, you'll need to open up port 22. | |
| 59 | 59 | |
| 60 | Now that we've disabled all incoming traffic by default, we need to | |
| 61 | open up some ports (or else no traffic would be able to come in). If you | |
| 62 | need to be able to `ssh` into the machine, you'll need to | |
| 63 | open up port 22. | |
| 64 | ||
| 65 | ```sh | |
| 60 | #+begin_src sh | |
| 66 | 61 | sudo ufw allow 22 |
| 67 | ``` | |
| 62 | #+end_src | |
| 68 | 63 | |
| 69 | 64 | You can also issue more restrictive rules. The following rule will allow |
| 70 | `ssh` connections only from machines on the local subnet. | |
| 65 | =ssh= connections only from machines on the local subnet. | |
| 71 | 66 | |
| 72 | ```sh | |
| 67 | #+begin_src sh | |
| 73 | 68 | sudo ufw allow proto tcp from 192.168.0.0/24 to any port 22 |
| 74 | ``` | |
| 69 | #+end_src | |
| 75 | 70 | |
| 76 | 71 | If you need to set a rule that isn't tcp, just append your connection |
| 77 | 72 | type to the end of the rule. |
| 78 | 73 | |
| 79 | ```sh | |
| 74 | #+begin_src sh | |
| 80 | 75 | sudo ufw allow 1900/udp |
| 81 | ``` | |
| 82 | ||
| 83 | ## Enable ufw | |
| 76 | #+end_src | |
| 84 | 77 | |
| 78 | * Enable ufw | |
| 85 | 79 | Now that the firewall is configured and ready to go, you can enable the |
| 86 | 80 | firewall. |
| 87 | 81 | |
| 88 | ```sh | |
| 82 | #+begin_src sh | |
| 89 | 83 | sudo ufw enable |
| 90 | ``` | |
| 84 | #+end_src | |
| 91 | 85 | |
| 92 | 86 | A restart may be required for the firewall to begin operating. |
| 93 | 87 | |
| 94 | ```sh | |
| 88 | #+begin_src sh | |
| 95 | 89 | sudo reboot now |
| 96 | ``` | |
| 97 | ||
| 98 | ## Checking Status | |
| 90 | #+end_src | |
| 99 | 91 | |
| 92 | * Checking Status | |
| 100 | 93 | Now that the firewall is enabled, let's check and see what the rules |
| 101 | 94 | look like. |
| 102 | 95 | |
| 103 | ```sh | |
| 96 | #+begin_src sh | |
| 104 | 97 | sudo ufw status numbered |
| 105 | ``` | |
| 98 | #+end_src | |
| 106 | 99 | |
| 107 | ```txt | |
| 100 | #+begin_src txt | |
| 108 | 101 | Status: active |
| 109 | 102 | |
| 110 | 103 | To Action From |
| 111 | 104 | -- ------ ---- |
| 112 | 105 | [ 1] 22 ALLOW IN Anywhere |
| 113 | 106 | [ 2] 22 (v6) ALLOW IN Anywhere (v6) |
| 114 | ``` | |
| 115 | ||
| 116 | ## Deleting Rules | |
| 107 | #+end_src | |
| 117 | 108 | |
| 109 | * Deleting Rules | |
| 118 | 110 | If you need to delete a rule, you need to know the number associated |
| 119 | 111 | with that rule. Let's delete the first rule in the table above. You'll |
| 120 | 112 | be asked to confirm the deletion as part of this process. |
| 121 | 113 | |
| 122 | ```sh | |
| 114 | #+begin_src sh | |
| 123 | 115 | sudo ufw delete 1 |
| 124 | ``` | |
| 125 | ||
| 126 | ## Managing App Rules | |
| 116 | #+end_src | |
| 127 | 117 | |
| 118 | * Managing App Rules | |
| 128 | 119 | Luckily, there's a convenient way for installed applications to create |
| 129 | files that ufw can easily implement so that you don't have to search | |
| 130 | and find which ports your application requires. To see if your device | |
| 131 | has any applications with pre-installed ufw rules, execute the following | |
| 120 | files that ufw can easily implement so that you don't have to search and | |
| 121 | find which ports your application requires. To see if your device has | |
| 122 | any applications with pre-installed ufw rules, execute the following | |
| 132 | 123 | command: |
| 133 | 124 | |
| 134 | ```sh | |
| 125 | #+begin_src sh | |
| 135 | 126 | sudo ufw app list |
| 136 | ``` | |
| 127 | #+end_src | |
| 137 | 128 | |
| 138 | 129 | The results should look something like this: |
| 139 | 130 | |
| 140 | ```txt | |
| 131 | #+begin_src txt | |
| 141 | 132 | Available applications: |
| 142 | 133 | OpenSSH |
| 143 | 134 | Samba |
| 144 | 135 | plexmediaserver |
| 145 | 136 | plexmediaserver-all |
| 146 | 137 | plexmediaserver-dlna |
| 147 | ``` | |
| 138 | #+end_src | |
| 148 | 139 | |
| 149 | 140 | If you want to get more information on a specific app rule, use the |
| 150 | `info` command. | |
| 141 | =info= command. | |
| 151 | 142 | |
| 152 | ```sh | |
| 143 | #+begin_src sh | |
| 153 | 144 | sudo ufw app info plexmediaserver-dlna |
| 154 | ``` | |
| 145 | #+end_src | |
| 155 | 146 | |
| 156 | 147 | You'll get a blurb of info back like this: |
| 157 | 148 | |
| 158 | ```txt | |
| 149 | #+begin_src txt | |
| 159 | 150 | Profile: plexmediaserver-dlna |
| 160 | 151 | Title: Plex Media Server (DLNA) |
| 161 | 152 | Description: The Plex Media Server (additional DLNA capability only) |
| @@ -163,29 +154,28 @@ Description: The Plex Media Server (additional DLNA capability only) | ||
| 163 | 154 | Ports: |
| 164 | 155 | 1900/udp |
| 165 | 156 | 32469/tcp |
| 166 | ``` | |
| 157 | #+end_src | |
| 167 | 158 | |
| 168 | 159 | You can add or delete app rules the same way that you'd add or delete |
| 169 | 160 | specific port rules. |
| 170 | 161 | |
| 171 | ```sh | |
| 162 | #+begin_src sh | |
| 172 | 163 | sudo ufw allow plexmediaserver-dlna |
| 173 | ``` | |
| 164 | #+end_src | |
| 174 | 165 | |
| 175 | ```sh | |
| 166 | #+begin_src sh | |
| 176 | 167 | sudo ufw delete RULE|NUM |
| 177 | ``` | |
| 178 | ||
| 179 | ## Creating App Rules | |
| 168 | #+end_src | |
| 180 | 169 | |
| 170 | * Creating App Rules | |
| 181 | 171 | If you'd like to create you own app rule, you'll need to create a file |
| 182 | in the `/etc/ufw/applications.d` directory. Within the file | |
| 183 | you create, you need to make sure the content is properly formatted. | |
| 172 | in the =/etc/ufw/applications.d= directory. Within the file you create, | |
| 173 | you need to make sure the content is properly formatted. | |
| 184 | 174 | |
| 185 | For example, here are the contents my `plexmediaserver` file, | |
| 186 | which creates three distinct app rules for ufw: | |
| 175 | For example, here are the contents my =plexmediaserver= file, which | |
| 176 | creates three distinct app rules for ufw: | |
| 187 | 177 | |
| 188 | ```config | |
| 178 | #+begin_src config | |
| 189 | 179 | [plexmediaserver] |
| 190 | 180 | title=Plex Media Server (Standard) |
| 191 | 181 | description=The Plex Media Server |
| @@ -200,24 +190,24 @@ ports=1900/udp|32469/tcp | ||
| 200 | 190 | title=Plex Media Server (Standard + DLNA) |
| 201 | 191 | description=The Plex Media Server (with additional DLNA capability) |
| 202 | 192 | ports=32400/tcp|3005/tcp|5353/udp|8324/tcp|32410:32414/udp|1900/udp|32469/tcp |
| 203 | ``` | |
| 193 | #+end_src | |
| 204 | 194 | |
| 205 | So, if I wanted to create a custom app rule called "mycustomrule," | |
| 206 | I'd create a file and add my content like this: | |
| 195 | So, if I wanted to create a custom app rule called "mycustomrule," I'd | |
| 196 | create a file and add my content like this: | |
| 207 | 197 | |
| 208 | ```sh | |
| 198 | #+begin_src sh | |
| 209 | 199 | sudo nano /etc/ufw/applications.d/mycustomrule |
| 210 | ``` | |
| 200 | #+end_src | |
| 211 | 201 | |
| 212 | ```config | |
| 202 | #+begin_src config | |
| 213 | 203 | [mycustomrule] |
| 214 | 204 | title=My Custom Rule |
| 215 | 205 | description=This is a temporary ufw app rule. |
| 216 | 206 | ports=88/tcp|9100/udp |
| 217 | ``` | |
| 207 | #+end_src | |
| 218 | 208 | |
| 219 | 209 | Then, I would just enable this rule in ufw. |
| 220 | 210 | |
| 221 | ```sh | |
| 211 | #+begin_src sh | |
| 222 | 212 | sudo ufw allow mycustomrule |
| 223 | ``` | |
| 213 | #+end_src | |
blog/unifi-ip-blocklist/index.org added +82
| @@ -0,0 +1,82 @@ | ||
| 1 | #+title: Block IP Addresses and Subnets with Unifi Network Firewall | |
| 2 | #+date: 2023-06-18 | |
| 3 | #+description: Learn how to use the Unifi Network Firewall to block IP addresses and subnets. | |
| 4 | #+filetags: :network: | |
| 5 | ||
| 6 | * Identifying Abusive IPs | |
| 7 | If you're like me and use Unifi network equipment at the edge of the | |
| 8 | network you manage, you may know that Unifi is only somewhat decent at | |
| 9 | identifying and blocking IPs that represent abusive or threat actors. | |
| 10 | ||
| 11 | While Unifi has a | |
| 12 | [[https://help.ui.com/hc/en-us/articles/360006893234-UniFi-Gateway-Threat-Management][threat | |
| 13 | management]] tool inside their Network application, it can be lacking in | |
| 14 | functionality and identification. For example, I have my UDM Pro set to | |
| 15 | identify and block almost all categories of threats available within the | |
| 16 | Unifi settings. However, I regularly identify abusive actors on my web | |
| 17 | server via the server logs. | |
| 18 | ||
| 19 | In addition, I have identified IP addresses and subnets directly within | |
| 20 | Unifi's logs that the UDM did not block for whatever reason. | |
| 21 | ||
| 22 | This guide is meant to be another step in the process to manually block | |
| 23 | abusive IP addresses or subnets that you have identified but are not | |
| 24 | being automatically blocked yet. | |
| 25 | ||
| 26 | * Create an IP Group Profile | |
| 27 | To start, login to the Unifi machine's web GUI and navigate to the | |
| 28 | Network app > Settings > Profiles. | |
| 29 | ||
| 30 | Within this page, choose the =IP Groups= tab and click =Create New=. | |
| 31 | ||
| 32 | #+caption: Network Profiles | |
| 33 | [[https://img.cleberg.net/blog/20230618-unifi-ip-blocklist/unifi_profiles.png]] | |
| 34 | ||
| 35 | Each IP Group profile can be used as one of three options: | |
| 36 | ||
| 37 | 1. Port Group | |
| 38 | 2. IPv4 Address/Subnet | |
| 39 | 3. IPv6 Address/Subnet | |
| 40 | ||
| 41 | In this example, I'm creating an IPv4 Address/Subnet group and adding a | |
| 42 | few different IP addresses and a subnet. Once you've added all IP | |
| 43 | addresses and subnets, click the =Apply= button that should appear at | |
| 44 | the bottom. | |
| 45 | ||
| 46 | #+caption: Network Profile IPs | |
| 47 | [[https://img.cleberg.net/blog/20230618-unifi-ip-blocklist/abusive_ips.png]] | |
| 48 | ||
| 49 | At this point, the IPv4 Address/Subnet has been created but not yet | |
| 50 | used. | |
| 51 | ||
| 52 | * Drop IP Group Profile via the Unifi Firewall | |
| 53 | To instruct the Unifi machine to block the profile we just created, we | |
| 54 | need to navigate to the Network app > Settings > Firewall & Security. | |
| 55 | ||
| 56 | Within this screen, find the Firewall Rules table and click | |
| 57 | =Create Entry=. This entry should contain the following settings: | |
| 58 | ||
| 59 | - Type: =Internet In= | |
| 60 | - Description: =<Your Custom Rule>= | |
| 61 | - Rule Applied: =Before Predefined Rules= | |
| 62 | - Action: =Drop= | |
| 63 | - Source Type: =Port/IP Group= | |
| 64 | - IPv4 Address Group: =<Name of the Group Profile You Created Above>= | |
| 65 | ||
| 66 | Customize the remaining configurations to your liking, and then save and | |
| 67 | enable the firewall rule. | |
| 68 | ||
| 69 | #+caption: Firewall Rule | |
| 70 | [[https://img.cleberg.net/blog/20230618-unifi-ip-blocklist/firewall_drop_rule.png]] | |
| 71 | ||
| 72 | Once enabled, the Unifi machine will be able to drop all incoming | |
| 73 | connections from the defined IP addresses and subnets within the created | |
| 74 | profile. | |
| 75 | ||
| 76 | #+begin_quote | |
| 77 | As a personal aside to this topic, I'm looking for a convenient way to | |
| 78 | update the firewall rules or profiles remotely (within the LAN) from the | |
| 79 | web server to accelerate this process. If you have an idea on how to | |
| 80 | automatically update Unifi IP groups or firewall rules, let me know! | |
| 81 | ||
| 82 | #+end_quote | |
content/blog/2023-12-03-unifi-nextdns.md → blog/unifi-nextdns/index.org renamed +58 −68
| @@ -1,72 +1,64 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-12-03 | |
| 3 | title = "How to Install NextDNS on the Unifi Dream Machine" | |
| 4 | description = "A guide to properly install the NextDNS client on the UDM Pro." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Overview | |
| 1 | #+title: How to Install NextDNS on the Unifi Dream Machine | |
| 2 | #+date: 2023-12-03 | |
| 3 | #+description: A guide to properly install the NextDNS client on the UDM Pro. | |
| 4 | #+filetags: :network: | |
| 8 | 5 | |
| 6 | * Overview | |
| 9 | 7 | I recently installed NextDNS on my Unifi Dream Machine router using the |
| 10 | [UnifiOS](https://github.com/nextdns/nextdns/wiki/UnifiOS) wiki page on | |
| 11 | NextDNS's GitHub repository. | |
| 8 | [[https://github.com/nextdns/nextdns/wiki/UnifiOS][UnifiOS]] wiki page | |
| 9 | on NextDNS's GitHub repository. | |
| 12 | 10 | |
| 13 | 11 | As a result of this, I wanted to write down the process in case the wiki |
| 14 | 12 | or installer ever gets lost. |
| 15 | 13 | |
| 16 | # Wiki | |
| 17 | ||
| 14 | * Wiki | |
| 18 | 15 | The following is copied from the wiki page linked above, with one |
| 19 | difference in the `ssh` command. | |
| 16 | difference in the =ssh= command. | |
| 20 | 17 | |
| 21 | 18 | Install instructions for Unifi Dream Machine (UDM) standard and pro |
| 22 | 19 | routers. |
| 23 | 20 | |
| 24 | ## Install | |
| 25 | ||
| 21 | ** Install | |
| 26 | 22 | Enable SSH: |
| 27 | 23 | |
| 28 | - Go to your unifi admin interface and select your device (not the | |
| 29 | controller settings, but the Dream Machine settings) | |
| 30 | - Click on "Settings" at the bottom of the page | |
| 31 | - Go to the "Advanced" section on the left pan | |
| 32 | - Enable SSH | |
| 33 | - Set a SSH password | |
| 24 | - Go to your unifi admin interface and select your device (not the | |
| 25 | controller settings, but the Dream Machine settings) | |
| 26 | - Click on "Settings" at the bottom of the page | |
| 27 | - Go to the "Advanced" section on the left pan | |
| 28 | - Enable SSH | |
| 29 | - Set a SSH password | |
| 34 | 30 | |
| 35 | Connect to your router using `ssh root@xxx.xxx.xxx.xxx` with | |
| 36 | the password you configured. | |
| 31 | Connect to your router using =ssh root@xxx.xxx.xxx.xxx= with the | |
| 32 | password you configured. | |
| 37 | 33 | |
| 38 | 34 | Run the following command and follow the instructions: |
| 39 | 35 | |
| 40 | ```sh | |
| 36 | #+begin_src sh | |
| 41 | 37 | sh -c 'sh -c "$(curl -sL https://nextdns.io/install)"' |
| 42 | ``` | |
| 38 | #+end_src | |
| 43 | 39 | |
| 44 | 40 | Note: Queries from the UDM itself won't be routed to NextDNS nor |
| 45 | 41 | encrypted due to current system limitation. All traffic from other |
| 46 | 42 | devices on then network will. |
| 47 | 43 | |
| 48 | ## Upgrade | |
| 49 | ||
| 44 | ** Upgrade | |
| 50 | 45 | To upgrade to the last version, simply re-run the installer above. If a |
| 51 | 46 | new version is available, the upgrade action will added to the list of |
| 52 | 47 | possible actions. |
| 53 | 48 | |
| 54 | ## Uninstall | |
| 55 | ||
| 49 | ** Uninstall | |
| 56 | 50 | To uninstall, re-run the installer above and select "Remove" in the |
| 57 | 51 | menu. |
| 58 | 52 | |
| 59 | ## Troubleshooting | |
| 60 | ||
| 53 | ** Troubleshooting | |
| 61 | 54 | If the installation fail, please the installer in debug mode and contact |
| 62 | 55 | us at team@nextdns.io with the transcript of the installation: |
| 63 | 56 | |
| 64 | ```sh | |
| 57 | #+begin_src sh | |
| 65 | 58 | sh -c 'DEBUG=1 sh -c "$(curl -sL https://nextdns.io/install)"' |
| 66 | ``` | |
| 67 | ||
| 68 | ### Content Filtering Conflict | |
| 59 | #+end_src | |
| 69 | 60 | |
| 61 | *** Content Filtering Conflict | |
| 70 | 62 | NextDNS CLI and the UDM Content Filtering or the Ad Blocking features |
| 71 | 63 | are incompatible. If you want to use NextDNS CLI, please make sure they |
| 72 | 64 | are disabled. |
| @@ -77,28 +69,26 @@ network, set the Content Filtering feature to None | ||
| 77 | 69 | To disable Ad Blocking, go to Settings > Application Firewall. In the |
| 78 | 70 | General tab, uncheck the Ad Blocking checkbox. |
| 79 | 71 | |
| 80 | ### APT Error | |
| 81 | ||
| 72 | *** APT Error | |
| 82 | 73 | If you get an apt error as follow: |
| 83 | 74 | |
| 84 | ```sh | |
| 75 | #+begin_src sh | |
| 85 | 76 | E: Failed to fetch http://security.debian.org/dists/stretch/updates/main/binary-arm64/Packages 404 Not Found [IP: 151.101.70.132 80] |
| 86 | ``` | |
| 77 | #+end_src | |
| 87 | 78 | |
| 88 | 79 | You may try to following: |
| 89 | 80 | |
| 90 | ```sh | |
| 81 | #+begin_src sh | |
| 91 | 82 | sed -i -e 's/deb.debian.org/archive.debian.org/g' \ |
| 92 | 83 | -e 's|security.debian.org|archive.debian.org/|g' \ |
| 93 | 84 | -e '/stretch-updates/d' /etc/apt/sources.list |
| 94 | ``` | |
| 95 | ||
| 96 | # install.sh | |
| 85 | #+end_src | |
| 97 | 86 | |
| 98 | Here are the contents of the `install.sh` file used above, as | |
| 99 | of 2023-12-03: | |
| 87 | ** install.sh | |
| 88 | Here are the contents of the =install.sh= file used above, as of | |
| 89 | 2023-12-03: | |
| 100 | 90 | |
| 101 | ```sh | |
| 91 | #+begin_src sh | |
| 102 | 92 | #!/bin/sh |
| 103 | 93 | |
| 104 | 94 | main() { |
| @@ -323,13 +313,13 @@ install_bin() { | ||
| 323 | 313 | fi |
| 324 | 314 | log_debug "Installing $INSTALL_RELEASE binary for $GOOS/$GOARCH to $bin_path" |
| 325 | 315 | case "$INSTALL_RELEASE" in |
| 326 | */*) | |
| 316 | ,*/*) | |
| 327 | 317 | # Snapshot |
| 328 | 318 | branch=${INSTALL_RELEASE%/*} |
| 329 | 319 | hash=${INSTALL_RELEASE#*/} |
| 330 | 320 | url="https://snapshot.nextdns.io/${branch}/nextdns-${hash}_${GOOS}_${GOARCH}.tar.gz" |
| 331 | 321 | ;; |
| 332 | *) | |
| 322 | ,*) | |
| 333 | 323 | url="https://github.com/nextdns/nextdns/releases/download/v${INSTALL_RELEASE}/nextdns_${INSTALL_RELEASE}_${GOOS}_${GOARCH}.tar.gz" |
| 334 | 324 | ;; |
| 335 | 325 | esac |
| @@ -631,12 +621,12 @@ install_type() { | ||
| 631 | 621 | echo "$FORCE_INSTALL_TYPE"; return 0 |
| 632 | 622 | fi |
| 633 | 623 | case "$INSTALL_RELEASE" in |
| 634 | */*) | |
| 624 | ,*/*) | |
| 635 | 625 | case $OS in |
| 636 | 626 | ubios) |
| 637 | 627 | echo "ubios_snapshot"; return 0 |
| 638 | 628 | ;; |
| 639 | *) | |
| 629 | ,*) | |
| 640 | 630 | # Snapshot mode always use binary install |
| 641 | 631 | echo "bin"; return 0 |
| 642 | 632 | ;; |
| @@ -664,7 +654,7 @@ install_type() { | ||
| 664 | 654 | . /etc/os-release |
| 665 | 655 | major=$(echo "$VERSION_ID" | cut -d. -f1) |
| 666 | 656 | case $major in |
| 667 | *[!0-9]*) | |
| 657 | ,*[!0-9]*) | |
| 668 | 658 | if [ "$VERSION_ID" = "19.07.0-rc1" ]; then |
| 669 | 659 | # No opkg support before 19.07.0-rc2 |
| 670 | 660 | echo "bin" |
| @@ -673,7 +663,7 @@ install_type() { | ||
| 673 | 663 | echo "openwrt" |
| 674 | 664 | fi |
| 675 | 665 | ;; |
| 676 | *) | |
| 666 | ,*) | |
| 677 | 667 | if [ "$major" -lt 19 ]; then |
| 678 | 668 | # No opkg support before 19.07.0-rc2 |
| 679 | 669 | echo "bin" |
| @@ -719,7 +709,7 @@ install_type() { | ||
| 719 | 709 | # TODO: pkg for xbps |
| 720 | 710 | echo "bin" |
| 721 | 711 | ;; |
| 722 | *) | |
| 712 | ,*) | |
| 723 | 713 | log_error "Unsupported installation for $(detect_os)" |
| 724 | 714 | return 1 |
| 725 | 715 | ;; |
| @@ -871,7 +861,7 @@ ask_bool() { | ||
| 871 | 861 | false) |
| 872 | 862 | msg="$msg [y|N]: " |
| 873 | 863 | ;; |
| 874 | *) | |
| 864 | ,*) | |
| 875 | 865 | msg="$msg (y/n): " |
| 876 | 866 | esac |
| 877 | 867 | while true; do |
| @@ -889,7 +879,7 @@ ask_bool() { | ||
| 889 | 879 | echo "false" |
| 890 | 880 | return 0 |
| 891 | 881 | ;; |
| 892 | *) | |
| 882 | ,*) | |
| 893 | 883 | echo "Invalid input, use yes or no" |
| 894 | 884 | ;; |
| 895 | 885 | esac |
| @@ -901,12 +891,12 @@ detect_endiannes() { | ||
| 901 | 891 | # Some firmwares do not contain hexdump, for those, try to detect endianness |
| 902 | 892 | # differently. |
| 903 | 893 | case $(cat /proc/cpuinfo) in |
| 904 | *BCM5300*) | |
| 894 | ,*BCM5300*) | |
| 905 | 895 | # RT-AC66U does not support Merlin version over 380.70 which |
| 906 | 896 | # lacks hexdump command. |
| 907 | 897 | echo "le" |
| 908 | 898 | ;; |
| 909 | *) | |
| 899 | ,*) | |
| 910 | 900 | log_error "Cannot determine endianness" |
| 911 | 901 | return 1 |
| 912 | 902 | ;; |
| @@ -937,10 +927,10 @@ detect_goarch() { | ||
| 937 | 927 | arm) |
| 938 | 928 | # FreeBSD does not include arm version |
| 939 | 929 | case "$(sysctl -b hw.model 2>/dev/null)" in |
| 940 | *A9*) | |
| 930 | ,*A9*) | |
| 941 | 931 | echo "armv7" |
| 942 | 932 | ;; |
| 943 | *) | |
| 933 | ,*) | |
| 944 | 934 | # Unknown version, fallback to the lowest |
| 945 | 935 | echo "armv5" |
| 946 | 936 | ;; |
| @@ -964,7 +954,7 @@ detect_goarch() { | ||
| 964 | 954 | # "out of memory allocating heap arena metadata". |
| 965 | 955 | echo "armv7" |
| 966 | 956 | ;; |
| 967 | *) | |
| 957 | ,*) | |
| 968 | 958 | echo "arm64" |
| 969 | 959 | ;; |
| 970 | 960 | esac |
| @@ -976,7 +966,7 @@ detect_goarch() { | ||
| 976 | 966 | # TODO: detect hardfloat |
| 977 | 967 | echo "$(uname -m)$(detect_endiannes)_softfloat" |
| 978 | 968 | ;; |
| 979 | *) | |
| 969 | ,*) | |
| 980 | 970 | log_error "Unsupported GOARCH: $(uname -m)" |
| 981 | 971 | return 1 |
| 982 | 972 | ;; |
| @@ -1003,7 +993,7 @@ detect_goos() { | ||
| 1003 | 993 | OpenBSD) |
| 1004 | 994 | echo "openbsd" |
| 1005 | 995 | ;; |
| 1006 | *) | |
| 996 | ,*) | |
| 1007 | 997 | log_error "Unsupported GOOS: $(uname -s)" |
| 1008 | 998 | return 1 |
| 1009 | 999 | esac |
| @@ -1080,7 +1070,7 @@ detect_os() { | ||
| 1080 | 1070 | OpenBSD) |
| 1081 | 1071 | echo "openbsd"; return 0 |
| 1082 | 1072 | ;; |
| 1083 | *) | |
| 1073 | ,*) | |
| 1084 | 1074 | esac |
| 1085 | 1075 | log_error "Unsupported OS: $(uname -o) $(grep ID "/etc/os-release" 2>/dev/null | xargs)" |
| 1086 | 1076 | return 1 |
| @@ -1099,7 +1089,7 @@ guess_host_type() { | ||
| 1099 | 1089 | darwin|steamos) |
| 1100 | 1090 | echo "workstation" |
| 1101 | 1091 | ;; |
| 1102 | *) | |
| 1092 | ,*) | |
| 1103 | 1093 | echo "unsure" |
| 1104 | 1094 | ;; |
| 1105 | 1095 | esac |
| @@ -1158,7 +1148,7 @@ bin_location() { | ||
| 1158 | 1148 | steamos) |
| 1159 | 1149 | echo "$HOME/.local/bin/nextdns" |
| 1160 | 1150 | ;; |
| 1161 | *) | |
| 1151 | ,*) | |
| 1162 | 1152 | log_error "Unknown bin location for $OS" |
| 1163 | 1153 | ;; |
| 1164 | 1154 | esac |
| @@ -1166,12 +1156,12 @@ bin_location() { | ||
| 1166 | 1156 | |
| 1167 | 1157 | is_version_current() { |
| 1168 | 1158 | case "$INSTALL_RELEASE" in |
| 1169 | */*) | |
| 1159 | ,*/*) | |
| 1170 | 1160 | # Snapshot |
| 1171 | 1161 | hash=${INSTALL_RELEASE#*/} |
| 1172 | 1162 | test "0.0.0-$hash" = "$CURRENT_RELEASE" |
| 1173 | 1163 | ;; |
| 1174 | *) | |
| 1164 | ,*) | |
| 1175 | 1165 | test "$INSTALL_RELEASE" = "$CURRENT_RELEASE" |
| 1176 | 1166 | ;; |
| 1177 | 1167 | esac |
| @@ -1196,7 +1186,7 @@ get_release() { | ||
| 1196 | 1186 | curl) cmd="curl -A curl -s" ;; |
| 1197 | 1187 | wget) cmd="wget -qO- -U curl" ;; |
| 1198 | 1188 | openssl) cmd="openssl_get" ;; |
| 1199 | *) | |
| 1189 | ,*) | |
| 1200 | 1190 | log_error "Cannot retrieve latest version" |
| 1201 | 1191 | return |
| 1202 | 1192 | ;; |
| @@ -1248,4 +1238,4 @@ openssl_get() { | ||
| 1248 | 1238 | |
| 1249 | 1239 | umask 0022 |
| 1250 | 1240 | main |
| 1251 | ``` | |
| 1241 | #+end_src | |
content/blog/2019-01-07-useful-css.md → blog/useful-css/index.org renamed +64 −74
| @@ -1,12 +1,10 @@ | ||
| 1 | +++ | |
| 2 | date = 2019-01-07 | |
| 3 | title = "Useful CSS Snippets" | |
| 4 | description = "Explore some useful CSS snippets." | |
| 5 | +++ | |
| 1 | #+title: Useful CSS Snippets | |
| 2 | #+date: 2019-01-07 | |
| 3 | #+description: Explore some useful CSS snippets. | |
| 4 | #+filetags: :dev: | |
| 6 | 5 | |
| 7 | # Introduction to CSS | |
| 8 | ||
| 9 | [CSS](https://en.wikipedia.org/wiki/CSS), the language used to markup | |
| 6 | * Introduction to CSS | |
| 7 | [[https://en.wikipedia.org/wiki/CSS][CSS]], the language used to markup | |
| 10 | 8 | HTML code and make it "pretty", is one of the most effective ways to |
| 11 | 9 | increase the attractiveness of a website. It can also lead to increased |
| 12 | 10 | user engagement, retention, and satisfaction. In fact, there are whole |
| @@ -15,12 +13,11 @@ known as UI design and UX design. | ||
| 15 | 13 | |
| 16 | 14 | Some web developers are used to the common CSS properties, such as |
| 17 | 15 | element sizing, fonts, colors, etc., but are not as well versed in |
| 18 | less-used properties and values such as `flexbox`, | |
| 19 | `clip-path`, and `transform`. This article will | |
| 20 | provide some insight into the less-used and unique CSS properties. | |
| 21 | ||
| 22 | # CSS Variables | |
| 16 | less-used properties and values such as =flexbox=, =clip-path=, and | |
| 17 | =transform=. This article will provide some insight into the less-used | |
| 18 | and unique CSS properties. | |
| 23 | 19 | |
| 20 | * CSS Variables | |
| 24 | 21 | The first topic today is CSS variables. Variables are not often used by |
| 25 | 22 | smaller developers. CSS variables allow you to give your website a |
| 26 | 23 | well-defined structure, where you can easily reuse CSS properties |
| @@ -29,15 +26,14 @@ throughout the project. | ||
| 29 | 26 | You can use variables to define things, such as color palettes. Then, |
| 30 | 27 | you can use these colors for backgrounds anywhere else in the HTML. This |
| 31 | 28 | could be extended, where extra variables could be defined for |
| 32 | `primary-text`, `quoted-text`, etc. Variables can | |
| 33 | also be used to define spacing (e.g. `32px` or | |
| 34 | `2rem`), which can then be applied to margins, padding, font | |
| 35 | sizes, and more. | |
| 29 | =primary-text=, =quoted-text=, etc. Variables can also be used to define | |
| 30 | spacing (e.g. =32px= or =2rem=), which can then be applied to margins, | |
| 31 | padding, font sizes, and more. | |
| 36 | 32 | |
| 37 | 33 | For example, here are some variables defined at the root of the website, |
| 38 | 34 | which allows for any subsequent CSS rules to use those variables: |
| 39 | 35 | |
| 40 | ```css | |
| 36 | #+begin_src css | |
| 41 | 37 | :root { |
| 42 | 38 | --primary-color: black; |
| 43 | 39 | --secondary-color: white; |
| @@ -47,39 +43,38 @@ body { | ||
| 47 | 43 | background-color: var(--primary-color); |
| 48 | 44 | color: var(--secondary-color); |
| 49 | 45 | } |
| 50 | ``` | |
| 51 | ||
| 52 | # CSS Box Shadows | |
| 46 | #+end_src | |
| 53 | 47 | |
| 48 | * CSS Box Shadows | |
| 54 | 49 | Box shadows were once my mortal enemy. No matter how hard I tried, I |
| 55 | 50 | just couldn't get them to work how I wanted. Because of this, my |
| 56 | favorite discovery has been CSSMatic's [box shadow | |
| 57 | generator](https://www.cssmatic.com/box-shadow). It provides an | |
| 58 | excellent tool to generate box shadows using their simple sliders. | |
| 59 | Surprisingly, this is the reason I learned how box shadows work! You can | |
| 60 | use the sliders and watch how the CSS code changes in the image that is | |
| 61 | displayed. Through this, you should understand that the basic structure | |
| 62 | for box shadows is: | |
| 63 | ||
| 64 | ```css | |
| 51 | favorite discovery has been CSSMatic's | |
| 52 | [[https://www.cssmatic.com/box-shadow][box shadow generator]]. It | |
| 53 | provides an excellent tool to generate box shadows using their simple | |
| 54 | sliders. Surprisingly, this is the reason I learned how box shadows | |
| 55 | work! You can use the sliders and watch how the CSS code changes in the | |
| 56 | image that is displayed. Through this, you should understand that the | |
| 57 | basic structure for box shadows is: | |
| 58 | ||
| 59 | #+begin_src css | |
| 65 | 60 | box-shadow: inset horizontal vertical blur spread color; |
| 66 | ``` | |
| 61 | #+end_src | |
| 67 | 62 | |
| 68 | 63 | Now, let's look at some basic examples! You can copy and paste the |
| 69 | 64 | following code into a site like CodePen or your own HTML files. Feel |
| 70 | 65 | free to play around with the code, experiment, and learn. |
| 71 | 66 | |
| 72 | ****Box Shadow #1**** | |
| 67 | *Box Shadow #1* | |
| 73 | 68 | |
| 74 | ```html | |
| 69 | #+begin_src html | |
| 75 | 70 | <div class="shadow-examples"> |
| 76 | 71 | <div class="box effect1"> |
| 77 | 72 | <h3>Effect 1</h3> |
| 78 | 73 | </div> |
| 79 | 74 | </div> |
| 80 | ``` | |
| 75 | #+end_src | |
| 81 | 76 | |
| 82 | ```css | |
| 77 | #+begin_src css | |
| 83 | 78 | .box h3 { |
| 84 | 79 | text-align: center; |
| 85 | 80 | position: relative; |
| @@ -94,19 +89,19 @@ free to play around with the code, experiment, and learn. | ||
| 94 | 89 | .effect1 { |
| 95 | 90 | box-shadow: 0 10px 6px -6px #777; |
| 96 | 91 | } |
| 97 | ``` | |
| 92 | #+end_src | |
| 98 | 93 | |
| 99 | ****Box Shadow #2**** | |
| 94 | *Box Shadow #2* | |
| 100 | 95 | |
| 101 | ```html | |
| 96 | #+begin_src html | |
| 102 | 97 | <div class="shadow-examples"> |
| 103 | 98 | <div class="box effect2"> |
| 104 | 99 | <h3>Effect 2</h3> |
| 105 | 100 | </div> |
| 106 | 101 | </div> |
| 107 | ``` | |
| 102 | #+end_src | |
| 108 | 103 | |
| 109 | ```css | |
| 104 | #+begin_src css | |
| 110 | 105 | .box h3 { |
| 111 | 106 | text-align: center; |
| 112 | 107 | position: relative; |
| @@ -121,28 +116,27 @@ free to play around with the code, experiment, and learn. | ||
| 121 | 116 | .effect2 { |
| 122 | 117 | box-shadow: 10px 10px 5px -5px rgba(0, 0, 0, 0.75); |
| 123 | 118 | } |
| 124 | ``` | |
| 119 | #+end_src | |
| 125 | 120 | |
| 126 | 121 | Try these box shadows out on your own and see how changing each shadow |
| 127 | 122 | value works. |
| 128 | 123 | |
| 129 | # CSS Flexbox | |
| 130 | ||
| 124 | * CSS Flexbox | |
| 131 | 125 | Now, let's move on to the best part of this article: flexbox. The |
| 132 | 126 | flexbox is by far my favorite new toy. I originally stumbled across this |
| 133 | 127 | solution after looking for more efficient ways of centering content |
| 134 | 128 | horizontally AND vertically. I had used a few hack-ish methods before, |
| 135 | 129 | but flexbox throws those out the window. The best part of it all is that |
| 136 | flexbox is *dead simple*. | |
| 130 | flexbox is /dead simple/. | |
| 137 | 131 | |
| 138 | 132 | Flexbox pertains to the parent div of any element. You want the parent |
| 139 | 133 | to be the flexbox in which items are arranged to use the flex methods. |
| 140 | 134 | It's easier to see this in action that explained, so let's see an |
| 141 | 135 | example. |
| 142 | 136 | |
| 143 | ****Flexbox**** | |
| 137 | *Flexbox* | |
| 144 | 138 | |
| 145 | ```html | |
| 139 | #+begin_src html | |
| 146 | 140 | <div class="flex-examples"> |
| 147 | 141 | <div class="sm-box"> |
| 148 | 142 | <h3>1</h3> |
| @@ -151,9 +145,9 @@ example. | ||
| 151 | 145 | <h3>2</h3> |
| 152 | 146 | </div> |
| 153 | 147 | </div> |
| 154 | ``` | |
| 148 | #+end_src | |
| 155 | 149 | |
| 156 | ```css | |
| 150 | #+begin_src css | |
| 157 | 151 | .flex-examples { |
| 158 | 152 | display: flex; |
| 159 | 153 | flex-wrap: wrap; |
| @@ -171,29 +165,25 @@ example. | ||
| 171 | 165 | background: #fff; |
| 172 | 166 | margin: 40px 10px; |
| 173 | 167 | } |
| 174 | ``` | |
| 175 | ||
| 176 | You may notice that we no longer need to use the `top` | |
| 177 | property for the `h3` elements in our code. This is because | |
| 178 | we set the display box to be a flex container for the small boxes, AND | |
| 179 | we made the small boxes flex containers for their elements (the h3 | |
| 180 | tags). Flex boxes can be nested like this to center content that is | |
| 181 | inside centered content. | |
| 182 | ||
| 183 | For the example above, we designated the `justify-content` | |
| 184 | property to be `flex-start` so that the boxes stack from the | |
| 185 | left side of the screen. This property can be changed to | |
| 186 | `center` to make the boxes appear in the center of the | |
| 187 | screen. | |
| 188 | ||
| 189 | For an interactive example, [check out this | |
| 190 | CodePen](https://codepen.io/LandonSchropp/pen/KpzzGo) from | |
| 191 | [LandonScropp](https://codepen.io/LandonSchropp/). Resize the window | |
| 192 | with dice to see how they collapse and re-align. | |
| 193 | ||
| 194 | # Even More CSS | |
| 195 | ||
| 196 | For more inspiration, you can visit [CodePen](https://www.codepen.io), | |
| 197 | [Dribbble](https://dribbble.com), or [UI | |
| 198 | Movement](https://uimovement.com) to browse the collections of many | |
| 199 | amazing web designers. | |
| 168 | #+end_src | |
| 169 | ||
| 170 | You may notice that we no longer need to use the =top= property for the | |
| 171 | =h3= elements in our code. This is because we set the display box to be | |
| 172 | a flex container for the small boxes, AND we made the small boxes flex | |
| 173 | containers for their elements (the h3 tags). Flex boxes can be nested | |
| 174 | like this to center content that is inside centered content. | |
| 175 | ||
| 176 | For the example above, we designated the =justify-content= property to | |
| 177 | be =flex-start= so that the boxes stack from the left side of the | |
| 178 | screen. This property can be changed to =center= to make the boxes | |
| 179 | appear in the center of the screen. | |
| 180 | ||
| 181 | For an interactive example, | |
| 182 | [[https://codepen.io/LandonSchropp/pen/KpzzGo][check out this CodePen]] | |
| 183 | from [[https://codepen.io/LandonSchropp/][LandonScropp]]. Resize the | |
| 184 | window with dice to see how they collapse and re-align. | |
| 185 | ||
| 186 | * Even More CSS | |
| 187 | For more inspiration, you can visit [[https://www.codepen.io][CodePen]], | |
| 188 | [[https://dribbble.com][Dribbble]], or [[https://uimovement.com][UI | |
| 189 | Movement]] to browse the collections of many amazing web designers. | |
content/blog/2021-03-28-vaporwave-vs-outrun.md → blog/vaporwave-vs-outrun/index.org renamed +51 −57
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-03-28 | |
| 3 | title = "Vaporwave vs Outrun" | |
| 4 | description = "Learn the differences between the vaporwave and Outrun aesthetics." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Overview | |
| 1 | #+title: Vaporwave vs Outrun | |
| 2 | #+date: 2021-03-28 | |
| 3 | #+description: Learn the differences between the vaporwave and Outrun aesthetics. | |
| 4 | #+filetags: :personal: | |
| 8 | 5 | |
| 6 | * Overview | |
| 9 | 7 | When it comes to an aesthetic that originated primarily online, there |
| 10 | 8 | tends to be a lot of confusion around what falls into each specific |
| 11 | 9 | genre. This post discusses Vaporwave and Outrun, which have become |
| @@ -13,58 +11,58 @@ almost synonymous in the minds of those online who aren't hardcore into | ||
| 13 | 11 | these genres of media. More specifically, Outrun is largely an unknown |
| 14 | 12 | term while all aesthetics in these two genres are usually attributed to |
| 15 | 13 | Vaporwave. For example, take a look at the image search results for |
| 16 | Vaporwave: the results include **a lot** of Outrun-themed images. | |
| 17 | You'll find a similar trend almost everywhere. | |
| 18 | ||
| 19 |  | |
| 14 | Vaporwave: the results include *a lot** of Outrun-themed images. You'll | |
| 15 | find a similar trend almost everywhere. | |
| 20 | 16 | |
| 21 | ## Vaporwave | |
| 17 | #+caption: Vaporwave Search Results | |
| 18 | [[https://img.cleberg.net/blog/20210328-vaporwave-vs-outrun/vaporwave-search-results.png]] | |
| 22 | 19 | |
| 23 |  | |
| 20 | * Vaporwave | |
| 21 | #+caption: Macintosh Plus Album Cover | |
| 22 | [[https://img.cleberg.net/blog/20210328-vaporwave-vs-outrun/macintosh-plus.png]] | |
| 24 | 23 | |
| 25 | 24 | Okay, so what is Vaporwave? I'm going to just copy-and-paste some |
| 26 | 25 | general info from the Wikipedia article on |
| 27 | [Vaporwave](https://en.wikipedia.org/wiki/Vaporwave), so that I'm not | |
| 26 | [[https://en.wikipedia.org/wiki/Vaporwave][Vaporwave]], so that I'm not | |
| 28 | 27 | repeating everything you can already search for online: |
| 29 | 28 | |
| 30 | > Vaporwave is a microgenre of electronic music, a visual art style, and | |
| 31 | > an Internet meme that emerged in the early 2010s. It is defined partly | |
| 32 | > by its slowed-down, chopped and screwed samples of smooth jazz, | |
| 33 | > elevator, R&B, and lounge music from the 1980s and 1990s. The | |
| 34 | > surrounding subculture is sometimes associated with an ambiguous or | |
| 35 | > satirical take on consumer capitalism and pop culture, and tends to be | |
| 36 | > characterized by a nostalgic or surrealist engagement with the popular | |
| 37 | > entertainment, technology and advertising of previous decades. | |
| 38 | > Visually, it incorporates early Internet imagery, late 1990s web | |
| 39 | > design, glitch art, anime, 3D-rendered objects, and cyberpunk tropes | |
| 40 | > in its cover artwork and music videos. | |
| 29 | #+begin_quote | |
| 30 | Vaporwave is a microgenre of electronic music, a visual art style, and | |
| 31 | an Internet meme that emerged in the early 2010s. It is defined partly | |
| 32 | by its slowed-down, chopped and screwed samples of smooth jazz, | |
| 33 | elevator, R&B, and lounge music from the 1980s and 1990s. The | |
| 34 | surrounding subculture is sometimes associated with an ambiguous or | |
| 35 | satirical take on consumer capitalism and pop culture, and tends to be | |
| 36 | characterized by a nostalgic or surrealist engagement with the popular | |
| 37 | entertainment, technology and advertising of previous decades. Visually, | |
| 38 | it incorporates early Internet imagery, late 1990s web design, glitch | |
| 39 | art, anime, 3D-rendered objects, and cyberpunk tropes in its cover | |
| 40 | artwork and music videos. | |
| 41 | #+end_quote | |
| 41 | 42 | |
| 42 | 43 | This is an excellent summary, and it helps address my point here: there |
| 43 | 44 | are specific aspects that make Vaporwave unique: |
| 44 | 45 | |
| 45 | ### Time Frame | |
| 46 | ||
| 46 | ** Time Frame | |
| 47 | 47 | The time frame for references, logos, etc. focuses mostly on the 1990s |
| 48 | 48 | in Vaporwave. You'll see old school Pepsi logos, Microsoft 95 screens, |
| 49 | 49 | tropical plants, classic marble sculptures, and many references from |
| 50 | 50 | Japan's influence in the 90s. |
| 51 | 51 | |
| 52 | ### Art | |
| 53 | ||
| 52 | ** Art | |
| 54 | 53 | The color scheme is generally a soft, light palette that uses pastel |
| 55 | 54 | colors. The backdrop will often be in a light-pink or teal blue. |
| 56 | 55 | |
| 57 | ### Music | |
| 58 | ||
| 56 | ** Music | |
| 59 | 57 | The musical genre of Vaporwave incorporates soft tunes, lounge music, |
| 60 | 58 | and sound effects that will make the listener reminisce of the 90s. The |
| 61 | 59 | sounds of the genre are generally slower-paced and calming. The major |
| 62 | breakthrough artist for Vaporwave was [Macintosh | |
| 63 | Plus](https://en.wikipedia.org/wiki/Vektroid), who released the album | |
| 64 | [Floral | |
| 65 | Shoppe](https://archive.org/details/MACINTOSHPLUS-FLORALSHOPPE_complete) | |
| 66 | in 2011. Another more recent example is the artist | |
| 67 | [sadbert](https://sadbert.bandcamp.com/), whose latest album | |
| 60 | breakthrough artist for Vaporwave was | |
| 61 | [[https://en.wikipedia.org/wiki/Vektroid][Macintosh Plus]], who released | |
| 62 | the album | |
| 63 | [[https://archive.org/details/MACINTOSHPLUS-FLORALSHOPPE_complete][Floral | |
| 64 | Shoppe]] in 2011. Another more recent example is the artist | |
| 65 | [[https://sadbert.bandcamp.com/][sadbert]], whose latest album | |
| 68 | 66 | incorporates the upbeat tones of the 1999 Dilbert TV series. |
| 69 | 67 | |
| 70 | 68 | Notice that Vaporwave doesn't include things like racing cars, |
| @@ -74,23 +72,21 @@ was becoming common in households, a reality that we have already | ||
| 74 | 72 | experienced. Focus on the most aesthetically-pleasing parts of that past |
| 75 | 73 | is a large part of Vaporwave. |
| 76 | 74 | |
| 77 | ## Outrun | |
| 78 | ||
| 79 |  | |
| 75 | * Outrun | |
| 76 | #+caption: Outrun | |
| 77 | [[https://img.cleberg.net/blog/20210328-vaporwave-vs-outrun/outrun.png]] | |
| 80 | 78 | |
| 81 | 79 | Now, let's get to Outrun. This one is a little trickier since the genre |
| 82 | 80 | has largely been lumped under the Vaporwave title for so long. However, |
| 83 | it stems from the [Synthwave](https://en.wikipedia.org/wiki/Synthwave) | |
| 84 | music genre and is likely named after the 1986 racer game, [Out | |
| 85 | Run](https://en.wikipedia.org/wiki/Out_Run). | |
| 86 | ||
| 87 | ### Time Frame | |
| 81 | it stems from the [[https://en.wikipedia.org/wiki/Synthwave][Synthwave]] | |
| 82 | music genre and is likely named after the 1986 racer game, | |
| 83 | [[https://en.wikipedia.org/wiki/Out_Run][Out Run]]. | |
| 88 | 84 | |
| 85 | ** Time Frame | |
| 89 | 86 | Outrun can be thought of as a retro-futuristic aesthetic born from the |
| 90 | 87 | 1980s. |
| 91 | 88 | |
| 92 | ### Art | |
| 93 | ||
| 89 | ** Art | |
| 94 | 90 | The color scheme uses a very dark color palette with the main colors |
| 95 | 91 | being deep oranges, blues, and purples. Red edges are common around |
| 96 | 92 | objects in Outrun art. The background of the Outrun aesthetic is almost |
| @@ -101,8 +97,7 @@ Classic sports cars, chrome robots, computer generated graphics and | ||
| 101 | 97 | fonts, and the occasional use of rain or palm trees can be found in |
| 102 | 98 | Outrun art. |
| 103 | 99 | |
| 104 | ### Music | |
| 105 | ||
| 100 | ** Music | |
| 106 | 101 | This aesthetic has a more aggressive and fast-paced style of music, |
| 107 | 102 | which tends to match the subject of the art in this aesthetic. |
| 108 | 103 | |
| @@ -110,20 +105,19 @@ Outrun enthusiasts love what people in the 1980s thought the future | ||
| 110 | 105 | would look like. Take a look at a common video game discussed in Outrun |
| 111 | 106 | circles, Far Cry 3: Blood Dragon: |
| 112 | 107 | |
| 113 |  | |
| 108 | #+caption: Fry Cry 3: Blood Dragon | |
| 109 | [[https://img.cleberg.net/blog/20210328-vaporwave-vs-outrun/far-cry.png]] | |
| 115 | 110 | |
| 116 | 111 | Another example that doesn't force the color scheme as hard as some |
| 117 | 112 | online art does is Kung Fury: |
| 118 | 113 | |
| 119 |  | |
| 121 | ||
| 122 |  | |
| 114 | #+caption: Kung Fury | |
| 115 | [[https://img.cleberg.net/blog/20210328-vaporwave-vs-outrun/kung-fury.png]] | |
| 124 | 116 | |
| 125 | ## Conclusion | |
| 117 | #+caption: Kung Fury Hacker Scene | |
| 118 | [[https://img.cleberg.net/blog/20210328-vaporwave-vs-outrun/kung-fury-hacker.png]] | |
| 126 | 119 | |
| 120 | * Conclusion | |
| 127 | 121 | While Vaporwave and Outrun share similarities, they are two distinct |
| 128 | 122 | aesthetics with many important distinctions. Someone who enjoys one may |
| 129 | 123 | not necessarily enjoy the other, so it's important to make sure we |
content/blog/2020-07-20-video-game-sales.md → blog/video-game-sales/index.org renamed +62 −68
| @@ -1,36 +1,33 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-07-20 | |
| 3 | title = "Data Exploration: Video Game Sales" | |
| 4 | description = "Exploring and visualizing data with Python." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Background Information | |
| 1 | #+title: Data Exploration: Video Game Sales | |
| 2 | #+date: 2020-07-20 | |
| 3 | #+description: Exploring and visualizing data with Python. | |
| 4 | #+filetags: :data: | |
| 8 | 5 | |
| 6 | * Background Information | |
| 9 | 7 | This dataset (obtained from |
| 10 | [Kaggle](https://www.kaggle.com/gregorut/videogamesales/data)) contains | |
| 11 | a list of video games with sales greater than 100,000 copies. It was | |
| 12 | generated by a scrape of vgchartz.com. | |
| 8 | [[https://www.kaggle.com/gregorut/videogamesales/data][Kaggle]]) | |
| 9 | contains a list of video games with sales greater than 100,000 copies. | |
| 10 | It was generated by a scrape of vgchartz.com. | |
| 13 | 11 | |
| 14 | 12 | Fields include: |
| 15 | 13 | |
| 16 | - Rank: Ranking of overall sales | |
| 17 | - Name: The game name | |
| 18 | - Platform: Platform of the game release (i.e. PC,PS4, etc.) | |
| 19 | - Year: Year of the game's release | |
| 20 | - Genre: Genre of the game | |
| 21 | - Publisher: Publisher of the game | |
| 22 | - NA~Sales~: Sales in North America (in millions) | |
| 23 | - EU~Sales~: Sales in Europe (in millions) | |
| 24 | - JP~Sales~: Sales in Japan (in millions) | |
| 25 | - Other~Sales~: Sales in the rest of the world (in millions) | |
| 26 | - Global~Sales~: Total worldwide sales. | |
| 14 | - Rank: Ranking of overall sales | |
| 15 | - Name: The game name | |
| 16 | - Platform: Platform of the game release (i.e. PC,PS4, etc.) | |
| 17 | - Year: Year of the game's release | |
| 18 | - Genre: Genre of the game | |
| 19 | - Publisher: Publisher of the game | |
| 20 | - NA_{Sales}: Sales in North America (in millions) | |
| 21 | - EU_{Sales}: Sales in Europe (in millions) | |
| 22 | - JP_{Sales}: Sales in Japan (in millions) | |
| 23 | - Other_{Sales}: Sales in the rest of the world (in millions) | |
| 24 | - Global_{Sales}: Total worldwide sales. | |
| 27 | 25 | |
| 28 | 26 | There are 16,598 records. 2 records were dropped due to incomplete |
| 29 | 27 | information. |
| 30 | 28 | |
| 31 | # Import the Data | |
| 32 | ||
| 33 | ```python | |
| 29 | * Import the Data | |
| 30 | #+begin_src python | |
| 34 | 31 | # Import the Python libraries we will be using |
| 35 | 32 | import pandas as pd |
| 36 | 33 | import numpy as np |
| @@ -41,55 +38,54 @@ import matplotlib.pyplot as plt | ||
| 41 | 38 | file = r'video_game_sales.csv' |
| 42 | 39 | df = pd.read_csv(file) |
| 43 | 40 | df |
| 44 | ``` | |
| 45 | ||
| 46 |  | |
| 41 | #+end_src | |
| 48 | 42 | |
| 49 | # Explore the Data | |
| 43 | #+caption: Dataframe Results | |
| 44 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/01_dataframe-min.png]] | |
| 50 | 45 | |
| 51 | ```python | |
| 46 | * Explore the Data | |
| 47 | #+begin_src python | |
| 52 | 48 | # With the description function, we can see the basic stats. For example, we can also see that the 'Year' column has some incomplete values. |
| 53 | 49 | df.describe() |
| 54 | ``` | |
| 50 | #+end_src | |
| 55 | 51 | |
| 56 |  | |
| 52 | #+caption: df.describe() | |
| 53 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/02_describe-min.png]] | |
| 57 | 54 | |
| 58 | ```python | |
| 55 | #+begin_src python | |
| 59 | 56 | # This function shows the rows and columns of NaN values. For example, df[179,3] = nan |
| 60 | 57 | np.where(pd.isnull(df)) |
| 61 | 58 | |
| 62 | 59 | (array([179, ..., 16553], dtype=int64), |
| 63 | 60 | array([3, ..., 5], dtype=int64)) |
| 64 | ``` | |
| 61 | #+end_src | |
| 65 | 62 | |
| 66 | # Visualize the Data | |
| 67 | ||
| 68 | ```python | |
| 63 | * Visualize the Data | |
| 64 | #+begin_src python | |
| 69 | 65 | # This function plots the global sales by platform |
| 70 | 66 | sns.catplot(x='Platform', y='Global_Sales', data=df, jitter=False).set_xticklabels(rotation=90) |
| 71 | ``` | |
| 67 | #+end_src | |
| 72 | 68 | |
| 73 |  | |
| 69 | #+caption: Plot of Global Sales by Platform | |
| 70 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/03_plot-min.png]] | |
| 75 | 71 | |
| 76 | ```python | |
| 72 | #+begin_src python | |
| 77 | 73 | # This function plots the global sales by genre |
| 78 | 74 | sns.catplot(x='Genre', y='Global_Sales', data=df, jitter=False).set_xticklabels(rotation=45) |
| 79 | ``` | |
| 75 | #+end_src | |
| 80 | 76 | |
| 81 |  | |
| 77 | #+caption: Plot of Global Sales by Genre | |
| 78 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/04_plot-min.png]] | |
| 83 | 79 | |
| 84 | ```python | |
| 80 | #+begin_src python | |
| 85 | 81 | # This function plots the global sales by year |
| 86 | 82 | sns.lmplot(x='Year', y='Global_Sales', data=df).set_xticklabels(rotation=45) |
| 87 | ``` | |
| 83 | #+end_src | |
| 88 | 84 | |
| 89 |  | |
| 85 | #+caption: Plot of Global Sales by Year | |
| 86 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/05_plot-min.png]] | |
| 91 | 87 | |
| 92 | ```python | |
| 88 | #+begin_src python | |
| 93 | 89 | # This function plots four different lines to show sales from different regions. |
| 94 | 90 | # The global sales plot line is commented-out, but can be included for comparison |
| 95 | 91 | df2 = df.groupby('Year').sum() |
| @@ -113,14 +109,13 @@ ax.plot(years, d, label='Other_Sales') | ||
| 113 | 109 | |
| 114 | 110 | ax.legend() |
| 115 | 111 | plt.show() |
| 116 | ``` | |
| 117 | ||
| 118 |  | |
| 112 | #+end_src | |
| 120 | 113 | |
| 121 | # Investigate Outliers | |
| 114 | #+caption: Plot of Regional Sales by Year | |
| 115 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/06_plot-min.png]] | |
| 122 | 116 | |
| 123 | ```python | |
| 117 | ** Investigate Outliers | |
| 118 | #+begin_src python | |
| 124 | 119 | # Find the game with the highest sales in North America |
| 125 | 120 | df.loc[df['NA_Sales'].idxmax()] |
| 126 | 121 | |
| @@ -140,30 +135,29 @@ Name: 0, dtype: object | ||
| 140 | 135 | # Explore statistics in the year 2006 (highest selling year) |
| 141 | 136 | df3 = df[(df['Year'] == 2006)] |
| 142 | 137 | df3.describe() |
| 143 | ``` | |
| 138 | #+end_src | |
| 144 | 139 | |
| 145 |  | |
| 140 | #+caption: Descriptive Statistics of 2006 Sales | |
| 141 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/07_2006_stats-min.png]] | |
| 147 | 142 | |
| 148 | ```python | |
| 143 | #+begin_src python | |
| 149 | 144 | # Plot the results of the previous dataframe (games from 2006) - we can see the year's results were largely carried by Wii Sports |
| 150 | 145 | sns.catplot(x="Genre", y="Global_Sales", data=df3, jitter=False).set_xticklabels(rotation=45) |
| 151 | ``` | |
| 146 | #+end_src | |
| 152 | 147 | |
| 153 |  | |
| 148 | #+caption: Plot of 2006 Sales | |
| 149 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/08_plot-min.png]] | |
| 155 | 150 | |
| 156 | ```python | |
| 151 | #+begin_src python | |
| 157 | 152 | # We can see 4 outliers in the graph above, so let's get the top 5 games from that dataframe |
| 158 | 153 | # The results below show that Nintendo had all top 5 games (3 on the Wii and 2 on the DS) |
| 159 | 154 | df3.sort_values(by=['Global_Sales'], ascending=False).head(5) |
| 160 | ``` | |
| 161 | ||
| 162 |  | |
| 155 | #+end_src | |
| 164 | 156 | |
| 165 | # Discussion | |
| 157 | #+caption: Outliers of 2006 Sales | |
| 158 | [[https://img.cleberg.net/blog/20200720-data-exploration-video-game-sales/09_outliers-min.png]] | |
| 166 | 159 | |
| 160 | * Discussion | |
| 167 | 161 | The purpose of exploring datasets is to ask questions, answer questions, |
| 168 | 162 | and discover intelligence that can be used to inform decision-making. |
| 169 | 163 | So, what have we found in this dataset? |
content/blog/2020-09-01-visual-recognition.md → blog/visual-recognition/index.org renamed +50 −57
| @@ -1,66 +1,62 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-09-01 | |
| 3 | title = "IBM Watson Visual Recognition" | |
| 4 | description = "Exploring and visualizing data with Python." | |
| 5 | +++ | |
| 1 | #+title: IBM Watson Visual Recognition | |
| 2 | #+date: 2020-09-01 | |
| 3 | #+description: Exploring and visualizing data with Python. | |
| 4 | #+filetags: :dev: | |
| 6 | 5 | |
| 7 | # What is IBM Watson? | |
| 8 | ||
| 9 | If you've never heard of [Watson](https://www.ibm.com/watson), this | |
| 6 | * What is IBM Watson? | |
| 7 | If you've never heard of [[https://www.ibm.com/watson][Watson]], this | |
| 10 | 8 | service is a suite of enterprise-ready AI services, applications, and |
| 11 | 9 | tooling provided by IBM. Watson contains quite a few useful tools for |
| 12 | 10 | data scientists and students, including the subject of this post today: |
| 13 | 11 | visual recognition. |
| 14 | 12 | |
| 15 | 13 | If you'd like to view the official documentation for the Visual |
| 16 | Recognition API, visit the [API | |
| 17 | Docs](https://cloud.ibm.com/apidocs/visual-recognition/visual-recognition-v3?code=python). | |
| 18 | ||
| 19 | # Prerequisites | |
| 14 | Recognition API, visit the | |
| 15 | [[https://cloud.ibm.com/apidocs/visual-recognition/visual-recognition-v3?code=python][API | |
| 16 | Docs]]. | |
| 20 | 17 | |
| 18 | * Prerequisites | |
| 21 | 19 | To be able to use Watson Visual Recognition, you'll need the following: |
| 22 | 20 | |
| 23 | 1. Create a free account on [IBM Watson | |
| 24 | Studio](https://www.ibm.com/cloud/watson-studio). | |
| 25 | 2. Add the [Watson Visual | |
| 26 | Recognition](https://www.ibm.com/cloud/watson-visual-recognition) | |
| 27 | service to your IBM Watson account. | |
| 28 | 3. Get your API key and URL. To do this, first go to the [profile | |
| 29 | dashboard](https://dataplatform.cloud.ibm.com/home2?context=cpdaas) | |
| 30 | for your IBM account and click on the Watson Visual Recognition | |
| 31 | service you created. This will be listed in the section titled | |
| 32 | **Your services**. Then click the **Credentials** tab and open the | |
| 33 | **Auto-generated credentials** dropdown. Copy your API key and URL | |
| 34 | so that you can use them in the Python script later. | |
| 35 | 4. **[Optional]** While not required, you can also create the Jupyter | |
| 36 | Notebook for this project right inside [Watson | |
| 37 | Studio](https://www.ibm.com/cloud/watson-studio). Watson Studio will | |
| 38 | save your notebooks inside an organized project and allow you to use | |
| 39 | their other integrated products, such as storage containers, AI | |
| 40 | models, documentation, external sharing, etc. | |
| 41 | ||
| 42 | # Calling the IBM Watson Visual Recognition API | |
| 43 | ||
| 21 | 1. Create a free account on | |
| 22 | [[https://www.ibm.com/cloud/watson-studio][IBM Watson Studio]]. | |
| 23 | 2. Add the [[https://www.ibm.com/cloud/watson-visual-recognition][Watson | |
| 24 | Visual Recognition]] service to your IBM Watson account. | |
| 25 | 3. Get your API key and URL. To do this, first go to the | |
| 26 | [[https://dataplatform.cloud.ibm.com/home2?context=cpdaas][profile | |
| 27 | dashboard]] for your IBM account and click on the Watson Visual | |
| 28 | Recognition service you created. This will be listed in the section | |
| 29 | titled *Your services*. Then click the *Credentials** tab and open the | |
| 30 | *Auto-generated credentials** dropdown. Copy your API key and URL so | |
| 31 | that you can use them in the Python script later. | |
| 32 | 4. *[Optional]** While not required, you can also create the Jupyter | |
| 33 | Notebook for this project right inside | |
| 34 | [[https://www.ibm.com/cloud/watson-studio][Watson Studio]]. Watson | |
| 35 | Studio will save your notebooks inside an organized project and allow | |
| 36 | you to use their other integrated products, such as storage | |
| 37 | containers, AI models, documentation, external sharing, etc. | |
| 38 | ||
| 39 | * Calling the IBM Watson Visual Recognition API | |
| 44 | 40 | Okay, now let's get started. |
| 45 | 41 | |
| 46 | 42 | To begin, we need to install the proper Python package for IBM Watson. |
| 47 | 43 | |
| 48 | ```sh | |
| 44 | #+begin_src sh | |
| 49 | 45 | pip install --upgrade --user "ibm-watson>=4.5.0" |
| 50 | ``` | |
| 46 | #+end_src | |
| 51 | 47 | |
| 52 | 48 | Next, we need to specify the API key, version, and URL given to us when |
| 53 | 49 | we created the Watson Visual Recognition service. |
| 54 | 50 | |
| 55 | ```python | |
| 51 | #+begin_src python | |
| 56 | 52 | apikey = "<your-apikey>" |
| 57 | 53 | version = "2018-03-19" |
| 58 | 54 | url = "<your-url>" |
| 59 | ``` | |
| 55 | #+end_src | |
| 60 | 56 | |
| 61 | 57 | Now, let's import the necessary libraries and authenticate our service. |
| 62 | 58 | |
| 63 | ```python | |
| 59 | #+begin_src python | |
| 64 | 60 | import json |
| 65 | 61 | from ibm_watson import VisualRecognitionV3 |
| 66 | 62 | from ibm_cloud_sdk_core.authenticators import IAMAuthenticator |
| @@ -72,20 +68,19 @@ visual_recognition = VisualRecognitionV3( | ||
| 72 | 68 | ) |
| 73 | 69 | |
| 74 | 70 | visual_recognition.set_service_url(url) |
| 75 | ``` | |
| 71 | #+end_src | |
| 76 | 72 | |
| 77 | **[Optional]** If you'd like to tell the API not to use any data to | |
| 73 | *[Optional]* If you'd like to tell the API not to use any data to | |
| 78 | 74 | improve their products, set the following header. |
| 79 | 75 | |
| 80 | ```python | |
| 76 | #+begin_src python | |
| 81 | 77 | visual_recognition.set_default_headers({'x-watson-learning-opt-out': "true"}) |
| 82 | ``` | |
| 78 | #+end_src | |
| 83 | 79 | |
| 84 | Now we have our API all set and ready to go. For this example, I'm | |
| 85 | going to include a `dict` of photos to load as we test out | |
| 86 | the API. | |
| 80 | Now we have our API all set and ready to go. For this example, I'm going | |
| 81 | to include a =dict= of photos to load as we test out the API. | |
| 87 | 82 | |
| 88 | ```python | |
| 83 | #+begin_src python | |
| 89 | 84 | data = [ |
| 90 | 85 | { |
| 91 | 86 | "title": "Grizzly Bear", |
| @@ -112,7 +107,7 @@ data = [ | ||
| 112 | 107 | "url": "https://example.com/photos/image6.jpg" |
| 113 | 108 | } |
| 114 | 109 | ] |
| 115 | ``` | |
| 110 | #+end_src | |
| 116 | 111 | |
| 117 | 112 | Now that we've set up our libraries and have the photos ready, let's |
| 118 | 113 | create a loop to call the API for each image. The code below shows a |
| @@ -123,7 +118,7 @@ to the console with dotted lines separating each section. | ||
| 123 | 118 | In the case of an API error, the codes and explanations are output to |
| 124 | 119 | the console. |
| 125 | 120 | |
| 126 | ```python | |
| 121 | #+begin_src python | |
| 127 | 122 | from ibm_watson import ApiException |
| 128 | 123 | |
| 129 | 124 | for x in range(len(data)): |
| @@ -144,10 +139,9 @@ try: | ||
| 144 | 139 | print("-----------------------------------------------") |
| 145 | 140 | except ApiException as ex: |
| 146 | 141 | print("Method failed with status code " + str(ex.code) + ": " + ex.message) |
| 147 | ``` | |
| 148 | ||
| 149 | # The Results | |
| 142 | #+end_src | |
| 150 | 143 | |
| 144 | * The Results | |
| 151 | 145 | Here we can see the full result set of our function above. If you view |
| 152 | 146 | each of the URLs that we sent to the API, you'll be able to see that it |
| 153 | 147 | was remarkably accurate. To be fair, these are clear high-resolution, |
| @@ -160,13 +154,13 @@ instead of attempting to write our own image recognition function. Each | ||
| 160 | 154 | of the classifications returned was a fair description of the image. |
| 161 | 155 | |
| 162 | 156 | If you wanted to restrict the results to those that are at least 90% |
| 163 | confident or greater, you would simply adjust the `threshold` | |
| 164 | in the `visual_recognition.classify()` function. | |
| 157 | confident or greater, you would simply adjust the =threshold= in the | |
| 158 | =visual_recognition.classify()= function. | |
| 165 | 159 | |
| 166 | 160 | When your program runs, it should show the output below for each photo |
| 167 | 161 | you provide. |
| 168 | 162 | |
| 169 | ```txt | |
| 163 | #+begin_src txt | |
| 170 | 164 | ---------------------------------------------------------------- |
| 171 | 165 | Image Title: Grizzly Bear |
| 172 | 166 | Image URL: https://example.com/photos/image1.jpg |
| @@ -179,10 +173,9 @@ animal ( 1 ) | ||
| 179 | 173 | Alaskan brown bear ( 0.759 ) |
| 180 | 174 | greenishness color ( 0.975 ) |
| 181 | 175 | ---------------------------------------------------------------- |
| 182 | ``` | |
| 183 | ||
| 184 | # Discussion | |
| 176 | #+end_src | |
| 185 | 177 | |
| 178 | * Discussion | |
| 186 | 179 | Now, this was a very minimal implementation of the API. We simply |
| 187 | 180 | supplied some images and looked to see how accurate the results were. |
| 188 | 181 | However, you could implement this type of API into many machine learning |
content/blog/2021-03-30-vps-web-server.md → blog/vps-web-server/index.org renamed +168 −186
| @@ -1,35 +1,34 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-03-30 | |
| 3 | title = "How to Set Up a VPS Web Server" | |
| 4 | description = "A beginner's guide to setting up a virtual private server (VPS)." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Shared Hosting vs. VPS | |
| 1 | #+title: How to Set Up a VPS Web Server | |
| 2 | #+date: 2021-03-30 | |
| 3 | #+description: A beginner's guide to setting up a virtual private server (VPS). | |
| 4 | #+filetags: :sysadmin: | |
| 8 | 5 | |
| 6 | * Shared Hosting vs. VPS | |
| 9 | 7 | Choosing a place to host a website is one of the most confusing |
| 10 | 8 | decisions for beginner web developers. Even for experienced web devs, |
| 11 | 9 | choosing between different forms of web hosting can be a daunting |
| 12 | 10 | choice. |
| 13 | 11 | |
| 14 | First, let's take a look at [shared web | |
| 15 | hosting](https://en.wikipedia.org/wiki/Shared_web_hosting_service). | |
| 16 | Shared web hosting is a product where you are purchasing a small piece | |
| 17 | of a web server that is being shared between many websites. As a result, | |
| 18 | the cost of shared hosting is extremely low. You won't have access to | |
| 19 | the server itself, which means you can't install your own software on | |
| 20 | the server, such as Docker. Usually, you are simply allowed to connect | |
| 21 | your domains to the server, set up domain security, and other small | |
| 22 | utilities. | |
| 23 | ||
| 24 | In contrast, a [virtual private | |
| 25 | server](https://en.wikipedia.org/wiki/Virtual_private_server) (VPS) is a | |
| 26 | virtual machine that replicates the environment of having a dedicated | |
| 27 | server to yourself. You are able to control the virtual server's host | |
| 28 | names, base file system, package manager, etc. Another great upside of a | |
| 29 | VPS is that since it's virtual, the company providing the VPS can | |
| 30 | dynamically increase the disk size, RAM size, or number of CPUs at any | |
| 31 | time. However, the virtual server is still physically located on a | |
| 32 | server that is shared between multiple virtual servers. | |
| 12 | First, let's take a look at | |
| 13 | [[https://en.wikipedia.org/wiki/Shared_web_hosting_service][shared web | |
| 14 | hosting]]. Shared web hosting is a product where you are purchasing a | |
| 15 | small piece of a web server that is being shared between many websites. | |
| 16 | As a result, the cost of shared hosting is extremely low. You won't have | |
| 17 | access to the server itself, which means you can't install your own | |
| 18 | software on the server, such as Docker. Usually, you are simply allowed | |
| 19 | to connect your domains to the server, set up domain security, and other | |
| 20 | small utilities. | |
| 21 | ||
| 22 | In contrast, a | |
| 23 | [[https://en.wikipedia.org/wiki/Virtual_private_server][virtual private | |
| 24 | server]] (VPS) is a virtual machine that replicates the environment of | |
| 25 | having a dedicated server to yourself. You are able to control the | |
| 26 | virtual server's host names, base file system, package manager, etc. | |
| 27 | Another great upside of a VPS is that since it's virtual, the company | |
| 28 | providing the VPS can dynamically increase the disk size, RAM size, or | |
| 29 | number of CPUs at any time. However, the virtual server is still | |
| 30 | physically located on a server that is shared between multiple virtual | |
| 31 | servers. | |
| 33 | 32 | |
| 34 | 33 | The choice between shared hosting and VPS mostly depends on your skill |
| 35 | 34 | level with system administration. If you're comforting working on a |
| @@ -38,8 +37,7 @@ a VPS is usually a better option. However, shared hosting is a fantastic | ||
| 38 | 37 | option for people who don't want to have to learn how to manage their |
| 39 | 38 | server. |
| 40 | 39 | |
| 41 | ## My Situation | |
| 42 | ||
| 40 | * My Situation | |
| 43 | 41 | I had used shared hosting for approximately 5 years before trying my |
| 44 | 42 | first VPS. I manage a homelab and have had success running a server and |
| 45 | 43 | performing typical sysadmin duties, but I was still hesitant to get a |
| @@ -48,49 +46,48 @@ networking part of a server - DNS and hostname configurations were not | ||
| 48 | 46 | my friend. |
| 49 | 47 | |
| 50 | 48 | As a little bit of background, I originally used |
| 51 | [Siteground](https://www.siteground.com) for my initially shared hosting | |
| 52 | and stayed on that platform for at least a year. However, the UI was | |
| 53 | clunky, and I didn't like how they handled certain technical aspects, | |
| 54 | so I switched to [Namecheap](https://www.namecheap.com). Namecheap was | |
| 55 | great because it is the service I primarily use for purchasing domain | |
| 56 | names, which made it incredibly easy to link them to my hosting service. | |
| 57 | However, it was still mediocre shared hosting, and Namecheap is | |
| 58 | notorious for not letting you use [Let's | |
| 59 | Encrypt](https://letsencrypt.org) to obtain free SSL/TLS certificates; | |
| 60 | Namecheap wants to make you purchase certificates through their store. | |
| 61 | ||
| 62 | Finally, I settled down with [iWebFusion](https://www.iwebfusion.net) | |
| 49 | [[https://www.siteground.com][Siteground]] for my initially shared | |
| 50 | hosting and stayed on that platform for at least a year. However, the UI | |
| 51 | was clunky, and I didn't like how they handled certain technical | |
| 52 | aspects, so I switched to [[https://www.namecheap.com][Namecheap]]. | |
| 53 | Namecheap was great because it is the service I primarily use for | |
| 54 | purchasing domain names, which made it incredibly easy to link them to | |
| 55 | my hosting service. However, it was still mediocre shared hosting, and | |
| 56 | Namecheap is notorious for not letting you use | |
| 57 | [[https://letsencrypt.org][Let's Encrypt]] to obtain free SSL/TLS | |
| 58 | certificates; Namecheap wants to make you purchase certificates through | |
| 59 | their store. | |
| 60 | ||
| 61 | Finally, I settled down with [[https://www.iwebfusion.net][iWebFusion]] | |
| 63 | 62 | for about the last year of my shared hosting. This service was pretty |
| 64 | 63 | great, came with free SSL/TLS, and I never had any complaints. |
| 65 | 64 | |
| 66 | 65 | However, I finally grew tired of not being able to install software on |
| 67 | 66 | my own web server. I wanted to be able to try out things like |
| 68 | [Postmill](https://postmill.xyz) or [Matrix](https://matrix.org). This | |
| 69 | is possible with a VPS, so I decided to grab a new domain name to try it | |
| 70 | out. | |
| 71 | ||
| 72 | ## Getting Started: Buying a VPS | |
| 67 | [[https://postmill.xyz][Postmill]] or [[https://matrix.org][Matrix]]. | |
| 68 | This is possible with a VPS, so I decided to grab a new domain name to | |
| 69 | try it out. | |
| 73 | 70 | |
| 71 | * Getting Started: Buying a VPS | |
| 74 | 72 | The first step to moving over to a VPS is (you guessed it): finding a |
| 75 | VPS provider. For my VPSs, I use [1984](https://1984hosting.com) and | |
| 73 | VPS provider. For my VPSs, I use [[https://1984hosting.com][1984]] and | |
| 76 | 74 | prefer their services much more than any alternative, due to their |
| 77 | location (Iceland), their [privacy | |
| 78 | policy](https://1984hosting.com/GDPR/), their respect for GDPR, and the | |
| 79 | ability to remain anonymous if you pay in Bitcoin or Monero. | |
| 75 | location (Iceland), their [[https://1984hosting.com/GDPR/][privacy | |
| 76 | policy]], their respect for GDPR, and the ability to remain anonymous if | |
| 77 | you pay in Bitcoin or Monero. | |
| 80 | 78 | |
| 81 | [Njalla](https://njal.la) is another good, privacy-oriented option for | |
| 79 | [[https://njal.la][Njalla]] is another good, privacy-oriented option for | |
| 82 | 80 | VPS services. |
| 83 | 81 | |
| 84 | 82 | You'll have to decide what specifications you want on your VPS. For me, |
| 85 | 83 | I only build and deploy low-resource HTML, PHP, and Python websites. |
| 86 | 84 | This means I can survive on the smallest VPS: 1 CPU, 1GB of RAM, and |
| 87 | 25GB SSD for \$5.00 per month. | |
| 85 | 25GB SSD for $5.00 per month. | |
| 88 | 86 | |
| 89 | 87 | As noted above, the great thing about a VPS is you can request your |
| 90 | 88 | provider to increase the resources at any time. |
| 91 | 89 | |
| 92 | ## Configuring DNS Settings | |
| 93 | ||
| 90 | * Configuring DNS Settings | |
| 94 | 91 | Okay, so now let's get into some actual work that has to be done to get |
| 95 | 92 | content moved from a shared host to a VPS. At this point, I'm assuming |
| 96 | 93 | you have a shared host with website content that you can still access, |
| @@ -98,143 +95,135 @@ and you've purchased a new VPS and can SSH into that server. | ||
| 98 | 95 | |
| 99 | 96 | The first change is minor, but it should be done immediately in order to |
| 100 | 97 | get things moving: DNS settings. Go to wherever your DNS settings are |
| 101 | handled. If your shared host also managed your DNS settings, you'll | |
| 102 | need to first move that DNS over to your new VPS provider. For me, I | |
| 103 | route my DNS through [Gandi](https://www.gandi.net). | |
| 98 | handled. If your shared host also managed your DNS settings, you'll need | |
| 99 | to first move that DNS over to your new VPS provider. For me, I route my | |
| 100 | DNS through [[https://www.gandi.net][Gandi]]. | |
| 104 | 101 | |
| 105 | Once you know where your DNS settings are, go ahead and update the | |
| 106 | `A` records to match the public IP address of your VPS. For | |
| 107 | example: | |
| 102 | Once you know where your DNS settings are, go ahead and update the =A= | |
| 103 | records to match the public IP address of your VPS. For example: | |
| 108 | 104 | |
| 109 | ```txt | |
| 105 | #+begin_src txt | |
| 110 | 106 | A example.com xxx.xxx.xxx.xxx |
| 111 | 107 | A subdomain xxx.xxx.xxx.xxx |
| 112 | 108 | CNAME www example.com. |
| 113 | ``` | |
| 109 | #+end_src | |
| 114 | 110 | |
| 115 | 111 | If you have any other records that require updates, such as MX or TXT |
| 116 | 112 | records for a mail server, be sure to update those accordingly. |
| 117 | 113 | Personally, I don't host my own mail server. I route all mail on my |
| 118 | custom domains to [Migadu](https://www.migadu.com). Hosting your own | |
| 114 | custom domains to [[https://www.migadu.com][Migadu]]. Hosting your own | |
| 119 | 115 | email server can become complex quickly and is not for beginners. |
| 120 | 116 | |
| 121 | 117 | DNS changes can take up to 48 hours to propagate, so be sure to give it |
| 122 | 118 | some time before assuming you've made an error. |
| 123 | 119 | |
| 124 | ## Server Updates and Packages | |
| 125 | ||
| 120 | * Server Updates and Packages | |
| 126 | 121 | Now that the DNS settings have been changed, let's set up our server |
| 127 | 122 | while we wait for the DNS to propagate. First up is to ssh into your |
| 128 | 123 | server. If you've signed up with a service like DigitalOcean, you can |
| 129 | 124 | add your SSH key to your account and to your VPS droplet so that you |
| 130 | 125 | don't need a password in order to SSH. |
| 131 | 126 | |
| 132 | ```sh | |
| 127 | #+begin_src sh | |
| 133 | 128 | ssh root@xxx.xxx.xxx.xxx |
| 134 | ``` | |
| 129 | #+end_src | |
| 135 | 130 | |
| 136 | 131 | The VPS that is used in this blog post runs Ubuntu 20.04 with an Apache |
| 137 | 132 | web server. If you're working on a different operating system (OS) or |
| 138 | want a different web server, such as Nginx, you'll have to use | |
| 139 | different commands to set it up. | |
| 133 | want a different web server, such as Nginx, you'll have to use different | |
| 134 | commands to set it up. | |
| 140 | 135 | |
| 141 | 136 | First, let's update and upgrade our server. |
| 142 | 137 | |
| 143 | **NOTE:** Since we have logged in to the server as `root` for | |
| 144 | now, we don't need to use the `sudo` modifier before our | |
| 145 | commands. | |
| 138 | *NOTE:* Since we have logged in to the server as =root= for now, we | |
| 139 | don't need to use the =sudo= modifier before our commands. | |
| 146 | 140 | |
| 147 | ```sh | |
| 141 | #+begin_src sh | |
| 148 | 142 | apt update && apt upgrade -y |
| 149 | ``` | |
| 150 | ||
| 151 | ## Create A User Account | |
| 143 | #+end_src | |
| 152 | 144 | |
| 153 | While being able to use `root` can be beneficial at times, | |
| 154 | you shouldn't use `root` unless you have to. | |
| 145 | * Create A User Account | |
| 146 | While being able to use =root= can be beneficial at times, you shouldn't | |
| 147 | use =root= unless you have to. | |
| 155 | 148 | |
| 156 | So let's set up a new user in our system. The `-m` option | |
| 157 | below tells the OS to create a home directory for the new user. | |
| 149 | So let's set up a new user in our system. The =-m= option below tells | |
| 150 | the OS to create a home directory for the new user. | |
| 158 | 151 | |
| 159 | ```sh | |
| 152 | #+begin_src sh | |
| 160 | 153 | adduser USERNAME |
| 161 | ``` | |
| 154 | #+end_src | |
| 162 | 155 | |
| 163 | 156 | Now, create a password for that user. |
| 164 | 157 | |
| 165 | ```sh | |
| 158 | #+begin_src sh | |
| 166 | 159 | passwd USERNAME |
| 167 | ``` | |
| 160 | #+end_src | |
| 168 | 161 | |
| 169 | 162 | Finally, add the user to the sudoers file, so they can perform |
| 170 | 163 | priveleged commands. |
| 171 | 164 | |
| 172 | ```sh | |
| 165 | #+begin_src sh | |
| 173 | 166 | usermod -a -G sudo USERNAME |
| 174 | ``` | |
| 167 | #+end_src | |
| 175 | 168 | |
| 176 | 169 | If you are using SSH keys and not passwords, you'll need to copy your |
| 177 | 170 | SSH key from your local machine to the VPS. If you haven't disabled |
| 178 | password-based SSH yet, the easiest way to do this is | |
| 179 | `ssh-copy-id` from your local computer (not from the VPS): | |
| 171 | password-based SSH yet, the easiest way to do this is =ssh-copy-id= from | |
| 172 | your local computer (not from the VPS): | |
| 180 | 173 | |
| 181 | ```sh | |
| 174 | #+begin_src sh | |
| 182 | 175 | ssh-copy-id testuser@xxx.xxx.xxx.xxx |
| 183 | ``` | |
| 176 | #+end_src | |
| 184 | 177 | |
| 185 | If you've disabled password-based SSH, you'll need to manually copy | |
| 186 | your SSH key into the `~/.ssh/authorized_keys` file. | |
| 187 | ||
| 188 | ## Install Software | |
| 178 | If you've disabled password-based SSH, you'll need to manually copy your | |
| 179 | SSH key into the =~/.ssh/authorized_keys= file. | |
| 189 | 180 | |
| 181 | * Install Software | |
| 190 | 182 | Our goal here is to host a web server, so the next step is to install |
| 191 | 183 | the Apache web server and any other packages we need. |
| 192 | 184 | |
| 193 | From this point on, I will be logged in as a user (not | |
| 194 | `root`) and will need to use the `sudo` modifier | |
| 195 | for most commands. | |
| 185 | From this point on, I will be logged in as a user (not =root=) and will | |
| 186 | need to use the =sudo= modifier for most commands. | |
| 196 | 187 | |
| 197 | ```sh | |
| 188 | #+begin_src sh | |
| 198 | 189 | sudo apt update; sudo apt upgrade -y; sudo apt autoremove -y |
| 199 | 190 | sudo apt install apache2 |
| 200 | ``` | |
| 191 | #+end_src | |
| 201 | 192 | |
| 202 | 193 | If you need other language support, such as PHP, you'll need to install |
| 203 | 194 | that too. |
| 204 | 195 | |
| 205 | ```sh | |
| 196 | #+begin_src sh | |
| 206 | 197 | sudo apt install libapache2-mod-php php-dom |
| 207 | 198 | sudo a2enmod php |
| 208 | 199 | sudo systemctl restart apache2 |
| 209 | ``` | |
| 210 | ||
| 211 | ## Website Files & Folders | |
| 200 | #+end_src | |
| 212 | 201 | |
| 202 | * Website Files & Folders | |
| 213 | 203 | Next up is to create the directories for the domain(s) we want to be |
| 214 | 204 | hosted on this web server. |
| 215 | 205 | |
| 216 | ```sh | |
| 206 | #+begin_src sh | |
| 217 | 207 | cd /var/www |
| 218 | 208 | sudo mkdir example.com |
| 219 | ``` | |
| 209 | #+end_src | |
| 220 | 210 | |
| 221 | We have a folder for `example.com` now, so let's add an | |
| 222 | `index.html` file and put it within a specific | |
| 223 | `public_html` folder. You don't need this | |
| 224 | `public_html` if you don't want it, but it helps with | |
| 225 | organizing items related to `example.com` that you don't | |
| 226 | want to publish to the internet. | |
| 211 | We have a folder for =example.com= now, so let's add an =index.html= | |
| 212 | file and put it within a specific =public_html= folder. You don't need | |
| 213 | this =public_html= if you don't want it, but it helps with organizing | |
| 214 | items related to =example.com= that you don't want to publish to the | |
| 215 | internet. | |
| 227 | 216 | |
| 228 | ```sh | |
| 217 | #+begin_src sh | |
| 229 | 218 | cd example.com |
| 230 | 219 | sudo mkdir public_html && cd public_html |
| 231 | 220 | sudo nano index.html |
| 232 | ``` | |
| 221 | #+end_src | |
| 233 | 222 | |
| 234 | You can put anything you want in this `index.html` file. If | |
| 235 | you can't think of anything, paste this in there: | |
| 223 | You can put anything you want in this =index.html= file. If you can't | |
| 224 | think of anything, paste this in there: | |
| 236 | 225 | |
| 237 | ```html | |
| 226 | #+begin_src html | |
| 238 | 227 | <!DOCTYPE html> |
| 239 | 228 | <html lang="en"> |
| 240 | 229 | <head> |
| @@ -246,36 +235,34 @@ you can't think of anything, paste this in there: | ||
| 246 | 235 | <h1>Hello, world!</h1> |
| 247 | 236 | </body> |
| 248 | 237 | </html> |
| 249 | ``` | |
| 238 | #+end_src | |
| 250 | 239 | |
| 251 | If you want something to be served at | |
| 252 | `example.com/page01/file.txt`, you'll have to create the | |
| 253 | `page01` directory under the `example.com` | |
| 240 | If you want something to be served at =example.com/page01/file.txt=, | |
| 241 | you'll have to create the =page01= directory under the =example.com= | |
| 254 | 242 | directory. For example: |
| 255 | 243 | |
| 256 | ```sh | |
| 244 | #+begin_src sh | |
| 257 | 245 | cd /var/www/example.com/public_html |
| 258 | 246 | sudo mkdir page01 |
| 259 | 247 | sudo nano file.txt |
| 260 | ``` | |
| 261 | ||
| 262 | ## Apache Configuration | |
| 248 | #+end_src | |
| 263 | 249 | |
| 250 | * Apache Configuration | |
| 264 | 251 | Now, let's set up the files that will tell the server where to find the |
| 265 | files for `example.com`. We will copy the default | |
| 266 | configuration file and create our own. | |
| 252 | files for =example.com=. We will copy the default configuration file and | |
| 253 | create our own. | |
| 267 | 254 | |
| 268 | ```sh | |
| 255 | #+begin_src sh | |
| 269 | 256 | cd /etc/apache2/sites-available |
| 270 | 257 | sudo cp 000-default.conf example.com.conf |
| 271 | 258 | sudo nano example.com.conf |
| 272 | ``` | |
| 259 | #+end_src | |
| 273 | 260 | |
| 274 | 261 | This configuration file will have a few default lines, but you'll need |
| 275 | 262 | to edit it to look similar to this (settings may change based on your |
| 276 | 263 | personal needs): |
| 277 | 264 | |
| 278 | ```config | |
| 265 | #+begin_src config | |
| 279 | 266 | <VirtualHost *:80> |
| 280 | 267 | ServerAdmin your-email@email-provider.com |
| 281 | 268 | ServerName example.com |
| @@ -284,85 +271,82 @@ personal needs): | ||
| 284 | 271 | ErrorLog ${APACHE_LOG_DIR}/error.log |
| 285 | 272 | CustomLog ${APACHE_LOG_DIR}/access.log combined |
| 286 | 273 | </VirtualHost> |
| 287 | ``` | |
| 274 | #+end_src | |
| 288 | 275 | |
| 289 | 276 | Now, enable the configuration for your new site, disable the default |
| 290 | 277 | configuration, and reload the web server. |
| 291 | 278 | |
| 292 | ```sh | |
| 279 | #+begin_src sh | |
| 293 | 280 | sudo a2ensite example.com.conf |
| 294 | 281 | sudo a2dissite 000-default.conf |
| 295 | 282 | sudo systemctl reload apache2 |
| 296 | ``` | |
| 283 | #+end_src | |
| 297 | 284 | |
| 298 | 285 | You can always run a test to make sure no errors or warnings are found |
| 299 | 286 | in your configuration files. |
| 300 | 287 | |
| 301 | ```sh | |
| 288 | #+begin_src sh | |
| 302 | 289 | sudo apache2ctl configtest |
| 303 | ``` | |
| 290 | #+end_src | |
| 304 | 291 | |
| 305 | 292 | Now, restart the web server entirely. After this, you should be able to |
| 306 | browse to `http://example.com` and see the HTML content you | |
| 307 | provided earlier. Note that SSL/TLS has not been enabled yet, so you | |
| 308 | won't be able to use the secure version yet | |
| 309 | (`https://example.com`). | |
| 293 | browse to =http://example.com= and see the HTML content you provided | |
| 294 | earlier. Note that SSL/TLS has not been enabled yet, so you won't be | |
| 295 | able to use the secure version yet (=https://example.com=). | |
| 310 | 296 | |
| 311 | ```sh | |
| 297 | #+begin_src sh | |
| 312 | 298 | sudo systemctl restart apache2 |
| 313 | ``` | |
| 299 | #+end_src | |
| 314 | 300 | |
| 315 | 301 | You can repeat this for as many websites as you need. Just create the |
| 316 | domain folders in `/var/www/`, add the configuration file, | |
| 317 | enable the configuration, and restart `apache2`. | |
| 318 | ||
| 319 | ## SSL/TLS Certificates: Serve Websites Over HTTPS | |
| 302 | domain folders in =/var/www/=, add the configuration file, enable the | |
| 303 | configuration, and restart =apache2=. | |
| 320 | 304 | |
| 305 | * SSL/TLS Certificates: Serve Websites Over HTTPS | |
| 321 | 306 | In order to serve secure content, you'll need to obtain SSL/TLS |
| 322 | 307 | certificates. Luckily, there's a free tool called |
| 323 | [Certbot](https://certbot.eff.org) that helps us with the process. | |
| 308 | [[https://certbot.eff.org][Certbot]] that helps us with the process. | |
| 324 | 309 | |
| 325 | The first step is to install `snapd` and `core` | |
| 326 | for Ubuntu. | |
| 310 | The first step is to install =snapd= and =core= for Ubuntu. | |
| 327 | 311 | |
| 328 | ```sh | |
| 312 | #+begin_src sh | |
| 329 | 313 | sudo apt install snapd |
| 330 | 314 | sudo snap install core |
| 331 | 315 | sudo snap refresh core |
| 332 | ``` | |
| 316 | #+end_src | |
| 333 | 317 | |
| 334 | Next, install the `certbot` snap package. | |
| 318 | Next, install the =certbot= snap package. | |
| 335 | 319 | |
| 336 | ```sh | |
| 320 | #+begin_src sh | |
| 337 | 321 | sudo snap install --classic certbot |
| 338 | ``` | |
| 322 | #+end_src | |
| 339 | 323 | |
| 340 | Execute the following command to ensure that the `certbot` | |
| 341 | command can be run. | |
| 324 | Execute the following command to ensure that the =certbot= command can | |
| 325 | be run. | |
| 342 | 326 | |
| 343 | ```sh | |
| 327 | #+begin_src sh | |
| 344 | 328 | sudo ln -s /snap/bin/certbot /usr/bin/certbot |
| 345 | ``` | |
| 329 | #+end_src | |
| 346 | 330 | |
| 347 | Finally, you can run `certbot` one of two ways: | |
| 331 | Finally, you can run =certbot= one of two ways: | |
| 348 | 332 | |
| 349 | 1. run it and let it alter your Apache configuration files | |
| 350 | automatically to enable HTTPS redirects. | |
| 351 | 2. run it and only allow it to create certificates. You'll need to | |
| 352 | manually alter the config files to enable HTTPS redirects. | |
| 333 | 1. run it and let it alter your Apache configuration files automatically | |
| 334 | to enable HTTPS redirects. | |
| 335 | 2. run it and only allow it to create certificates. You'll need to | |
| 336 | manually alter the config files to enable HTTPS redirects. | |
| 353 | 337 | |
| 354 | 338 | Run certbot and allow automatic config changes: |
| 355 | 339 | |
| 356 | ```sh | |
| 340 | #+begin_src sh | |
| 357 | 341 | sudo certbot --apache |
| 358 | ``` | |
| 342 | #+end_src | |
| 359 | 343 | |
| 360 | 344 | Run certbot for certificates only and don't allow it to alter config |
| 361 | 345 | files: |
| 362 | 346 | |
| 363 | ```sh | |
| 347 | #+begin_src sh | |
| 364 | 348 | sudo certbot certonly --apache |
| 365 | ``` | |
| 349 | #+end_src | |
| 366 | 350 | |
| 367 | 351 | The Certbot packages on your system come with a cron job or systemd |
| 368 | 352 | timer that will renew your certificates automatically before they |
| @@ -370,48 +354,46 @@ expire. You will not need to run Certbot again unless you change your | ||
| 370 | 354 | configuration. You can test automatic renewal for your certificates by |
| 371 | 355 | running this command: |
| 372 | 356 | |
| 373 | ```sh | |
| 357 | #+begin_src sh | |
| 374 | 358 | sudo certbot renew --dry-run |
| 375 | ``` | |
| 376 | ||
| 377 | Now, test your domains by going to `https://example.com`. | |
| 359 | #+end_src | |
| 378 | 360 | |
| 379 | ## Firewall Security | |
| 361 | Now, test your domains by going to =https://example.com=. | |
| 380 | 362 | |
| 363 | * Firewall Security | |
| 381 | 364 | To enable better security on your server, you'll need to enable a basic |
| 382 | firewall. For Ubuntu, we'll use [the uncomplicated | |
| 383 | firewall](https://cleberg.net/blog/secure-your-network-with-the-uncomplicated-firewall.html). | |
| 365 | firewall. For Ubuntu, we'll use | |
| 366 | [[../secure-your-network-with-the-uncomplicated-firewall/][the | |
| 367 | uncomplicated firewall]]. | |
| 384 | 368 | |
| 385 | 369 | Now, add the following rules to the firewall allow SSH, Apache, and |
| 386 | 370 | HTTP(S) connections. If you need to, you can enable different ports for |
| 387 | 371 | specifics applications, SFTP, etc. |
| 388 | 372 | |
| 389 | ```sh | |
| 373 | #+begin_src sh | |
| 390 | 374 | sudo ufw default deny incoming |
| 391 | 375 | sudo ufw default allow outgoing |
| 392 | 376 | sudo ufw allow OpenSSH |
| 393 | 377 | sudo ufw allow Apache |
| 394 | 378 | sudo ufw allow proto tcp from any to any port 80,443 |
| 395 | ``` | |
| 379 | #+end_src | |
| 396 | 380 | |
| 397 | 381 | Once you've added all the rules you need, enable the firewall. |
| 398 | 382 | |
| 399 | ```sh | |
| 383 | #+begin_src sh | |
| 400 | 384 | sudo ufw enable |
| 401 | ``` | |
| 402 | ||
| 403 | ## Troubleshooting | |
| 385 | #+end_src | |
| 404 | 386 | |
| 387 | * Troubleshooting | |
| 405 | 388 | If you run into any issues during your VPS set-up, be sure to walk back |
| 406 | 389 | through your actions and make sure you didn't miss any steps. |
| 407 | 390 | |
| 408 | 391 | Many websites have fantastic guides to setting up various web servers. |
| 409 | This is one of the areas [where DigitalOcean | |
| 410 | shines](https://www.digitalocean.%20com/community/tutorials). For | |
| 411 | simpler or more Linux-oriented questions, I suggest using [Linuxize] | |
| 412 | (<https://linuxize.com>). | |
| 413 | ||
| 414 | If you're getting certain errors (e.g. =500 Internal Server Error=) and | |
| 415 | need to debug locally, you can view the `access.log` and | |
| 416 | `error.log` files in the `/var/log/apache/` | |
| 417 | directory. | |
| 392 | This is one of the areas | |
| 393 | [[https://www.digitalocean.%20com/community/tutorials][where | |
| 394 | DigitalOcean shines]]. For simpler or more Linux-oriented questions, I | |
| 395 | suggest using [Linuxize] ([[https://linuxize.com]]). | |
| 396 | ||
| 397 | If you're getting certain errors (e.g. =500 Internal Server Error=) and | |
| 398 | need to debug locally, you can view the =access.log= and =error.log= | |
| 399 | files in the =/var/log/apache/= directory. | |
content/blog/2020-12-27-website-redesign.md → blog/website-redesign/index.org renamed +34 −40
| @@ -1,11 +1,9 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-12-27 | |
| 3 | title = "Redesigning My Website: The 5 KB Result" | |
| 4 | description = "A retrospective on my recent website redesign." | |
| 5 | +++ | |
| 6 | ||
| 7 | # A Brief History | |
| 1 | #+title: Redesigning My Website: The 5 KB Result | |
| 2 | #+date: 2020-12-27 | |
| 3 | #+description: A retrospective on my recent website redesign. | |
| 4 | #+filetags: :sysadmin: | |
| 8 | 5 | |
| 6 | * A Brief History | |
| 9 | 7 | As a form of continuous learning and entertainment, I've been running a |
| 10 | 8 | handful of websites since 2016 when I took my first programming courses |
| 11 | 9 | in college. I maintain one main website, the place I consider the |
| @@ -14,35 +12,33 @@ subdirectories and subdomains. | ||
| 14 | 12 | |
| 15 | 13 | One of the parts I've enjoyed the most about web development is the |
| 16 | 14 | aspect of designing an identity for a web page and working to find |
| 17 | exciting ways to display the site's content. Inevitably, this means | |
| 18 | I've changed the designs for my websites more times than I could | |
| 19 | possibly count. Since I don't really host anything on my main webpage | |
| 20 | that's vital, it allows me the freedom to change things as inspiration | |
| 21 | strikes. | |
| 15 | exciting ways to display the site's content. Inevitably, this means I've | |
| 16 | changed the designs for my websites more times than I could possibly | |
| 17 | count. Since I don't really host anything on my main webpage that's | |
| 18 | vital, it allows me the freedom to change things as inspiration strikes. | |
| 22 | 19 | |
| 23 | Historically, I've relied on core utilities for spacing, components, | |
| 24 | and layouts from [Bootstrap](https://getbootstrap.com) and added custom | |
| 20 | Historically, I've relied on core utilities for spacing, components, and | |
| 21 | layouts from [[https://getbootstrap.com][Bootstrap]] and added custom | |
| 25 | 22 | CSS for fonts, accents, colors, and other items. I also tend to create |
| 26 | 23 | sites with no border radius on items, visible borders, and content that |
| 27 | 24 | takes up the entire screen (using whitespace inside components instead |
| 28 | 25 | of whitespace around my components). |
| 29 | 26 | |
| 30 | # The Redesign Process | |
| 31 | ||
| 27 | * The Redesign Process | |
| 32 | 28 | About a week ago, I found myself wishing for a new design yet again. The |
| 33 | prior design was largely inspired by IBM's [Carbon Design | |
| 34 | System](https://www.carbondesignsystem.com) and relied on jQuery, | |
| 35 | Bootstrap, along with some compressed | |
| 36 | [.webp](https://en.wikipedia.org/wiki/WebP) images. | |
| 29 | prior design was largely inspired by IBM's | |
| 30 | [[https://www.carbondesignsystem.com][Carbon Design System]] and relied | |
| 31 | on jQuery, Bootstrap, along with some compressed | |
| 32 | [[https://en.wikipedia.org/wiki/WebP][.webp]] images. | |
| 37 | 33 | |
| 38 | 34 | To anyone who knows my preferences toward web design - and even in my |
| 39 | 35 | personal life - it should be no surprise that I immediately started |
| 40 | 36 | looking for inspiration on minimalism. While there are some decent |
| 41 | 37 | minimalistic designs on sites like |
| 42 | [Dribbble](https://dribbble.com/search/shots/popular/web-design?q=minimalism), | |
| 43 | people seem to mostly discuss [brutalist web | |
| 44 | design](https://brutalist-web.design) when you ask about minimalism. | |
| 45 | While brutalist web design doesn't have to be minimal, it often is. | |
| 38 | [[https://dribbble.com/search/shots/popular/web-design?q=minimalism][Dribbble]], | |
| 39 | people seem to mostly discuss [[https://brutalist-web.design][brutalist | |
| 40 | web design]] when you ask about minimalism. While brutalist web design | |
| 41 | doesn't have to be minimal, it often is. | |
| 46 | 42 | |
| 47 | 43 | I suppose, in a way, I did create a brutalist website since my HTML is |
| 48 | 44 | semantic and accessible, hyperlinks are colored and underlined, and all |
| @@ -64,28 +60,26 @@ also helped to move all categories to a single page, rather than have | ||
| 64 | 60 | each category on its own page. |
| 65 | 61 | |
| 66 | 62 | The final big piece to finish the |
| 67 | "[KonMari](https://en.wikipedia.org/wiki/Marie_Kondo#KonMari_method)"-like | |
| 63 | "[[https://en.wikipedia.org/wiki/Marie_Kondo#KonMari_method][KonMari]]"-like | |
| 68 | 64 | part of my process was to remove Bootstrap CSS in its entirety. However, |
| 69 | this meant pulling out a few very useful classes, such as `.img-fluid` | |
| 65 | this meant pulling out a few very useful classes, such as =.img-fluid= | |
| 70 | 66 | and the default font stacks to keep in my custom CSS. |
| 71 | 67 | |
| 72 | 68 | After removing all the unnecessary pieces, I was finally able to |
| 73 | 69 | reorganize my content and add a very small amount of custom CSS to make |
| 74 | 70 | everything pretty. This took a brief amount of time, effectively just |
| 75 | consisting of me converting `<div>` tags into things like | |
| 76 | `<ul>` lists and choosing accent colors. | |
| 77 | ||
| 78 | # The Results | |
| 79 | ||
| 80 | ## Reflection | |
| 71 | consisting of me converting =<div>= tags into things like =<ul>= lists | |
| 72 | and choosing accent colors. | |
| 81 | 73 | |
| 74 | * The Results | |
| 75 | ** Reflection | |
| 82 | 76 | So, what did all of this reorganizing do to my webpages? Well, first, my |
| 83 | websites are now **ridiculously fast**. Since the prior designs were | |
| 84 | also minimal and didn't have many images, they measured up in | |
| 85 | Firefox's Network Monitor around 300 KB - 600KB. After making the | |
| 86 | changes, my main site is at 5 KB transferred (22 KB total), and my blog | |
| 87 | is at 6.5 KB transferred (13 KB total). **That means the redesigned | |
| 88 | pages are less than 2% the size of the old designs.** | |
| 77 | websites are now *ridiculously fast*. Since the prior designs were also | |
| 78 | minimal and didn't have many images, they measured up in Firefox's | |
| 79 | Network Monitor around 300 KB - 600KB. After making the changes, my main | |
| 80 | site is at 5 KB transferred (22 KB total), and my blog is at 6.5 KB | |
| 81 | transferred (13 KB total). *That means the redesigned pages are less | |
| 82 | than 2% the size of the old designs.* | |
| 89 | 83 | |
| 90 | 84 | Google Lighthouse ranks the new webpage as 100 in performance, |
| 91 | 85 | accessibility, and best practices, with SEO at 92 since they think tap |
| @@ -98,5 +92,5 @@ separate CSS file, and the CSS for my main website is simply embedded in | ||
| 98 | 92 | the HTML file. |
| 99 | 93 | |
| 100 | 94 | Now that everything is complete, I can confidently say I'm happy with |
| 101 | the result and proud to look at the fastest set of websites I've | |
| 102 | created so far. | |
| 95 | the result and proud to look at the fastest set of websites I've created | |
| 96 | so far. | |
content/blog/2023-07-12-mullvad-wireguard-lan.md → blog/wireguard-lan/index.org renamed +54 −55
| @@ -1,30 +1,28 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-07-12 | |
| 3 | title = "Enable LAN Access in Mullvad Wireguard Conf Files" | |
| 4 | description = "Learn how to enable LAN access manually in Mullvad configuration files." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Download Configuration Files from Mullvad | |
| 8 | ||
| 9 | To begin, you'll need [Wireguard configuration files from | |
| 10 | Mullvad](https://mullvad.net/account/wireguard-config). You can choose | |
| 11 | any of the options as you download them. For example, I enabled the kill | |
| 12 | switch, selected all countries, and selected a few content filters. | |
| 1 | #+title: Enable LAN Access in Mullvad Wireguard Conf Files | |
| 2 | #+date: 2023-07-12 | |
| 3 | #+description: Learn how to enable LAN access manually in Mullvad configuration files. | |
| 4 | #+filetags: :linux: | |
| 5 | ||
| 6 | * Download Configuration Files from Mullvad | |
| 7 | To begin, you'll need | |
| 8 | [[https://mullvad.net/account/wireguard-config][Wireguard configuration | |
| 9 | files from Mullvad]]. You can choose any of the options as you download | |
| 10 | them. For example, I enabled the kill switch, selected all countries, | |
| 11 | and selected a few content filters. | |
| 13 | 12 | |
| 14 | 13 | Once downloaded, unzip the files and move them to the Wireguard folder |
| 15 | 14 | on your system. |
| 16 | 15 | |
| 17 | ```sh | |
| 16 | #+begin_src sh | |
| 18 | 17 | cd ~/Downloads |
| 19 | 18 | unzip mullvad_wireguard_linux_all_all.zip |
| 20 | 19 | doas mv *.conf /etc/wireguard/ |
| 21 | ``` | |
| 22 | ||
| 23 | ### Configuration File Layout | |
| 20 | #+end_src | |
| 24 | 21 | |
| 22 | ** Configuration File Layout | |
| 25 | 23 | The default configuration files will look something like this: |
| 26 | 24 | |
| 27 | ```conf | |
| 25 | #+begin_src conf | |
| 28 | 26 | [Interface] |
| 29 | 27 | # Device: <redacted> |
| 30 | 28 | PrivateKey = <redacted> |
| @@ -37,45 +35,46 @@ PreDown = iptables -D OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m ad | ||
| 37 | 35 | PublicKey = <redacted> |
| 38 | 36 | AllowedIPs = <redacted> |
| 39 | 37 | Endpoint = <redacted> |
| 40 | ``` | |
| 38 | #+end_src | |
| 41 | 39 | |
| 42 | > Note: If you didn't select the kill switch option, you won't see the | |
| 43 | > `PostUp` and `PreDown` lines. In this case, | |
| 44 | > you'll need to modify the script below to simply append those lines | |
| 45 | > to the `[Interface]` block. | |
| 46 | ||
| 47 | ## Editing the Configuration Files | |
| 40 | #+begin_quote | |
| 41 | Note: If you didn't select the kill switch option, you won't see the | |
| 42 | =PostUp= and =PreDown= lines. In this case, you'll need to modify the | |
| 43 | script below to simply append those lines to the =[Interface]= block. | |
| 44 | #+end_quote | |
| 48 | 45 | |
| 46 | * Editing the Configuration Files | |
| 49 | 47 | Once you have the files, you'll need to edit them and replace the |
| 50 | `PostUp` and `PreDown` lines to enable LAN access. | |
| 48 | =PostUp= and =PreDown= lines to enable LAN access. | |
| 51 | 49 | |
| 52 | 50 | I recommend that you do this process as root, since you'll need to be |
| 53 | able to access files in `/etc/wireguard`, which are generally | |
| 54 | owned by root. You can also try using `sudo` or | |
| 55 | `doas`, but I didn't test that scenario so you may need to | |
| 56 | adjust, as necessary. | |
| 51 | able to access files in =/etc/wireguard=, which are generally owned by | |
| 52 | root. You can also try using =sudo= or =doas=, but I didn't test that | |
| 53 | scenario so you may need to adjust, as necessary. | |
| 57 | 54 | |
| 58 | ```sh | |
| 55 | #+begin_src sh | |
| 59 | 56 | su |
| 60 | ``` | |
| 57 | #+end_src | |
| 61 | 58 | |
| 62 | 59 | Create the Python file that we'll be using to update the Wireguard |
| 63 | 60 | configuration files. |
| 64 | 61 | |
| 65 | ```sh | |
| 62 | #+begin_src sh | |
| 66 | 63 | nano replace.py |
| 67 | ``` | |
| 64 | #+end_src | |
| 68 | 65 | |
| 69 | 66 | Within the Python file, copy and paste the logic below. This script will |
| 70 | 67 | open a directory, loop through every configuration file within the |
| 71 | directory, and replace the `PostUp` and `PreDown` | |
| 72 | lines with the new LAN-enabled iptables commands. | |
| 68 | directory, and replace the =PostUp= and =PreDown= lines with the new | |
| 69 | LAN-enabled iptables commands. | |
| 70 | ||
| 71 | #+begin_quote | |
| 72 | Note: If your LAN is on a subnet other than =192.168.1.0/24=, you'll | |
| 73 | need to update the Python script below appropriately. | |
| 73 | 74 | |
| 74 | > Note: If your LAN is on a subnet other than | |
| 75 | > `192.168.1.0/24`, you'll need to update the Python script | |
| 76 | > below appropriately. | |
| 75 | #+end_quote | |
| 77 | 76 | |
| 78 | ```python | |
| 77 | #+begin_src python | |
| 79 | 78 | import os |
| 80 | 79 | import fileinput |
| 81 | 80 | |
| @@ -94,25 +93,25 @@ for file in os.listdir(dir): | ||
| 94 | 93 | print(line, end="") |
| 95 | 94 | |
| 96 | 95 | print("--- done ---") |
| 97 | ``` | |
| 96 | #+end_src | |
| 98 | 97 | |
| 99 | 98 | Once you're done, save and close the file. You can now run the Python |
| 100 | 99 | script and watch as each file is updated. |
| 101 | 100 | |
| 102 | ```sh | |
| 101 | #+begin_src sh | |
| 103 | 102 | python3 replace.py |
| 104 | ``` | |
| 103 | #+end_src | |
| 105 | 104 | |
| 106 | To confirm it worked, you can `cat` one of the configuration | |
| 107 | files to inspect the new logic and connect to one to test it out. | |
| 105 | To confirm it worked, you can =cat= one of the configuration files to | |
| 106 | inspect the new logic and connect to one to test it out. | |
| 108 | 107 | |
| 109 | ```sh | |
| 108 | #+begin_src sh | |
| 110 | 109 | cat /etc/wireguard/us-chi-wg-001.conf |
| 111 | ``` | |
| 110 | #+end_src | |
| 112 | 111 | |
| 113 | 112 | The configuration files should now look like this: |
| 114 | 113 | |
| 115 | ```conf | |
| 114 | #+begin_src conf | |
| 116 | 115 | [Interface] |
| 117 | 116 | # Device: <redacted> |
| 118 | 117 | PrivateKey = <redacted> |
| @@ -125,20 +124,20 @@ PreDown = iptables -D OUTPUT ! -o %i -m mark ! --mark $(wg show %i fwmark) -m ad | ||
| 125 | 124 | PublicKey = <redacted> |
| 126 | 125 | AllowedIPs = <redacted> |
| 127 | 126 | Endpoint = <redacted> |
| 128 | ``` | |
| 127 | #+end_src | |
| 129 | 128 | |
| 130 | If you connect to a Wireguard interface, such as | |
| 131 | `us-chi-wg-001`, you can test your SSH functionality and see | |
| 132 | that it works even while on the VPN. | |
| 129 | If you connect to a Wireguard interface, such as =us-chi-wg-001=, you | |
| 130 | can test your SSH functionality and see that it works even while on the | |
| 131 | VPN. | |
| 133 | 132 | |
| 134 | ```sh | |
| 133 | #+begin_src sh | |
| 135 | 134 | wg-quick up us-chi-wg-001 |
| 136 | 135 | ssh user@lan-host |
| 137 | ``` | |
| 136 | #+end_src | |
| 138 | 137 | |
| 139 | 138 | To confirm your VPN connection, you can curl Mullvad's connection API: |
| 140 | 139 | |
| 141 | ```sh | |
| 140 | #+begin_src sh | |
| 142 | 141 | curl https://am.i.mullvad.net/connected |
| 143 | 142 | # You are connected to Mullvad (server us-chi-wg-001). Your IP address is <redacted> |
| 144 | ``` | |
| 143 | #+end_src | |
content/blog/2024-02-06-zfs.md → blog/zfs/index.org renamed +134 −131
| @@ -1,42 +1,43 @@ | ||
| 1 | +++ | |
| 2 | date = 2024-02-06 | |
| 3 | title = "How to Create a ZFS Pool on Ubuntu Linux" | |
| 4 | description = "Learn how to create a simple ZFS pool on Ubuntu Linux." | |
| 5 | +++ | |
| 1 | #+title: How to Create a ZFS Pool on Ubuntu Linux | |
| 2 | #+date: 2024-02-06 | |
| 3 | #+description: Learn how to create a simple ZFS pool on Ubuntu Linux. | |
| 4 | #+filetags: :linux: | |
| 6 | 5 | |
| 7 | 6 | This post details the process I used to create ZFS pools, datasets, and |
| 8 | 7 | snapshots on Ubuntu Server. |
| 9 | 8 | |
| 10 | I found the following pages very helpful while going through this process: | |
| 9 | I found the following pages very helpful while going through this | |
| 10 | process: | |
| 11 | 11 | |
| 12 | - [Setup a ZFS storage pool](https://ubuntu.com/tutorials/setup-zfs-storage-pool) | |
| 13 | - [Kernel/Reference/ZFS](https://wiki.ubuntu.com/Kernel/Reference/ZFS) | |
| 14 | - [ZFS for Dummies](https://blog.victormendonca.com/2020/11/03/zfs-for-dummies/) | |
| 15 | ||
| 16 | ## Installation | |
| 12 | - [[https://ubuntu.com/tutorials/setup-zfs-storage-pool][Setup a ZFS | |
| 13 | storage pool]] | |
| 14 | - [[https://wiki.ubuntu.com/Kernel/Reference/ZFS][Kernel/Reference/ZFS]] | |
| 15 | - [[https://blog.victormendonca.com/2020/11/03/zfs-for-dummies/][ZFS for | |
| 16 | Dummies]] | |
| 17 | 17 | |
| 18 | * Installation | |
| 18 | 19 | To start, I installed the ZFS package with the following command: |
| 19 | 20 | |
| 20 | ```sh | |
| 21 | #+begin_src sh | |
| 21 | 22 | sudo apt install zfsutils-linux |
| 22 | ``` | |
| 23 | #+end_src | |
| 23 | 24 | |
| 24 | Once installed, you can check the version to see if it installed correctly. | |
| 25 | Once installed, you can check the version to see if it installed | |
| 26 | correctly. | |
| 25 | 27 | |
| 26 | ```sh | |
| 28 | #+begin_src sh | |
| 27 | 29 | > zsf --version |
| 28 | 30 | |
| 29 | 31 | zfs-2.1.5-1ubuntu6~22.04.2 |
| 30 | 32 | zfs-kmod-2.1.5-1ubuntu6~22.04.1 |
| 31 | ``` | |
| 32 | ||
| 33 | ## ZFS Configuration | |
| 33 | #+end_src | |
| 34 | 34 | |
| 35 | * ZFS Configuration | |
| 35 | 36 | Now that ZFS is installed, we can create and configure the pool. |
| 36 | 37 | |
| 37 | You have various options for configuring ZFS pools that all come different pros | |
| 38 | and cons. I suggest visiting the links at the top of this post or searching | |
| 39 | online for the best configuration for your use-case. | |
| 38 | You have various options for configuring ZFS pools that all come | |
| 39 | different pros and cons. I suggest visiting the links at the top of this | |
| 40 | post or searching online for the best configuration for your use-case. | |
| 40 | 41 | |
| 41 | 42 | - Striped VDEVs (Raid0) |
| 42 | 43 | - Mirrored VDEVs (Raid1) |
| @@ -46,22 +47,21 @@ online for the best configuration for your use-case. | ||
| 46 | 47 | - RAIDz3 |
| 47 | 48 | - Nested RAIDz (Raid50, Raid60) |
| 48 | 49 | |
| 49 | I will be using Raid10 in this guide. However, the majority of the steps are the | |
| 50 | same regardless of your chosen pool configuration. | |
| 51 | ||
| 52 | ### Creating the Pool | |
| 50 | I will be using Raid10 in this guide. However, the majority of the steps | |
| 51 | are the same regardless of your chosen pool configuration. | |
| 53 | 52 | |
| 54 | To start, let's list the disks available to use. You can use `fdisk` command to | |
| 55 | see all available disks. | |
| 53 | ** Creating the Pool | |
| 54 | To start, let's list the disks available to use. You can use =fdisk= | |
| 55 | command to see all available disks. | |
| 56 | 56 | |
| 57 | ```sh | |
| 57 | #+begin_src sh | |
| 58 | 58 | sudo fdisk -l |
| 59 | ``` | |
| 59 | #+end_src | |
| 60 | 60 | |
| 61 | Or, if you currently have them mounted, you can use the `df` command to view | |
| 62 | your disks. | |
| 61 | Or, if you currently have them mounted, you can use the =df= command to | |
| 62 | view your disks. | |
| 63 | 63 | |
| 64 | ```sh | |
| 64 | #+begin_src sh | |
| 65 | 65 | > sudo df -h |
| 66 | 66 | |
| 67 | 67 | Filesystem Size Used Avail Use% Mounted on |
| @@ -72,116 +72,118 @@ Filesystem Size Used Avail Use% Mounted on | ||
| 72 | 72 | /dev/sdd1 9.1T 8.7T 435G 96% /mnt/white-01 |
| 73 | 73 | /dev/sde1 7.3T 28K 6.9T 1% /mnt/red-03 |
| 74 | 74 | /dev/sdf1 7.3T 28K 6.9T 1% /mnt/red-04 |
| 75 | ``` | |
| 75 | #+end_src | |
| 76 | 76 | |
| 77 | If you're going to use mounted disks, make sure to umount them before creating | |
| 78 | the pool. | |
| 77 | If you're going to use mounted disks, make sure to umount them before | |
| 78 | creating the pool. | |
| 79 | 79 | |
| 80 | ```sh | |
| 80 | #+begin_src sh | |
| 81 | 81 | sudo umount /dev/sda1 |
| 82 | 82 | sudo umount /dev/sdb1 |
| 83 | ``` | |
| 83 | #+end_src | |
| 84 | 84 | |
| 85 | Now that I've identified the disks I want to use and have them unmounted, let's | |
| 86 | create the pool. For this example, I will call it `tank`. | |
| 85 | Now that I've identified the disks I want to use and have them | |
| 86 | unmounted, let's create the pool. For this example, I will call it | |
| 87 | =tank=. | |
| 87 | 88 | |
| 88 | ```sh | |
| 89 | #+begin_src sh | |
| 89 | 90 | sudo zpool create -f -m /mnt/pool tank mirror /dev/sda /dev/sdb |
| 90 | ``` | |
| 91 | #+end_src | |
| 91 | 92 | |
| 92 | See below for the results of the new ZFS pool named `tank`, with a vdev | |
| 93 | automatically named `mirror-0`. | |
| 93 | See below for the results of the new ZFS pool named =tank=, with a vdev | |
| 94 | automatically named =mirror-0=. | |
| 94 | 95 | |
| 95 | ```sh | |
| 96 | #+begin_src sh | |
| 96 | 97 | > zfs list |
| 97 | 98 | |
| 98 | 99 | NAME USED AVAIL REFER MOUNTPOINT |
| 99 | 100 | tank 396K 7.14T 96K /tank |
| 100 | ``` | |
| 101 | #+end_src | |
| 101 | 102 | |
| 102 | ```sh | |
| 103 | #+begin_src sh | |
| 103 | 104 | > zpool status |
| 104 | 105 | |
| 105 | 106 | pool: tank |
| 106 | 107 | state: ONLINE |
| 107 | 108 | config: |
| 108 | 109 | |
| 109 | NAME STATE READ WRITE CKSUM | |
| 110 | tank ONLINE 0 0 0 | |
| 111 | mirror-0 ONLINE 0 0 0 | |
| 112 | sda ONLINE 0 0 0 | |
| 113 | sdb ONLINE 0 0 0 | |
| 110 | NAME STATE READ WRITE CKSUM | |
| 111 | tank ONLINE 0 0 0 | |
| 112 | mirror-0 ONLINE 0 0 0 | |
| 113 | sda ONLINE 0 0 0 | |
| 114 | sdb ONLINE 0 0 0 | |
| 114 | 115 | |
| 115 | 116 | errors: No known data errors |
| 116 | ``` | |
| 117 | #+end_src | |
| 117 | 118 | |
| 118 | We can also look at the mounted filesystem to see where the pool is mounted and | |
| 119 | some quick stats. | |
| 119 | We can also look at the mounted filesystem to see where the pool is | |
| 120 | mounted and some quick stats. | |
| 120 | 121 | |
| 121 | ```sh | |
| 122 | #+begin_src sh | |
| 122 | 123 | > df -h |
| 123 | 124 | |
| 124 | 125 | Filesystem Size Used Avail Use% Mounted on |
| 125 | 126 | ... |
| 126 | 127 | tank 7.2T 128K 7.2T 1% /tank |
| 127 | ``` | |
| 128 | #+end_src | |
| 128 | 129 | |
| 129 | ### Expanding the Pool | |
| 130 | ** Expanding the Pool | |
| 131 | If you want to expand this pool, you will need to add a new VDEV to the | |
| 132 | pool. Since I am using 2 disks per VDEV, I will need to add a new 2-disk | |
| 133 | VDEV to the existing =tank= pool. | |
| 130 | 134 | |
| 131 | If you want to expand this pool, you will need to add a new VDEV to the pool. | |
| 132 | Since I am using 2 disks per VDEV, I will need to add a new 2-disk VDEV to the | |
| 133 | existing `tank` pool. | |
| 134 | ||
| 135 | ```sh | |
| 135 | #+begin_src sh | |
| 136 | 136 | sudo zpool add tank mirror /dev/sdX /dev/sdY |
| 137 | ``` | |
| 137 | #+end_src | |
| 138 | 138 | |
| 139 | If you're adding disks of different sizes, you'll need to use the `-f` flag. | |
| 140 | Keep in mind that the max size will be limited to the smallest disk added. | |
| 139 | If you're adding disks of different sizes, you'll need to use the =-f= | |
| 140 | flag. Keep in mind that the max size will be limited to the smallest | |
| 141 | disk added. | |
| 141 | 142 | |
| 142 | ```sh | |
| 143 | #+begin_src sh | |
| 143 | 144 | sudo zpool add -f tank mirror /dev/sdX /dev/sdY |
| 144 | ``` | |
| 145 | #+end_src | |
| 145 | 146 | |
| 146 | I added two 8TB hard drives and this process took around 10 seconds to complete. | |
| 147 | I added two 8TB hard drives and this process took around 10 seconds to | |
| 148 | complete. | |
| 147 | 149 | |
| 148 | When viewing the pool again, you can see that the pool has now doubled in size. | |
| 149 | We have 14.3 TB useable space and the same space used for mirroring. | |
| 150 | When viewing the pool again, you can see that the pool has now doubled | |
| 151 | in size. We have 14.3 TB useable space and the same space used for | |
| 152 | mirroring. | |
| 150 | 153 | |
| 151 | ```sh | |
| 154 | #+begin_src sh | |
| 152 | 155 | > zfs list |
| 153 | 156 | |
| 154 | 157 | NAME USED AVAIL REFER MOUNTPOINT |
| 155 | 158 | tank 145G 14.3T 104K /tank |
| 156 | 159 | tank/cloud 145G 14.3T 145G /tank/cloud |
| 157 | 160 | tank/media 96K 14.3T 96K /tank/media |
| 158 | ``` | |
| 159 | ||
| 160 | #### Converting Disks | |
| 161 | #+end_src | |
| 161 | 162 | |
| 162 | Some disks, such as NTFS-formatted drives, will need to be partitioned and | |
| 163 | formatted prior to being added to the pool. | |
| 163 | *** Converting Disks | |
| 164 | Some disks, such as NTFS-formatted drives, will need to be partitioned | |
| 165 | and formatted prior to being added to the pool. | |
| 164 | 166 | |
| 165 | 167 | Start by identifying the disks you want to format and add to the pool. |
| 166 | 168 | |
| 167 | ```sh | |
| 169 | #+begin_src sh | |
| 168 | 170 | sudo fdisk -l | grep /dev |
| 169 | ``` | |
| 171 | #+end_src | |
| 170 | 172 | |
| 171 | I am going to format my `/dev/sdc` and `/dev/sdd` disks with the `fdisk` | |
| 173 | I am going to format my =/dev/sdc= and =/dev/sdd= disks with the =fdisk= | |
| 172 | 174 | command. |
| 173 | 175 | |
| 174 | See below for instructions on how to use `fdisk`. Here's what I did to create | |
| 175 | basic Linux formatted disks: | |
| 176 | See below for instructions on how to use =fdisk=. Here's what I did to | |
| 177 | create basic Linux formatted disks: | |
| 176 | 178 | |
| 177 | - `g` : Create GPT partition table | |
| 178 | - `n` : Create a new partition, hit Enter for all default options | |
| 179 | - `t` : Change partition type to `20` for `Linux filesystem` | |
| 180 | - `w` : Write the changes to disk and exit | |
| 179 | - =g= : Create GPT partition table | |
| 180 | - =n= : Create a new partition, hit Enter for all default options | |
| 181 | - =t= : Change partition type to =20= for =Linux filesystem= | |
| 182 | - =w= : Write the changes to disk and exit | |
| 181 | 183 | |
| 182 | 184 | I repeated this process for both disks. |
| 183 | 185 | |
| 184 | ```sh | |
| 186 | #+begin_src sh | |
| 185 | 187 | > sudo fdisk /dev/sdc |
| 186 | 188 | |
| 187 | 189 | Welcome to fdisk (util-linux 2.37.2). |
| @@ -227,95 +229,96 @@ Help: | ||
| 227 | 229 | G create a new empty SGI (IRIX) partition table |
| 228 | 230 | o create a new empty DOS partition table |
| 229 | 231 | s create a new empty Sun partition table |
| 230 | ``` | |
| 232 | #+end_src | |
| 231 | 233 | |
| 232 | 234 | Once the drives are formatted, we can add these disks to the pool. |
| 233 | 235 | |
| 234 | ```sh | |
| 236 | #+begin_src sh | |
| 235 | 237 | sudo zpool add tank mirror /dev/sdc /dev/sdd |
| 236 | ``` | |
| 238 | #+end_src | |
| 237 | 239 | |
| 238 | 240 | When we list the pool again, we can see that our size is now updated to |
| 239 | 241 | approximately 22TB. This represents my hard drives totalling 45.6TB when |
| 240 | shown with `fdisk -l`, with a Raid10 configuration using 22TB for mirroring | |
| 241 | and 22TB of useable space. | |
| 242 | shown with =fdisk -l=, with a Raid10 configuration using 22TB for | |
| 243 | mirroring and 22TB of useable space. | |
| 242 | 244 | |
| 243 | ```sh | |
| 245 | #+begin_src sh | |
| 244 | 246 | > zfs list |
| 245 | 247 | |
| 246 | 248 | NAME USED AVAIL REFER MOUNTPOINT |
| 247 | 249 | tank 145G 21.7T 104K /tank |
| 248 | 250 | tank/cloud 145G 21.7T 145G /tank/cloud |
| 249 | 251 | tank/media 145GT 21.7T 96K /tank/media |
| 250 | ``` | |
| 252 | #+end_src | |
| 251 | 253 | |
| 252 | ### Creating Datasets | |
| 254 | ** Creating Datasets | |
| 255 | According to | |
| 256 | [[https://docs.oracle.com/cd/E18752_01/html/819-5461/ftyue.html][ZFS | |
| 257 | Terminology]], a =dataset= can refer to “clones, file systems, | |
| 258 | snapshots, and volumes. | |
| 253 | 259 | |
| 254 | According to [ZFS | |
| 255 | Terminology](https://docs.oracle.com/cd/E18752_01/html/819-5461/ftyue.html), a | |
| 256 | `dataset` can refer to "clones, file systems, snapshots, and volumes. | |
| 260 | For this guide, I will use the =dataset= term to refer to file systems | |
| 261 | created under a pool. | |
| 257 | 262 | |
| 258 | For this guide, I will use the `dataset` term to refer to file systems created | |
| 259 | under a pool. | |
| 263 | Within my =tank= pool, I am going to create some datasets to help | |
| 264 | organize my files. This will give me location to store data rather than | |
| 265 | simply dumping everything at the =/tank/= location. | |
| 260 | 266 | |
| 261 | Within my `tank` pool, I am going to create some datasets to help organize my | |
| 262 | files. This will give me location to store data rather than simply dumping | |
| 263 | everything at the `/tank/` location. | |
| 264 | ||
| 265 | ```sh | |
| 267 | #+begin_src sh | |
| 266 | 268 | sudo zfs create tank/cloud |
| 267 | 269 | sudo zfs create tank/media |
| 268 | ``` | |
| 270 | #+end_src | |
| 269 | 271 | |
| 270 | Once created, you can see these datasets in the output of your pool list: | |
| 272 | Once created, you can see these datasets in the output of your pool | |
| 273 | list: | |
| 271 | 274 | |
| 272 | ```sh | |
| 275 | #+begin_src sh | |
| 273 | 276 | > zfs list |
| 274 | 277 | NAME USED AVAIL REFER MOUNTPOINT |
| 275 | 278 | tank 752K 7.14T 104K /tank |
| 276 | 279 | tank/cloud 96K 7.14T 96K /tank/cloud |
| 277 | 280 | tank/media 96K 7.14T 96K /tank/media |
| 278 | ``` | |
| 279 | ||
| 280 | ### Creating Snapshots | |
| 281 | #+end_src | |
| 281 | 282 | |
| 282 | Next, let's create our first snapshot. We can do this by calling the `snapshot` | |
| 283 | command and give it an output name. I will be throwing the current date and time | |
| 284 | into my example. | |
| 283 | ** Creating Snapshots | |
| 284 | Next, let's create our first snapshot. We can do this by calling the | |
| 285 | =snapshot= command and give it an output name. I will be throwing the | |
| 286 | current date and time into my example. | |
| 285 | 287 | |
| 286 | ```sh | |
| 288 | #+begin_src sh | |
| 287 | 289 | sudo zfs snapshot tank@$(date '+%Y-%m-%d_%H-%M') |
| 288 | ``` | |
| 290 | #+end_src | |
| 289 | 291 | |
| 290 | 292 | We can list the snapshots in our pool with the following command: |
| 291 | 293 | |
| 292 | ```sh | |
| 294 | #+begin_src sh | |
| 293 | 295 | > zfs list -t snapshot |
| 294 | 296 | NAME USED AVAIL REFER MOUNTPOINT |
| 295 | 297 | tank@2024-02-06_19-41 0B - 104K - |
| 296 | ``` | |
| 297 | ||
| 298 | ### Destroy Snapshots | |
| 298 | #+end_src | |
| 299 | 299 | |
| 300 | ** Destroy Snapshots | |
| 300 | 301 | You can always destroy snapshots that are no longer needed: |
| 301 | 302 | |
| 302 | ```sh | |
| 303 | #+begin_src sh | |
| 303 | 304 | sudo zfs destroy tank@2024-02-06_19-41 |
| 304 | ``` | |
| 305 | #+end_src | |
| 305 | 306 | |
| 306 | 307 | Once deleted, they will no longer appear in the list: |
| 307 | 308 | |
| 308 | ```sh | |
| 309 | #+begin_src sh | |
| 309 | 310 | > zfs list -t snapshot |
| 310 | 311 | no datasets available |
| 311 | ``` | |
| 312 | ||
| 313 | ## My Thoughts on ZFS So Far | |
| 312 | #+end_src | |
| 314 | 313 | |
| 315 | - I sacrificed 25TB to be able to mirror my data, but I feel more comfortable | |
| 316 | with the potential to save my data by quickly replacing a disk if I need to. | |
| 314 | * My Thoughts on ZFS So Far | |
| 315 | - I sacrificed 25TB to be able to mirror my data, but I feel more | |
| 316 | comfortable with the potential to save my data by quickly replacing a | |
| 317 | disk if I need to. | |
| 317 | 318 | - The set-up was surprisingly easy and fast. |
| 318 | - Disk I/O is fast as well. I was worried that the data transfer speeds would be | |
| 319 | slower due to the RAID configuration. | |
| 320 | - Media streaming and transcoding has seen no noticeable drop in performance. | |
| 321 | - My only limitation really is the number of HDD bays in my server HDD cage. | |
| 319 | - Disk I/O is fast as well. I was worried that the data transfer speeds | |
| 320 | would be slower due to the RAID configuration. | |
| 321 | - Media streaming and transcoding has seen no noticeable drop in | |
| 322 | performance. | |
| 323 | - My only limitation really is the number of HDD bays in my server HDD | |
| 324 | cage. | |
content/blog/2020-12-29-zork.md → blog/zork/index.org renamed +45 −50
| @@ -1,25 +1,23 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-12-29 | |
| 3 | title = "Zork: Let's Explore a Classic" | |
| 4 | description = "A video game review for Zork." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Download (Free) | |
| 1 | #+title: Zork: Let's Explore a Classic | |
| 2 | #+date: 2020-12-29 | |
| 3 | #+description: A video game review for Zork. | |
| 4 | #+filetags: :gaming: | |
| 8 | 5 | |
| 6 | * Download (Free) | |
| 9 | 7 | Before we get into the game itself, you should know that you can |
| 10 | download Zork for free from Infocom's [download | |
| 11 | page](http://infocom-if.org/downloads/downloads.html). So feel free to | |
| 12 | boot it up and take a ride back to the 1980s with this masterpiece. | |
| 13 | ||
| 14 | # Game Description | |
| 15 | ||
| 16 | Zork is an interactive, text-based computer game originally released in | |
| 17 | 1980. This series, split into three separate games, introduced a robust | |
| 18 | and sophisticated text parser to gamers. People were largely used to the | |
| 19 | simple commands used in the popular game [Colossal Cave | |
| 20 | Adventure](https://en.wikipedia.org/wiki/Colossal_Cave_Adventure), but | |
| 21 | Zork allowed users to send more complex commands that included | |
| 22 | prepositions and conjunctions. | |
| 8 | download Zork for free from Infocom's | |
| 9 | [[http://infocom-if.org/downloads/downloads.html][download page]]. So | |
| 10 | feel free to boot it up and take a ride back to the 1980s with this | |
| 11 | masterpiece. | |
| 12 | ||
| 13 | * Game Description | |
| 14 | Zork is an interactive, text-based computer game originally released | |
| 15 | in 1980. This series, split into three separate games, introduced a | |
| 16 | robust and sophisticated text parser to gamers. People were largely used | |
| 17 | to the simple commands used in the popular game | |
| 18 | [[https://en.wikipedia.org/wiki/Colossal_Cave_Adventure][Colossal Cave | |
| 19 | Adventure]], but Zork allowed users to send more complex commands that | |
| 20 | included prepositions and conjunctions. | |
| 23 | 21 | |
| 24 | 22 | Zork tracks your score as you explore the map, find tools, and collect |
| 25 | 23 | trophy items (e.g., a jewel-encrusted egg). When you place your trophy |
| @@ -28,59 +26,57 @@ points. Collecting the Twenty Treasures of Zork and placing them within | ||
| 28 | 26 | the trophy case wins the game. However, you must explore the map, solve |
| 29 | 27 | puzzles, and avoid being eaten by a grue to collect these treasures. |
| 30 | 28 | |
| 31 | # The Map | |
| 32 | ||
| 29 | * The Map | |
| 33 | 30 | Since Zork is a vast and complex game, it helps to have a map as you |
| 34 | 31 | explore and collect your trophies. However, if you want to play the game |
| 35 | 32 | as it was truly intended, you should try to play it without using the |
| 36 | 33 | map. |
| 37 | 34 | |
| 38 |  | |
| 39 | ||
| 40 | *[Map Source](https://www.filfre.net/2012/01/exploring-zork-part-1/)* | |
| 35 | #+caption: Zork Map | |
| 36 | [[https://img.cleberg.net/blog/20201229-zork/zork_map.png]] | |
| 41 | 37 | |
| 42 | # In-Game Screenshots | |
| 38 | /[[https://www.filfre.net/2012/01/exploring-zork-part-1/][Map Source]]/ | |
| 43 | 39 | |
| 40 | * In-Game Screenshots | |
| 44 | 41 | After playing the game (for the first time ever) for several weeks |
| 45 | 42 | around 2014, I was finally able to beat the game with some online help |
| 46 | 43 | to find the last couple items. As I was writing this post, I installed |
| 47 | 44 | the game again to grab some screenshots to show off the true glory of |
| 48 | this game. As noted in [Jimmy Maher's | |
| 49 | playthrough](https://www.filfre.net/2012/01/exploring-zork-part-1/), the | |
| 50 | original Zork games looked quite a bit different due to the older | |
| 51 | hardware of computers like the Apple II and multiple bug fixes that | |
| 52 | Infocom pushed out after the game's initial release. My play-through | |
| 53 | uses the [Zork | |
| 54 | Anthology](https://store.steampowered.com/app/570580/Zork_Anthology/) | |
| 55 | version, which utilizes DOSBox on Windows. | |
| 45 | this game. As noted in | |
| 46 | [[https://www.filfre.net/2012/01/exploring-zork-part-1/][Jimmy Maher's | |
| 47 | playthrough]], the original Zork games looked quite a bit different due | |
| 48 | to the older hardware of computers like the Apple II and multiple bug | |
| 49 | fixes that Infocom pushed out after the game's initial release. My | |
| 50 | play-through uses the | |
| 51 | [[https://store.steampowered.com/app/570580/Zork_Anthology/][Zork | |
| 52 | Anthology]] version, which utilizes DOSBox on Windows. | |
| 56 | 53 | |
| 57 | 54 | The first screenshot here shows the introductory information, which |
| 58 | doesn't include instructions of any kind for the player. If you | |
| 59 | haven't played text adventures before, try to use simple commands like | |
| 60 | "go west," "look around," or "hit troll with elvish sword." | |
| 55 | doesn't include instructions of any kind for the player. If you haven't | |
| 56 | played text adventures before, try to use simple commands like "go | |
| 57 | west," "look around," or "hit troll with elvish sword." | |
| 61 | 58 | |
| 62 |  | |
| 59 | #+caption: Zork Screen, pt. 1 | |
| 60 | [[https://img.cleberg.net/blog/20201229-zork/zork_01.png]] | |
| 64 | 61 | |
| 65 | 62 | In this second screenshot, we see the player has entered the house and |
| 66 | 63 | found the trophy case in the living room. The lantern and sword in this |
| 67 | 64 | room allow the player to explore dark areas and attack enemies. If you |
| 68 | don't use the lantern, you won't be able to see anything in dark | |
| 69 | areas, and you may be eaten by a grue. | |
| 65 | don't use the lantern, you won't be able to see anything in dark areas, | |
| 66 | and you may be eaten by a grue. | |
| 70 | 67 | |
| 71 |  | |
| 68 | #+caption: Zork Screen, pt. 2 | |
| 69 | [[https://img.cleberg.net/blog/20201229-zork/zork_02.png]] | |
| 73 | 70 | |
| 74 | 71 | Finally, we see that the player has found the first treasure: a |
| 75 | 72 | jewel-encrusted egg. These treasures can be taken back to the house and |
| 76 | 73 | placed in the trophy case or carried until you feel like you want to put |
| 77 | 74 | things away. |
| 78 | 75 | |
| 79 |  | |
| 81 | ||
| 82 | # Conclusion | |
| 76 | #+caption: Zork Screen, pt 3. | |
| 77 | [[https://img.cleberg.net/blog/20201229-zork/zork_03.png]] | |
| 83 | 78 | |
| 79 | * Conclusion | |
| 84 | 80 | It's been quite a few years since I first played Zork, but I clearly |
| 85 | 81 | remember the late nights and bloodshot eyes that helped me find all the |
| 86 | 82 | treasures. This game is well worth the time and effort, even though the |
| @@ -90,6 +86,5 @@ and skills learned in early video games like Zork can actually help you, | ||
| 90 | 86 | even when playing newer games. |
| 91 | 87 | |
| 92 | 88 | If you do decide to play Zork, you can download Zork I, II, and III from |
| 93 | Infocom's [download | |
| 94 | page](http://infocom-if.org/downloads/downloads.html) for free or search | |
| 95 | the internet for an online version. | |
| 89 | Infocom's [[http://infocom-if.org/downloads/downloads.html][download | |
| 90 | page]] for free or search the internet for an online version. | |
build.sh deleted −6
| @@ -1,6 +0,0 @@ | ||
| 1 | #!/bin/sh | |
| 2 | ||
| 3 | cd ~/Source/cleberg.net/ | |
| 4 | rm -rf public/ | |
| 5 | zola build --force | |
| 6 | scp -r public/* ubuntu:/var/www/cleberg.net/ | |
config.toml deleted −21
| @@ -1,21 +0,0 @@ | ||
| 1 | # Site settings | |
| 2 | base_url = "https://cleberg.net" | |
| 3 | title = "cleberg.net" | |
| 4 | description = "The personal website of Christian Cleberg." | |
| 5 | author = "Christian Cleberg" | |
| 6 | ||
| 7 | # RSS settings | |
| 8 | generate_feed = true | |
| 9 | feed_filename = "atom.xml" | |
| 10 | ||
| 11 | [markdown] | |
| 12 | highlight_code = true | |
| 13 | highlight_theme = "css" | |
| 14 | highlight_themes_css = [ | |
| 15 | { theme = "ayu-dark", filename = "syntax-theme-dark.css" }, | |
| 16 | { theme = "inspired-github", filename = "syntax-theme-light.css" }, | |
| 17 | ] | |
| 18 | external_links_target_blank = true | |
| 19 | lazy_async_image = true | |
| 20 | ||
| 21 | [extra] | |
content/blog/2018-12-08-aes-encryption.md deleted −124
| @@ -1,124 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2018-12-08 | |
| 3 | title = "AES Encryption" | |
| 4 | description = "An exploration of the AES encryption standard." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Basic AES | |
| 8 | ||
| 9 | If you're not familiar with encryption techniques, | |
| 10 | [AES](https://en.wikipedia.org/wiki/Advanced_Encryption_Standard) is the | |
| 11 | **Advanced Encryption Standard**. This specification was established by | |
| 12 | the National Institute of Standards and Technology, sub-selected from | |
| 13 | the Rijndael family of ciphers (128, 192, and 256 bits) in 2001. | |
| 14 | Furthering its popularity and status, the US government chose AES as | |
| 15 | their default encryption method for top-secret data, removing the | |
| 16 | previous standard which had been in place since 1977. | |
| 17 | ||
| 18 | AES has proven to be an extremely safe encryption method, with 7-round | |
| 19 | and 8-round attacks making no material improvements since the release of | |
| 20 | this encryption standard almost two decades ago. | |
| 21 | ||
| 22 | > Though many papers have been published on the cryptanalysis of AES, | |
| 23 | > the fastest single-key attacks on round-reduced AES variants [20, | |
| 24 | > 33] so far are only slightly more powerful than those proposed 10 | |
| 25 | > years ago [23,24]. | |
| 26 | > | |
| 27 | > - [Bogdonav, et | |
| 28 | > al.](http://research.microsoft.com/en-us/projects/cryptanalysis/aesbc.pdf) | |
| 29 | ||
| 30 | # How Secure is AES? | |
| 31 | ||
| 32 | In theory, AES-256 is non-crackable due to the massive number of | |
| 33 | combinations that can be produced. However, AES-128 is no longer | |
| 34 | recommended as a viable implementation to protect important data. | |
| 35 | ||
| 36 | A semi-short [comic | |
| 37 | strip](http://www.moserware.com/2009/09/stick-figure-guide-to-advanced.html) | |
| 38 | from Moserware quickly explains AES for the public to understand. | |
| 39 | Basically AES encrypts the data by obscuring the relationship between | |
| 40 | the data and the encrypted data. Additionally, this method spreads the | |
| 41 | message out. Lastly, the key produced by AES is the secret to decrypting | |
| 42 | it. Someone may know the method of AES, but without the key, they are | |
| 43 | powerless. | |
| 44 | ||
| 45 | To obscure and spread the data out, AES creates a | |
| 46 | substitution-permutation network. Wikipedia has a wonderful [example of | |
| 47 | an SP | |
| 48 | network](https://upload.wikimedia.org/wikipedia/commons/thumb/c/cd/SubstitutionPermutationNetwork2.png/468px-SubstitutionPermutationNetwork2.png) | |
| 49 | available. This network sends the data through a set of S boxes (using | |
| 50 | the unique key) to substitute the bits with another block of bits. Then, | |
| 51 | a P box will permutate, or rearrange, the bits. This is done over and | |
| 52 | over, with the key being derived from the last round. For AES, the key | |
| 53 | size specifies the number of transformation rounds: 10, 12, and 14 | |
| 54 | rounds for 128-bit, 192-bit, and 256-bit keys, respectively. | |
| 55 | ||
| 56 | # The Process | |
| 57 | ||
| 58 | 1. \*KeyExpansion=: Using [Rijndael's key | |
| 59 | schedule](https://en.m.wikipedia.org/wiki/Advanced_Encryption_Standard), | |
| 60 | the keys are dynamically generated. | |
| 61 | 2. **AddRoundKey**: Each byte of the data is combined with this key | |
| 62 | using bitwise xor. | |
| 63 | 3. **SubBytes**: This is followed by the substitution of each byte of | |
| 64 | data. | |
| 65 | 4. **ShiftRows**: Then, the final three rows are shifted a certain | |
| 66 | number of steps, dictated by the cipher. | |
| 67 | 5. **MixColumns**: After the rows have been shifted, the columns are | |
| 68 | mixed and combined. | |
| 69 | ||
| 70 | This process does not necessarily stop after one full round. Steps 2 | |
| 71 | through 5 will repeat for the number of rounds specified by the key. | |
| 72 | However, the final round excludes the MixColumns step. As you can see, | |
| 73 | this is a fairly complex process. One must have a solid understanding of | |
| 74 | general mathematic principles to fully understand how the sequence works | |
| 75 | (and to even attempt to find a weakness). | |
| 76 | ||
| 77 | According to research done by Bogdanov et al., it would take billions of | |
| 78 | years to brute force a 126-bit key with current hardware. Additionally, | |
| 79 | this brute force attack would require storing 2^88^ bits of data! | |
| 80 | However, there are a few different attacks that have been used to show | |
| 81 | vulnerabilities with the use of this technology. Side-channel attacks | |
| 82 | use inadvertent leaks of data from the hardware or software, which can | |
| 83 | allow attackers to obtain the key or run programs on a user's hardware. | |
| 84 | ||
| 85 | Please note that this is not something you should run out and try to | |
| 86 | implement in your `Hello, World!` app after only a few hours of | |
| 87 | research. While AES (basically all encryption methods) is extremely | |
| 88 | efficient in what it does, it takes a lot of time and patience to | |
| 89 | understand. If you're looking for something which currently implements | |
| 90 | AES, check out the [Legion of the Bouncy | |
| 91 | Castle](https://www.bouncycastle.org/documentation.html) for Java | |
| 92 | implementations of cryptographic algorithms. | |
| 93 | ||
| 94 | # Why Does Encryption Matter? | |
| 95 | ||
| 96 | There are limitless reasons to enable encryption at-rest or in-transit | |
| 97 | for various aspects of your digital life. You can research specific | |
| 98 | examples, such as [Australia passes new law to thwart strong | |
| 99 | encryption](https://arstechnica.com/tech-policy/2018/12/australia-passes-new-law-to-thwart-strong-encryption/). | |
| 100 | However, I will simply list a few basic reasons to always enable | |
| 101 | encryption, where feasible: | |
| 102 | ||
| 103 | 1. Privacy is a human right and is recognized as a national right in | |
| 104 | some countries (e.g., [US Fourth | |
| 105 | Amendment](https://www.law.cornell.edu/wex/fourth_amendment)). | |
| 106 | 2. "Why not?" Encryption rarely affects performance or speed, so | |
| 107 | there's usually not a reason to avoid it in the first place. | |
| 108 | 3. Your digital identity and activity (texts, emails, phone calls, | |
| 109 | online accounts, etc.) are extremely valuable and can result in | |
| 110 | terrible consequences, such as identity theft, if leaked to other | |
| 111 | parties. Encrypting this data prevents such leaks from ruining | |
| 112 | lives. | |
| 113 | 4. Wiping or factory-resetting does not actually wipe all data from the | |
| 114 | storage device. There are methods to read data from the physical | |
| 115 | disks/boards inside devices. | |
| 116 | 5. Corporations, governments, and other nefarious groups/individuals | |
| 117 | are actively looking for ways to collect personal information about | |
| 118 | anyone they can. If someone's data is unencrypted, that person may | |
| 119 | become a target due to the ease of data collection. | |
| 120 | ||
| 121 | ****Read More:**** | |
| 122 | ||
| 123 | - [Federal Information Processing Standards Publication | |
| 124 | 197](http://nvlpubs.nist.gov/nistpubs/FIPS/NIST.FIPS.197.pdf) | |
content/blog/2019-12-03-the-ansoff-matrix.md deleted −205
| @@ -1,205 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2019-12-03 | |
| 3 | title = "The Ansoff Matrix" | |
| 4 | description = "Learn about the Ansoff Matrix, a strategic management tool." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Overview | |
| 8 | ||
| 9 | As the world of business evolves, managers must approach business | |
| 10 | planning and strategy with a contemporary mindset. According to Dess, | |
| 11 | McNamara, Eisner, and Lee, managers must be willing to adapt to the | |
| 12 | modern business environment by going beyond "'incremental | |
| 13 | management', whereby they view their job as making a series of small, | |
| 14 | minor changes to improve the efficiency of the firm's operations"[^1]. | |
| 15 | ||
| 16 | One reason that strategic management is crucial is because most | |
| 17 | businesses that fail in the United States each year fail due to a lack | |
| 18 | of strategic focus or direction[^2]. The rate of failure for businesses | |
| 19 | with poor strategies shows that strategic planning and management are | |
| 20 | crucial to a business's strength and longevity, injecting the critical | |
| 21 | factors of growth and direction into a company's business plan. | |
| 22 | ||
| 23 | One of the most significant strategic planning and management frameworks | |
| 24 | that companies can use is the [Ansoff | |
| 25 | Matrix](https://en.wikipedia.org/wiki/Ansoff_matrix). While this | |
| 26 | framework has unique purposes and use-cases, it can effectively help an | |
| 27 | organization grow and compete. Specifically, the Ansoff matrix is one of | |
| 28 | the most effective frameworks for companies who want to focus on | |
| 29 | increasing sales revenue or profitability[^3]. | |
| 30 | ||
| 31 | This framework uses a two-by-two figure to show the four strategic | |
| 32 | options for companies to use in this framework: market penetration, | |
| 33 | market development, product development, and diversification (see | |
| 34 | **Figure 1**). The x-axis of the matrix focuses on the firm's markets | |
| 35 | and also determines if the firm is looking to enter new markets or | |
| 36 | innovate in its current markets. The y-axis of the matrix focuses on the | |
| 37 | firm's products and determines if the firm wants to pursue strategies | |
| 38 | around their existing products or explore new products. | |
| 39 | ||
| 40 |  | |
| 42 | ||
| 43 | # Strategic Options | |
| 44 | ||
| 45 | ## Market Penetration | |
| 46 | ||
| 47 | The most straightforward strategy in the Ansoff matrix is to focus on | |
| 48 | existing products in existing markets, also known as market | |
| 49 | penetration[^4]. Companies such as Coca-Cola have used market | |
| 50 | penetration successfully by investing a lot of money to get further | |
| 51 | value out of their current markets. Coca-Cola does this by introducing | |
| 52 | new features such as Christmas-themed bottles, personal names on the | |
| 53 | bottles, and other marketing schemes. | |
| 54 | ||
| 55 | ## Market Development | |
| 56 | ||
| 57 | Market development extends existing products into new markets in an | |
| 58 | attempt to increase the number of buyers. One interesting way that | |
| 59 | Coca-Cola used this strategy comes from the stigma that Diet Coke is a | |
| 60 | woman's drink[^5]. Coca-Cola introduced Coca-Cola Zero, which contained | |
| 61 | the same nutritional content as Diet Coke, but was packaged in a dark | |
| 62 | black can to appear more "manly"[^6]. | |
| 63 | ||
| 64 | ## Product Development | |
| 65 | ||
| 66 | Product development uses existing markets to introduce new products so | |
| 67 | that the firm can better meet customer needs[^7]. The extreme end of | |
| 68 | diversification is home to companies such as Johnson & Johnson, a | |
| 69 | healthcare company that has developed a business portfolio of more than | |
| 70 | 60,000 different products[^8]. Johnson & Johnson's dedication to | |
| 71 | continuous diversification has led them to a balance sheet rating of | |
| 72 | "AAA", industry recognition for diversification, and increases in | |
| 73 | their investor dividends for 57 consecutive years[^9]. | |
| 74 | ||
| 75 | ## Related Diversification | |
| 76 | ||
| 77 | Diversification, the final strategy of the Ansoff Matrix, is more | |
| 78 | difficult than the others since it involves exploring both new markets | |
| 79 | and new products. Related diversification is a diversification strategy | |
| 80 | that closely relates to the firm's core business. Coca-Cola's best | |
| 81 | example of related diversification is its acquisition of Glaceau and | |
| 82 | Vitamin Water, which expanded their drinking lines of business[^10]. | |
| 83 | ||
| 84 | ## Unrelated Diversification | |
| 85 | ||
| 86 | Unrelated diversification is a diversification strategy that does not | |
| 87 | really relate to the firm's core business but still diversifies their | |
| 88 | business portfolio. A good example of this would be a coffee company who | |
| 89 | has decided to enter the market for bicycle sales. The main purpose of | |
| 90 | this strategy is to an extremely diverse company that will not go | |
| 91 | bankrupt if one market goes through difficult times. However, this | |
| 92 | requires a lot of independent skills and heavy investments since the | |
| 93 | company most likely cannot easily transfer knowledge between the markets | |
| 94 | they compete in. | |
| 95 | ||
| 96 | # Requirements for Success | |
| 97 | ||
| 98 | To use the Ansoff Matrix framework, managers need to formulate corporate | |
| 99 | goals and objectives. Without goals and direction, management frameworks | |
| 100 | do not present much practical utility. Further, the Ansoff Matrix | |
| 101 | requires the managers involved to make tactical decisions and create a | |
| 102 | path for the company to take toward their goals. Lastly, both the Ansoff | |
| 103 | Matrix needs to consider both internal and external perspectives | |
| 104 | throughout the strategy formulation process. | |
| 105 | ||
| 106 | One interesting probability is that companies will be using multiple | |
| 107 | strategic planning and management frameworks at the same time. While | |
| 108 | this may sound like it could crowd the management process, there are | |
| 109 | numerous reasons to do so. For example, the Ansoff Matrix and the | |
| 110 | Balanced Scorecard are relatively popular, and they cover entirely | |
| 111 | different parts of a company's strategy. Using the results from the | |
| 112 | Balanced Scorecard could inform a company of the potential product and | |
| 113 | market demands, such as from customer or supplier survey results, to | |
| 114 | help the company determine which Ansoff Matrix strategy to pursue. | |
| 115 | However, a combined approach at this level would require mature | |
| 116 | frameworks and focused managers who are able to strategize at a high | |
| 117 | level. | |
| 118 | ||
| 119 | Lastly, it should be noted that the author of the Ansoff matrix, Igor | |
| 120 | Ansoff, often used the term [paralysis by | |
| 121 | analysis](https://en.wikipedia.org/wiki/Analysis_paralysis) to explain | |
| 122 | the mistake of companies who overuse analysis and spend too much time | |
| 123 | planning. Companies need to understand the utility of a strategic | |
| 124 | management framework while ensuring that the company is poised to | |
| 125 | execute as efficiently as they have planned. | |
| 126 | ||
| 127 | # Footnotes | |
| 128 | ||
| 129 | [^1]: | |
| 130 | ```example | |
| 131 | Dess, G. G., McNamara, G., Eisner, A. B., Lee, S. H. (2019). Strategic | |
| 132 | ``` | |
| 133 | ||
| 134 | management: Text & cases, ninth edition. New York, NY: McGraw-Hill | |
| 135 | Education. | |
| 136 | ||
| 137 | [^2]: | |
| 138 | ```example | |
| 139 | Juneja, P. (n.d.). Benefits of strategic management. Management Study | |
| 140 | ``` | |
| 141 | ||
| 142 | Guide. Retrieved from | |
| 143 | <https://www.managementstudyguide.com/strategic-management-benefits.htm>. | |
| 144 | ||
| 145 | [^3]: | |
| 146 | ```example | |
| 147 | Meldrum M., McDonald M. (1995) The Ansoff matrix. In: Key Marketing | |
| 148 | ``` | |
| 149 | ||
| 150 | Concepts. London: Palgrave. | |
| 151 | ||
| 152 | [^4]: | |
| 153 | ```example | |
| 154 | Meldrum M., McDonald M. (1995) The Ansoff matrix. In: Key Marketing | |
| 155 | ``` | |
| 156 | ||
| 157 | Concepts. London: Palgrave. | |
| 158 | ||
| 159 | [^5]: | |
| 160 | ```example | |
| 161 | Oakley, T. (2015). Coca-Cola: The Ansoff matrix. The Marketing Agenda. | |
| 162 | ``` | |
| 163 | ||
| 164 | Retrieved from | |
| 165 | <https://themarketingagenda.com/2015/03/28/coca-cola-ansoff-matrix/>. | |
| 166 | ||
| 167 | [^6]: | |
| 168 | ```example | |
| 169 | Oakley, T. (2015). Coca-Cola: The Ansoff matrix. The Marketing Agenda. | |
| 170 | ``` | |
| 171 | ||
| 172 | Retrieved from | |
| 173 | <https://themarketingagenda.com/2015/03/28/coca-cola-ansoff-matrix/>. | |
| 174 | ||
| 175 | [^7]: | |
| 176 | ```example | |
| 177 | Oakley, T. (2015). Coca-Cola: The Ansoff matrix. The Marketing Agenda. | |
| 178 | ``` | |
| 179 | ||
| 180 | Retrieved from | |
| 181 | <https://themarketingagenda.com/2015/03/28/coca-cola-ansoff-matrix/>. | |
| 182 | ||
| 183 | [^8]: | |
| 184 | ```example | |
| 185 | Lemke, T. (2019). The most diversified companies in the stock market. The | |
| 186 | ``` | |
| 187 | ||
| 188 | balance. Retrieved from | |
| 189 | <https://www.thebalance.com/the-most-diversified-companies-in-the-stock-market-4169730>. | |
| 190 | ||
| 191 | [^9]: | |
| 192 | ```example | |
| 193 | Johnson & Johnson. (2018). 2018 Investor Fact Sheet. [PDF file]. Retrieved | |
| 194 | ``` | |
| 195 | ||
| 196 | from | |
| 197 | [http://www.investor.jnj.com/_document/2018-investor-fact-sheet-4-19'id=0000016a-5681-d475-a17f-d78db54a0000](http://www.investor.jnj.com/\_document/2018-investor-fact-sheet-4-19'id=0000016a-5681-d475-a17f-d78db54a0000). | |
| 198 | ||
| 199 | [^10]: | |
| 200 | ```example | |
| 201 | Oakley, T. (2015). Coca-Cola: The Ansoff matrix. The Marketing Agenda. | |
| 202 | ``` | |
| 203 | ||
| 204 | Retrieved from | |
| 205 | <https://themarketingagenda.com/2015/03/28/coca-cola-ansoff-matrix/>. | |
content/blog/2019-12-16-password-security.md deleted −126
| @@ -1,126 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2019-12-16 | |
| 3 | title = "Password Security" | |
| 4 | description = "Password security basics." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Users | |
| 8 | ||
| 9 | ## Why Does It Matter? | |
| 10 | ||
| 11 | Information security, including passwords and identities, has become one | |
| 12 | of the most important digital highlights of the last decade. With | |
| 13 | [billions of people affected by data breaches each | |
| 14 | year](https://www.usatoday.com/story/money/2018/12/28/data-breaches-2018-billions-hit-growing-number-cyberattacks/2413411002/), | |
| 15 | there's a greater need to introduce strong information security | |
| 16 | systems. If you think you've been part of a breach, or you want to | |
| 17 | check and see, you can use [Have I Been | |
| 18 | Pwned](https://haveibeenpwned.com/) to see if your email has been | |
| 19 | involved in any public breaches. Remember that there's a possibility | |
| 20 | that a company experienced a breach and did not report it to anyone. | |
| 21 | ||
| 22 | ## How Do I Protect Myself? | |
| 23 | ||
| 24 | The first place to start with any personal security check-up is to | |
| 25 | gather a list of all the different websites, apps, or programs that | |
| 26 | require you to have login credentials. Optionally, once you know where | |
| 27 | your information is being stored, you can sort the list from the | |
| 28 | most-important items such as banks or government logins to less | |
| 29 | important items such as your favorite meme site. You will want to ensure | |
| 30 | that your critical logins are secure before getting to the others. | |
| 31 | ||
| 32 | Once you think you have a good idea of all your different authentication | |
| 33 | methods, I recommend using a password manager such as | |
| 34 | [Bitwarden](https://bitwarden.com/). Using a password manager allows you | |
| 35 | to automatically save your logins, create randomized passwords, and | |
| 36 | transfer passwords across devices. However, you'll need to memorize | |
| 37 | your "vault password" that allows you to open the password manager. | |
| 38 | It's important to make this something hard to guess since it would | |
| 39 | allow anyone who has it to access every password you've stored in | |
| 40 | there. | |
| 41 | ||
| 42 | Personally, I recommend using a | |
| 43 | [passphrase](https://en.wikipedia.org/wiki/Passphrase) instead of a | |
| 44 | [password](https://en.wikipedia.org/wiki/Password) for your vault | |
| 45 | password. Instead of using a string of characters (whether random or | |
| 46 | simple), use a phrase and add in symbols and a number. For example, your | |
| 47 | vault password could be `Racing-Alphabet-Gourd-Parrot3`. Swap | |
| 48 | the symbols out for whichever symbol you want, move the number around, | |
| 49 | and fine-tune the passphrase until you are confident that you can | |
| 50 | remember it whenever necessary. | |
| 51 | ||
| 52 | Once you've stored your passwords, make sure you continually check up | |
| 53 | on your account and make sure you aren't following bad password | |
| 54 | practices. Krebs on Security has a great [blog post on password | |
| 55 | recommendations](https://krebsonsecurity.com/password-dos-and-donts/). | |
| 56 | Any time that a data breach happens, make sure you check to see if you | |
| 57 | were included, and if you need to reset any account passwords. | |
| 58 | ||
| 59 | # Developers | |
| 60 | ||
| 61 | ## What Are the Basic Requirements? | |
| 62 | ||
| 63 | When developing any password-protected application, there are a few | |
| 64 | basic rules that anyone should follow even if they do not follow any | |
| 65 | official guidelines such as NIST. The foremost practice is to require | |
| 66 | users to use passwords that are at least 8 characters and cannot easily | |
| 67 | be guessed. This sounds extremely simple, but it requires quite a few | |
| 68 | different strategies. First, the application should check the potential | |
| 69 | passwords against a dictionary of insecure passwords such | |
| 70 | `password`, `1234abc`, or | |
| 71 | `application_name`. | |
| 72 | ||
| 73 | Next, the application should offer guidance on the strength of passwords | |
| 74 | being entered during enrollment. Further, NIST officially recommends | |
| 75 | **not** implementing any composition rules that make passwords hard to | |
| 76 | remember (e.g. passwords with letters, numbers, and special characters) | |
| 77 | and instead encouraging the use of long pass phrases which can include | |
| 78 | spaces. It should be noted that to be able to keep spaces within | |
| 79 | passwords, all unicode characters should be supported, and passwords | |
| 80 | should not be truncated. | |
| 81 | ||
| 82 | ## What Does NIST Recommend? | |
| 83 | ||
| 84 | The National Institute of Standards and Technology | |
| 85 | ([NIST](https://www.nist.gov)) in the US Department of Commerce | |
| 86 | regularly publishes information around information security and digital | |
| 87 | identity guidelines. Recently, NIST published [Special Publication | |
| 88 | 800-63b](https://pages.nist.gov/800-63-3/sp800-63b.html): Digital | |
| 89 | Identity Guidelines and Authentication and Lifecycle Management. | |
| 90 | ||
| 91 | > A Memorized Secret authenticator - commonly referred to as a password | |
| 92 | > or, if numeric, a PIN - is a secret value intended to be chosen and | |
| 93 | > memorized by the user. Memorized secrets need to be of sufficient | |
| 94 | > complexity and secrecy that it would be impractical for an attacker to | |
| 95 | > guess or otherwise discover the correct secret value. A memorized | |
| 96 | > secret is something you know. | |
| 97 | > | |
| 98 | > - NIST Special Publication 800-63B | |
| 99 | ||
| 100 | NIST offers a lot of guidance on passwords, but I'm going to highlight | |
| 101 | just a few of the important factors: | |
| 102 | ||
| 103 | - Require passwords to be a minimum of 8 characters (6 characters if | |
| 104 | randomly generated and be generated using an approved random bit | |
| 105 | generator). | |
| 106 | - Compare potential passwords against a list that contains values | |
| 107 | known to be commonly-used, expected, or compromised. | |
| 108 | - Offer guidance on password strength, such as a strength meter. | |
| 109 | - Implement a rate-limiting mechanism to limit the number of failed | |
| 110 | authentication attempts for each user account. | |
| 111 | - Do not require composition rules for passwords and do not require | |
| 112 | passwords to be changed periodically (unless compromised). | |
| 113 | - Allow pasting of user identification and passwords to facilitate the | |
| 114 | use of password managers. | |
| 115 | - Allow users to view the password as it is being entered. | |
| 116 | - Use secure forms of communication and storage, including salting and | |
| 117 | hashing passwords using a one-way key derivation function. | |
| 118 | ||
| 119 | NIST offers further guidance on other devices that require specific | |
| 120 | security policies, querying for passwords, and more. All the information | |
| 121 | discussed so far comes from [NIST | |
| 122 | SP800-63b](https://pages.nist.gov/800-63-3/sp800-63b.html) but NIST | |
| 123 | offers a lot of information on digital identities, enrollment, identity | |
| 124 | proofing, authentication, lifecycle management, federation, and | |
| 125 | assertions in the total [NIST SP800-63 Digital Identity | |
| 126 | Guidelines](https://pages.nist.gov/800-63-3/). | |
content/blog/2020-01-26-steam-on-ntfs.md deleted −95
| @@ -1,95 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-01-26 | |
| 3 | title = "Linux Gaming Tweak: Steam on NTFS Drives" | |
| 4 | description = "Learn how to fix Steam NTFS issues on Linux." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Auto-Mount Steam Drives | |
| 8 | ||
| 9 |  | |
| 10 | ||
| 11 | If you want to see how to install Steam on Linux, see my other post: | |
| 12 | [Linux Software](/blog/linux-software/). | |
| 13 | ||
| 14 | Are you having trouble launching games, even though they've installed | |
| 15 | correctly? This may happen if you're storing your games on an | |
| 16 | NTFS-formatted drive. This shouldn't be an issue if you're storing | |
| 17 | your games on the same drive that Steam is on, but some gamers prefer to | |
| 18 | put Steam on their main drive and game files on another SSD or HDD. | |
| 19 | ||
| 20 | To fix this problem, you'll need to try a few things. First, you'll | |
| 21 | need to install the `ntfs-3g` package, which is meant for | |
| 22 | better interoperability with Linux. | |
| 23 | ||
| 24 | ```sh | |
| 25 | sudo apt install ntfs-3g | |
| 26 | ``` | |
| 27 | ||
| 28 | Next, you should set up the `/etc/fstab` file to | |
| 29 | automatically mount your drives on boot. To automatically mount your | |
| 30 | drives when the computer boots up, you'll have to create the folders | |
| 31 | you want to mount your drive to first. I store mine in the | |
| 32 | `/mnt` folder using names that I'll recognize, but you can | |
| 33 | create your folders wherever you want. | |
| 34 | ||
| 35 | ```sh | |
| 36 | mkdir /path/to/folder | |
| 37 | ``` | |
| 38 | ||
| 39 | For example: | |
| 40 | ||
| 41 | ```sh | |
| 42 | mkdir /mnt/steam_library | |
| 43 | ``` | |
| 44 | ||
| 45 | To automatically mount drives upon system boot, you will need to collect | |
| 46 | a few items. The UUID is the identification number connected to | |
| 47 | whichever drive you're using to store Steam games. | |
| 48 | ||
| 49 | Drives are usually labeled similar to `/dev/nvme0n1p1` or | |
| 50 | `/dev/sda1`, so you'll need to find the line in the output | |
| 51 | of the command below that correlates to your drive and copy the UUID | |
| 52 | over to the `/etc/fstab` file. | |
| 53 | ||
| 54 | ```sh | |
| 55 | sudo blkid | grep UUID= | |
| 56 | ``` | |
| 57 | ||
| 58 | Next, you'll need your `uid` and `gid`. To find | |
| 59 | these, run the following command: | |
| 60 | ||
| 61 | ```sh | |
| 62 | id -u && id -g | |
| 63 | ``` | |
| 64 | ||
| 65 | Now that you have collected the necessary information, open the | |
| 66 | `/etc/fstab` file: | |
| 67 | ||
| 68 | ```sh | |
| 69 | sudo nano /etc/fstab | |
| 70 | ``` | |
| 71 | ||
| 72 | Each drive you want to mount on boot should have its own line in the | |
| 73 | `/etc/fstab` file that looks similar to this: | |
| 74 | ||
| 75 | ```config | |
| 76 | UUID=B64E53824E5339F7 /mnt/steam_library ntfs-3g uid=1000,gid=1000 0 0 | |
| 77 | ``` | |
| 78 | ||
| 79 | Now all you need to do is unmount your drive and re-mount it. You can | |
| 80 | unmount the drive by doing this (be sure to use the correct drive name | |
| 81 | here): | |
| 82 | ||
| 83 | ```sh | |
| 84 | sudo umount /dev/sdxX | |
| 85 | ``` | |
| 86 | ||
| 87 | You can re-mount all your drives by executing the following: | |
| 88 | ||
| 89 | ```sh | |
| 90 | sudo mount -a | |
| 91 | ``` | |
| 92 | ||
| 93 | If you don't know what your drive name is, or you're nervous about | |
| 94 | unmounting and re-mounting, simply reboot your computer, and it will be | |
| 95 | done for you automatically. | |
content/blog/2020-05-19-customizing-ubuntu.md deleted −210
| @@ -1,210 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-05-19 | |
| 3 | title = "Beginner's Guide: Customizing Ubuntu" | |
| 4 | description = "A beginner's guide to customizing the Ubuntu operating system." | |
| 5 | +++ | |
| 6 | ||
| 7 | # More Information | |
| 8 | ||
| 9 | For inspiration on designing your *nix computer, check out the | |
| 10 | [r/unixporn](https://libredd.it/r/unixporn) subreddit! | |
| 11 | ||
| 12 | # Customizing Ubuntu | |
| 13 | ||
| 14 | New to Linux and want to add a personal touch to your machine? One of | |
| 15 | the best perks of Linux is that it is **extremely** customizable. You | |
| 16 | can change the styles of the windows, shell (status bars/docks), icons, | |
| 17 | fonts, terminals, and more. | |
| 18 | ||
| 19 | In this post, I'm going to go through customization on Ubuntu 20.04 | |
| 20 | (GNOME) since most new users tend to choose Ubuntu-based distros. If | |
| 21 | you've found a way to install Arch with i3-gaps, I'm assuming you know | |
| 22 | how to find more advanced tutorials out there on customizations. | |
| 23 | ||
| 24 | ## Required Tools | |
| 25 | ||
| 26 |  | |
| 28 | ||
| 29 | Ubuntu 20.04 ships with the default desktop environment | |
| 30 | [Gnome](https://www.gnome.org/), which includes the handy | |
| 31 | `gnome-tweaks` tool to quickly change designs. To install | |
| 32 | this, just open your terminal and enter the following command: | |
| 33 | ||
| 34 | ```sh | |
| 35 | sudo apt install gnome-tweaks | |
| 36 | ``` | |
| 37 | ||
| 38 | After you've finished installing the tool, simply launch the Tweaks | |
| 39 | application, and you'll be able to access the various customization | |
| 40 | options available by default on Ubuntu. You might even like some of the | |
| 41 | pre-installed options. | |
| 42 | ||
| 43 | ## GNOME Application Themes | |
| 44 | ||
| 45 | To change the themes applied to applications in GNOME, you will need to | |
| 46 | change the Applications dropdown in the Appearance section of Tweaks. To | |
| 47 | add more themes, you will have to find your preferred theme online and | |
| 48 | follow the steps below to have it show up in the Tweaks tool. While you | |
| 49 | may find themes anywhere, one of the most popular sites for GNOME themes | |
| 50 | is [gnome-look.org](https://www.gnome-look.org/). This website contains | |
| 51 | themes for applications, shells, icons, and cursors. | |
| 52 | ||
| 53 | Steps to import themes into Tweaks: | |
| 54 | ||
| 55 | 1. Download the theme. | |
| 56 | 2. These files are usually compressed (.zip, .tar.gz, .tar.xz), so you | |
| 57 | will need to extract the contents. This is easiest when opening the | |
| 58 | file explorer, right-clicking the compressed file, and choosing | |
| 59 | "Extract here." | |
| 60 | 3. Move the theme folder to `/usr/share/themes/`. You can do | |
| 61 | so with the following command: | |
| 62 | `sudo mv theme-folder/ /usr/share/themes/`. | |
| 63 | - Icons and cursors will be moved to the | |
| 64 | `/usr/share/icons/` folder. | |
| 65 | - Fonts will be moved to the `/usr/share/fonts/` folder | |
| 66 | Alternatively, you can move them to the | |
| 67 | `/usr/share/fonts/opentype/` or | |
| 68 | `/usr/share/fonts/opentype/` folders, if you have a | |
| 69 | specific font type. | |
| 70 | 4. Close tweaks if it is open. Re-open Tweaks and your new theme will | |
| 71 | be available in the Applications dropdown in the Appearance section | |
| 72 | of Tweaks. | |
| 73 | ||
| 74 | If the theme is not showing up after you've moved it into the themes | |
| 75 | folder, you may have uncompressed the folder into a sub-folder. You can | |
| 76 | check this by entering the theme folder and listing the contents: | |
| 77 | ||
| 78 | ```sh | |
| 79 | cd /usr/share/themes/Mojave-Dark && ls -la | |
| 80 | ``` | |
| 81 | ||
| 82 | This is an example of what the contents of your theme folder should look | |
| 83 | like. If you just see another folder there, you should move that folder | |
| 84 | up into the `/usr/share/themes/` folder. | |
| 85 | ||
| 86 | ```sh | |
| 87 | cinnamon COPYING gnome-shell gtk-2.0 gtk-3.0 index.theme metacity-1 plank xfwm4 | |
| 88 | ``` | |
| 89 | ||
| 90 | ## GNOME Shell Themes | |
| 91 | ||
| 92 | To change the appearance of the title bar, default dock, app menu, and | |
| 93 | other parts of the GNOME shell, you'll need to install the [user | |
| 94 | themes](https://extensions.gnome.org/extension/19/user-themes/) | |
| 95 | extension on [Gnome Extensions](https://extensions.gnome.org/). To be | |
| 96 | able to install extensions, you will first need to install the browser | |
| 97 | extension that the website instructs you to. See this screenshot for the | |
| 98 | blue box with a link to the extension. | |
| 99 | ||
| 100 |  | |
| 102 | ||
| 103 | After the browser extension is installed, you will need to install the | |
| 104 | native host connector: | |
| 105 | ||
| 106 | ```sh | |
| 107 | sudo apt install chrome-gnome-shell | |
| 108 | ``` | |
| 109 | ||
| 110 | Finally, you can go the [user | |
| 111 | themes](https://extensions.gnome.org/extension/19/user-themes/) | |
| 112 | extension page and click the installation button. This will enable the | |
| 113 | Shell option in Tweaks. Now you can move shell themes to the | |
| 114 | `/usr/share/themes` directory, using the same steps mentioned | |
| 115 | in the previous section, and enable the new theme in Tweaks. | |
| 116 | ||
| 117 | ## Icons & Cursors | |
| 118 | ||
| 119 | Icons and cursors are installed exactly the same way, so I'm grouping | |
| 120 | these together in this post. Both of these items will need to follow the | |
| 121 | same process as installing themes, except you will want to move your | |
| 122 | font folders to the `/usr/share/icons/` directory instead. | |
| 123 | ||
| 124 | ## Fonts | |
| 125 | ||
| 126 | Fonts are one of the overlooked parts of customization, but a good font | |
| 127 | can make the whole screen look different. For example, I have installed | |
| 128 | the [IBM Plex](https://github.com/IBM/plex/releases) fonts on my system. | |
| 129 | This follows the same process as installing themes, except you will want | |
| 130 | to move your font folders to the `/usr/share/fonts/` | |
| 131 | directory instead. | |
| 132 | ||
| 133 | ## Terminal | |
| 134 | ||
| 135 | If you spend a lot of time typing commands, you know how important the | |
| 136 | style and functionality of the terminal is. After spending a lot of time | |
| 137 | using the default GNOME terminal with [unix | |
| 138 | shell](https://en.wikipedia.org/wiki/Bash_(Unix_shell)), I decided to | |
| 139 | try some different options. I ended up choosing | |
| 140 | [Terminator](https://terminator-gtk3.readthedocs.io/en/latest/) with | |
| 141 | [zsh](https://en.wikipedia.org/wiki/Z_shell). | |
| 142 | ||
| 143 | Terminator is great if you need to open multiple terminals at one time | |
| 144 | by simply right-clicking and splitting the screen into as many terminals | |
| 145 | as you want. While this project hasn't been updated in a while, [it is | |
| 146 | coming under new | |
| 147 | development](https://github.com/gnome-terminator/terminator/issues/1). | |
| 148 | However, this terminal is great and I haven't experienced any errors | |
| 149 | yet. | |
| 150 | ||
| 151 | For the shell choice, I decided to choose zsh after trying it out on a | |
| 152 | fresh Manjaro installation. Zsh is great if you like to change the | |
| 153 | themes of your terminal, include icons, or add plugins. | |
| 154 | ||
| 155 | The desktop uses the | |
| 156 | [zsh-autosuggestions](https://github.com/zsh-users/zsh-autosuggestions) | |
| 157 | to suggest past commands as you type. In addition, it suggests | |
| 158 | corrections if you misspell a command. Lastly, it uses the | |
| 159 | `af-magic` theme, which adds dashed lines between commands, | |
| 160 | moving the user@host tag to the right side of the terminal, and changes | |
| 161 | the colors. There are plenty of plugins and themes to choose from. Just | |
| 162 | figure out what you like and add it to your `~/.zshrc` file! | |
| 163 | ||
| 164 | ### Steps to Replicate My Terminal | |
| 165 | ||
| 166 | To install zsh on Ubuntu, enter the following command into a terminal: | |
| 167 | ||
| 168 | ```sh | |
| 169 | sudo apt install zsh | |
| 170 | ``` | |
| 171 | ||
| 172 | Then, enter the next command to activate zsh: | |
| 173 | ||
| 174 | ```sh | |
| 175 | sudo chsh -s $(which zsh) $(whoami) | |
| 176 | ``` | |
| 177 | ||
| 178 | To install Terminator on Ubuntu: | |
| 179 | ||
| 180 | ```sh | |
| 181 | sudo apt install terminator | |
| 182 | ``` | |
| 183 | ||
| 184 | To install Oh My Zsh on Ubuntu: | |
| 185 | ||
| 186 | ```sh | |
| 187 | sh -c "$(curl -fsSL https://raw.github.com/ohmyzsh/ohmyzsh/master/tools/install.sh)" | |
| 188 | ``` | |
| 189 | ||
| 190 | To install zsh-autosuggestions via Oh My Zsh: | |
| 191 | ||
| 192 | ```sh | |
| 193 | git clone https://github.com/zsh-users/zsh-autosuggestions ${ZSH_CUSTOM:-~/.oh-my-zsh/custom}/plugins/zsh-autosuggestions | |
| 194 | ``` | |
| 195 | ||
| 196 | Then, add the following plugin wording to your `~/.zshrc` | |
| 197 | file (the default config usually has the `git` plugin | |
| 198 | activated, so just add any other plugins to the parentheses separated by | |
| 199 | a space): | |
| 200 | ||
| 201 | ```sh | |
| 202 | nano ~/.zshrc | |
| 203 | ``` | |
| 204 | ||
| 205 | ```sh | |
| 206 | plugins=(git zsh-autosuggestions) | |
| 207 | ``` | |
| 208 | ||
| 209 | Finally, you need to log out of your computer and log back in so your | |
| 210 | user shell can refresh. | |
content/blog/2020-08-22-redirect-github-pages.md deleted −136
| @@ -1,136 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-08-22 | |
| 3 | title = "Redirect GitHub Pages from Subdomain to the Top-Level Domain" | |
| 4 | description = "Learn how to redirect Github pages to the TLD." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Short answer | |
| 8 | ||
| 9 | ## Step 1 | |
| 10 | ||
| 11 | Add a new file CNAME to your GitHub Pages repository containing only one | |
| 12 | line: your top-level domain name. E.g.: `example.com` | |
| 13 | ||
| 14 | ## Step 2 | |
| 15 | ||
| 16 | [Optional] but highly recommended | |
| 17 | ||
| 18 | 2.1: Remove all other top-level records (prefixed with @) of type A from | |
| 19 | your DNS configuration. | |
| 20 | ||
| 21 | 2.2: Remove a CNAME record for the second-level domain www if it is | |
| 22 | present. | |
| 23 | ||
| 24 | ## Step 3 | |
| 25 | ||
| 26 | Add these 5 entries to the very top of your DNS configuration: | |
| 27 | ||
| 28 | ```txt | |
| 29 | @ A 185.199.108.153 | |
| 30 | @ A 185.199.109.153 | |
| 31 | @ A 185.199.110.153 | |
| 32 | @ A 185.199.111.153 | |
| 33 | www CNAME your_github_username.github.io. | |
| 34 | ``` | |
| 35 | ||
| 36 | Replace `your_github_username` with your actual GitHub | |
| 37 | username. | |
| 38 | ||
| 39 | ## Step 4 | |
| 40 | ||
| 41 | Wait for your DNS changes to propagate. DNS changes aren't effective | |
| 42 | immediately. They can take up to a full day to propagate. | |
| 43 | ||
| 44 | # Long answer | |
| 45 | ||
| 46 | This issue has two sides. One is the DNS configuration itself. Another | |
| 47 | one is the way GitHub Pages will forward HTTP requests. | |
| 48 | ||
| 49 | We need to know a few things to understand what GitHub is trying to say | |
| 50 | in their documentation. | |
| 51 | ||
| 52 | ## DNS Entry Types | |
| 53 | ||
| 54 | There are two types of DNS records which interest us: CNAME and A. | |
| 55 | ||
| 56 | `A` is also known as `Apex` or sometimes as | |
| 57 | `root entry`. It forwards requests to a specified fixed IP | |
| 58 | address. `CNAME` entry forwards requests to a specified URL | |
| 59 | (actual valid plain text URL, not an IP address). | |
| 60 | ||
| 61 | ## DNS Load balancing | |
| 62 | ||
| 63 | GitHub has one central URL address which accepts all DNS requests for | |
| 64 | GitHub Pages: `http://username.github.io`. That URL is | |
| 65 | resolved to different IP addresses based on your geographical location. | |
| 66 | Website hosted on GitHub Pages is a simple collection of | |
| 67 | `HTML`, `CSS` and `JS` files. GitHub | |
| 68 | distributes these files to different servers across the globe. So that | |
| 69 | when your browser sends a request from Europe, it receives data from a | |
| 70 | server in Europe. The same is valid for the requests from Asia and the | |
| 71 | USA. | |
| 72 | ||
| 73 | ## What GitHub is trying to say | |
| 74 | ||
| 75 | Since `A` records in DNS must contain IP addresses, and they | |
| 76 | must be either `185.199.108.153` or | |
| 77 | `185.199.109.153` or `185.199.110.153` or | |
| 78 | `185.199.111.153`, there is no way to forward requests to a | |
| 79 | server located somewhere in Europe or Asia. Your website hosted at | |
| 80 | GitHub Pages will be downloaded from a central GitHub Pages server. | |
| 81 | There is a minor risk that if GitHub Pages DNS servers | |
| 82 | (`x.x.x.153`) are down for some reason, all custom domains | |
| 83 | which use fixed GitHub Pages IP addresses will not be accessible (their | |
| 84 | DNS requests will not be resolvable). | |
| 85 | ||
| 86 | That is why GitHub strongly suggests to either use a second-level domain | |
| 87 | for your GitHub Pages (e.g. `blog.example.com`) or use a DNS | |
| 88 | service provider that supports a record type `ALIAS` that | |
| 89 | acts as `A` record but forwards request to a URL address | |
| 90 | (e.g. `username.github.io`) instead of a fixed IP address. | |
| 91 | ||
| 92 | ## How GitHub Pages treats HTTP requests | |
| 93 | ||
| 94 | After a DNS request for `your_github_username.github.io` is | |
| 95 | resolved into an IP address, e.g. `185.199.108.153` your | |
| 96 | browser sends an HTTP request to that server with an HTTP header | |
| 97 | `Host`. Below are `curl` examples that load the | |
| 98 | same website (these examples might not work if you are behind a proxy | |
| 99 | server): | |
| 100 | ||
| 101 | ```sh | |
| 102 | curl --header "Host: your_github_username.github.io" http://185.199.108.153/ | |
| 103 | curl --header "Host: www.example.com" http://185.199.108.153/ | |
| 104 | curl --header "Host: example.com" http://185.199.108.153/ | |
| 105 | ``` | |
| 106 | ||
| 107 | This way GitHub Pages servers know which user website to serve. | |
| 108 | ||
| 109 | > GitHub Pages server will automatically redirect HTTP requests to the | |
| 110 | > top-level domain if your `CNAME` file contains | |
| 111 | > `example.com` but `www.example.com` is | |
| 112 | > requested. | |
| 113 | > | |
| 114 | > The same is valid if your `CNAME` file contains | |
| 115 | > `www.example.com` but the header `Host` in the | |
| 116 | > `HTTP` request contains `example.com`. | |
| 117 | ||
| 118 | ## Why can't I add a `CNAME` record entry that accepts a top-level request (`@`) to my DNS configuration? | |
| 119 | ||
| 120 | Quote from the GitHub Pages documentation: | |
| 121 | ||
| 122 | > Warning: Do not create a CNAME record for your custom apex domain! | |
| 123 | > Doing so may cause issues with other services, such as email, on that | |
| 124 | > domain. | |
| 125 | ||
| 126 | # References: | |
| 127 | ||
| 128 | 1. [Setting up a custom domain with GitHub | |
| 129 | Pages](https://docs.github.com/en/github/working-with-github-pages/configuring-a-custom-domain-for-your-github-pages-site) | |
| 130 | 2. [My custom domain isn't | |
| 131 | working](https://docs.github.com/en/github/working-with-github-pages/troubleshooting-custom-domains-and-github-pages) | |
| 132 | 3. [Cannot access my GitHub Pages website by IP | |
| 133 | Address](https://serverfault.com/questions/589370/cannot-access-my-github-pages-website-by-ip-address) | |
| 134 | 4. [How do I set up GitHub Pages to redirect DNS requests from a | |
| 135 | subdomain (e.g. www) to the top-level domain (TLD, Apex | |
| 136 | record)?](https://stackoverflow.com/questions/23375422/how-do-i-set-up-github-pages-to-redirect-dns-requests-from-a-subdomain-e-g-www) | |
content/blog/2020-12-28-neon-drive.md deleted −94
| @@ -1,94 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2020-12-28 | |
| 3 | title = "Neon Drive: A Nostalgic 80s Arcade Racing Game" | |
| 4 | description = "A video game review for Neon Drive." | |
| 5 | +++ | |
| 6 | ||
| 7 | # Game Description | |
| 8 | ||
| 9 | [Neon Drive](https://store.steampowered.com/app/433910/Neon_Drive/) | |
| 10 | presents itself as a simple arcade-style game inspired by the arcade | |
| 11 | race games of the 1980s, yet it has managed to take up hours of my life | |
| 12 | without much effort. The game description, directly from the Steam page, | |
| 13 | is intriguing enough to entice anyone who's been looking for a good | |
| 14 | arcade racing game: | |
| 15 | ||
| 16 | > Neon Drive is a slick retro-futuristic arcade game that will make your | |
| 17 | > brain melt. You've been warned. From beautiful cityscapes and ocean | |
| 18 | > roads to exploding enemy spaceships, Neon Drive has it all. | |
| 19 | ||
| 20 | # Gameplay | |
| 21 | ||
| 22 | The game holds true to the | |
| 23 | [retro-futurism](https://en.wikipedia.org/wiki/Retrofuturism) style, | |
| 24 | including chrome female robots, pixelated arcade machines, and | |
| 25 | [outrun](https://teddit.net/r/outrun/) aesthetics. | |
| 26 | ||
| 27 | Each level of the game is shown as a separate arcade machine. Each | |
| 28 | arcade machine lets you play on Normal, Hard, Insane, Practice, and Free | |
| 29 | Run. To beat each arcade, you must reach the end of the level without | |
| 30 | crashing your car into the various obstacles on the course. Basic levels | |
| 31 | let you move left or right to avoid blocks in the road. Later levels put | |
| 32 | you through other tests, such as dodging traffic or blasting asteroids. | |
| 33 | ||
| 34 | The game uses synthwave music to keep you on track to make the correct | |
| 35 | moves by timing the beats of the songs to the correct moves on the | |
| 36 | screen. It reminds me of the early Guitar Hero games, as well as mobile | |
| 37 | apps like VOEZ - repetition and staying on-beat is the only way to win. | |
| 38 | ||
| 39 | # In-Game Screenshots | |
| 40 | ||
| 41 | Taking a look at the main menu, you can see that Neon Drive plays into | |
| 42 | every stereotype you can think of around retro-futuristic, synthwave | |
| 43 | arcades (in a good way). | |
| 44 | ||
| 45 |  | |
| 47 | ||
| 48 | Once you get into the first level, we see that the choice of car fits | |
| 49 | right in with the stereotypical cars of the 80s, like the | |
| 50 | [DeLorean](https://en.wikipedia.org/wiki/DMC_DeLorean) or the [Ferrari | |
| 51 | F40](https://en.wikipedia.org/wiki/Ferrari_F40). Each new level comes | |
| 52 | with new color schemes and cars, so you should never get tired of the | |
| 53 | aesthetic. | |
| 54 | ||
| 55 |  | |
| 57 | ||
| 58 | Personally, I love the orange and blue colors used in level 2: | |
| 59 | ||
| 60 |  | |
| 62 | ||
| 63 | If you're the competitive type and getting 100% on all arcade machines | |
| 64 | isn't enough, there are leaderboards for the regular part of the game, | |
| 65 | and the endurance game mode. | |
| 66 | ||
| 67 |  | |
| 68 | ||
| 69 | # Other Suggestions | |
| 70 | ||
| 71 | Neon Drive sits nicely within the well-founded cult genre of Outrun. | |
| 72 | Other games that I've enjoyed in this same spectrum are: | |
| 73 | ||
| 74 | - [Far Cry 3: Blood | |
| 75 | Dragon](https://store.steampowered.com/app/233270/Far_Cry_3__Blood_Dragon/) | |
| 76 | - [Retrowave](https://store.steampowered.com/app/1239690/Retrowave/) | |
| 77 | - [Slipstream](https://store.steampowered.com/app/732810/Slipstream/) | |
| 78 | ||
| 79 | Although these games aren't necessarily in the same genre, they do have | |
| 80 | aspects that place them close enough to interest gamers that enjoyed | |
| 81 | Neon Drive: | |
| 82 | ||
| 83 | - [Black Ice](https://store.steampowered.com/app/311800/Black_Ice/) | |
| 84 | - [Cloudpunk](https://store.steampowered.com/app/746850/Cloudpunk/) | |
| 85 | - [Need for Speed: | |
| 86 | Heat](https://store.steampowered.com/app/1222680/Need_for_Speed_Heat/) | |
| 87 | - [VirtuaVerse](https://store.steampowered.com/app/1019310/VirtuaVerse/) | |
| 88 | ||
| 89 | Of course, if all you really care about is the arcade aspect of these | |
| 90 | games, you can check out the [Atari | |
| 91 | Vault](https://store.steampowered.com/app/400020/Atari_Vault/) or any of | |
| 92 | the other classic games sold on Steam by companies like Namco, Atari. | |
| 93 | For something like Nintendo, you'd have to settle for buying used | |
| 94 | classic consoles or delve into the world of emulation. | |
content/blog/2021-10-09-apache-redirect.md deleted −46
| @@ -1,46 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2021-10-09 | |
| 3 | title = "Apache Redirect HTML Files to a Directory" | |
| 4 | description = "A guide on redirecting HTML files to directory in Apache." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## The Problem | |
| 8 | ||
| 9 | After recently switching static site generators (SSG), my blog URLs | |
| 10 | changed with no option to preserve the classic `.html` | |
| 11 | extension at the end of my blog post URLs. | |
| 12 | ||
| 13 | I really disliked using my old SSG ([Jekyll](https://jekyllrb.com)) and | |
| 14 | prefer my new tool ([Zola](https://www.getzola.org)) much more, so I was | |
| 15 | determined to figure out a way to get the proper redirect set up so that | |
| 16 | people who find my posts online aren't constantly met by 404 errors. | |
| 17 | ||
| 18 | ## The Solution | |
| 19 | ||
| 20 | To solve this problem, I really needed to solve two pieces: | |
| 21 | ||
| 22 | 1. Redirect all blog post URL requests from | |
| 23 | `/blog/some-post.html` to `/blog/some-post/`. | |
| 24 | 2. Ensure that no other `.html` files are redirected, such | |
| 25 | as `index.html`. | |
| 26 | ||
| 27 | After *a lot* of tweaking and testing, I believe I have finally found | |
| 28 | the solution. The solution is shown below. | |
| 29 | ||
| 30 | ```conf | |
| 31 | RewriteEngine On | |
| 32 | RewriteCond %{REQUEST_URI} !\index.html$ [NC] | |
| 33 | RewriteRule ^(.*).html$ https://example.com/$1 [R=301,L] | |
| 34 | ``` | |
| 35 | ||
| 36 | This piece of code in the Apache `.conf` or | |
| 37 | `.htaccess` file will do the following: | |
| 38 | ||
| 39 | 1. Turn on the RewriteEngine so that we can modify URLs. | |
| 40 | 2. Ignore any `index.html` files from the rule we are about | |
| 41 | to specify. | |
| 42 | 3. Find any `.html` files within the website directory and | |
| 43 | redirect it to exclude the file extension. | |
| 44 | 4. The final piece is adding the trailing slash (`/`) at the | |
| 45 | end of the URL - you'll notice that I don't have an Apache rule | |
| 46 | for that since Apache handles that automatically. | |
content/blog/2022-02-17-exiftool.md deleted −67
| @@ -1,67 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-02-17 | |
| 3 | title = "Stripping Image Metadata with exiftool" | |
| 4 | description = "A simple guide to remove exif data with exiftool." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Why Strip Metadata? | |
| 8 | ||
| 9 | Okay, so you want to strip metadata from your photos. Perhaps you take | |
| 10 | pictures of very rare birds, and the location metadata is a gold mine | |
| 11 | for poachers, or perhaps you're just privacy-oriented like me and | |
| 12 | prefer to strip metadata from publicly-available images. | |
| 13 | ||
| 14 | There are various components of image metadata that you may want to | |
| 15 | delete before releasing a photo to the public. Here's an incomplete | |
| 16 | list of things I could easily see just by inspecting a photo on my | |
| 17 | laptop: | |
| 18 | ||
| 19 | - Location (Latitude & Longitude) | |
| 20 | - Dimensions | |
| 21 | - Device Make & Model | |
| 22 | - Color Space | |
| 23 | - Color Profile | |
| 24 | - Focal Length | |
| 25 | - Alpha Channel | |
| 26 | - Red Eye | |
| 27 | - Metering Mode | |
| 28 | - F Number | |
| 29 | ||
| 30 | Regardless of your reasoning, I'm going to explain how I used the | |
| 31 | `exiftool` package in Linux to automatically strip metadata | |
| 32 | from all images in a directory (+ subdirectories). | |
| 33 | ||
| 34 | ## Installing `exiftool` | |
| 35 | ||
| 36 | First things first: we need to install the tool. I'm running Debian 11 | |
| 37 | on my server (Ubuntu will work the same), so the command is as simple | |
| 38 | as: | |
| 39 | ||
| 40 | ```sh | |
| 41 | sudo apt install exiftool | |
| 42 | ``` | |
| 43 | ||
| 44 | There are different tools that can accomplish the same thing across | |
| 45 | distributions, but I really only care to test out this one package. | |
| 46 | ||
| 47 | ## Recursively Strip Data | |
| 48 | ||
| 49 | I actually use this tool extensively to strip any photos uploaded to the | |
| 50 | website that serves all the images for my blog | |
| 51 | (`img.cleberg.net`). | |
| 52 | ||
| 53 | The following command is incredibly useful and can be modified to | |
| 54 | include any image extensions that `exiftool` supports: | |
| 55 | ||
| 56 | ```sh | |
| 57 | exiftool -r -all= -ext jpg -ext png /path/to/directory/ | |
| 58 | ``` | |
| 59 | ||
| 60 | See below for the results of my most recent usage of | |
| 61 | `exiftool` after I uploaded the image for this blog post. You | |
| 62 | can see that the command will let you know how many directories were | |
| 63 | scanned, how many images were updated, and how many images were | |
| 64 | unchanged. | |
| 65 | ||
| 66 |  | |
content/blog/2022-02-20-nginx-caching.md deleted −72
| @@ -1,72 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-02-20 | |
| 3 | title = "Caching Static Content with Nginx" | |
| 4 | description = "Learn how to enable the static content cache in Nginx." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Update Your Nginx Config to Cache Static Files | |
| 8 | ||
| 9 | If you run a website on Nginx that serves static content (i.e., content | |
| 10 | that is not dynamic and changing with interactions from the user), you | |
| 11 | would likely benefit from caching that content on the client-side. If | |
| 12 | you're used to Apache and looking for the Nginx equivalent, this post | |
| 13 | should help. | |
| 14 | ||
| 15 | Luckily, setting up the cache is as easy as identifying the file types | |
| 16 | you want to cache and determining the expiration length. To include more | |
| 17 | file types, simply use the bar separator (`|`) and type the | |
| 18 | new file extension you want to include. | |
| 19 | ||
| 20 | ```config | |
| 21 | server { | |
| 22 | ... | |
| 23 | ||
| 24 | location ~* .(css|js|jpg|jpeg|gif|png|ico)$ { | |
| 25 | expires 30d; | |
| 26 | } | |
| 27 | ||
| 28 | ... | |
| 29 | } | |
| 30 | ``` | |
| 31 | ||
| 32 | I have seen some people who prefer to set `expires` as | |
| 33 | `365d` or even `max`, but that is only for stable, | |
| 34 | infrequently changing websites. As my site often changes (i.e., I'm | |
| 35 | never content with my website), I need to know that my readers are | |
| 36 | seeing the new content without waiting too long. | |
| 37 | ||
| 38 | So, I went ahead and set the expiration date at `30d`, which | |
| 39 | is short enough to refresh for readers but long enough that | |
| 40 | clients/browsers won't be re-requesting the static files too often, | |
| 41 | hopefully resulting in faster loading times, as images should be the | |
| 42 | only thing slowing down my site. | |
| 43 | ||
| 44 | ## Testing Results | |
| 45 | ||
| 46 | To test my changes to the Nginx configuration, I used the [HTTP Header | |
| 47 | Live](https://addons.mozilla.org/en-US/firefox/addon/http-header-live/) | |
| 48 | extension on my Gecko browser and used the sidebar to inspect the | |
| 49 | headers of a recent image from my blog. | |
| 50 | ||
| 51 | In the image below, you can see that the `Cache-Control` | |
| 52 | header is now present and set to 2592000, which is 30 days represented | |
| 53 | in seconds (30 days \_ 24 hours/day \_ 60 minutes/hour \* 60 | |
| 54 | seconds/minute = 2,592,000 seconds). | |
| 55 | ||
| 56 | The `Expires` field is now showing 22 March 2022, which is 30 | |
| 57 | days from the day of this post, 20 February 2022. | |
| 58 | ||
| 59 |  | |
| 61 | ||
| 62 | ## Caveats | |
| 63 | ||
| 64 | Remember that this caching system is **client-side**, which means that | |
| 65 | content is only cached for as long as a client allows it. For example, | |
| 66 | my browser purges all caches, data, etc. upon exit, so this caching | |
| 67 | policy will only work as long as my browser remains open and running. | |
| 68 | ||
| 69 | If you need to test updates to your site, you'll need to clear the | |
| 70 | cache to see updates for any file extension you configured. This can | |
| 71 | often be done with the `Shift + F5` or `Ctrl + F5` | |
| 72 | key combinations in most browsers. | |
content/blog/2022-02-22-tuesday.md deleted −41
| @@ -1,41 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-02-22 | |
| 3 | title = "Tuesday" | |
| 4 | description = "2-22-22 || 22-2-22" | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Tuesday, Twosday | |
| 8 | ||
| 9 | I'm taking a break from my usual technology-related posts and writing | |
| 10 | about something a little more enjoyable today. | |
| 11 | ||
| 12 | Today is Tuesday, February 22nd, 2022. Today is 02-22-2022. Today is | |
| 13 | Twosday. | |
| 14 | ||
| 15 | Let's look at everything that fell in place today: | |
| 16 | ||
| 17 | 1. Written in the `m-dd-yy` or `dd-m-yy` formats, | |
| 18 | today is 2-22-22 or 22-2-22, which is a neat little palindrome in | |
| 19 | either format. (The last ubiquitous six-digit palindrome was | |
| 20 | 1-11-11.) | |
| 21 | 2. Today is Tuesday, which is why everyone is using the nickname | |
| 22 | Twosday to call out these similarities. | |
| 23 | 3. Falling on Tuesday means today is the 2nd day of the week (for most | |
| 24 | cultures. For the US, it's the 3rd day of the week since we start | |
| 25 | on Sunday). | |
| 26 | 4. The only culture I could find with a connection to a `2` | |
| 27 | is that some Slavic languages derived their version of Tuesday from | |
| 28 | the Old Church Slavonic word `въторъ`, meaning "the | |
| 29 | second." | |
| 30 | 5. Written in the classic monospaced, digital font (think of digital | |
| 31 | clocks from the 80s/90s), there is nice symmetry to the numbers | |
| 32 | ([view the image | |
| 33 | here](https://img.cleberg.net/blog/20220222-tuesday/digital_font.png)!). | |
| 34 | 6. This one isn't naturally-occurring, but it seems people around the | |
| 35 | world are celebrating the day. For example, a group is putting | |
| 36 | together | |
| 37 | [[<https://www.eventbrite.com/e/2-22-22-a-collective-wedding-ceremony-at-the-state-capitol-tickets-211434605597>][a | |
| 38 | wedding of 222 couples at the California State Capitol in | |
| 39 | Sacramento]], concluding at exactly 2:22 PM. These couples will | |
| 40 | record their marriage dates as 2-22-22 2:22 PM. Tickets were on sale | |
| 41 | for \$222.22. | |
content/blog/2022-03-03-financial-database.md deleted −271
| @@ -1,271 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-03-03 | |
| 3 | title = "Maintaining a Personal Financial Database" | |
| 4 | description = "An example project showing to build and maintain a simple financial database." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Personal Financial Tracking | |
| 8 | ||
| 9 | For the last 6-ish years, I've tracked my finances in a spreadsheet. | |
| 10 | This is common practice in the business world, but any good dev will | |
| 11 | cringe at the thought of storing long-term data in a spreadsheet. A | |
| 12 | spreadsheet is not for long-term storage or as a source of data to pull | |
| 13 | data/reports. | |
| 14 | ||
| 15 | As I wanted to expand the functionality of my financial data (e.g., | |
| 16 | adding more reports), I decided to migrate the data into a database. To | |
| 17 | run reports, I would query the database and use a language like Python | |
| 18 | or Javascript to process the data, perform calculations, and visualize | |
| 19 | the data. | |
| 20 | ||
| 21 | ## SQLite | |
| 22 | ||
| 23 | When choosing the type of database I wanted to use for this project, I | |
| 24 | was split between three options: | |
| 25 | ||
| 26 | 1. MySQL: The database I have the most experience with and have used | |
| 27 | for years. | |
| 28 | 2. PostgreSQL: A database I'm new to, but want to learn. | |
| 29 | 3. SQLite: A database that I've used for a couple projects and have | |
| 30 | moderate experience. | |
| 31 | ||
| 32 | I ended up choosing SQLite since it can be maintained within a single | |
| 33 | `.sqlite` file, which allows me more flexibility for storage | |
| 34 | and backup. I keep this file in my cloud storage and pull it up whenever | |
| 35 | needed. | |
| 36 | ||
| 37 | ### GUI Editing | |
| 38 | ||
| 39 | Since I didn't want to try and import 1000--1500 records into my new | |
| 40 | database via the command line, I opted to use [DB Browser for SQLite | |
| 41 | (DB4S)](https://sqlitebrowser.org/) as a GUI tool. This application is | |
| 42 | excellent, and I don't see myself going back to the CLI when working in | |
| 43 | this database. | |
| 44 | ||
| 45 | DB4S allows you to copy a range of cells from a spreadsheet and paste it | |
| 46 | straight into the SQL table. I used this process for all 36 accounts, | |
| 47 | 1290 account statements, and 126 pay statements. Overall, I'm guessing | |
| 48 | this took anywhere between 4--8 hours. In comparison, it probably took | |
| 49 | me 2-3 days to initially create the spreadsheet. | |
| 50 | ||
| 51 |  | |
| 52 | ||
| 53 | ### Schema | |
| 54 | ||
| 55 | The schema for this database is actually extremely simple and involves | |
| 56 | only three tables (for now): | |
| 57 | ||
| 58 | 1. Accounts | |
| 59 | 2. Statements | |
| 60 | 3. Payroll | |
| 61 | ||
| 62 | **Accounts** | |
| 63 | ||
| 64 | The Accounts table contains summary information about an account, such | |
| 65 | as a car loan or a credit card. By viewing this table, you can find | |
| 66 | high-level data, such as interest rate, credit line, or owner. | |
| 67 | ||
| 68 | ```sql | |
| 69 | CREATE TABLE "Accounts" ( | |
| 70 | "AccountID" INTEGER NOT NULL UNIQUE, | |
| 71 | "AccountType" TEXT, | |
| 72 | "AccountName" TEXT, | |
| 73 | "InterestRate" NUMERIC, | |
| 74 | "CreditLine" NUMERIC, | |
| 75 | "State" TEXT, | |
| 76 | "Owner" TEXT, | |
| 77 | "Co-Owner" TEXT, | |
| 78 | PRIMARY KEY("AccountID" AUTOINCREMENT) | |
| 79 | ) | |
| 80 | ``` | |
| 81 | ||
| 82 | **Statements** | |
| 83 | ||
| 84 | The Statements table uses the same unique identifier as the Accounts | |
| 85 | table, meaning you can join the tables to find a monthly statement for | |
| 86 | any of the accounts listed in the Accounts table. Each statement has an | |
| 87 | account ID, statement date, and total balance. | |
| 88 | ||
| 89 | ```sql | |
| 90 | CREATE TABLE "Statements" ( | |
| 91 | "StatementID" INTEGER NOT NULL UNIQUE, | |
| 92 | "AccountID" INTEGER, | |
| 93 | "StatementDate" INTEGER, | |
| 94 | "Balance" NUMERIC, | |
| 95 | PRIMARY KEY("StatementID" AUTOINCREMENT), | |
| 96 | FOREIGN KEY("AccountID") REFERENCES "Accounts"("AccountID") | |
| 97 | ) | |
| 98 | ``` | |
| 99 | ||
| 100 | **Payroll** | |
| 101 | ||
| 102 | The Payroll table is a separate entity, unrelated to the Accounts or | |
| 103 | Statements tables. This table contains all information you would find on | |
| 104 | a pay statement from an employer. As you change employers or obtain new | |
| 105 | perks/benefits, just add new columns to adapt to the new data. | |
| 106 | ||
| 107 | ```sql | |
| 108 | CREATE TABLE "Payroll" ( | |
| 109 | "PaycheckID" INTEGER NOT NULL UNIQUE, | |
| 110 | "PayDate" TEXT, | |
| 111 | "Payee" TEXT, | |
| 112 | "Employer" TEXT, | |
| 113 | "JobTitle" TEXT, | |
| 114 | "IncomeRegular" NUMERIC, | |
| 115 | "IncomePTO" NUMERIC, | |
| 116 | "IncomeHoliday" NUMERIC, | |
| 117 | "IncomeBonus" NUMERIC, | |
| 118 | "IncomePTOPayout" NUMERIC, | |
| 119 | "IncomeReimbursements" NUMERIC, | |
| 120 | "FringeHSA" NUMERIC, | |
| 121 | "FringeStudentLoan" NUMERIC, | |
| 122 | "Fringe401k" NUMERIC, | |
| 123 | "PreTaxMedical" NUMERIC, | |
| 124 | "PreTaxDental" NUMERIC, | |
| 125 | "PreTaxVision" NUMERIC, | |
| 126 | "PreTaxLifeInsurance" NUMERIC, | |
| 127 | "PreTax401k" NUMERIC, | |
| 128 | "PreTaxParking" NUMERIC, | |
| 129 | "PreTaxStudentLoan" NUMERIC, | |
| 130 | "PreTaxOther" NUMERIC, | |
| 131 | "TaxFederal" NUMERIC, | |
| 132 | "TaxSocial" NUMERIC, | |
| 133 | "TaxMedicare" NUMERIC, | |
| 134 | "TaxState" NUMERIC, | |
| 135 | PRIMARY KEY("PaycheckID" AUTOINCREMENT) | |
| 136 | ) | |
| 137 | ``` | |
| 138 | ||
| 139 | ### Python Reporting | |
| 140 | ||
| 141 | Once I created the database tables and imported all my data, the only | |
| 142 | step left was to create a process to report and visualize on various | |
| 143 | aspects of the data. | |
| 144 | ||
| 145 | In order to explore and create the reports I'm interested in, I | |
| 146 | utilized a two-part process involving Jupyter Notebooks and Python | |
| 147 | scripts. | |
| 148 | ||
| 149 | 1. Step 1: Jupyter Notebooks | |
| 150 | ||
| 151 | When I need to explore data, try different things, and re-run my | |
| 152 | code cell-by-cell, I use Jupyter Notebooks. For example, I explored | |
| 153 | the `Accounts` table until I found the following useful | |
| 154 | information: | |
| 155 | ||
| 156 | ```python | |
| 157 | import sqlite3 | |
| 158 | import pandas as pd | |
| 159 | import matplotlib | |
| 160 | ||
| 161 | # Set up database filename and connect | |
| 162 | db = "finances.sqlite" | |
| 163 | connection = sqlite3.connect(db) | |
| 164 | df = pd.read_sql_query("SELECT * FROM Accounts", connection) | |
| 165 | ||
| 166 | # Set global matplotlib variables | |
| 167 | %matplotlib inline | |
| 168 | matplotlib.rcParams['text.color'] = 'white' | |
| 169 | matplotlib.rcParams['axes.labelcolor'] = 'white' | |
| 170 | matplotlib.rcParams['xtick.color'] = 'white' | |
| 171 | matplotlib.rcParams['ytick.color'] = 'white' | |
| 172 | matplotlib.rcParams['legend.labelcolor'] = 'black' | |
| 173 | ||
| 174 | # Display graph | |
| 175 | df.groupby(['AccountType']).sum().plot.pie(title='Credit Line by Account Type', y='CreditLine', figsize=(5,5), autopct='%1.1f%%') | |
| 176 | ``` | |
| 177 | ||
| 178 | 2. Step 2: Python Scripts | |
| 179 | ||
| 180 | Once I explored enough through the notebooks and had a list of | |
| 181 | reports I wanted, I moved on to create a Python project with the | |
| 182 | following structure: | |
| 183 | ||
| 184 | ```txt | |
| 185 | finance/ | |
| 186 | ├── notebooks/ | |
| 187 | │ │ ├── account_summary.ipynb | |
| 188 | │ │ ├── account_details.ipynb | |
| 189 | │ │ └── payroll.ipynb | |
| 190 | ├── public/ | |
| 191 | │ │ ├── image-01.png | |
| 192 | │ │ └── image-0X.png | |
| 193 | ├── src/ | |
| 194 | │ └── finance.sqlite | |
| 195 | ├── venv/ | |
| 196 | ├── _init.py | |
| 197 | ├── database.py | |
| 198 | ├── process.py | |
| 199 | ├── requirements.txt | |
| 200 | └── README.md | |
| 201 | ``` | |
| 202 | ||
| 203 | This structure allows me to: | |
| 204 | ||
| 205 | 1. Compile all required python packages into | |
| 206 | `requirements.txt` for easy installation if I move to | |
| 207 | a new machine. | |
| 208 | 2. Activate a virtual environment in `venv/` so I don't | |
| 209 | need to maintain a system-wide Python environment just for this | |
| 210 | project. | |
| 211 | 3. Keep my `notebooks/` folder to continuously explore | |
| 212 | the data as I see fit. | |
| 213 | 4. Maintain a local copy of the database in `src/` for | |
| 214 | easy access. | |
| 215 | 5. Export reports, images, HTML files, etc. to | |
| 216 | `public/`. | |
| 217 | ||
| 218 | Now, onto the differences between the code in a Jupyter Notebook and | |
| 219 | the actual Python files. To create the report in the Notebook | |
| 220 | snippet above, I created the following function inside | |
| 221 | `process.py`: | |
| 222 | ||
| 223 | ```python | |
| 224 | # Create summary pie chart | |
| 225 | def summary_data(accounts: pandas.DataFrame) -> None: | |
| 226 | accounts_01 = accounts[accounts["Owner"] == "Person01"] | |
| 227 | accounts_02 = accounts[accounts["Owner"] == "Person02"] | |
| 228 | for x in range(1, 4): | |
| 229 | if x == 1: | |
| 230 | df = accounts | |
| 231 | account_string = "All Accounts" | |
| 232 | elif x == 2: | |
| 233 | df = accounts_01 | |
| 234 | account_string = "Person01's Accounts" | |
| 235 | elif x == 3: | |
| 236 | df = accounts_02 | |
| 237 | account_string = "Person02's Accounts" | |
| 238 | print(f"Generating pie chart summary image for {account_string}...") | |
| 239 | summary_chart = ( | |
| 240 | df.groupby(["AccountType"]) | |
| 241 | .sum() | |
| 242 | .plot.pie( | |
| 243 | title=f"Credit Line by Type for {account_string}", | |
| 244 | y="CreditLine", | |
| 245 | autopct="%1.1f%%", | |
| 246 | ) | |
| 247 | ) | |
| 248 | summary_chart.figure.savefig(f"public/summary_chart_{x}.png", dpi=1200) | |
| 249 | ``` | |
| 250 | ||
| 251 | The result? A high-quality pie chart that is read directly by the | |
| 252 | `public/index.html` template I use. | |
| 253 | ||
| 254 |  | |
| 256 | ||
| 257 | Other charts generated by this project include: | |
| 258 | ||
| 259 | - Charts of account balances over time. | |
| 260 | - Line chart of effective tax rate (taxes divided by taxable | |
| 261 | income). | |
| 262 | - Salary projections and error limits using past income and | |
| 263 | inflation rates. | |
| 264 | - Multi-line chart of gross income, taxable income, and net | |
| 265 | income. | |
| 266 | ||
| 267 | The best thing about this project? I can improve it at any given | |
| 268 | time, shaping it into whatever helps me the most for that time. I | |
| 269 | imagine that I will be introducing an asset tracking table soon to | |
| 270 | track the depreciating value of cars, houses, etc. Who knows what's | |
| 271 | next? | |
content/blog/2022-03-08-plex-migration.md deleted −253
| @@ -1,253 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-03-08 | |
| 3 | title = "Migrating Plex to a New Server (& Nvidia Transcoding)" | |
| 4 | description = "A retrospective on migrating Plex between servers and enabling Nvidia GPU transcoding." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Migration Phases | |
| 8 | ||
| 9 | I recently decided to migrate my server from an old OptiPlex desktop | |
| 10 | machine to a custom-built tower with better hardware in every category. | |
| 11 | In order to do this, I would need to properly migrate a full Plex | |
| 12 | installation. | |
| 13 | ||
| 14 | The second part of this migration is that the new server uses an Nvidia | |
| 15 | GPU and does not have any integrated graphics, which requires extra work | |
| 16 | for installation, but provides much better hardware transcoding options | |
| 17 | for Plex. | |
| 18 | ||
| 19 | Therefore, I have broken this migration down into three phases: | |
| 20 | ||
| 21 | 1. [Configure the New Server](#phase-1-configure-the-new-server) | |
| 22 | 2. [Migrate Plex Data & Devices](#phase-2-migrate-plex-data-devices) | |
| 23 | 3. [Configure GPU Transcoding](#phase-3-configure-gpu-transcoding) | |
| 24 | ||
| 25 | ------------------------------------------------------------------------ | |
| 26 | ||
| 27 | ## Phase 1: Configure the New Server | |
| 28 | ||
| 29 | ### Choosing an OS | |
| 30 | ||
| 31 | In order to migrate Plex to my new server, I first needed to choose an | |
| 32 | appropriate operating system (OS) and install it on the machine. Given | |
| 33 | that I have encountered numerous issues installing other Linux | |
| 34 | distributions properly with Nvidia graphics, I chose [Ubuntu | |
| 35 | Server](https://ubuntu.com/download/server). | |
| 36 | ||
| 37 | The first step is to create a bootable USB with Ubuntu Server. This is | |
| 38 | easy with [Etcher](https://www.balena.io/etcher/), an app that runs on | |
| 39 | many different platforms. Just download the Ubuntu Server | |
| 40 | `.iso` image, launch Etcher, and install the | |
| 41 | `.iso` on the USB. | |
| 42 | ||
| 43 | Once the USB is created, insert it into my server, reboot, and click | |
| 44 | `Esc` (or any of the `F1-12` keys) until the BIOS | |
| 45 | menu appears. Finally, launch the USB boot drive. | |
| 46 | ||
| 47 | ### Booting with Nvidia | |
| 48 | ||
| 49 | In order to install Ubuntu Server with an Nvidia Graphics card (and no | |
| 50 | integrated graphics on this device for some reason), you'll have to | |
| 51 | configure the boot menu to allow different graphics drivers to be | |
| 52 | loaded. | |
| 53 | ||
| 54 | When booting from the USB, the machine will launch the initial | |
| 55 | installation menu. From this menu, type `e` to view the | |
| 56 | default command options that come with the device - it's a good idea to | |
| 57 | take a photo of this screen, so you can enter these commands on the next | |
| 58 | screen (along with adding support for Nvidia). | |
| 59 | ||
| 60 | Finally, type `Ctrl + C` to enter the command line. From this | |
| 61 | command line, enter the commands found on the `e` screen. | |
| 62 | \*Remember to add `nomodeset` to the `linux ...` | |
| 63 | line so that your Nvidia device will display the installation screens | |
| 64 | properly!\* | |
| 65 | ||
| 66 | Here's an example of the commands I pulled from the `e` | |
| 67 | screen and entered on the command line. | |
| 68 | ||
| 69 | ```sh | |
| 70 | setparams 'Install Ubuntu Server' | |
| 71 | setgfxpayload=keep | |
| 72 | linux /casper/vmlinuz quiet nomodeset --- | |
| 73 | initrd /casper/initrd | |
| 74 | boot | |
| 75 | ``` | |
| 76 | ||
| 77 |  | |
| 79 | ||
| 80 |  | |
| 82 | ||
| 83 | Once the machine is rebooted, enter the `e` screen again and | |
| 84 | add `nomodeset` to the `linux ...` line again and | |
| 85 | press `Ctrl + X` to save the boot options. | |
| 86 | ||
| 87 | The machine is now fully installed and can properly display on an | |
| 88 | external display using the Nvidia GPU. | |
| 89 | ||
| 90 | Always remember to update and upgrade on a new installation: | |
| 91 | ||
| 92 | ```sh | |
| 93 | sudo apt update; sudo apt upgrade -y; sudo apt autoremove -y | |
| 94 | ``` | |
| 95 | ||
| 96 | ------------------------------------------------------------------------ | |
| 97 | ||
| 98 | ## Phase 2: Migrate Plex Data & Devices | |
| 99 | ||
| 100 | This phase uses the great Plex article on migrations ([Move an | |
| 101 | Installation to Another | |
| 102 | System](https://support.plex.tv/articles/201370363-move-an-install-to-another-system/)) | |
| 103 | and adds a bit more information to help with commands and context. | |
| 104 | ||
| 105 | ### Terminology | |
| 106 | ||
| 107 | **Source:** The original server that is being replaced.\ | |
| 108 | **Destination:** The new server.\ | |
| 109 | **Client:** Any application that can be used to modify settings for both | |
| 110 | source/destination. | |
| 111 | ||
| 112 | ### Step 01: [Client] Update Settings | |
| 113 | ||
| 114 | Open up a Plex app and *disable* the `Account` \> | |
| 115 | `Library` \> | |
| 116 | `Empty trash automatically after every scan` preference for | |
| 117 | the source server. | |
| 118 | ||
| 119 | ### Step 02: [Destination] Install Plex | |
| 120 | ||
| 121 | Open up the [Plex Media Server download | |
| 122 | page](https://www.plex.tv/media-server-downloads/) and copy the link for | |
| 123 | the appropriate platform. | |
| 124 | ||
| 125 | Execute the following commands on the destination server to install | |
| 126 | Plex: | |
| 127 | ||
| 128 | ```sh | |
| 129 | wget <url> | |
| 130 | sudo dpkg -i <filename> | |
| 131 | sudo systemctl stop plexmediaserver.service | |
| 132 | ``` | |
| 133 | ||
| 134 | ### Step 03: [Source] Stop Plex & Migrate Data | |
| 135 | ||
| 136 | First, stop the Plex service so that no data is created or modified | |
| 137 | during the migration. | |
| 138 | ||
| 139 | ```sh | |
| 140 | sudo systemctl stop plexmediaserver.service | |
| 141 | ``` | |
| 142 | ||
| 143 | Next, copy the data to the new server. To find where the Plex data | |
| 144 | directory is located, Plex has another excellent article available: | |
| 145 | [Where is the Plex Media Server data directory | |
| 146 | located?](https://support.plex.tv/articles/202915258-where-is-the-plex-media-server-data-directory-located/). | |
| 147 | ||
| 148 | There are many ways to copy the data to the new server and will largely | |
| 149 | depend on the size of the folder being copied. Personally, my data | |
| 150 | folder was \~23GB and I opted to simply use the `scp` command | |
| 151 | to copy the files over SSH. | |
| 152 | ||
| 153 | This process was throttled by the old server's slow HDD and ports and | |
| 154 | took approximately 90 minutes to complete. In comparison, moving the | |
| 155 | data from the new server's `home/user/` directory to the | |
| 156 | `/var/.../Plex Media Server` directory took 2-3 minutes. | |
| 157 | ||
| 158 | ```sh | |
| 159 | scp -r "/var/lib/plexmediaserver/Library/Application Support/Plex Media Server" your_user@xxx.xxx.xxx.xxx:"'/path/to/destination/'" | |
| 160 | ``` | |
| 161 | ||
| 162 | ### Step 04: [Destination] Update File Permissions | |
| 163 | ||
| 164 | In case you move the data directory to a common area on the new server, | |
| 165 | it will have to be moved to the proper location before Plex can function | |
| 166 | properly: | |
| 167 | ||
| 168 | ```sh | |
| 169 | mv "Plex Media Server" /var/lib/plexmediaserver/Library/Application Support/ | |
| 170 | ``` | |
| 171 | ||
| 172 | To ensure permissions were retained properly, the server will need to | |
| 173 | show that all files and folders in the data directory are owned by | |
| 174 | `plex:plex` (or whichever user is running the Plex | |
| 175 | application). | |
| 176 | ||
| 177 | ```sh | |
| 178 | sudo chown -R plex:plex "/var/lib/plexmediaserver/Library/Application Support/Plex Media Server" | |
| 179 | ``` | |
| 180 | ||
| 181 | Finally, start the service and check the status. | |
| 182 | ||
| 183 | ```sh | |
| 184 | sudo systemctl start plexmediaserver.service | |
| 185 | sudo systemctl status plexmediaserver.service | |
| 186 | ``` | |
| 187 | ||
| 188 | ### Step 05: [Client] Update Libraries & Metadata | |
| 189 | ||
| 190 | The first step - now that the new server is up and running - is to sign | |
| 191 | out of the client and sign back in. Once this is done, update any | |
| 192 | library locations, if necessary. This was unnecessary in my case since I | |
| 193 | simply moved my storage drives from the source server to the destination | |
| 194 | server. | |
| 195 | ||
| 196 | Next, perform the following actions in the client: | |
| 197 | ||
| 198 | 1. On the left sidebar, click `More` \> Three-Dot Menu \> | |
| 199 | `Scan Library Files` | |
| 200 | 2. *Enable* the `Account` \> `Library` \> | |
| 201 | `Empty trash automatically after every scan` preference | |
| 202 | for the source server. | |
| 203 | 3. On the left sidebar, click `More` \> Three-Dot Menu \> | |
| 204 | `Manage Server` \> `Empty Trash` | |
| 205 | 4. On the left sidebar, click `More` \> Three-Dot Menu \> | |
| 206 | `Manage Server` \> `Clean Bundles` | |
| 207 | 5. On the left sidebar, click `More` \> Three-Dot Menu \> | |
| 208 | `Manage Server` \> `Optimize Database` | |
| 209 | ||
| 210 | Finally, double-check the Remote Access settings to make sure no changes | |
| 211 | have caused issues with accessing the server from outside the network. | |
| 212 | ||
| 213 | In my case, I use a single port forwarding rule in my router and needed | |
| 214 | to update the Local LAN IP Address to the new server IP address. | |
| 215 | ||
| 216 |  | |
| 218 | ||
| 219 | ------------------------------------------------------------------------ | |
| 220 | ||
| 221 | ## Phase 3: Configure GPU Transcoding | |
| 222 | ||
| 223 | The final piece to the migration is enabling hardware transcoding so | |
| 224 | that Plex can fully utilize the new Nvidia GPU available in the server. | |
| 225 | The first step is to install Nvidia graphics drivers. This process may | |
| 226 | take a few minutes, but the commands are pretty simple: | |
| 227 | ||
| 228 | ```sh | |
| 229 | sudo add-apt-repository ppa:graphics-drivers/ppa | |
| 230 | sudo apt update | |
| 231 | sudo apt-get install ubuntu-drivers-common | |
| 232 | sudo ubuntu-drivers autoinstall | |
| 233 | ``` | |
| 234 | ||
| 235 | Finally, reboot so that the changes are loaded: | |
| 236 | ||
| 237 | ```sh | |
| 238 | sudo reboot now | |
| 239 | ``` | |
| 240 | ||
| 241 | To ensure that the Nvidia graphics drivers are working properly, run the | |
| 242 | following command to view the available GPUs, statistics, and processes: | |
| 243 | ||
| 244 | ```sh | |
| 245 | sudo nvidia-smi | |
| 246 | ``` | |
| 247 | ||
| 248 |  | |
| 249 | ||
| 250 | Finally, enable hardware transcoding settings in the Plex application: | |
| 251 | ||
| 252 |  | |
content/blog/2022-03-24-server-hardening.md deleted −353
| @@ -1,353 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-03-24 | |
| 3 | title = "Hardening a Public-Facing Home Server" | |
| 4 | description = "Learn some basic techniques to harden a home server and network." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Post Updates | |
| 8 | ||
| 9 | > After reviewing this post today (2022-10-04), I noticed quite a few | |
| 10 | > gaps in my write-up and wanted to add a few things, even though this | |
| 11 | > blog is really just a retrospective and knowledge dump for myself. I | |
| 12 | > left things intact and simply crossed them out (~~like this~~) for | |
| 13 | > posterity. | |
| 14 | ||
| 15 | ## Planning Data Flows & Security | |
| 16 | ||
| 17 | ### My Personal Data Flow | |
| 18 | ||
| 19 | ```txt | |
| 20 | ┌───────┐ ┌─────────────────┐ | |
| 21 | ┌──► VLAN1 ├───► Private Devices │ | |
| 22 | │ └───────┘ └─────────────────┘ | |
| 23 | ┌──────────┐ ┌────────┐ ┌──────────┐ ┌────────┐ │ | |
| 24 | │ Internet ├───► Router ├───► Firewall ├───► Switch ├──┤ | |
| 25 | └──────────┘ └────────┘ └──────────┘ └────────┘ │ | |
| 26 | │ ┌───────┐ ┌───────────────┐ | |
| 27 | └──► VLAN2 ├───► Public Server │ | |
| 28 | └───────┘ └───────────────┘ | |
| 29 | ``` | |
| 30 | ||
| 31 | ### Thought Process | |
| 32 | ||
| 33 | To serve content from your home server and harden your security posture, | |
| 34 | you have to think about the transport of data from `server` | |
| 35 | to `client`. | |
| 36 | ||
| 37 | Let's start with the actual server itself. Think about the following: | |
| 38 | ||
| 39 | - Do I have a firewall enabled? Do I need to update this to allow new | |
| 40 | ports or IPs? | |
| 41 | - Do I have an IPS/IDS that may prevent outside traffic? | |
| 42 | - Do I have any other security software installed? | |
| 43 | - Are the services hosted inside Docker containers, behind a reverse | |
| 44 | proxy, or virtualized? If so, are they configured to allow outside | |
| 45 | traffic? | |
| 46 | ||
| 47 | Once the data leaves the server, where does it go? In my case, it goes | |
| 48 | to a managed switch. In this case, I asked the following: | |
| 49 | ||
| 50 | - What configurations is the switch using? | |
| 51 | - Am I using VLANs? | |
| 52 | - Yes, I am using 802.1Q VLANs. | |
| 53 | - Are the VLANs configured properly? | |
| 54 | - Yes, as shown in the [Switch](#switch) section below, I have a | |
| 55 | separate VLAN to allow outside traffic to and from the server | |
| 56 | alone. No other devices, except for a service port, and in that | |
| 57 | VLAN. | |
| 58 | ||
| 59 | At this point, the data has been processed through the switch. Where | |
| 60 | does it go next? In my case, it's pretty simple: it goes to the | |
| 61 | router/modem device. | |
| 62 | ||
| 63 | - Does my ISP block any ports that I need? | |
| 64 | - This is an important step that a lot of people run into when | |
| 65 | self-hosting at home. Use an online port-checker tool for your | |
| 66 | IP or call your ISP if you think ports are blocked. | |
| 67 | - Is there a router firewall? | |
| 68 | - Yes, I checked that it's configured to allow the ports I need | |
| 69 | to run my services publicly. Common web servers and reverse | |
| 70 | proxies require ports 80 and 443, but other services like media | |
| 71 | servers or games can require unique ports, so be sure to check | |
| 72 | the documentation for your service(s). | |
| 73 | - Are there any other settings affecting inbound/outbound traffic? | |
| 74 | - Schedules or access blocks | |
| 75 | - Static Routing | |
| 76 | - QoS | |
| 77 | - Port Forwarding | |
| 78 | - DMZ Hosting | |
| 79 | - Remote Management (this can sometimes mess with services that | |
| 80 | also require the use of ports 80 and 443) | |
| 81 | ||
| 82 | Once the data leaves my router, it goes to the upstream ISP and can be | |
| 83 | accessed publicly. | |
| 84 | ||
| 85 | ## Server | |
| 86 | ||
| 87 | +The services I run on my server are installed straight into the OS, | |
| 88 | without any use of Docker or VMs, so I don't need any extra application | |
| 89 | configuration to make them accessible to the outside world.+ | |
| 90 | ||
| 91 | As of 2022-10-04, the paragraph above is no longer true as I now run a | |
| 92 | reverse proxy with Nginx and host many services inside Docker. However, | |
| 93 | it doesn't change anything regarding this post as I still just need to | |
| 94 | open ports 80 & 443 and create the necessary website configuration | |
| 95 | files. | |
| 96 | ||
| 97 | When creating new services - either installed directly on bare metal or | |
| 98 | within something like Docker - I ensure that I read through the | |
| 99 | documentation thoroughly to understand a few key things: - What network | |
| 100 | activities should this app perform (if any)? Using which ports and | |
| 101 | protocols? - Does this app require any commands/services to be run as | |
| 102 | `root`? - Does this app log errors, authentication | |
| 103 | failures/successes, or anything else that would be useful for an | |
| 104 | investigation? | |
| 105 | ||
| 106 | For extra security, I use limit all incoming connections to SSH | |
| 107 | connections through my server firewall (`ufw`) and disable | |
| 108 | common SSH settings. After all of that, I use `fail2ban` as a | |
| 109 | preventative measure against brute-force login attempts. | |
| 110 | ||
| 111 | As another piece of security, you can randomize your SSH port to ensure | |
| 112 | that random scanners or attackers can't easily try to force their way | |
| 113 | into your network. For example, you can edit the port rules in your | |
| 114 | server to block all connection requests to port `22` but | |
| 115 | forward all remote connections from port `12345` to your | |
| 116 | server's port `22`. Then you just need to SSH to your | |
| 117 | network via your randomized port. | |
| 118 | ||
| 119 | ### `ufw` | |
| 120 | ||
| 121 | To see how to configure `ufw`, see my other post: [Secure | |
| 122 | Your Network with the Uncomplicated | |
| 123 | Firewall](/blog/secure-your-network-with-the-uncomplicated-firewall/). | |
| 124 | ||
| 125 | The general notion with an on-device firewall is that you want to deny | |
| 126 | all incoming connections by default and then selectively open certain | |
| 127 | ports for services or users that you know need access. | |
| 128 | ||
| 129 | If you know that you will only be logging into this server from a | |
| 130 | certain set or list of IPs, you can always set the firewall to only | |
| 131 | allow connections to port 22 from those IPs. | |
| 132 | ||
| 133 | For a quick start to only allow SSH connections to the server, use this: | |
| 134 | ||
| 135 | ```sh | |
| 136 | sudo ufw default deny incoming | |
| 137 | sudo ufw default allow outgoing | |
| 138 | sudo ufw allow 22 | |
| 139 | sudo ufw enable | |
| 140 | ``` | |
| 141 | ||
| 142 |  | |
| 143 | ||
| 144 | ### `ssh` | |
| 145 | ||
| 146 | 1. Using SSH Keys | |
| 147 | ||
| 148 | First, make sure you have an SSH keypair generated on the device(s) | |
| 149 | that you'll be using to log in to the server. If you don't have an | |
| 150 | SSH key, run this command: | |
| 151 | ||
| 152 | ```sh | |
| 153 | ssh-keygen | |
| 154 | ``` | |
| 155 | ||
| 156 | Now that we have an SSH key, copy it to the server with the | |
| 157 | following command, which will ask for the user's password before | |
| 158 | accepting the key: | |
| 159 | ||
| 160 | ```sh | |
| 161 | ssh-copy-id my_user@my_server | |
| 162 | ``` | |
| 163 | ||
| 164 | If you have multiple keys, you'll need to specify which to use. | |
| 165 | After it's complete, `ssh` back into the server as that | |
| 166 | user and make sure it doesn't ask for a password. | |
| 167 | ||
| 168 | 2. Disable Password & Root Authentication | |
| 169 | ||
| 170 | Now that we can access the server without a password, we will | |
| 171 | disable password authentication and disable anyone from using | |
| 172 | `ssh` to login as `root`. | |
| 173 | ||
| 174 | To do this, open the `sshd_config` file: | |
| 175 | ||
| 176 | ```sh | |
| 177 | sudo nano /etc/ssh/sshd_config | |
| 178 | ``` | |
| 179 | ||
| 180 | You'll need to update the parameters to the values below. If one of | |
| 181 | these rules is commented-out or doesn't exist, create the rule at | |
| 182 | the bottom of the file. | |
| 183 | ||
| 184 | ```config | |
| 185 | PermitRootLogin no | |
| 186 | PasswordAuthentication no | |
| 187 | PubkeyAuthentication yes | |
| 188 | ``` | |
| 189 | ||
| 190 | Finally, restart the `ssh` service: | |
| 191 | ||
| 192 | ```sh | |
| 193 | sudo systemctl restart sshd.service | |
| 194 | ``` | |
| 195 | ||
| 196 | To test that everything's working so far, open ANOTHER terminal and | |
| 197 | try logging in as `root` over SSH. It is very important | |
| 198 | that you keep your current SSH session open and test with an | |
| 199 | additional session, or you will lock yourself out at some point and | |
| 200 | will need to use a recovery method (e.g., hooking monitor up to home | |
| 201 | server) to get yourself back in. | |
| 202 | ||
| 203 | 3. Enable MFA for `ssh` | |
| 204 | ||
| 205 | This part is optional, but I highly recommend it. So far, we've | |
| 206 | ensured that no one can log into our user on the server without | |
| 207 | using our secret key, and we've ensured that no one can log in | |
| 208 | remotely as `root`. Next, you can enable MFA | |
| 209 | authentication for `ssh` connections. | |
| 210 | ||
| 211 | This process involves editing a couple files and installing an MFA | |
| 212 | package, so I will not include all the details in this post. To see | |
| 213 | how to configure MFA for `ssh`, see my other post: | |
| 214 | [Enabling MFA for SSH](/blog/enable-totp-mfa-for-ssh/). | |
| 215 | ||
| 216 |  | |
| 218 | ||
| 219 | ### `fail2ban` | |
| 220 | ||
| 221 | I haven't written a post on how I use `fail2ban`, but it's | |
| 222 | quite simple. I use the default `sshd` jail, but you can | |
| 223 | always create new jails for respective applications or ports. For | |
| 224 | example, if you use Nginx as your web server, you can use the | |
| 225 | `nginx-http-auth` jail. | |
| 226 | ||
| 227 | In order to get it up and running, use the following commands: | |
| 228 | ||
| 229 | ```sh | |
| 230 | sudo apt install fail2ban | |
| 231 | sudo fail2ban-client start sshd | |
| 232 | sudo fail2ban-client status sshd | |
| 233 | ``` | |
| 234 | ||
| 235 | This should be used as a last-resort defense and shouldn't be a | |
| 236 | replacement for the security measures mentioned above. | |
| 237 | ||
| 238 |  | |
| 239 | ||
| 240 | ## Switch | |
| 241 | ||
| 242 | Between the router and any local devices is my managed switch, which is | |
| 243 | used to create VLANs. The example below shows how I would isolate the | |
| 244 | VLANs if I were starting to host a single service at home. | |
| 245 | ||
| 246 | ### 802.1Q VLAN Configuration | |
| 247 | ||
| 248 | In this configuration, port 8 is the public server that needs to be | |
| 249 | accessed from the outside. Port 23 is my 'dedicated service port' for | |
| 250 | this server. In order to SSH to this server, I need to plug my laptop | |
| 251 | into port 23 or else I cannot SSH. Otherwise, I'd need to hook up a | |
| 252 | monitor and keyboard directly to the server to manage it. | |
| 253 | ||
| 254 | VLAN ID VLAN Name Member Ports Tagged Ports Untagged Ports | |
| 255 | --------- ----------- -------------- -------------- ---------------- | |
| 256 | 1 Default 1-24 1-24 | |
| 257 | 2 Server 1,8,23 1,8,23 | |
| 258 | ||
| 259 | ### 802.1Q VLAN PVID Setting | |
| 260 | ||
| 261 | Once the VLAN is created, I simply add the `VLAN ID` of | |
| 262 | `2` as the `PVID` for any related ports (in this | |
| 263 | case, see that ports `8` and `23` have a PVID of | |
| 264 | `2`). | |
| 265 | ||
| 266 | Port PVID | |
| 267 | ------ ------ | |
| 268 | 1 1 | |
| 269 | 2 1 | |
| 270 | 3 1 | |
| 271 | 4 1 | |
| 272 | 5 1 | |
| 273 | 6 1 | |
| 274 | 7 1 | |
| 275 | 8 2 | |
| 276 | 9 1 | |
| 277 | 10 1 | |
| 278 | 11 1 | |
| 279 | 12 1 | |
| 280 | 13 1 | |
| 281 | 14 1 | |
| 282 | 15 1 | |
| 283 | 16 1 | |
| 284 | 17 1 | |
| 285 | 18 1 | |
| 286 | 19 1 | |
| 287 | 20 1 | |
| 288 | 21 1 | |
| 289 | 22 1 | |
| 290 | 23 2 | |
| 291 | 24 1 | |
| 292 | ||
| 293 | ## Router | |
| 294 | ||
| 295 | On my router, the configuration was as easy as opening the firewall | |
| 296 | settings and unblocking the ports I needed for my services (e.g., | |
| 297 | HTTP/S, Plex, SSH, MySQL, etc.). | |
| 298 | ||
| 299 | +Since I'm relying on an ISP-provided modem/router combo for now (not | |
| 300 | by choice), I do not use any other advanced settings on my router that | |
| 301 | would inhibit any valid traffic to these services.+ | |
| 302 | ||
| 303 | The paragraph above regarding the ISP-owned router is no longer accurate | |
| 304 | as I now use the Ubiquiti Unifi Dream Machine Pro as my router. Within | |
| 305 | this router, I enabled port forwarding/firewall rules, segregate the | |
| 306 | network based on the device, and enable traffic restrictions (e.g., | |
| 307 | silently drop traffic from certain countries and threat categories). | |
| 308 | ||
| 309 | If you have the option with your ISP, I recommend using a personal | |
| 310 | router with software that you are familiar with so that you can explore | |
| 311 | all the options available to you. | |
| 312 | ||
| 313 | ## Physical Security | |
| 314 | ||
| 315 | One large piece of self-hosting that people generally don't discuss | |
| 316 | online is physical security. However, physical security is very | |
| 317 | important for everyone who hosts a server like this. Exactly *how* | |
| 318 | important it is depends on the server use/purpose. | |
| 319 | ||
| 320 | If you self-host customer applications that hold protected data (HIPAA, | |
| 321 | GDPR, COPPA, etc.), then physical security is extremely important and | |
| 322 | cannot be ignored. If you simply host a blog and some hobby sites, then | |
| 323 | it's a relatively minor consideration, but one you still need to think | |
| 324 | about. | |
| 325 | ||
| 326 | ### Location | |
| 327 | ||
| 328 | The first consideration is quite simple: location. - Is the server | |
| 329 | within a property you own or housed on someone else's property? - Is it | |
| 330 | nearby (in your house, in your work office, in your neighbor's garage, | |
| 331 | in a storage unit, etc.)? - Do you have 24/7 access to the server? - Are | |
| 332 | there climate considerations, such as humidity, fires, tornadoes, | |
| 333 | monsoons? - Do you have emergency equipment nearby in case of emergency? | |
| 334 | ||
| 335 | ### Hardware Ownership | |
| 336 | ||
| 337 | Secondly, consider the hardware itself: - Do you own the server in its | |
| 338 | entirety? - Are any other users able to access the server, even if your | |
| 339 | data/space is segregated? - If you're utilizing a third party, do they | |
| 340 | have any documentation to show responsibility? This could be a SOC 1/2/3 | |
| 341 | report, ISO compliance report, internal security/safety documentation. | |
| 342 | ||
| 343 | ### Physical Controls | |
| 344 | ||
| 345 | Regardless of who owns the hardware, ensure that there are adequate | |
| 346 | safeguards in place, if necessary. These usually don't apply to small | |
| 347 | home servers and are usually covered already if you're utilizing a | |
| 348 | third party. | |
| 349 | ||
| 350 | These can include: - Server bezel locks - Server room locks - physical, | |
| 351 | digital, or biometric authentication - Security cameras - Raised | |
| 352 | floors/lowered ceilings with proper guards/gates in-place within the | |
| 353 | floors or ceilings - Security personnel - Log sheets and/or guest badges | |
content/blog/2022-06-24-fedora-i3.md deleted −158
| @@ -1,158 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-06-24 | |
| 3 | title = "Rebooting My Love Affair with Linux" | |
| 4 | description = "A retrospective on moving from macOS to Linux." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Leaving macOS | |
| 8 | ||
| 9 | As I noted [in a recent post](/blog/foss-macos-apps), I have been | |
| 10 | planning on migrating from macOS back to a Linux-based OS. I am happy to | |
| 11 | say that I have finally completed my migration and am now stuck in the | |
| 12 | wonderful world of Linux again. | |
| 13 | ||
| 14 | My decision to leave macOS really came down to just a few important | |
| 15 | things: | |
| 16 | ||
| 17 | - Apple Security (Gatekeeper) restricting me from running any software | |
| 18 | I want. Even if you disable Gatekeeper and allow software to bypass | |
| 19 | the rest of the device installation security, you still have to | |
| 20 | repeat that process every time the allowed software is updated. | |
| 21 | - macOS sends out nearly constant connections, pings, telemetry, etc. | |
| 22 | to a myriad of mysterious Apple services. I'm not even going to | |
| 23 | dive into how many macOS apps have constant telemetry on, as well. | |
| 24 | - Lastly, I just *really* missed the customization and freedom that | |
| 25 | comes with Linux. Being able to switch to entirely new kernel, OS, | |
| 26 | or desktop within minutes is a freedom I took for granted when I | |
| 27 | switched to macOS. | |
| 28 | ||
| 29 | Now that I've covered macOS, I'm going to move on to more exciting | |
| 30 | topics: my personal choice of OS, DE, and various customizations I'm | |
| 31 | using. | |
| 32 | ||
| 33 | ## Fedora | |
| 34 | ||
| 35 | After trying a ton of distros (I think I booted and tested around 20-25 | |
| 36 | distros), I finally landed on [Fedora Linux](https://getfedora.org/). I | |
| 37 | have quite a bit of experience with Fedora and enjoy the | |
| 38 | `dnf` package manager. Fedora allows me to keep up-to-date | |
| 39 | with recent software (I'm looking at you, Debian), but still provides a | |
| 40 | level of stability you don't find in every distro. | |
| 41 | ||
| 42 | In a very close second place was Arch Linux, as well as its spin-off: | |
| 43 | Garuda Linux (Garuda w/ sway is *beautiful*). Arch is great for | |
| 44 | compatibility and the massive community it has, but I have just never | |
| 45 | had the time to properly sit down and learn the methodology behind their | |
| 46 | packaging systems. | |
| 47 | ||
| 48 | Basically, everything else I tested was unacceptable in at least one way | |
| 49 | or another. Void (`glibc`) was great, but doesn't support | |
| 50 | all the software I need. Slackware worked well as a tui, but I wasn't | |
| 51 | skilled enough to get a tiling window manager (WM) working on it. | |
| 52 | ||
| 53 | ### i3 | |
| 54 | ||
| 55 | One of the reasons I settled on Fedora is that it comes with an official | |
| 56 | i3 spin. Being able to use a tiling WM, such as i3 or sway, is one of | |
| 57 | the biggest things I wanted to do as soon as I adopted Linux again. | |
| 58 | ||
| 59 | I will probably set up a dotfile repository soon, so that I don't lose | |
| 60 | any of my configurations, but nothing big has been configured thus far. | |
| 61 | ||
| 62 | The two main things I have updated in i3wm are natural scrolling and | |
| 63 | binding my brightness keys to the `brightnessctl` program. | |
| 64 | ||
| 65 | 1. Natural Scrolling | |
| 66 | ||
| 67 | You can enable natural scrolling by opening the following file: | |
| 68 | ||
| 69 | ```sh | |
| 70 | sudo nano /usr/share/X11/xorg.conf.d/40-libinput.conf | |
| 71 | ``` | |
| 72 | ||
| 73 | Within the `40-libinput.conf` file, find the following | |
| 74 | input sections and enable the natural scrolling option. | |
| 75 | ||
| 76 | This is the `pointer` section: | |
| 77 | ||
| 78 | ```conf | |
| 79 | Section "InputClass" | |
| 80 | Identifier "libinput pointer catchall" | |
| 81 | MatchIsPointer "on" | |
| 82 | MatchDevicePath "/dev/input/event*" | |
| 83 | Driver "libinput" | |
| 84 | Option "NaturalScrolling" "True" | |
| 85 | EndSection | |
| 86 | ``` | |
| 87 | ||
| 88 | This is the `touchpad` section: | |
| 89 | ||
| 90 | ```conf | |
| 91 | Section "InputClass" | |
| 92 | Identifier "libinput touchpad catchall" | |
| 93 | MatchIsTouchpad "on" | |
| 94 | MatchDevicePath "/dev/input/event*" | |
| 95 | Driver "libinput" | |
| 96 | Option "NaturalScrolling" "True" | |
| 97 | EndSection | |
| 98 | ``` | |
| 99 | ||
| 100 | 2. Enabling Brightness Keys | |
| 101 | ||
| 102 | Likewise, enabling brightness key functionality is as simple as | |
| 103 | binding the keys to the `brightnessctl` program. | |
| 104 | ||
| 105 | To do this, open up your i3 config file. Mine is located here: | |
| 106 | ||
| 107 | ```sh | |
| 108 | nano /home/<my-user>/.config/i3/config | |
| 109 | ``` | |
| 110 | ||
| 111 | ```conf | |
| 112 | # Use brightnessctl to adjust brightness. | |
| 113 | bindsym XF86MonBrightnessDown exec --no-startup-id brightnessctl --min-val=2 -q set 3%- | |
| 114 | bindsym XF86MonBrightnessUp exec --no-startup-id brightnessctl -q set 3%+ | |
| 115 | ``` | |
| 116 | ||
| 117 | 3. `polybar` | |
| 118 | ||
| 119 | Instead of using the default `i3status` bar, I have opted | |
| 120 | to use `polybar` instead (as you can also see in the | |
| 121 | screenshot above). | |
| 122 | ||
| 123 | My config for this menu bar is basically just the default settings | |
| 124 | with modified colors and an added battery block to quickly show me | |
| 125 | the machine's battery info. | |
| 126 | ||
| 127 | 4. `alacritty` | |
| 128 | ||
| 129 | Not much to say on this part yet, as I haven't configured it much, | |
| 130 | but I installed `alacritty` as my default terminal, and I | |
| 131 | am using `zsh` and the shell. | |
| 132 | ||
| 133 | ## Software Choices | |
| 134 | ||
| 135 | Again, I'm not going to say much that I haven't said yet in other blog | |
| 136 | posts, so I'll just do a quick rundown of the apps I installed | |
| 137 | immediately after I set up the environment. | |
| 138 | ||
| 139 | Flatpak Apps: | |
| 140 | ||
| 141 | - Cryptomator | |
| 142 | - pCloud | |
| 143 | - Signal | |
| 144 | ||
| 145 | Fedora Packages: | |
| 146 | ||
| 147 | - gomuks | |
| 148 | - neomutt | |
| 149 | - neofetch | |
| 150 | - Firefox | |
| 151 | - uBlock Origin | |
| 152 | - Bitwarden | |
| 153 | - Stylus | |
| 154 | - Privacy Redirect | |
| 155 | ||
| 156 | Other: | |
| 157 | ||
| 158 | - exiftool | |
content/blog/2022-07-25-curseradio.md deleted −106
| @@ -1,106 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-07-25 | |
| 3 | title = "CurseRadio: Listening to the Radio on the Comand Line" | |
| 4 | description = "Use Curse Radio to listen to radio on the command-line." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Overview | |
| 8 | ||
| 9 | While exploring some interesting Linux applications, I stumbled across | |
| 10 | [curseradio](https://github.com/chronitis/curseradio), a command-line | |
| 11 | radio player based on Python. | |
| 12 | ||
| 13 | This application is fantastic and incredibly easy to install, so I | |
| 14 | wanted to dedicate a post today to this app. Let's look at the features | |
| 15 | within the app and then walk through the installation process I took to | |
| 16 | get `curseradio` working. | |
| 17 | ||
| 18 | ## Features | |
| 19 | ||
| 20 |  | |
| 21 | ||
| 22 | The radio player itself is quite minimal. As you can see in the | |
| 23 | screenshot above, it contains a simple plaintext list of all available | |
| 24 | categories, which can be broken down further and further. In addition, | |
| 25 | radio shows are available for listening, alongside regular radio | |
| 26 | stations. | |
| 27 | ||
| 28 | For example, the `Sports` > `Pro Basketball` > | |
| 29 | `Shows` category contains a number of specific shows related | |
| 30 | to Professional Basketball. | |
| 31 | ||
| 32 | Aside from being able to play any of the listed stations/shows, you can | |
| 33 | make a channel your favorite by pressing `f`. It will now | |
| 34 | show up at the top of the radio player in the `Favourites` | |
| 35 | category. | |
| 36 | ||
| 37 | ### Commands/Shortcuts | |
| 38 | ||
| 39 | Key(s) Command | |
| 40 | ------------ --------------------------------- | |
| 41 | ↑, ↓ navigate | |
| 42 | PgUp, PgDn navigate quickly | |
| 43 | Home, End to top/bottom | |
| 44 | Enter open/close folders, play stream | |
| 45 | k stop playing stream | |
| 46 | q quit | |
| 47 | f toggle favourite | |
| 48 | ||
| 49 | ## Installation | |
| 50 | ||
| 51 | ### Dependencies | |
| 52 | ||
| 53 | Before installing `curseradio`, a handful of system and | |
| 54 | Python packages are required. To get started, install | |
| 55 | `python3`, `pip3`, and `mpv` on your | |
| 56 | system. In this example, I'm using Fedora Linux, which uses the | |
| 57 | `dnf` package manager. You may need to adjust this if you're | |
| 58 | using a different system. | |
| 59 | ||
| 60 | ```sh | |
| 61 | sudo dnf install python3 pip3 mpv | |
| 62 | ``` | |
| 63 | ||
| 64 | Next, use `pip3` to install `requests`, | |
| 65 | `xdg`, and `lxml`: | |
| 66 | ||
| 67 | ```sh | |
| 68 | pip3 install requests xdg lxml | |
| 69 | ``` | |
| 70 | ||
| 71 | ### Repository Source Installation | |
| 72 | ||
| 73 | Once all the dependencies are installed, we can clone the source code | |
| 74 | and enter that directory: | |
| 75 | ||
| 76 | ```sh | |
| 77 | git clone https://github.com/chronitis/curseradio && cd curseradio | |
| 78 | ``` | |
| 79 | ||
| 80 | Once you're within the `curseradio` directory, you can | |
| 81 | install the application with the provided `setup.py` script. | |
| 82 | ||
| 83 | ```sh | |
| 84 | sudo python3 setup.py install | |
| 85 | ``` | |
| 86 | ||
| 87 | In my case, I ran into a few errors and needed to create the folders | |
| 88 | that curseradio wanted to use for its installation. If you don't get | |
| 89 | any errors, you can skip this and run the app. | |
| 90 | ||
| 91 | ```sh | |
| 92 | sudo mkdir /usr/local/lib/python3.10/ | |
| 93 | sudo mkdir /usr/local/lib/python3.10/site-packages/ | |
| 94 | ``` | |
| 95 | ||
| 96 | ```sh | |
| 97 | sudo chown -R $USER:$USER /usr/local/lib/python3.10/ | |
| 98 | ``` | |
| 99 | ||
| 100 | ## Run the Application | |
| 101 | ||
| 102 | Once fully installed without errors, you can run the application! | |
| 103 | ||
| 104 | ```sh | |
| 105 | python3 /usr/local/bin/curseradio | |
| 106 | ``` | |
content/blog/2022-09-21-graphene-os.md deleted −167
| @@ -1,167 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-09-21 | |
| 3 | title = "Installing Graphene OS on the Pixel 6 Pro" | |
| 4 | description = "A retrospective on the successful command-line installation of Graphene OS on a Pixel 6 Pro." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Introduction | |
| 8 | ||
| 9 | After using iOS for a couple of years, I finally took the plunge and | |
| 10 | purchased a Pixel 6 Pro in order to test and use [GrapheneOS] | |
| 11 | (<https://grapheneos.org>). | |
| 12 | ||
| 13 | The installation process was rather quick once you have the tools and | |
| 14 | files you need. Overall, it can be done in just a few minutes. | |
| 15 | ||
| 16 | ## Gathering Tools & Files | |
| 17 | ||
| 18 | ### Android Tools | |
| 19 | ||
| 20 | First, in order to interact with the device, we will need the [Android | |
| 21 | platform | |
| 22 | tools](https://developer.android.com/studio/releases/platform-tools.html). | |
| 23 | Find the Linux download and save the ZIP folder to your preferred | |
| 24 | location. | |
| 25 | ||
| 26 | Once we've downloaded the files, we will need to unzip them, enter the | |
| 27 | directory, and move the necessary executables to a central location, | |
| 28 | such as `/usr/bin/`. For this installation, we only need the | |
| 29 | `fastboot` and `adb` executables. | |
| 30 | ||
| 31 | ```sh | |
| 32 | cd ~/Downloads | |
| 33 | ``` | |
| 34 | ||
| 35 | ```sh | |
| 36 | unzip platform-tools_r33.0.3-linux.zip | |
| 37 | cd platform-tools | |
| 38 | sudo mv fastboot /usr/bin/ | |
| 39 | sudo mv adb /usr/bin | |
| 40 | ``` | |
| 41 | ||
| 42 | ### GrapheneOS Files | |
| 43 | ||
| 44 | Next, we need the [GrapheneOS files](https://grapheneos.org/releases) | |
| 45 | for our device and model. For example, the Pixel 6 Pro is codenamed | |
| 46 | `raven` on the release page. | |
| 47 | ||
| 48 | Once we have the links, let's download them to our working directory: | |
| 49 | ||
| 50 | ```sh | |
| 51 | curl -O https://releases.grapheneos.org/factory.pub | |
| 52 | curl -0 https://releases.grapheneos.org/raven-factory-2022091400.zip | |
| 53 | curl -0 https://releases.grapheneos.org/raven-factory-2022091400.zip.sig | |
| 54 | ``` | |
| 55 | ||
| 56 | 1. Validate Integrity | |
| 57 | ||
| 58 | In order to validate the integrity of the downloaded files, we will | |
| 59 | need the `signify` package and Graphene's | |
| 60 | `factory.pub` file. | |
| 61 | ||
| 62 | ```sh | |
| 63 | sudo dnf install signify | |
| 64 | ``` | |
| 65 | ||
| 66 | ```sh | |
| 67 | curl -O https://releases.grapheneos.org/factory.pub | |
| 68 | ``` | |
| 69 | ||
| 70 | Then we can validate the files and ensure that no data was corrupted | |
| 71 | or modified before it was saved to our device. | |
| 72 | ||
| 73 | ```sh | |
| 74 | signify -Cqp factory.pub -x raven-factory-2022091400.zip.sig && echo verified | |
| 75 | ``` | |
| 76 | ||
| 77 | 2. Unzip Files | |
| 78 | ||
| 79 | Once the files are verified, we can unzip the Graphene image and | |
| 80 | enter the directory: | |
| 81 | ||
| 82 | ```sh | |
| 83 | unzip raven-factory-2022091400.zip && cd raven-factory-2022091400 | |
| 84 | ``` | |
| 85 | ||
| 86 | ## Installation Process | |
| 87 | ||
| 88 | ### Enable Developer Debugging & OEM Unlock | |
| 89 | ||
| 90 | Before we can actually flash anything to the phone, we will need to | |
| 91 | enable OEM Unlocking, as well as either USB Debugging or Wireless | |
| 92 | Debugging, depending on which method we will be using. | |
| 93 | ||
| 94 | To start, enable developer mode by going to `Settings` > | |
| 95 | `About` and tapping `Build Number` seven (7) | |
| 96 | times. You may need to enter your PIN to enable this mode. | |
| 97 | ||
| 98 | Once developer mode is enabled, go to `Settings` > | |
| 99 | `System` > `Devloper Options` and enable OEM | |
| 100 | Unlocking, as well as USB or Wireless Debugging. In my case, I chose USB | |
| 101 | Debugging and performed all actions via USB cable. | |
| 102 | ||
| 103 | Once these options are enabled, plug the phone into the computer and | |
| 104 | execute the following command: | |
| 105 | ||
| 106 | ```sh | |
| 107 | adb devices | |
| 108 | ``` | |
| 109 | ||
| 110 | If an unauthorized error occurs, make sure the USB mode on the phone is | |
| 111 | changed from charging to something like "File Transfer" or "PTP." | |
| 112 | You can find the USB mode in the notification tray. | |
| 113 | ||
| 114 | ### Reboot Device | |
| 115 | ||
| 116 | Once we have found the device via `adb`, we can either boot | |
| 117 | into the bootloader interface by holding the volume down button while | |
| 118 | the phone reboots or by executing the following command: | |
| 119 | ||
| 120 | ```sh | |
| 121 | adb reboot bootloader | |
| 122 | ``` | |
| 123 | ||
| 124 | ### Unlock the Bootloader | |
| 125 | ||
| 126 | The phone will reboot and load the bootloader screen upon startup. At | |
| 127 | this point, we are ready to start the actual flashing of GrapheneOS onto | |
| 128 | the device. | |
| 129 | ||
| 130 | **NOTE**: In my situation, I needed to use `sudo` with every | |
| 131 | `fastboot` command, but not with `adb` commands. I | |
| 132 | am not sure if this is standard or a Fedora quirk, but I'm documenting | |
| 133 | my commands verbatim in this post. | |
| 134 | ||
| 135 | First, we start by unlocking the bootloader so that we can load other | |
| 136 | ROMs: | |
| 137 | ||
| 138 | ```sh | |
| 139 | sudo fastboot flashing unlock | |
| 140 | ``` | |
| 141 | ||
| 142 | ### Flashing Factory Images | |
| 143 | ||
| 144 | Once the phone is unlocked, we can flash it with the | |
| 145 | `flash-all.sh` script found inside the | |
| 146 | `raven-factory-2022091400` folder we entered earlier: | |
| 147 | ||
| 148 | ```sh | |
| 149 | sudo ./flash-all.sh | |
| 150 | ``` | |
| 151 | ||
| 152 | This process should take a few minutes and will print informational | |
| 153 | messages as things progress. Avoid doing anything on the phone while | |
| 154 | this process is operating. | |
| 155 | ||
| 156 | ### Lock the Bootloader | |
| 157 | ||
| 158 | If everything was successful, the phone should reboot a few times and | |
| 159 | finally land back on the bootloader screen. At this point, we can | |
| 160 | re-lock the bootloader to enable full verified boot and protect the | |
| 161 | device from unwanted flashing or erasure of data. | |
| 162 | ||
| 163 | ```sh | |
| 164 | sudo fastboot flashing lock | |
| 165 | ``` | |
| 166 | ||
| 167 | Once done, the device will be wiped and ready for a fresh set-up! | |
content/blog/2022-10-22-alpine-linux.md deleted −280
| @@ -1,280 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-10-22 | |
| 3 | title = "Alpine Linux: My New Server OS" | |
| 4 | description = "A retrospective on installing and configuring Alpine Linux as my new server operating system." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Alpine Linux | |
| 8 | ||
| 9 | [Alpine Linux](https://alpinelinux.org) is a very small distro, built on | |
| 10 | musl libc and busybox. It uses ash as the default shell, OpenRC as the | |
| 11 | init system, and apk as the package manager. According to their website, | |
| 12 | an Alpine container "requires no more than 8 MB and a minimal | |
| 13 | installation to disk requires around 130 MB of storage." An actual bare | |
| 14 | metal machine is recommended to have 100 MB of RAM and 0-700 MB of | |
| 15 | storage space. | |
| 16 | ||
| 17 | Historically, I've used Ubuntu's minimal installation image as my | |
| 18 | server OS for the last five years. Ubuntu worked well and helped as my | |
| 19 | original server contained an nVidia GPU and no onboard graphics, so | |
| 20 | quite a few distros won't boot or install without a lot of tinkering. | |
| 21 | ||
| 22 | Alpine has given me a huge increase in performance across my Docker apps | |
| 23 | and Nginx websites. CPU load for the new server I'm using to test | |
| 24 | Alpine hovers around 0-5% on average with an Intel(R) Core(TM) i3-6100 | |
| 25 | CPU @ 3.70GHz. | |
| 26 | ||
| 27 | The only services I haven't moved over to Alpine are Plex Media Server | |
| 28 | and Syncthing, which may increase CPU load quite a bit depending on how | |
| 29 | many streams are running. | |
| 30 | ||
| 31 | ### Installation | |
| 32 | ||
| 33 | In terms of installation, Alpine has an incredibly useful | |
| 34 | [wiki](https://wiki.alpinelinux.org/wiki/Installation) that will guide a | |
| 35 | user throughout the installation and post-installation processes, as | |
| 36 | well as various other articles and guides. | |
| 37 | ||
| 38 | To install Alpine, find an appropriate [image to | |
| 39 | download](https://alpinelinux.org/downloads/) and flash it to a USB | |
| 40 | using software such as Rufus or Etcher. I opted to use the Standard | |
| 41 | image for my x86~64~ architecture. | |
| 42 | ||
| 43 | Once the USB is ready, plug it into the machine and reboot. Note that | |
| 44 | you may have to use a key such as `Esc` or `F1-12` | |
| 45 | to access the boot menu. The Alpine Linux terminal will load quickly and | |
| 46 | for a login. | |
| 47 | ||
| 48 | To log in to the installation image, use the `root` account; | |
| 49 | there is no password. Once logged-in, execute the setup command: | |
| 50 | ||
| 51 | ```sh | |
| 52 | setup-alpine | |
| 53 | ``` | |
| 54 | ||
| 55 | The setup script will ask a series of questions to configure the system. | |
| 56 | Be sure to answer carefully or else you may have to re-configure the | |
| 57 | system after boot. | |
| 58 | ||
| 59 | - Keyboard Layout (Local keyboard language and usage mode, e.g., us | |
| 60 | and variant of us-nodeadkeys.) | |
| 61 | - Hostname (The name for the computer.) | |
| 62 | - Network (For example, automatic IP address discovery with the | |
| 63 | "DHCP" protocol.) | |
| 64 | - DNS Servers (Domain Name Servers to query. For privacy reasons, it | |
| 65 | is NOT recommended to route every local request to servers like | |
| 66 | Google's 8.8.8.8 .) | |
| 67 | - Timezone | |
| 68 | - Proxy (Proxy server to use for accessing the web. Use "none" for | |
| 69 | direct connections to the internet.) | |
| 70 | - Mirror (From where to download packages. Choose the organization you | |
| 71 | trust giving your usage patterns to.) | |
| 72 | - SSH (Secure SHell remote access server. "Openssh" is part of the | |
| 73 | default install image. Use "none" to disable remote login, e.g. on | |
| 74 | laptops.) | |
| 75 | - NTP (Network Time Protocol client used for keeping the system clock | |
| 76 | in sync with a time-server. Package "chrony" is part of the | |
| 77 | default install image.) | |
| 78 | - Disk Mode (Select between diskless (disk="none"), "data" or | |
| 79 | "sys", as described above.) | |
| 80 | ||
| 81 | Once the setup script is finished, be sure to reboot the machine and | |
| 82 | remove the USB device. | |
| 83 | ||
| 84 | ```sh | |
| 85 | reboot | |
| 86 | ``` | |
| 87 | ||
| 88 | ### Post-Installation | |
| 89 | ||
| 90 | There are many things you can do once your Alpine Linux system is up and | |
| 91 | running, and it largely depends on what you'll use the machine for. | |
| 92 | I'm going to walk through my personal post-installation setup for my | |
| 93 | web server. | |
| 94 | ||
| 95 | 1. Upgrade the System | |
| 96 | ||
| 97 | First, login as `root` in order to update and upgrade the | |
| 98 | system: | |
| 99 | ||
| 100 | ```sh | |
| 101 | apk -U upgrade | |
| 102 | ``` | |
| 103 | ||
| 104 | 2. Adding a User | |
| 105 | ||
| 106 | I needed to add a user so that I don't need to log in as root. Note | |
| 107 | that if you're used to using the `sudo` command, you | |
| 108 | will now need to use the `doas` command on Alpine Linux. | |
| 109 | ||
| 110 | ```sh | |
| 111 | apk add doas | |
| 112 | adduser <username> | |
| 113 | adduser <username> wheel | |
| 114 | ``` | |
| 115 | ||
| 116 | You can now log out and log back in using the newly-created user: | |
| 117 | ||
| 118 | ```sh | |
| 119 | exit | |
| 120 | ``` | |
| 121 | ||
| 122 | 3. Enable Community Packages | |
| 123 | ||
| 124 | In order to install more common packages that aren't found in the | |
| 125 | `main` repository, you will need to enable the | |
| 126 | `community` repository: | |
| 127 | ||
| 128 | ```sh | |
| 129 | doas nano /etc/apk/repositories | |
| 130 | ``` | |
| 131 | ||
| 132 | Uncomment the community line for whichever version of Alpine you're | |
| 133 | running: | |
| 134 | ||
| 135 | ```sh | |
| 136 | /media/usb/apks | |
| 137 | http://dl-cdn.alpinelinux.org/alpine/v3.16/main | |
| 138 | http://dl-cdn.alpinelinux.org/alpine/v3.16/community | |
| 139 | #http://dl-cdn.alpinelinux.org/alpine/edge/main | |
| 140 | #http://dl-cdn.alpinelinux.org/alpine/edge/community | |
| 141 | #http://dl-cdn.alpinelinux.org/alpine/edge/testing | |
| 142 | ``` | |
| 143 | ||
| 144 | 4. Install Required Packages | |
| 145 | ||
| 146 | Now that the community packages are available, you can install any | |
| 147 | packages you need. In my case, I installed the web server packages I | |
| 148 | need for my services: | |
| 149 | ||
| 150 | ```sh | |
| 151 | doas apk add nano nginx docker docker-compose ufw | |
| 152 | ``` | |
| 153 | ||
| 154 | 5. SSH | |
| 155 | ||
| 156 | If you didn't install OpenSSH as part of the installation, you can | |
| 157 | do so now: | |
| 158 | ||
| 159 | ```sh | |
| 160 | doas apk add openssh | |
| 161 | ``` | |
| 162 | ||
| 163 | Next, either create a new key or copy your SSH key to the server | |
| 164 | from your current machines: | |
| 165 | ||
| 166 | ```sh | |
| 167 | # Create a new key | |
| 168 | ssh-keygen | |
| 169 | ``` | |
| 170 | ||
| 171 | If you need to copy an existing SSH key from a current machine: | |
| 172 | ||
| 173 | ```sh | |
| 174 | # Copy key from existing machines | |
| 175 | ssh-copy-id <username>@<ip_address> | |
| 176 | ``` | |
| 177 | ||
| 178 | 6. Firewall | |
| 179 | ||
| 180 | Lastly, I installed `ufw` above as my firewall. To set | |
| 181 | up, default to deny incoming and allow outgoing connections. Then | |
| 182 | selectively allow other ports or apps as needed. | |
| 183 | ||
| 184 | ```sh | |
| 185 | doas ufw default deny incoming | |
| 186 | doas ufw default allow outgoing | |
| 187 | doas ufw allow SSH | |
| 188 | doas ufw allow "WWW Full" | |
| 189 | doas ufw allow 9418 # Git server port | |
| 190 | ``` | |
| 191 | ||
| 192 | 7. Change Hostname | |
| 193 | ||
| 194 | If you don't like the hostname set during installation, you just | |
| 195 | need to edit two files. First, edit the simple hostname file: | |
| 196 | ||
| 197 | ```sh | |
| 198 | doas nano /etc/hostname | |
| 199 | ``` | |
| 200 | ||
| 201 | ```sh | |
| 202 | <hostname> | |
| 203 | ``` | |
| 204 | ||
| 205 | Next, edit the `hosts` file: | |
| 206 | ||
| 207 | ```sh | |
| 208 | doas nano /etc/hosts | |
| 209 | ``` | |
| 210 | ||
| 211 | ```sh | |
| 212 | 127.0.0.1 <hostname>.local <hostname> localhost.local localhost | |
| 213 | ::1 <hostname> <hostname>.local | |
| 214 | ``` | |
| 215 | ||
| 216 | ## Nginx Web Server | |
| 217 | ||
| 218 | To set up my web server, I simply created the `www` user and | |
| 219 | created the necessary files. | |
| 220 | ||
| 221 | ```sh | |
| 222 | doas adduser -D -g 'www' www | |
| 223 | mkdir /www | |
| 224 | doas mkdir /www | |
| 225 | doas chown -R www:www /var/lib/nginx/ | |
| 226 | doas chown -R www:www /www | |
| 227 | ``` | |
| 228 | ||
| 229 | If you're running a simple webroot, you can alter the main | |
| 230 | `nginx.conf` file. Otherwise, you can drop configuration | |
| 231 | files in the following directory. You don't need to enable or symlink | |
| 232 | the configuration file like you do in other systems. | |
| 233 | ||
| 234 | ```sh | |
| 235 | doas nano /etc/nginx/http.d/example_website.conf | |
| 236 | ``` | |
| 237 | ||
| 238 | Once the configuration is set and pointed at the `/www` | |
| 239 | directory to serve files, enable the Nginx service: | |
| 240 | ||
| 241 | ```sh | |
| 242 | # Note that 'default' must be included or Nginx will not start on boot | |
| 243 | doas rc-update add nginx default | |
| 244 | ``` | |
| 245 | ||
| 246 | ## Docker Containers | |
| 247 | ||
| 248 | Docker works exactly the same as other systems. Either execute a | |
| 249 | `docker run` command or create a | |
| 250 | `docker-compose.yml` file and do | |
| 251 | `docker-compose up -d`. | |
| 252 | ||
| 253 | ## Git Server | |
| 254 | ||
| 255 | I went in-depth on how to self-host a git server in another post: | |
| 256 | [Self-Hosting a Personal Git Server](/blog/git-server/). | |
| 257 | ||
| 258 | However, there are a few differences with Alpine. First note that in | |
| 259 | order to change the `git` user's shell, you must do a few | |
| 260 | things a little different: | |
| 261 | ||
| 262 | ```sh | |
| 263 | doas apk add libuser | |
| 264 | doas touch /etc/login.defs | |
| 265 | doas mkdir /etc/default | |
| 266 | doas touch /etc/default/useradd | |
| 267 | doas lchsh git | |
| 268 | ``` | |
| 269 | ||
| 270 | ## Thoughts on Alpine | |
| 271 | ||
| 272 | So far, I love Alpine Linux. I have no complaints about anything at this | |
| 273 | point, but I'm not completely finished with the migration yet. Once | |
| 274 | I'm able to upgrade my hardware to a rack-mounted server, I will | |
| 275 | migrate Plex and Syncthing over to Alpine as well - possibly putting | |
| 276 | Plex into a container or VM. | |
| 277 | ||
| 278 | The performance is stellar, the `apk` package manager is | |
| 279 | seamless, and system administration tasks are effortless. My only regret | |
| 280 | is that I didn't install Alpine sooner. | |
content/blog/2022-10-30-linux-display-manager.md deleted −81
| @@ -1,81 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-10-30 | |
| 3 | title = "How to Disable or Change the Display Manager on Void Linux" | |
| 4 | description = "Learn how to remove or modify the display manager on Void Linux." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Display Manager Services | |
| 8 | ||
| 9 | In order to change the [display | |
| 10 | manager](https://en.wikipedia.org/wiki/Display_manager) on Void Linux - | |
| 11 | or any other Linux distro - you need to identify the currently enabled | |
| 12 | display manager. | |
| 13 | ||
| 14 | ### Disabling the Current Display Manager | |
| 15 | ||
| 16 | Void Linux only has one ISO available for download with a pre-built | |
| 17 | display manager at the time of this post: the XFCE ISO. If you've | |
| 18 | installed this version, the pre-assigned display manager is | |
| 19 | `lxdm`. If you installed another display manager, replace | |
| 20 | `lxdm` in the following command with the display manager you | |
| 21 | have installed. | |
| 22 | ||
| 23 | To disable `lxdm`, simply remove the service symlink: | |
| 24 | ||
| 25 | ```sh | |
| 26 | sudo rm /var/service/lxdm | |
| 27 | ``` | |
| 28 | ||
| 29 | ### Enabling a New Display Manager | |
| 30 | ||
| 31 | If you want to enable a new display manager, you can do so after | |
| 32 | `lxdm` is disabled. Make sure to replace | |
| 33 | `<new_display_manager>` with your new DM, such as | |
| 34 | `gdm`, `xdm`, etc. | |
| 35 | ||
| 36 | ```sh | |
| 37 | sudo ln -s /etc/sv/<new_display_manager> /var/service | |
| 38 | ``` | |
| 39 | ||
| 40 | ## Set Up `.xinitrc` | |
| 41 | ||
| 42 | Depending on your setup, you may need to create a few X files, such as | |
| 43 | `~/.xinitrc`. For my personal set-up, I created this file to | |
| 44 | launch the i3wm as my desktop. | |
| 45 | ||
| 46 | ```sh | |
| 47 | nano ~/.xinitrc | |
| 48 | ``` | |
| 49 | ||
| 50 | ```sh | |
| 51 | #!/bin/sh | |
| 52 | ||
| 53 | exec i3 | |
| 54 | ``` | |
| 55 | ||
| 56 | If you run a desktop other than i3, simply replace `i3` with | |
| 57 | the shell command that launches that desktop. | |
| 58 | ||
| 59 | ## Set Up Your Shell Profile | |
| 60 | ||
| 61 | Finally, in order to automatically launch an X session upon login, you | |
| 62 | will need to edit the `.bash_profile` (bash) or | |
| 63 | `.zprofile` (zsh) files for your shell: | |
| 64 | ||
| 65 | ```sh | |
| 66 | nano ~/.zprofile | |
| 67 | ``` | |
| 68 | ||
| 69 | Add the following snippet to the end of the shell profile file. This | |
| 70 | will execute the `startx` command upon login. | |
| 71 | ||
| 72 | ```sh | |
| 73 | if [ -z "${DISPLAY}" ] && [ "${XDG_VTNR}" -eq 1 ]; then | |
| 74 | exec startx | |
| 75 | fi | |
| 76 | ``` | |
| 77 | ||
| 78 | Alternatively, you can ignore this step and simply choose to manually | |
| 79 | execute `startx` upon login. This can be useful if you have | |
| 80 | issues with your desktop or like to manually launch different desktops | |
| 81 | by choice. | |
content/blog/2022-12-01-nginx-compression.md deleted −79
| @@ -1,79 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-12-01 | |
| 3 | title = "Enable GZIP Compression in Nginx" | |
| 4 | description = "Learn how to enable compression in Nginx." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Text Compression | |
| 8 | ||
| 9 | Text compression allows a web server to serve text-based resources | |
| 10 | faster than uncompressed data. This can speed up things like First | |
| 11 | Contentful Paint, Tie to Interactive, and Speed Index. | |
| 12 | ||
| 13 | ## Enable Nginx Compression with gzip | |
| 14 | ||
| 15 | In order to enable text compression on Nginx, we need to enable it | |
| 16 | within the configuration file: | |
| 17 | ||
| 18 | ```sh | |
| 19 | nano /etc/nginx/nginx.conf | |
| 20 | ``` | |
| 21 | ||
| 22 | Within the `http` block, find the section that shows | |
| 23 | something like the block below. This is the default gzip configuration I | |
| 24 | found in my `nginx.conf` file on Alpine Linux 3.17. Yours may | |
| 25 | look slightly different, just make sure that you're not creating any | |
| 26 | duplicate gzip options. | |
| 27 | ||
| 28 | ```conf | |
| 29 | # Enable gzipping of responses. | |
| 30 | #gzip on; | |
| 31 | ||
| 32 | # Set the Vary HTTP header as defined in the RFC 2616. Default is 'off'. | |
| 33 | gzip_vary on; | |
| 34 | ``` | |
| 35 | ||
| 36 | Remove the default gzip lines and replace them with the following: | |
| 37 | ||
| 38 | ```conf | |
| 39 | # Enable gzipping of responses. | |
| 40 | gzip on; | |
| 41 | gzip_vary on; | |
| 42 | gzip_min_length 10240; | |
| 43 | gzip_proxied expired no-cache no-store private auth; | |
| 44 | gzip_types text/plain text/css text/xml text/javascript application/x-javascript application/xml; | |
| 45 | gzip_disable "MSIE [1-6]"; | |
| 46 | ``` | |
| 47 | ||
| 48 | ## Explanations of ngx~httpgzipmodule~ Options | |
| 49 | ||
| 50 | Each of the lines above enables a different aspect of the gzip response | |
| 51 | for Nginx. Here are the full explanations: | |
| 52 | ||
| 53 | - `gzip` -- Enables or disables gzipping of responses. | |
| 54 | - `gzip_vary` -- Enables or disables inserting the "Vary: | |
| 55 | Accept-Encoding" response header field if the directives gzip, | |
| 56 | gzip~static~, or gunzip are active. | |
| 57 | - `gzip_min_length` -- Sets the minimum length of a | |
| 58 | response that will be gzipped. The length is determined only from | |
| 59 | the "Content-Length" response header field. | |
| 60 | - `gzip_proxied` -- Enables or disables gzipping of | |
| 61 | responses for proxied requests depending on the request and | |
| 62 | response. The fact that the request is proxied is determined by the | |
| 63 | presence of the "Via" request header field. | |
| 64 | - `gzip_types` -- Enables gzipping of responses for the | |
| 65 | specified MIME types in addition to "text/html". The special value | |
| 66 | "*" matches any MIME type (0.8.29). Responses with the | |
| 67 | "text/html" type are always compressed. | |
| 68 | - `gzip_disable` -- Disables gzipping of responses for | |
| 69 | requests with "User-Agent" header fields matching any of the | |
| 70 | specified regular expressions. | |
| 71 | - The special mask "msie6" (0.7.12) corresponds to the regular | |
| 72 | expression "MSIE [4-6].", but works faster. Starting from | |
| 73 | version 0.8.11, "MSIE 6.0; ... SV1" is excluded from this | |
| 74 | mask. | |
| 75 | ||
| 76 | More information on these directives and their options can be found on | |
| 77 | the [Module | |
| 78 | ngx~httpgzipmodule~](https://nginx.org/en/docs/http/ngx_http_gzip_module.html) | |
| 79 | page in Nginx's documentation. | |
content/blog/2022-12-17-st.md deleted −94
| @@ -1,94 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2022-12-17 | |
| 3 | title = "Simple Terminal" | |
| 4 | description = "Instructions for building simple terminal on Fedora." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## st | |
| 8 | ||
| 9 | [st](https://st.suckless.org) standards for Simple Terminal, a simple | |
| 10 | terminal implementation for X made by the | |
| 11 | [suckless](https://suckless.org) team. | |
| 12 | ||
| 13 | This post walks through the dependencies needed and process to build and | |
| 14 | install `st` on Fedora Workstation. | |
| 15 | ||
| 16 | ### Obtain Files | |
| 17 | ||
| 18 | To start, obtain the source files for `st` via | |
| 19 | `git clone`. | |
| 20 | ||
| 21 | ```sh | |
| 22 | mkdir ~/suckless && cd ~/suckless | |
| 23 | git clone https://git.suckless.org/st && cd st | |
| 24 | ``` | |
| 25 | ||
| 26 | ### Dependencies | |
| 27 | ||
| 28 | Once you have the files and are in the `st` directory, ensure | |
| 29 | the following packages are installed. | |
| 30 | ||
| 31 | ```sh | |
| 32 | sudo dnf update && sudo dnf upgrade | |
| 33 | sudo dnf install gcc patch libX11-devel libXft-devel | |
| 34 | ``` | |
| 35 | ||
| 36 | ### Building | |
| 37 | ||
| 38 | Before building, ensure that you read the README file. | |
| 39 | ||
| 40 | ```sh | |
| 41 | cat README | |
| 42 | ``` | |
| 43 | ||
| 44 | Once you've read the instructions, open the `config.mk` file | |
| 45 | and ensure it matches your setup. If you're not sure, leave the default | |
| 46 | options within the file. | |
| 47 | ||
| 48 | Finally, you can build `st` with the following command. | |
| 49 | Ensure you run as root (e.g., `sudo`) or else you may not end | |
| 50 | up with a usable application file. | |
| 51 | ||
| 52 | ```sh | |
| 53 | sudo make clean install | |
| 54 | ``` | |
| 55 | ||
| 56 | ### Customization (Patches) | |
| 57 | ||
| 58 | Note that customizing `st` requires you to modify the source | |
| 59 | files or to download one of the [available | |
| 60 | patches](https://st.suckless.org/patches/) for suckless.org. | |
| 61 | ||
| 62 | If you've already installed `st` and want to customize or | |
| 63 | install a patch, start by uninstalling the current program. | |
| 64 | ||
| 65 | ```sh | |
| 66 | cd ~/suckless/st | |
| 67 | sudo make uninstall | |
| 68 | ``` | |
| 69 | ||
| 70 | Next, grab the `<path>.diff` file from the page of the patch | |
| 71 | you chose. For example, I will be using the | |
| 72 | [defaultfontsize](https://st.suckless.org/patches/defaultfontsize/) | |
| 73 | patch in the below example. | |
| 74 | ||
| 75 | ```sh | |
| 76 | wget https://st.suckless.org/patches/defaultfontsize/st-defaultfontsize-20210225-4ef0cbd.diff | |
| 77 | ``` | |
| 78 | ||
| 79 | Once the file is downloaded inside the `st` folder, apply the | |
| 80 | patch and re-install the program. You may need to install the | |
| 81 | `patch` command if you don't have it installed already (you | |
| 82 | should have installed it above). | |
| 83 | ||
| 84 | ```sh | |
| 85 | patch -i st-defaultfontsize-20210225-4ef0cbd.diff | |
| 86 | sudo make clean install | |
| 87 | ``` | |
| 88 | ||
| 89 | Once installed, you can use the default font size patch to launch | |
| 90 | `st` with any font size you wish: | |
| 91 | ||
| 92 | ```sh | |
| 93 | st -z 16 | |
| 94 | ``` | |
content/blog/2023-02-02-exploring-hare.md deleted −171
| @@ -1,171 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-02-02 | |
| 3 | title = "Exploring the Hare Programming Language" | |
| 4 | description = "A retrospective on my first time using the Hare Programming Language." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## A Quick Note | |
| 8 | ||
| 9 | By no means am I a professional developer, so this post will be rather | |
| 10 | short. I won't be going into depth on the specification or anything | |
| 11 | that technical. | |
| 12 | ||
| 13 | Instead, I will simply be talking about how I (a relatively basic | |
| 14 | hobbyist programmer) have been playing with Hare and what intrigues me | |
| 15 | about the language. | |
| 16 | ||
| 17 | ## Hare | |
| 18 | ||
| 19 | The [Hare](https://harelang.org) programming language is a | |
| 20 | straightforward language that should look familiar if you've ever | |
| 21 | programmed with C, Rust, or other languages that aim to build software | |
| 22 | at the system-level. | |
| 23 | ||
| 24 | The Hare homepage states the following: | |
| 25 | ||
| 26 | > Hare is a systems programming language designed to be simple, stable, | |
| 27 | > and robust. Hare uses a static type system, manual memory management, | |
| 28 | > and minimal runtime. It is well-suited to writing operating systems, | |
| 29 | > system tools, compilers, networking software, and other low-level, | |
| 30 | > high performance tasks. | |
| 31 | ||
| 32 | I have found this all to be true while playing with it for the first | |
| 33 | time today. In the next few sections, I'm going to walk through my | |
| 34 | installation and first program. | |
| 35 | ||
| 36 | ### Installation | |
| 37 | ||
| 38 | I'm currently running Alpine Linux on my Thinkpad, so the installation | |
| 39 | was quite easy as there is a package for Hare in the `apk` | |
| 40 | repositories. | |
| 41 | ||
| 42 | ```sh | |
| 43 | doas apk add hare hare-doc | |
| 44 | ``` | |
| 45 | ||
| 46 | However, I was able to install Hare from scratch on Fedora Linux a short | |
| 47 | while ago, which was also very easy to do. If you need further | |
| 48 | instructions and Hare doesn't have a package on your system, take a | |
| 49 | look at the [Hare Installation](https://harelang.org/installation/) | |
| 50 | page. | |
| 51 | ||
| 52 | ### Creating a Test Project | |
| 53 | ||
| 54 | In order to play with the language, I created | |
| 55 | [hare-test](https://git.sr.ht/~cmc/hare-projects) and will be putting | |
| 56 | any of my Hare-related adventures in here. | |
| 57 | ||
| 58 | > **Update:** I also created a simple Hare program for creating a file | |
| 59 | > from user input: | |
| 60 | > [files.ha](https://git.sr.ht/~cmc/hare-projects/tree/main/item/files/files.ha) | |
| 61 | ||
| 62 | Luckily, Hare doesn't require any complex set-up tools or build | |
| 63 | environment. Once you have Hare installed, you simply need to create a | |
| 64 | file ending with `.ha` and you can run a Hare program. | |
| 65 | ||
| 66 | I created a file called `rgb.ha` in order to test out the | |
| 67 | random number generation and passing parameters between functions. | |
| 68 | ||
| 69 | ```sh | |
| 70 | nano rgb.ha | |
| 71 | ``` | |
| 72 | ||
| 73 | Within this file, I was able to easily import a few of the [standard | |
| 74 | library modules](https://harelang.org/tutorials/stdlib/): | |
| 75 | `fmt`, `math::random`, and `datetime`. | |
| 76 | ||
| 77 | With these modules, I created two functions: | |
| 78 | ||
| 79 | 1. `main`: This function calls the `generate_rgb` | |
| 80 | function and then prints out the returned values. | |
| 81 | 2. `generate_rgb`: This function uses the current Unix epoch | |
| 82 | time to generate a pseudo-random value and uses this value to create | |
| 83 | three more random values between 0 and 255. These three numbers | |
| 84 | represent a color in RGB format. | |
| 85 | ||
| 86 | > **Note**: Some syntax coloring may look odd, as Zola currently | |
| 87 | > doesn't have a syntax highlighting theme for Hare. Instead, I'm | |
| 88 | > using the C theme, which may not be exactly accurate when coloring the | |
| 89 | > code below. | |
| 90 | ||
| 91 | ```c | |
| 92 | use datetime; | |
| 93 | use fmt; | |
| 94 | use math::random; | |
| 95 | ||
| 96 | export fn main() void = { | |
| 97 | const rgb = generate_rgb(); | |
| 98 | fmt::printfln("RGB: ({}, {}, {})", rgb[0], rgb[1], rgb[2])!; | |
| 99 | }; | |
| 100 | ||
| 101 | fn generate_rgb() []u64 = { | |
| 102 | // Use the current Unix epoch time as the seed value | |
| 103 | let datetime = datetime::epochunix(&datetime::now()); | |
| 104 | ||
| 105 | // Generate initial pseudo-random value | |
| 106 | // You must cast the datetime from int to u64 | |
| 107 | let x = random::init(datetime: u64); | |
| 108 | ||
| 109 | // Generate RGB values between (0, 255) using pseudo-random init value | |
| 110 | let r = random::u64n(&x, 255); | |
| 111 | let g = random::u64n(&x, 255); | |
| 112 | let b = random::u64n(&x, 255); | |
| 113 | ||
| 114 | // Structure data as array and return | |
| 115 | let rgb_array: [3]u64 = [r, g, b]; | |
| 116 | return rgb_array; | |
| 117 | }; | |
| 118 | ``` | |
| 119 | ||
| 120 | ### Running a Program | |
| 121 | ||
| 122 | Once you have a Hare file written and ready to run, you simply need to | |
| 123 | run it: | |
| 124 | ||
| 125 | ```sh | |
| 126 | hare run file.ha | |
| 127 | ``` | |
| 128 | ||
| 129 | You can also compile the program into an executable: | |
| 130 | ||
| 131 | ```sh | |
| 132 | hare build -o example file.ha | |
| 133 | ./example | |
| 134 | ``` | |
| 135 | ||
| 136 | ### Initial Thoughts | |
| 137 | ||
| 138 | 1. Documentation Improvements Would Help | |
| 139 | ||
| 140 | While I was able to piece everything together eventually, the | |
| 141 | biggest downfall right now in Hare's documentation. For such a new | |
| 142 | project, the documentation is in a great spot. However, bare | |
| 143 | specifications don't help as much as a brief examples section | |
| 144 | would. | |
| 145 | ||
| 146 | For example, it took me a while to figure out what the | |
| 147 | `u64n` function was looking for. I could tell that it | |
| 148 | took two parameters and the second was my max value (255), but | |
| 149 | couldn't figure out what the first value should be. Eventually, I | |
| 150 | inspected the `random.ha` file in the [Hare source | |
| 151 | code](https://git.sr.ht/~sircmpwn/hare/tree/master/item/math/random/random.ha) | |
| 152 | and found the test suite that helped me discover that it needed an | |
| 153 | `init()` value in the form of `&var`. | |
| 154 | ||
| 155 | 2. More Basic Modules | |
| 156 | ||
| 157 | This is another point that comes from Hare being new and awaiting | |
| 158 | more contributions, but there are some basic functions that I would | |
| 159 | personally enjoy seeing in Hare, such as one to convert decimal | |
| 160 | (base 10) values to hexadecimal (base 16). | |
| 161 | ||
| 162 | If I'm feeling comfortable with my math, I may work on the list of | |
| 163 | functions I want and see if any can make it into the Hare source | |
| 164 | code. | |
| 165 | ||
| 166 | 3. Overall Thoughts | |
| 167 | ||
| 168 | Overall, I actually really enjoy Hare. It's not as tedious to get a | |
| 169 | project up and running as Rust, but it's also simpler and more | |
| 170 | user-friendly than learning C. I am going to continue playing with | |
| 171 | it and see if I can make anything of particular value. | |
content/blog/2023-06-18-unifi-ip-blocklist.md deleted −87
| @@ -1,87 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-06-18 | |
| 3 | title = "Block IP Addresses and Subnets with Unifi Network Firewall" | |
| 4 | description = "Learn how to use the Unifi Network Firewall to block IP addresses and subnets." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Identifying Abusive IPs | |
| 8 | ||
| 9 | If you're like me and use Unifi network equipment at the edge of the | |
| 10 | network you manage, you may know that Unifi is only somewhat decent at | |
| 11 | identifying and blocking IPs that represent abusive or threat actors. | |
| 12 | ||
| 13 | While Unifi has a [threat | |
| 14 | management](https://help.ui.com/hc/en-us/articles/360006893234-UniFi-Gateway-Threat-Management) | |
| 15 | tool inside their Network application, it can be lacking in | |
| 16 | functionality and identification. For example, I have my UDM Pro set to | |
| 17 | identify and block almost all categories of threats available within the | |
| 18 | Unifi settings. However, I regularly identify abusive actors on my web | |
| 19 | server via the server logs. | |
| 20 | ||
| 21 | In addition, I have identified IP addresses and subnets directly within | |
| 22 | Unifi's logs that the UDM did not block for whatever reason. | |
| 23 | ||
| 24 | This guide is meant to be another step in the process to manually block | |
| 25 | abusive IP addresses or subnets that you have identified but are not | |
| 26 | being automatically blocked yet. | |
| 27 | ||
| 28 | ## Create an IP Group Profile | |
| 29 | ||
| 30 | To start, login to the Unifi machine's web GUI and navigate to the | |
| 31 | Network app \> Settings \> Profiles. | |
| 32 | ||
| 33 | Within this page, choose the `IP Groups` tab and click | |
| 34 | `Create New`. | |
| 35 | ||
| 36 |  | |
| 38 | ||
| 39 | Each IP Group profile can be used as one of three options: | |
| 40 | ||
| 41 | 1. Port Group | |
| 42 | 2. IPv4 Address/Subnet | |
| 43 | 3. IPv6 Address/Subnet | |
| 44 | ||
| 45 | In this example, I'm creating an IPv4 Address/Subnet group and adding a | |
| 46 | few different IP addresses and a subnet. Once you've added all IP | |
| 47 | addresses and subnets, click the `Apply` button that should | |
| 48 | appear at the bottom. | |
| 49 | ||
| 50 |  | |
| 52 | ||
| 53 | At this point, the IPv4 Address/Subnet has been created but not yet | |
| 54 | used. | |
| 55 | ||
| 56 | ## Drop IP Group Profile via the Unifi Firewall | |
| 57 | ||
| 58 | To instruct the Unifi machine to block the profile we just created, we | |
| 59 | need to navigate to the Network app \> Settings \> Firewall & Security. | |
| 60 | ||
| 61 | Within this screen, find the Firewall Rules table and click | |
| 62 | `Create Entry`. This entry should contain the following | |
| 63 | settings: | |
| 64 | ||
| 65 | - Type: `Internet In` | |
| 66 | - Description: `<Your Custom Rule>` | |
| 67 | - Rule Applied: `Before Predefined Rules` | |
| 68 | - Action: `Drop` | |
| 69 | - Source Type: `Port/IP Group` | |
| 70 | - IPv4 Address Group: | |
| 71 | `<Name of the Group Profile You Created Above>` | |
| 72 | ||
| 73 | Customize the remaining configurations to your liking, and then save and | |
| 74 | enable the firewall rule. | |
| 75 | ||
| 76 |  | |
| 78 | ||
| 79 | Once enabled, the Unifi machine will be able to drop all incoming | |
| 80 | connections from the defined IP addresses and subnets within the created | |
| 81 | profile. | |
| 82 | ||
| 83 | > As a personal aside to this topic, I'm looking for a convenient way | |
| 84 | > to update the firewall rules or profiles remotely (within the LAN) | |
| 85 | > from the web server to accelerate this process. If you have an idea on | |
| 86 | > how to automatically update Unifi IP groups or firewall rules, let me | |
| 87 | > know! | |
content/blog/2023-06-20-audit-review-template.md deleted −80
| @@ -1,80 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-06-20 | |
| 3 | title = "Audit Testing Review Template" | |
| 4 | description = "A handy reference template for audit reviews." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Overview | |
| 8 | ||
| 9 | This post is a *very* brief overview on the basic process to review | |
| 10 | audit test results, focusing on work done as part of a financial | |
| 11 | statement audit (FSA) or service organization controls (SOC) report. | |
| 12 | ||
| 13 | While there are numerous different things to review and look for - all | |
| 14 | varying wildly depending on the report, client, and tester - this list | |
| 15 | serves as a solid base foundation for a reviewer. | |
| 16 | ||
| 17 | I have used this throughout my career as a starting point to my reviews, | |
| 18 | and it has worked wonders for creating a consistent and objective | |
| 19 | template to my reviews. The goal is to keep this base high-level enough | |
| 20 | to be used on a wide variety of engagements, while still ensuring that | |
| 21 | all key areas are covered. | |
| 22 | ||
| 23 | ## Review Template | |
| 24 | ||
| 25 | 1. [ ] Check all documents for spelling and grammar. | |
| 26 | 2. [ ] Ensure all acronyms are fully explained upon first use. | |
| 27 | 3. [ ] For all people referenced, use their full names and job titles | |
| 28 | upon first use. | |
| 29 | 4. [ ] All supporting documents must cross-reference to the lead sheet | |
| 30 | and vice-versa. | |
| 31 | 5. [ ] Verify that the control has been adequately tested: | |
| 32 | - [ ] **Test of Design**: Did the tester obtain information | |
| 33 | regarding how the control should perform normally and abnormally | |
| 34 | (e.g., emergency scenarios)? | |
| 35 | - [ ] **Test of Operating Effectiveness**: Did the tester inquire, | |
| 36 | observe, inspect, or re-perform sufficient evidence to support | |
| 37 | their conclusion over the control? Inquiry alone is not | |
| 38 | adequate! | |
| 39 | 6. [ ] For any information used in the control, whether by the control | |
| 40 | operator or by the tester, did the tester appropriately document the | |
| 41 | source (system or person), extraction method, parameters, and | |
| 42 | completeness and accuracy (C&A)? | |
| 43 | - [ ] For any reports, queries, etc. used in the extraction, did | |
| 44 | the tester include a copy and notate C&A considerations? | |
| 45 | 7. [ ] Did the tester document the specific criteria that the control | |
| 46 | is being tested against? | |
| 47 | 8. [ ] Did the tester notate in the supporting documents where each | |
| 48 | criterion was satisfied? | |
| 49 | 9. [ ] If testing specific policies or procedures, are the documents | |
| 50 | adequate? | |
| 51 | - [ ] e.g., a test to validate that a review of policy XYZ occurs | |
| 52 | periodically should also evaluate the sufficiency of the policy | |
| 53 | itself, if meant to cover the risk that such a policy does not | |
| 54 | exist and is not reviewed. | |
| 55 | 10. [ ] Does the test cover the appropriate period under review? | |
| 56 | - [ ] If the test is meant to cover only a portion of the audit | |
| 57 | period, do other controls exist to mitigate the risks that exist | |
| 58 | for the remainder of the period? | |
| 59 | 11. [ ] For any computer-aided audit tools (CAATs) or other automation | |
| 60 | techniques used in the test, is the use of such tools explained and | |
| 61 | appropriately documented? | |
| 62 | 12. [ ] If prior-period documentation exists, are there any missing | |
| 63 | pieces of evidence that would further enhance the quality of the | |
| 64 | test? | |
| 65 | 13. [ ] Was any information discovered during the walkthrough or inquiry | |
| 66 | phase that was not incorporated into the test? | |
| 67 | 14. [ ] Are there new rules or expectations from your company's | |
| 68 | internal guidance or your regulatory bodies that would affect the | |
| 69 | audit approach for this control? | |
| 70 | 15. [ ] Was an exception, finding, or deficiency identified as a result | |
| 71 | of this test? | |
| 72 | - [ ] Was the control deficient in design, operation, or both? | |
| 73 | - [ ] What was the root cause of the finding? | |
| 74 | - [ ] Does the finding indicate other findings or potential fraud? | |
| 75 | - [ ] What's the severity and scope of the finding? | |
| 76 | - [ ] Do other controls exist as a form of compensation against | |
| 77 | the finding's severity, and do they mitigate the risk within | |
| 78 | the control objective? | |
| 79 | - [ ] Does the finding exist at the end of the period, or was it | |
| 80 | resolved within the audit period? | |
content/blog/2023-06-28-backblaze-b2.md deleted −188
| @@ -1,188 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-06-28 | |
| 3 | title = "Getting Started with Backblaze B2 Cloud Storage" | |
| 4 | description = "An introduction to the free ttier of Backblaze B2 Cloud Storage." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Overview | |
| 8 | ||
| 9 | Backblaze [B2 Cloud | |
| 10 | Storage](https://www.backblaze.com/b2/cloud-storage.html) is an | |
| 11 | inexpensive and reliable on-demand cloud storage and backup solution. | |
| 12 | ||
| 13 | The service starts at \$5/TB/month (\$0.005/GB/month) with a download | |
| 14 | rate of \$0.01/GB/month. | |
| 15 | ||
| 16 | However, there are free tiers: | |
| 17 | ||
| 18 | - The first 10 GB of storage is free. | |
| 19 | - The first 1 GB of data downloaded each day is free. | |
| 20 | - Class A transactions are free. | |
| 21 | - The first 2500 Class B transactions each day are free. | |
| 22 | - The first 2500 Class C transactions each day are free. | |
| 23 | ||
| 24 | You can see which API calls fall into categories A, B, or C here: | |
| 25 | [Pricing Organized by API | |
| 26 | Calls](https://www.backblaze.com/b2/b2-transactions-price.html). | |
| 27 | ||
| 28 | For someone like me, who wants an offsite backup of their server's | |
| 29 | `/home/` directory and various other server configs that fall | |
| 30 | under 10 GB total, Backblaze is a great solution from a financial | |
| 31 | perspective. | |
| 32 | ||
| 33 | ## Create An Account | |
| 34 | ||
| 35 | To start with Backblaze, you'll need to [create a free | |
| 36 | account](https://www.backblaze.com/b2/sign-up.html) - no payment method | |
| 37 | is required to sign up. | |
| 38 | ||
| 39 | Once you have an account, you can test out the service with their web | |
| 40 | GUI, their mobile app, or their CLI tool. I'm going to use the CLI tool | |
| 41 | below to test a file upload and then sync an entire directory to my | |
| 42 | Backblaze bucket. | |
| 43 | ||
| 44 | ## Create a Bucket | |
| 45 | ||
| 46 | Before you can start uploading, you need to create a bucket. If you're | |
| 47 | familiar with other object storage services, this will feel familiar. If | |
| 48 | not, it's pretty simple to create one. | |
| 49 | ||
| 50 | As their webpage says: | |
| 51 | ||
| 52 | > A bucket is a container that holds files that are uploaded into B2 | |
| 53 | > Cloud Storage. The bucket name must be globally unique and must have a | |
| 54 | > minimum of 6 characters. A limit of 100 buckets may be created per | |
| 55 | > account. An unlimited number of files may be uploaded into a bucket. | |
| 56 | ||
| 57 | Once you click the `Create a Bucket` button on their webpage | |
| 58 | or mobile app, you need to provide the following: | |
| 59 | ||
| 60 | - Bucket Unique Name | |
| 61 | - Files in Bucket are: `Private` or `Public` | |
| 62 | - Default Encryption: `Disable` or `Enable` | |
| 63 | - Object Lock: `Disable` or `Enable` | |
| 64 | ||
| 65 | For my bucket, I created a private bucket with encryption enabled and | |
| 66 | object lock disabled. | |
| 67 | ||
| 68 | Once your bucket is created, you can test the upload/download feature on | |
| 69 | their web GUI or mobile app! At this point, you have a fully functional | |
| 70 | bucket and account. | |
| 71 | ||
| 72 | ## Linux CLI Tool | |
| 73 | ||
| 74 | ### Installation | |
| 75 | ||
| 76 | To install the `b2` CLI tool, you'll need to download it | |
| 77 | from the [CLI | |
| 78 | Tools](https://www.backblaze.com/docs/cloud-storage-command-line-tools) | |
| 79 | page. I recommend copying the URL from the link that says | |
| 80 | `Linux` and using wget to download it, as shown below. | |
| 81 | ||
| 82 | Once downloaded, make the file executable and move it to a location on | |
| 83 | your `$PATH`, so that you can execute that command from | |
| 84 | anywhere on the machine. | |
| 85 | ||
| 86 | ```sh | |
| 87 | wget <b2_cli_url> | |
| 88 | chmod +x b2_linux | |
| 89 | mv b2_linux /usr/bin/b2 | |
| 90 | ``` | |
| 91 | ||
| 92 | ### Log In | |
| 93 | ||
| 94 | The first step after installation is to log in. To do this, execute the | |
| 95 | following command and provide your `<applicationKeyId>` and | |
| 96 | `<applicationKey>`. | |
| 97 | ||
| 98 | If you don't want to provide these values in the command itself, you | |
| 99 | can simply execute the base command and it will request them in an | |
| 100 | interactive prompt. | |
| 101 | ||
| 102 | ```sh | |
| 103 | # if you want to provide the keys directly: | |
| 104 | b2 authorize-account [<applicationKeyId>] [<applicationKey>] | |
| 105 | ||
| 106 | # or, if you don't want your keys in your shell history: | |
| 107 | b2 authorize-account | |
| 108 | ``` | |
| 109 | ||
| 110 | ### Upload a Test File | |
| 111 | ||
| 112 | In order to test the functionality of the CLI tool, I'll start by | |
| 113 | uploading a single test file to the bucket I created above. We can do | |
| 114 | this with the `upload_file` function. | |
| 115 | ||
| 116 | The command is issued as follows: | |
| 117 | ||
| 118 | ```sh | |
| 119 | b2 upload_file <bucket_name> <local_file> <remote_file> | |
| 120 | ``` | |
| 121 | ||
| 122 | In my situation, I executed the following command with my username. | |
| 123 | ||
| 124 | ```sh | |
| 125 | b2 upload_file my_unique_bucket /home/<user>/test.md test.md | |
| 126 | ``` | |
| 127 | ||
| 128 | To confirm that the file was uploaded successfully, list the files in | |
| 129 | your bucket: | |
| 130 | ||
| 131 | ```sh | |
| 132 | b2 ls <bucket_name> | |
| 133 | ``` | |
| 134 | ||
| 135 | ```txt | |
| 136 | test.md | |
| 137 | ``` | |
| 138 | ||
| 139 | ### Sync a Directory | |
| 140 | ||
| 141 | If you have numerous files, you can use the `sync` function | |
| 142 | to perform functionality similar to `rsync`, where you can | |
| 143 | check what's in your bucket and sync anything that is new or modified. | |
| 144 | ||
| 145 | The command is issued as follows: | |
| 146 | ||
| 147 | ```sh | |
| 148 | b2 sync <source file location> <B2 bucket destination> | |
| 149 | ``` | |
| 150 | ||
| 151 | In my case, I can sync my user's entire home directory to my bucket | |
| 152 | without specifying any of the files directly: | |
| 153 | ||
| 154 | ```sh | |
| 155 | b2 sync /home/<user>/ "b2://<bucketName>/home/<user>" | |
| 156 | ``` | |
| 157 | ||
| 158 | ## Caveats | |
| 159 | ||
| 160 | ### Timing of Updates to the Web GUI | |
| 161 | ||
| 162 | When performing actions over a bucket, there is a slight delay in the | |
| 163 | web GUI when inspecting a bucket or its file. Note that simple actions | |
| 164 | such as uploading or deleting files may have a delay of a few minutes up | |
| 165 | to 24 hours. In my experience (\<10 GB and \~20,000 files), any actions | |
| 166 | took only a few minutes to update across clients. | |
| 167 | ||
| 168 | ### Symlinks | |
| 169 | ||
| 170 | Note that symlinks are resolved by b2, so if you have a link from | |
| 171 | `/home/<user>/nas-storage` that symlinks out to a | |
| 172 | `/mnt/nas-storage` folder that has 10TB of data, | |
| 173 | `b2` will resolve that link and start uploading all 10TB of | |
| 174 | data linked within the folder. | |
| 175 | ||
| 176 | If you're not sure if you have any symlinks, a symlink will look like | |
| 177 | this (note the `->` symbol): | |
| 178 | ||
| 179 | ```sh | |
| 180 | > ls -lha | |
| 181 | lrwxrwxrwx 1 root root 20 Jun 28 13:32 nas -> /mnt/nas-storage/ | |
| 182 | ``` | |
| 183 | ||
| 184 | You can recursively find symlink in a path with the following command: | |
| 185 | ||
| 186 | ```sh | |
| 187 | ls -lR /path/to/search | grep '^l' | |
| 188 | ``` | |
content/blog/2023-08-18-agile-auditing.md deleted −158
| @@ -1,158 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-08-18 | |
| 3 | title = "Agile Auditing: An Introduction" | |
| 4 | description = "A quick introduction to using the Agile methodology in an audit." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## What is Agile Auditing? | |
| 8 | ||
| 9 | [Agile](https://en.wikipedia.org/wiki/Agile_software_development), the | |
| 10 | collaborative philosophy behind many software development methods, has | |
| 11 | been picking up steam as a beneficial tool to use in the external and | |
| 12 | internal auditing world. | |
| 13 | ||
| 14 | This blog post will walk through commonly used terms within Agile, | |
| 15 | Scrum, and Kanban in order to translate these terms and roles into | |
| 16 | audit-specific terms. | |
| 17 | ||
| 18 | Whether your team is in charge of a financial statement audit, an | |
| 19 | attestation (SOC 1, SOC 2, etc.), or a unique internal audit, the terms | |
| 20 | used throughout this post should still apply. | |
| 21 | ||
| 22 | ## Agile | |
| 23 | ||
| 24 | To start, I'll take a look at Agile. | |
| 25 | ||
| 26 | > The Agile methodology is a project management approach that involves | |
| 27 | > breaking the project into phases and emphasizes continuous | |
| 28 | > collaboration and improvement. Teams follow a cycle of planning, | |
| 29 | > executing, and evaluating. | |
| 30 | ||
| 31 | While this approach may seem familiar to what audit teams have | |
| 32 | historically done, an audit team must make distinct changes in their | |
| 33 | mentality and how they approach and manage a project. | |
| 34 | ||
| 35 | ### Agile Values | |
| 36 | ||
| 37 | The Agile Manifesto, written in 2001 at a summit in Utah, contain a set | |
| 38 | of four main values that comprise the Agile approach: | |
| 39 | ||
| 40 | 1. Individuals and interactions over processes and tools. | |
| 41 | 2. Working software over comprehensive documentation. | |
| 42 | 3. Customer collaboration over contract negotiation. | |
| 43 | 4. Responding to change over following a plan. | |
| 44 | ||
| 45 | Beyond the four values, [twelve | |
| 46 | principles](https://agilemanifesto.org/principles.html) were also | |
| 47 | written as part of the summit. | |
| 48 | ||
| 49 | In order to relate these values to an audit or attestation engagement, | |
| 50 | we need to shift the focus from software development to the main goal of | |
| 51 | an engagement: completing sufficient audit testing to address to | |
| 52 | relevant risks over the processes and controls at hand. | |
| 53 | ||
| 54 | Audit Examples: | |
| 55 | ||
| 56 | - Engagement teams must value the team members, client contacts, and | |
| 57 | their interactions over the historical processes and tools that have | |
| 58 | been used. | |
| 59 | - Engagement teams must value a final report that contains sufficient | |
| 60 | audit documentation over excessive documentation or scope creep. | |
| 61 | - Engagement teams must collaborate with the audit clients as much as | |
| 62 | feasible to ensure that both sides are constantly updated with | |
| 63 | current knowledge of the engagement's status and any potential | |
| 64 | findings, rather than waiting for pre-set meetings or the end of the | |
| 65 | engagement to communicate. | |
| 66 | - Engagement teams must be able to respond to change in an | |
| 67 | engagement's schedule, scope, or environment to ensure that the | |
| 68 | project is completed in a timely manner and that all relevant areas | |
| 69 | are tested. | |
| 70 | - In terms of an audit department's portfolio, they must be able | |
| 71 | to respond to changes in their company's or client's | |
| 72 | environment and be able to dynamically change their audit plan | |
| 73 | accordingly. | |
| 74 | ||
| 75 | ## Scrum | |
| 76 | ||
| 77 | The above section discusses the high-level details of the Agile | |
| 78 | philosophy and how an audit team can potentially mold that mindset into | |
| 79 | the audit world, but how does a team implement these ideas? | |
| 80 | ||
| 81 | There are many methods that use an Agile mindset, but I prefer | |
| 82 | [Scrum](https://en.wikipedia.org/wiki/Scrum_(software_development)). | |
| 83 | Scrum is a framework based on Agile that enables a team to work through | |
| 84 | a project through a series of roles, ceremonies, artifacts, and values. | |
| 85 | ||
| 86 | Let's dive into each of these individually. | |
| 87 | ||
| 88 | ### Scrum Team | |
| 89 | ||
| 90 | A scrum project is only as good as the team running the project. | |
| 91 | Standard scrum teams are separated into three distinct areas: | |
| 92 | ||
| 93 | 1. **Product Owner (Client Contact)**: The client contact is the audit | |
| 94 | equivalent of the product owner in Scrum. They are responsible for | |
| 95 | partnering with the engagement or audit team to ensure progress is | |
| 96 | being made, priorities are established, and clear guidance is given | |
| 97 | when questions or findings arise within each sprint. | |
| 98 | 2. **Scrum Master (Engagement Lead)**: The engagement or audit team | |
| 99 | lead is responsible for coaching the team and the client contact on | |
| 100 | the scrum process, tracking team progress against plan, scheduling | |
| 101 | necessary resources, and helping remove obstacles. | |
| 102 | 3. **Scrum Developers (Engagement Members)**: The engagement or audit | |
| 103 | team is the set of team members responsible for getting the work | |
| 104 | done. These team members will work on each task, report progress, | |
| 105 | resolve obstacles, and collaborate with other team members and the | |
| 106 | client contact to ensure goals are being met. | |
| 107 | ||
| 108 | ### Scrum Ceremonies | |
| 109 | ||
| 110 | Scrum ceremonies are events that are performed on a regular basis. | |
| 111 | ||
| 112 | 1. **Sprint Planning**: The team works together to plan the upcoming | |
| 113 | sprint goal and which user stories (tasks) will be added to the | |
| 114 | sprint to achieve that goal. | |
| 115 | 2. **Sprint**: The time period, typically at least one week and no more | |
| 116 | than one month in length, where the team works on the stories and | |
| 117 | anything in the backlog. | |
| 118 | 3. **Daily Scrum**: A very short meeting held each day, typically 15 | |
| 119 | minutes, to quickly emphasize alignment on the sprint goal and plan | |
| 120 | the next 24 hours. Each team member may share what they did the day | |
| 121 | before, what they'll do today, and any obstacles to their work. | |
| 122 | 4. **Sprint Review**: At the end of each sprint, the team will gather | |
| 123 | and discuss the progress, obstacles, and backlog from the previous | |
| 124 | sprint. | |
| 125 | 5. **Sprint Retrospective**: More specific than the sprint review, the | |
| 126 | retrospective is meant to discuss what worked and what did not work | |
| 127 | during the sprint. This may be processes, tools, people, or even | |
| 128 | things related to the Scrum ceremonies. | |
| 129 | ||
| 130 | One additional ceremony that may be applicable is organizing the | |
| 131 | backlog. This is typically the responsibility of the engagement leader | |
| 132 | and is meant to prioritize and clarify what needs to be done to complete | |
| 133 | items in the backlog. | |
| 134 | ||
| 135 | ### Artifacts | |
| 136 | ||
| 137 | While artifacts are generally not customizable in the audit world (i.e., | |
| 138 | each control test must include some kind of working paper with evidence | |
| 139 | supporting the test results), I wanted to include some quick notes on | |
| 140 | associating scrum artifact terms with an audit. | |
| 141 | ||
| 142 | 1. **Product Backlog**: This is the overall backlog of unfinished audit | |
| 143 | tasks from all prior sprints. | |
| 144 | 2. **Sprint Backlog**: This is the backlog of unfinished audit tasks | |
| 145 | from one individual sprint. | |
| 146 | 3. **Increment**: This is the output of each sprint - generally this is | |
| 147 | best thought of as any documentation prepared during the sprint, | |
| 148 | such as risk assessments, control working papers, deficiency | |
| 149 | analysis, etc. | |
| 150 | ||
| 151 | ## Kanban | |
| 152 | ||
| 153 | Last but not least, Kanban is a methodology that relies on boards to | |
| 154 | categorize work into distinct, descriptive categories that allow an | |
| 155 | agile or scrum team to effectively plan the work of a sprint or project. | |
| 156 | ||
| 157 | See Atlassian's [Kanban](https://www.atlassian.com/agile/kanban) page | |
| 158 | for more information. | |
content/blog/2023-10-04-digital-minimalism.md deleted −106
| @@ -1,106 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-10-04 | |
| 3 | title = "Digital Minimalism" | |
| 4 | description = "My personal retrospective on digital minimalism." | |
| 5 | +++ | |
| 6 | ||
| 7 | I've written [a note about minimalism](/wiki/#digital-garden) | |
| 8 | before, but I wanted to dedicate some time to reflect on digital | |
| 9 | minimalism and how I've been able to minimize the impact of digital | |
| 10 | devices in my life. | |
| 11 | ||
| 12 | > These changes crept up on us and happened fast, before we had a chance | |
| 13 | > to step back and ask what we really wanted out of the rapid advances | |
| 14 | > of the past decade. We added new technologies to the periphery of our | |
| 15 | > experience for minor reasons, then woke one morning to discover that | |
| 16 | > they had colonized the core of our daily life. We didn't, in other | |
| 17 | > words, sign up for the digital world in which we're currently | |
| 18 | > entrenched; we seem to have stumbled backward into it. | |
| 19 | > | |
| 20 | > *(Digital Minimalism, 2019)* | |
| 21 | ||
| 22 | ## The Principles of Digital Minimalism | |
| 23 | ||
| 24 | As noted in Cal Newport's book, *Digital Minimalism*, there are three | |
| 25 | main principles to digital minimalism that I tend to agree with: | |
| 26 | ||
| 27 | 1. Clutter is costly. | |
| 28 | - Digital minimalists recognize that cluttering their time and | |
| 29 | attention with too many devices, apps, and services creates an | |
| 30 | overall negative cost that can swamp the small benefits that | |
| 31 | each individual item provides in isolation. | |
| 32 | 2. Optimization is important. | |
| 33 | - Digital minimalists believe that deciding a particular | |
| 34 | technology supports something they value is only the first step. | |
| 35 | To truly extract its full potential benefit, it's necessary to | |
| 36 | think carefully about how they'll use the technology. | |
| 37 | 3. Intentionality is satisfying. | |
| 38 | - Digital minimalists derive significant satisfaction from their | |
| 39 | general commitment to being more intentional about how they | |
| 40 | engage with new technologies. This source of satisfaction is | |
| 41 | independent of the specific decisions they make and is one of | |
| 42 | the biggest reasons that minimalism tends to be immensely | |
| 43 | meaningful to its practitioners. | |
| 44 | ||
| 45 | ## Taking Action | |
| 46 | ||
| 47 | In order to put the logic into practice, I've created a few new habits | |
| 48 | and continued performing old habits that are working well: | |
| 49 | ||
| 50 | ### Using Devices With Intention | |
| 51 | ||
| 52 | - I already rarely use "social media", mostly limited to forums such | |
| 53 | as Hacker News and Tildes, so I've just tweaked my behavior to stop | |
| 54 | looking for content in those places when I'm bored. | |
| 55 | - Use devices with intention. Each time I pick up a digital device, | |
| 56 | there should be an intention to use the device to improve my current | |
| 57 | situation. No more endless scrolling or searching for something to | |
| 58 | interest me. | |
| 59 | ||
| 60 | ### Prevent Distractions | |
| 61 | ||
| 62 | - Disable (most) notifications on all devices. I spent 15-30 minutes | |
| 63 | going through the notifications on my phone, watch, and computer to | |
| 64 | ensure that only a select few apps have the ability to interrupt me: | |
| 65 | Calendar, Messages, Phone, Reminders, & Signal. | |
| 66 | - Disable badges for any apps except the ones mentioned in the bullet | |
| 67 | above. | |
| 68 | - Set-up focus profiles across devices so that I can enable different | |
| 69 | modes, such as Personal when I only want to see notifications from | |
| 70 | people I care about or Do Not Disturb, where absolutely nothing can | |
| 71 | interrupt me. | |
| 72 | - Clean up my home screens. This one was quite easy as I already | |
| 73 | maintain a minimalist set-up, but I went extreme by limiting my | |
| 74 | phone to just eight apps on the home screen and four in the dock. If | |
| 75 | I need another app, I'll have to search or use the app library. | |
| 76 | - Remove the work profile from my phone. This was a tough decision as | |
| 77 | having my work profile on my device definitely makes my life easier | |
| 78 | at times, but it also has quite a negative effect when I'm "always | |
| 79 | online" and can see the notifications and team activity 24/7. I | |
| 80 | believe creating a distinct barrier between my work and personal | |
| 81 | devices will be beneficial in the end. | |
| 82 | ||
| 83 | ### Creating Alternative Activities | |
| 84 | ||
| 85 | This is the most difficult piece, as most of my hobbies and interests | |
| 86 | lie in the digital world. However, I'm making a concerted effort to put | |
| 87 | devices down unless necessary and force myself to perform other | |
| 88 | activities in the physical world instead. | |
| 89 | ||
| 90 | I've started with a few basics that are always readily available to me: | |
| 91 | ||
| 92 | - Do a chore, such as organizing or cleaning. | |
| 93 | - Read a book, study a piece of art, etc. | |
| 94 | - Exercise or get outdoors. | |
| 95 | - Participate in a hobby, such as photography, birding, disc golf, | |
| 96 | etc. | |
| 97 | - Let yourself be bored and wander into creativity. | |
| 98 | ||
| 99 | ## Making Progress | |
| 100 | ||
| 101 | I'll be taking notes as I continue down this journey and hope to see | |
| 102 | positive trends. I've always been a minimalist in the physical world | |
| 103 | and it feels refreshing to filter out the clutter that has come to | |
| 104 | dominate my digital life over the years. | |
| 105 | ||
| 106 | I'm excited to see where this journey leads. | |
content/blog/2023-11-08-scli.md deleted −157
| @@ -1,157 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2023-11-08 | |
| 3 | title = "Installing scli on Alpine Linux (musl)" | |
| 4 | description = "Learn how to properly configure scli for musl-based systems." | |
| 5 | +++ | |
| 6 | ||
| 7 | [scli](https://github.com/isamert/scli) is a command-line tool that | |
| 8 | allows you to connect to your Signal messenger account. This program | |
| 9 | utilizes a two-pane display that shows you chats on the left and the | |
| 10 | focused conversation on the right. | |
| 11 | ||
| 12 | This guide will show you how to install `scli` and its | |
| 13 | dependencies on Alpine Linux, which requires some extra work due to | |
| 14 | musl. | |
| 15 | ||
| 16 | If you're using a non-musl system, you can likely following the | |
| 17 | `scli` README and download the packaged binaries for an | |
| 18 | easier installation process. | |
| 19 | ||
| 20 | ## Dependencies | |
| 21 | ||
| 22 | In order to use `scli`, you need a few dependencies: | |
| 23 | ||
| 24 | - `openjdk17-jre` - Used as a dependency for the | |
| 25 | `signal-cli` tool. Version may vary. | |
| 26 | - `signal-cli` - Used as the backbone of the | |
| 27 | `scli` tool. | |
| 28 | - `findutils` - Replaces the standard Busybox version of | |
| 29 | `xargs`. | |
| 30 | - `urwid` - A console user interface library for Python. | |
| 31 | - `urwid-readline` - For GNU emacs-like keybinds on the | |
| 32 | input line. | |
| 33 | - `qrencode` - Displays a QR code in the terminal to link | |
| 34 | the device using your phone. Not necessary if you're only linking | |
| 35 | on desktop and can copy/paste the connection URL. | |
| 36 | ||
| 37 | Let's start by installing the packages available via Alpine's | |
| 38 | repositories. Be sure to install the latest version of | |
| 39 | `openjdk`. If you run into Java-related issues, uninstall | |
| 40 | `openjdk` and install an older version. | |
| 41 | ||
| 42 | ```sh | |
| 43 | doas apk add openjdk17-jre findutils qrencode | |
| 44 | ``` | |
| 45 | ||
| 46 | Next, let's install `signal-cli`. Be sure to export the | |
| 47 | version of `signal-cli` that you want. I use version | |
| 48 | `0.12.4` below, but that may be outdated by the time you're | |
| 49 | reading this. | |
| 50 | ||
| 51 | ```sh | |
| 52 | export VERSION="0.12.4" | |
| 53 | wget https://github.com/AsamK/signal-cli/releases/download/v"${VERSION}"/signal-cli-"${VERSION}".tar.gz | |
| 54 | doas tar xf signal-cli-"${VERSION}".tar.gz -C /opt | |
| 55 | doas ln -sf /opt/signal-cli-${VERSION}"/bin/signal/cli /usr/local/bin | |
| 56 | ``` | |
| 57 | ||
| 58 | Finally, install the `urwid` packages using the Python | |
| 59 | packaging utility. | |
| 60 | ||
| 61 | ```sh | |
| 62 | pip3 install urwid urwid-readline | |
| 63 | ``` | |
| 64 | ||
| 65 | ## Installation | |
| 66 | ||
| 67 | Now that we have all of the dependencies we need, we can install | |
| 68 | `scli`. Start by simply cloning the repository. | |
| 69 | ||
| 70 | ```sh | |
| 71 | git clone https://github.com/isamert/scli | |
| 72 | ``` | |
| 73 | ||
| 74 | When I cloned this repository on 2023-11-08, I found a bug in the logic | |
| 75 | that required a fix. You must edit the `scli` file and | |
| 76 | replace the one instance of `RLIMIT_OFILE` with | |
| 77 | `RLIMIT_NOFILE`. | |
| 78 | ||
| 79 | ```sh | |
| 80 | cd scli | |
| 81 | nano scli | |
| 82 | ``` | |
| 83 | ||
| 84 | Once complete, you can move this program to anywhere on your | |
| 85 | `$PATH`. I chose the following directory. | |
| 86 | ||
| 87 | ```sh | |
| 88 | doas mv scli /usr/local/bin/scli | |
| 89 | ``` | |
| 90 | ||
| 91 | ## Initial Setup | |
| 92 | ||
| 93 | Now that everything is installed, we can login and configure the client. | |
| 94 | Start by generating a connection link. | |
| 95 | ||
| 96 | ```sh | |
| 97 | signal-cli link -n "YOUR-DEVICE-NICKNAME" | tee >(xargs -L 1 qrencode -t utf8) | |
| 98 | ``` | |
| 99 | ||
| 100 | This will generate a connection link and related QR code for you to use | |
| 101 | to link the devices together. Once complete, **wait patiently** for the | |
| 102 | connection process to finish. | |
| 103 | ||
| 104 | Once it completes, it will exit and return you to the prompt. From here, | |
| 105 | you need to perform an initial `receive` command to start | |
| 106 | things off. The `USERNAME` variable should be your phone | |
| 107 | number, such as `+15551237890`. | |
| 108 | ||
| 109 | ```sh | |
| 110 | signal-cli -u USERNAME receive | |
| 111 | ``` | |
| 112 | ||
| 113 | Also be sure to test the daemon to ensure it works properly. If no | |
| 114 | errors occur, it's working. If you run into errors because you're not | |
| 115 | running a DBUS session, see my notes below. | |
| 116 | ||
| 117 | ```sh | |
| 118 | signal-cli -u USERNAME daemon | |
| 119 | ``` | |
| 120 | ||
| 121 | Once the initial reception is complete, you are ready to use | |
| 122 | `scli`. | |
| 123 | ||
| 124 | This process will differ depending on your desktop environment (DE). If | |
| 125 | you are running a DE, you likely have a DBUS session running already and | |
| 126 | can simply launch the program. | |
| 127 | ||
| 128 | However, if you're like me and running your computer straight on the | |
| 129 | TTY without a DE, you'll need to start a DBUS session for this program. | |
| 130 | ||
| 131 | ```sh | |
| 132 | # If you're not running a DBUS session yet, you need to start one for scli | |
| 133 | dbus-run-session -- scli | |
| 134 | ||
| 135 | # OR - If you're already running a DBUS session, simply run scli | |
| 136 | scli | |
| 137 | ``` | |
| 138 | ||
| 139 | ## Configuration | |
| 140 | ||
| 141 | Lastly, there are a number of configuration options that you can pass | |
| 142 | via the command or in the `~/.config/sclirc` file. See the | |
| 143 | Github README for more information on configuration options. | |
| 144 | ||
| 145 | ```sh | |
| 146 | nano ~/.config/sclirc | |
| 147 | ``` | |
| 148 | ||
| 149 | ```conf | |
| 150 | # ~/.config/sclirc | |
| 151 | ||
| 152 | wrap-at = 80 | |
| 153 | enable-notifications = true | |
| 154 | ``` | |
| 155 | ||
| 156 | That's it! Following this guide, I have a functional `scli` | |
| 157 | program that successfully sends messages to my contacts and myself! | |
content/blog/2024-01-08-dont-say-hello.md deleted −17
| @@ -1,17 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2024-01-08 | |
| 3 | title = "Don't Say Hello" | |
| 4 | description = "A short post describing my displeasure with cliffhanger conversations." | |
| 5 | +++ | |
| 6 | ||
| 7 | I recently came back from a winter break and have started working again... only to immediately run into the dilemma of people sending me cliffhanger messages again. | |
| 8 | ||
| 9 | ## No Hello | |
| 10 | ||
| 11 | A year or two ago, I discovered [no hello](https://nohello.net/en/) and have thought about it often since then. I've even sent it to a few people since then (who wouldn't take offense to it). | |
| 12 | ||
| 13 | I work in a fast-paced environment where efficiency is extremely valuable. Therefore, I have always held a deep displeasure for conversations where people start with "Hello" and then. | |
| 14 | ||
| 15 | I searched back through my work messages and found that I received ~50 messages from ~10 people last year from people that contained "hi", "hey", or "hello" and did not contain any indication of the purpose of the conversation. I also noticed that a few of the users were responsible for the large majority of the cliffhangers. | |
| 16 | ||
| 17 | There's no real point to this post, just a desparate request for people to please stop doing this. | |
content/blog/2024-01-09-macos-customization.md deleted −166
| @@ -1,166 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2024-01-09 | |
| 3 | title = "Customizing macOS" | |
| 4 | description = "Learn how to customize macOS beyond the standard, built-in options provided by Apple." | |
| 5 | +++ | |
| 6 | ||
| 7 | I have been using macOS more than Linux lately, so I wrote this post to describe | |
| 8 | some simple options to customize macOS beyond the normal built-in settings | |
| 9 | menu. | |
| 10 | ||
| 11 | While not all-encompassing, the options below should be a good start for anyone | |
| 12 | looking to dive down the rabbit hole. | |
| 13 | ||
| 14 | ## Basics | |
| 15 | ||
| 16 | ### Package Management | |
| 17 | ||
| 18 | To install a lot of software on macOS, you will need | |
| 19 | [Homebrew](https://brew.sh/). You can use their installation script to get | |
| 20 | started. Simply open the `Terminal` application and paste the following snippet: | |
| 21 | ||
| 22 | ```sh | |
| 23 | /bin/bash -c "$(curl -fsSL https://raw.githubusercontent.com/Homebrew/install/HEAD/install.sh)" | |
| 24 | ``` | |
| 25 | ||
| 26 | This will allow you to easily install and manage applications and other software | |
| 27 | easily through the `brew` command. | |
| 28 | ||
| 29 | ### Terminal | |
| 30 | ||
| 31 | If you're serious about customizing your macOS system, I highly recommend | |
| 32 | installing a terminal emulator that you like and if you're not comfortable on | |
| 33 | the command line yet, start learning. A lot of customization options require you | |
| 34 | to edit hidden files, which is easiest in a terminal. | |
| 35 | ||
| 36 | There are options like iTerm2, Kitty, Alacritty, Hyper, Warp, or the built-in | |
| 37 | Terminal app. | |
| 38 | ||
| 39 | I use [iTerm2](https://iterm2.com/), which can be installed with Homebrew: | |
| 40 | ||
| 41 | ```sh | |
| 42 | brew install iterm2 | |
| 43 | ``` | |
| 44 | ||
| 45 |  | |
| 46 | ||
| 47 | To install color schemes, such as the Dracula scheme shown in the screenshot | |
| 48 | above, you visit [iTerm Themes](https://iterm2colorschemes.com/) and follow | |
| 49 | their installation instructions to install any of the themes. | |
| 50 | ||
| 51 | ## Desktop | |
| 52 | ||
| 53 | ### Window Management | |
| 54 | ||
| 55 | [yabai](https://github.com/koekeishiya/yabai) is a tiling window manager for | |
| 56 | macOS. While other window managers exist, I found that most of them struggled to | |
| 57 | create logical layouts and to allow me to easily move windows around the screen. | |
| 58 | ||
| 59 | Some advanced settings for yabai are only available if partially disable System | |
| 60 | Integrity Protection (SIP). However, I chose not to do this and it hasn't | |
| 61 | affected my basic usage of yabai at all. | |
| 62 | ||
| 63 | Refer to the [yabai | |
| 64 | wiki](https://github.com/koekeishiya/yabai/wiki/Installing-yabai-(latest-release)) | |
| 65 | for installation instructions. You will need to ensure that yabai is allowed to | |
| 66 | access the accessibility and screen recording APIs. | |
| 67 | ||
| 68 | You can see a basic three-pane layout atuomatically configured by yabai for me as I opened the windows below. | |
| 69 | ||
| 70 |  | |
| 71 | ||
| 72 | ### Keyboard Shortcuts | |
| 73 | ||
| 74 | [skhd](https://github.com/koekeishiya/skhd) is a simple hotkey daemon that | |
| 75 | allows you to define hotkeys in a file for usage on your system. | |
| 76 | ||
| 77 | Installation is simple: | |
| 78 | ||
| 79 | ```sh | |
| 80 | brew install koekeishiya/formulae/skhd | |
| 81 | skhd --start-service | |
| 82 | ``` | |
| 83 | ||
| 84 | After installation, be sure to allow `skhd` access to the accessibility API in | |
| 85 | the macOS privacy settings. | |
| 86 | ||
| 87 | You can configure your hotkeys in the `~/.config/skhd/skhdrc` file: | |
| 88 | ||
| 89 | ```sh | |
| 90 | nano ~/.config/skhd/skhdrc | |
| 91 | ``` | |
| 92 | ||
| 93 | For example, I have hotkeys to open my browser and terminal: | |
| 94 | ||
| 95 | ```conf | |
| 96 | # Terminal | |
| 97 | cmd - return : /Applications/iTerm.app/Contents/MacOS/iTerm2 | |
| 98 | ||
| 99 | # Browser | |
| 100 | cmd + shift - return : /Applications/LibreWolf.app/Contents/MacOS/librewolf | |
| 101 | ``` | |
| 102 | ||
| 103 | ### Widgets | |
| 104 | ||
| 105 | [uebersicht](https://github.com/felixhageloh/uebersicht/) is a handy | |
| 106 | desktop-based widget tool with a plethora of community-made widgets available in | |
| 107 | the [widgets gallery](https://tracesof.net/uebersicht-widgets/). You can also | |
| 108 | write your own widgets with this tool. | |
| 109 | ||
| 110 | To install, simply download the latest release from the [uebersicht | |
| 111 | website](https://tracesof.net/uebersicht/) and copy it to the Applications | |
| 112 | folder. | |
| 113 | ||
| 114 | See below for an example of the | |
| 115 | [Mond](https://tracesof.net/uebersicht-widgets/#Mond) widget in action. | |
| 116 | ||
| 117 |  | |
| 118 | ||
| 119 | ### Status Bar | |
| 120 | ||
| 121 | [SketchyBar](https://github.com/FelixKratz/SketchyBar) is a customizable | |
| 122 | replacement for the macOS status or menu bar. | |
| 123 | ||
| 124 | You can browse a discussion where various users shared their | |
| 125 | [configurations](https://github.com/FelixKratz/SketchyBar/discussions/47?sort=top) | |
| 126 | for inspiration or to copy their dotfiles. | |
| 127 | ||
| 128 | See below for a quick (& slightly broken) copy of | |
| 129 | [zer0yu's](https://github.com/zer0yu/dotfiles) SketchyBar configuration. | |
| 130 | ||
| 131 |  | |
| 132 | ||
| 133 | ### Dock | |
| 134 | ||
| 135 | The easiest way to customize the dock is to install | |
| 136 | [uBar](https://ubarapp.com/), which uses a Windows-like menu bar as the default | |
| 137 | style. | |
| 138 | ||
| 139 | However, the built-in macOS dock cannot be disabled and can only be set to | |
| 140 | "always hidden". This can be annoying as it will pop out any time your mouse | |
| 141 | cursor passes closely to the dock edge of the screen. Because of this, I simply | |
| 142 | use the built-in dock instead of customizing it with third-party software. | |
| 143 | ||
| 144 | Regardless, see below for the default installation style of uBar. | |
| 145 | ||
| 146 |  | |
| 147 | ||
| 148 | ### Application Icons | |
| 149 | ||
| 150 | You can also customize the icon of any application in macOS, which will show up | |
| 151 | in Finder, the Dock, Launchpad, search results, etc. I recommend using | |
| 152 | [macOSicons](https://macosicons.com/) to download icons you want, and then apply | |
| 153 | them by following this process. | |
| 154 | ||
| 155 | 1. Open the Finder application. | |
| 156 | 2. Navigate to the `Applications` folder. | |
| 157 | 3. Right-click an application of your choice, and select `Get Info`. | |
| 158 | 4. Drag the image you downloaded on top of the application's icon at the top of | |
| 159 | information window (you will see a green "plus" symbol when you're hovering | |
| 160 | over it). | |
| 161 | 5. Release the new icon on top of the old icon and it will update! | |
| 162 | ||
| 163 | You can see an example of me dragging a new `signal.icns` file onto my | |
| 164 | Signal.app information window to update it below: | |
| 165 | ||
| 166 |  | |
content/blog/2024-01-13-local-llm.md deleted −103
| @@ -1,103 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2024-01-13 | |
| 3 | title = "Running Local LLMs on macOS and iOS" | |
| 4 | description = "Finding some useful applications for running local LLMs on macOS and iOS." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## Requirements | |
| 8 | ||
| 9 | I've recently started playing with large language models (LLMs), mostly in the | |
| 10 | popular chatbot form, as part of my job and have decided to see if there's a | |
| 11 | consistent and reliable way to interact with these models on Apple devices | |
| 12 | without sacrificing privacy or requiring in-depth technical setup. | |
| 13 | ||
| 14 | My requirements for this test: | |
| 15 | ||
| 16 | - Open source platform | |
| 17 | - On-device model files | |
| 18 | - Minimal required configuration | |
| 19 | - Preferably pre-built, but a simple build process is acceptable | |
| 20 | ||
| 21 | I tested a handful of apps and have summarized my favorite (so far) for macOS | |
| 22 | and iOS below. | |
| 23 | ||
| 24 | > TL;DR - Here are the two that met my requirements and I have found the easiest | |
| 25 | > to install and use so far: | |
| 26 | ||
| 27 | - macOS: [Ollama](https://ollama.ai/) | |
| 28 | - iOS : [LLM Farm](https://llmfarm.site/) | |
| 29 | ||
| 30 | ## macOS | |
| 31 | ||
| 32 | [Ollama](https://ollama.ai/) is a simple Go application for macOS and Linux that | |
| 33 | can run various LLMs locally. | |
| 34 | ||
| 35 | For macOS, you can download the pplication on the [Ollama download | |
| 36 | page](https://ollama.ai/download/mac) and install it by unzipping the | |
| 37 | `Ollama.app` file and moving it to the `Applications` folder. | |
| 38 | ||
| 39 | If you prefer the command line, you can run these commands after the download | |
| 40 | finished: | |
| 41 | ||
| 42 | ```sh | |
| 43 | cd ~/Downloads && \ | |
| 44 | unzip Ollama-darwin.zip && \ | |
| 45 | mv ~/Downloads/Ollama.app /Applications/ | |
| 46 | ``` | |
| 47 | ||
| 48 | After running the app, the app will ask you to open a terminal and run the | |
| 49 | default `llama2` model, which will open an interactive chat session in the | |
| 50 | terminal. You can startfully using the application at this point. | |
| 51 | ||
| 52 |  | |
| 53 | ||
| 54 | If you don't want to use the default `llama2` model, you can download and run | |
| 55 | additional models found on the [Models](https://ollama.ai/library) page. | |
| 56 | ||
| 57 | To see the information for the currently-used model, you can run the `/show | |
| 58 | info` command in the chat. | |
| 59 | ||
| 60 |  | |
| 61 | ||
| 62 | ### Community Integrations | |
| 63 | ||
| 64 | I highly recommend browsing the [Community | |
| 65 | Integrations](https://github.com/jmorganca/ollama#community-integrations) | |
| 66 | section of the project to see how you would prefer to extend Ollama beyond a | |
| 67 | simple command-line interface. There are options for APIs, browser UIs, advanced | |
| 68 | terminal configurations, and more. | |
| 69 | ||
| 70 |  | |
| 71 | ||
| 72 | ## iOS | |
| 73 | ||
| 74 | While there are a handful of decent macOS options, it was quite difficult to | |
| 75 | find an iOS app that offered an open source platform without an extensive | |
| 76 | configuration and building process. I found LLM Farm to be decent enough in | |
| 77 | quality to sit at the top of my list - however, it's definitely not user | |
| 78 | friendly enough for me to consider using it on a daily basis. | |
| 79 | ||
| 80 | [LLM Farm](https://llmfarm.site/) is available on TestFlight, so there's no | |
| 81 | manual build process required. However, you can view the [LLMFarm | |
| 82 | repository](https://github.com/guinmoon/LLMFarm) if you wish. | |
| 83 | ||
| 84 | The caveat is that you will have to manually download the model files from the | |
| 85 | links in the | |
| 86 | [models.md](https://github.com/guinmoon/LLMFarm/blob/main/models.md) file to | |
| 87 | your iPhone to use the app - there's currently no option in the app to reach out | |
| 88 | and grab the latest version of any supported model. | |
| 89 | ||
| 90 | Once you have a file downloaded, you simply create a new chat and select the | |
| 91 | downloaded model file and ensure the inference matches the requirement in the | |
| 92 | `models.md` file. | |
| 93 | ||
| 94 | See below for a test of the ORCA Mini v3 model: | |
| 95 | ||
| 96 | | Chat List | Chat | | |
| 97 | |--------------------------------------------------------------------------------------------------------|--------------------------------------------------------------------------------------| | |
| 98 | |  |  | |
| 99 | ||
| 100 | [Enchanted](https://github.com/AugustDev/enchanted) is also an iOS for private | |
| 101 | AI models, but it requires a public-facing Ollama API, which did not meet my | |
| 102 | "on device requirement." Nonetheless, it's an interesting looking app and I will | |
| 103 | likely set it up to test soon. | |
content/blog/2024-01-16-audit-dashboard.md deleted −134
| @@ -1,134 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2024-01-26 | |
| 3 | title = "Building an Audit Status Dashboard" | |
| 4 | description = "Learn how to utilize Alteryx Designer and Power BI Desktop to build a simple status tracking dashboard for an audit or other engagement." | |
| 5 | +++ | |
| 6 | ||
| 7 | Alteryx and Power BI are powerful tools that can help turn your old-school audit trackers into interactive tools that provide useful insights and potential action plans. | |
| 8 | ||
| 9 | With these tools, we are going to build the following dashboard: | |
| 10 | ||
| 11 | 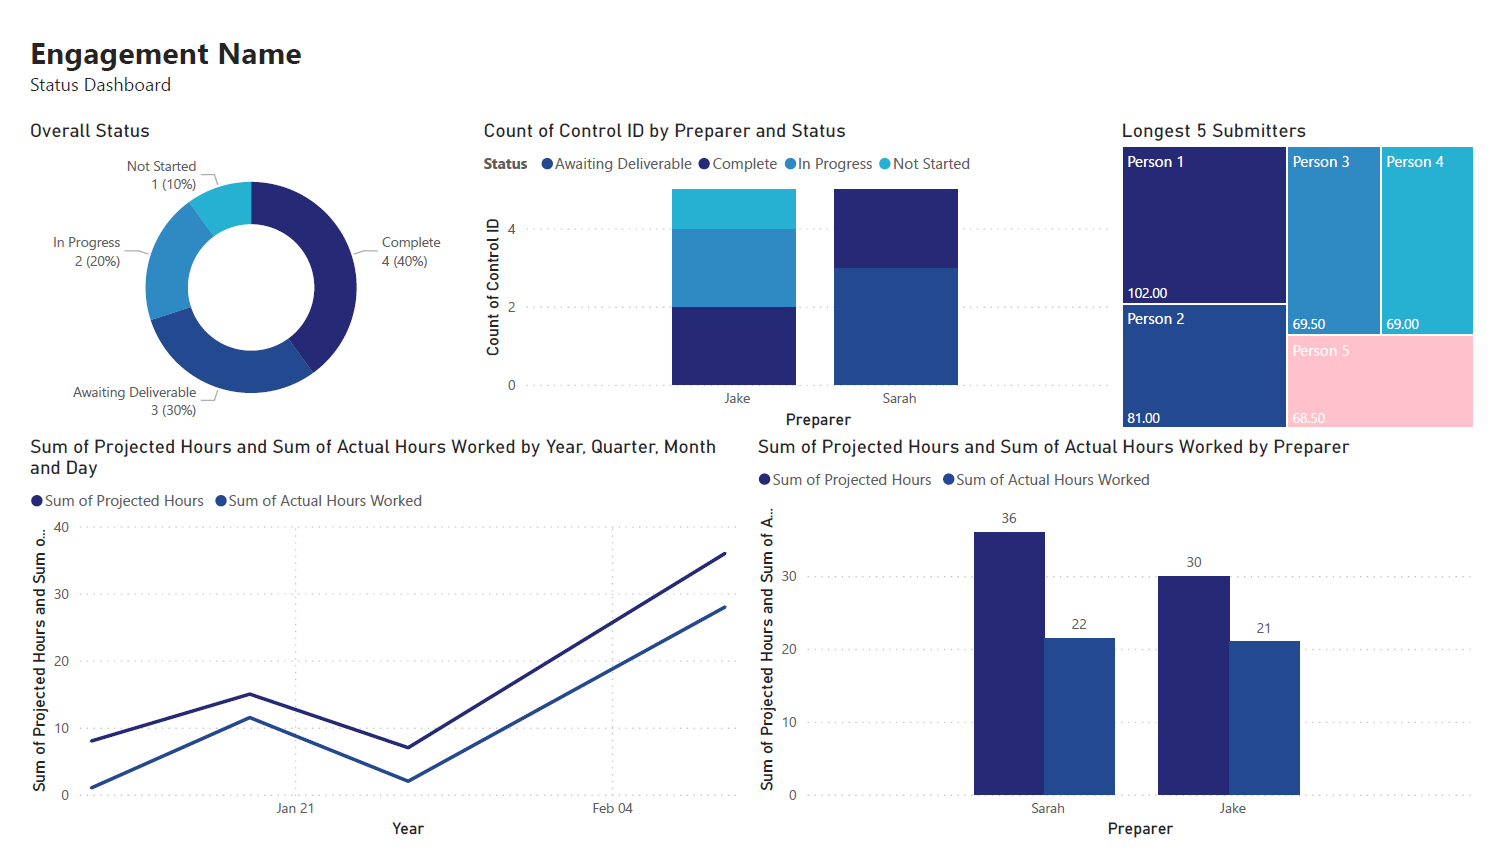 | |
| 12 | 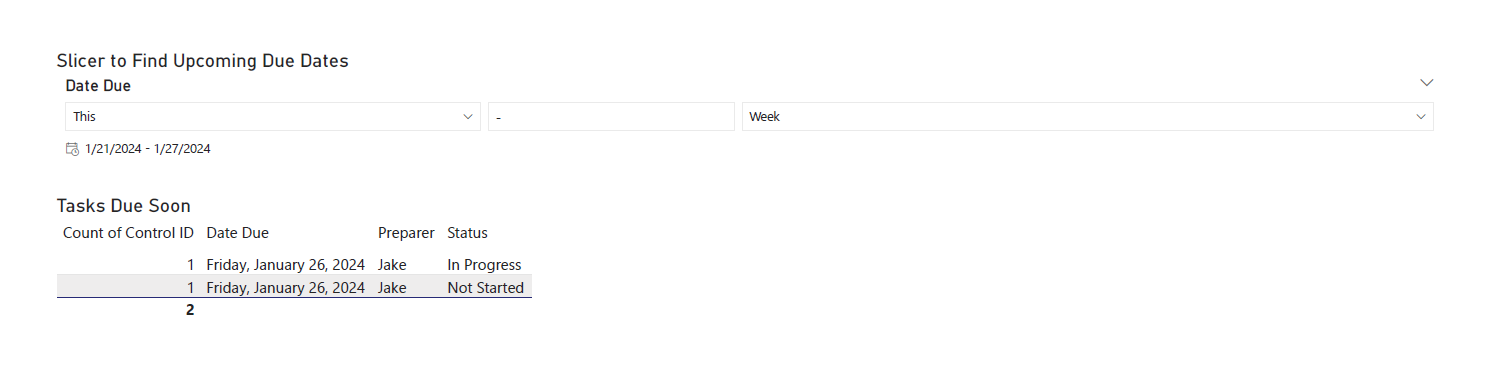 | |
| 13 | ||
| 14 | ## Requirements | |
| 15 | ||
| 16 | This project assumes the following: | |
| 17 | ||
| 18 | - You have access to Alteryx Designer and Power BI Desktop. | |
| 19 | - If you only have Power BI Desktop, you may need to perform some analysis in Power BI instead of Alteryx. | |
| 20 | - Your data is in a format that can be imported into Alteryx and/or Power BI. | |
| 21 | - You have a basic understanding of data types and visualization. | |
| 22 | ||
| 23 | ## Alteryx: Data Preparation & Analysis | |
| 24 | ||
| 25 | ### Import Data | |
| 26 | ||
| 27 | With Alteryx, importing data is easy with the use of the `Input Data` tool. Simply drag this tool onto the canvas from the `In/Out` tab in the Ribbon to create it as a node. | |
| 28 | ||
| 29 | You can choose the File Format manually or simply connect to your file/database and let Alteryx determine the format for you. For this example, we will be importing an Excel file and changing the `Start Data Import on Line` variable to `2`. | |
| 30 | ||
| 31 |  | |
| 32 | ||
| 33 | ### Transform Data | |
| 34 | ||
| 35 | Next, let's replace null data and remove whitespace to clean up our data. We can do this with the `Data Cleansing` tool in the `Preparation` tab in the Ribbon. | |
| 36 | ||
| 37 | Ensure that the following options are enabled: | |
| 38 | ||
| 39 | - Replace Nulls | |
| 40 | - Replace with Blanks (String Fields) | |
| 41 | - Replace with 0 (Numeric Fields) | |
| 42 | - Remove Unwanted Characters | |
| 43 | - Leading and Trailing Whitespace | |
| 44 | ||
| 45 | 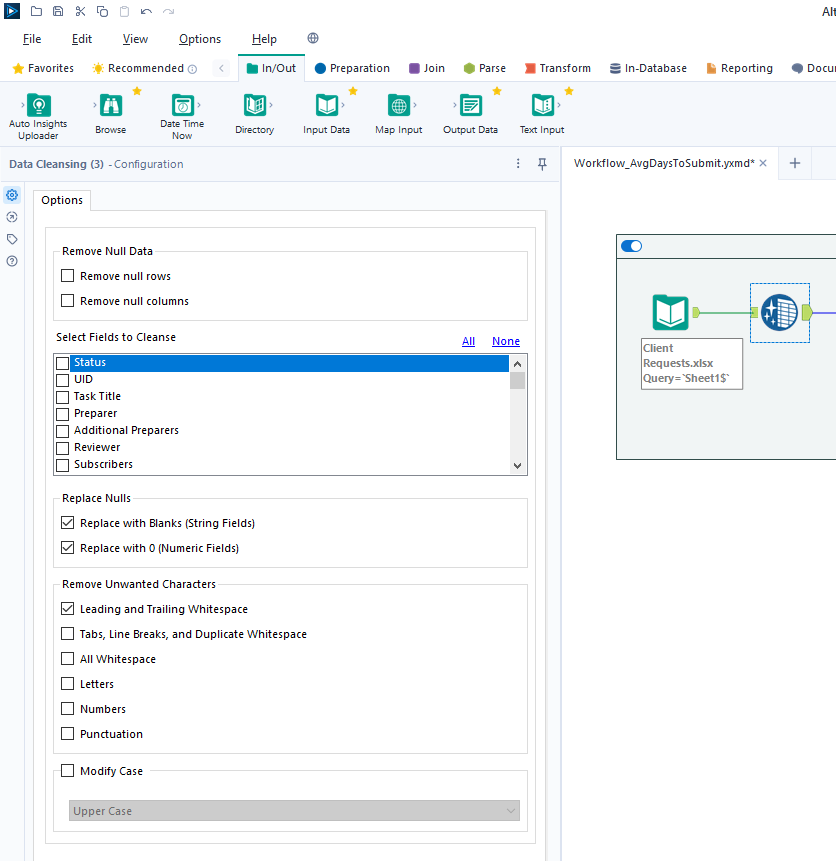 | |
| 46 | ||
| 47 | For our next step, we will transform the date fields from strings to datetime format. Add a `Datetime` tool for each field you want to transform - in the example below, I am using the tool twice for the "Started On" and "Submitted On" fields. | |
| 48 | ||
| 49 | 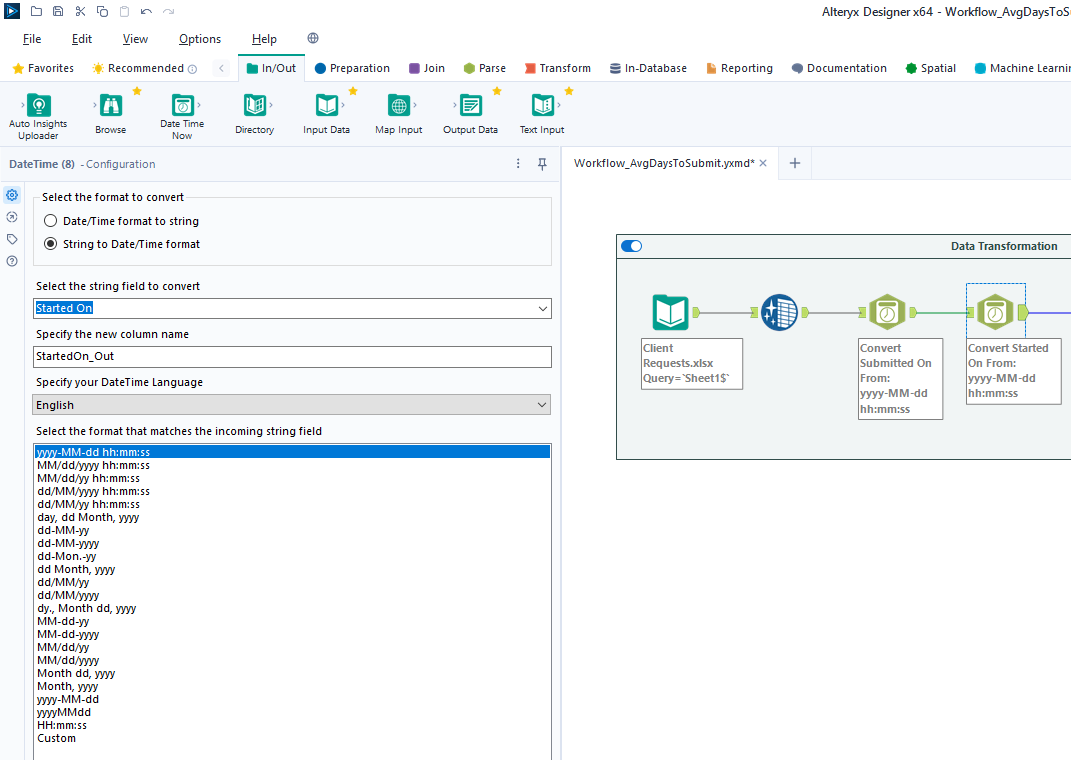 | |
| 50 | ||
| 51 | Now that the dates are in the correct format, let's perform a calculation based on those fields. Start by adding a `Filter` tool, naming a new Output Column, and pasting the formula below into it (the two fields used in this formula must match the output of the `Datetime` tools above): | |
| 52 | ||
| 53 | ```txt | |
| 54 | DateTimeDiff([SubmittedOn_Out],[StartedOn_Out], "days") | |
| 55 | ``` | |
| 56 | ||
| 57 | 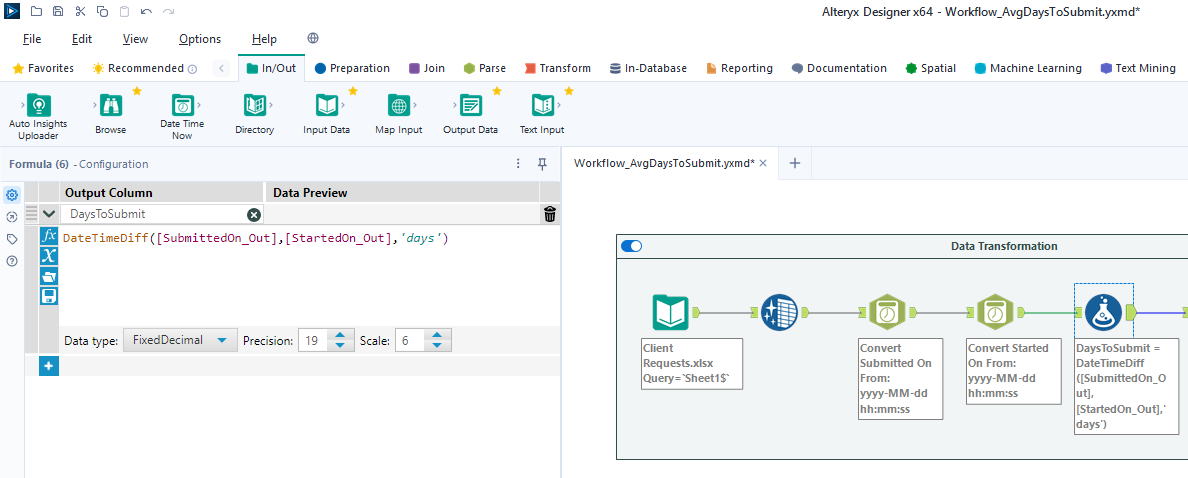 | |
| 58 | ||
| 59 | ### Export Data | |
| 60 | ||
| 61 | Finalize the process by exporting the transformed data set to a new file, for use in the following visualization step. | |
| 62 | ||
| 63 | 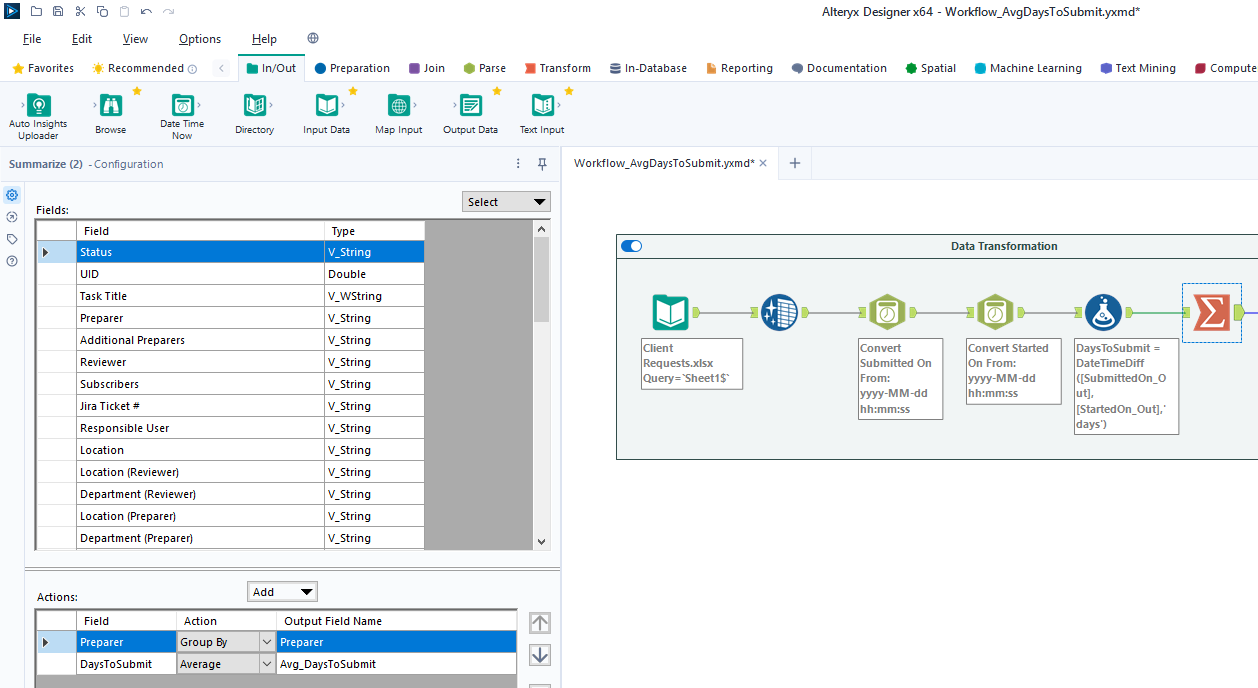 | |
| 64 | ||
| 65 | ## Power BI: Data Visualization | |
| 66 | ||
| 67 | ### Import Data | |
| 68 | ||
| 69 | To start, open the Power BI Desktop application. Upon first use, Power BI will ask if you want to open an existing dashboard or import new data. | |
| 70 | ||
| 71 | As we are creating our first dashboard, let's import our data. In my example below, I'm importing data from the "Tracker" sheet of the Excel file I'm using for this project. | |
| 72 | ||
| 73 | During this process, I also imported the export from the Alteryx workflow above. Therefore, we have two different files available for use in our dashboard. | |
| 74 | ||
| 75 | 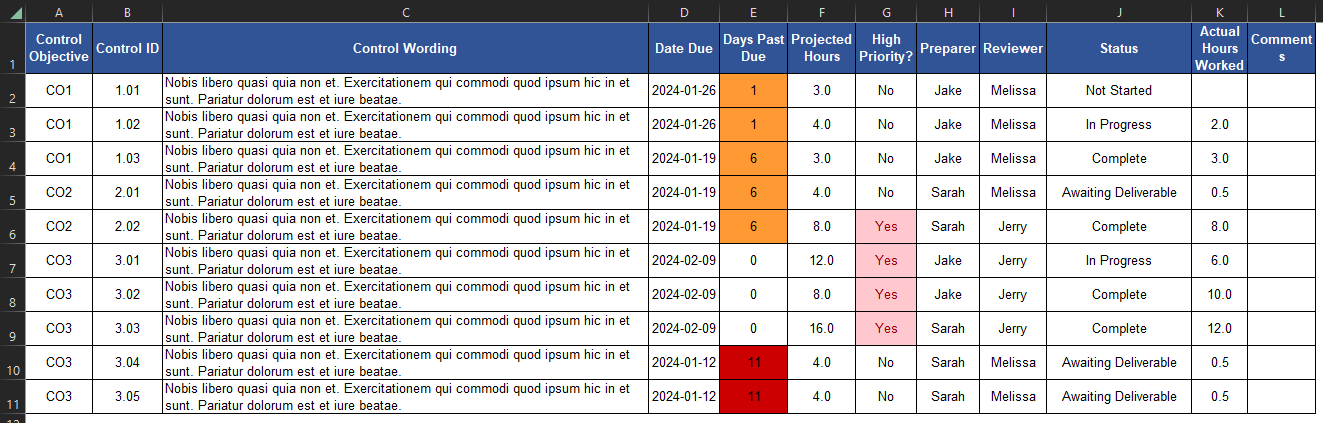 | |
| 76 | ||
| 77 | 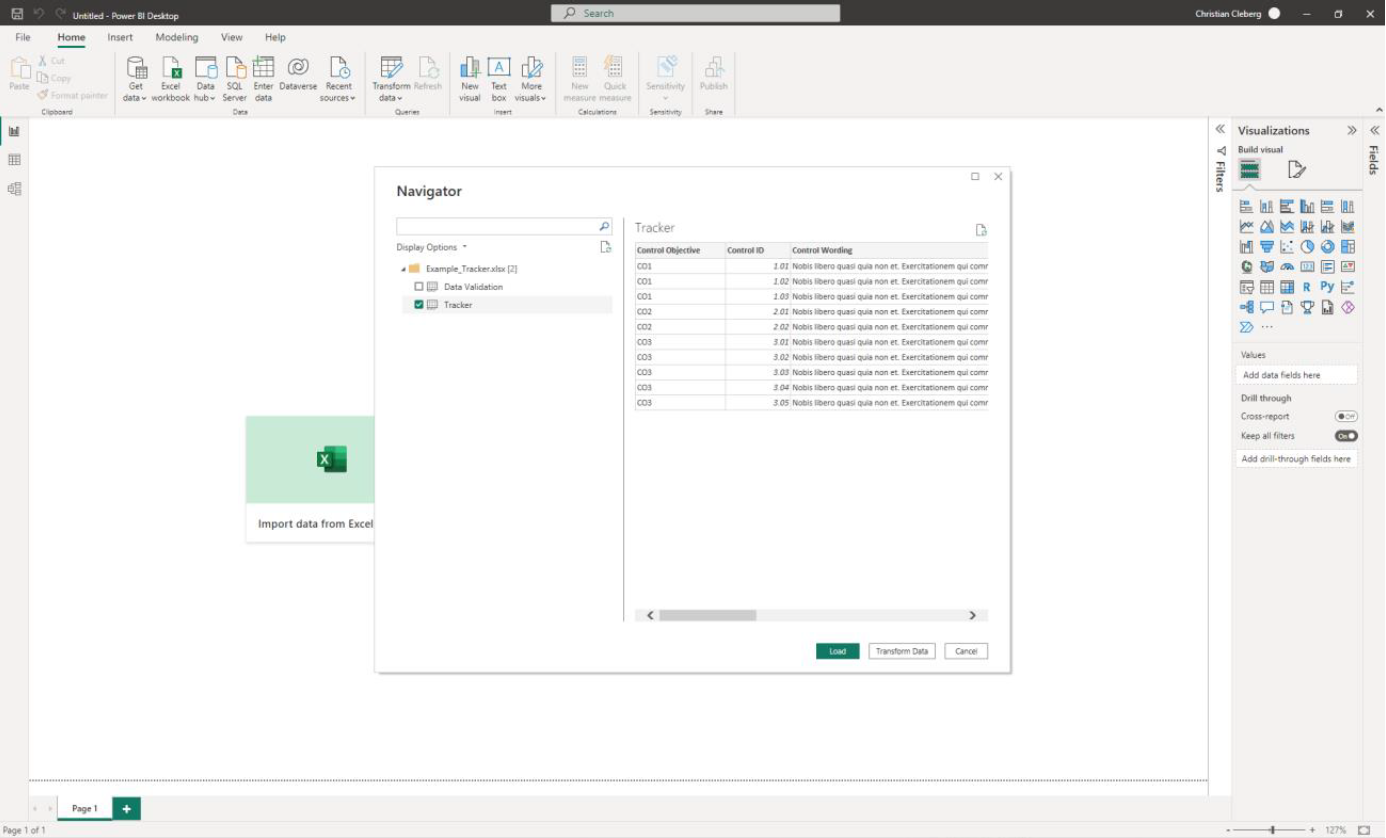 | |
| 78 | ||
| 79 | ### Add Visuals | |
| 80 | ||
| 81 | To create the dashboard below, you will need to follow the list instructions below and format as needed: | |
| 82 | ||
| 83 |  | |
| 84 |  | |
| 85 | ||
| 86 | Instructions to create the visuals above: | |
| 87 | ||
| 88 | - `Text Box`: Explain the name and purpose of the dashboard. You can also add images and logos at the top of the dashboard. | |
| 89 | - `Donut Chart`: Overall status of the project. | |
| 90 | - `Legend`: Status | |
| 91 | - `Values`: Count of Status | |
| 92 | - `Stacked Column Chart`: Task count by assignee. | |
| 93 | - `X-axis`: Preparer | |
| 94 | - `Y-axis`: Count of Control ID | |
| 95 | - `Legend`: Status | |
| 96 | - `Treemap`: Top N client submitters by average days to submit. | |
| 97 | - `Details`: Preparer | |
| 98 | - `Values`: Sum of Avg_DaysToSubmit | |
| 99 | - `Line Chart`: Projected vs. actual hours over time. | |
| 100 | - `Clustered Bar Chart`: Projected vs. actual hours per person. | |
| 101 | - `Slicer & Table` - Upcoming due dates. | |
| 102 | - `Slicer`: | |
| 103 | - `Values`: Date Due | |
| 104 | - `Table`: | |
| 105 | - `Columns`: Count of Control ID, Date Due, Preparer, Status | |
| 106 | ||
| 107 | ### Format the Dashboard | |
| 108 | ||
| 109 | You can choose a theme in the View tab of the Ribbon. You can even browse for custom JSON files that define themes, such as ones found online or custom ones created by your organization. | |
| 110 | ||
| 111 | For each visual, you can click the `Format` button in the `Visualizations` side pane and explore the options. You can custom options such as: | |
| 112 | ||
| 113 | - Visual | |
| 114 | - Legend | |
| 115 | - Colors | |
| 116 | - Data labels | |
| 117 | - Category labels | |
| 118 | - General | |
| 119 | - Properties | |
| 120 | - Title | |
| 121 | - Effects | |
| 122 | - Header icons | |
| 123 | - Tooltips | |
| 124 | - Alt text | |
| 125 | ||
| 126 | You can always look online for inspiration when trying to decide how best to organize and style your dashboard. | |
| 127 | ||
| 128 | ## Sharing the Results | |
| 129 | ||
| 130 | Generally, you have a few different options for sharing your dashboards with others: | |
| 131 | ||
| 132 | 1. Export the dashboard as a PDF in the file menu of Power BI. This will export all tabs and visuals as they are set when the export button is pressed. You will lose all interactivity with this option. | |
| 133 | 2. Send the full Power BI file to those you wish to share the dashboard. This will retain all settings and interactivity. However, you will also need to send the source files if they need to refresh the dashboard and you will need to re-send the files if you make updates. | |
| 134 | 3. Store the dashboard in a synced location, such as a shared drive or Microsoft Teams. Depending on how a user configures their local Windows paths, the data source paths may not be compatible for all users with such a setup. | |
content/blog/2024-01-27-tableau-dashboard.md deleted −122
| @@ -1,122 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2024-01-27 | |
| 3 | title = "Data Visualization: Mapping Omaha Crime Data with Tableau" | |
| 4 | description = "Learn how to utilize Tableau Public to build a dashboard to map crimes across Omaha." | |
| 5 | +++ | |
| 6 | ||
| 7 | In this project, I am going to show you how to use Tableau Public for free to create simple dashboards. | |
| 8 | ||
| 9 | I will be creating simple visuals from an Omaha crime data set and combining them to create the dashboard below. You can view this dashboard interactively online here: [Omaha Crime Data (2015 - 2023)](https://public.tableau.com/app/profile/c.c7042/viz/OmahaCrimeData2015-2023/OmahaCrimeData2015-2023#1). | |
| 10 | ||
| 11 |  | |
| 12 | ||
| 13 | ## Gather the Data | |
| 14 | ||
| 15 | You can download incident data from the Omaha Police Department on their [Incident Data Download](https://police.cityofomaha.org/crime-information/incident-data-download) page. They currently have files for the years 2015 through 2023. | |
| 16 | ||
| 17 | Each file will be downloaded as a CSV file, approximately 3 MB - 8 MB. | |
| 18 | ||
| 19 | ## Clean and Transform the Data | |
| 20 | ||
| 21 | I have used Python to combine the files into a single CSV file, as well as adding a custom `datetime` column. You could do this step in any software you prefer, but I prefer Python as its free, easy to use, and has a plethora of support resources online. | |
| 22 | ||
| 23 | Start by opening a terminal, navigating to your Downloads directory, and creating a python script. | |
| 24 | ||
| 25 | ```sh | |
| 26 | cd ~/Downloads | |
| 27 | nano data_processing.py | |
| 28 | ``` | |
| 29 | ||
| 30 | Within the Python script, paste the following: | |
| 31 | ||
| 32 | ```python | |
| 33 | # Import modules | |
| 34 | import pandas as pd | |
| 35 | import glob | |
| 36 | import os | |
| 37 | ||
| 38 | # Import the data | |
| 39 | path = r"~/Downloads/*.csv" | |
| 40 | files = glob.glob(path) | |
| 41 | ||
| 42 | list = [] | |
| 43 | ||
| 44 | for file in files: | |
| 45 | df_tmp = pd.read_csv(file) | |
| 46 | li.append(df_tmp) | |
| 47 | ||
| 48 | df = pd.concat(list, axis=0, ignore_index=True) | |
| 49 | ||
| 50 | # Create a combined datetime column | |
| 51 | df["datetime"] = pd.to_datetime( | |
| 52 | df["date"] + " " + df["time"], | |
| 53 | format="%m/%d/%Y %H:%M:%S" | |
| 54 | ) | |
| 55 | df.head() | |
| 56 | ||
| 57 | # Export the combined data | |
| 58 | df.to_csv(r"~/Downloads/combined_incidents.csv") | |
| 59 | ``` | |
| 60 | ||
| 61 | Once pasted, save and close the file. You can execute the file like so: | |
| 62 | ||
| 63 | ```sh | |
| 64 | python3 data_processing.py | |
| 65 | ``` | |
| 66 | ||
| 67 | After this, you should have a combined data file that contains all incidents between 2015 and 2023. Mine was approximately 55 MB. | |
| 68 | ||
| 69 | ## Tableau Public | |
| 70 | ||
| 71 | [Tableau Public](https://public.tableau.com/) is a free-to-use web application that allows you to create visualizations by uploading data sources. Note that there's no way to keep the data and visualizations private, so don't upload anything private. | |
| 72 | ||
| 73 | After creating an account, you can click the `Create` > `Web Authoring` link to create your first visualization. | |
| 74 | ||
| 75 |  | |
| 76 | ||
| 77 | ### Upload the Data | |
| 78 | ||
| 79 | Once you've opened your first project, Tableau will ask you to connect to your data. For this project, click the `Upload from computer` button and select the CSV file previously combined in the step above. | |
| 80 | ||
| 81 |  | |
| 82 | ||
| 83 | Once connected, you can refresh the preview of the data with the `Refresh Data Source` button in the toolbar. | |
| 84 | ||
| 85 |  | |
| 86 | ||
| 87 | If you need to edit any of the data types, column names, etc., you can do so now. Once complete, generate an extract so that you can start creating visualizations. | |
| 88 | ||
| 89 | ### Create Visualizations | |
| 90 | ||
| 91 | To start, create a worksheet in the toolbar at the bottom of the screen. | |
| 92 | ||
| 93 | Within this screen, select a column from the `Data` side bar on the left and drag it into the `Columns` or `Rows` area of the canvas. | |
| 94 | ||
| 95 | See below for the map visualization. You can recreate this by adding the following fields: | |
| 96 | ||
| 97 | - `Columns`: Lon | |
| 98 | - `Rows`: Lat | |
| 99 | - `Marks`: | |
| 100 | - Description | |
| 101 | - Datetime | |
| 102 | - `Filters`: Datetime | |
| 103 | ||
| 104 |  | |
| 105 | ||
| 106 | You can repeat this process for each visualization you want to create. Explore your options by dragging data fields to different areas and by opening the field options to explore what operations can be performed on different data types (e.g., average, count, etc.). | |
| 107 | ||
| 108 | ### Create Dashboard | |
| 109 | ||
| 110 | To create a dashboard, click the button on the toolbar at the bottom of the screen. Within the dashboard, drag each sheet from the left side bar onto the dashboard canvas. | |
| 111 | ||
| 112 |  | |
| 113 | ||
| 114 | ### Formatting | |
| 115 | ||
| 116 | You can explore a ton of different formatting options throughout the worksheets and dashboard. Specifically for maps, you can alter the map layers, background, and visible features through the `Map` menu in the top file menu of the editing screen. | |
| 117 | ||
| 118 | In the finished dashboard below, I opted for a dark mode with a map that showed county lines and city names. | |
| 119 | ||
| 120 | There's a ton of other options available to be used in a dashboard like this, but this project shows a quick preview of what you can do in Tableau Public. | |
| 121 | ||
| 122 |  | |
content/blog/2024-02-13-ubuntu-emergency-mode.md deleted −71
| @@ -1,71 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2024-02-13 | |
| 3 | title = "Stuck in Ubuntu's Emergency Mode? Try Fixing the Fstab File" | |
| 4 | description = "Learn how to fix a missing disk issue that can lock you in Ubuntu's emergency mode." | |
| 5 | +++ | |
| 6 | ||
| 7 | ### The Problem | |
| 8 | ||
| 9 | I recently [migrated my hard drives to a ZFS pool](/blog/zfs/) and found myself | |
| 10 | stuck in Ubuntu's emergency mode after the first reboot I performed after | |
| 11 | creating the ZFS pool. | |
| 12 | ||
| 13 | My server was stuck in the boot process and showed the following error on the | |
| 14 | screen: | |
| 15 | ||
| 16 | ```txt | |
| 17 | You are in emergency mode. | |
| 18 | After logging in, type "journalctl -xb" to view system logs, | |
| 19 | "systemctl reboot" to reboot, "systemctl default" | |
| 20 | or ^D to try again to boot into default mode". | |
| 21 | ``` | |
| 22 | ||
| 23 | After rebooting the server and watching the logs scroll on a monitor, I noticed | |
| 24 | the root cause was related to a very long search for certain drives. I kept | |
| 25 | seeing errors like this: | |
| 26 | ||
| 27 | ```txt | |
| 28 | [ TIME ] Timed out waiting of device dev-disk-by/[disk-uuid] | |
| 29 | ``` | |
| 30 | ||
| 31 | I realized that I had not removed the `/etc/fstab` references that asked Ubuntu | |
| 32 | to mount two disks on boot, but I had recently changed those disks to be part of | |
| 33 | my ZFS pool instead. Therefore, Ubuntu was trying to identify and mount a disk | |
| 34 | that was not available. | |
| 35 | ||
| 36 | Now that we have an idea of the issue, let's move to solution. | |
| 37 | ||
| 38 | ### The Solution | |
| 39 | ||
| 40 | In order to fix the issue, I waited until I was allowed to type the root user's | |
| 41 | password, and then I executed the following command: | |
| 42 | ||
| 43 | ```sh | |
| 44 | nano /etc/fstab | |
| 45 | ``` | |
| 46 | ||
| 47 | Within the `fstab` file, I needed to comment/remove the following lines at the | |
| 48 | bottom of the file. You can comment-out a line by prepending a `#` symbol at the | |
| 49 | beginning of the line. You can also delete the line entirely. | |
| 50 | ||
| 51 | ```conf | |
| 52 | # What it looked like when running into the issue: | |
| 53 | UUID=B64E53824E5339F7 /mnt/white-01 ntfs-3g uid=1000,gid=1000 0 0 | |
| 54 | UUID=E69867E59867B32B /mnt/white-02 ntfs-3g uid=1000,gid=1000 0 0 | |
| 55 | ||
| 56 | # What I changed it to, in order to fix the issue: | |
| 57 | # UUID=B64E53824E5339F7 /mnt/white-01 ntfs-3g uid=1000,gid=1000 0 0 | |
| 58 | # UUID=E69867E59867B32B /mnt/white-02 ntfs-3g uid=1000,gid=1000 0 0 | |
| 59 | ``` | |
| 60 | ||
| 61 | Once removing the lines above from the `/etc/fstab` file, save and exit the file | |
| 62 | by hitting the `Ctrl` + `x` key combo. | |
| 63 | ||
| 64 | You can now hit `Ctrl` + `D` to continue, or reboot: | |
| 65 | ||
| 66 | ```sh | |
| 67 | systemctl reboot | |
| 68 | ``` | |
| 69 | ||
| 70 | Once rebooted, I was able to watch the machine boot properly and launch to the | |
| 71 | TTY login screen without errors! | |
content/blog/2024-02-21-self-hosting-otter-wiki.md deleted −135
| @@ -1,135 +0,0 @@ | ||
| 1 | +++ | |
| 2 | date = 2024-02-21 | |
| 3 | title = "Self-Hosting An Otter Wiki" | |
| 4 | description = "Learn how to easily self-host An Otter Wiki." | |
| 5 | +++ | |
| 6 | ||
| 7 | ## An Otter Wiki | |
| 8 | ||
| 9 | [An Otter Wiki](https://otterwiki.com/) is an easy to use wiki software that | |
| 10 | takes almost no effort to set up and maintain. | |
| 11 | ||
| 12 | ## Installation | |
| 13 | ||
| 14 | To install An Otter Wiki, I'm going to use Docker Compose to create the | |
| 15 | container and then use Nginx as a reverse proxy to allow external access via a | |
| 16 | subdomain I own. | |
| 17 | ||
| 18 | ### Docker Compose | |
| 19 | ||
| 20 | Start by creating a directory for the container's files. | |
| 21 | ||
| 22 | ```sh | |
| 23 | mkdir ~/otterwiki | |
| 24 | ``` | |
| 25 | ||
| 26 | Next, create the `docker-compose.yml` file to define the container's parameters. | |
| 27 | ||
| 28 | ```sh | |
| 29 | nano ~/otterwiki/docker-compose.yml | |
| 30 | ``` | |
| 31 | ||
| 32 | Within the file, paste the following content. You can read the project's | |
| 33 | documentation if you want to further override or customize the container. | |
| 34 | ||
| 35 | ```conf | |
| 36 | version: '3' | |
| 37 | services: | |
| 38 | otterwiki: | |
| 39 | image: redimp/otterwiki:2 | |
| 40 | restart: unless-stopped | |
| 41 | # Internal port must be assigned to port 80 | |
| 42 | # External port can be customized | |
| 43 | ports: | |
| 44 | - 8337:80 | |
| 45 | volumes: | |
| 46 | - ./app-data:/app-data | |
| 47 | ``` | |
| 48 | ||
| 49 | Once the file is saved and closed, you can launch the container. | |
| 50 | ||
| 51 | ```sh | |
| 52 | cd ~/otterwiki | |
| 53 | sudo docker-compose up -d | |
| 54 | ``` | |
| 55 | ||
| 56 | The container is now available at `localhost:8337`. Next, we will use Nginx to | |
| 57 | serve this app externally. | |
| 58 | ||
| 59 | ### Nginx | |
| 60 | ||
| 61 | To access the app externally, let's set up a reverse proxy. I'll start by | |
| 62 | creating the Nginx configuration file for my wiki. | |
| 63 | ||
| 64 | ```sh | |
| 65 | sudo nano /etc/nginx/sites-available/wiki | |
| 66 | ``` | |
| 67 | ||
| 68 | Within the file, I have saved the following content. This assumes you already | |
| 69 | have a TLS/SSL cert to use with this subdomain. If not, simply remove the | |
| 70 | `ssl_*` variables, remove the `80` server block, and change the `443` | |
| 71 | server block to `80` to serve the app without SSL. | |
| 72 | ||
| 73 | ```conf | |
| 74 | server { | |
| 75 | if ($host ~ ^[^.]+\.example\.com$) { | |
| 76 | return 301 https://$host$request_uri; | |
| 77 | } | |
| 78 | ||
| 79 | listen [::]:80; | |
| 80 | listen 80; | |
| 81 | server_name wiki.example.com; | |
| 82 | return 404; | |
| 83 | } | |
| 84 | ||
| 85 | server { | |
| 86 | listen [::]:443 ssl http2; | |
| 87 | listen 443 ssl http2; | |
| 88 | server_name wiki.example.com; | |
| 89 | access_log /var/log/nginx/wiki.access.log; | |
| 90 | error_log /var/log/nginx/wiki.error.log; | |
| 91 | ||
| 92 | ssl_certificate /etc/letsencrypt/live/example.com/fullchain.pem; | |
| 93 | ssl_certificate_key /etc/letsencrypt/live/example.com/privkey.pem; | |
| 94 | include /etc/letsencrypt/options-ssl-nginx.conf; | |
| 95 | ssl_dhparam /etc/letsencrypt/ssl-dhparams.pem; | |
| 96 | ||
| 97 | location / { | |
| 98 | set $upstream_wiki http://127.0.0.1:8337; | |
| 99 | proxy_pass $upstream_wiki; | |
| 100 | ||
| 101 | proxy_set_header Host $http_host; | |
| 102 | proxy_set_header X-Real-IP $remote_addr; | |
| 103 | proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for; | |
| 104 | proxy_set_header X-Forwarded-Host $http_host; | |
| 105 | } | |
| 106 | } | |
| 107 | ``` | |
| 108 | ||
| 109 | Save and close the configuration file. On Nginx, we need to symlink the file to | |
| 110 | enable it. | |
| 111 | ||
| 112 | ```sh | |
| 113 | sudo ln -s /etc/nginx/sites-available/wiki /etc/nginx/sites-enabled/wiki | |
| 114 | ``` | |
| 115 | ||
| 116 | Once enabled, restart the Nginx server to start serving the app externally. | |
| 117 | ||
| 118 | ```sh | |
| 119 | sudo systemctl restart nginx.service | |
| 120 | ``` | |
| 121 | ||
| 122 | ## Screenshots | |
| 123 | ||
| 124 | In the screenshot below, you can see the initial launch screen for An Otter | |
| 125 | Wiki. Start by creating your admin account and configure the app as necessary. | |
| 126 | ||
| 127 |  | |
| 128 | ||
| 129 | You can also see the default editing screen for creating and editing pages. It's | |
| 130 | as easy as typing Markdown and hitting the save button. | |
| 131 | ||
| 132 |  | |
| 133 | ||
| 134 | Overall, I like An Otter Wiki and will be looking forward to seeing how much use | |
| 135 | I get out of it going forward. | |
content/blog/_index.md deleted −4
| @@ -1,4 +0,0 @@ | ||
| 1 | +++ | |
| 2 | title = "Blog" | |
| 3 | sort_by = "date" | |
| 4 | +++ | |
| \ No newline at end of file | ||
content/salary/index.md deleted −54
| @@ -1,54 +0,0 @@ | ||
| 1 | +++ | |
| 2 | title = "Salary" | |
| 3 | description = "A summary of my salaries throughout my career." | |
| 4 | +++ | |
| 5 | ||
| 6 | ## Salary Transparency | |
| 7 | ||
| 8 | The data below details the base salary information for each job I've | |
| 9 | held. This information is posted publicly to ensure others in my | |
| 10 | position have a solid reference point when determining if their current | |
| 11 | or proposed salary is appropriate. | |
| 12 | ||
| 13 | While sites like Glassdoor are locking salary data behind a paywall, | |
| 14 | LinkedIn is discontinuing LinkedIn Salary, and helpful websites like Big | |
| 15 | 4 Transparency are extremely rare, I wanted to provide my personal data | |
| 16 | publicly and freely to those who need it. | |
| 17 | ||
| 18 | I have seen what can happen when great employees don't know the market | |
| 19 | values for their skills and I happily help those in my teams, so I'm | |
| 20 | happy to extend this information to the online community. | |
| 21 | ||
| 22 | As a final note, there are numerous reasons that people in the same role | |
| 23 | are paid differently (expertise, years of experience, certifications, | |
| 24 | education, etc.) and that the data in this table should only be used as | |
| 25 | a single point of reference, not the whole story. | |
| 26 | ||
| 27 | ## Salary Data | |
| 28 | ||
| 29 | Note: When in a role that gives periodic raises, I will create a new | |
| 30 | record with the new base salary in the table below. See the KPMG records | |
| 31 | for an example of a raise while in the same role. | |
| 32 | ||
| 33 | | Title | Company | Location | Start | End | Salary | | |
| 34 | |------------------------------------------------|------------------------|----------------|:-------:|:-------:|----------| | |
| 35 | | Senior Associate, Technology Assurance - Audit | KPMG | Omaha, NE | 2023-10 | Current | $116,700 | | |
| 36 | | Senior Associate, Technology Assurance - Audit | KPMG | Omaha, NE | 2022-06 | 2023-10 | $110,000 | | |
| 37 | | Senior Technology Risk Consultant | Ernst & Young | Des Moines, IA | 2021-09 | 2022-06 | $89,500 | | |
| 38 | | Senior IT Auditor | Ameritas | Lincoln, NE | 2021-05 | 2021-09 | $72,000 | | |
| 39 | | IT Auditor | Ameritas | Lincoln, NE | 2020-04 | 2021-05 | $65,000 | | |
| 40 | | IS Auditor II | Nelnet | Lincoln, NE | 2019-12 | 2020-04 | $58,000 | | |
| 41 | | IS Auditor I | Nelnet | Lincoln, NE | 2019-06 | 2019-12 | $20/hour | | |
| 42 | | Internal Audit Intern | Ameritas | Lincoln, NE | 2018-02 | 2019-06 | $16/hour | | |
| 43 | | Teaching Assistant | University of Nebraska | Lincoln, NE | 2017-08 | 2018-05 | $7/hour | | |
| 44 | | Community Management Intern | Walgreens | Lincoln, NE | 2017-06 | 2018-02 | $14/hour | | |
| 45 | ||
| 46 | This page was inspired by [Xe](https://xeiaso.net/), and I'm quoting | |
| 47 | the following wording from them as I want to reiterate this piece: | |
| 48 | ||
| 49 | > Please consider publishing your salary data like this as well. By | |
| 50 | > open, voluntary transparency we can help to end stigmas around | |
| 51 | > discussing pay and help ensure that the next generations of people in | |
| 52 | > tech are treated fairly. Stigmas thrive in darkness but die in the | |
| 53 | > light of day. You can help end the stigma by playing your cards out in | |
| 54 | > the open like this. | |
content/services/index.md deleted −18
| @@ -1,18 +0,0 @@ | ||
| 1 | +++ | |
| 2 | title = "Services" | |
| 3 | description = "Publicly-available services hosted on cleberg.net." | |
| 4 | +++ | |
| 5 | ||
| 6 | - [AnonymousOverflow](https://ao.cleberg.net) - A StackOverflow proxy | |
| 7 | - [CyberChef](https://cyberchef.cleberg.net) - The Cyber Swiss Army Knife | |
| 8 | - [FileArchive](https://files.cleberg.net) - An interesting file archive | |
| 9 | - [FlashPaper](https://paste.cleberg.net) - One-time encrypted password/secret sharing | |
| 10 | - [GotHub](https://gh.cleberg.net) - An alternative front-end for GitHub | |
| 11 | - [ifconfig.php](https://ip.cleberg.net) - A \"whatsmyip\" tool | |
| 12 | - [Invidious](https://invidious.cleberg.net) - A YouTube proxy | |
| 13 | - [Office](https://office.cleberg.net) - The world\'s smallest office suite | |
| 14 | - [SearXNG](https://search.cleberg.net) - A privacy-respecting, open metasearch engine | |
| 15 | ||
| 16 | See the [git | |
| 17 | log](https://git.cleberg.net/cleberg.net.git/log) | |
| 18 | if you want to see changes that have been made. | |
index.org added +28
| @@ -0,0 +1,28 @@ | ||
| 1 | #+title: cleberg.net | |
| 2 | #+options: toc:nil | |
| 3 | #+options: \n:t | |
| 4 | ||
| 5 | #+begin_quote | |
| 6 | Do AIs dream in electric sheep? | |
| 7 | He hoped it had nanosecond nightmares. | |
| 8 | #+end_quote | |
| 9 | ||
| 10 | * Recent Blog Posts | |
| 11 | ||
| 12 | - 2024-02-21 [[./blog/self-hosting-otter-wiki/][Self-Hosting An Otter Wiki]] | |
| 13 | - 2024-02-13 [[./blog/ubuntu-emergency-mode/][Stuck in Ubuntu's Emergency Mode? Try Fixing the Fstab File]] | |
| 14 | - 2024-02-06 [[./blog/zfs/][How to Create a ZFS Pool on Ubuntu Linux]] | |
| 15 | ||
| 16 | [[./blog/][All Posts →]] | |
| 17 | ||
| 18 | * Everything Else | |
| 19 | ||
| 20 | - [[./salary/][Salary]] | |
| 21 | - [[./services/][Services]] | |
| 22 | - [[./wiki/][Wiki]] | |
| 23 | ||
| 24 | * Contact | |
| 25 | ||
| 26 | - hello [at] cleberg.net ([[./gpg.txt][GPG]]) | |
| 27 | - [[https://matrix.to/#/@cyborg:matrix.tchncs.de][@cyborg:@matrix.tchncs.de]] | |
| 28 | - [[https://git.cleberg.net/cleberg.net.git][Git]] | |
salary/index.org added +50
| @@ -0,0 +1,50 @@ | ||
| 1 | #+title: Salary | |
| 2 | #+description: A historical log of my jobs and salaries. | |
| 3 | ||
| 4 | * Salary Transparency | |
| 5 | ||
| 6 | The data below details the base salary information for each job I've held. This | |
| 7 | information is posted publicly to ensure others in my position have a solid | |
| 8 | reference point when determining if their current or proposed salary is | |
| 9 | appropriate. | |
| 10 | ||
| 11 | While sites like Glassdoor are locking salary data behind a paywall, LinkedIn is | |
| 12 | discontinuing LinkedIn Salary, and helpful websites like Big 4 Transparency are | |
| 13 | extremely rare, I wanted to provide my personal data publicly and freely to | |
| 14 | those who need it. | |
| 15 | ||
| 16 | I have seen what can happen when great employees don't know the market values | |
| 17 | for their skills and I happily help those in my teams, so I'm happy to extend | |
| 18 | this information to the online community. | |
| 19 | ||
| 20 | As a final note, there are numerous reasons that people in the same role are | |
| 21 | paid differently (expertise, years of experience, certifications, education, | |
| 22 | etc.) and that the data in this table should only be used as a single point of | |
| 23 | reference, not the whole story. | |
| 24 | ||
| 25 | * Salary Data | |
| 26 | ||
| 27 | Note: When in a role that gives periodic raises, I will create a new record with | |
| 28 | the new base salary in the table below. See the KPMG records for an example of a | |
| 29 | raise while in the same role. | |
| 30 | ||
| 31 | | Title | Company | Location | Start | End | Salary | | |
| 32 | |------------------------------------------------+------------------------+----------------+---------+---------+----------| | |
| 33 | | Senior IT & Security Auditor | Gemini | Remote | 2024-03 | Current | $122,000 | | |
| 34 | | Senior Associate, Technology Assurance - Audit | KPMG | Omaha, NE | 2023-10 | 2024-03 | $116,700 | | |
| 35 | | Senior Associate, Technology Assurance - Audit | KPMG | Omaha, NE | 2022-06 | 2023-10 | $110,000 | | |
| 36 | | Senior Technology Risk Consultant | Ernst & Young | Des Moines, IA | 2021-09 | 2022-06 | $89,500 | | |
| 37 | | Senior IT Auditor | Ameritas | Lincoln, NE | 2021-05 | 2021-09 | $72,000 | | |
| 38 | | IT Auditor | Ameritas | Lincoln, NE | 2020-04 | 2021-05 | $65,000 | | |
| 39 | | IS Auditor II | Nelnet | Lincoln, NE | 2019-12 | 2020-04 | $58,000 | | |
| 40 | | IS Auditor I | Nelnet | Lincoln, NE | 2019-06 | 2019-12 | $20/hour | | |
| 41 | | Internal Audit Intern | Ameritas | Lincoln, NE | 2018-02 | 2019-06 | $16/hour | | |
| 42 | | Teaching Assistant | University of Nebraska | Lincoln, NE | 2017-08 | 2018-05 | $7/hour | | |
| 43 | | Community Management Intern | Walgreens | Lincoln, NE | 2017-06 | 2018-02 | $14/hour | | |
| 44 | ||
| 45 | This page was inspired by [[https://xeiaso.net/][Xe]], and I'm quoting the following wording from them as | |
| 46 | I want to reiterate this piece: | |
| 47 | ||
| 48 | #+begin_quote | |
| 49 | Please consider publishing your salary data like this as well. By open, voluntary transparency we can help to end stigmas around discussing pay and help ensure that the next generations of people in tech are treated fairly. Stigmas thrive in darkness but die in the light of day. You can help end the stigma by playing your cards out in the open like this. | |
| 50 | #+end_quote | |
services/index.org added +14
| @@ -0,0 +1,14 @@ | ||
| 1 | #+title: Services | |
| 2 | #+description: Publicly-available services hosted on cleberg.net. | |
| 3 | ||
| 4 | - [[https://ao.cleberg.net/][AnonymousOverflow]] - A StackOverflow proxy | |
| 5 | - [[https://cyberchef.cleberg.net/][CyberChef]] - The Cyber Swiss Army Knife | |
| 6 | - [[https://files.cleberg.net/][FileArchive]] - An interesting file archive | |
| 7 | - [[https://paste.cleberg.net/][FlashPaper]] - One-time encrypted password/secret sharing | |
| 8 | - [[https://gh.cleberg.net/][GotHub]] - An alternative front-end for GitHub | |
| 9 | - [[https://ip.cleberg.net/][ifconfig.php]] - A "whatsmyip" tool | |
| 10 | - [[https://invidious.cleberg.net/][Invidious]] - A YouTube proxy | |
| 11 | - [[https://office.cleberg.net/][Office]] - The world's smallest office suite | |
| 12 | - [[https://search.cleberg.net/][SearXNG]] - A privacy-respecting, open metasearch engine | |
| 13 | ||
| 14 | See the [[https://git.cleberg.net/cleberg.net.git/log][git log]] if you want to see changes that have been made. | |
static/gpg.txt deleted −52
| @@ -1,52 +0,0 @@ | ||
| 1 | -----BEGIN PGP PUBLIC KEY BLOCK----- | |
| 2 | ||
| 3 | mQINBGN0Z8YBEAC6gWrNuB0nyAVkIuCsErIqpO7ngH0HV2sZD54t0ge9on0Fb+QA | |
| 4 | S/oRSK3bcwgR09lnIwPDWpQqlPpzKib2bZ9USBMD0lcgPb0hMr0fafs/+/FCRQV1 | |
| 5 | Pvc/e37n2/KHRW2KoiM4sOFT9LYxi7LBGgXffusx6uVBzrNUacTFFd/pMNkPd5uX | |
| 6 | /J4IT+QbDh1bKw4CtLNvoh7xTcfdpzdqpHfNkjm+24pEnbrv6QrSpBzol4uulaB+ | |
| 7 | 5I8JF938/FBHBndVMT9UQcGRtX+ttZTp9U7m0TzCAsyrVV/V8rEbcGTMlU+yyUjR | |
| 8 | TDRX4Dwj79IfL+vLZgFGLd8GwO08AirNkHYaZwzvYi42I5Bh8cX1L2IippYL8YYF | |
| 9 | ASX26pXC6mxTwC/hjCA7rzyIMD5sf1UailYm5MvrhEujRYOPWDU+kex2t2HJpzvN | |
| 10 | vYSVIS0sKi7iHr82VA+/spR6Ii07/84zZPQ1h/sXJLaDolQV2pU7WJBPyFO957Er | |
| 11 | BggugSpB1U/blgU+B9vOR+2sMEReRQwVF7aVhQ2Wy5wOZRHlmTZVMNO5SawXkiTp | |
| 12 | Bt4IwhThzMcUQstXxf5V44pPsB5uQE3n4WdROfJTOiB2cZJZOiXe3iPiiTsVsBc2 | |
| 13 | tcqxJmwplMS4jNddJ9Nh0NTCKNk3Yt0iZzWlQDKAzR1uSGW9fQGAdh/UZQARAQAB | |
| 14 | tCVDaHJpc3RpYW4gQ2xlYmVyZyA8aGVsbG9AY2xlYmVyZy5uZXQ+iQJRBBMBCAA7 | |
| 15 | FiEEOReXP7FZu7hhlFOFaUUaUXrAyzcFAmN0Z8YCGwMFCwkIBwICIgIGFQoJCAsC | |
| 16 | BBYCAwECHgcCF4AACgkQaUUaUXrAyzcrIQ//ZzCvcNKi2exZ4MfH68q9cIrJtHA3 | |
| 17 | +FQ/3yTwAMiXmaTctHTcME+4Um12TCJMH/PwOkmxjolln5LfNHC8emcNs9Uaoga7 | |
| 18 | 1Cy8ihqKbQMaZN1ZHrgaddeTs7+N1+/u8yAZPXo+N6pmLaeuPfn1MMhcejTbo+C/ | |
| 19 | c22/yj97ym6Iuc9oodnbHb2rxhGKReQLJmqzBHWd0syFbYDopmhY2MjMawVirPG7 | |
| 20 | vt6EbiFHkWLBY08FYbOQWT4bXdSHlLxT3q5m+j0HdVjHxd/vOk+dc3FPtK8ZpTVC | |
| 21 | qKa2oQ6dl4fjp8GVbu4f4SMDDJRR1iOoLTNEhKDSZHkZdjH0/LQRLsf49cqbff1Y | |
| 22 | mpxJcNv1/RmgzctTmBAoGt2RS8mT97H8AUW7v7PGs3eS/OkrY1e4cuTrmcafEaMy | |
| 23 | J2L7aUxDVVUCvRKsONXx+zSLin7ByRHypqRfxGqnpQUDPW4Oty6CewsSXktDjIUx | |
| 24 | FXzMwfuNXKS/KHqcUxamE0rL8O2d3CJI4YAbWu2Y0GtBetfuaaOgi56cYqv86zGu | |
| 25 | os0oga1ZakiCeRPgEaipPaZZMf6pCvucF2VyaUHwIOMcSVEH5nhHO4McgYLSZucx | |
| 26 | na5qcLk06EP+1HjmifGqPmkxHTW/ez5x6m/QT9jOzyRu94p3IG5DT1Lh8kl6gid7 | |
| 27 | YntCGrwcsvw8zKi5Ag0EY3RnxgEQANj1c0ZS3npmtj1V5m+vsq1mK2g4K66senuC | |
| 28 | Gf+wTudYgcUzBhcTtEwzFJTwFFUMkfpgmkgYrlMB7iH+85YxiDR2sBhMg56haJXn | |
| 29 | LGnSaWqHVE4P0yyHI/6QasYxdJWfYkSH9m3B8yW1VKs4eSSL6S/U/qdHzDRRZCEX | |
| 30 | lNhvplrWcWv6Ifk/aYJ+njwn+jhXT4j8lbhem5oCbg4olY84bs+rfvWHTrWdGD1N | |
| 31 | sHkbLEwLgnmJou7vkVY9vkIMhbgpvNp1CEx0zOGTMhlPrCYBCFUGR7Bnoqwwl/C4 | |
| 32 | CTBwZxBE5bNBpsEdySYhmHW+YHRHIxeboLmOyoc0CpT/zhu2y5JxqJBiGEDYhTM/ | |
| 33 | V2nNqKGDgUenXqjwoBw5oCNQJ35NNgFgEbphhs71W7VVwEPRdppcem33TcpFBeoE | |
| 34 | vTzCfK6xJA82ASJHKz0hajEQchJ5jJZYo4wRZJGFv2jMIhq24DLIqxgjZeBKLEzl | |
| 35 | RigfuuCrAsQBIMtTUSUUvxjB/b+UDYssqi9Q+8F7FcwqE9egaj7xVQprTAYcGW7S | |
| 36 | zxfjzFSbJSl+b4WQSewFtmFIx62RYemBH+YPxbwOhQAuRWgEg0E6xeuILu22xydf | |
| 37 | DEkbk1GEXH3ilYxl4LhFy2EmUbvB8rxh5Vk3A1KVaBe/ndPhwznTe7X9ypRHzQiV | |
| 38 | Jkc2vVGjABEBAAGJAjYEGAEIACAWIQQ5F5c/sVm7uGGUU4VpRRpResDLNwUCY3Rn | |
| 39 | xgIbDAAKCRBpRRpResDLN60xD/9pEDZK7SXZy/nhVdHMKn2UyF7F8dEXYxILmXp0 | |
| 40 | 53zDDVN5D7luHjcI5pYynWqlgXWPAaCOthWtexr3r3b8fVSc7yxi497fFa3jiVkn | |
| 41 | VNYjDCa4SK5H6Rdf6I5rv+SS1PPmiVFKL7xuWcJ9YucHACdeH0UUmPCMmHHDc9SY | |
| 42 | MGUPjadFxjCGtBz8itS+ufDiZsTU9ov7XRE+pVyrDlMSVD1Ex02vMRtr+UD9lkYb | |
| 43 | KGs32TEDw28+OgvSZc81P6/BuxmG2XxgvU5OOrlVFOs4VU5P0TnZVxbVuKyO4fkZ | |
| 44 | sxSApn+U4lU89dM0M1l1S2NZtvkWTIW2jFvzwXDCPxs5GAXAGtnEO8gjGICo2QV3 | |
| 45 | VovHMTmPz7Bo87fqGZkfZatzvAeHW92FIhQBOdgSiCwSDRPVVdPTpQ27BaUrfH8p | |
| 46 | aS81RhlCWgKptFKj4+MAqGEf9V6jUIKn5EvdSxCZ5XXHmaBL/kXxTPaDJiK8nMKv | |
| 47 | dr/iwtb23SwNrBLQkYcI+6aZj4jcqr5T0H2EsC8h9jQWMG+S9/BzhJOI/QeepHvD | |
| 48 | VJQve5jozXbz+iBRLrWbEgbNydL/LT9iQCWaWt2HCPQ7bPrxKqya8fUMPxi3VCZZ | |
| 49 | AuXpJzywCyVuzpuChuvdMflHbmx1r8uJjSmUCJf6ngt0TQMXiwL3vsECTV7ZtVge | |
| 50 | 0jZ4tA== | |
| 51 | =pl2G | |
| 52 | -----END PGP PUBLIC KEY BLOCK----- | |
static/styles.css +468 −208
| @@ -1,127 +1,59 @@ | ||
| 1 | /*! normalize.css v8.0.1 | MIT License | github.com/necolas/normalize.css */ | |
| 2 | ||
| 3 | /* Document | |
| 4 | ========================================================================== */ | |
| 5 | ||
| 6 | /** | |
| 7 | * 1. Correct the line height in all browsers. | |
| 8 | * 2. Prevent adjustments of font size after orientation changes in iOS. | |
| 9 | */ | |
| 10 | ||
| 1 | /*!normalize.css v8.0.1 | MIT License | github.com/necolas/normalize.css*/ | |
| 11 | 2 | html { |
| 12 | line-height: 1.15; /* 1 */ | |
| 13 | -webkit-text-size-adjust: 100%; /* 2 */ | |
| 3 | line-height: 1.15; | |
| 4 | -webkit-text-size-adjust: 100%; | |
| 14 | 5 | } |
| 15 | 6 | |
| 16 | /* Sections | |
| 17 | ========================================================================== */ | |
| 18 | ||
| 19 | /** | |
| 20 | * Remove the margin in all browsers. | |
| 21 | */ | |
| 22 | ||
| 23 | 7 | body { |
| 24 | 8 | margin: 0; |
| 25 | 9 | } |
| 26 | 10 | |
| 27 | /** | |
| 28 | * Render the `main` element consistently in IE. | |
| 29 | */ | |
| 30 | ||
| 31 | 11 | main { |
| 32 | 12 | display: block; |
| 33 | 13 | } |
| 34 | 14 | |
| 35 | /** | |
| 36 | * Correct the font size and margin on `h1` elements within `section` and | |
| 37 | * `article` contexts in Chrome, Firefox, and Safari. | |
| 38 | */ | |
| 39 | ||
| 40 | 15 | h1 { |
| 41 | 16 | font-size: 2em; |
| 42 | 17 | margin: 0.67em 0; |
| 43 | 18 | } |
| 44 | 19 | |
| 45 | /* Grouping content | |
| 46 | ========================================================================== */ | |
| 47 | ||
| 48 | /** | |
| 49 | * 1. Add the correct box sizing in Firefox. | |
| 50 | * 2. Show the overflow in Edge and IE. | |
| 51 | */ | |
| 52 | ||
| 53 | 20 | hr { |
| 54 | box-sizing: content-box; /* 1 */ | |
| 55 | height: 0; /* 1 */ | |
| 56 | overflow: visible; /* 2 */ | |
| 21 | box-sizing: content-box; | |
| 22 | height: 0; | |
| 23 | overflow: visible; | |
| 57 | 24 | } |
| 58 | 25 | |
| 59 | /** | |
| 60 | * 1. Correct the inheritance and scaling of font size in all browsers. | |
| 61 | * 2. Correct the odd `em` font sizing in all browsers. | |
| 62 | */ | |
| 63 | ||
| 64 | 26 | pre { |
| 65 | font-family: monospace, monospace; /* 1 */ | |
| 66 | font-size: 1em; /* 2 */ | |
| 27 | font-family: monospace, monospace; | |
| 28 | font-size: 1em; | |
| 67 | 29 | } |
| 68 | 30 | |
| 69 | /* Text-level semantics | |
| 70 | ========================================================================== */ | |
| 71 | ||
| 72 | /** | |
| 73 | * Remove the gray background on active links in IE 10. | |
| 74 | */ | |
| 75 | ||
| 76 | 31 | a { |
| 77 | background-color: transparent; | |
| 32 | background-color: initial; | |
| 78 | 33 | } |
| 79 | 34 | |
| 80 | /** | |
| 81 | * 1. Remove the bottom border in Chrome 57- | |
| 82 | * 2. Add the correct text decoration in Chrome, Edge, IE, Opera, and Safari. | |
| 83 | */ | |
| 84 | ||
| 85 | 35 | abbr[title] { |
| 86 | border-bottom: none; /* 1 */ | |
| 87 | text-decoration: underline; /* 2 */ | |
| 88 | text-decoration: underline dotted; /* 2 */ | |
| 36 | border-bottom: none; | |
| 37 | text-decoration: underline; | |
| 38 | text-decoration: underline dotted; | |
| 89 | 39 | } |
| 90 | 40 | |
| 91 | /** | |
| 92 | * Add the correct font weight in Chrome, Edge, and Safari. | |
| 93 | */ | |
| 94 | ||
| 95 | 41 | b, |
| 96 | 42 | strong { |
| 97 | 43 | font-weight: bolder; |
| 98 | 44 | } |
| 99 | 45 | |
| 100 | /** | |
| 101 | * 1. Correct the inheritance and scaling of font size in all browsers. | |
| 102 | * 2. Correct the odd `em` font sizing in all browsers. | |
| 103 | */ | |
| 104 | ||
| 105 | 46 | code, |
| 106 | 47 | kbd, |
| 107 | 48 | samp { |
| 108 | font-family: monospace, monospace; /* 1 */ | |
| 109 | font-size: 1em; /* 2 */ | |
| 49 | font-family: monospace, monospace; | |
| 50 | font-size: 1em; | |
| 110 | 51 | } |
| 111 | 52 | |
| 112 | /** | |
| 113 | * Add the correct font size in all browsers. | |
| 114 | */ | |
| 115 | ||
| 116 | 53 | small { |
| 117 | 54 | font-size: 80%; |
| 118 | 55 | } |
| 119 | 56 | |
| 120 | /** | |
| 121 | * Prevent `sub` and `sup` elements from affecting the line height in | |
| 122 | * all browsers. | |
| 123 | */ | |
| 124 | ||
| 125 | 57 | sub, |
| 126 | 58 | sup { |
| 127 | 59 | font-size: 75%; |
| @@ -138,62 +70,31 @@ sup { | ||
| 138 | 70 | top: -0.5em; |
| 139 | 71 | } |
| 140 | 72 | |
| 141 | /* Embedded content | |
| 142 | ========================================================================== */ | |
| 143 | ||
| 144 | /** | |
| 145 | * Remove the border on images inside links in IE 10. | |
| 146 | */ | |
| 147 | ||
| 148 | 73 | img { |
| 149 | 74 | border-style: none; |
| 150 | 75 | } |
| 151 | 76 | |
| 152 | /* Forms | |
| 153 | ========================================================================== */ | |
| 154 | ||
| 155 | /** | |
| 156 | * 1. Change the font styles in all browsers. | |
| 157 | * 2. Remove the margin in Firefox and Safari. | |
| 158 | */ | |
| 159 | ||
| 160 | 77 | button, |
| 161 | 78 | input, |
| 162 | 79 | optgroup, |
| 163 | 80 | select, |
| 164 | 81 | textarea { |
| 165 | font-family: inherit; /* 1 */ | |
| 166 | font-size: 100%; /* 1 */ | |
| 167 | line-height: 1.15; /* 1 */ | |
| 168 | margin: 0; /* 2 */ | |
| 82 | font-family: inherit; | |
| 83 | font-size: 100%; | |
| 84 | line-height: 1.15; | |
| 85 | margin: 0; | |
| 169 | 86 | } |
| 170 | 87 | |
| 171 | /** | |
| 172 | * Show the overflow in IE. | |
| 173 | * 1. Show the overflow in Edge. | |
| 174 | */ | |
| 175 | ||
| 176 | 88 | button, |
| 177 | 89 | input { |
| 178 | /* 1 */ | |
| 179 | 90 | overflow: visible; |
| 180 | 91 | } |
| 181 | 92 | |
| 182 | /** | |
| 183 | * Remove the inheritance of text transform in Edge, Firefox, and IE. | |
| 184 | * 1. Remove the inheritance of text transform in Firefox. | |
| 185 | */ | |
| 186 | ||
| 187 | 93 | button, |
| 188 | 94 | select { |
| 189 | /* 1 */ | |
| 190 | 95 | text-transform: none; |
| 191 | 96 | } |
| 192 | 97 | |
| 193 | /** | |
| 194 | * Correct the inability to style clickable types in iOS and Safari. | |
| 195 | */ | |
| 196 | ||
| 197 | 98 | button, |
| 198 | 99 | [type="button"], |
| 199 | 100 | [type="reset"], |
| @@ -201,10 +102,6 @@ button, | ||
| 201 | 102 | -webkit-appearance: button; |
| 202 | 103 | } |
| 203 | 104 | |
| 204 | /** | |
| 205 | * Remove the inner border and padding in Firefox. | |
| 206 | */ | |
| 207 | ||
| 208 | 105 | button::-moz-focus-inner, |
| 209 | 106 | [type="button"]::-moz-focus-inner, |
| 210 | 107 | [type="reset"]::-moz-focus-inner, |
| @@ -213,10 +110,6 @@ button::-moz-focus-inner, | ||
| 213 | 110 | padding: 0; |
| 214 | 111 | } |
| 215 | 112 | |
| 216 | /** | |
| 217 | * Restore the focus styles unset by the previous rule. | |
| 218 | */ | |
| 219 | ||
| 220 | 113 | button:-moz-focusring, |
| 221 | 114 | [type="button"]:-moz-focusring, |
| 222 | 115 | [type="reset"]:-moz-focusring, |
| @@ -224,133 +117,68 @@ button:-moz-focusring, | ||
| 224 | 117 | outline: 1px dotted ButtonText; |
| 225 | 118 | } |
| 226 | 119 | |
| 227 | /** | |
| 228 | * Correct the padding in Firefox. | |
| 229 | */ | |
| 230 | ||
| 231 | 120 | fieldset { |
| 232 | 121 | padding: 0.35em 0.75em 0.625em; |
| 233 | 122 | } |
| 234 | 123 | |
| 235 | /** | |
| 236 | * 1. Correct the text wrapping in Edge and IE. | |
| 237 | * 2. Correct the color inheritance from `fieldset` elements in IE. | |
| 238 | * 3. Remove the padding so developers are not caught out when they zero out | |
| 239 | * `fieldset` elements in all browsers. | |
| 240 | */ | |
| 241 | ||
| 242 | 124 | legend { |
| 243 | box-sizing: border-box; /* 1 */ | |
| 244 | color: inherit; /* 2 */ | |
| 245 | display: table; /* 1 */ | |
| 246 | max-width: 100%; /* 1 */ | |
| 247 | padding: 0; /* 3 */ | |
| 248 | white-space: normal; /* 1 */ | |
| 125 | box-sizing: border-box; | |
| 126 | color: inherit; | |
| 127 | display: table; | |
| 128 | max-width: 100%; | |
| 129 | padding: 0; | |
| 130 | white-space: normal; | |
| 249 | 131 | } |
| 250 | 132 | |
| 251 | /** | |
| 252 | * Add the correct vertical alignment in Chrome, Firefox, and Opera. | |
| 253 | */ | |
| 254 | ||
| 255 | 133 | progress { |
| 256 | 134 | vertical-align: baseline; |
| 257 | 135 | } |
| 258 | 136 | |
| 259 | /** | |
| 260 | * Remove the default vertical scrollbar in IE 10+. | |
| 261 | */ | |
| 262 | ||
| 263 | 137 | textarea { |
| 264 | 138 | overflow: auto; |
| 265 | 139 | } |
| 266 | 140 | |
| 267 | /** | |
| 268 | * 1. Add the correct box sizing in IE 10. | |
| 269 | * 2. Remove the padding in IE 10. | |
| 270 | */ | |
| 271 | ||
| 272 | 141 | [type="checkbox"], |
| 273 | 142 | [type="radio"] { |
| 274 | box-sizing: border-box; /* 1 */ | |
| 275 | padding: 0; /* 2 */ | |
| 143 | box-sizing: border-box; | |
| 144 | padding: 0; | |
| 276 | 145 | } |
| 277 | 146 | |
| 278 | /** | |
| 279 | * Correct the cursor style of increment and decrement buttons in Chrome. | |
| 280 | */ | |
| 281 | ||
| 282 | 147 | [type="number"]::-webkit-inner-spin-button, |
| 283 | 148 | [type="number"]::-webkit-outer-spin-button { |
| 284 | 149 | height: auto; |
| 285 | 150 | } |
| 286 | 151 | |
| 287 | /** | |
| 288 | * 1. Correct the odd appearance in Chrome and Safari. | |
| 289 | * 2. Correct the outline style in Safari. | |
| 290 | */ | |
| 291 | ||
| 292 | 152 | [type="search"] { |
| 293 | -webkit-appearance: textfield; /* 1 */ | |
| 294 | outline-offset: -2px; /* 2 */ | |
| 153 | -webkit-appearance: textfield; | |
| 154 | outline-offset: -2px; | |
| 295 | 155 | } |
| 296 | 156 | |
| 297 | /** | |
| 298 | * Remove the inner padding in Chrome and Safari on macOS. | |
| 299 | */ | |
| 300 | ||
| 301 | 157 | [type="search"]::-webkit-search-decoration { |
| 302 | 158 | -webkit-appearance: none; |
| 303 | 159 | } |
| 304 | 160 | |
| 305 | /** | |
| 306 | * 1. Correct the inability to style clickable types in iOS and Safari. | |
| 307 | * 2. Change font properties to `inherit` in Safari. | |
| 308 | */ | |
| 309 | ||
| 310 | 161 | ::-webkit-file-upload-button { |
| 311 | -webkit-appearance: button; /* 1 */ | |
| 312 | font: inherit; /* 2 */ | |
| 162 | -webkit-appearance: button; | |
| 163 | font: inherit; | |
| 313 | 164 | } |
| 314 | 165 | |
| 315 | /* Interactive | |
| 316 | ========================================================================== */ | |
| 317 | ||
| 318 | /* | |
| 319 | * Add the correct display in Edge, IE 10+, and Firefox. | |
| 320 | */ | |
| 321 | ||
| 322 | 166 | details { |
| 323 | 167 | display: block; |
| 324 | 168 | } |
| 325 | 169 | |
| 326 | /* | |
| 327 | * Add the correct display in all browsers. | |
| 328 | */ | |
| 329 | ||
| 330 | 170 | summary { |
| 331 | 171 | display: list-item; |
| 332 | 172 | } |
| 333 | 173 | |
| 334 | /* Misc | |
| 335 | ========================================================================== */ | |
| 336 | ||
| 337 | /** | |
| 338 | * Add the correct display in IE 10+. | |
| 339 | */ | |
| 340 | ||
| 341 | 174 | template { |
| 342 | 175 | display: none; |
| 343 | 176 | } |
| 344 | 177 | |
| 345 | /** | |
| 346 | * Add the correct display in IE 10. | |
| 347 | */ | |
| 348 | ||
| 349 | 178 | [hidden] { |
| 350 | 179 | display: none; |
| 351 | 180 | } |
| 352 | 181 | |
| 353 | /* CUSTOM CSS */ | |
| 354 | 182 | :root { |
| 355 | 183 | --bg: #fff; |
| 356 | 184 | --bg-bright: #eee; |
| @@ -368,8 +196,19 @@ template { | ||
| 368 | 196 | body { |
| 369 | 197 | background-color: var(--bg); |
| 370 | 198 | color: var(--fg); |
| 371 | font-family: -apple-system, BlinkMacSystemFont, avenir next, avenir, segoe ui, | |
| 372 | helvetica neue, helvetica, Cantarell, Ubuntu, roboto, noto, arial, | |
| 199 | font-family: | |
| 200 | -apple-system, | |
| 201 | BlinkMacSystemFont, | |
| 202 | avenir next, | |
| 203 | avenir, | |
| 204 | segoe ui, | |
| 205 | helvetica neue, | |
| 206 | helvetica, | |
| 207 | Cantarell, | |
| 208 | Ubuntu, | |
| 209 | roboto, | |
| 210 | noto, | |
| 211 | arial, | |
| 373 | 212 | sans-serif; |
| 374 | 213 | font-size: 1rem; |
| 375 | 214 | line-height: 1.5; |
| @@ -390,6 +229,7 @@ footer { | ||
| 390 | 229 | } |
| 391 | 230 | |
| 392 | 231 | footer p { |
| 232 | font-size: 90%; | |
| 393 | 233 | margin: 0; |
| 394 | 234 | } |
| 395 | 235 | |
| @@ -433,8 +273,13 @@ table { | ||
| 433 | 273 | border-collapse: collapse; |
| 434 | 274 | color: var(--fg); |
| 435 | 275 | border-color: var(--bg-bright); |
| 436 | font-family: Menlo, Consolas, Monaco, Liberation Mono, Lucida Console, monospace; | |
| 437 | font-size: 0.9rem; | |
| 276 | font-family: | |
| 277 | Menlo, | |
| 278 | Consolas, | |
| 279 | Monaco, | |
| 280 | Liberation Mono, | |
| 281 | Lucida Console, | |
| 282 | monospace; | |
| 438 | 283 | } |
| 439 | 284 | |
| 440 | 285 | thead, |
| @@ -448,7 +293,13 @@ td { | ||
| 448 | 293 | pre > code, |
| 449 | 294 | time, |
| 450 | 295 | code { |
| 451 | font-family: Menlo, Consolas, Monaco, Liberation Mono, Lucida Console, monospace; | |
| 296 | font-family: | |
| 297 | Menlo, | |
| 298 | Consolas, | |
| 299 | Monaco, | |
| 300 | Liberation Mono, | |
| 301 | Lucida Console, | |
| 302 | monospace; | |
| 452 | 303 | font-size: 1rem; |
| 453 | 304 | } |
| 454 | 305 | |
| @@ -510,7 +361,7 @@ details { | ||
| 510 | 361 | } |
| 511 | 362 | |
| 512 | 363 | summary { |
| 513 | font-weight: bold; | |
| 364 | font-weight: 700; | |
| 514 | 365 | } |
| 515 | 366 | |
| 516 | 367 | .footnote-definition { |
| @@ -545,3 +396,412 @@ summary { | ||
| 545 | 396 | --code: #ffb454; |
| 546 | 397 | } |
| 547 | 398 | } |
| 399 | ||
| 400 | /* Org Styles */ | |
| 401 | p.verse { | |
| 402 | margin-left: 3%; | |
| 403 | } | |
| 404 | .timestamp { | |
| 405 | color: var(--bg-light); | |
| 406 | } | |
| 407 | .timestamp-kwd { | |
| 408 | color: var(--timestamp-kwd); | |
| 409 | } | |
| 410 | .org-right { | |
| 411 | margin-left: auto; | |
| 412 | margin-right: 0px; | |
| 413 | text-align: right; | |
| 414 | } | |
| 415 | .org-left { | |
| 416 | margin-left: 0px; | |
| 417 | margin-right: auto; | |
| 418 | text-align: left; | |
| 419 | } | |
| 420 | .org-center { | |
| 421 | margin-left: auto; | |
| 422 | margin-right: auto; | |
| 423 | text-align: center; | |
| 424 | } | |
| 425 | .underline { | |
| 426 | text-decoration: underline; | |
| 427 | } | |
| 428 | .todo { | |
| 429 | font-family: monospace; | |
| 430 | color: red; | |
| 431 | } | |
| 432 | .done { | |
| 433 | font-family: monospace; | |
| 434 | color: green; | |
| 435 | } | |
| 436 | .priority { | |
| 437 | font-family: monospace; | |
| 438 | color: orange; | |
| 439 | } | |
| 440 | .tag { | |
| 441 | background-color: #eee; | |
| 442 | font-family: monospace; | |
| 443 | padding: 2px; | |
| 444 | font-size: 80%; | |
| 445 | font-weight: normal; | |
| 446 | } | |
| 447 | ||
| 448 | .code-highlighted { | |
| 449 | background-color: var(--highlight); | |
| 450 | } | |
| 451 | .org-info-js_info-navigation { | |
| 452 | border-style: none; | |
| 453 | } | |
| 454 | #org-info-js_console-label { | |
| 455 | font-size: 10px; | |
| 456 | font-weight: bold; | |
| 457 | white-space: nowrap; | |
| 458 | } | |
| 459 | .org-info-js_search-highlight { | |
| 460 | background-color: var(--highlight); | |
| 461 | color: var(--fg); | |
| 462 | font-weight: bold; | |
| 463 | } | |
| 464 | ||
| 465 | caption.t-above { | |
| 466 | caption-side: top; | |
| 467 | } | |
| 468 | caption.t-bottom { | |
| 469 | caption-side: bottom; | |
| 470 | } | |
| 471 | td, | |
| 472 | th { | |
| 473 | vertical-align: top; | |
| 474 | } | |
| 475 | th.org-right { | |
| 476 | text-align: center; | |
| 477 | } | |
| 478 | th.org-left { | |
| 479 | text-align: center; | |
| 480 | } | |
| 481 | th.org-center { | |
| 482 | text-align: center; | |
| 483 | } | |
| 484 | td.org-right { | |
| 485 | text-align: right; | |
| 486 | } | |
| 487 | td.org-left { | |
| 488 | text-align: left; | |
| 489 | } | |
| 490 | td.org-center { | |
| 491 | text-align: center; | |
| 492 | } | |
| 493 | dt { | |
| 494 | font-weight: bold; | |
| 495 | } | |
| 496 | .footpara { | |
| 497 | display: inline; | |
| 498 | } | |
| 499 | .footdef { | |
| 500 | margin-bottom: 1em; | |
| 501 | } | |
| 502 | .figure { | |
| 503 | padding: 1em; | |
| 504 | } | |
| 505 | .figure p { | |
| 506 | text-align: center; | |
| 507 | } | |
| 508 | .equation-container { | |
| 509 | display: table; | |
| 510 | text-align: center; | |
| 511 | width: 100%; | |
| 512 | } | |
| 513 | .equation { | |
| 514 | vertical-align: middle; | |
| 515 | } | |
| 516 | .equation-label { | |
| 517 | display: table-cell; | |
| 518 | text-align: right; | |
| 519 | vertical-align: middle; | |
| 520 | } | |
| 521 | .inlinetask { | |
| 522 | padding: 10px; | |
| 523 | border: 2px solid var(--bg); | |
| 524 | margin: 10px; | |
| 525 | background: var(--task); | |
| 526 | } | |
| 527 | #org-div-home-and-up { | |
| 528 | text-align: right; | |
| 529 | font-size: 70%; | |
| 530 | white-space: nowrap; | |
| 531 | } | |
| 532 | ||
| 533 | pre.src { | |
| 534 | position: relative; | |
| 535 | overflow: auto; | |
| 536 | } | |
| 537 | pre.src:before { | |
| 538 | display: none; | |
| 539 | position: absolute; | |
| 540 | top: -8px; | |
| 541 | right: 12px; | |
| 542 | padding: 3px; | |
| 543 | color: var(--fg); | |
| 544 | background-color: var(--bg-lightest-opac); | |
| 545 | } | |
| 546 | pre.src:hover:before { | |
| 547 | display: inline; | |
| 548 | margin-top: 14px; | |
| 549 | } | |
| 550 | ||
| 551 | /* Languages per Org manual */ | |
| 552 | pre.src-asymptote:before { | |
| 553 | content: "Asymptote"; | |
| 554 | } | |
| 555 | pre.src-awk:before { | |
| 556 | content: "Awk"; | |
| 557 | } | |
| 558 | pre.src-authinfo::before { | |
| 559 | content: "Authinfo"; | |
| 560 | } | |
| 561 | pre.src-C:before { | |
| 562 | content: "C"; | |
| 563 | } | |
| 564 | /* pre.src-C++ doesn't work in CSS */ | |
| 565 | pre.src-clojure:before { | |
| 566 | content: "Clojure"; | |
| 567 | } | |
| 568 | pre.src-css:before { | |
| 569 | content: "CSS"; | |
| 570 | } | |
| 571 | pre.src-D:before { | |
| 572 | content: "D"; | |
| 573 | } | |
| 574 | pre.src-ditaa:before { | |
| 575 | content: "ditaa"; | |
| 576 | } | |
| 577 | pre.src-dot:before { | |
| 578 | content: "Graphviz"; | |
| 579 | } | |
| 580 | pre.src-calc:before { | |
| 581 | content: "Emacs Calc"; | |
| 582 | } | |
| 583 | pre.src-emacs-lisp:before { | |
| 584 | content: "Emacs Lisp"; | |
| 585 | } | |
| 586 | pre.src-fortran:before { | |
| 587 | content: "Fortran"; | |
| 588 | } | |
| 589 | pre.src-gnuplot:before { | |
| 590 | content: "gnuplot"; | |
| 591 | } | |
| 592 | pre.src-haskell:before { | |
| 593 | content: "Haskell"; | |
| 594 | } | |
| 595 | pre.src-hledger:before { | |
| 596 | content: "hledger"; | |
| 597 | } | |
| 598 | pre.src-java:before { | |
| 599 | content: "Java"; | |
| 600 | } | |
| 601 | pre.src-js:before { | |
| 602 | content: "Javascript"; | |
| 603 | } | |
| 604 | pre.src-latex:before { | |
| 605 | content: "LaTeX"; | |
| 606 | } | |
| 607 | pre.src-ledger:before { | |
| 608 | content: "Ledger"; | |
| 609 | } | |
| 610 | pre.src-lisp:before { | |
| 611 | content: "Lisp"; | |
| 612 | } | |
| 613 | pre.src-lilypond:before { | |
| 614 | content: "Lilypond"; | |
| 615 | } | |
| 616 | pre.src-lua:before { | |
| 617 | content: "Lua"; | |
| 618 | } | |
| 619 | pre.src-matlab:before { | |
| 620 | content: "MATLAB"; | |
| 621 | } | |
| 622 | pre.src-mscgen:before { | |
| 623 | content: "Mscgen"; | |
| 624 | } | |
| 625 | pre.src-ocaml:before { | |
| 626 | content: "Objective Caml"; | |
| 627 | } | |
| 628 | pre.src-octave:before { | |
| 629 | content: "Octave"; | |
| 630 | } | |
| 631 | pre.src-org:before { | |
| 632 | content: "Org mode"; | |
| 633 | } | |
| 634 | pre.src-oz:before { | |
| 635 | content: "OZ"; | |
| 636 | } | |
| 637 | pre.src-plantuml:before { | |
| 638 | content: "Plantuml"; | |
| 639 | } | |
| 640 | pre.src-processing:before { | |
| 641 | content: "Processing.js"; | |
| 642 | } | |
| 643 | pre.src-python:before { | |
| 644 | content: "Python"; | |
| 645 | } | |
| 646 | pre.src-R:before { | |
| 647 | content: "R"; | |
| 648 | } | |
| 649 | pre.src-ruby:before { | |
| 650 | content: "Ruby"; | |
| 651 | } | |
| 652 | pre.src-sass:before { | |
| 653 | content: "Sass"; | |
| 654 | } | |
| 655 | pre.src-scheme:before { | |
| 656 | content: "Scheme"; | |
| 657 | } | |
| 658 | pre.src-screen:before { | |
| 659 | content: "Gnu Screen"; | |
| 660 | } | |
| 661 | pre.src-sed:before { | |
| 662 | content: "Sed"; | |
| 663 | } | |
| 664 | pre.src-sh:before { | |
| 665 | content: "shell"; | |
| 666 | } | |
| 667 | pre.src-sql:before { | |
| 668 | content: "SQL"; | |
| 669 | } | |
| 670 | pre.src-sqlite:before { | |
| 671 | content: "SQLite"; | |
| 672 | } | |
| 673 | /* additional languages in org.el's org-babel-load-languages alist */ | |
| 674 | pre.src-forth:before { | |
| 675 | content: "Forth"; | |
| 676 | } | |
| 677 | pre.src-io:before { | |
| 678 | content: "IO"; | |
| 679 | } | |
| 680 | pre.src-J:before { | |
| 681 | content: "J"; | |
| 682 | } | |
| 683 | pre.src-makefile:before { | |
| 684 | content: "Makefile"; | |
| 685 | } | |
| 686 | pre.src-maxima:before { | |
| 687 | content: "Maxima"; | |
| 688 | } | |
| 689 | pre.src-perl:before { | |
| 690 | content: "Perl"; | |
| 691 | } | |
| 692 | pre.src-picolisp:before { | |
| 693 | content: "Pico Lisp"; | |
| 694 | } | |
| 695 | pre.src-scala:before { | |
| 696 | content: "Scala"; | |
| 697 | } | |
| 698 | pre.src-shell:before { | |
| 699 | content: "Shell Script"; | |
| 700 | } | |
| 701 | pre.src-ebnf2ps:before { | |
| 702 | content: "ebfn2ps"; | |
| 703 | } | |
| 704 | /* additional language identifiers per "defun org-babel-execute" | |
| 705 | in ob-*.el */ | |
| 706 | pre.src-cpp:before { | |
| 707 | content: "C++"; | |
| 708 | } | |
| 709 | pre.src-abc:before { | |
| 710 | content: "ABC"; | |
| 711 | } | |
| 712 | pre.src-coq:before { | |
| 713 | content: "Coq"; | |
| 714 | } | |
| 715 | pre.src-groovy:before { | |
| 716 | content: "Groovy"; | |
| 717 | } | |
| 718 | /* additional language identifiers from org-babel-shell-names in | |
| 719 | ob-shell.el: ob-shell is the only babel language using a lambda to put | |
| 720 | the execution function name together. */ | |
| 721 | pre.src-bash:before { | |
| 722 | content: "bash"; | |
| 723 | } | |
| 724 | pre.src-csh:before { | |
| 725 | content: "csh"; | |
| 726 | } | |
| 727 | pre.src-ash:before { | |
| 728 | content: "ash"; | |
| 729 | } | |
| 730 | pre.src-dash:before { | |
| 731 | content: "dash"; | |
| 732 | } | |
| 733 | pre.src-ksh:before { | |
| 734 | content: "ksh"; | |
| 735 | } | |
| 736 | pre.src-mksh:before { | |
| 737 | content: "mksh"; | |
| 738 | } | |
| 739 | pre.src-posh:before { | |
| 740 | content: "posh"; | |
| 741 | } | |
| 742 | /* Additional Emacs modes also supported by the LaTeX listings package */ | |
| 743 | pre.src-ada:before { | |
| 744 | content: "Ada"; | |
| 745 | } | |
| 746 | pre.src-asm:before { | |
| 747 | content: "Assembler"; | |
| 748 | } | |
| 749 | pre.src-caml:before { | |
| 750 | content: "Caml"; | |
| 751 | } | |
| 752 | pre.src-delphi:before { | |
| 753 | content: "Delphi"; | |
| 754 | } | |
| 755 | pre.src-html:before { | |
| 756 | content: "HTML"; | |
| 757 | } | |
| 758 | pre.src-idl:before { | |
| 759 | content: "IDL"; | |
| 760 | } | |
| 761 | pre.src-mercury:before { | |
| 762 | content: "Mercury"; | |
| 763 | } | |
| 764 | pre.src-metapost:before { | |
| 765 | content: "MetaPost"; | |
| 766 | } | |
| 767 | pre.src-modula-2:before { | |
| 768 | content: "Modula-2"; | |
| 769 | } | |
| 770 | pre.src-pascal:before { | |
| 771 | content: "Pascal"; | |
| 772 | } | |
| 773 | pre.src-ps:before { | |
| 774 | content: "PostScript"; | |
| 775 | } | |
| 776 | pre.src-prolog:before { | |
| 777 | content: "Prolog"; | |
| 778 | } | |
| 779 | pre.src-simula:before { | |
| 780 | content: "Simula"; | |
| 781 | } | |
| 782 | pre.src-tcl:before { | |
| 783 | content: "tcl"; | |
| 784 | } | |
| 785 | pre.src-tex:before { | |
| 786 | content: "TeX"; | |
| 787 | } | |
| 788 | pre.src-plain-tex:before { | |
| 789 | content: "Plain TeX"; | |
| 790 | } | |
| 791 | pre.src-verilog:before { | |
| 792 | content: "Verilog"; | |
| 793 | } | |
| 794 | pre.src-vhdl:before { | |
| 795 | content: "VHDL"; | |
| 796 | } | |
| 797 | pre.src-xml:before { | |
| 798 | content: "XML"; | |
| 799 | } | |
| 800 | pre.src-nxml:before { | |
| 801 | content: "XML"; | |
| 802 | } | |
| 803 | /* add a generic configuration mode; LaTeX export needs an additional | |
| 804 | (add-to-list 'org-latex-listings-langs '(conf " ")) in .emacs */ | |
| 805 | pre.src-conf:before { | |
| 806 | content: "Configuration File"; | |
| 807 | } | |
static/styles.min.css deleted −1
| @@ -1 +0,0 @@ | ||
| 1 | /*!normalize.css v8.0.1 | MIT License | github.com/necolas/normalize.css*/html{line-height:1.15;-webkit-text-size-adjust:100%}body{margin:0}main{display:block}h1{font-size:2em;margin:.67em 0}hr{box-sizing:content-box;height:0;overflow:visible}pre{font-family:monospace,monospace;font-size:1em}a{background-color:initial}abbr[title]{border-bottom:none;text-decoration:underline;text-decoration:underline dotted}b,strong{font-weight:bolder}code,kbd,samp{font-family:monospace,monospace;font-size:1em}small{font-size:80%}sub,sup{font-size:75%;line-height:0;position:relative;vertical-align:baseline}sub{bottom:-.25em}sup{top:-.5em}img{border-style:none}button,input,optgroup,select,textarea{font-family:inherit;font-size:100%;line-height:1.15;margin:0}button,input{overflow:visible}button,select{text-transform:none}button,[type=button],[type=reset],[type=submit]{-webkit-appearance:button}button::-moz-focus-inner,[type=button]::-moz-focus-inner,[type=reset]::-moz-focus-inner,[type=submit]::-moz-focus-inner{border-style:none;padding:0}button:-moz-focusring,[type=button]:-moz-focusring,[type=reset]:-moz-focusring,[type=submit]:-moz-focusring{outline:1px dotted ButtonText}fieldset{padding:.35em .75em .625em}legend{box-sizing:border-box;color:inherit;display:table;max-width:100%;padding:0;white-space:normal}progress{vertical-align:baseline}textarea{overflow:auto}[type=checkbox],[type=radio]{box-sizing:border-box;padding:0}[type=number]::-webkit-inner-spin-button,[type=number]::-webkit-outer-spin-button{height:auto}[type=search]{-webkit-appearance:textfield;outline-offset:-2px}[type=search]::-webkit-search-decoration{-webkit-appearance:none}::-webkit-file-upload-button{-webkit-appearance:button;font:inherit}details{display:block}summary{display:list-item}template{display:none}[hidden]{display:none}:root{--bg:#fff;--bg-bright:#eee;--fg:#111;--link:#00f;--code:#f00}@media(prefers-reduced-motion:no-preference){:root{scroll-behavior:smooth}}body{background-color:var(--bg);color:var(--fg);font-family:-apple-system,BlinkMacSystemFont,avenir next,avenir,segoe ui,helvetica neue,helvetica,Cantarell,Ubuntu,roboto,noto,arial,sans-serif;font-size:1rem;line-height:1.5;max-width:45em;margin:0 auto;padding:0 1rem}.site-nav,footer{border-color:var(--fg)}footer{border-top:1px dotted;padding-top:1rem;margin:1rem 0}footer p{margin:0}.site-nav{border-bottom:1px dotted}.site-nav ul{list-style-type:none;display:flex;align-items:center;padding:0}.site-nav ul li{margin-right:.5rem}h1,h2,h3,h4{color:var(--fg)}a,a:visited{color:var(--link);text-decoration:none}a:hover{text-decoration:underline}img{width:100%}table{border-collapse:collapse;color:var(--fg);border-color:var(--bg-bright);font-family:Menlo,Consolas,Monaco,Liberation Mono,Lucida Console,monospace}thead,th,tr,td{border:1px solid var(--bg-bright);padding:.25rem}pre>code,time,code{font-family:Menlo,Consolas,Monaco,Liberation Mono,Lucida Console,monospace;font-size:1rem}pre{background-color:var(--bg-bright)!important;border-radius:5px;margin:.5rem 0;padding:.5rem;overflow-x:auto}:not(pre)>code{color:var(--code);font-family:inherit}aside{background-color:var(--bg-bright);padding:1rem}blockquote{background-color:var(--bg-bright);border-left:10px solid var(--link);border-radius:5px;margin:1rem 0;padding:.5rem 1rem}blockquote p{margin:0}.post{display:flex}.post time{flex-shrink:0;margin-right:.5rem}.post-metadata{border:1px dotted var(--fg);border-top:none;padding:1rem}.post-metadata h1{margin:0}.post-metadata p{margin:0}details{margin-top:1rem}summary{font-weight:700}.footnote-definition{display:flex;justify-content:flex-start;align-items:top;margin:1rem 0}.footnote-definition sup{font-size:inherit;top:0;line-height:inherit;padding-right:.5rem}.footnote-definition sup::after{content:"."}.footnote-definition p{display:inline-block;margin:0}@media(prefers-color-scheme:dark){:root{--bg:#111111;--bg-bright:#2a2a2a;--fg:#c9c9c9;--link:#f07178;--code:#ffb454}} | |
| \ No newline at end of file | ||
static/syntax-theme-dark.css added +280
| @@ -0,0 +1,280 @@ | ||
| 1 | /* | |
| 2 | * theme "ayu" generated by syntect | |
| 3 | */ | |
| 4 | ||
| 5 | .z-code { | |
| 6 | color: #bfbab0; | |
| 7 | background-color: #0f1419; | |
| 8 | } | |
| 9 | ||
| 10 | .z-comment, .z-punctuation.z-definition.z-comment { | |
| 11 | color: #5c6773; | |
| 12 | font-style: italic; | |
| 13 | } | |
| 14 | .z-variable { | |
| 15 | color: #bfbab0; | |
| 16 | } | |
| 17 | .z-string, .z-constant.z-other.z-symbol { | |
| 18 | color: #c2d94c; | |
| 19 | } | |
| 20 | .z-constant.z-numeric { | |
| 21 | color: #f29718; | |
| 22 | } | |
| 23 | .z-string.z-regexp, .z-constant.z-character.z-escape { | |
| 24 | color: #95e6cb; | |
| 25 | } | |
| 26 | .z-constant.z-language { | |
| 27 | color: #f29718; | |
| 28 | } | |
| 29 | .z-constant.z-character, .z-constant.z-other { | |
| 30 | color: #f29718; | |
| 31 | } | |
| 32 | .z-variable.z-member { | |
| 33 | color: #ec5f67; | |
| 34 | } | |
| 35 | .z-keyword, .z-keyword.z-operator.z-word { | |
| 36 | color: #ff7733; | |
| 37 | } | |
| 38 | .z-keyword.z-operator { | |
| 39 | color: #f29668; | |
| 40 | } | |
| 41 | .z-punctuation.z-separator, .z-punctuation.z-terminator { | |
| 42 | color: #bfbab0; | |
| 43 | } | |
| 44 | .z-punctuation.z-section { | |
| 45 | color: #bfbab0; | |
| 46 | } | |
| 47 | .z-punctuation.z-accessor { | |
| 48 | color: #f29668; | |
| 49 | } | |
| 50 | .z-punctuation.z-definition.z-annotation { | |
| 51 | color: #bfbab0; | |
| 52 | } | |
| 53 | .z-variable.z-other.z-dollar.z-only.z-js, .z-variable.z-other.z-object.z-dollar.z-only.z-js, .z-variable.z-type.z-dollar.z-only.z-js, .z-support.z-class.z-dollar.z-only.z-js { | |
| 54 | color: #e6b673; | |
| 55 | } | |
| 56 | .z-storage { | |
| 57 | color: #ff7733; | |
| 58 | } | |
| 59 | .z-storage.z-type { | |
| 60 | color: #ff7733; | |
| 61 | } | |
| 62 | .z-entity.z-name.z-function { | |
| 63 | color: #ffb454; | |
| 64 | } | |
| 65 | .z-entity.z-name, .z-entity.z-name.z-tag, .z-entity.z-name.z-label) { | |
| 66 | color: #59c2ff; | |
| 67 | } | |
| 68 | .z-entity.z-other.z-inherited-class { | |
| 69 | color: #59c2ff; | |
| 70 | text-decoration: underline; | |
| 71 | } | |
| 72 | .z-variable.z-parameter { | |
| 73 | color: #f29718; | |
| 74 | } | |
| 75 | .z-variable.z-language { | |
| 76 | color: #39bae6; | |
| 77 | font-style: italic; | |
| 78 | } | |
| 79 | .z-entity.z-name.z-tag, .z-meta.z-tag.z-sgml { | |
| 80 | color: #39bae6; | |
| 81 | } | |
| 82 | .z-punctuation.z-definition.z-tag.z-end, .z-punctuation.z-definition.z-tag.z-begin, .z-punctuation.z-definition.z-tag { | |
| 83 | color: #39bae6; | |
| 84 | } | |
| 85 | .z-entity.z-other.z-attribute-name { | |
| 86 | color: #ffb454; | |
| 87 | } | |
| 88 | .z-variable.z-function, .z-variable.z-annotation { | |
| 89 | color: #ffb454; | |
| 90 | } | |
| 91 | .z-support.z-function, .z-support.z-macro { | |
| 92 | color: #f07178; | |
| 93 | } | |
| 94 | .z-support.z-constant { | |
| 95 | color: #f29668; | |
| 96 | font-style: italic; | |
| 97 | } | |
| 98 | .z-support.z-type, .z-support.z-class { | |
| 99 | color: #39bae6; | |
| 100 | font-style: italic; | |
| 101 | } | |
| 102 | .z-invalid { | |
| 103 | color: #ff3333; | |
| 104 | } | |
| 105 | .z-invalid.z-deprecated { | |
| 106 | color: #ffffff; | |
| 107 | background-color: #ff7733; | |
| 108 | } | |
| 109 | .z-meta.z-diff, .z-meta.z-diff.z-header { | |
| 110 | color: #c594c5; | |
| 111 | } | |
| 112 | .z-source.z-ruby .z-variable.z-other.z-readwrite { | |
| 113 | color: #ffb454; | |
| 114 | } | |
| 115 | .z-source.z-css .z-entity.z-name.z-tag, .z-source.z-sass .z-entity.z-name.z-tag, .z-source.z-scss .z-entity.z-name.z-tag, .z-source.z-less .z-entity.z-name.z-tag, .z-source.z-stylus .z-entity.z-name.z-tag { | |
| 116 | color: #59c2ff; | |
| 117 | } | |
| 118 | .z-source.z-css .z-support.z-type, .z-source.z-sass .z-support.z-type, .z-source.z-scss .z-support.z-type, .z-source.z-less .z-support.z-type, .z-source.z-stylus .z-support.z-type { | |
| 119 | color: #5c6773; | |
| 120 | } | |
| 121 | .z-support.z-type.z-property-name { | |
| 122 | color: #39bae6; | |
| 123 | } | |
| 124 | .z-constant.z-numeric.z-line-number.z-find-in-files { | |
| 125 | color: #5c6773; | |
| 126 | } | |
| 127 | .z-constant.z-numeric.z-line-number.z-match { | |
| 128 | color: #ff7733; | |
| 129 | } | |
| 130 | .z-entity.z-name.z-filename.z-find-in-files { | |
| 131 | color: #c2d94c; | |
| 132 | } | |
| 133 | .z-message.z-error { | |
| 134 | color: #ff3333; | |
| 135 | } | |
| 136 | .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 137 | color: #39bae6; | |
| 138 | } | |
| 139 | .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 140 | color: #39bae6; | |
| 141 | } | |
| 142 | .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 143 | color: #39bae6; | |
| 144 | } | |
| 145 | .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 146 | color: #39bae6; | |
| 147 | } | |
| 148 | .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 149 | color: #39bae6; | |
| 150 | } | |
| 151 | .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 152 | color: #39bae6; | |
| 153 | } | |
| 154 | .z-source.z-json .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 155 | color: #39bae6; | |
| 156 | } | |
| 157 | .z-source.z-json .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 158 | color: #39bae6; | |
| 159 | } | |
| 160 | .z-source.z-json .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json, .z-source.z-json .z-meta.z-structure.z-dictionary.z-json .z-punctuation.z-definition.z-string { | |
| 161 | color: #39bae6; | |
| 162 | } | |
| 163 | .z-markup.z-heading { | |
| 164 | color: #ff7733; | |
| 165 | font-weight: bold; | |
| 166 | } | |
| 167 | .z-string.z-other.z-link, .z-markup.z-underline.z-link { | |
| 168 | color: #95e6cb; | |
| 169 | text-decoration: underline; | |
| 170 | font-style: italic; | |
| 171 | } | |
| 172 | .z-punctuation.z-definition.z-image { | |
| 173 | color: #ffb454; | |
| 174 | } | |
| 175 | .z-markup.z-italic { | |
| 176 | color: #f07178; | |
| 177 | font-style: italic; | |
| 178 | } | |
| 179 | .z-markup.z-bold { | |
| 180 | color: #f07178; | |
| 181 | font-weight: bold; | |
| 182 | } | |
| 183 | .z-markup.z-italic .z-markup.z-bold, .z-markup.z-bold .z-markup.z-italic { | |
| 184 | font-weight: bold; | |
| 185 | font-style: italic; | |
| 186 | } | |
| 187 | .z-markup.z-raw { | |
| 188 | background-color: #bfbab0; | |
| 189 | } | |
| 190 | .z-markup.z-raw.z-inline { | |
| 191 | background-color: #bfbab0; | |
| 192 | } | |
| 193 | .z-meta.z-separator { | |
| 194 | color: #5c6773; | |
| 195 | background-color: #bfbab0; | |
| 196 | font-weight: bold; | |
| 197 | } | |
| 198 | .z-markup.z-quote { | |
| 199 | color: #f29718; | |
| 200 | font-style: italic; | |
| 201 | } | |
| 202 | .z-markup.z-list.z-numbered.z-bullet, .z-markup.z-list .z-punctuation.z-definition.z-list_item { | |
| 203 | color: #95e6cb; | |
| 204 | } | |
| 205 | .z-markup.z-inserted { | |
| 206 | color: #c2d94c; | |
| 207 | } | |
| 208 | .z-markup.z-changed { | |
| 209 | color: #39bae6; | |
| 210 | } | |
| 211 | .z-markup.z-deleted { | |
| 212 | color: #f07178; | |
| 213 | } | |
| 214 | .z-markup.z-strike { | |
| 215 | color: #e6b673; | |
| 216 | } | |
| 217 | .z-markup.z-table { | |
| 218 | color: #39bae6; | |
| 219 | background-color: #bfbab0; | |
| 220 | } | |
| 221 | .z-text.z-html.z-markdown .z-markup.z-raw.z-inline { | |
| 222 | color: #f29668; | |
| 223 | } | |
| 224 | .z-text.z-html.z-markdown .z-meta.z-dummy.z-line-break { | |
| 225 | color: #5c6773; | |
| 226 | } | |
| 227 | .z-markup.z-raw.z-block.z-fenced.z-markdown { | |
| 228 | color: #bfbab0; | |
| 229 | background-color: #bfbab0; | |
| 230 | } | |
| 231 | .z-punctuation.z-definition.z-fenced.z-markdown, .z-variable.z-language.z-fenced.z-markdown { | |
| 232 | color: #5c6773; | |
| 233 | background-color: #bfbab0; | |
| 234 | } | |
| 235 | .z-variable.z-language.z-fenced.z-markdown { | |
| 236 | color: #5c6773; | |
| 237 | } | |
| 238 | .z-markup.z-inserted.z-git_gutter { | |
| 239 | color: #c2d94c; | |
| 240 | } | |
| 241 | .z-markup.z-changed.z-git_gutter { | |
| 242 | color: #39bae6; | |
| 243 | } | |
| 244 | .z-markup.z-deleted.z-git_gutter { | |
| 245 | color: #ff3333; | |
| 246 | } | |
| 247 | .z-markup.z-ignored.z-git_gutter { | |
| 248 | color: #20272c; | |
| 249 | } | |
| 250 | .z-markup.z-untracked.z-git_gutter { | |
| 251 | color: #20272c; | |
| 252 | } | |
| 253 | .z-gutter_color { | |
| 254 | color: #ffffff; | |
| 255 | } | |
| 256 | .z-acejump.z-label.z-blue { | |
| 257 | color: #ffffff; | |
| 258 | background-color: #39bae6; | |
| 259 | } | |
| 260 | .z-acejump.z-label.z-green { | |
| 261 | color: #ffffff; | |
| 262 | background-color: #c2d94c; | |
| 263 | } | |
| 264 | .z-acejump.z-label.z-orange { | |
| 265 | color: #ffffff; | |
| 266 | background-color: #ff7733; | |
| 267 | } | |
| 268 | .z-acejump.z-label.z-purple { | |
| 269 | color: #ffffff; | |
| 270 | background-color: #f07178; | |
| 271 | } | |
| 272 | .z-sublimelinter.z-mark.z-warning { | |
| 273 | color: #39bae6; | |
| 274 | } | |
| 275 | .z-sublimelinter.z-gutter-mark { | |
| 276 | color: #ffffff; | |
| 277 | } | |
| 278 | .z-sublimelinter.z-mark.z-error { | |
| 279 | color: #ff3333; | |
| 280 | } | |
static/syntax-theme-light.css added +407
| @@ -0,0 +1,407 @@ | ||
| 1 | /* | |
| 2 | * theme "GitHub" generated by syntect | |
| 3 | */ | |
| 4 | ||
| 5 | .z-code { | |
| 6 | color: #323232; | |
| 7 | background-color: #ffffff; | |
| 8 | } | |
| 9 | ||
| 10 | .z-comment { | |
| 11 | color: #969896; | |
| 12 | font-style: italic; | |
| 13 | } | |
| 14 | .z-string { | |
| 15 | color: #183691; | |
| 16 | } | |
| 17 | .z-regexp-operator { | |
| 18 | color: #a71d5d; | |
| 19 | } | |
| 20 | .z-string.z-regexp.z-characterclass .z-punctuation.z-definition.z-string.z-begin, .z-string.z-regexp.z-characterclass .z-punctuation.z-definition.z-string.z-end { | |
| 21 | color: #a71d5d; | |
| 22 | } | |
| 23 | .z-constant.z-numeric { | |
| 24 | color: #0086b3; | |
| 25 | } | |
| 26 | .z-constant.z-language { | |
| 27 | color: #0086b3; | |
| 28 | } | |
| 29 | .z-constant.z-character, .z-constant.z-other, .z-variable.z-other.z-constant { | |
| 30 | color: #0086b3; | |
| 31 | } | |
| 32 | .z-variable { | |
| 33 | color: #323232; | |
| 34 | } | |
| 35 | .z-keyword { | |
| 36 | color: #a71d5d; | |
| 37 | font-weight: bold; | |
| 38 | } | |
| 39 | .z-bitwise-operator { | |
| 40 | color: #a71d5d; | |
| 41 | font-weight: bold; | |
| 42 | } | |
| 43 | .z-storage { | |
| 44 | color: #a71d5d; | |
| 45 | font-weight: bold; | |
| 46 | } | |
| 47 | .z-storage.z-type { | |
| 48 | color: #a71d5d; | |
| 49 | font-weight: bold; | |
| 50 | } | |
| 51 | .z-entity.z-name.z-class { | |
| 52 | color: #0086b3; | |
| 53 | } | |
| 54 | .z-entity.z-other.z-inherited-class { | |
| 55 | color: #0086b3; | |
| 56 | } | |
| 57 | .z-entity.z-name.z-function { | |
| 58 | color: #795da3; | |
| 59 | font-weight: bold; | |
| 60 | } | |
| 61 | .z-variable.z-parameter { | |
| 62 | color: #323232; | |
| 63 | } | |
| 64 | .z-entity.z-name.z-tag { | |
| 65 | color: #63a35c; | |
| 66 | } | |
| 67 | .z-entity.z-other.z-attribute-name { | |
| 68 | color: #795da3; | |
| 69 | } | |
| 70 | .z-support.z-function { | |
| 71 | color: #62a35c; | |
| 72 | } | |
| 73 | .z-support.z-constant { | |
| 74 | color: #0086b3; | |
| 75 | } | |
| 76 | .z-support.z-type, .z-support.z-class { | |
| 77 | color: #0086b3; | |
| 78 | } | |
| 79 | .z-support.z-other.z-variable { | |
| 80 | color: #323232; | |
| 81 | } | |
| 82 | .z-invalid, .z-invalid.z-illegal, .z-invalid.z-deprecated { | |
| 83 | color: #b52a1d; | |
| 84 | background-color: #f5f5f5; | |
| 85 | font-weight: bold; | |
| 86 | } | |
| 87 | .z-entity.z-name.z-filename.z-find-in-files { | |
| 88 | color: #323232; | |
| 89 | font-weight: bold; | |
| 90 | } | |
| 91 | .z-constant.z-numeric.z-line-number.z-find-in-files, .z-constant.z-numeric.z-line-number.z-match.z-find-in-files { | |
| 92 | color: #b3b3b3; | |
| 93 | } | |
| 94 | .z-meta.z-diff.z-header { | |
| 95 | color: #969896; | |
| 96 | background-color: #ffffff; | |
| 97 | font-style: italic; | |
| 98 | } | |
| 99 | .z-meta.z-diff.z-header .z-punctuation.z-definition.z-from-file.z-diff { | |
| 100 | color: #bd2c00; | |
| 101 | background-color: #ffecec; | |
| 102 | font-weight: bold; | |
| 103 | font-style: italic; | |
| 104 | } | |
| 105 | .z-meta.z-diff.z-header .z-punctuation.z-definition.z-to-file.z-diff { | |
| 106 | color: #55a532; | |
| 107 | background-color: #eaffea; | |
| 108 | font-weight: bold; | |
| 109 | font-style: italic; | |
| 110 | } | |
| 111 | .z-meta.z-diff.z-range { | |
| 112 | color: #969896; | |
| 113 | font-weight: bold; | |
| 114 | font-style: italic; | |
| 115 | } | |
| 116 | .z-markup.z-deleted { | |
| 117 | background-color: #ffecec; | |
| 118 | } | |
| 119 | .z-markup.z-deleted .z-punctuation.z-definition.z-inserted { | |
| 120 | color: #bd2c00; | |
| 121 | font-weight: bold; | |
| 122 | } | |
| 123 | .z-markup.z-inserted { | |
| 124 | background-color: #eaffea; | |
| 125 | } | |
| 126 | .z-markup.z-inserted .z-punctuation.z-definition.z-inserted { | |
| 127 | color: #55a532; | |
| 128 | font-weight: bold; | |
| 129 | } | |
| 130 | .z-markup.z-deleted.z-git_gutter { | |
| 131 | color: #bd2c00; | |
| 132 | } | |
| 133 | .z-markup.z-inserted.z-git_gutter { | |
| 134 | color: #55a532; | |
| 135 | } | |
| 136 | .z-markup.z-changed.z-git_gutter { | |
| 137 | color: #0086b3; | |
| 138 | } | |
| 139 | .z-markup.z-ignored.z-git_gutter { | |
| 140 | color: #b3b3b3; | |
| 141 | } | |
| 142 | .z-markup.z-untracked.z-git_gutter { | |
| 143 | color: #b3b3b3; | |
| 144 | } | |
| 145 | .z-source.z-css .z-punctuation.z-definition.z-entity { | |
| 146 | color: #323232; | |
| 147 | } | |
| 148 | .z-source.z-css .z-entity.z-other.z-attribute-name.z-pseudo-class, .z-source.z-css .z-entity.z-other.z-attribute-name.z-pseudo-element { | |
| 149 | color: #a71d5d; | |
| 150 | } | |
| 151 | .z-source.z-css .z-meta.z-value, .z-source.z-css .z-support.z-constant, .z-source.z-css .z-support.z-function { | |
| 152 | color: #323232; | |
| 153 | } | |
| 154 | .z-source.z-css .z-constant.z-other.z-color { | |
| 155 | color: #ed6a43; | |
| 156 | } | |
| 157 | .z-source.z-scss .z-punctuation.z-definition.z-entity { | |
| 158 | color: #323232; | |
| 159 | } | |
| 160 | .z-source.z-scss .z-entity.z-other.z-attribute-name.z-pseudo-class, .z-source.z-scss .z-entity.z-other.z-attribute-name.z-pseudo-element { | |
| 161 | color: #a71d5d; | |
| 162 | } | |
| 163 | .z-source.z-scss .z-support.z-constant.z-property-value, .z-source.z-scss .z-support.z-function { | |
| 164 | color: #323232; | |
| 165 | } | |
| 166 | .z-source.z-scss .z-variable { | |
| 167 | color: #a71d5d; | |
| 168 | } | |
| 169 | .z-variable.z-language.z-this.z-js { | |
| 170 | color: #ed6a43; | |
| 171 | } | |
| 172 | .z-source.z-js .z-entity.z-name.z-function { | |
| 173 | color: #323232; | |
| 174 | } | |
| 175 | .z-source.z-js .z-meta.z-function .z-entity.z-name.z-function, .z-source.z-js .z-entity.z-name.z-function .z-meta.z-function { | |
| 176 | color: #795da3; | |
| 177 | font-weight: bold; | |
| 178 | } | |
| 179 | .z-entity.z-name.z-type.z-new.z-js { | |
| 180 | color: #795da3; | |
| 181 | } | |
| 182 | .z-variable.z-language.z-prototype.z-js { | |
| 183 | color: #0086b3; | |
| 184 | } | |
| 185 | .z-source.z-js .z-support.z-function { | |
| 186 | color: #0086b3; | |
| 187 | } | |
| 188 | .z-support.z-type.z-object.z-console.z-js { | |
| 189 | color: #795da3; | |
| 190 | } | |
| 191 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 192 | color: #183691; | |
| 193 | font-weight: bold; | |
| 194 | } | |
| 195 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 196 | color: #323232; | |
| 197 | } | |
| 198 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 199 | color: #183691; | |
| 200 | font-weight: bold; | |
| 201 | } | |
| 202 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 203 | color: #323232; | |
| 204 | } | |
| 205 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 206 | color: #183691; | |
| 207 | font-weight: bold; | |
| 208 | } | |
| 209 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 210 | color: #323232; | |
| 211 | } | |
| 212 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 213 | color: #183691; | |
| 214 | font-weight: bold; | |
| 215 | } | |
| 216 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 217 | color: #323232; | |
| 218 | } | |
| 219 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 220 | color: #183691; | |
| 221 | font-weight: bold; | |
| 222 | } | |
| 223 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 224 | color: #323232; | |
| 225 | } | |
| 226 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 227 | color: #183691; | |
| 228 | font-weight: bold; | |
| 229 | } | |
| 230 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 231 | color: #323232; | |
| 232 | } | |
| 233 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 234 | color: #183691; | |
| 235 | font-weight: bold; | |
| 236 | } | |
| 237 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 238 | color: #323232; | |
| 239 | } | |
| 240 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 241 | color: #183691; | |
| 242 | font-weight: bold; | |
| 243 | } | |
| 244 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 245 | color: #323232; | |
| 246 | } | |
| 247 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 248 | color: #183691; | |
| 249 | font-weight: bold; | |
| 250 | } | |
| 251 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 252 | color: #323232; | |
| 253 | } | |
| 254 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 255 | color: #183691; | |
| 256 | font-weight: bold; | |
| 257 | } | |
| 258 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 259 | color: #323232; | |
| 260 | } | |
| 261 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 262 | color: #183691; | |
| 263 | font-weight: bold; | |
| 264 | } | |
| 265 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 266 | color: #323232; | |
| 267 | } | |
| 268 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 269 | color: #183691; | |
| 270 | font-weight: bold; | |
| 271 | } | |
| 272 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 273 | color: #323232; | |
| 274 | } | |
| 275 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 276 | color: #183691; | |
| 277 | font-weight: bold; | |
| 278 | } | |
| 279 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 280 | color: #323232; | |
| 281 | } | |
| 282 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 283 | color: #183691; | |
| 284 | font-weight: bold; | |
| 285 | } | |
| 286 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 287 | color: #323232; | |
| 288 | } | |
| 289 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 290 | color: #183691; | |
| 291 | font-weight: bold; | |
| 292 | } | |
| 293 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 294 | color: #323232; | |
| 295 | } | |
| 296 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 297 | color: #183691; | |
| 298 | font-weight: bold; | |
| 299 | } | |
| 300 | .z-meta .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 301 | color: #323232; | |
| 302 | } | |
| 303 | .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 304 | color: #183691; | |
| 305 | font-weight: bold; | |
| 306 | } | |
| 307 | .z-meta .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 308 | color: #323232; | |
| 309 | } | |
| 310 | .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 311 | color: #183691; | |
| 312 | font-weight: bold; | |
| 313 | } | |
| 314 | .z-meta .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 315 | color: #323232; | |
| 316 | } | |
| 317 | .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 318 | color: #183691; | |
| 319 | font-weight: bold; | |
| 320 | } | |
| 321 | .z-meta .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 322 | color: #323232; | |
| 323 | } | |
| 324 | .z-meta .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 325 | color: #183691; | |
| 326 | font-weight: bold; | |
| 327 | } | |
| 328 | .z-meta .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 329 | color: #323232; | |
| 330 | } | |
| 331 | .z-meta.z-structure.z-dictionary.z-json .z-string.z-quoted.z-double.z-json { | |
| 332 | color: #183691; | |
| 333 | font-weight: bold; | |
| 334 | } | |
| 335 | .z-meta.z-structure.z-dictionary.z-json .z-meta.z-structure.z-dictionary.z-value.z-json .z-string.z-quoted.z-double.z-json { | |
| 336 | color: #323232; | |
| 337 | } | |
| 338 | .z-source.z-python .z-keyword { | |
| 339 | font-weight: bold; | |
| 340 | } | |
| 341 | .z-source.z-python .z-storage { | |
| 342 | font-weight: bold; | |
| 343 | } | |
| 344 | .z-source.z-python .z-storage.z-type { | |
| 345 | font-weight: bold; | |
| 346 | } | |
| 347 | .z-source.z-python .z-entity.z-name.z-function { | |
| 348 | color: #323232; | |
| 349 | font-weight: bold; | |
| 350 | } | |
| 351 | .z-source.z-php .z-entity.z-name.z-type.z-class { | |
| 352 | color: #323232; | |
| 353 | font-weight: bold; | |
| 354 | } | |
| 355 | .z-variable.z-language.z-ruby { | |
| 356 | color: #ed6a43; | |
| 357 | } | |
| 358 | .z-entity.z-name.z-type.z-module.z-ruby { | |
| 359 | color: #795da3; | |
| 360 | font-weight: bold; | |
| 361 | } | |
| 362 | .z-entity.z-name.z-type.z-class.z-ruby { | |
| 363 | color: #795da3; | |
| 364 | font-weight: bold; | |
| 365 | } | |
| 366 | .z-entity.z-other.z-inherited-class.z-ruby { | |
| 367 | color: #795da3; | |
| 368 | font-weight: bold; | |
| 369 | } | |
| 370 | .z-punctuation.z-definition.z-heading.z-markdown, .z-punctuation.z-definition.z-italic.z-markdown, .z-punctuation.z-definition.z-bold.z-markdown, .z-punctuation.z-definition.z-string.z-begin.z-markdown, .z-punctuation.z-definition.z-string.z-end.z-markdown, .z-punctuation.z-definition.z-metadata.z-markdown, .z-punctuation.z-definition.z-link.z-markdown, .z-punctuation.z-definition.z-blockquote.z-markdown, .z-punctuation.z-definition.z-raw.z-markdown { | |
| 371 | color: #a71d5d; | |
| 372 | } | |
| 373 | .z-text.z-html.z-markdown .z-meta.z-separator { | |
| 374 | color: #b3b3b3; | |
| 375 | } | |
| 376 | .z-text.z-html.z-markdown .z-markup.z-heading { | |
| 377 | font-weight: bold; | |
| 378 | } | |
| 379 | .z-text.z-html.z-markdown .z-markup.z-raw.z-block { | |
| 380 | color: #323232; | |
| 381 | } | |
| 382 | .z-text.z-html.z-markdown .z-markup.z-raw.z-inline { | |
| 383 | color: #323232; | |
| 384 | } | |
| 385 | .z-text.z-html.z-markdown .z-meta.z-link, .z-text.z-html.z-markdown .z-meta.z-image { | |
| 386 | color: #4183c4; | |
| 387 | } | |
| 388 | .z-text.z-html.z-markdown .z-markup.z-underline.z-link, .z-text.z-html.z-markdown .z-constant.z-other.z-reference { | |
| 389 | font-style: italic; | |
| 390 | } | |
| 391 | .z-text.z-html.z-markdown .z-markup.z-list { | |
| 392 | color: #ed6a43; | |
| 393 | } | |
| 394 | .z-text.z-html.z-markdown .z-markup.z-bold { | |
| 395 | font-weight: bold; | |
| 396 | } | |
| 397 | .z-text.z-html.z-markdown .z-markup.z-italic { | |
| 398 | font-style: italic; | |
| 399 | } | |
| 400 | .z-text.z-html.z-markdown .z-markup.z-bold .z-markup.z-italic { | |
| 401 | font-weight: bold; | |
| 402 | font-style: italic; | |
| 403 | } | |
| 404 | .z-text.z-html.z-markdown .z-markup.z-italic .z-markup.z-bold { | |
| 405 | font-weight: bold; | |
| 406 | font-style: italic; | |
| 407 | } | |
templates/base.html deleted −48
| @@ -1,48 +0,0 @@ | ||
| 1 | <!doctype html> | |
| 2 | <html lang="en"> | |
| 3 | <head> | |
| 4 | {% block title %} | |
| 5 | <title>cleberg.net</title> | |
| 6 | {% endblock %} | |
| 7 | <meta name="viewport" content="width=device-width, initial-scale=1.0"> | |
| 8 | <meta name="theme-color" content="#111" media="(prefers-color-scheme: dark)"> | |
| 9 | <meta name="theme-color" content="#fff" media="(prefers-color-scheme: light)"> | |
| 10 | {% if page %} | |
| 11 | {% if page.description %} | |
| 12 | <meta name="description" content="{{ page.description }}"> | |
| 13 | {% elif config.description %} | |
| 14 | <meta name="description" content="{{ config.description }}"> | |
| 15 | {% endif %} | |
| 16 | {% elif config.description %} | |
| 17 | <meta name="description" content="{{ config.description }}" /> | |
| 18 | {% endif %} | |
| 19 | ||
| 20 | {% block rss %} | |
| 21 | <link rel="alternate" type="application/atom+xml" title="RSS" href="{{ get_url(path="atom.xml", trailing_slash=false) }}"> | |
| 22 | {% endblock %} | |
| 23 | ||
| 24 | {% block css %} | |
| 25 | <link rel="stylesheet" href="/styles.min.css"> | |
| 26 | {% endblock css %} | |
| 27 | ||
| 28 | {% block extra_head %}{% endblock extra_head %} | |
| 29 | </head> | |
| 30 | <body> | |
| 31 | <nav class="site-nav" aria-label="site-nav" role="navigation"> | |
| 32 | <ul> | |
| 33 | <li><a href="/">Home</a></li> | |
| 34 | <li><a href="/blog/">Blog</a></li> | |
| 35 | <li><a href="/services/">Services</a></li> | |
| 36 | <li><a href="/wiki/">Wiki</a></li> | |
| 37 | </ul> | |
| 38 | </nav> | |
| 39 | ||
| 40 | <main>{% block content %}{% endblock content %}</main> | |
| 41 | ||
| 42 | <footer> | |
| 43 | <p>Last build: {{ now() | date(format="%Y-%m-%d %H:%M:%S") }}</p> | |
| 44 | <p><a href="https://git.cleberg.net/cleberg.net.git" target="_blank" rel="noopener">Source Code</a></p> | |
| 45 | <p><a href="/atom.xml">Atom RSS Feed</a></p> | |
| 46 | </footer> | |
| 47 | </body> | |
| 48 | </html> | |
templates/index.html deleted −40
| @@ -1,40 +0,0 @@ | ||
| 1 | {% extends "base.html" %} | |
| 2 | ||
| 3 | {% block content %} | |
| 4 | <section> | |
| 5 | <h1>cleberg.net</h1> | |
| 6 | <blockquote>Do AIs dream in electric sheep?<br>He hoped it had nanosecond nightmares.</blockquote> | |
| 7 | </section> | |
| 8 | <section> | |
| 9 | <h2>Recent Blog Posts</h2> | |
| 10 | {% set section = get_section(path="blog/_index.md") %} | |
| 11 | {% set i = 0 %} | |
| 12 | {% for page in section.pages %} | |
| 13 | {% if i < 3%} | |
| 14 | {% set_global i = i + 1%} | |
| 15 | <div class="post"> | |
| 16 | <time datetime="{{ page.date | date(format='%Y-%m-%d %H:%M:%S') }}">{{ page.date }}</time> | |
| 17 | <a href="/blog/{{ page.slug }}/">{{ page.title }}</a> | |
| 18 | </div> | |
| 19 | {% endif %} | |
| 20 | {% endfor %} | |
| 21 | <br> | |
| 22 | <a href="/blog/">All Posts →</a> | |
| 23 | </section> | |
| 24 | <section> | |
| 25 | <h2>Everything Else</h2> | |
| 26 | <ul> | |
| 27 | <li><a href="/salary/">Salary</a></li> | |
| 28 | <li><a href="/services/">Services</a></li> | |
| 29 | <li><a href="/wiki/">Wiki</a></li> | |
| 30 | </ul> | |
| 31 | </section> | |
| 32 | <section> | |
| 33 | <h2>Contact</h2> | |
| 34 | <ul> | |
| 35 | <li>hello [at] cleberg.net (<a href="/gpg.txt">GPG</a>)</li> | |
| 36 | <li><a href="https://matrix.to/#/@cyborg:matrix.tchncs.de" target="_blank" rel="noopener">@cyborg:@matrix.tchncs.de</a></li> | |
| 37 | <li><a href="https://git.cleberg.net/cleberg.net.git" target="_blank" rel="noopener">Git</a></li> | |
| 38 | </ul> | |
| 39 | </section> | |
| 40 | {% endblock content %} | |
templates/page.html deleted −48
| @@ -1,48 +0,0 @@ | ||
| 1 | {% extends "base.html" %} | |
| 2 | ||
| 3 | {% block title %} | |
| 4 | <title>{{ page.title }} | cleberg.net</title> | |
| 5 | {% endblock %} | |
| 6 | ||
| 7 | {% block css %} | |
| 8 | <link rel="stylesheet" href="/syntax-theme-dark.css" media="(prefers-color-scheme: dark)"> | |
| 9 | <link rel="stylesheet" href="/syntax-theme-light.css" media="(prefers-color-scheme: light)"> | |
| 10 | <link rel="stylesheet" href="/styles.css"> | |
| 11 | {% endblock css %} | |
| 12 | ||
| 13 | {% block content %} | |
| 14 | <section class="post-metadata"> | |
| 15 | <h1>{{ page.title }}</h1> | |
| 16 | {% if page.date %} | |
| 17 | <p><time datetime="{{ page.date | date(format='%Y-%m-%d %H:%M:%S') }}">{{ page.date }}</time></p> | |
| 18 | {% endif %} | |
| 19 | <p>{{ page.word_count }} words; {{ page.reading_time }} minute(s)</p> | |
| 20 | {% if page.toc %} | |
| 21 | <details open> | |
| 22 | <summary>Table of Contents</summary> | |
| 23 | <nav class="page-nav" aria-label="page-nav" role="navigation"> | |
| 24 | <ul> | |
| 25 | {% for h1 in page.toc %} | |
| 26 | <li> | |
| 27 | <a href="{{ h1.permalink | safe }}">{{ h1.title }}</a> | |
| 28 | {% if h1.children %} | |
| 29 | <ul> | |
| 30 | {% for h2 in h1.children %} | |
| 31 | <li> | |
| 32 | <a href="{{ h2.permalink | safe }}">{{ h2.title }}</a> | |
| 33 | </li> | |
| 34 | {% endfor %} | |
| 35 | </ul> | |
| 36 | {% endif %} | |
| 37 | </li> | |
| 38 | {% endfor %} | |
| 39 | </ul> | |
| 40 | </nav> | |
| 41 | </details> | |
| 42 | {% endif %} | |
| 43 | </section> | |
| 44 | ||
| 45 | <article role="article"> | |
| 46 | {{ page.content | safe }} | |
| 47 | </article> | |
| 48 | {% endblock content %} | |
templates/section.html deleted −18
| @@ -1,18 +0,0 @@ | ||
| 1 | {% extends "base.html" %} | |
| 2 | ||
| 3 | {% block content %} | |
| 4 | <h1>{{ section.title }}</h1> | |
| 5 | <p>Use <code>Ctrl + F</code> to search blog post titles for keywords.</p> | |
| 6 | <p>You can also add the <a href="/atom.xml">Atom RSS Feed</a> to your feed reader.</p> | |
| 7 | {% set post_date = "1970-01-01" | date(format="%Y") %} | |
| 8 | {% for page in section.pages %} | |
| 9 | {% if post_date != page.date | date(format="%Y") %} | |
| 10 | {% set_global post_date = page.date | date(format="%Y") %} | |
| 11 | <h2>{{ post_date }}</h2> | |
| 12 | {% endif %} | |
| 13 | <div class="post"> | |
| 14 | <time datetime="{{ page.date | date(format='%Y-%m-%d %H:%M:%S') }}">{{ page.date }}</time> | |
| 15 | <a href="/blog/{{ page.slug }}/">{{ page.title }}</a> | |
| 16 | </div> | |
| 17 | {% endfor %} | |
| 18 | {% endblock content %} | |
content/wiki/index.md → wiki/index.org renamed +41 −37
| @@ -1,79 +1,83 @@ | ||
| 1 | +++ | |
| 2 | title = "Wiki" | |
| 3 | description = "An informal wiki of sorts." | |
| 4 | +++ | |
| 1 | #+title: Wiki | |
| 2 | #+description: An informal wiki of sorts. | |
| 5 | 3 | |
| 6 | 4 | An informal wiki of sorts. |
| 7 | 5 | |
| 8 | ## Digital Garden | |
| 6 | * Digital Garden | |
| 9 | 7 | |
| 10 | > At times, wilderness is exactly what readers want: a rich collection | |
| 11 | > of resources and links. At times, rigid formality suits readers | |
| 12 | > perfectly, providing precisely the information they want, no more and | |
| 13 | > no less. Indeed, individual hypertexts and Web sites may contain | |
| 14 | > sections that tend toward each extreme. | |
| 8 | #+begin_quote | |
| 9 | At times, wilderness is exactly what readers want: a rich collection of | |
| 10 | resources and links. At times, rigid formality suits readers perfectly, | |
| 11 | providing precisely the information they want, no more and no less. | |
| 12 | Indeed, individual hypertexts and Web sites may contain sections that | |
| 13 | tend toward each extreme. | |
| 15 | 14 | |
| 16 | > Often, however, designers should strive for the comfort, interest, and | |
| 17 | > habitability of parks and gardens: places that invite visitors to | |
| 18 | > remain, and that are designed to engage and delight them, to invite | |
| 19 | > them to linger, to explore, and to reflect. | |
| 15 | #+end_quote | |
| 20 | 16 | |
| 21 | [Hypertext Garden](https://www.eastgate.com/garden/) | |
| 17 | #+begin_quote | |
| 18 | Often, however, designers should strive for the comfort, interest, and | |
| 19 | habitability of parks and gardens: places that invite visitors to | |
| 20 | remain, and that are designed to engage and delight them, to invite them | |
| 21 | to linger, to explore, and to reflect. | |
| 22 | 22 | |
| 23 | ## Git | |
| 23 | #+end_quote | |
| 24 | ||
| 25 | [[https://www.eastgate.com/garden/][Hypertext Garden]] | |
| 26 | ||
| 27 | * Git | |
| 24 | 28 | |
| 25 | 29 | I want to get rid of all local modifications and go back to the working |
| 26 | 30 | tree of the most recent commit: |
| 27 | 31 | |
| 28 | ```sh | |
| 32 | #+begin_src sh | |
| 29 | 33 | git restore . |
| 30 | ``` | |
| 34 | #+end_src | |
| 31 | 35 | |
| 32 | 36 | Revert a specified commit: |
| 33 | 37 | |
| 34 | ```sh | |
| 38 | #+begin_src sh | |
| 35 | 39 | git revert commit-id |
| 36 | ``` | |
| 40 | #+end_src | |
| 37 | 41 | |
| 38 | 42 | Reset the repository to a specific commit in the git log: |
| 39 | 43 | |
| 40 | ```sh | |
| 44 | #+begin_src sh | |
| 41 | 45 | git reset --mixed commit-id |
| 42 | ``` | |
| 46 | #+end_src | |
| 43 | 47 | |
| 44 | 48 | I need to commit and push changes to a remote that has been changed |
| 45 | 49 | since my most recent pull: |
| 46 | 50 | |
| 47 | ```sh | |
| 51 | #+begin_src sh | |
| 48 | 52 | git pull --rebase |
| 49 | ``` | |
| 53 | #+end_src | |
| 50 | 54 | |
| 51 | ## Hardware | |
| 55 | * Hardware | |
| 52 | 56 | |
| 53 | ### Laptops | |
| 57 | ** Laptops | |
| 54 | 58 | |
| 55 | #### macOS | |
| 59 | *** macOS | |
| 56 | 60 | |
| 57 | 61 | | Category | Details | |
| 58 | | -------- | --------------- | | |
| 59 | | Model | Macbook Pro 16" | | |
| 62 | |----------+-----------------| | |
| 63 | | Model | Macbook Pro 16” | | |
| 60 | 64 | | CPU | Apple M2 Pro | |
| 61 | 65 | | RAM | 16GB | |
| 62 | 66 | | Storage | 512GB SSD | |
| 63 | 67 | |
| 64 | #### Linux | |
| 68 | *** Linux | |
| 65 | 69 | |
| 66 | 70 | | Category | Details | |
| 67 | | -------- | ------------------------------------------- | | |
| 71 | |----------+---------------------------------------------| | |
| 68 | 72 | | Model | Lenovo ThinkPad E15 Gen 4, model 21ED0048US | |
| 69 | 73 | | CPU | AMD Ryzen 5 5625U with Radeon Graphics | |
| 70 | 74 | | RAM | 16 GB | |
| 71 | 75 | | Storage | 256 GB SSD | |
| 72 | 76 | |
| 73 | ### Servers | |
| 77 | ** Servers | |
| 74 | 78 | |
| 75 | 79 | | Category | Details | |
| 76 | | ------------------ | -------------------------------------- | | |
| 80 | |--------------------+----------------------------------------| | |
| 77 | 81 | | Case | Rosewill RSV-R4100U 4U | |
| 78 | 82 | | Motherboard | NZXT B550 | |
| 79 | 83 | | CPU | AMD Ryzen 7 5700G with Radeon Graphics | |
| @@ -82,7 +86,7 @@ git pull --rebase | ||
| 82 | 86 | | Storage (HDD Bay) | 48TB HDD | |
| 83 | 87 | | PSU | Corsair RM850 PSU | |
| 84 | 88 | |
| 85 | ### Networking Equipment | |
| 89 | ** Networking Equipment | |
| 86 | 90 | |
| 87 | 91 | - UDM-Pro |
| 88 | 92 | - USW-24-PoE |
| @@ -96,9 +100,9 @@ git pull --rebase | ||
| 96 | 100 | - USW 24-Port Patch Panel |
| 97 | 101 | - USW Switch Lite 8 PoE |
| 98 | 102 | |
| 99 | ## Software | |
| 103 | * Software | |
| 100 | 104 | |
| 101 | ### Laptop | |
| 105 | ** Laptop | |
| 102 | 106 | |
| 103 | 107 | Alpine 3.18.2; no DE. |
| 104 | 108 | |
| @@ -128,7 +132,7 @@ I have Sway installed and configured, but only launch it when I must. | ||
| 128 | 132 | - zola |
| 129 | 133 | - zsh |
| 130 | 134 | |
| 131 | ### Server | |
| 135 | ** Server | |
| 132 | 136 | |
| 133 | 137 | Ubuntu 22.04.1; no DE. |
| 134 | 138 | |